
Exploit Database 2022 Update
Exploit Database 2022 Update
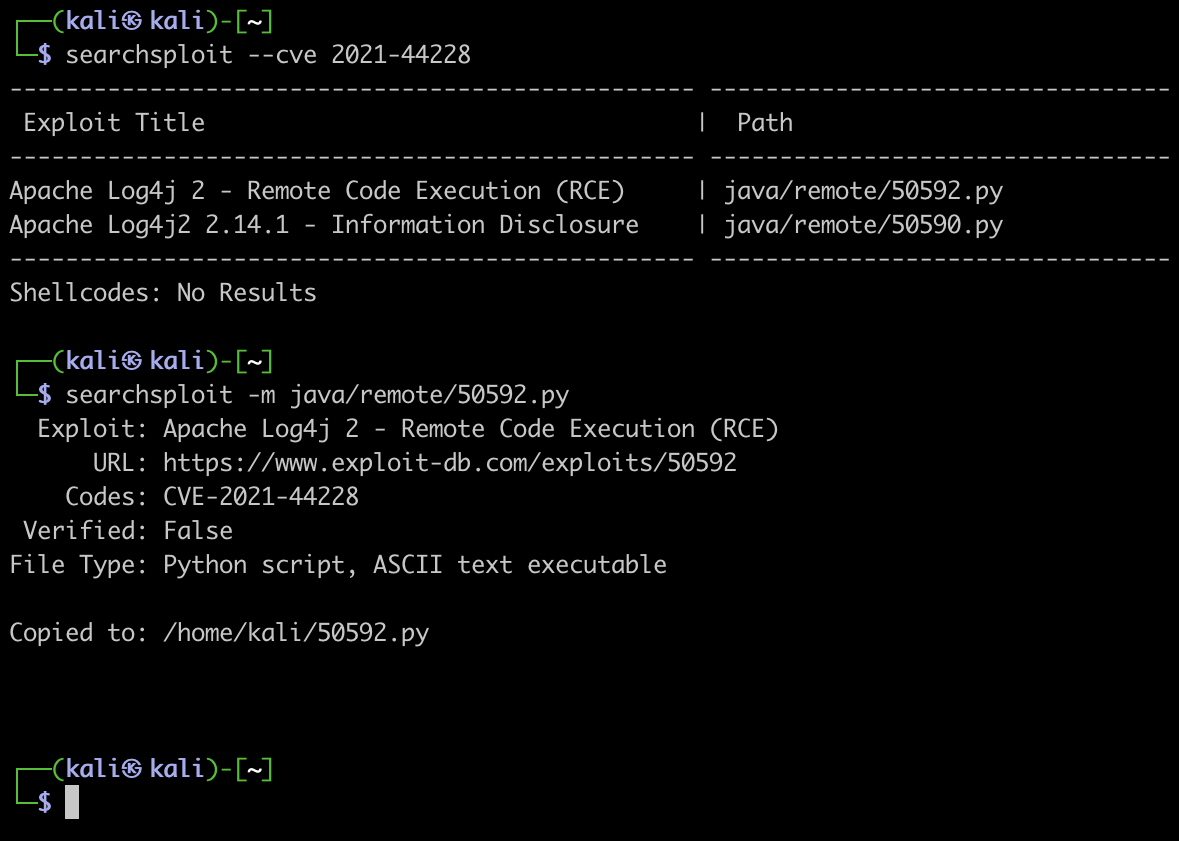
Exploit Database 2022 Update
Exploit Database SearchSploit Update | Offensive Security

Exploit Database | Learn With Exploit Database | 2022 - YouTube

An Update on the Oct 2022 Exploit | Sovryn

New Update KRNL Exploit January 2022 - YouTube
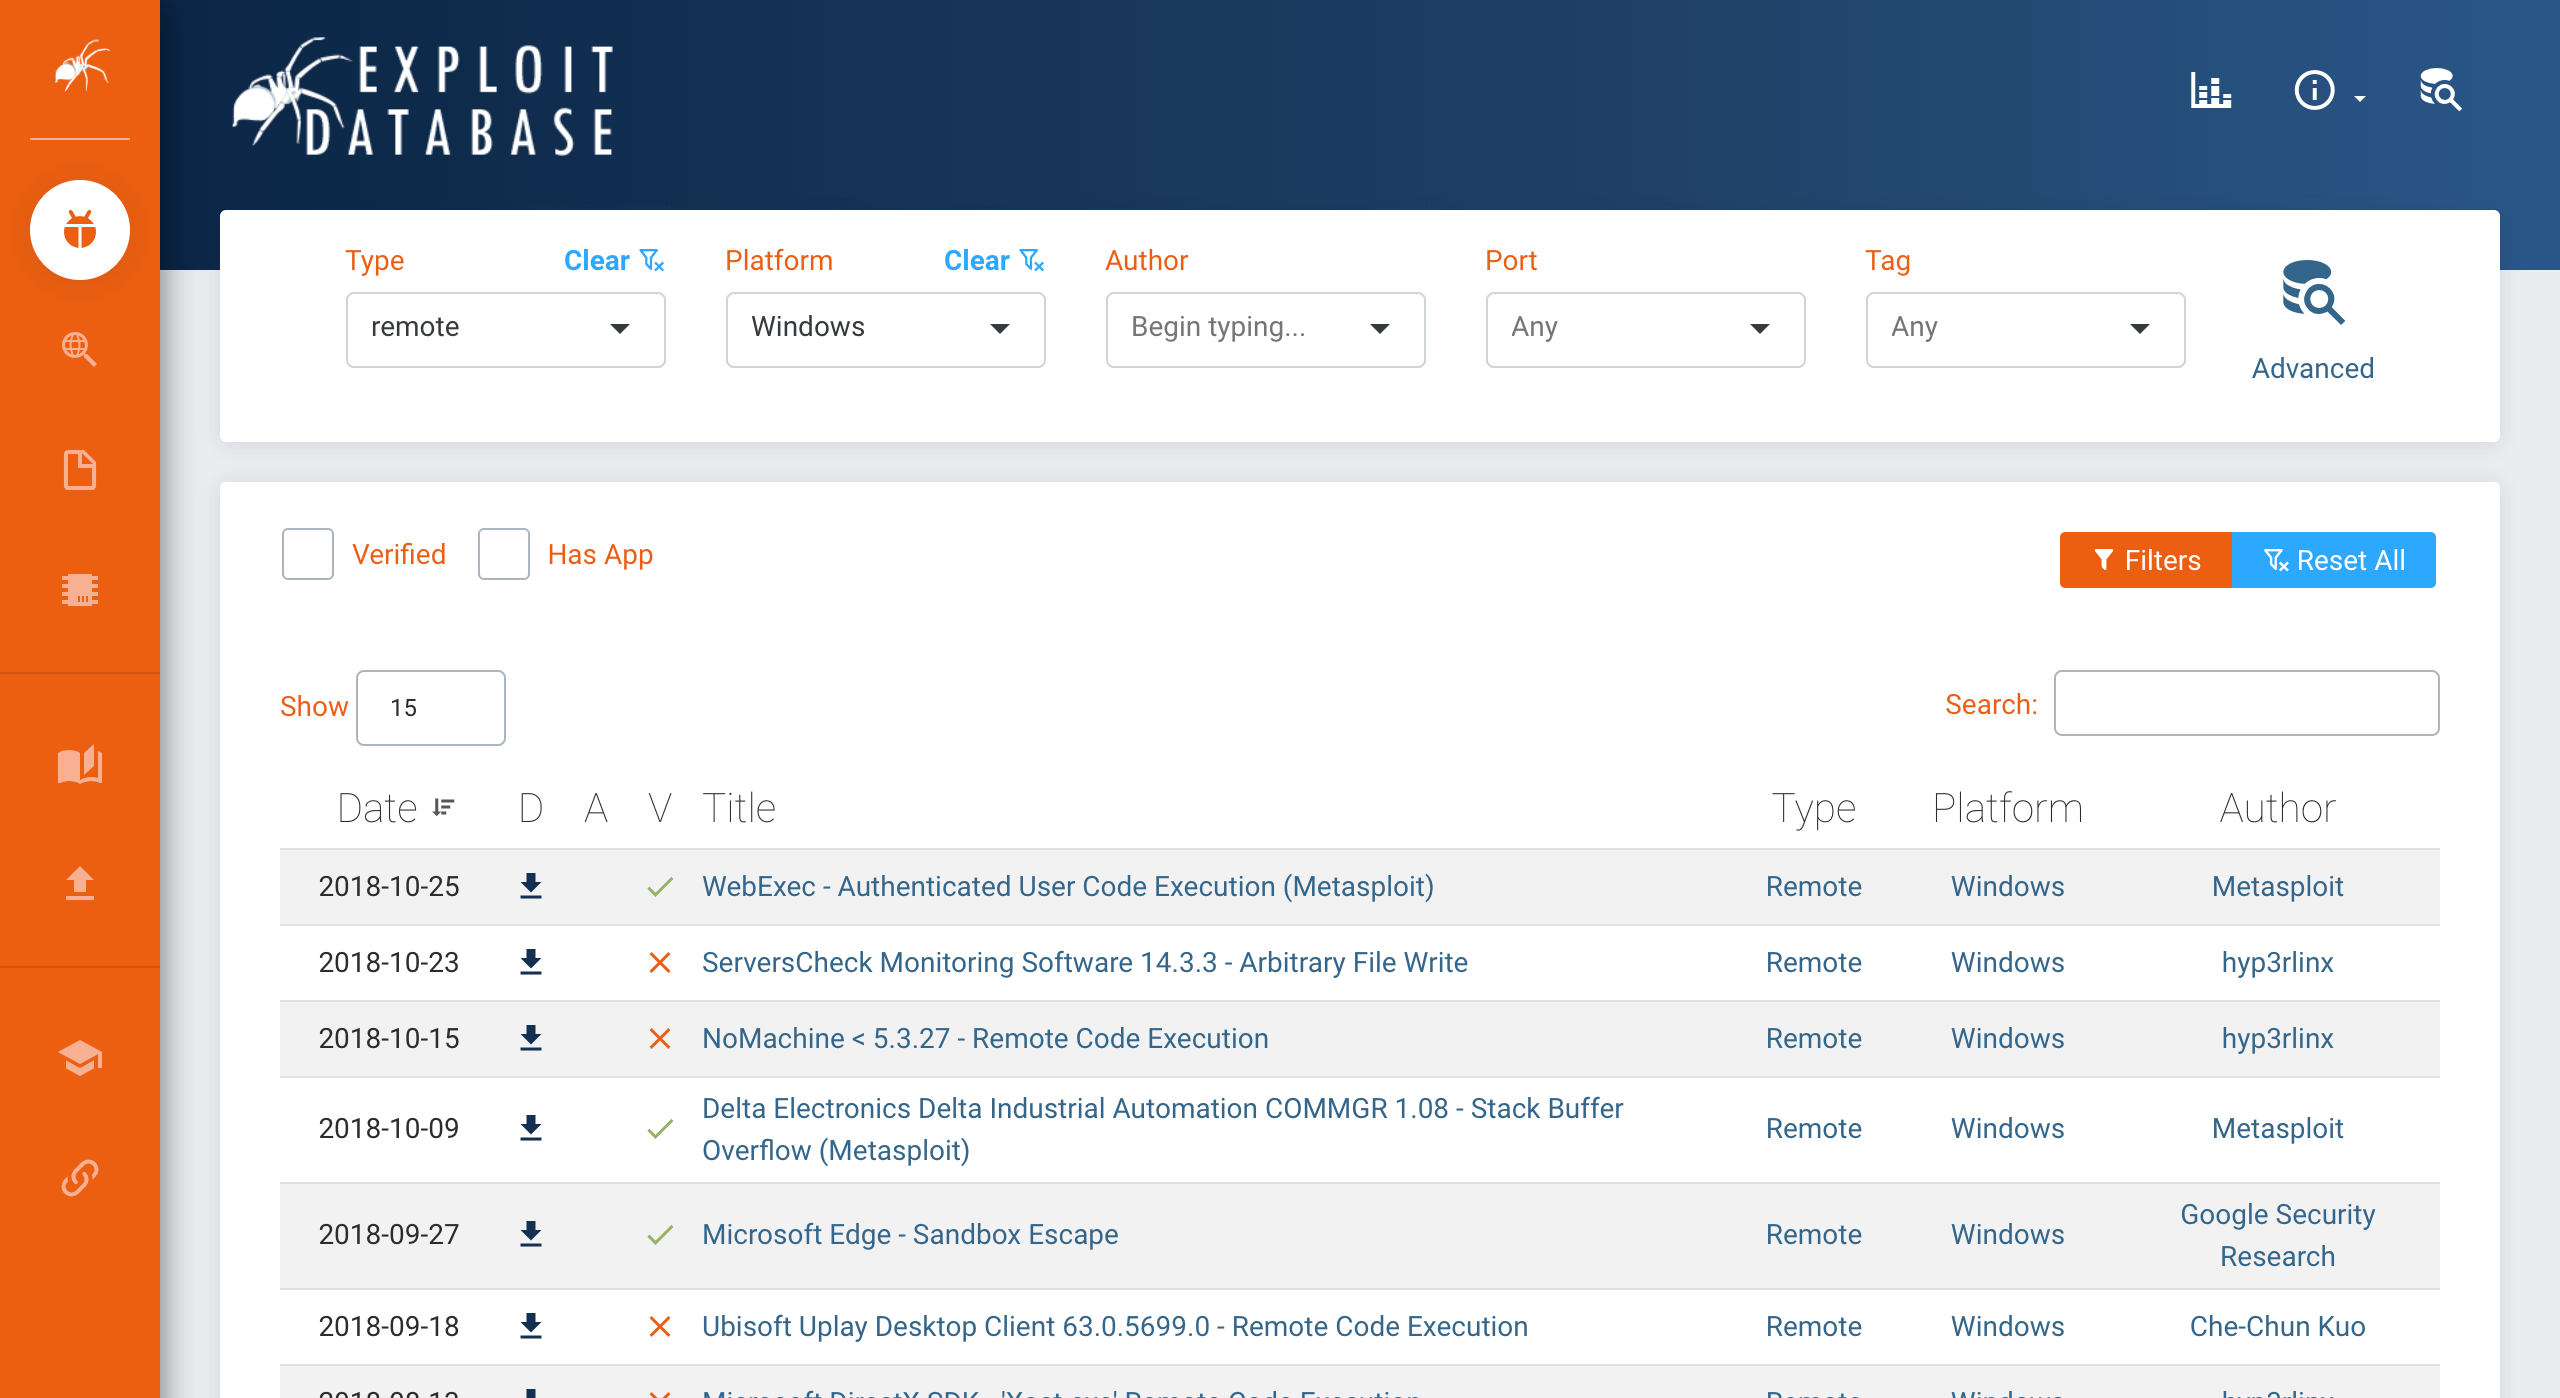
Exploit Database Redesign
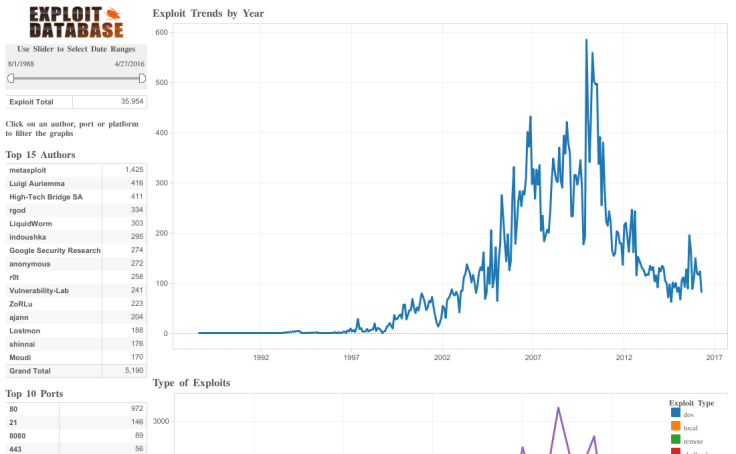
Workbook: Computer Exploit Database Visualized
Exploit Database Redesign
Exploit Database hosted on Github
Advertisement Space (300x250)
Exploit Database - EcuRed
Exploit Database Redesign

VulnCheck Exploit Database (XDB) | Community | VulnCheck
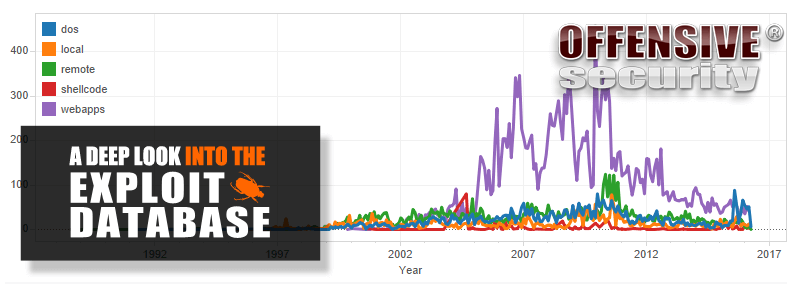
A Decade of Exploit Database Data
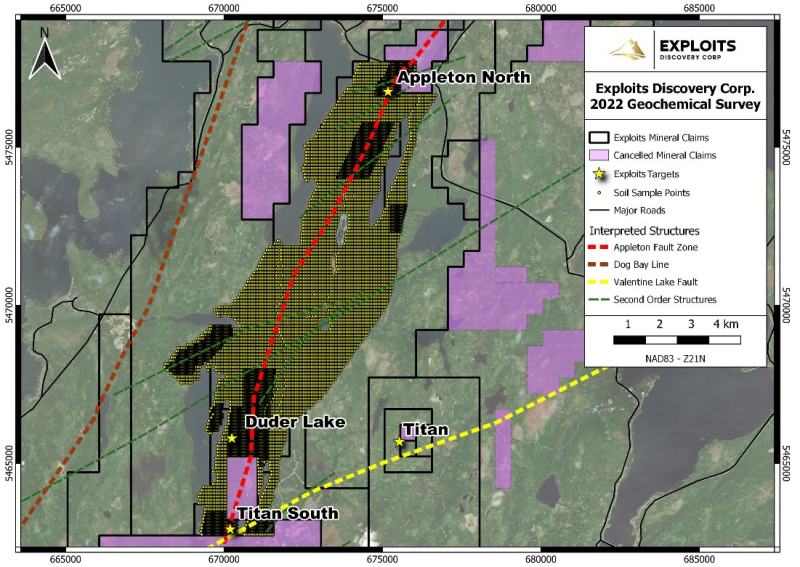
EXPLOITS Provides an Update of 2022 Exploration Plans and Remaining ...

Exploit Prevention Update - Announcements - Developer Forum | Roblox
GitHub - offensive-security/exploitdb: The legacy Exploit Database ...

Update Windows now to patch this critical Microsoft Word exploit CVE ...

Keysight’s Take on CVE-2022-30190 MSDT Follina Exploit

Atlassian Bitbucket Server and Data Center Exploit - CVE-2022-36804 ...
Advertisement Space (336x280)

Keysight’s Take on CVE-2022-30190 MSDT Follina Exploit
Q2-2022 API Vulnerability & Exploit full report - Wallarm
Zoho ManageEngine Exploit Attempt - CVE-2022-47966 — ExtraHop
Windows HTTP Stack Exploit Attempt - CVE-2022-21907 — ExtraHop
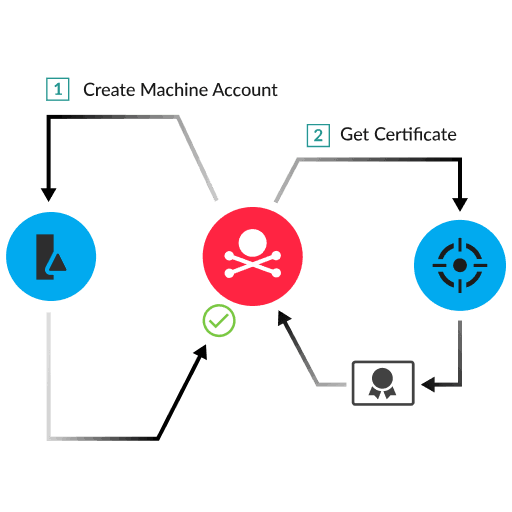
Active Directory Domain Services Exploit Attempt - CVE-2022-26923 ...
Threat Advisory: Monitoring CVE-2022-42889 "Text4Shell" Exploit Attempts

WSO2 Exploit Attempt - CVE-2022-29464 — ExtraHop
Spring4Shell Exploit Attempt - CVE-2022-22965 — ExtraHop
Oct 2023 Cybercrime Update | Disinformation, DDoS and Scams as Gangs ...

Keysight’s Take on CVE-2022-30190 MSDT Follina Exploit
Advertisement Space (336x280)
CVE-2022-39952: FortiNAC Remote Code Execution Exploit Explained

CVE-2022-41974, CVE-2022-41973, CVE-2022-3328 Exploit Detection: Three ...
Mitigating Apache Commons Text Exploit - CVE-2022-42889 - Oracle Forums

ASEC Weekly Malware Statistics (October 3rd, 2022 – October 9th, 2022 ...
News Explorer — Nearly $1M Stolen From Balancer After Exploit Alert ...