
Adding And Configuring Inputs Splunk Cloud Platform Last Updated
Adding and configuring inputs | Splunk Cloud Platform (last updated ...
Adding and configuring inputs | Splunk Cloud Platform (last updated ...
Create modular inputs | Splunk Cloud Platform (last updated 2025-07 ...
Create modular inputs | Splunk Cloud Platform (last updated 2025-07 ...
Modular inputs basic example | Splunk Cloud Platform (last updated 2025 ...
Modular inputs basic example | Splunk Cloud Platform (last updated 2025 ...
Inputs | Splunk Enterprise, Splunk Cloud Platform (last updated 2026-05 ...
Inputs | Splunk Enterprise, Splunk Cloud Platform (last updated 2026-05 ...
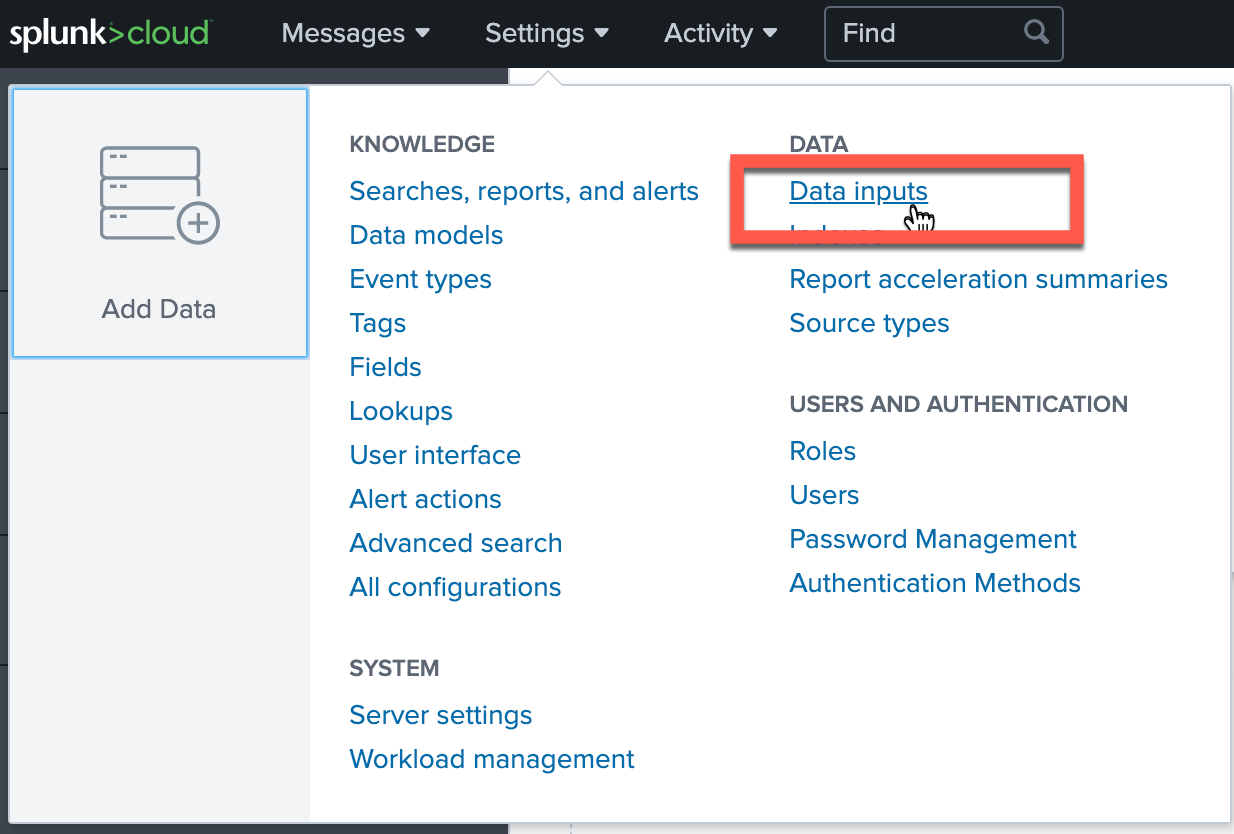
Splunk Cloud Platform and BYOL Integrations | Cribl Docs

Installing and Configuring for Splunk Cloud
Advertisement Space (300x250)
Developer tools for modular inputs | Splunk Cloud Platform (last ...
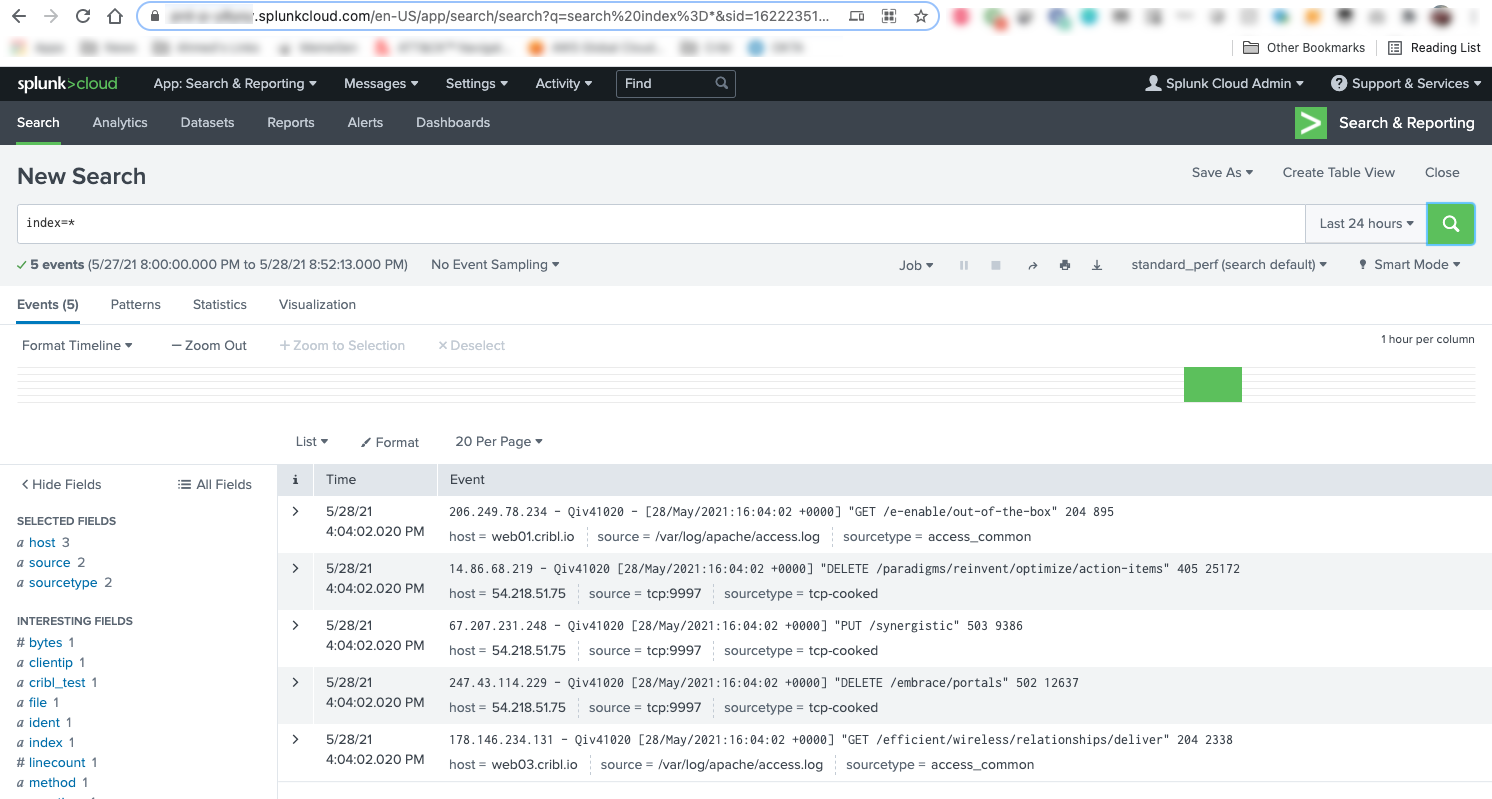
Splunk Cloud Platform and BYOL Integrations | Cribl Docs

Installing and Configuring for Splunk Cloud

Installing and Configuring for Splunk Cloud
Use inputs to make dashboards dynamic | Splunk Cloud Platform (last ...
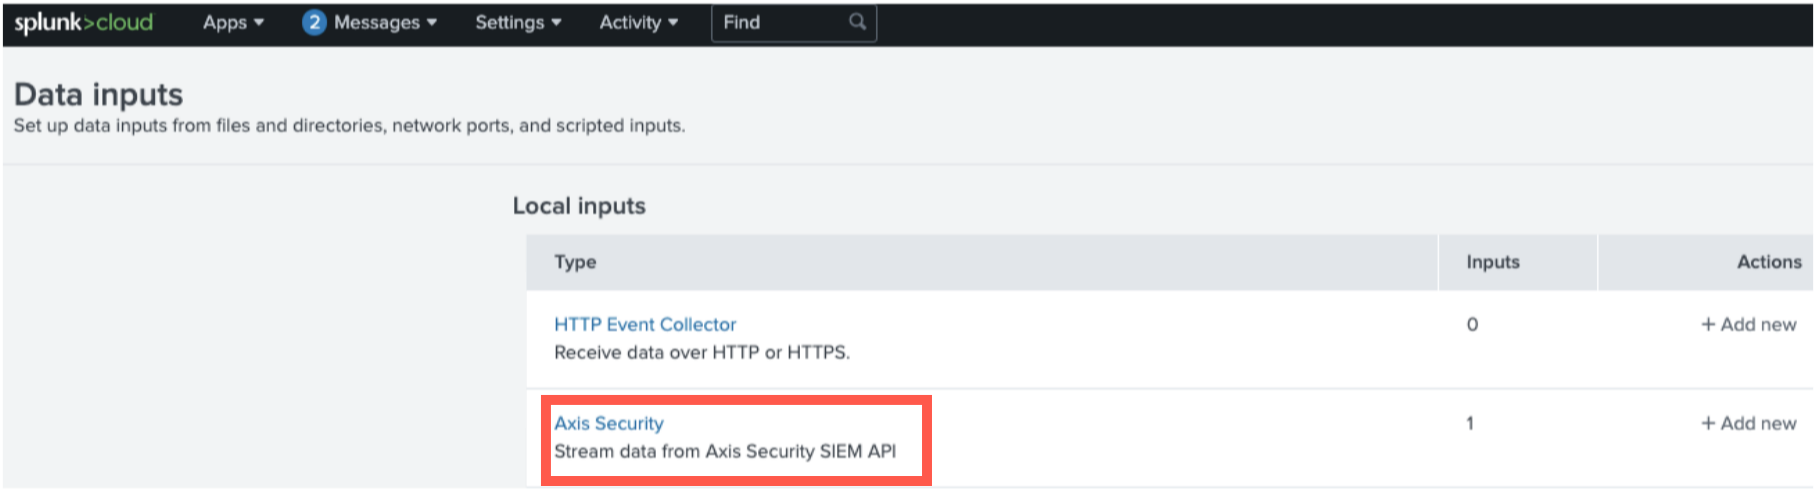
Sending Logs to Splunk Enterprise and Splunk Cloud
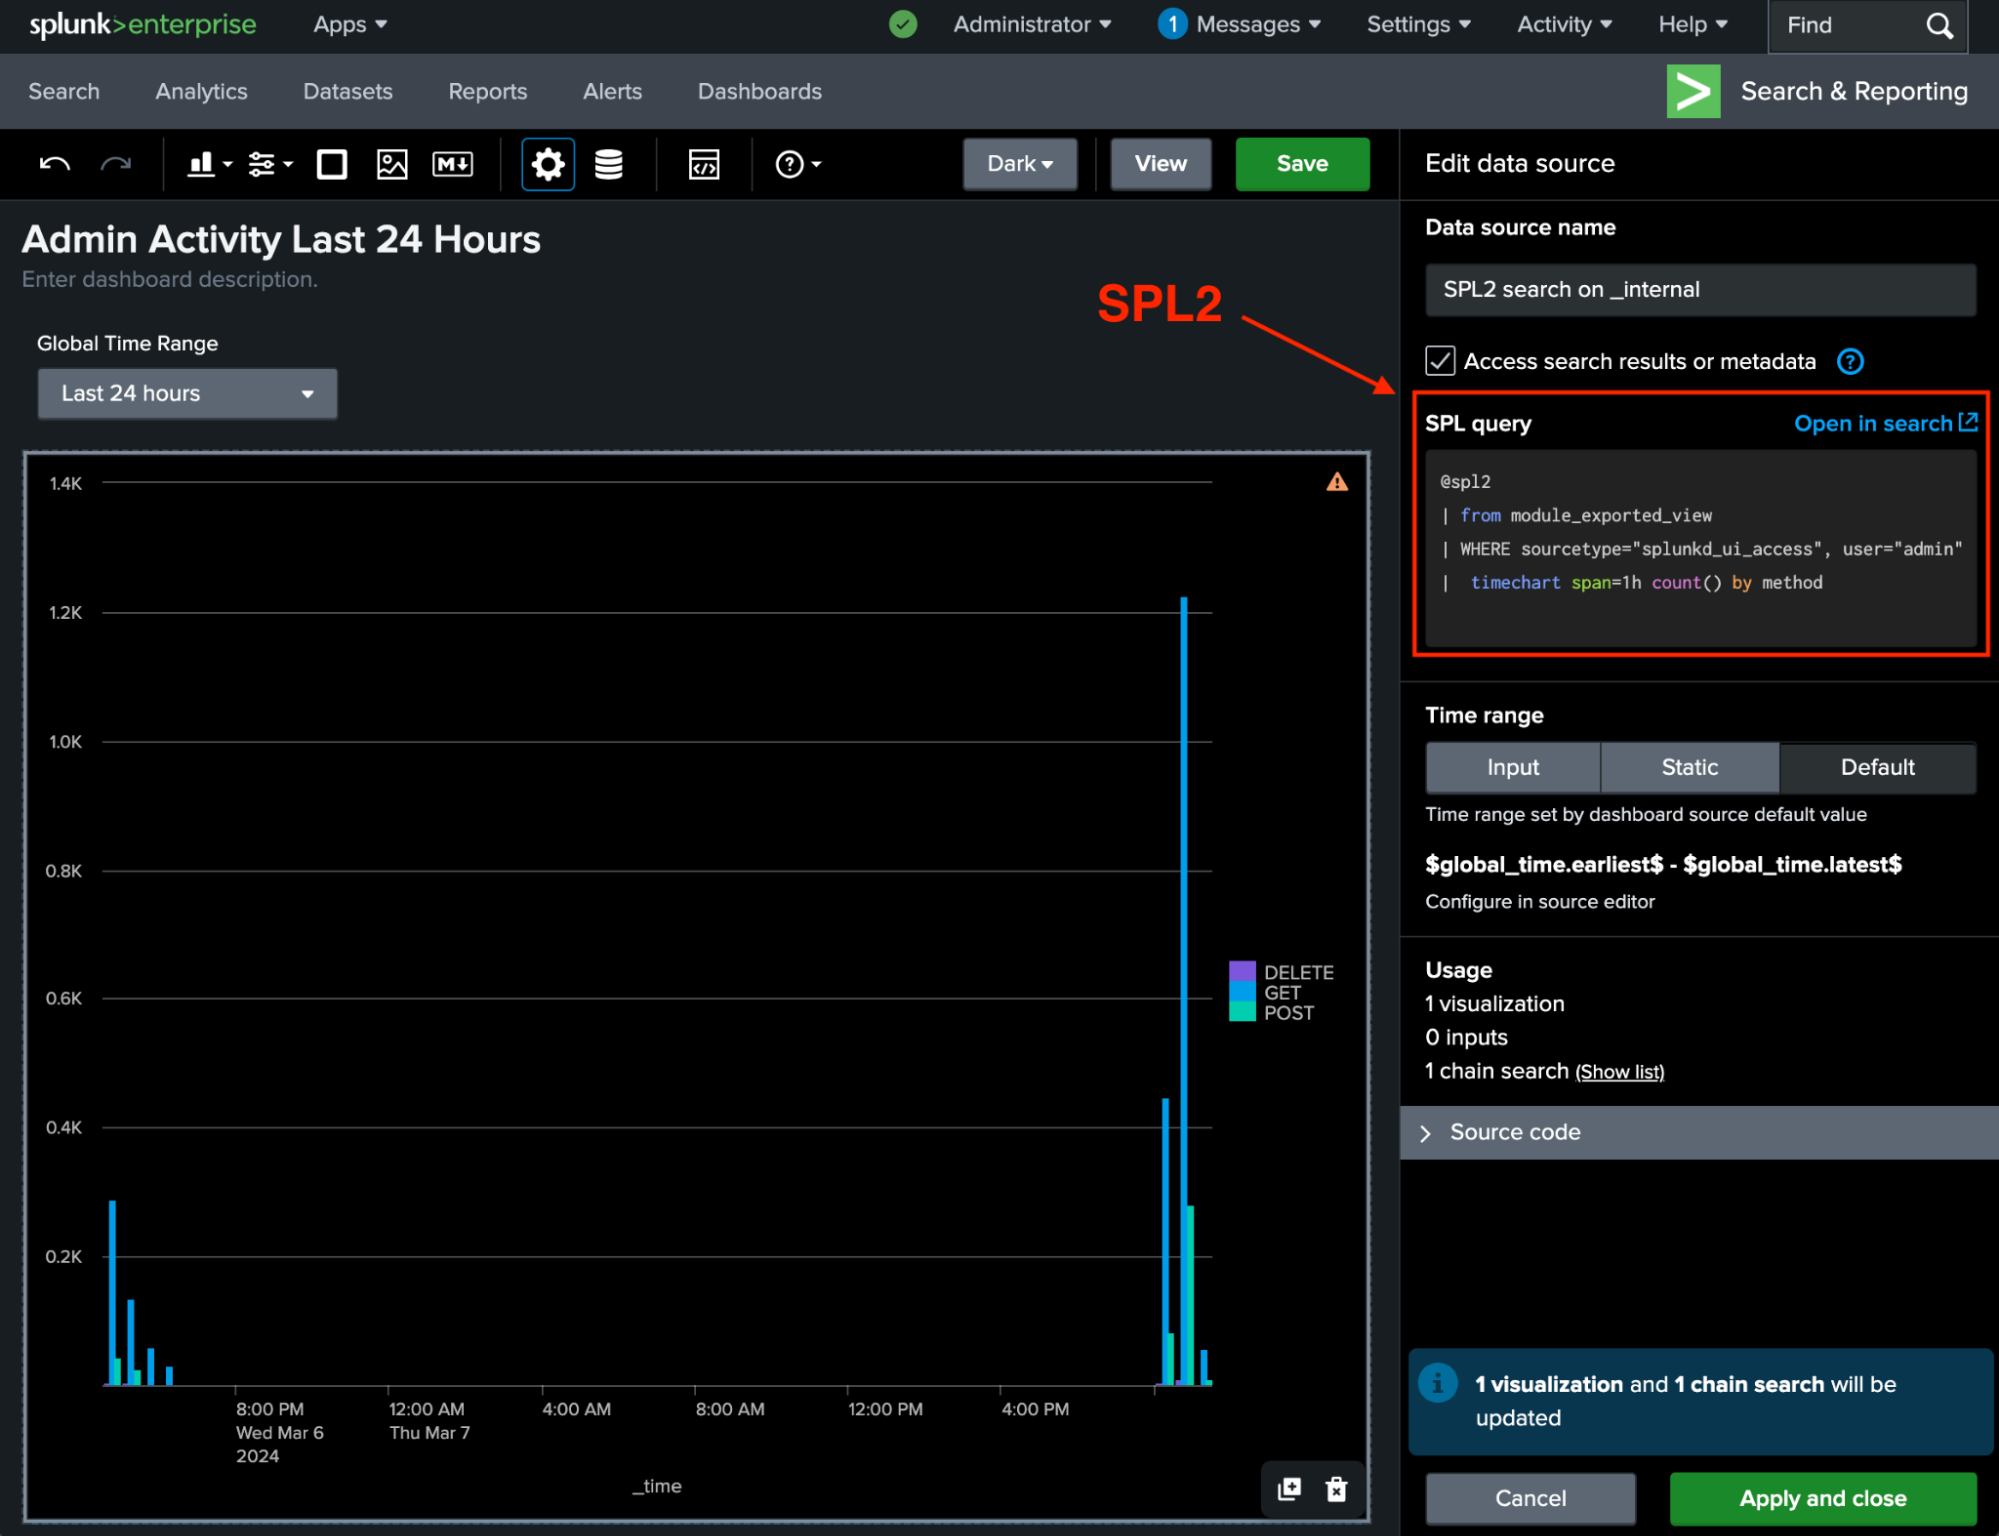
Introducing Inputs Data Manager on Splunk Cloud | Splunk
Monitor and correlate data for the Cisco Cloud Security Umbrella Splunk ...
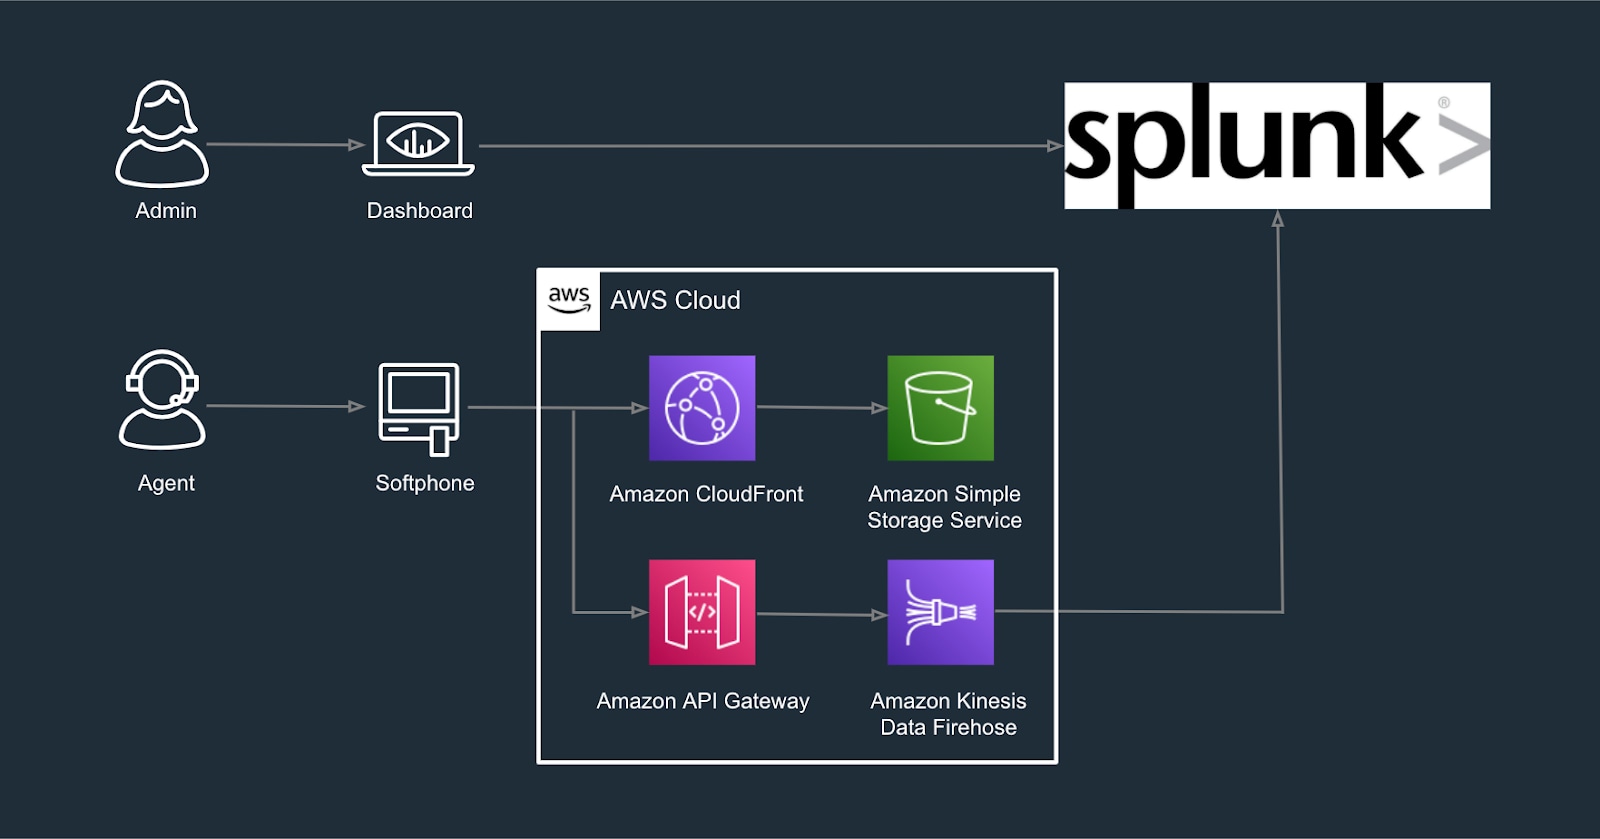
Introducing Inputs Data Manager on Splunk Cloud | Splunk
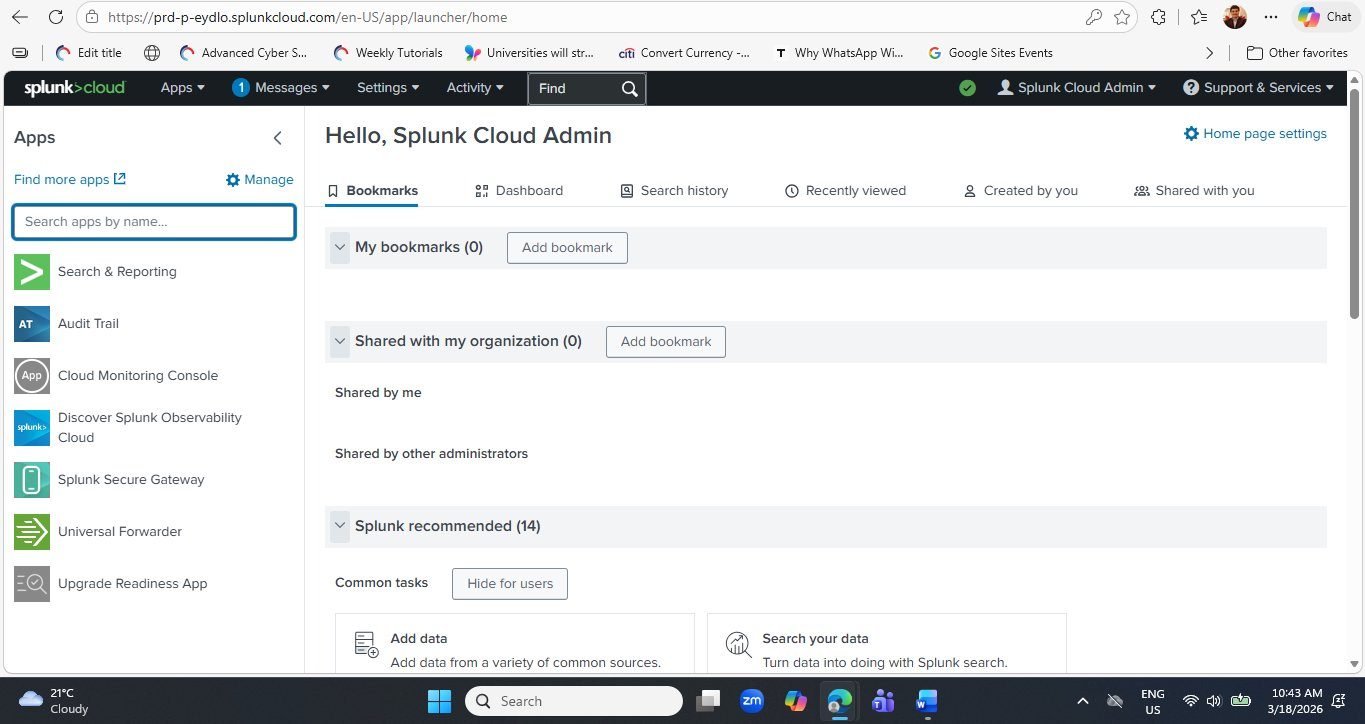
Getting Started with Splunk Cloud Platform 2026 — Step-by-Step Beginner ...
Advertisement Space (336x280)
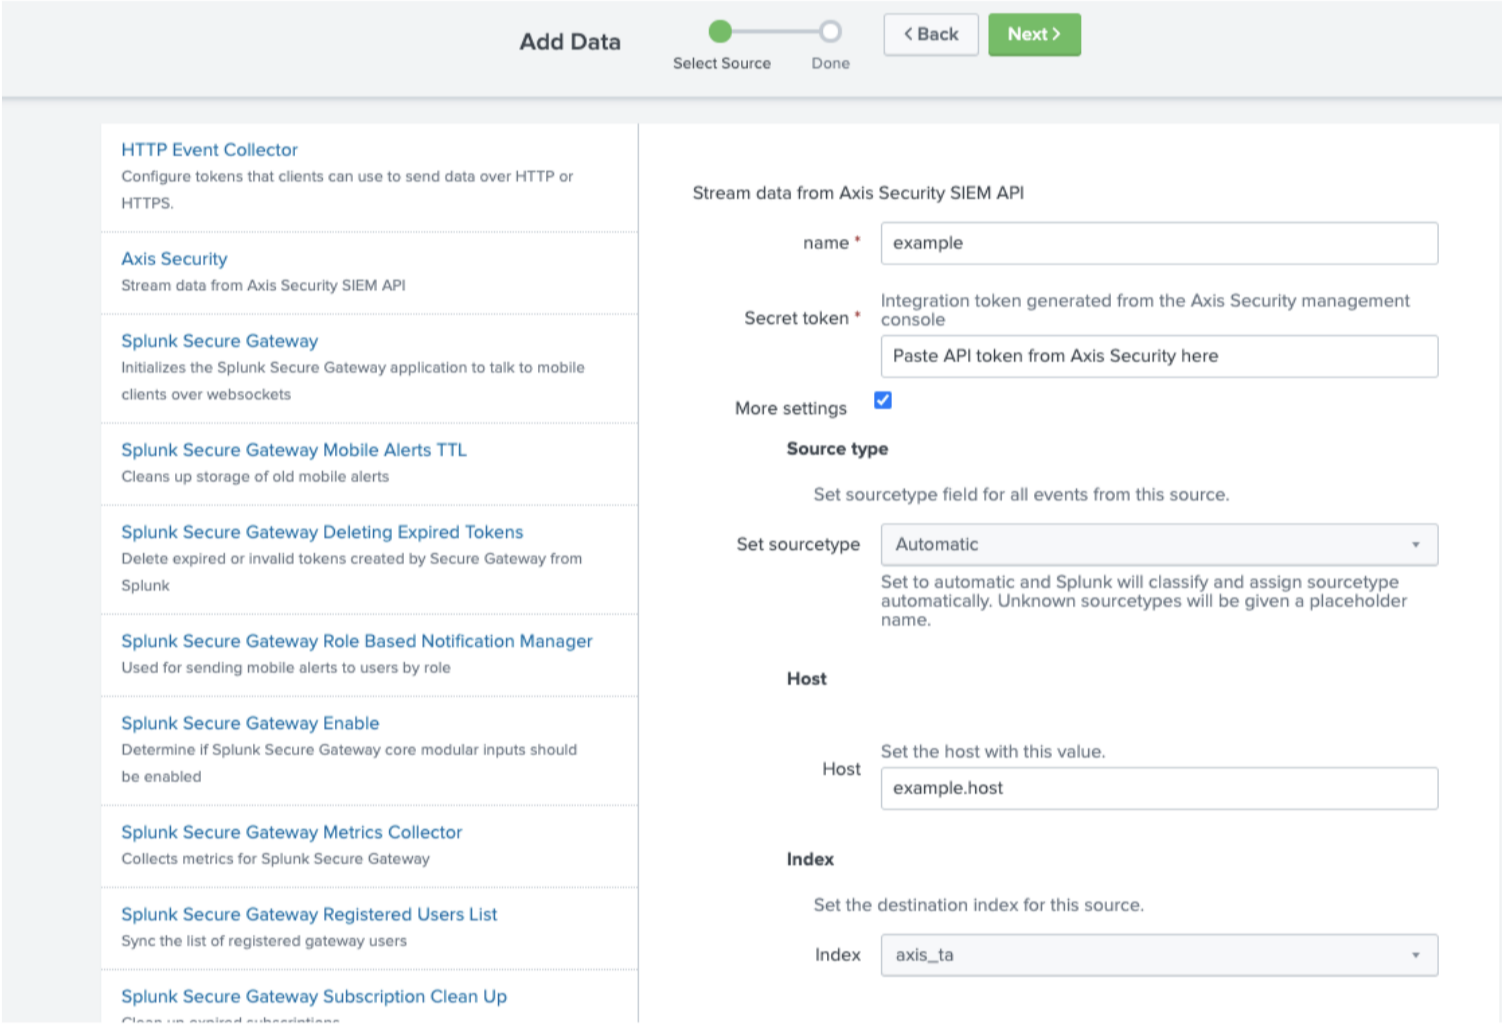
Sending Logs to Splunk Enterprise and Splunk Cloud
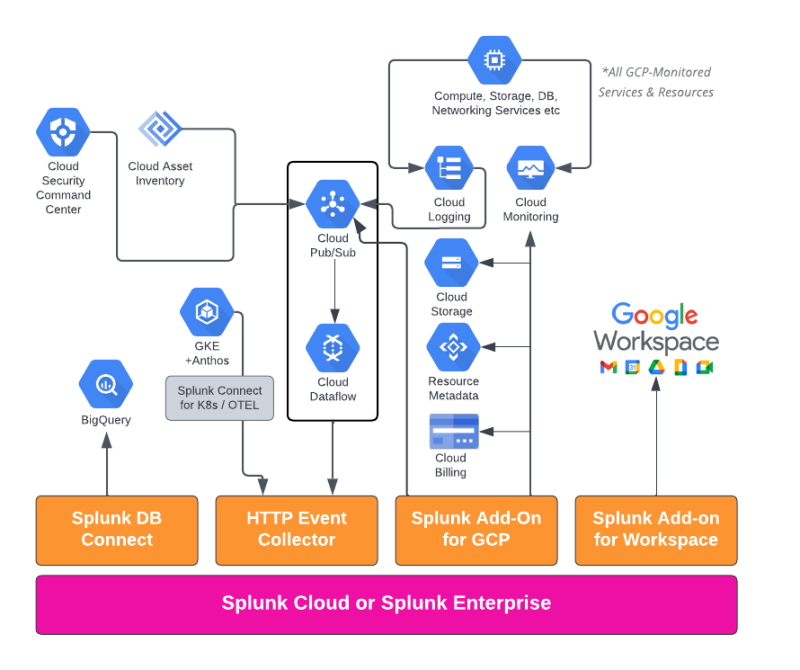
Getting Google Cloud Platform data into the Splunk platform - Splunk ...
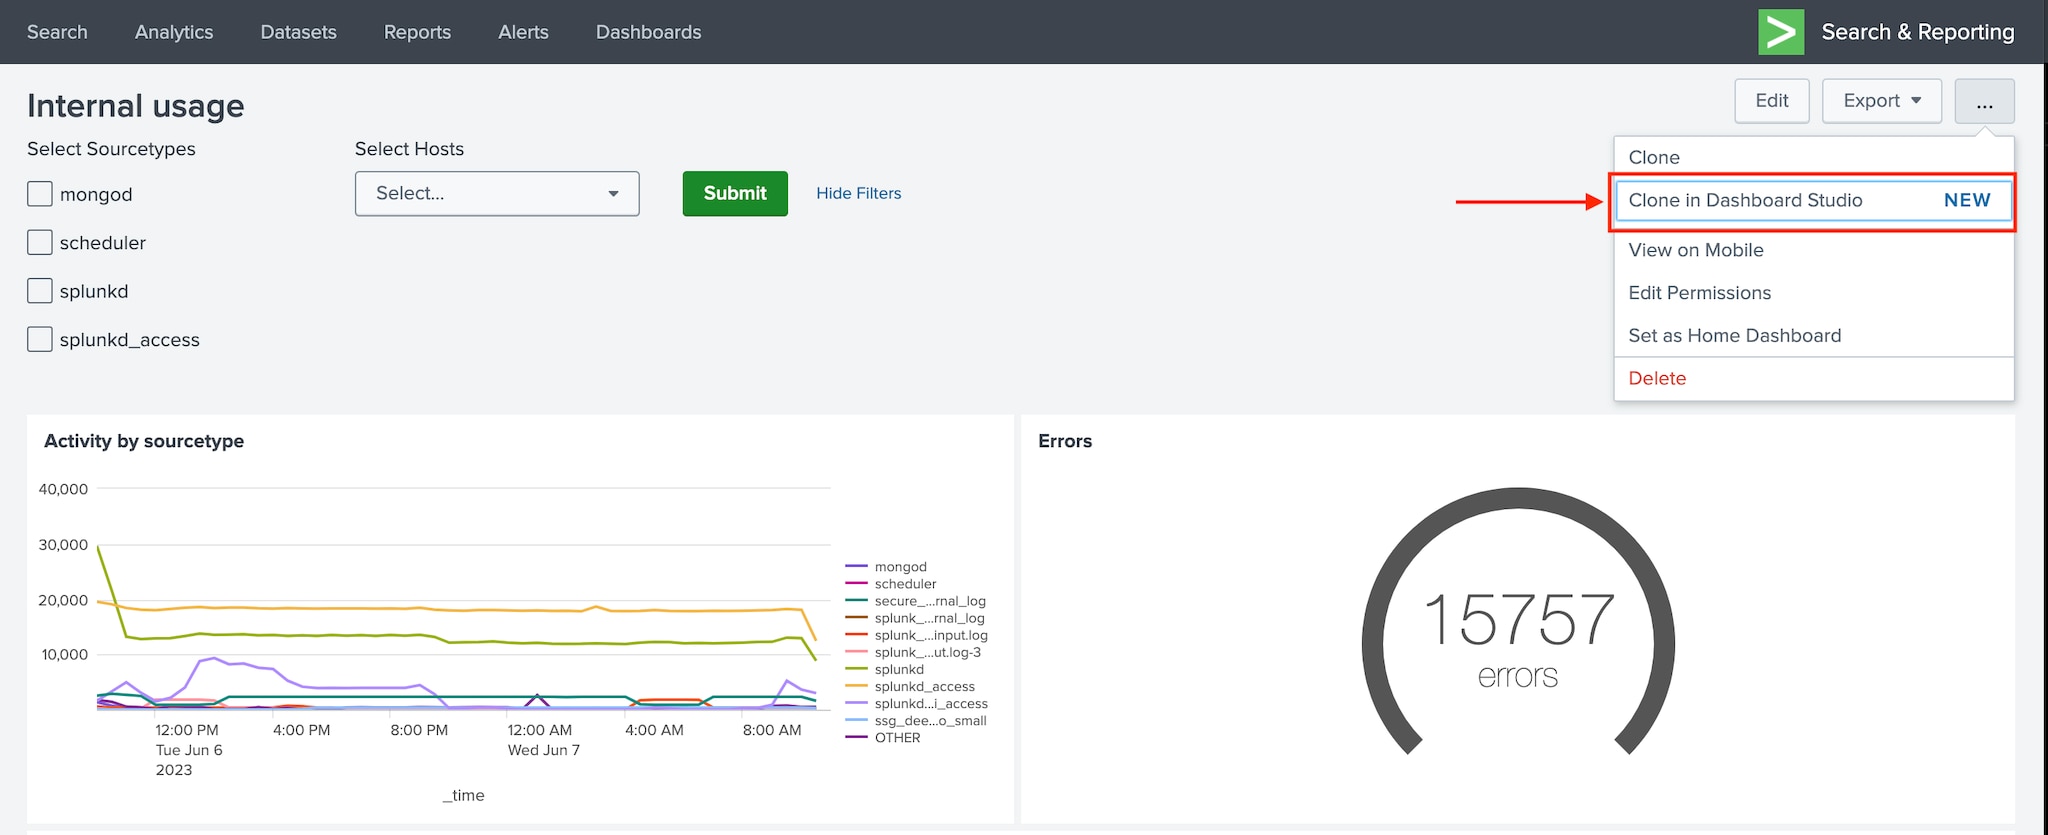
Dashboard Studio: Drilldown to New Features in Splunk Cloud Platform 9. ...
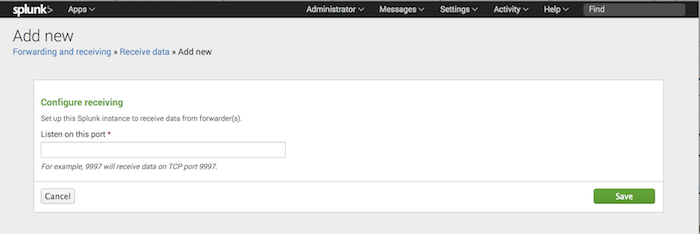
Install and configure a Splunk platform indexer - Splunk Documentation

What’s New in Splunk Cloud Platform 9.0.2305?! - Splunk Community

Configure IP allow lists for Splunk Cloud Platform | Splunk Cloud ...
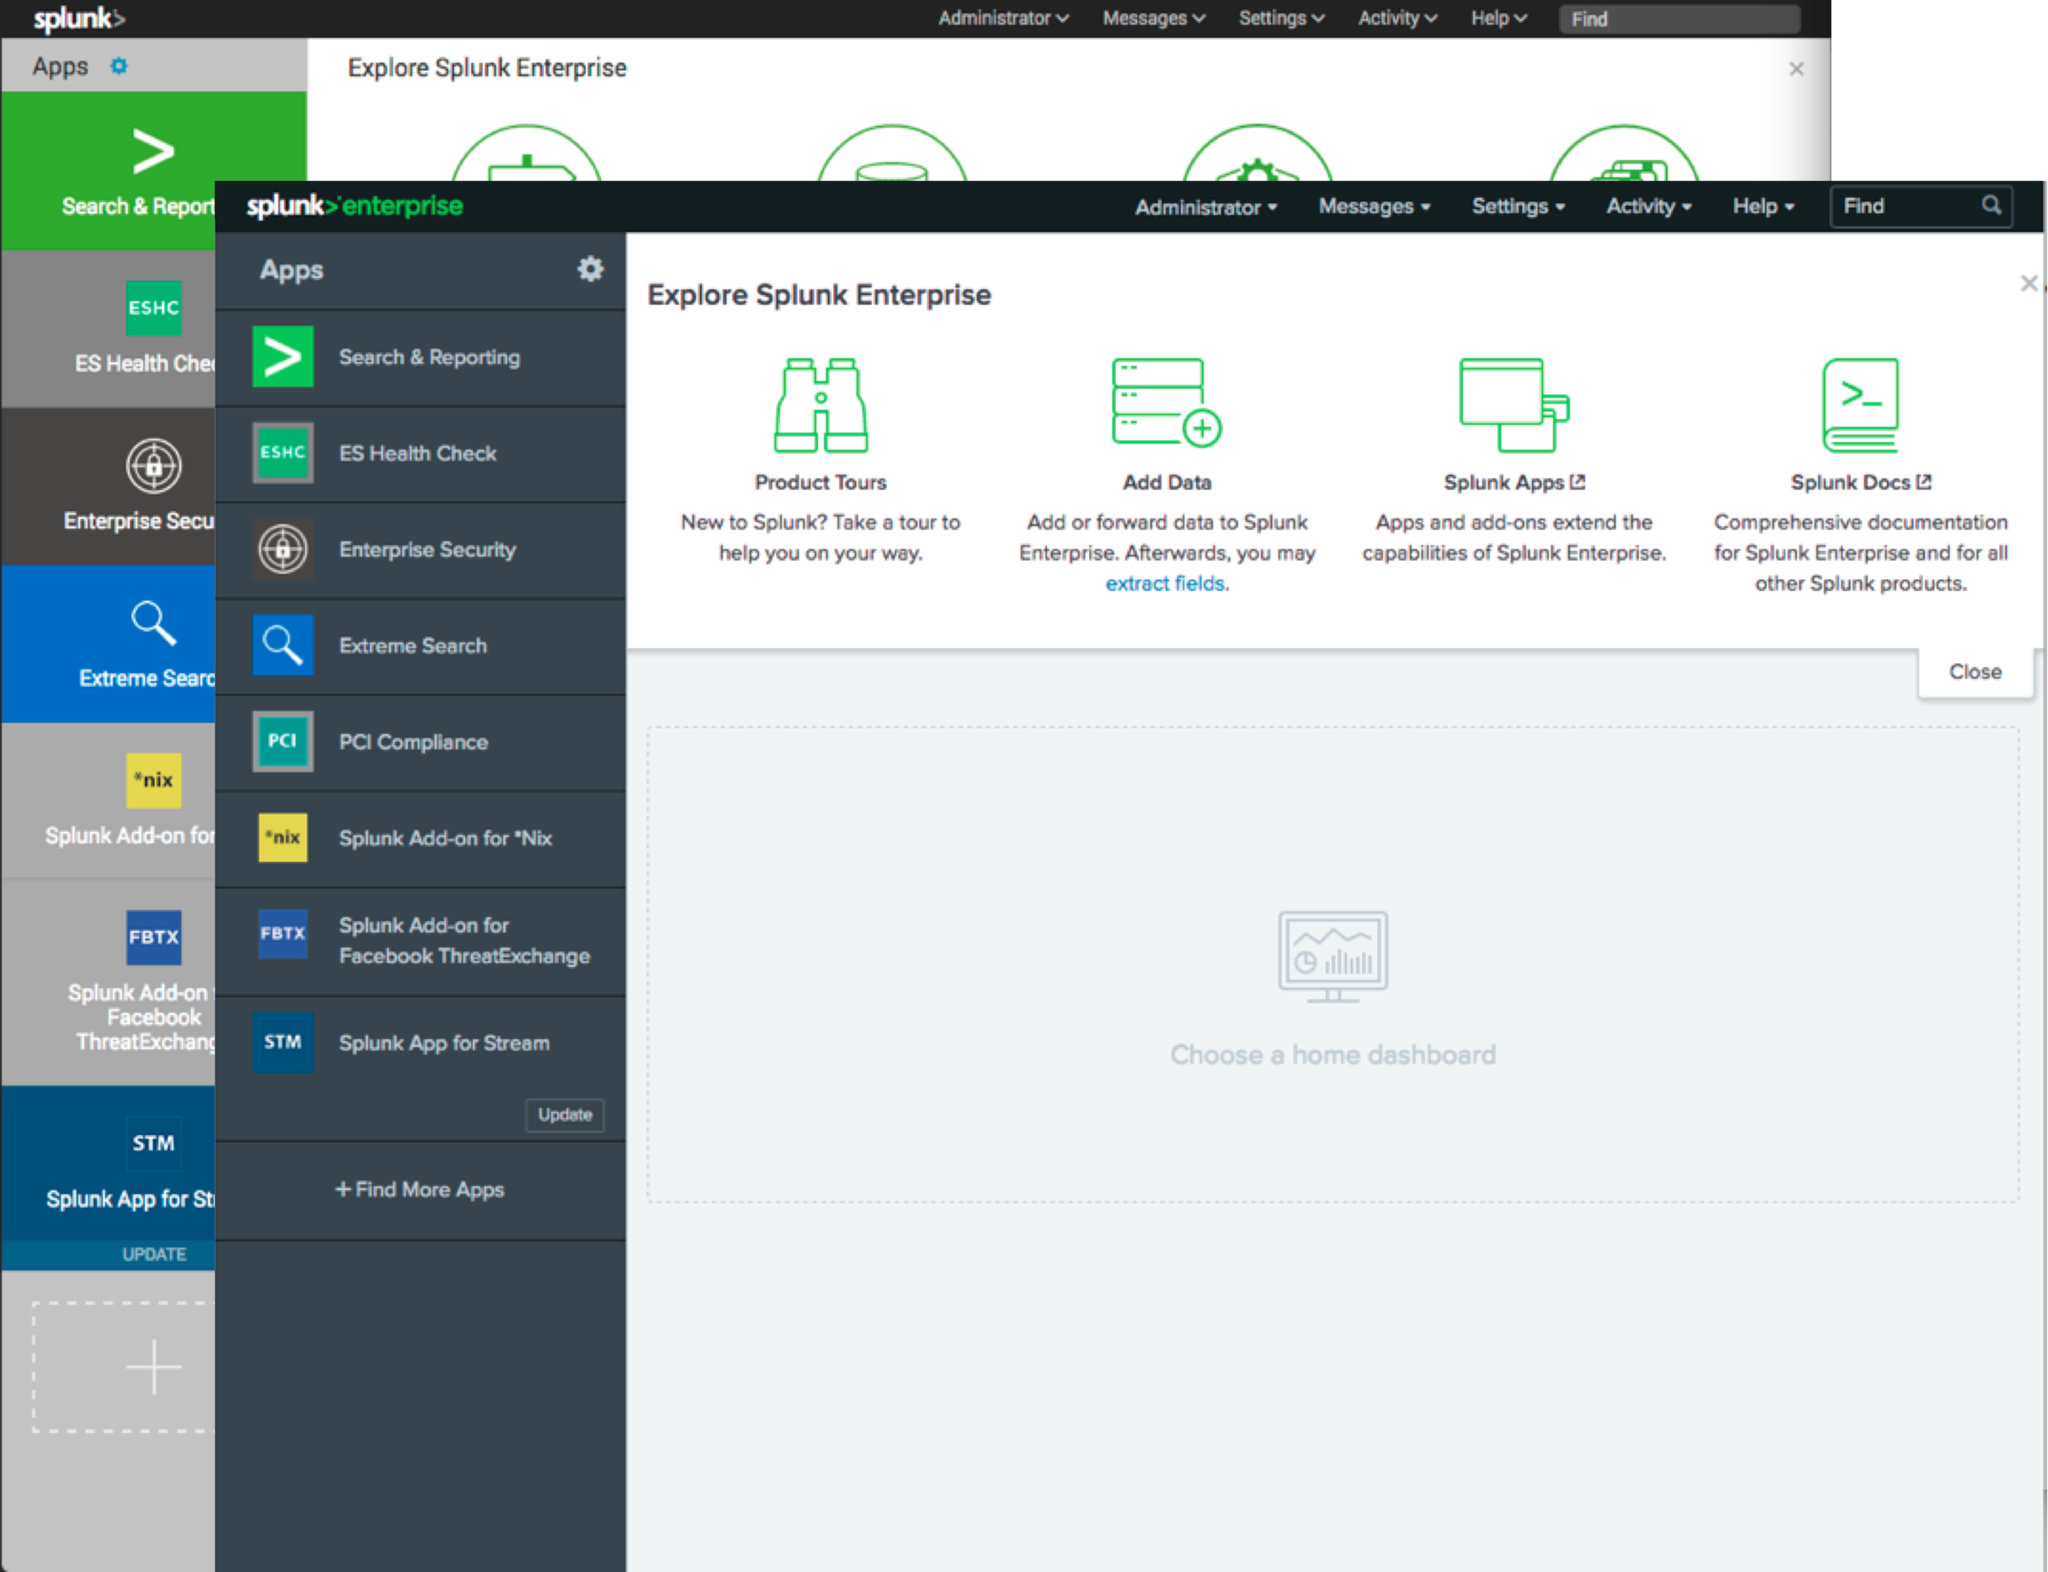
What's New in Splunk Cloud Platform | Splunk
A Unified Security and Observability Platform | Splunk
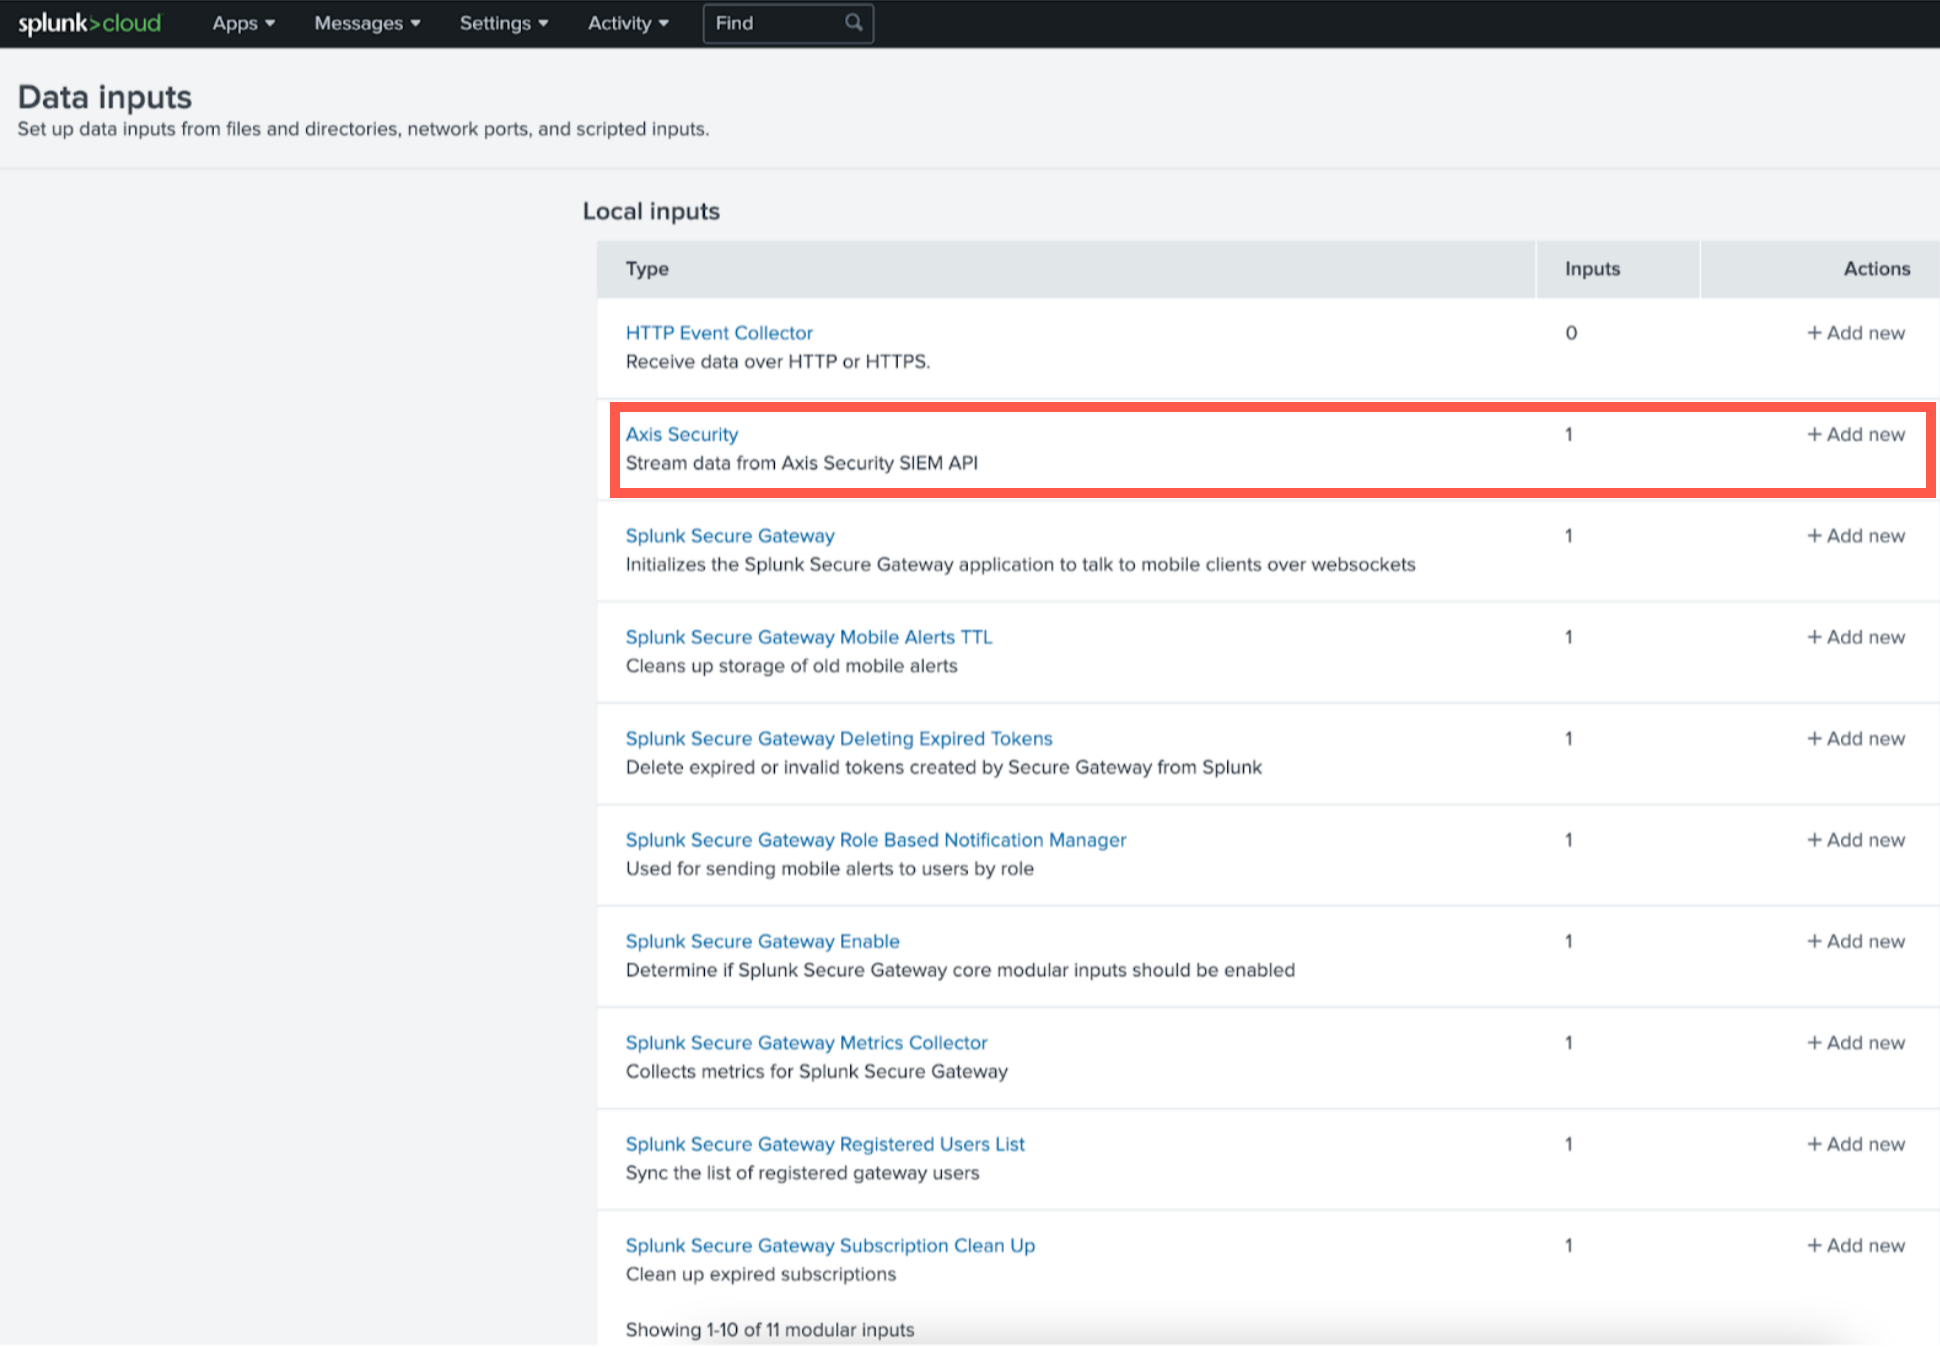
Sending Logs to Splunk Enterprise and Splunk Cloud
Configure Splunk UBA | Splunk Enterprise, Splunk Cloud Platform (last ...
Advertisement Space (336x280)
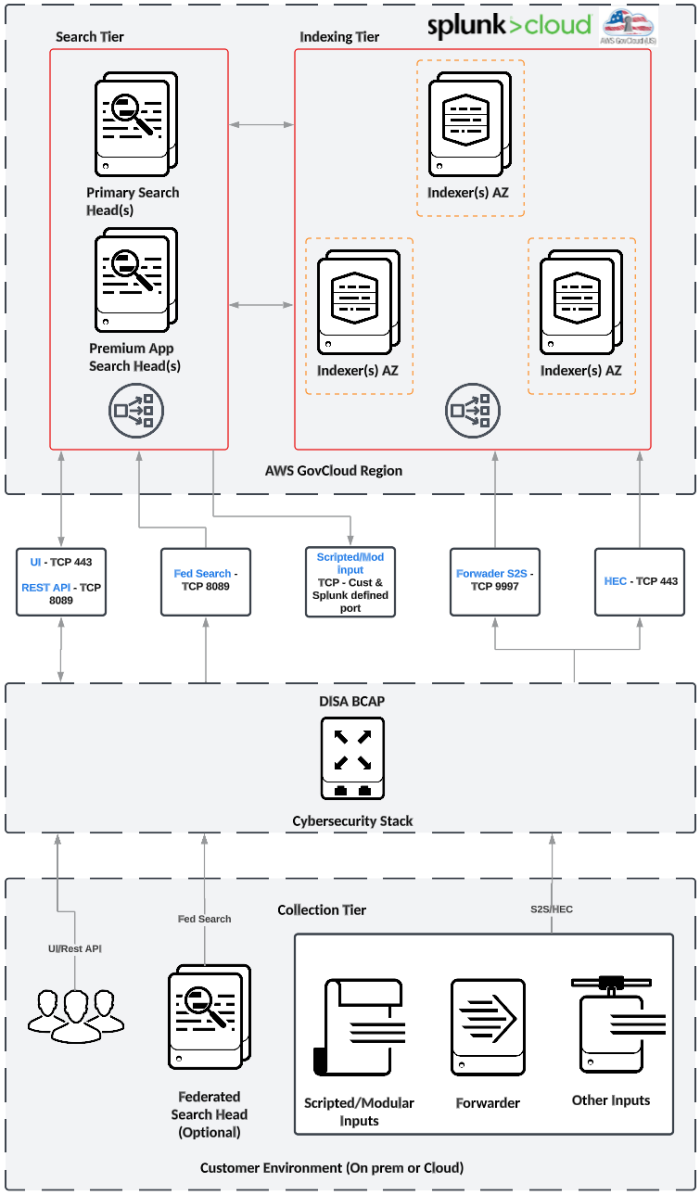
Splunk Cloud Platform IL5 - Splunk Documentation
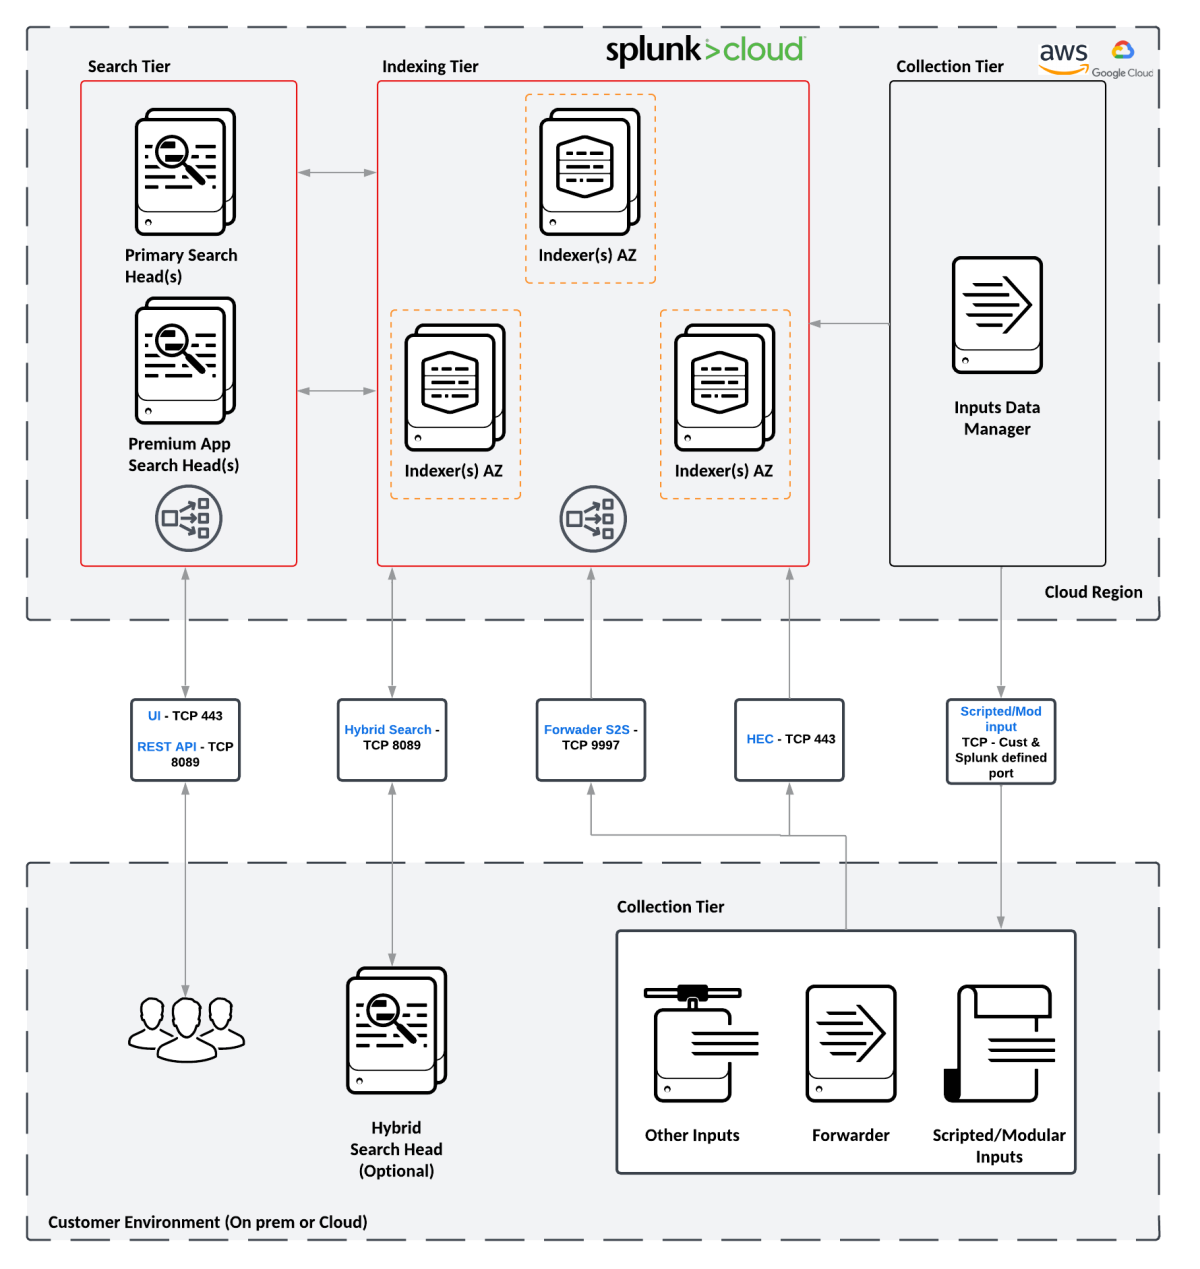
Splunk Cloud Platform Experiences - Splunk Documentation
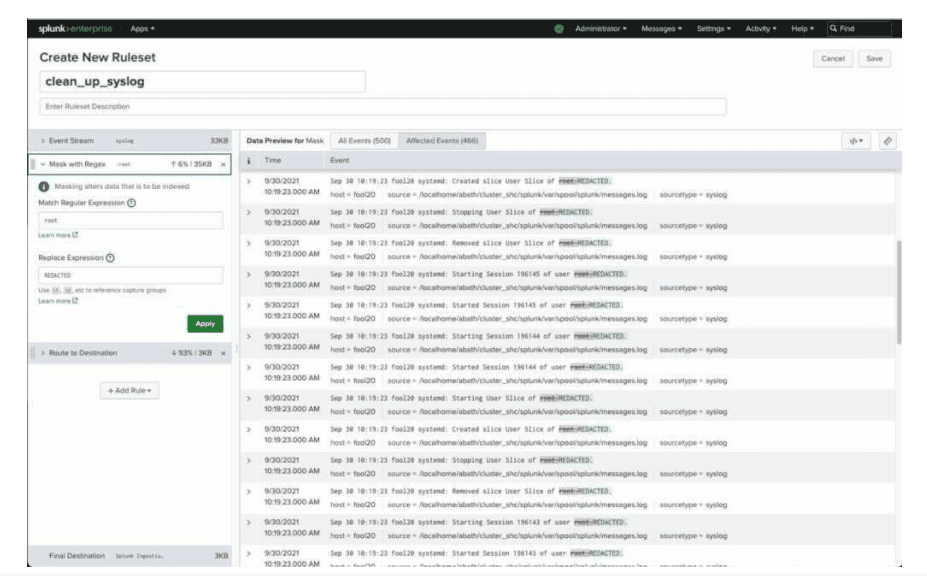
Splunk geeft Cloud Platform grote update - Techzine.nl

5 Splunk Monitoring and Creating Inputs - Jacob ElasticSearch7 Book

New Release | Splunk Cloud Platform 10.1.2507 - Splunk Community
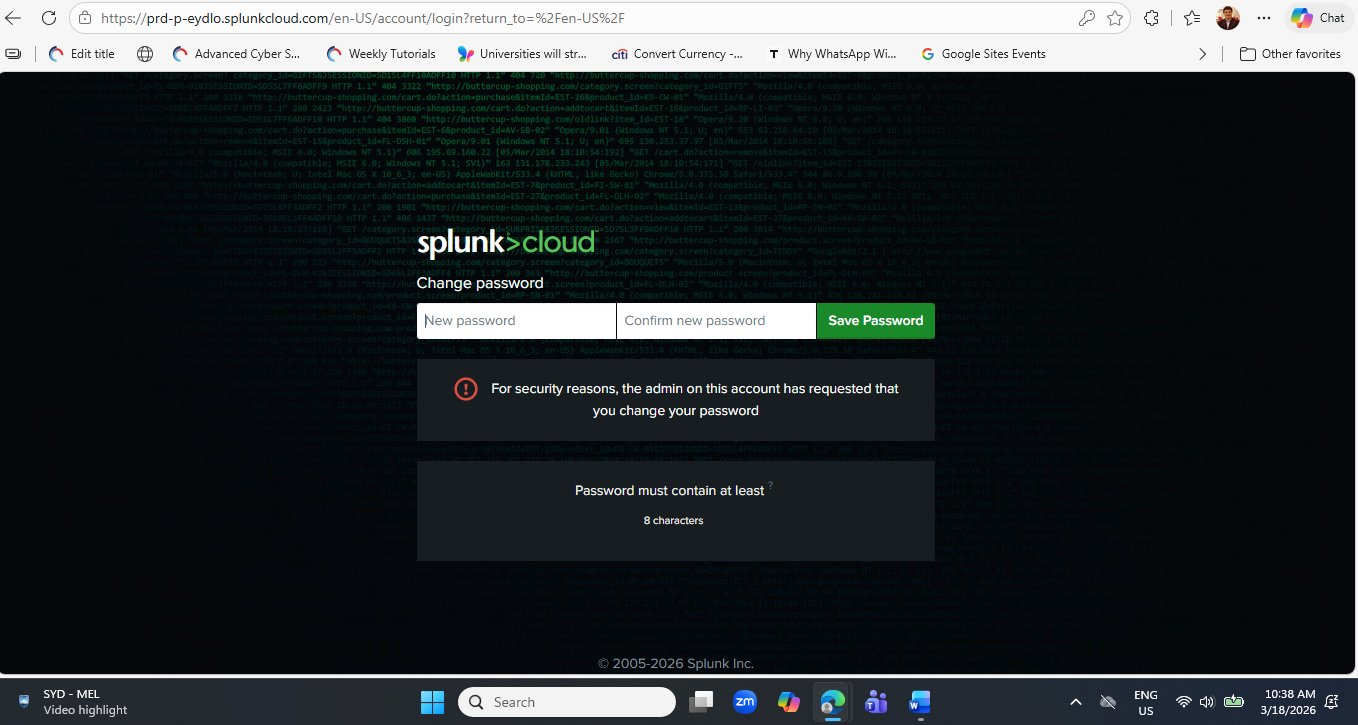
Getting Started with Splunk Cloud Platform 2026 — Step-by-Step Beginner ...