
Append Command In Splunk Lognalytics

Append Command In Splunk | Lognalytics
Append Command In Splunk | Lognalytics

Append Command In Splunk | Lognalytics
Append Command In Splunk | Lognalytics

Append Command In Splunk | Lognalytics
Abstract Command In Splunk | Lognalytics
Datamodel Command In Splunk | Lognalytics

Datamodel Command In Splunk | Lognalytics

Abstract Command In Splunk | Lognalytics

Dedup Command In Splunk | Lognalytics
Advertisement Space (300x250)

Addcoltotals Command Splunk | Lognalytics

Splunk SPL append Command Tutorial - Combine Multiple Search Results ...
Solved: Adding or removing the append command changes a pr... - Splunk ...

Addcoltotals Command Splunk | Lognalytics
Unable to append Custom Content from one instance to another in Splunk ...
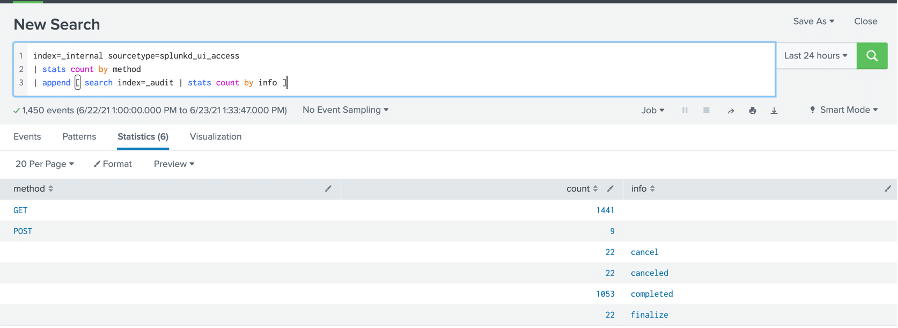
How to Combine Multiple Data Sources in Splunk SPL | TekStream Solutions
Using the append Command - Kinney Group

Solved: Append causing dashboard panels to use colours for... - Splunk ...
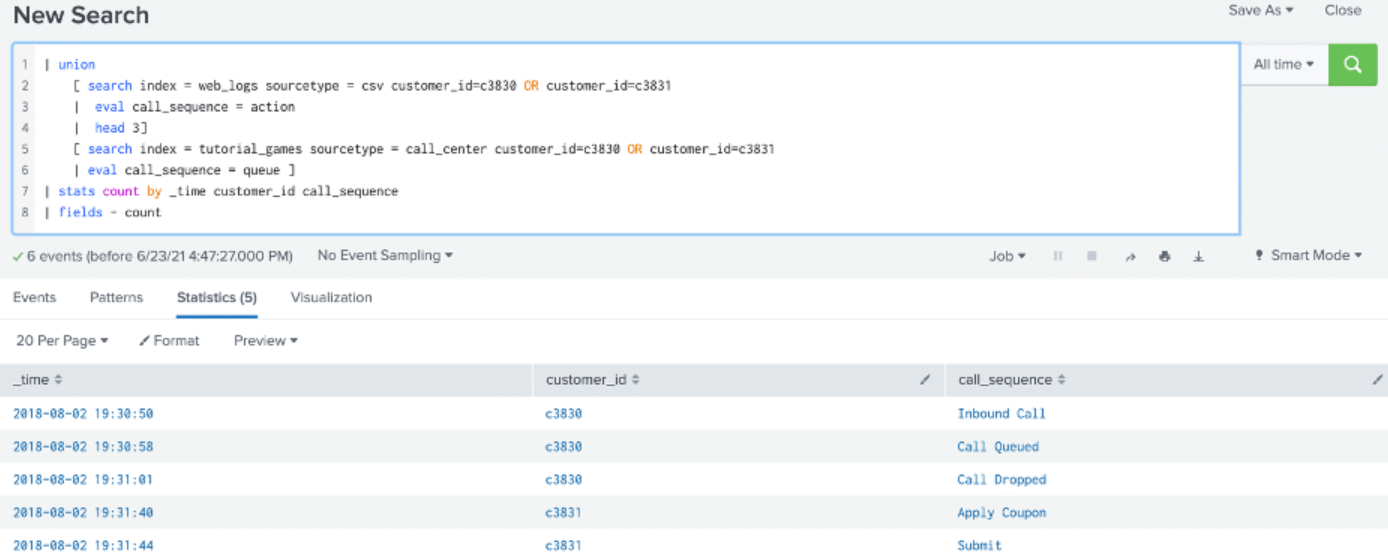
Combining multiple data sources in SPL - Splunk Lantern
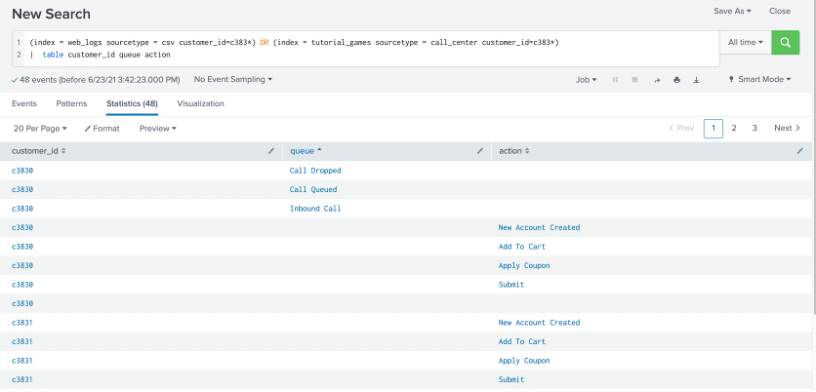
How to Combine Multiple Data Sources in Splunk SPL | TekStream Solutions
Advertisement Space (336x280)
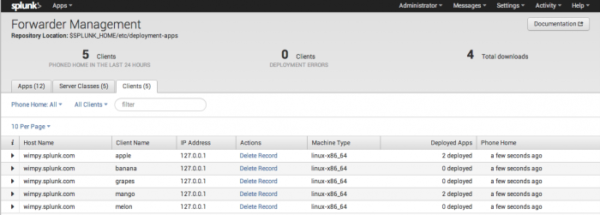
Configure Deployment Client Splunk | Lognalytics

Splunk Commands – Append , Chart and Dedup - Security Investigation
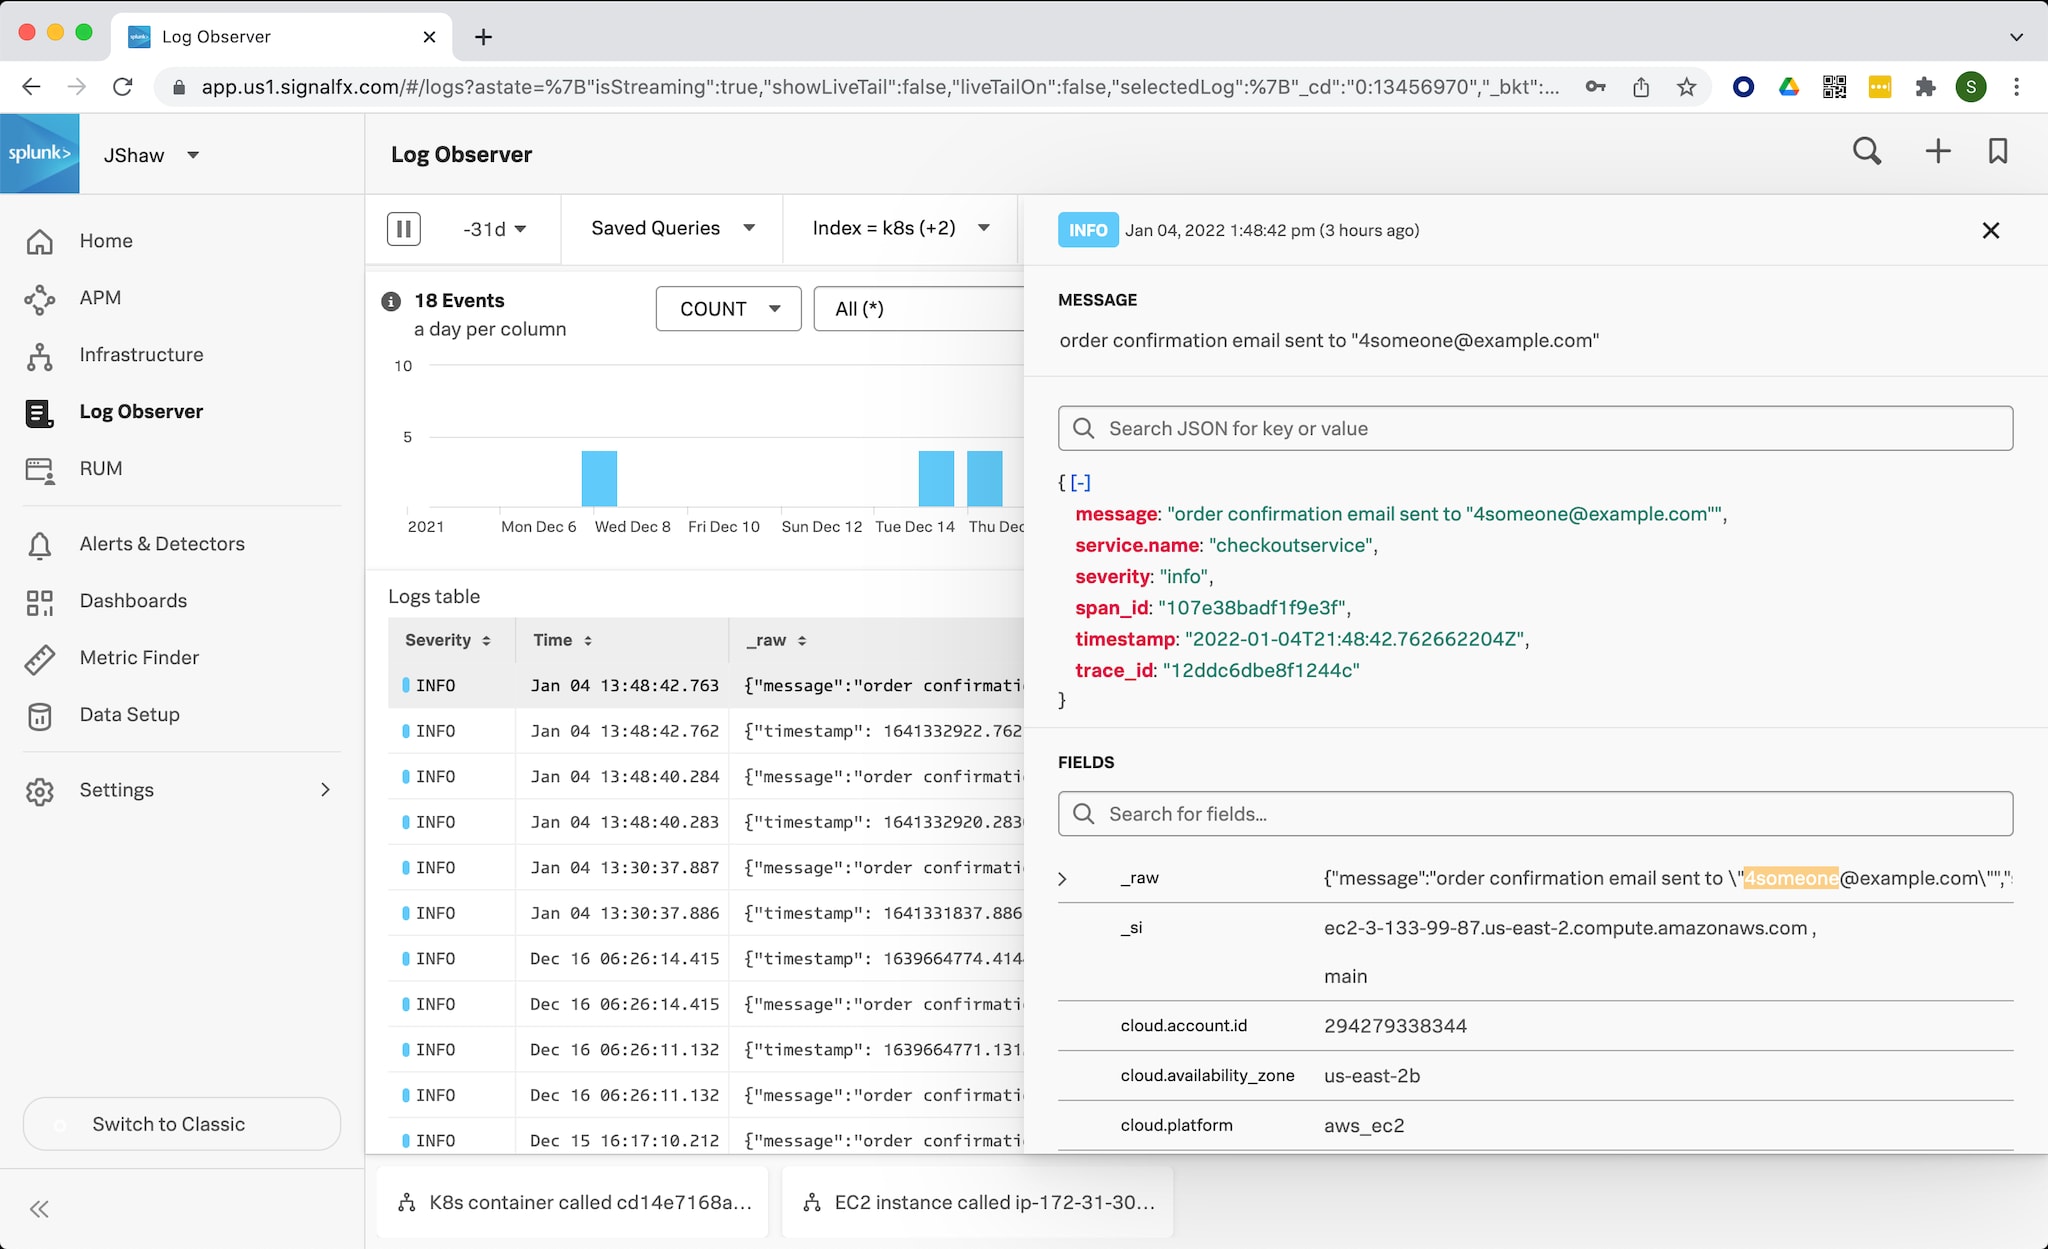
Explore Splunk Cloud Data in Splunk Observability with Log Observer ...
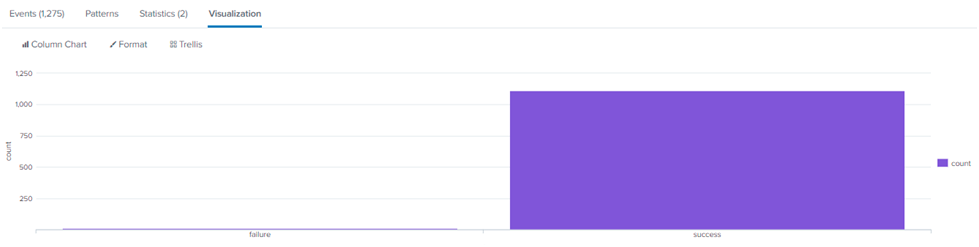
Splunk Commands – Append , Chart and Dedup - Security Investigation
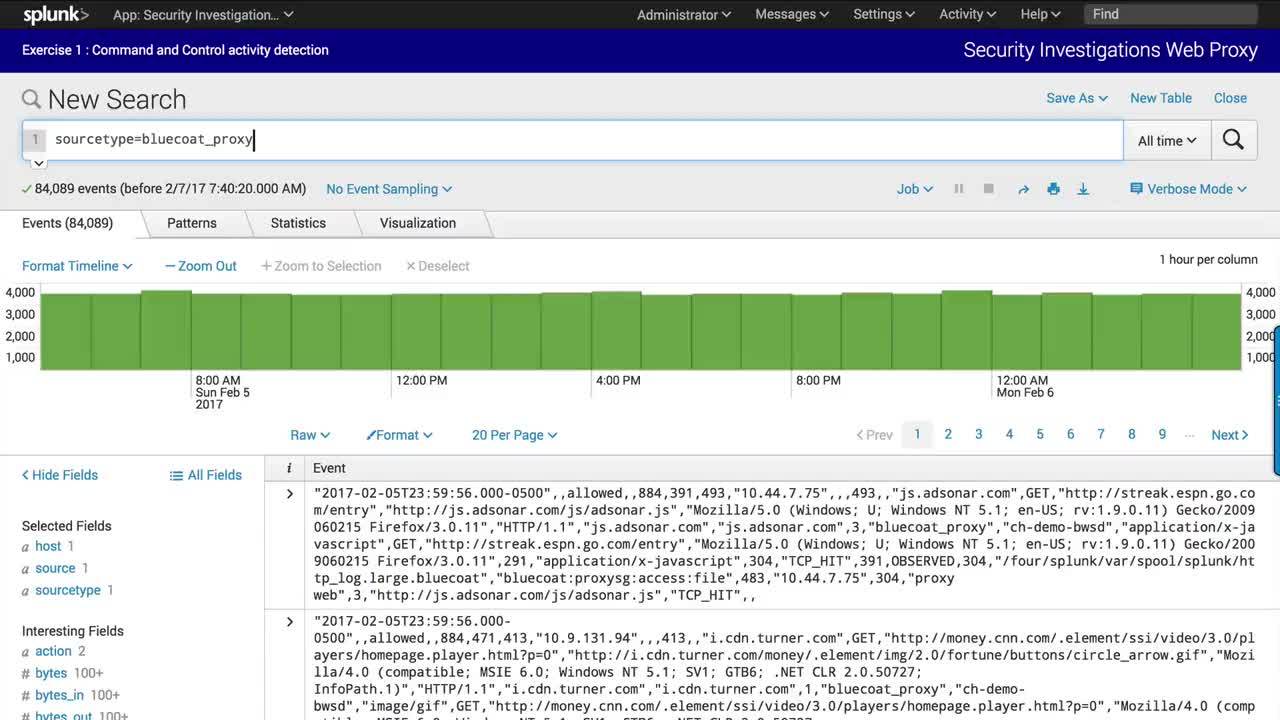
Splunk for Security Investigation: Command and Control Analysis | Splunk
Splunk Commands – Append , Chart and Dedup - Security Investigation

Splunk Commands – Append , Chart and Dedup - Security Investigation

How to add eval command to props.conf? - Splunk Community

How to Analyze Logs in Splunk 2025 | Complete Log Analytics Tutorial ...

How to add eval command to props.conf? - Splunk Community
Advertisement Space (336x280)

Splunk Like Command _ Splunk Quick Reference Guide – EXWJ
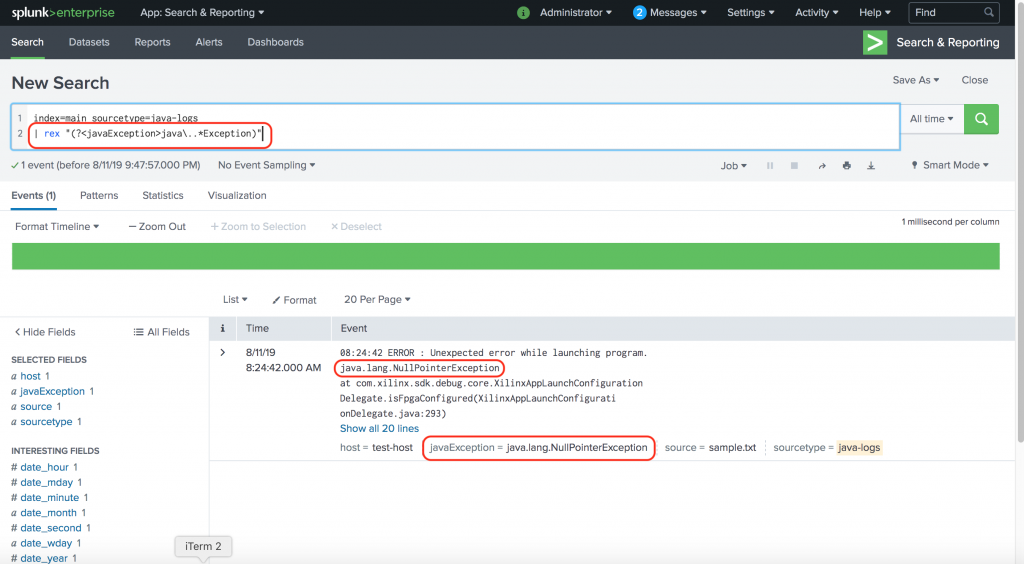
How to use rex command to extract fields in Splunk? - Karunsubramanian.com

Splunk Appendpipe Example at Wendy Rodgers blog

OpenSSH Log Analysis Using Splunk Cloud | by Aishat Olayinka Yusuf | Medium
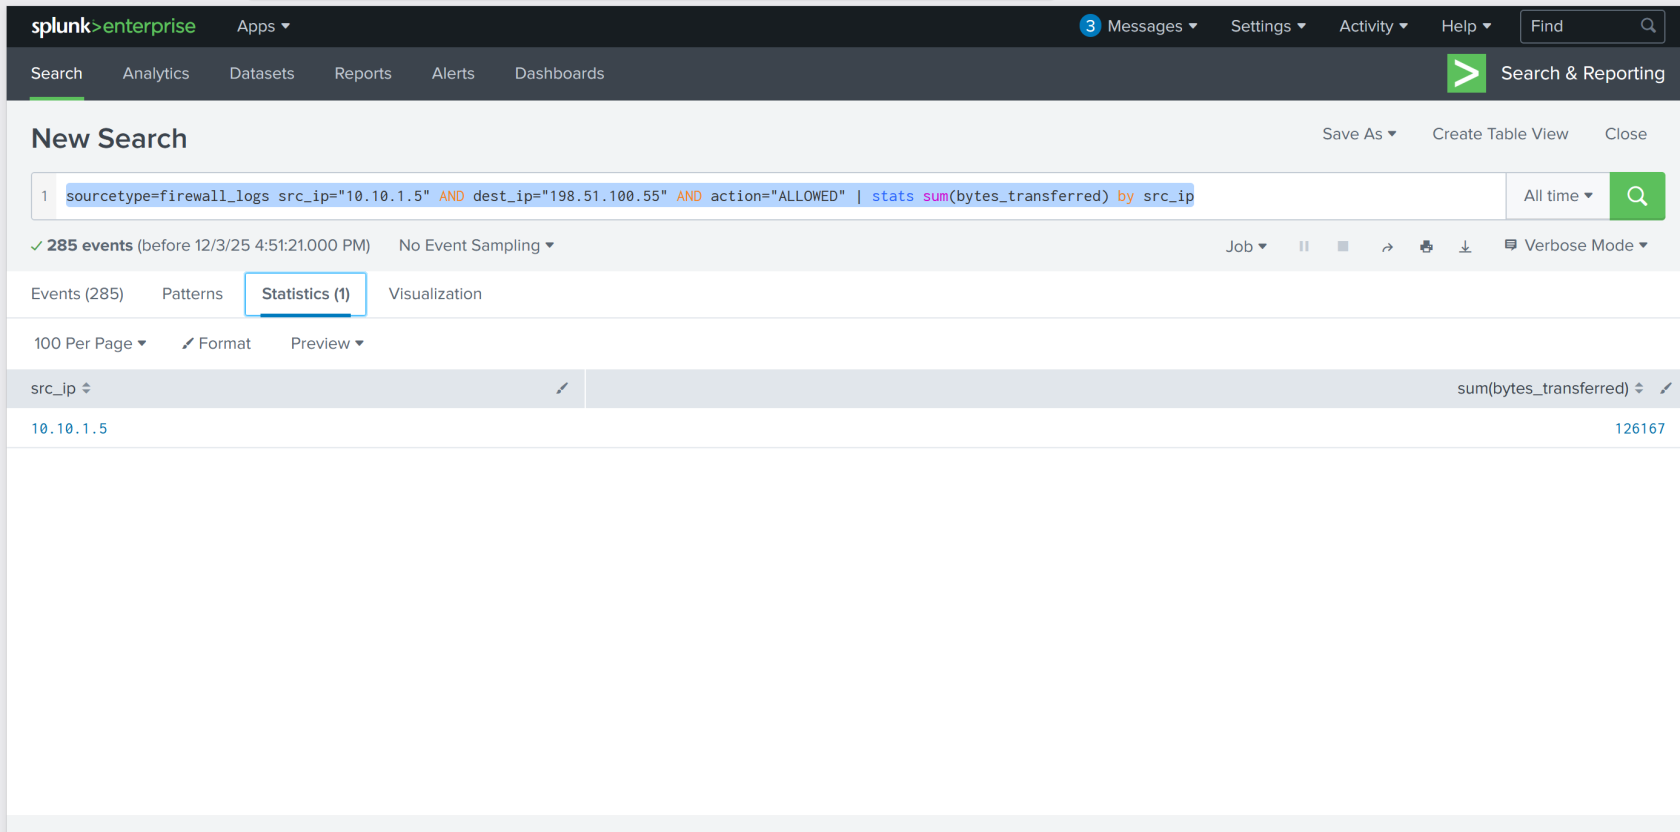
Log Analysis with Splunk | David Rizzo | Portfolio
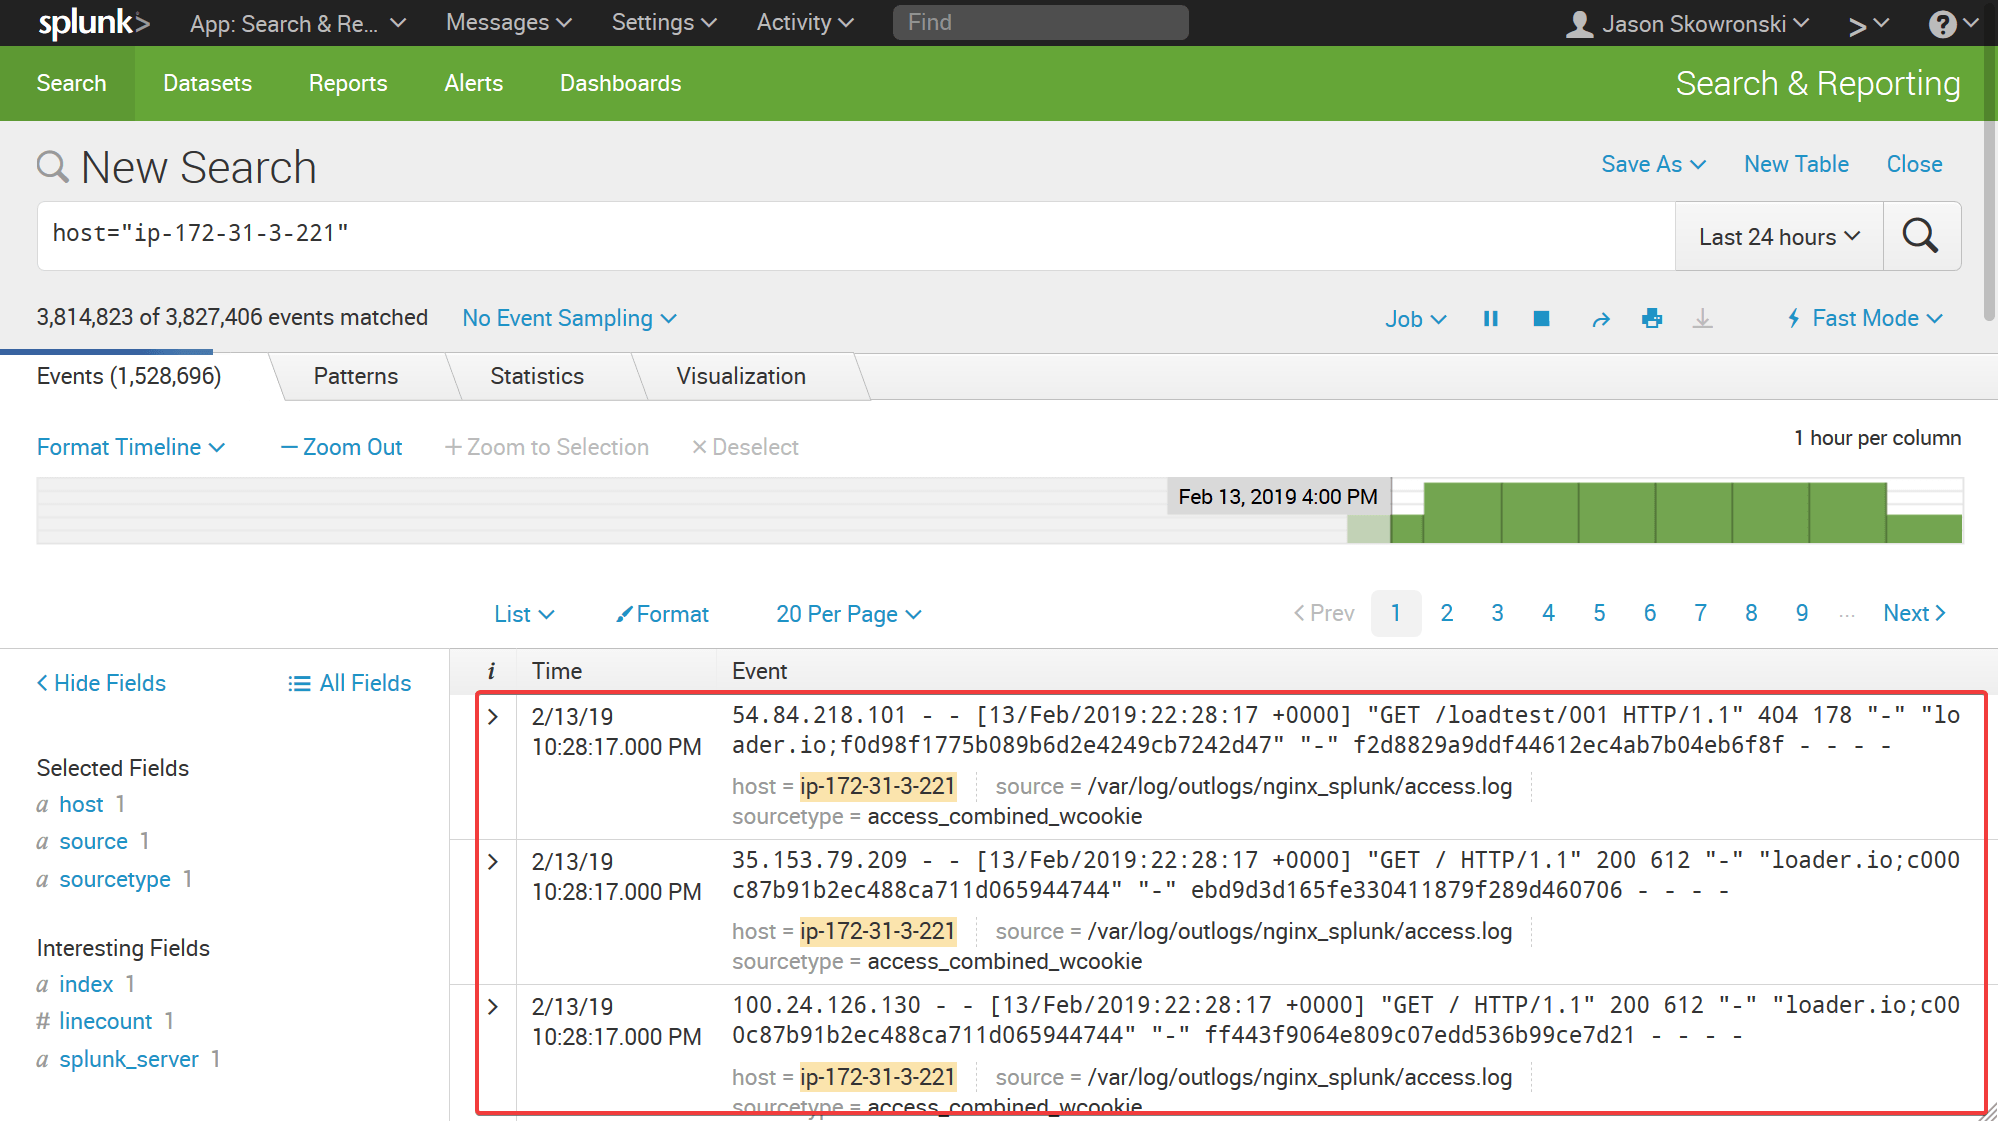
Splunk logs query - lilyneed