
Cookie Csrf Tokencsrf Segmentfault
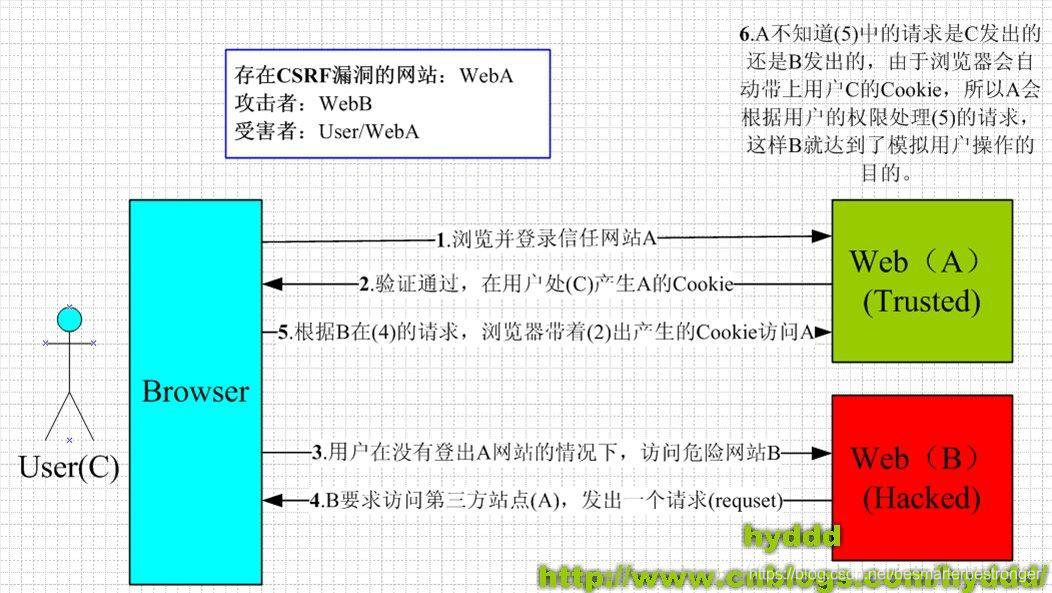
cookie - Csrf Token防止csrf攻击的原理? - SegmentFault 思否
SameSite cookie attributes vs CSRF tokens - which provides better ...

CSRF where token is duplicated in cookie writeup - cyberhub.es

CSRF where token is duplicated in cookie - Lab#06 - YouTube

CSRF - CSRF where token is tied to non-session cookie - YouTube

CSRF where token is duplicated in cookie (Video Solution) | 2020 - YouTube

cookie - Spring Security 认证方式的深度思考 - 张喜硕 - SegmentFault 思否
Missing CSRF token when cookie is set · Issue #385 · vimalloc/flask-jwt ...

The CSRF cookie value did not match the CSRF parameter value exception ...
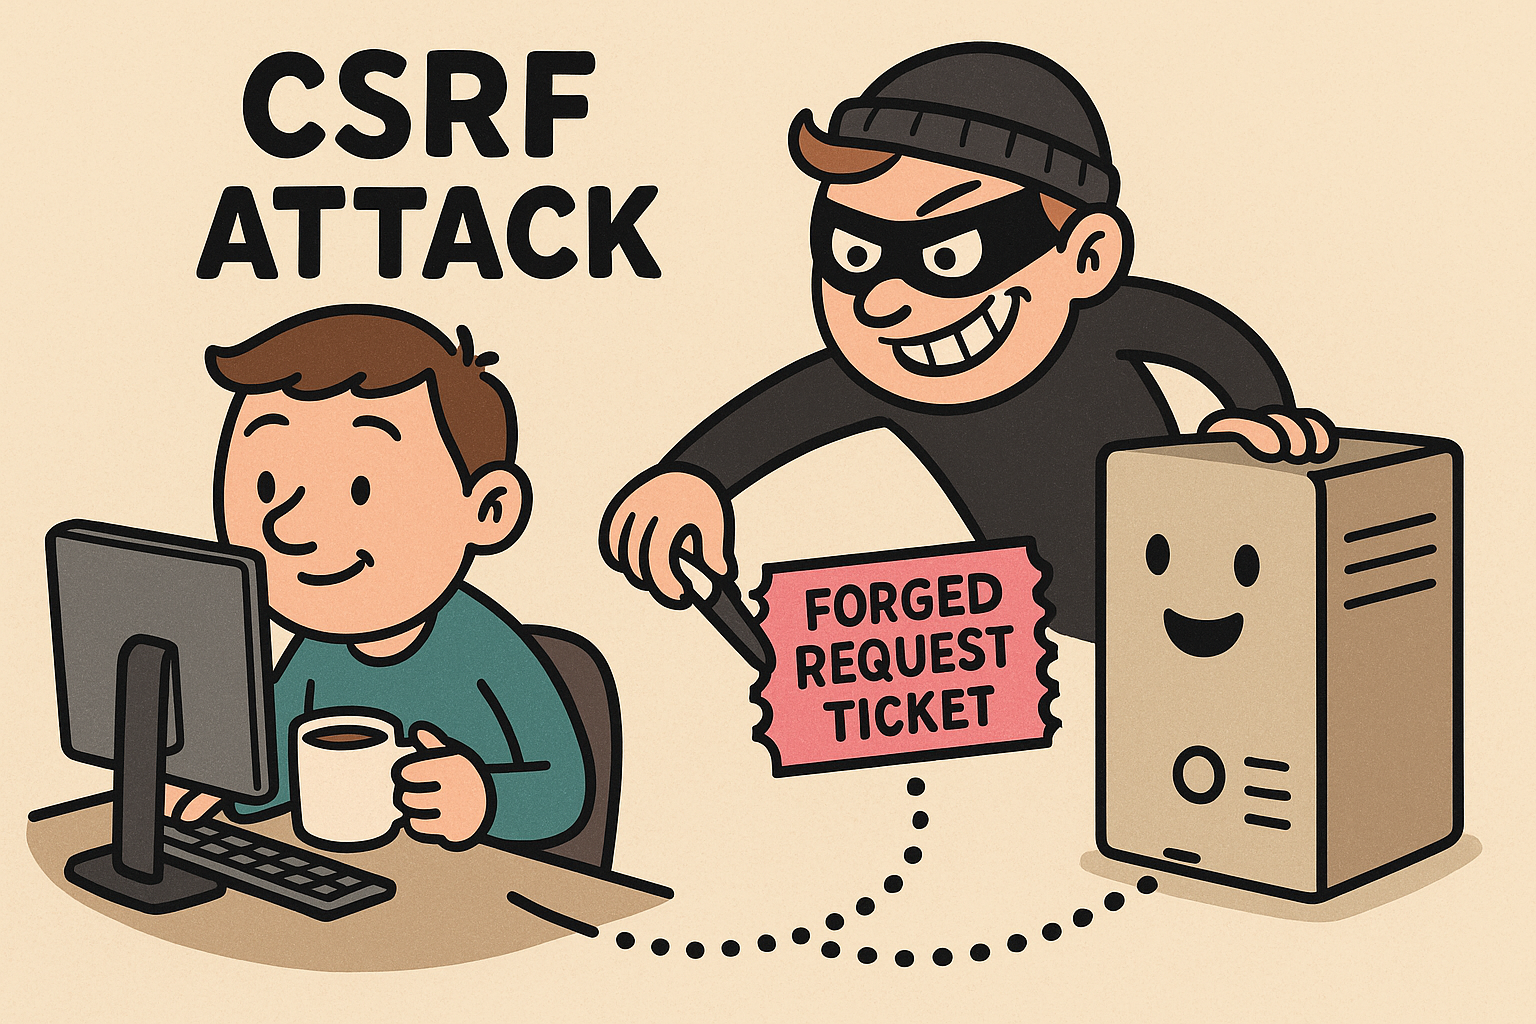
[PortSwigger Academy] CSRF where token is duplicated in cookie 풀이
Advertisement Space (300x250)
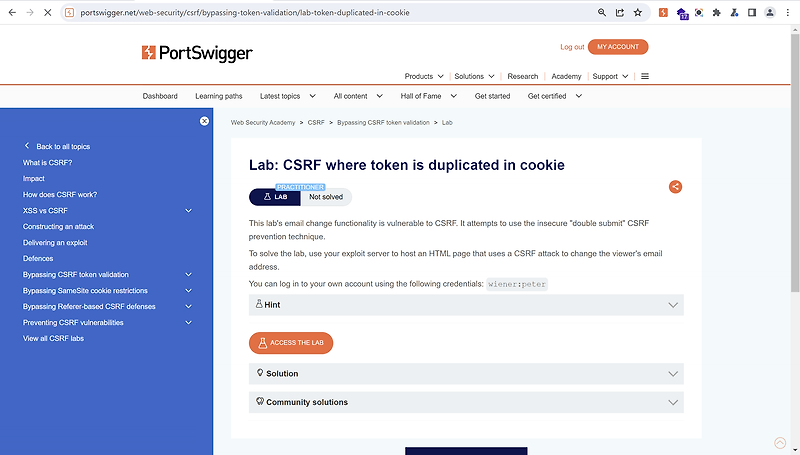
Lab: CSRF where token is duplicated in cookie 문제 풀이(WriteUp)

CSRF mitigation with JWT and cookie · Issue #2205 · hasura/graphql ...

CSRF Cookie is not set with react frontend - Templates & Frontend ...

CSRF Token Management in Spring Boot | PDF | Http Cookie | Web Development
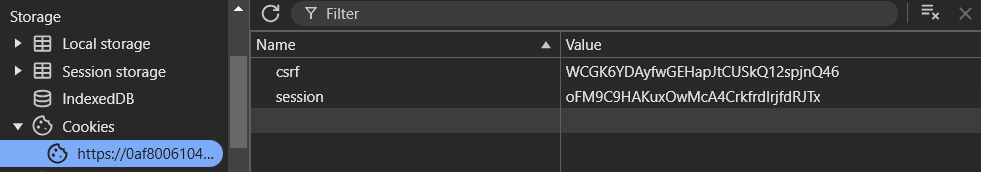
CSRF where token is duplicated in cookie writeup - cyberhub.es

python - Django 的 CSRF 是什么原理? - SegmentFault 思否
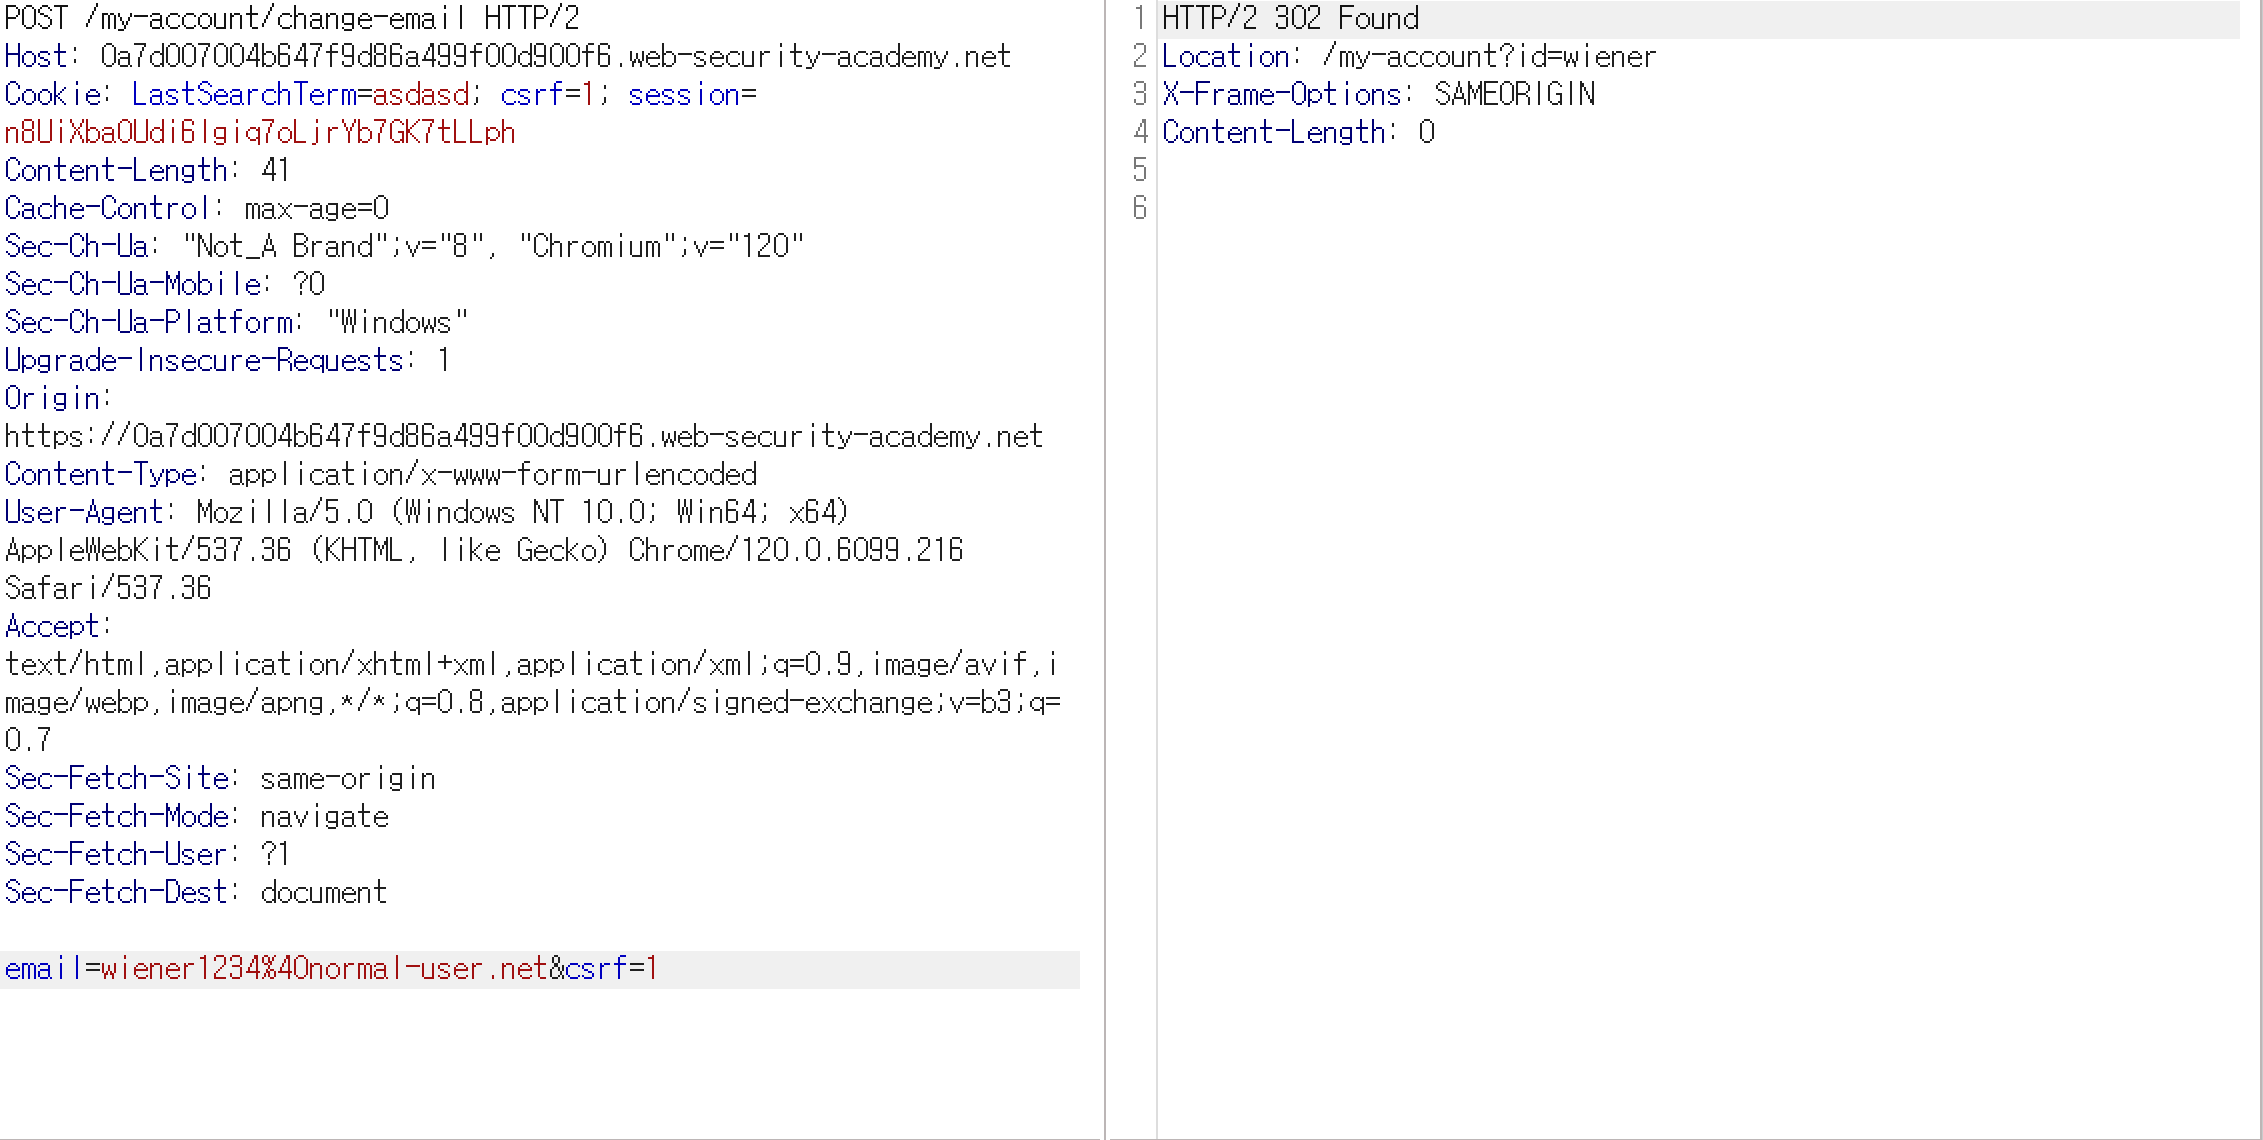
Lab: CSRF where token is duplicated in cookie 문제 풀이(WriteUp)
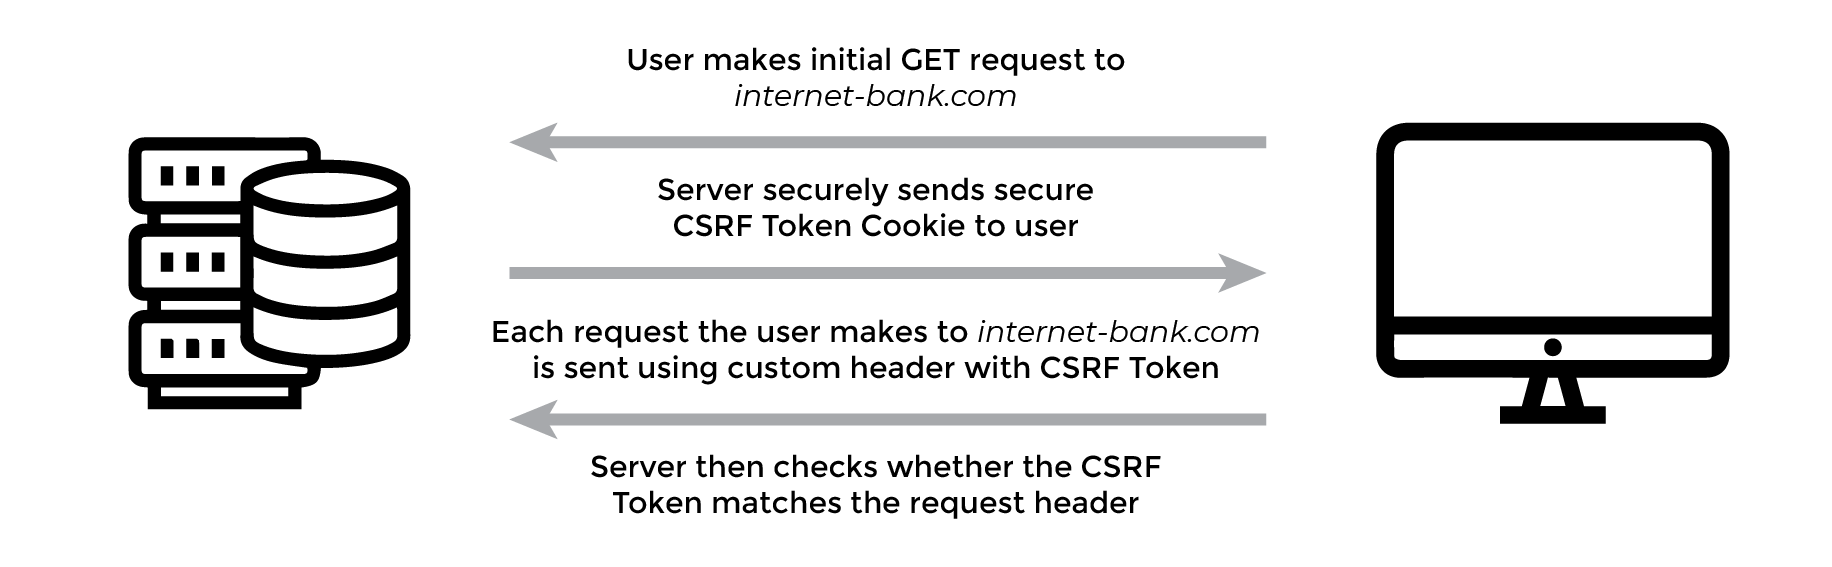
CSRF protection in an Angular application 🔐 - How to implement?
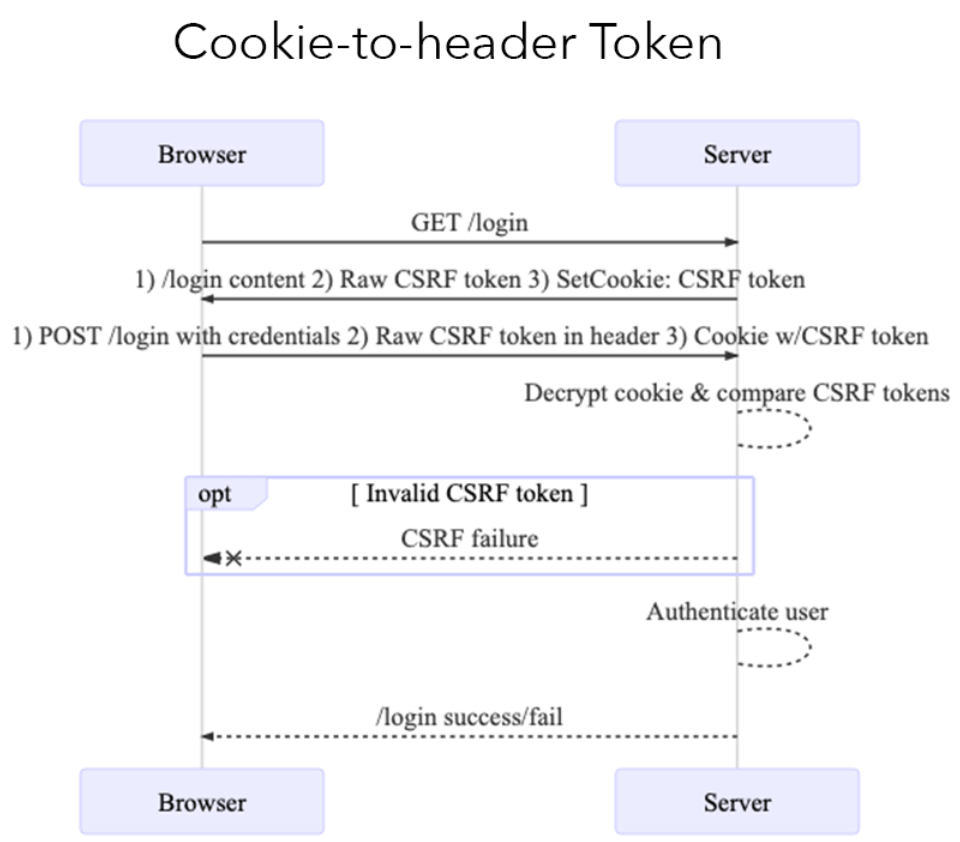
2.4 CSRF Protection in Angular | Angular Security Training
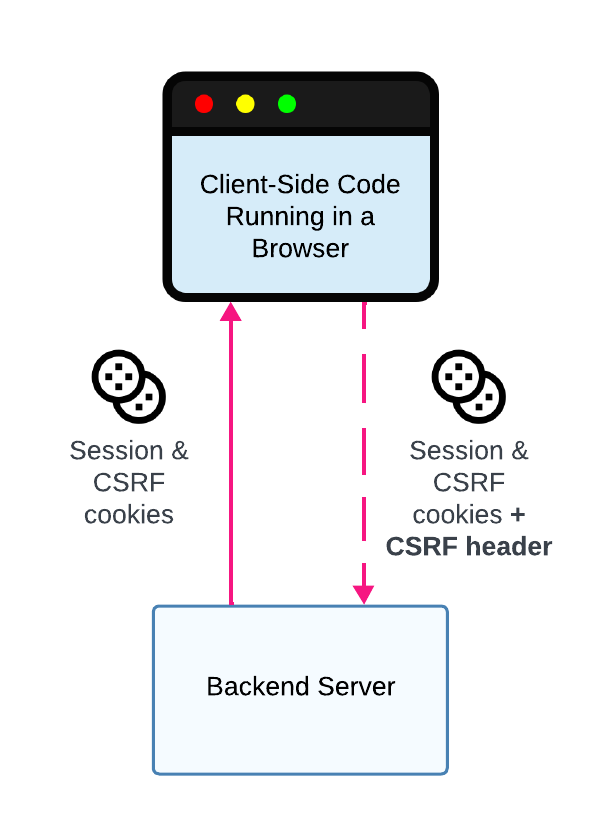
CSRF Protection
Advertisement Space (336x280)
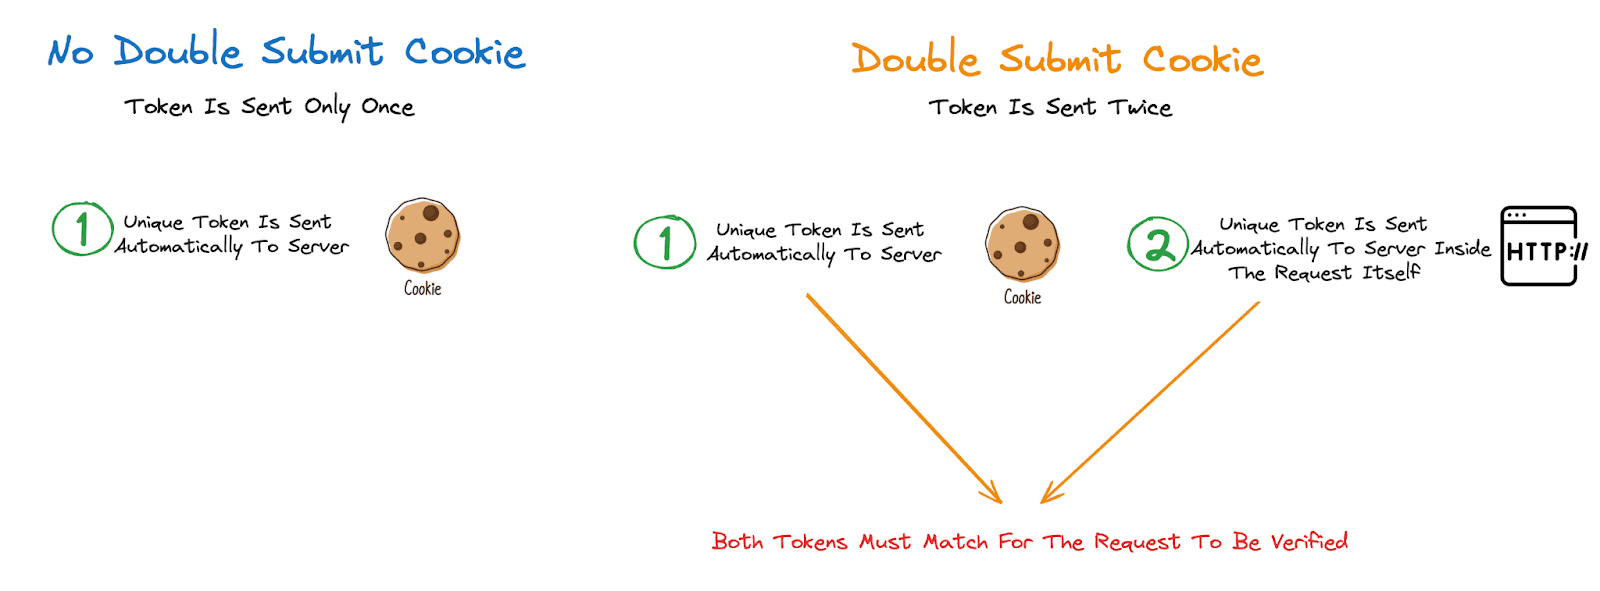
What is CSRF (Cross Site Request Forgery)

CSRF Protection - Backend Server
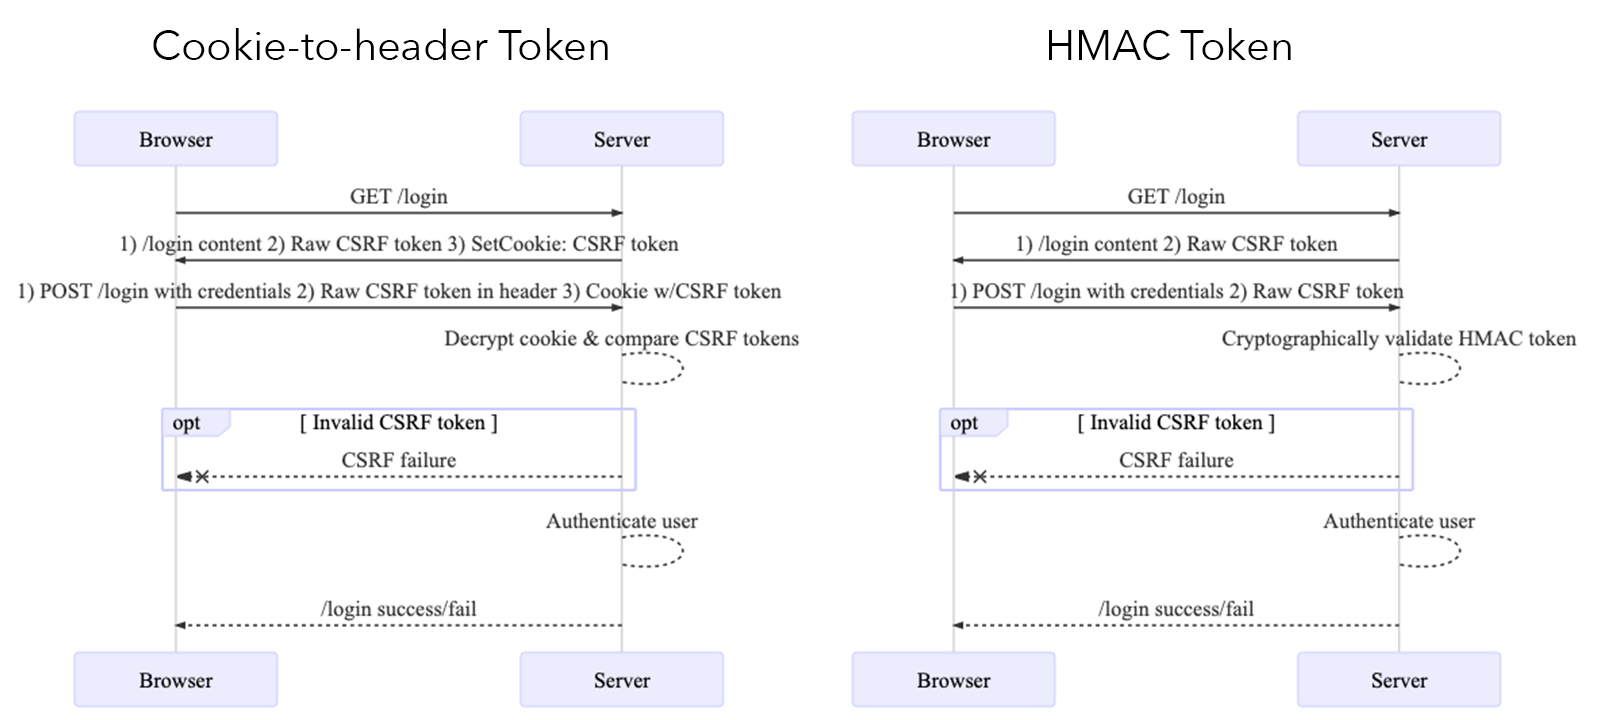
Better CSRF Protection
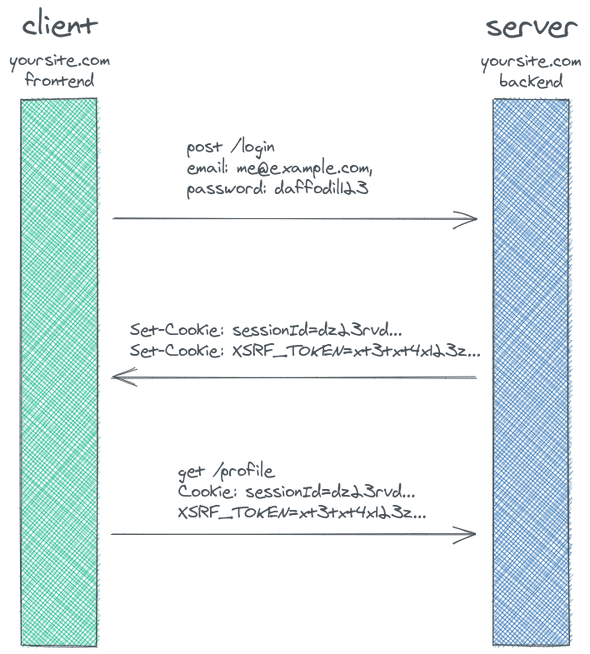
Using Cookie-Based CSRF Tokens for Your Single Page Application | TypeOfNaN
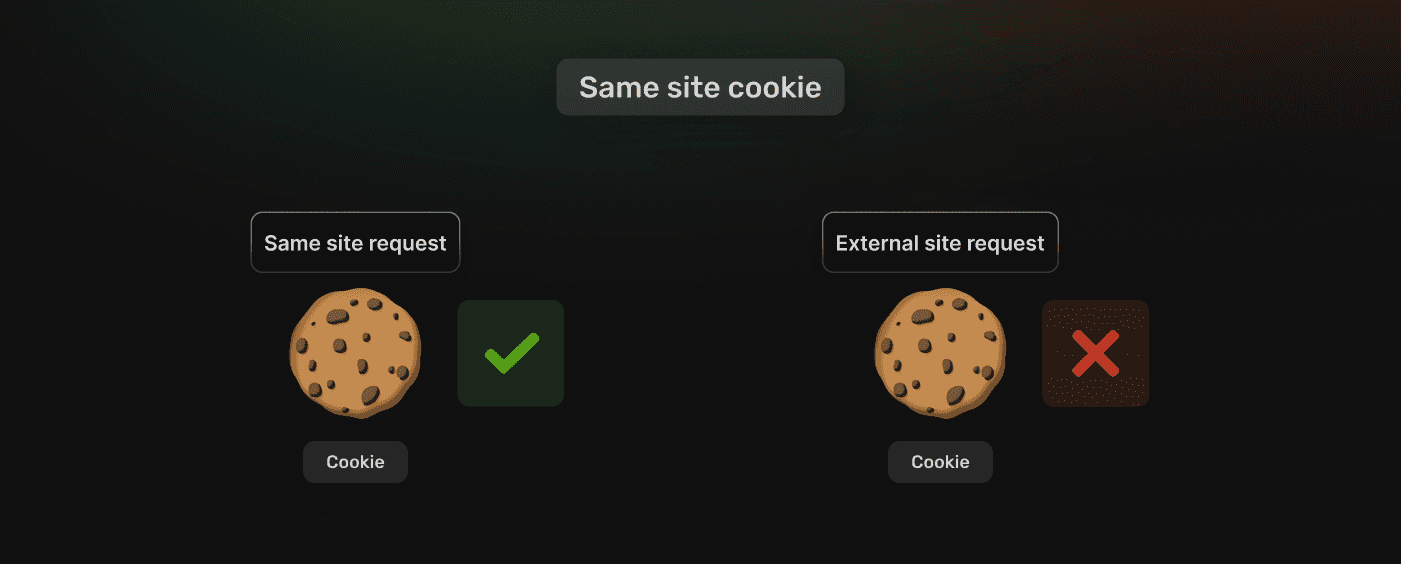
What is CSRF (Cross Site Request Forgery)

How to send Django CSRF token in response header (insted of cookies ...

CSRF where token is tied to non-session cookie| PortSwigger | CSRF Labs ...
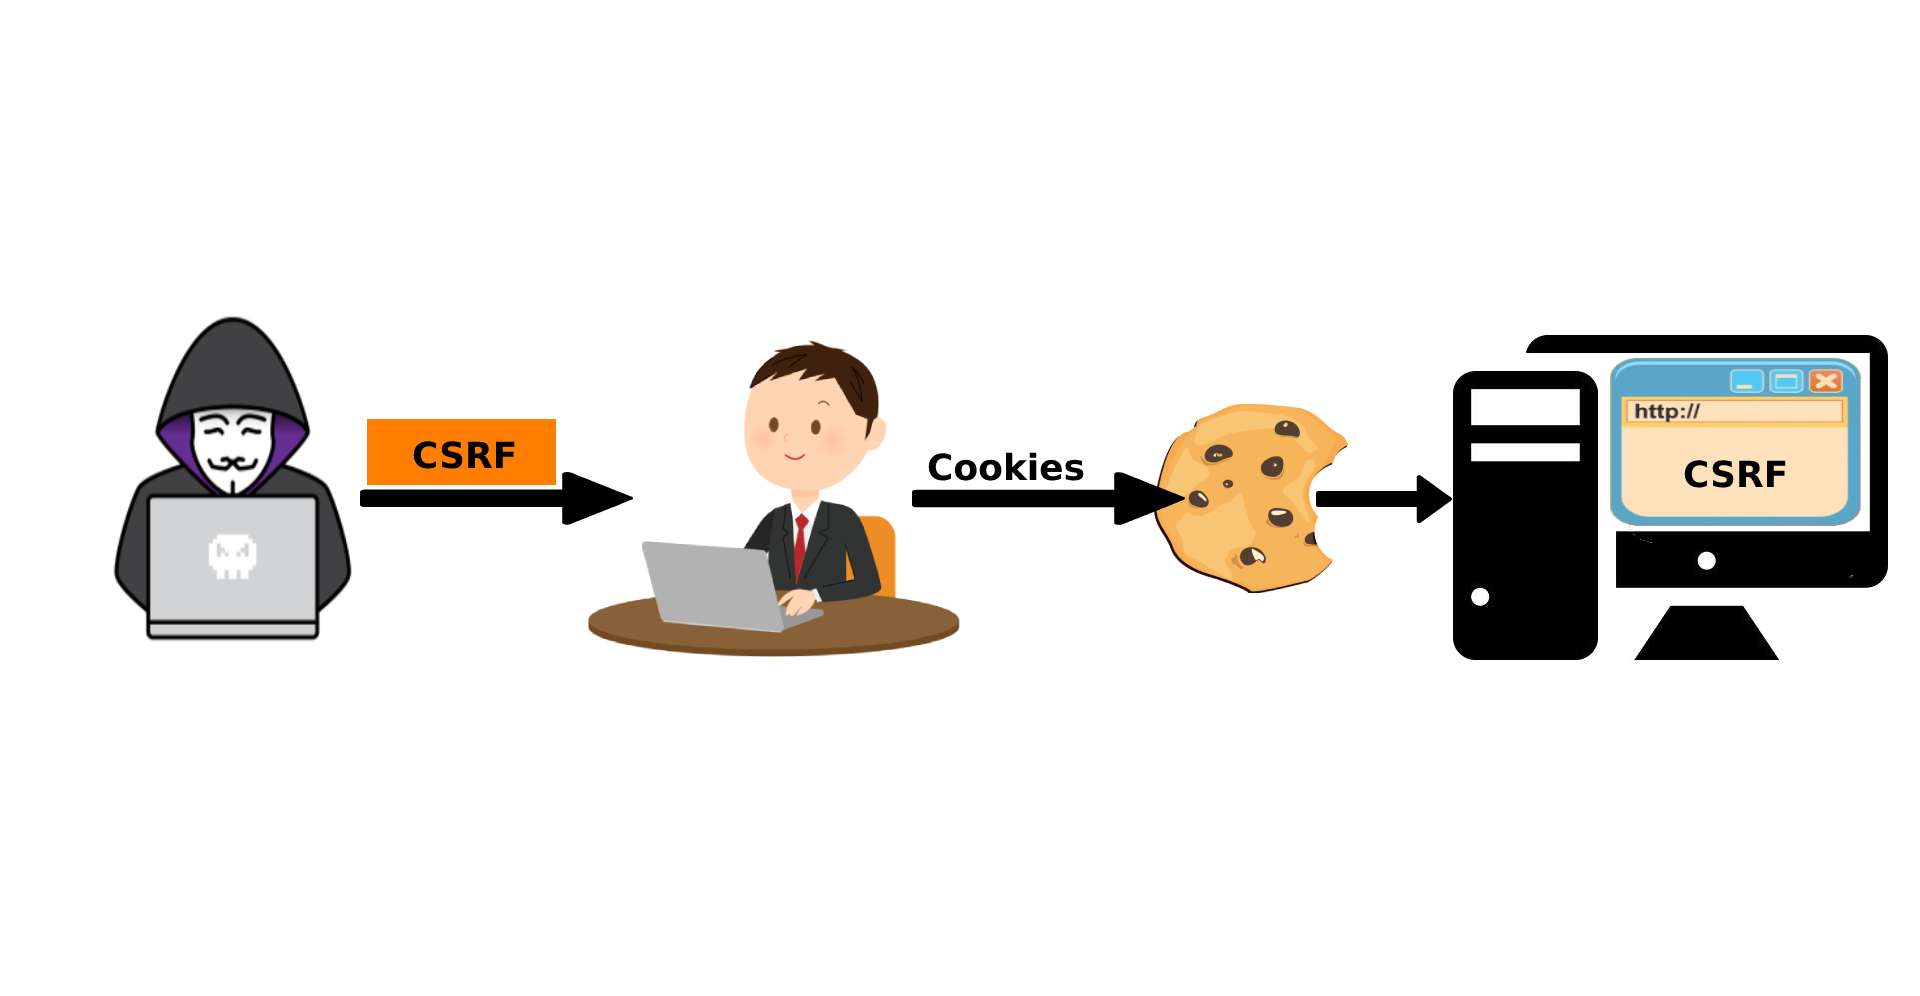
CSRF Token 왜 필요하죠...?

前端 - Cookie&Token&Session再提一嘴 - Kieran Blog - SegmentFault 思否

CSRF Token
Advertisement Space (336x280)
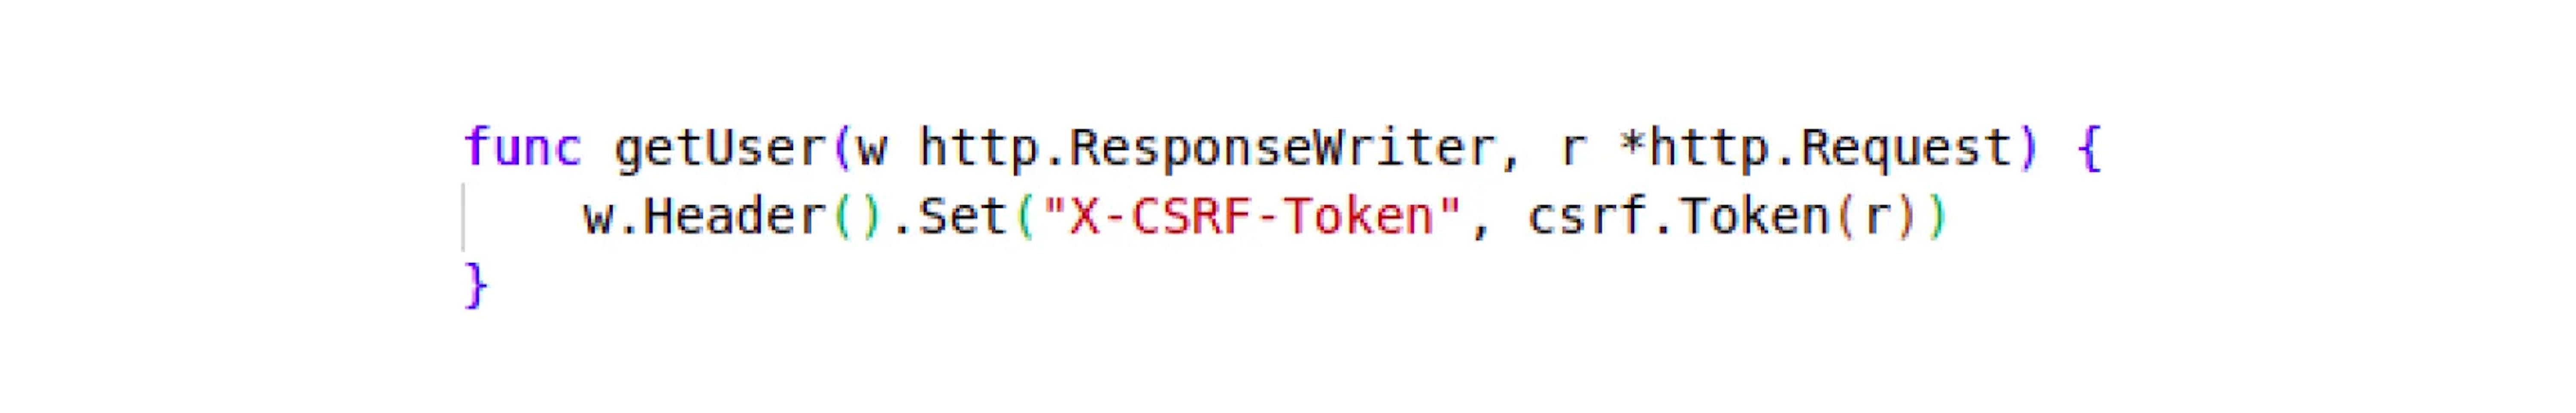
Overview of SOP, CORS, and CSRF

How to validate CSRF tokens? - Stack Overflow
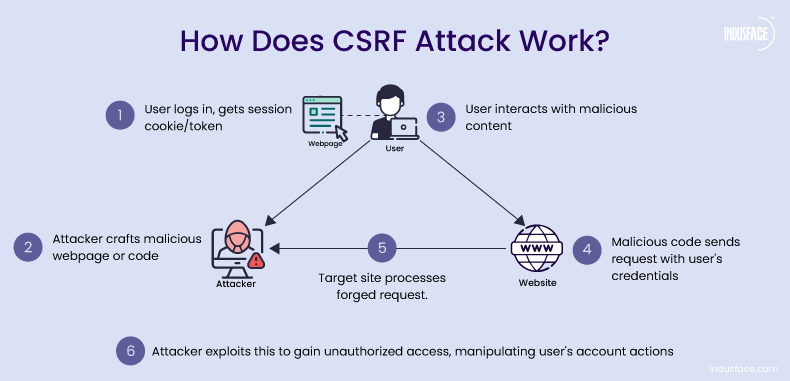
How Does Csrf Work : How to use Django’s CSRF protection – SWVML
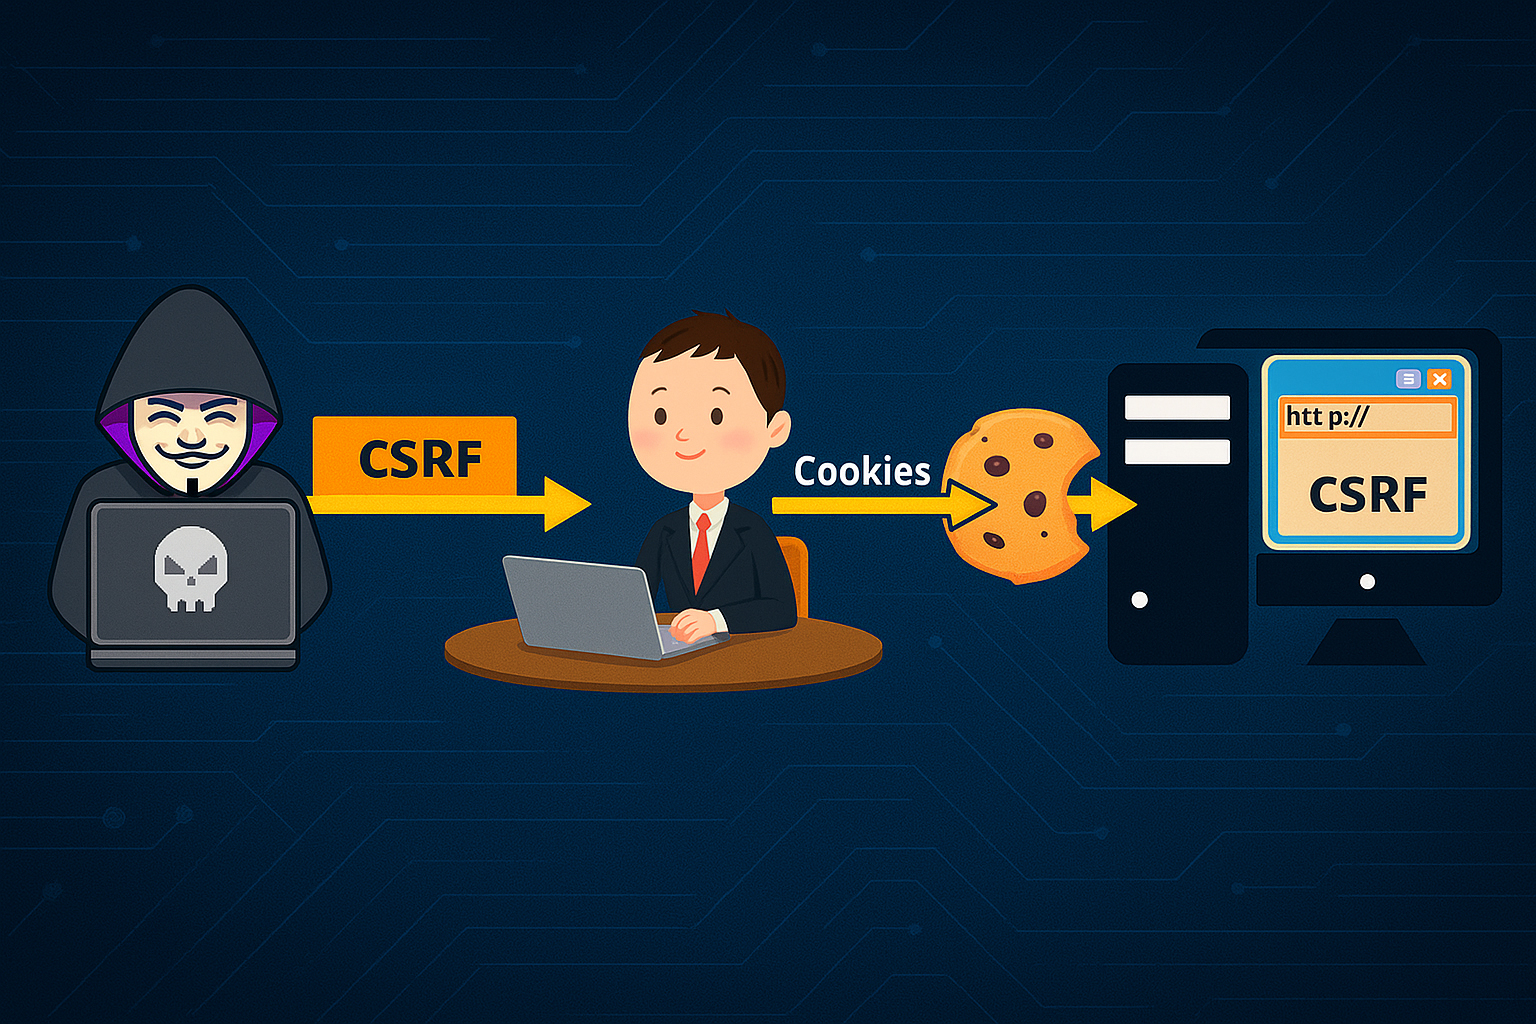
CSRF Token Là Gì? Cách Hoạt Động Và Hướng Dẫn Ngăn Chặn Tấn Công CSRF ...
CSRF: Double-Submit Cookie vs Synchronizer Token
Protección de Aplicaciones Web: Token CSRF y Prevención de Ataques