
Deleted Process Binary Attack On Linux Sandfly Security

Deleted Process Binary Attack on Linux | Sandfly Security
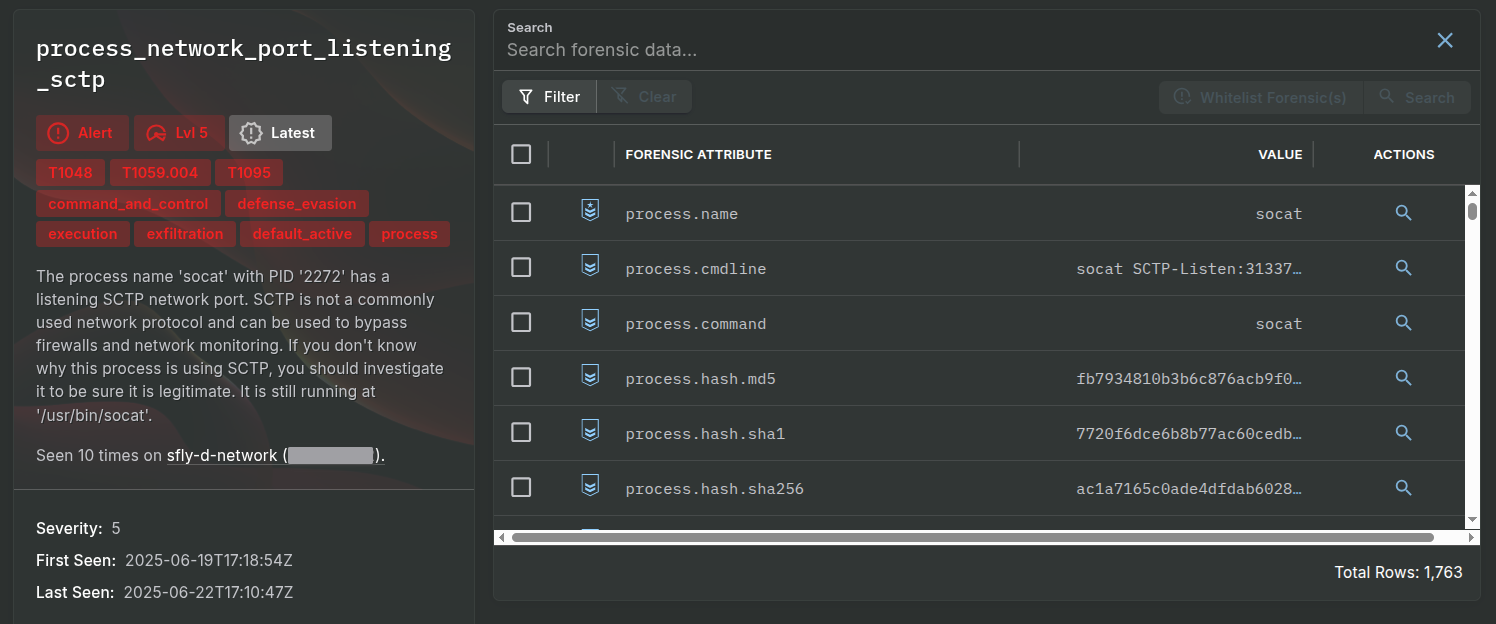
SCTP Protocol Attack Risks on Linux | Sandfly Security

Linux Process Running with Hidden Binary Name Attack

Detecting Linux Binary File Poisoning | Sandfly Security

Detecting Linux Binary File Poisoning | Sandfly Security

Detecting Linux Binary File Poisoning | Sandfly Security

Sandfly Agentless Security for Linux | Splunkbase

How To Recover A Deleted Binary From Active Linux Malware

How To Recover A Deleted Binary From Active Linux Malware

How To Recover A Deleted Binary From Active Linux Malware
Advertisement Space (300x250)

How To Recover A Deleted Binary From Active Linux Malware

How To Recover A Deleted Binary From Active Linux Malware

Sandfly 2.8.0 – Agentless Active Attack Response for Linux
3. Linux Process Tracing | Learning Linux Binary Analysis

Doing DFIR in Linux? Remember, if the malware process binary is deleted ...
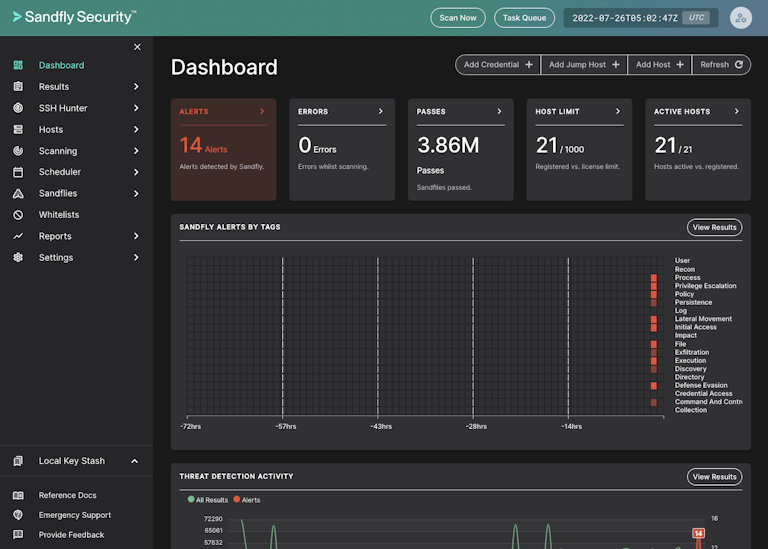
Sandfly Security | Agentless Linux Security
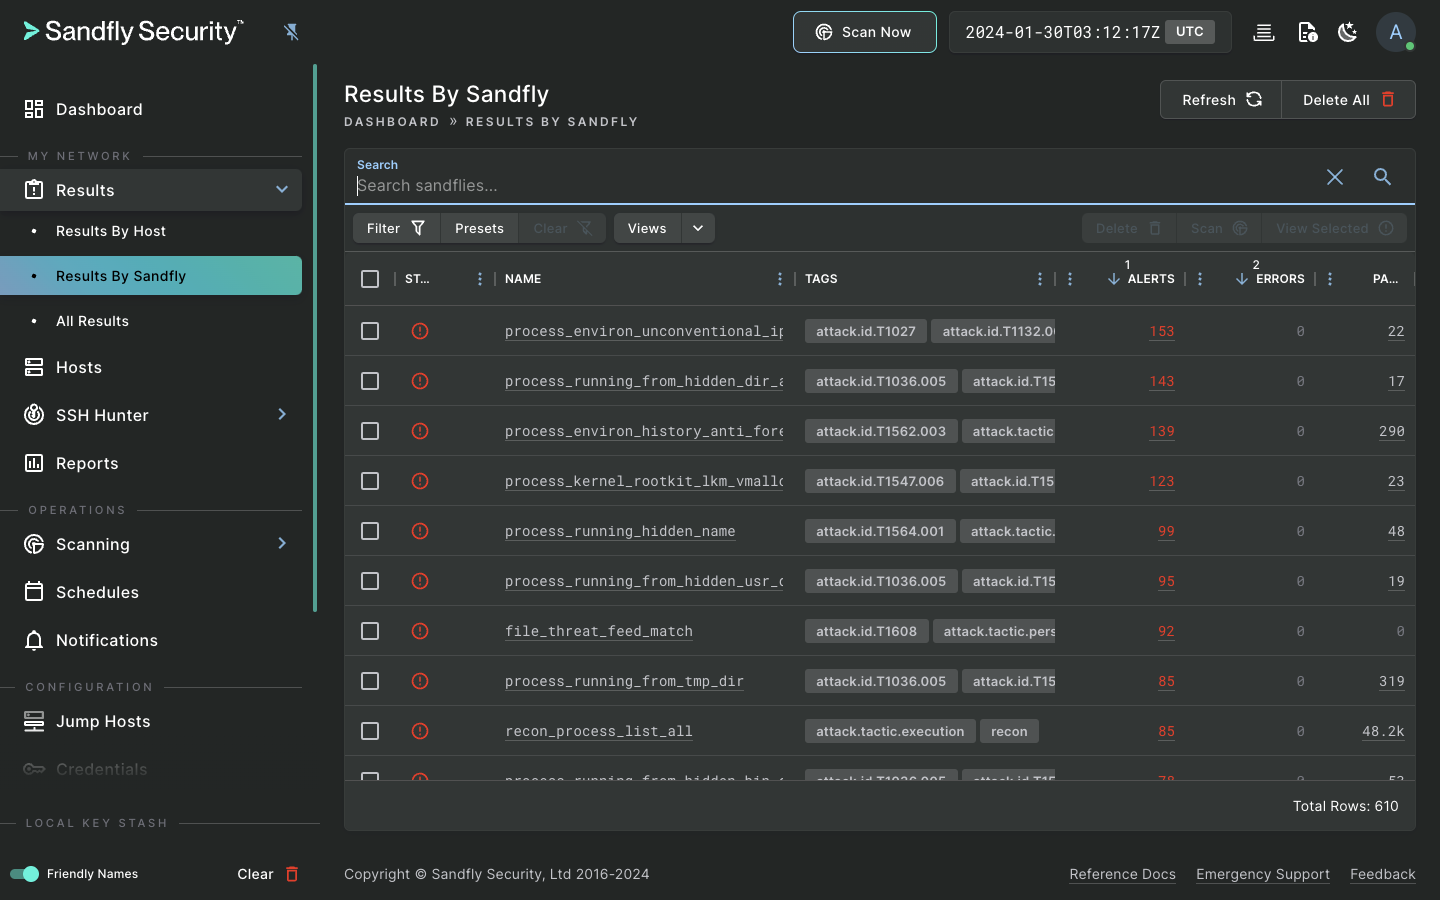
Sandfly Security | Agentless Linux EDR and Incident Response

Sandfly 2.8.0 – Agentless Active Attack Response for Linux
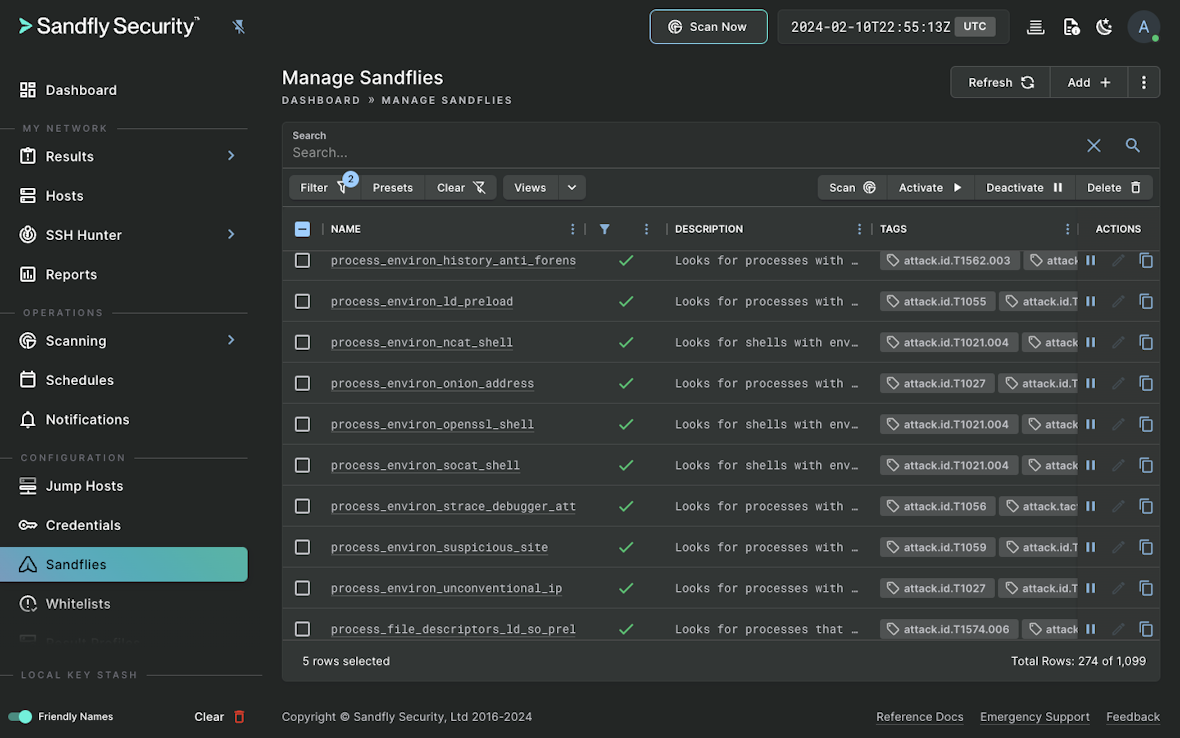
EDR Threat Detection for Linux | Sandfly Security
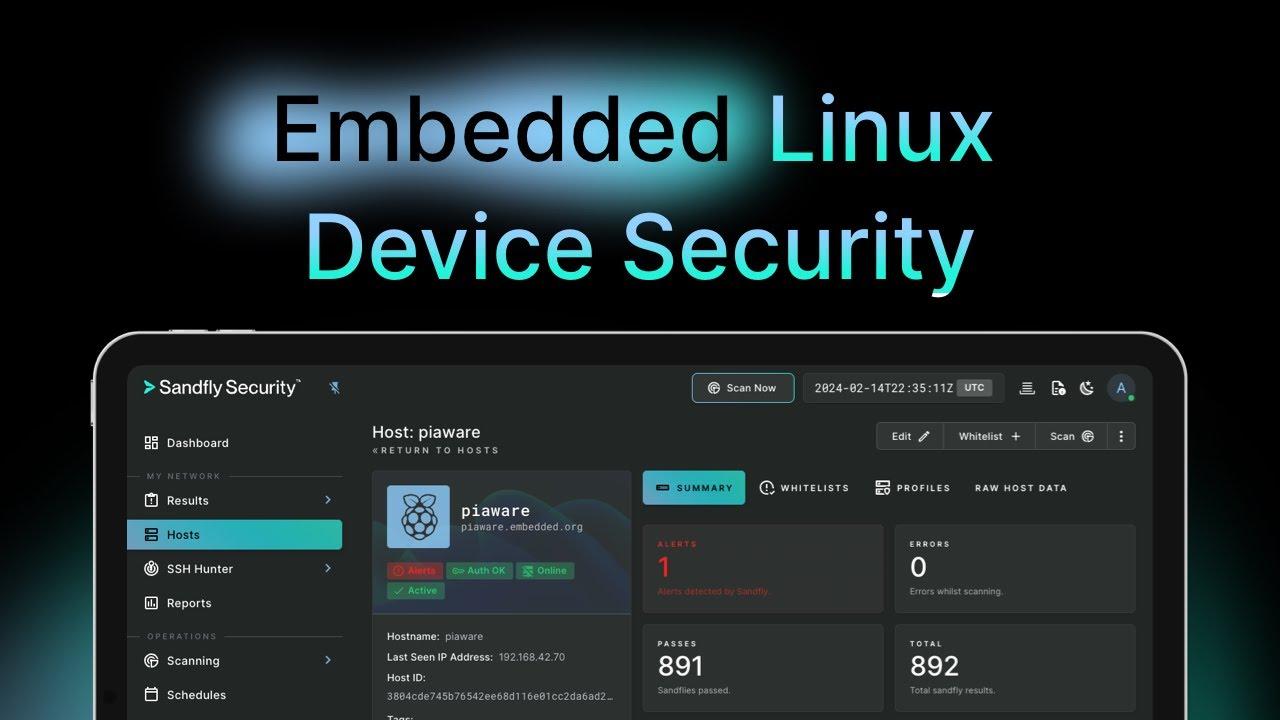
Linux Device and Appliance Security | Sandfly Security
Advertisement Space (336x280)
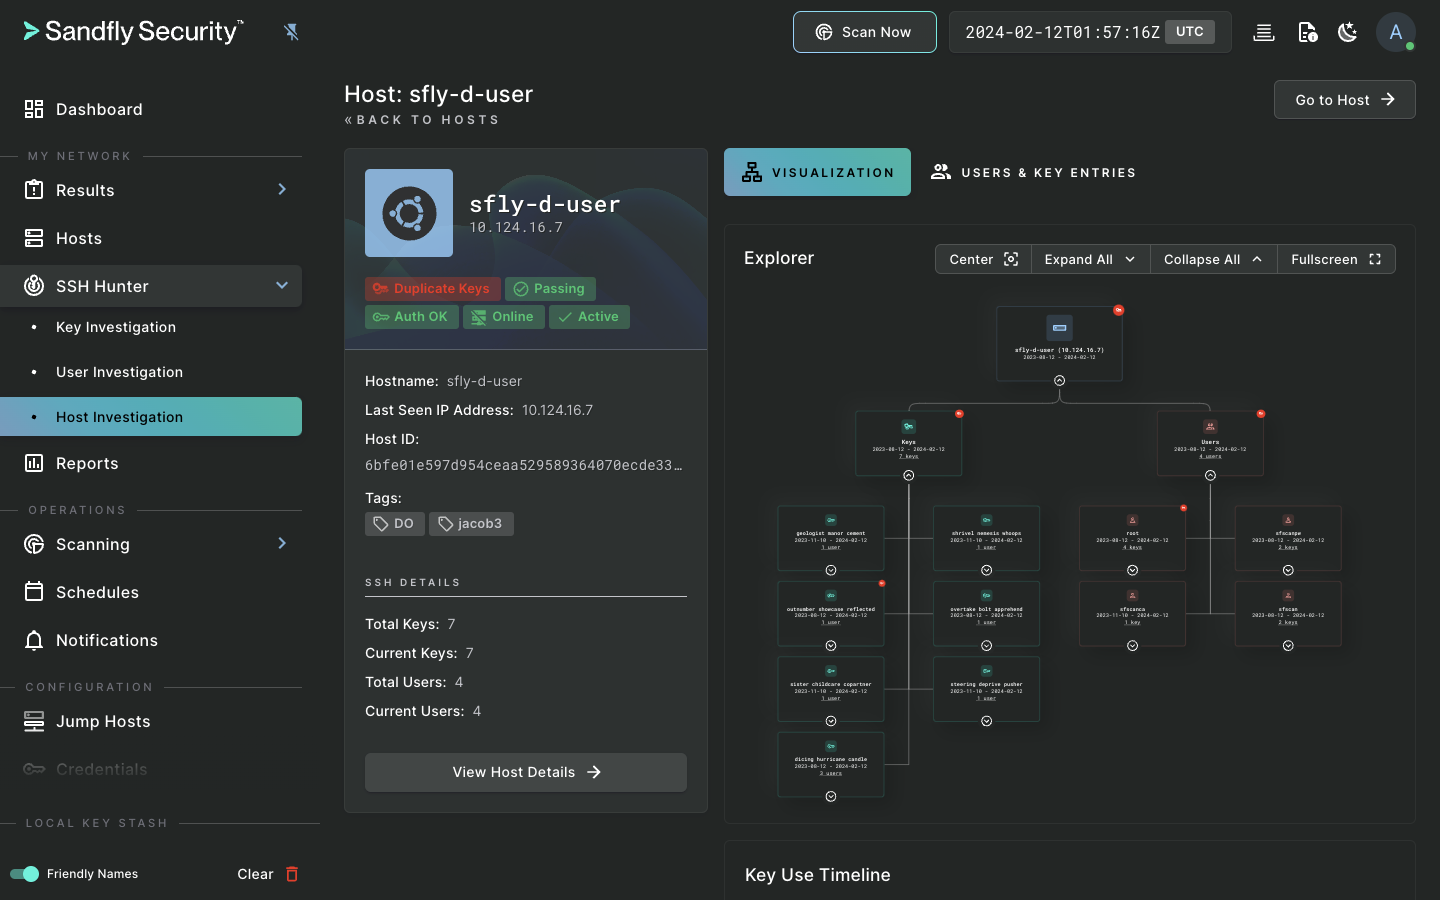
Sandfly Security | Agentless Linux EDR and Incident Response

Sandfly Security | Agentless Linux EDR and Incident Response
Getting Linux Visibility with Sandfly Security
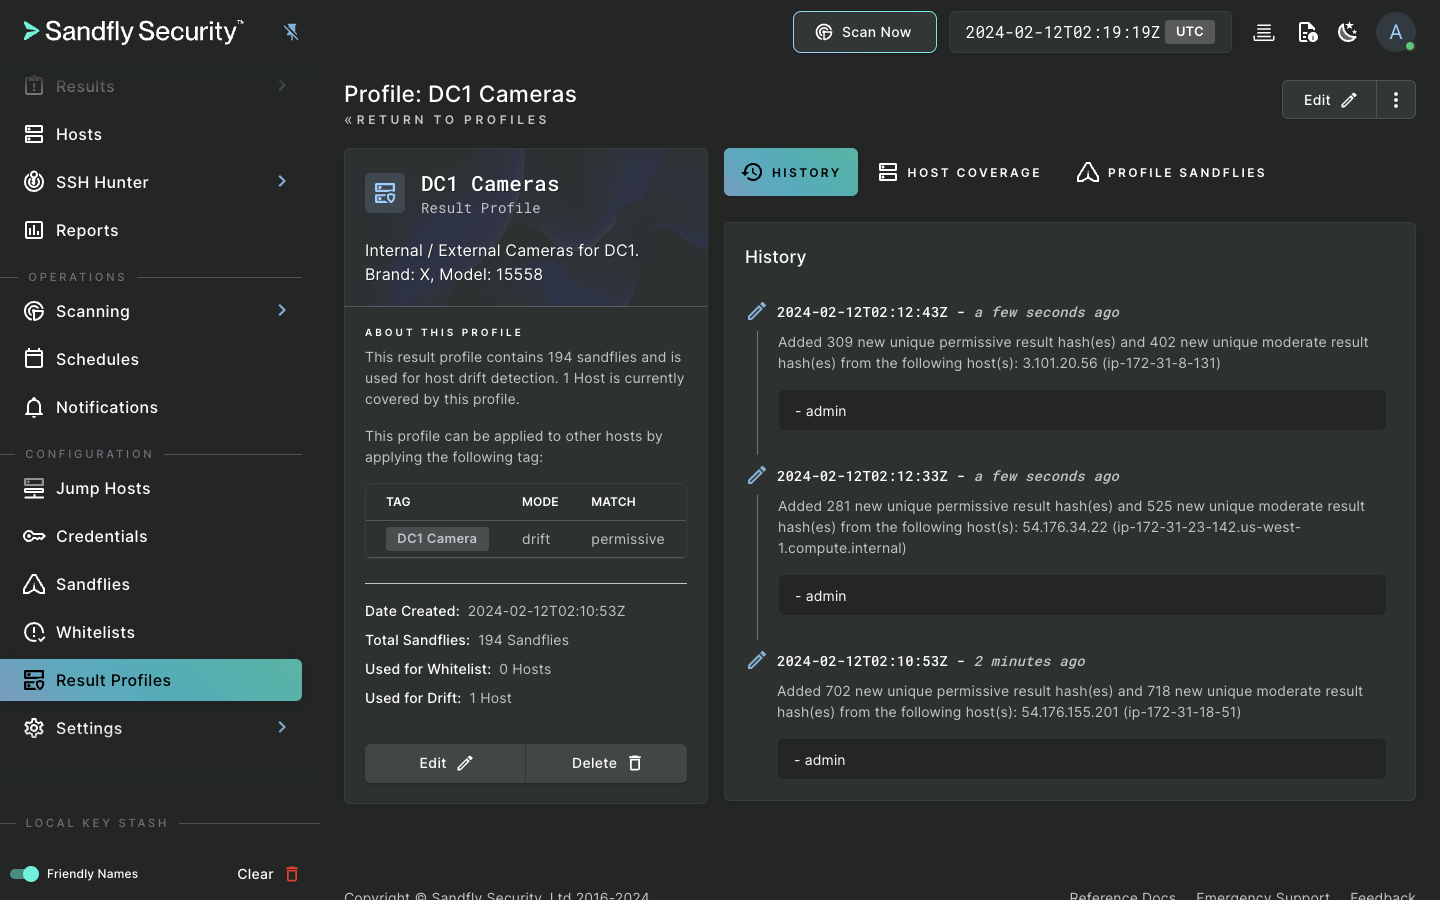
Sandfly Security | Agentless Linux EDR and Incident Response
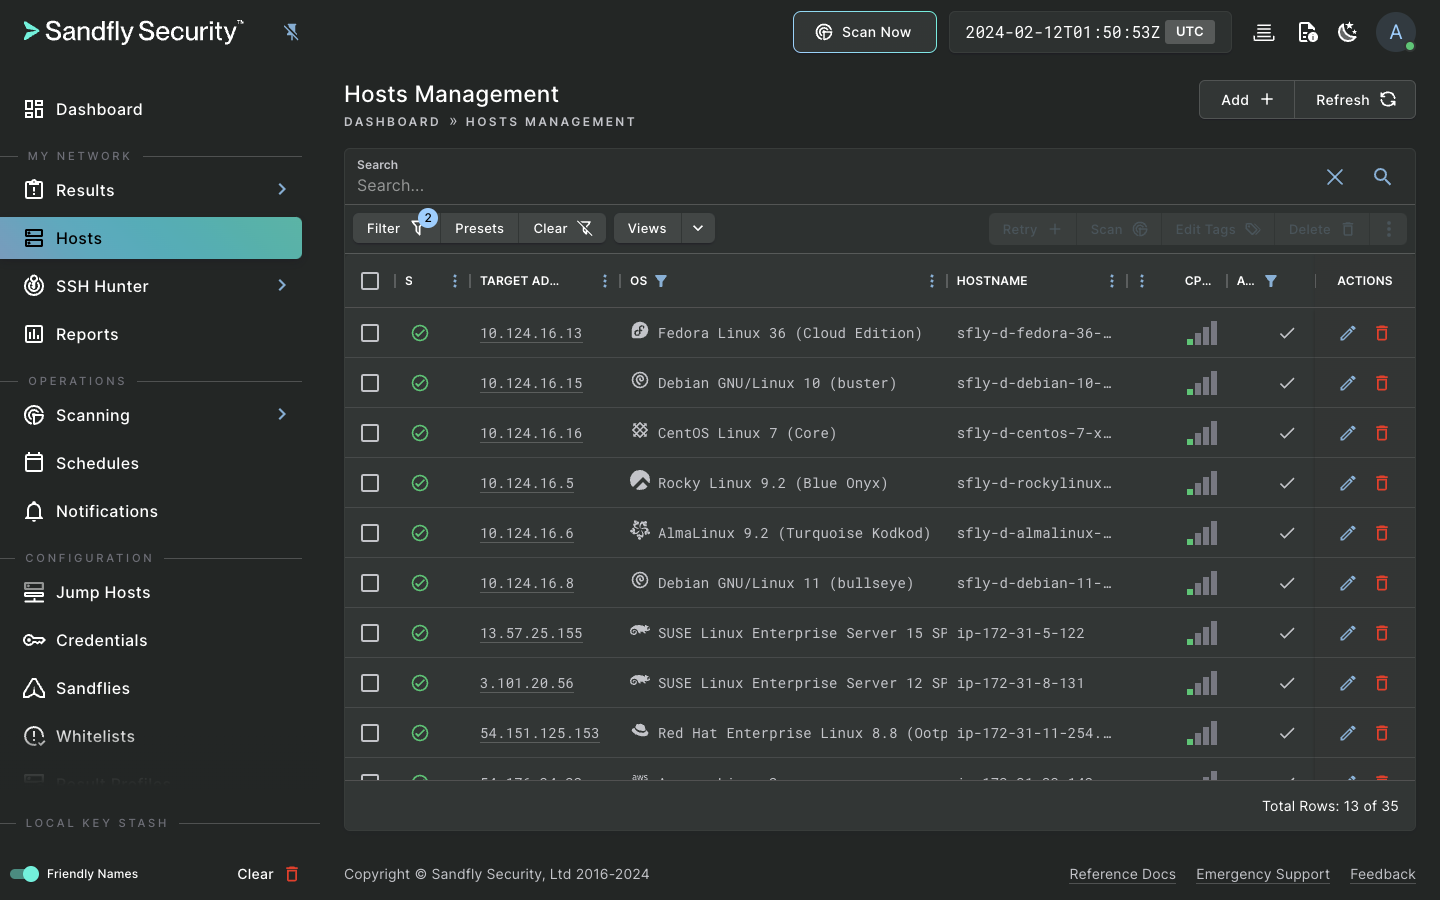
Sandfly Security | Agentless Linux EDR and Incident Response

Sandfly 2.8.0 – Agentless Active Attack Response for Linux

Sandfly 2.8.0 – Agentless Active Attack Response for Linux
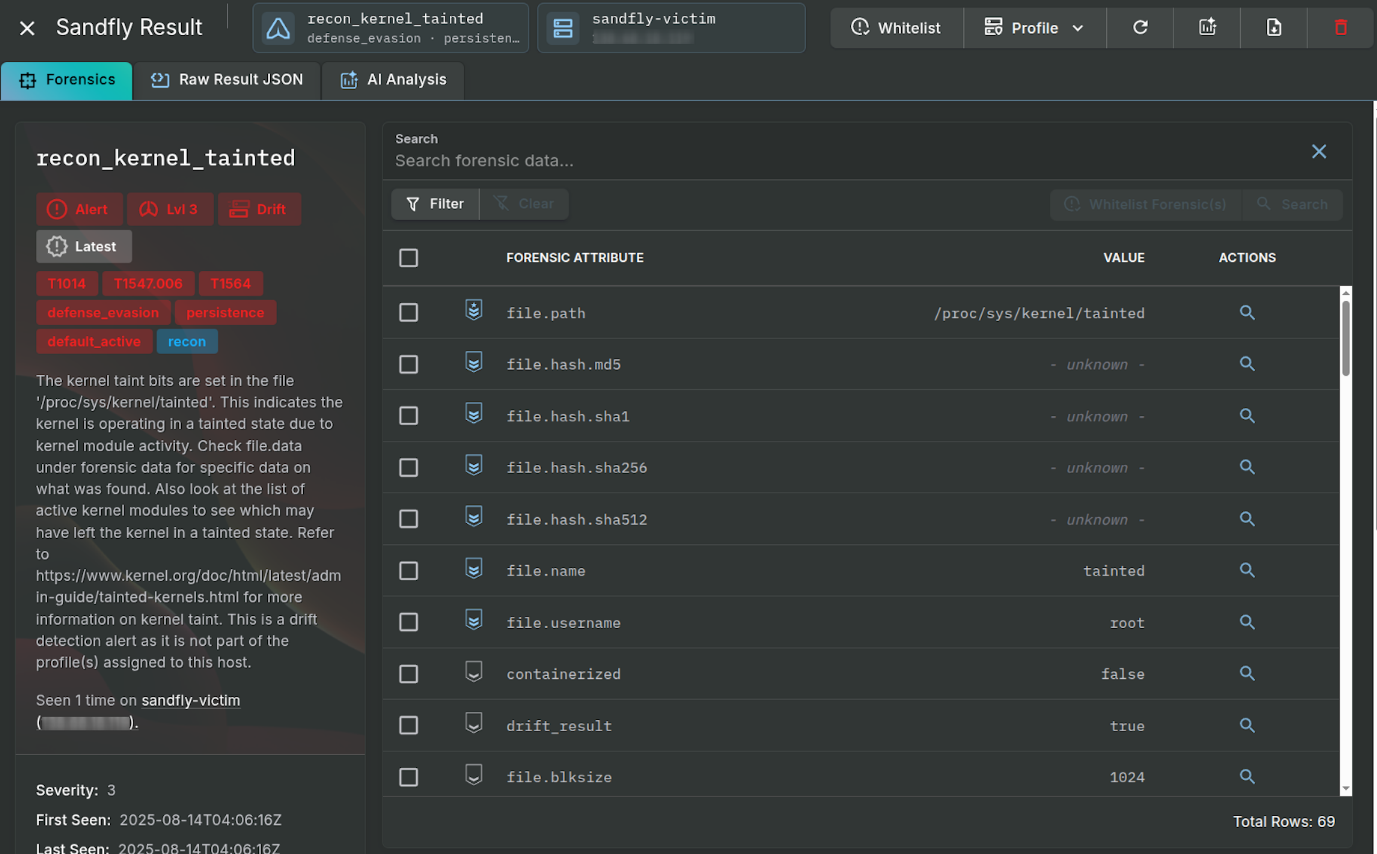
Sandfly Security | 에이전트리스 Linux 보안
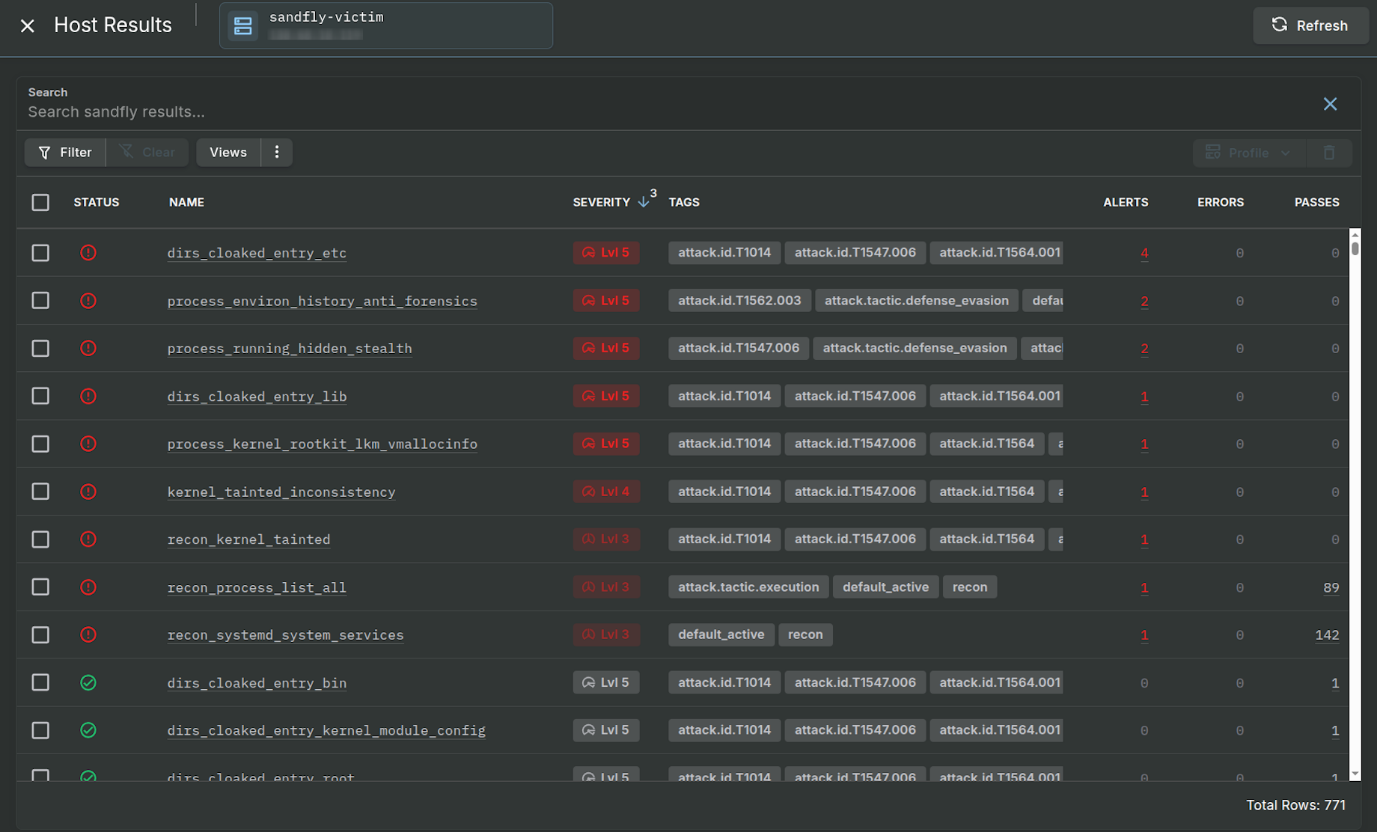
Sandfly Security | 에이전트리스 Linux 보안
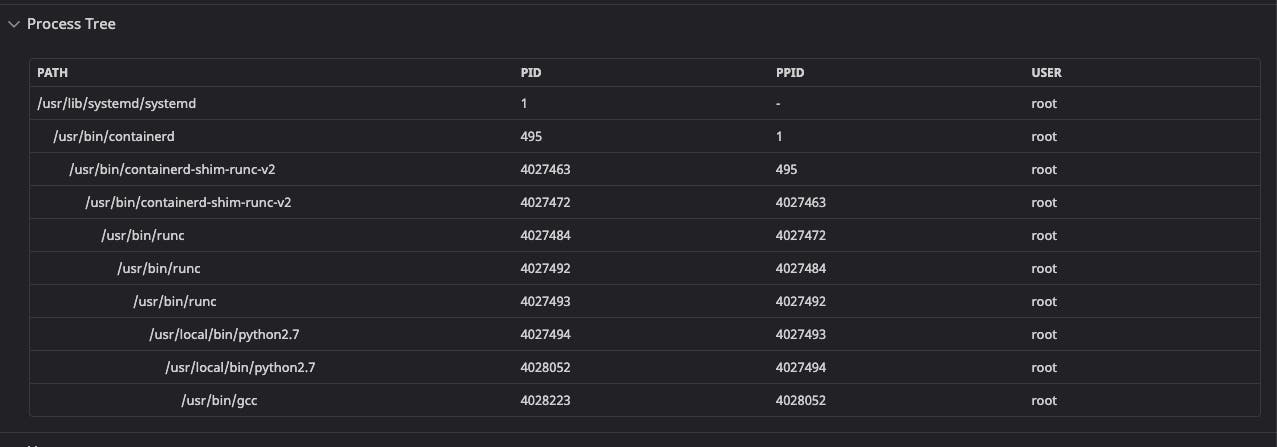
How to detect security threats in Linux processes | Datadog
Advertisement Space (336x280)
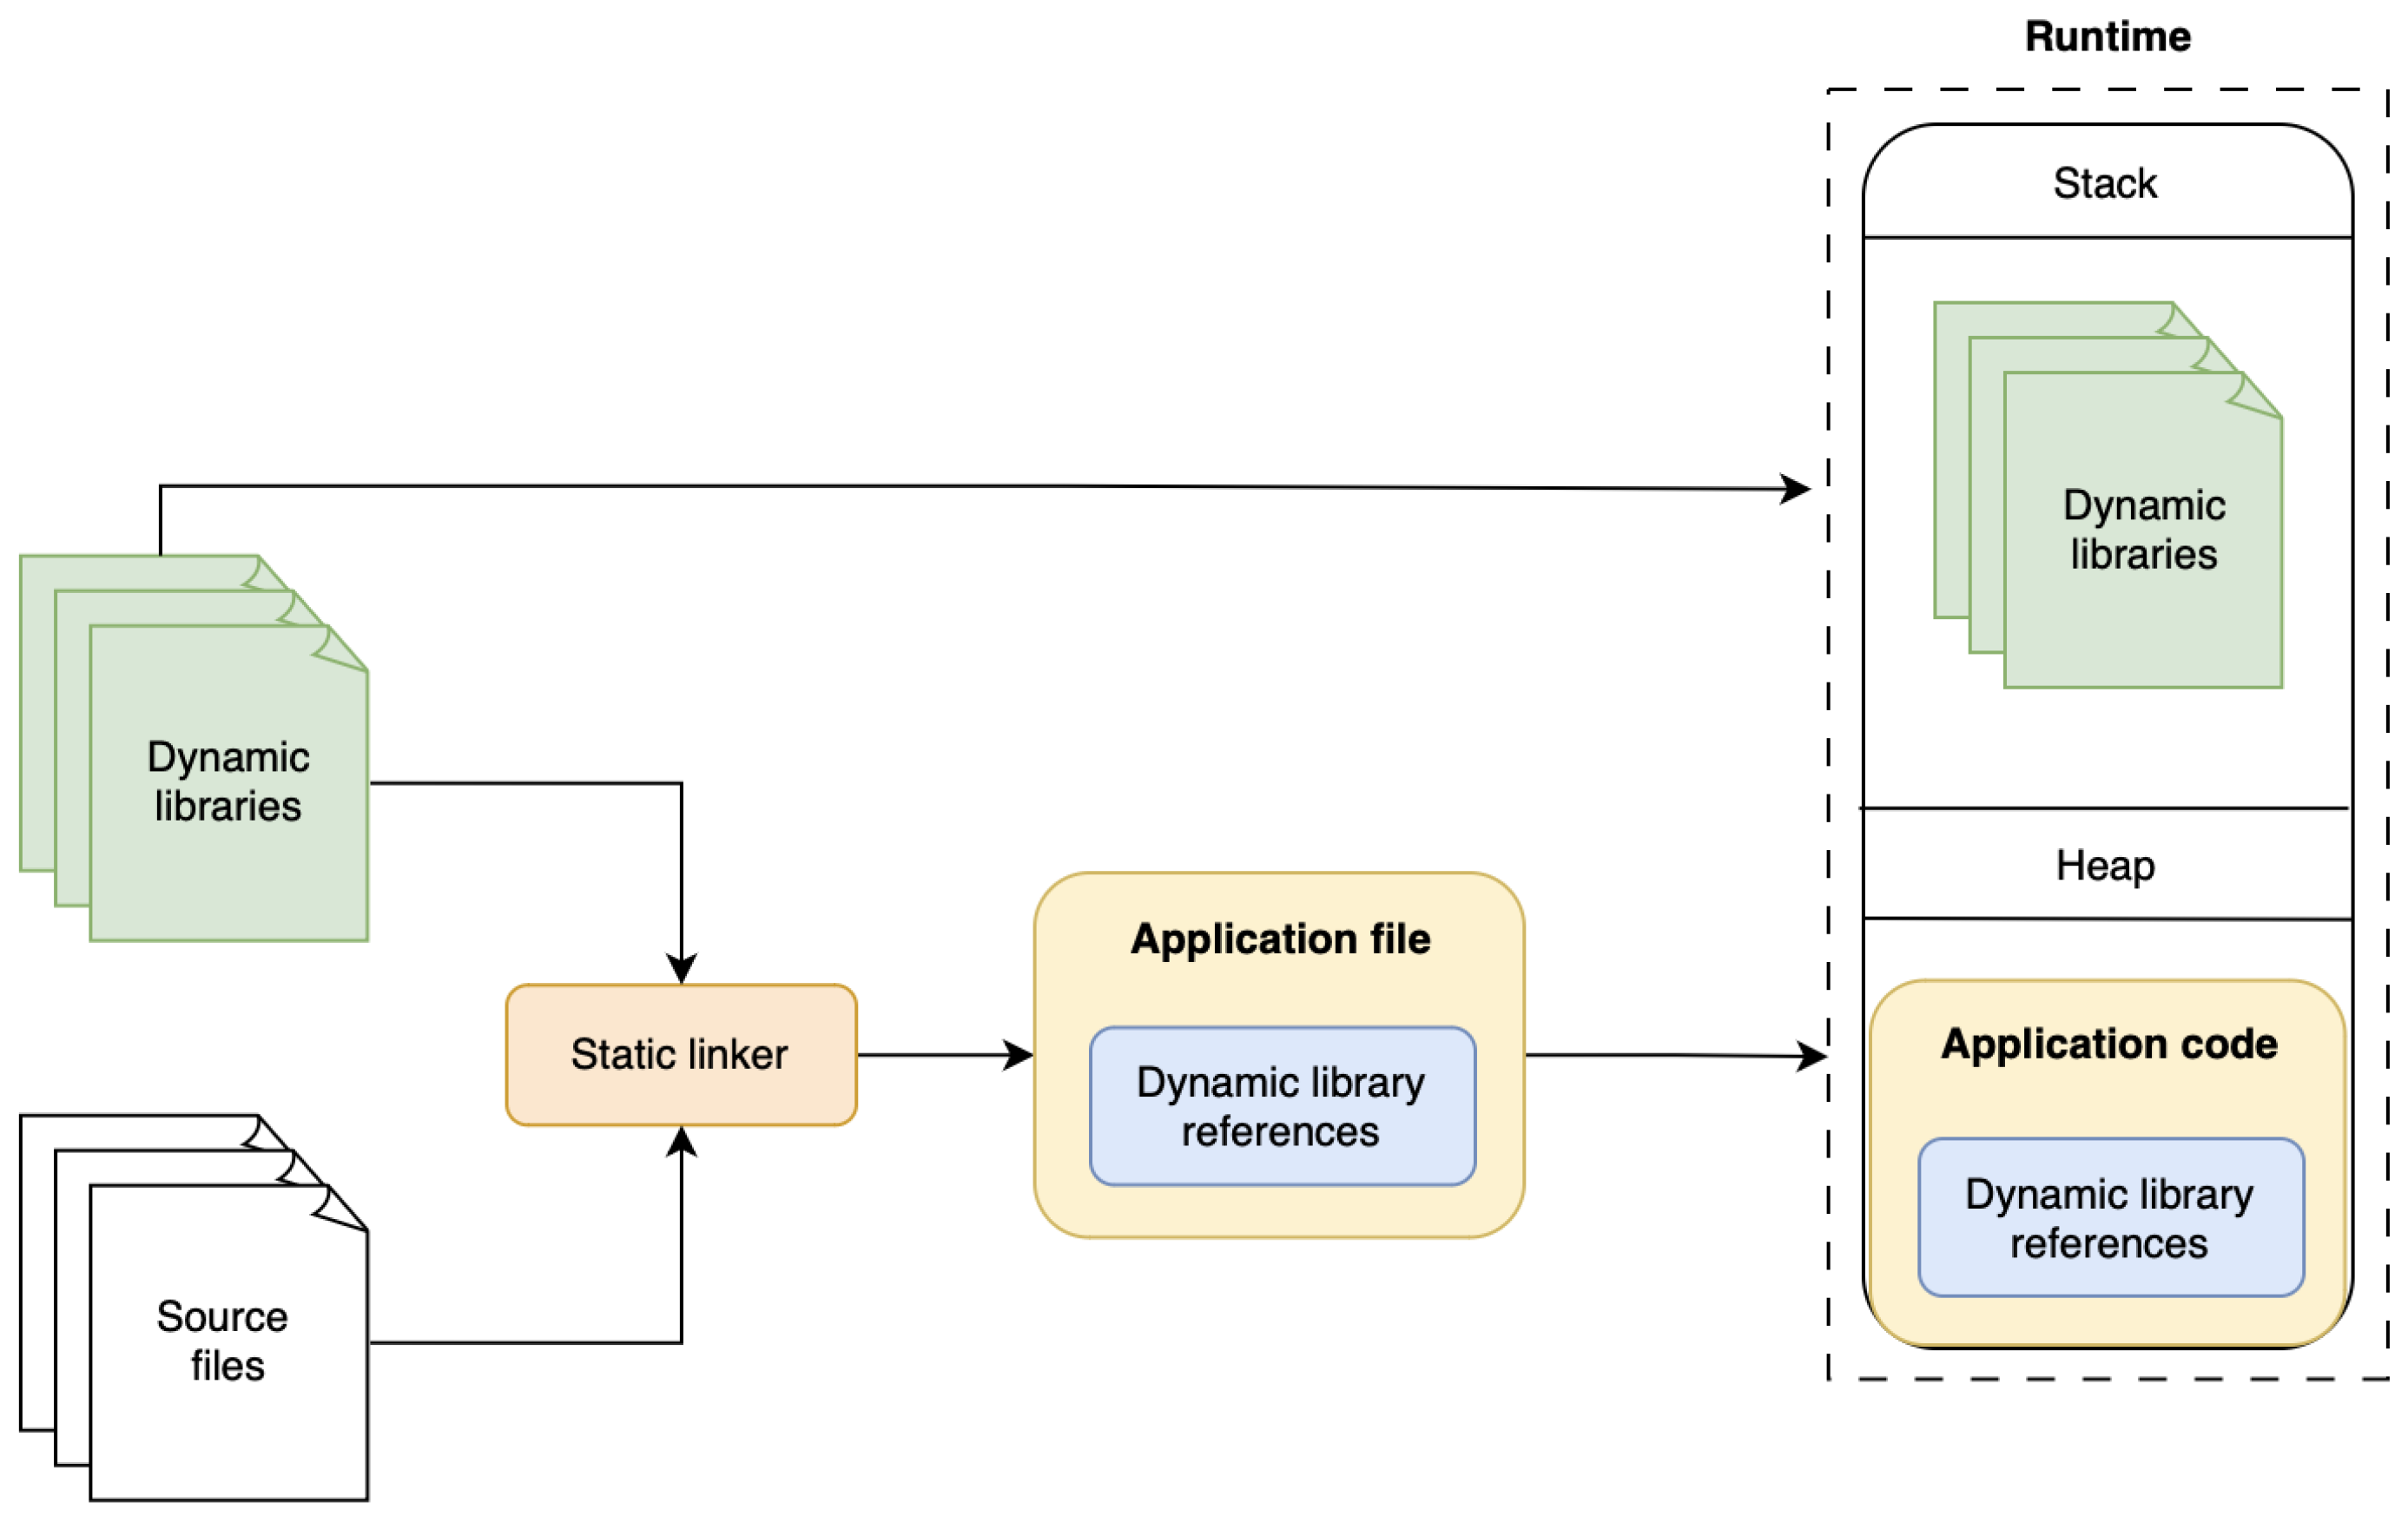
Linux IoT Malware Variant Classification Using Binary Lifting and ...
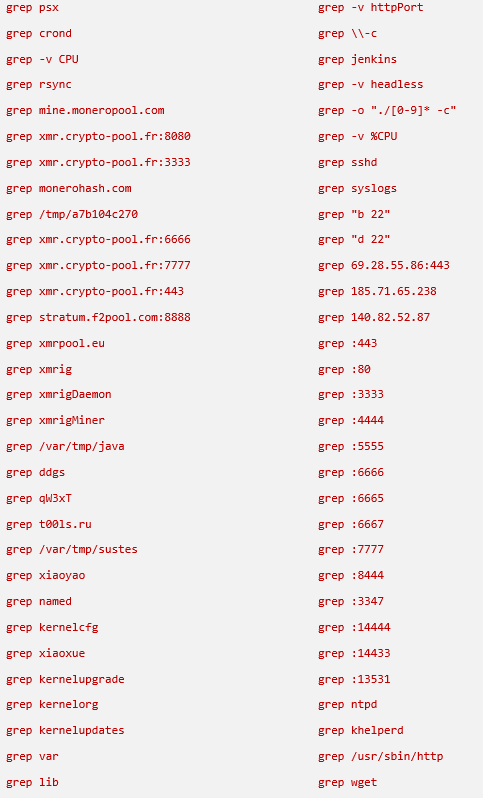
Uncovering Linux based cyberattack using Azure Security Center
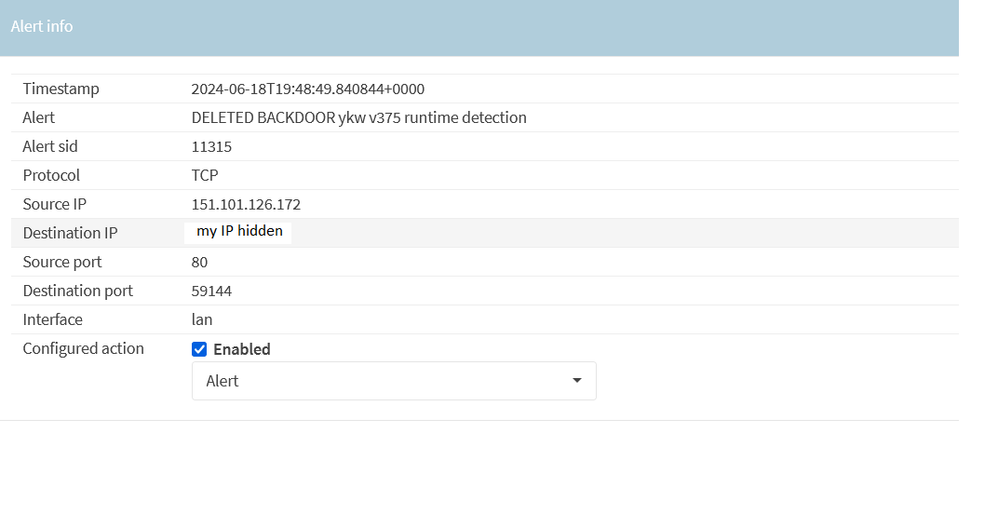
ET DELETED TinyPE Binary - Possibly Hostile and ET MALWARE VMProtect ...
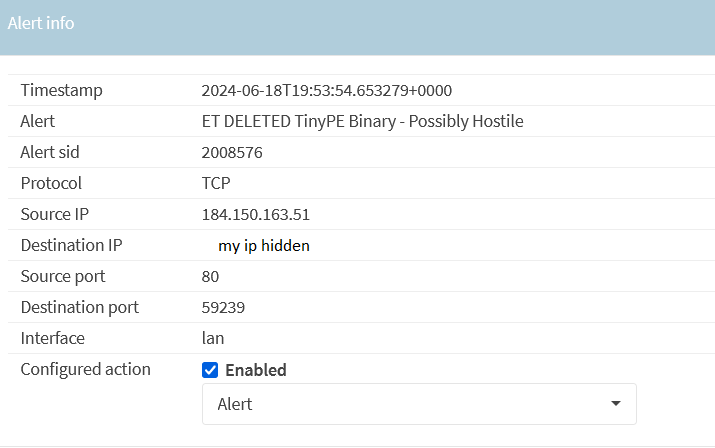
ET DELETED TinyPE Binary - Possibly Hostile and ET MALWARE VMProtect ...

Sandfly 2.1 Released | Sandfly Security

Basic Linux Malware Process Forensics for Incident Responders