
Ebpf Verifier Ensures Safe Kernel Code Execution System Design

eBPF Verifier Ensures Safe Kernel Code Execution | System Design ...
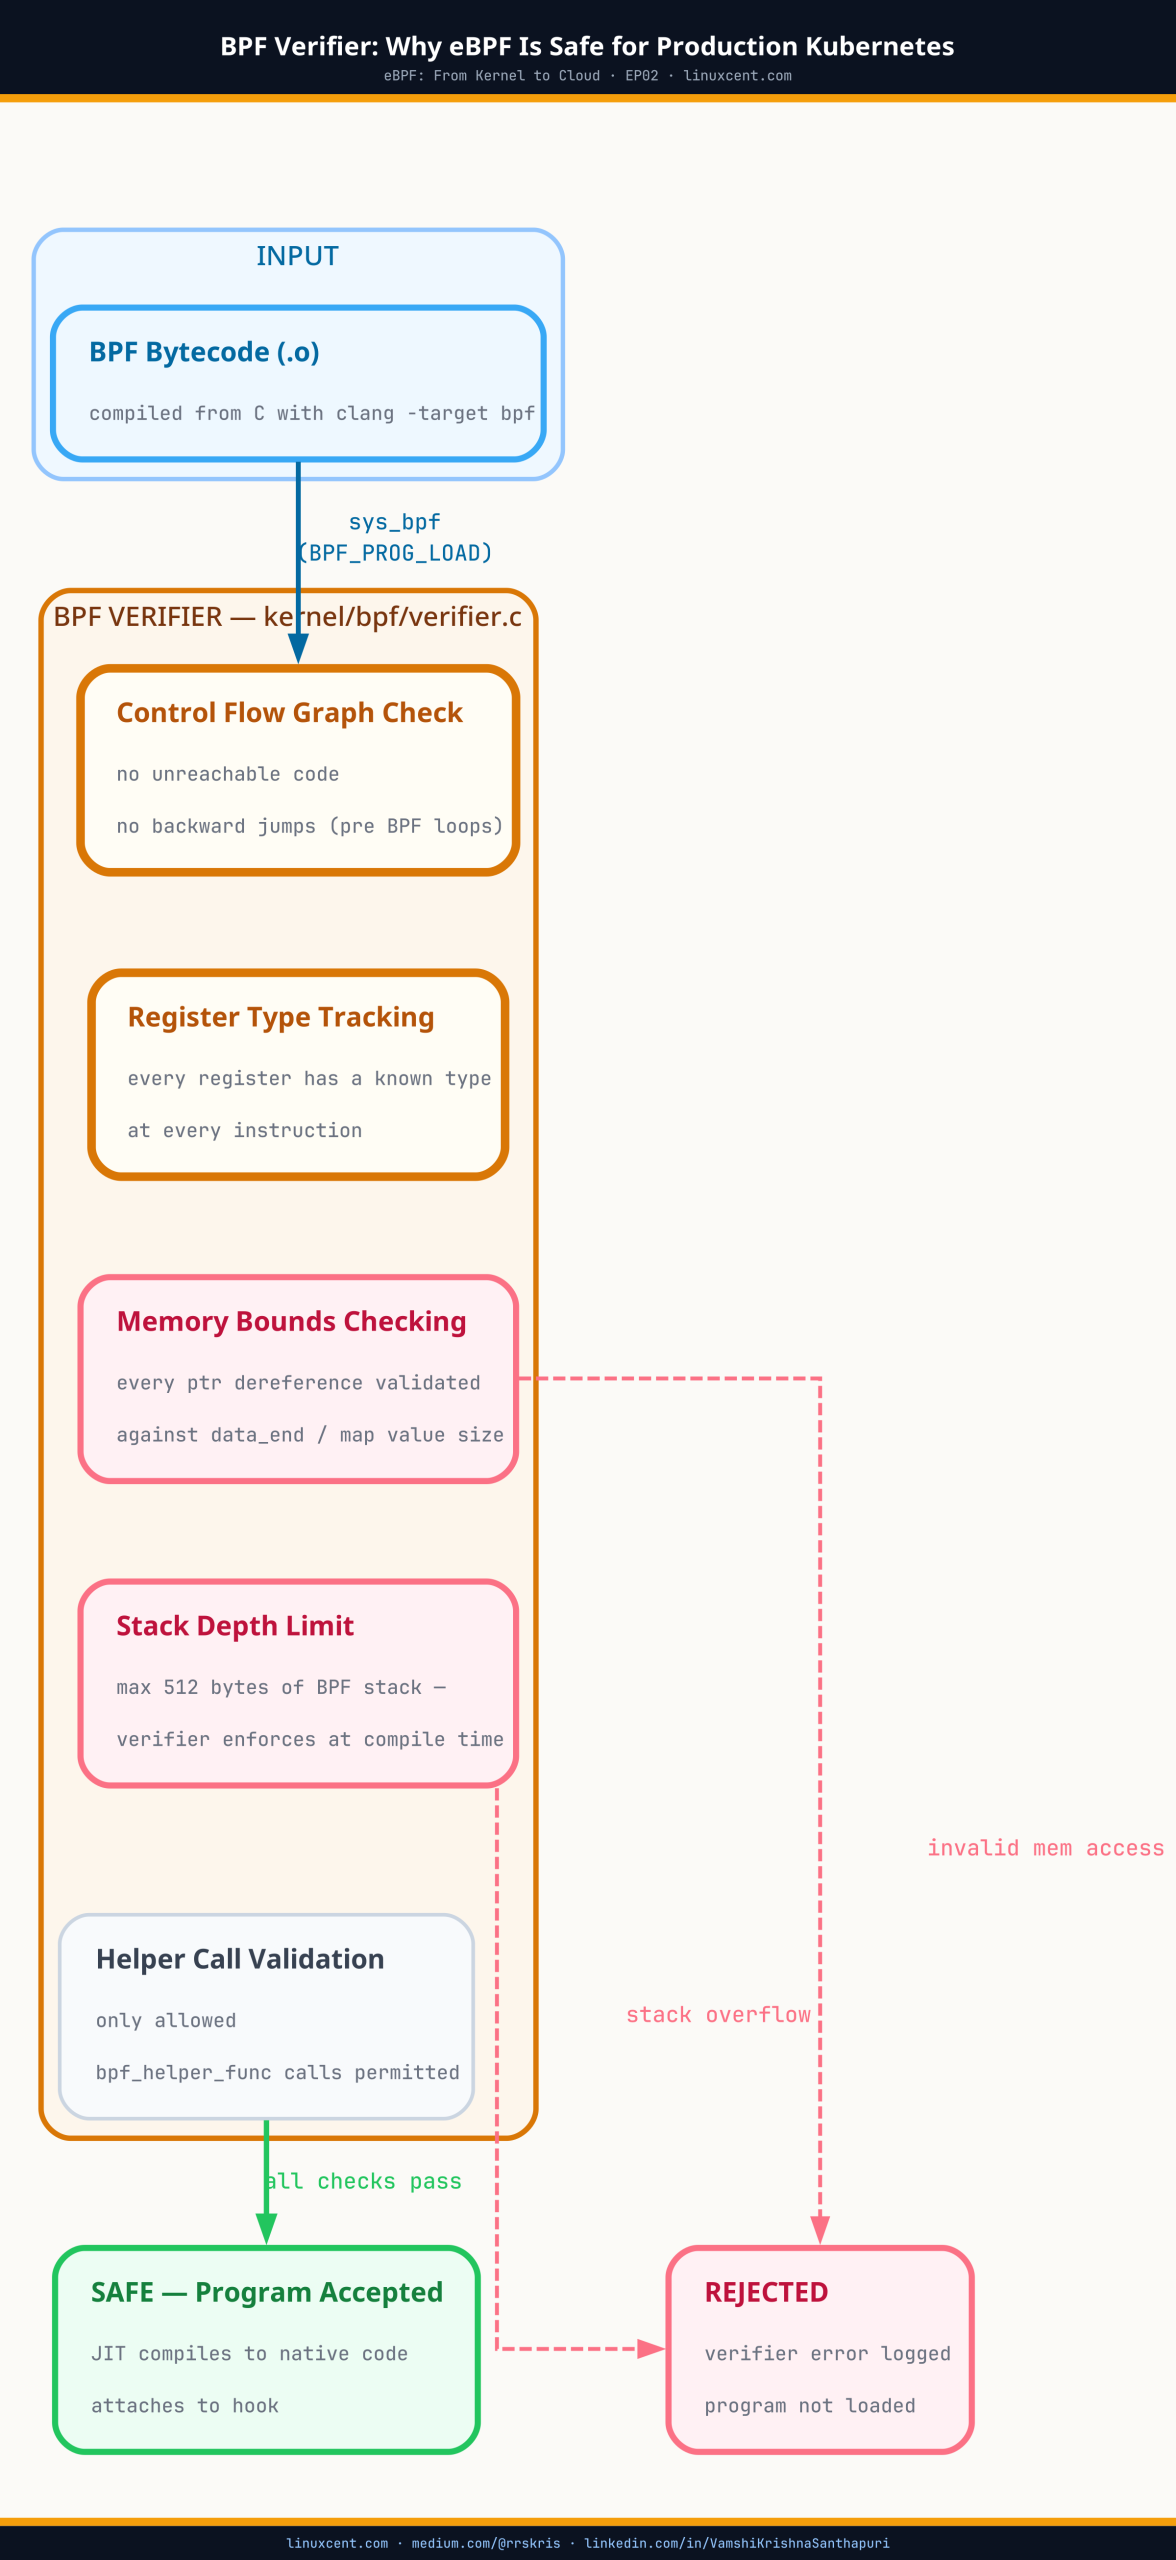
BPF Verifier Explained: Why eBPF Is Safe for Production Kubernetes
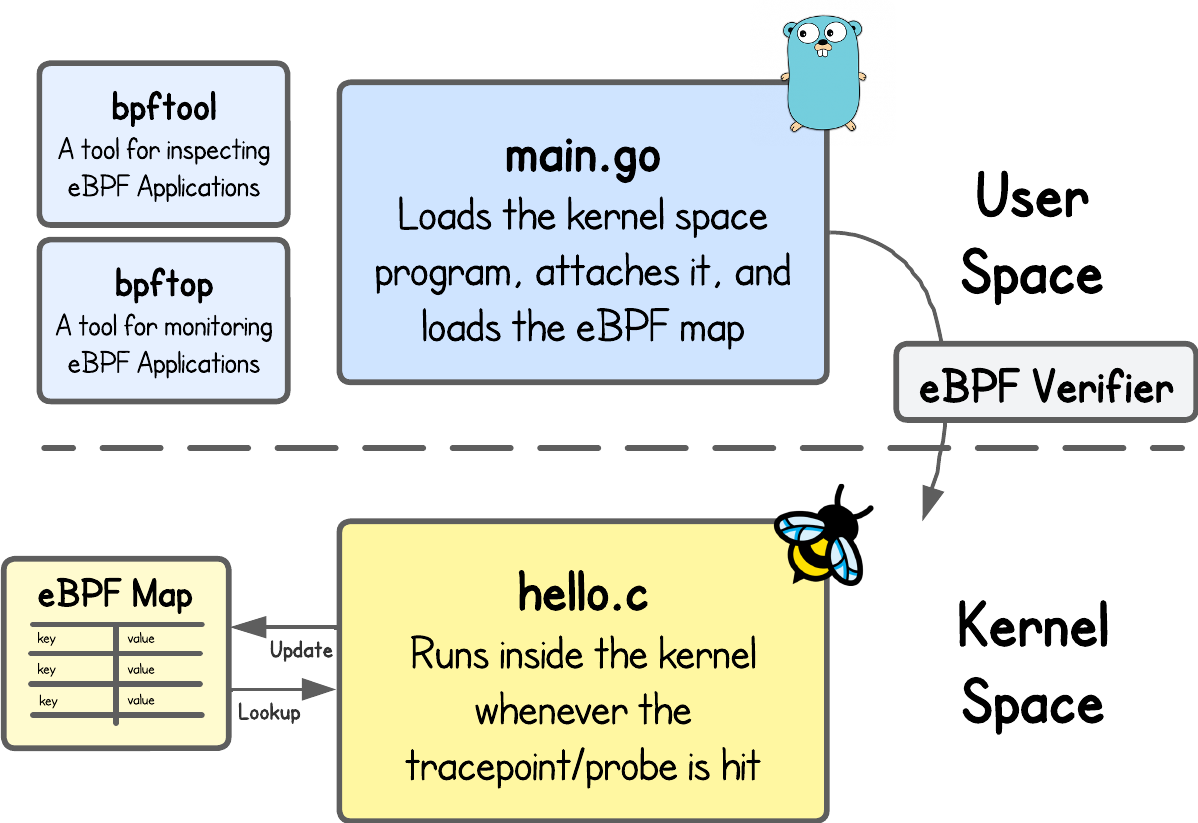
eBPF Verifier: Why the Kernel Can Safely Run eBPF Programs
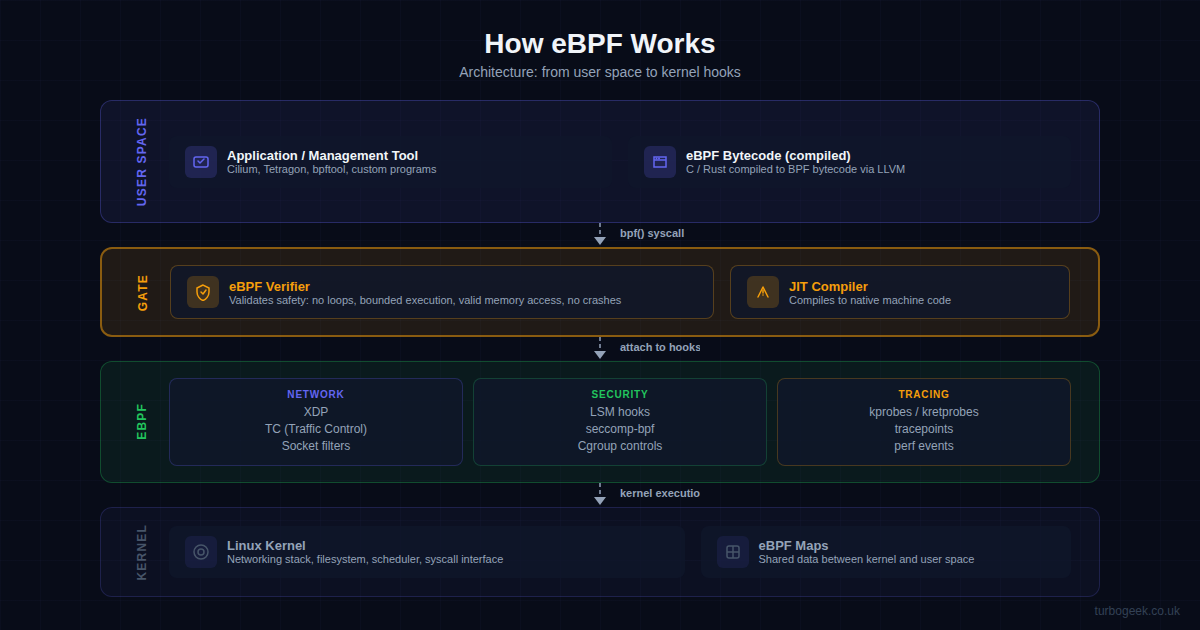
eBPF Security on Linux: Kernel Security Guide
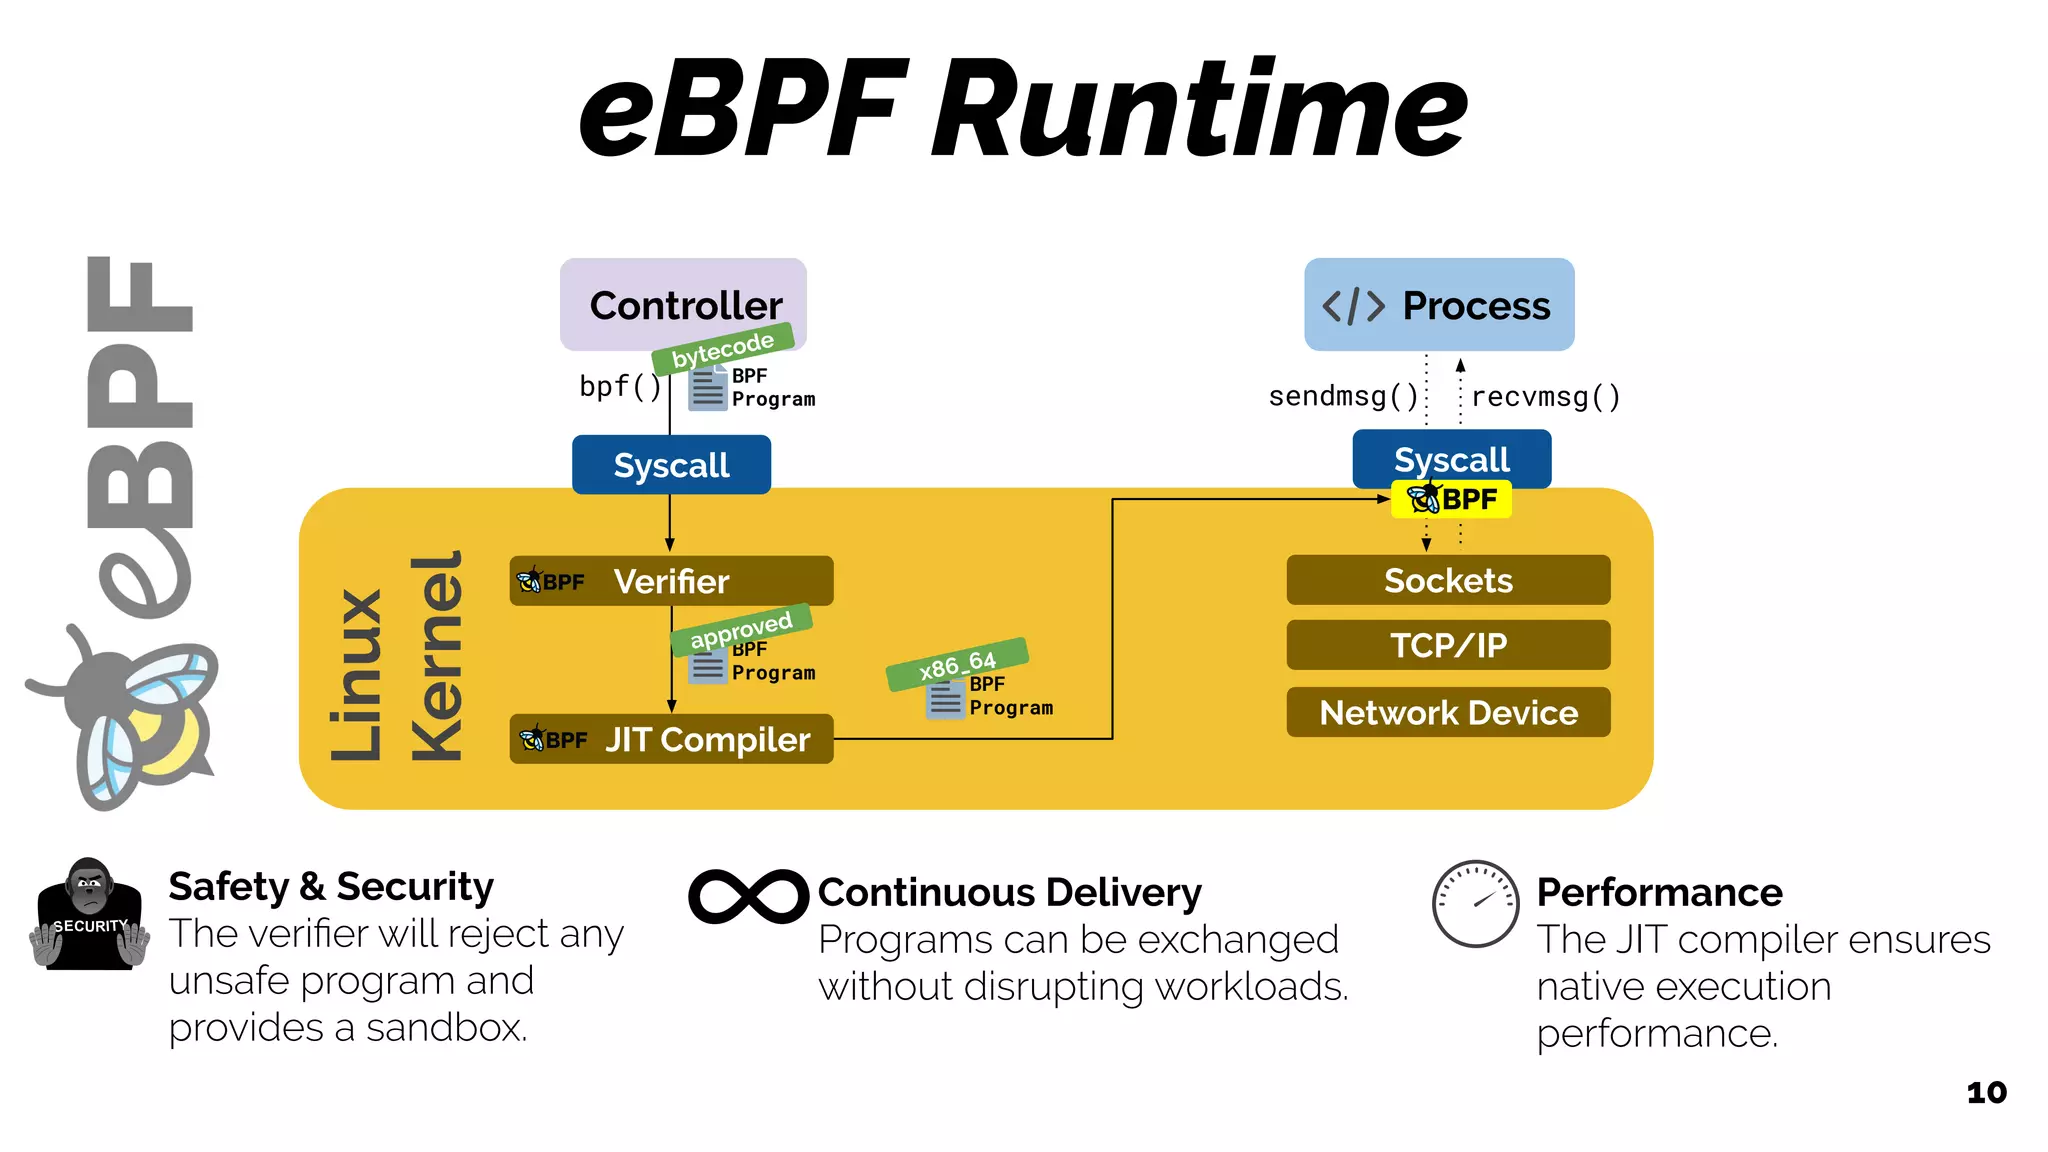
eBPF - Rethinking the Linux Kernel | PDF

2: Linux kernel eBPF architecture. | Download Scientific Diagram
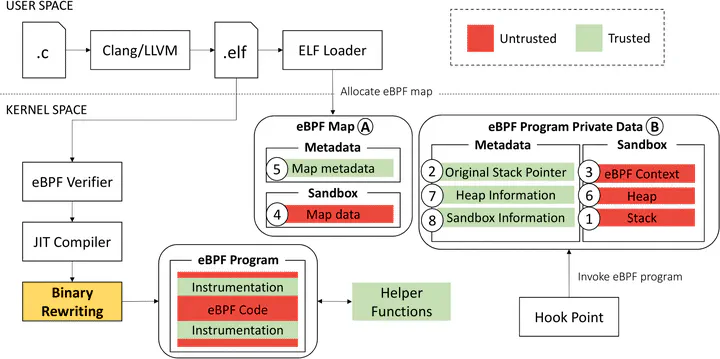
SafeBPF: Hardware-assisted Defense-in-depth for eBPF Kernel Extensions ...
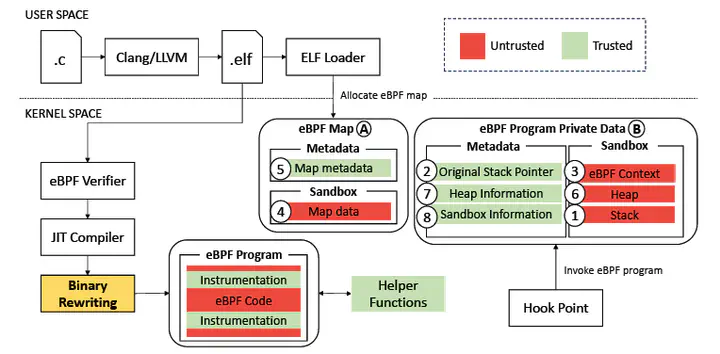
SafeBPF: Hardware-assisted Defense-in-depth for eBPF Kernel Extensions ...

eBPF for Next-level Linux System Monitoring and Performance
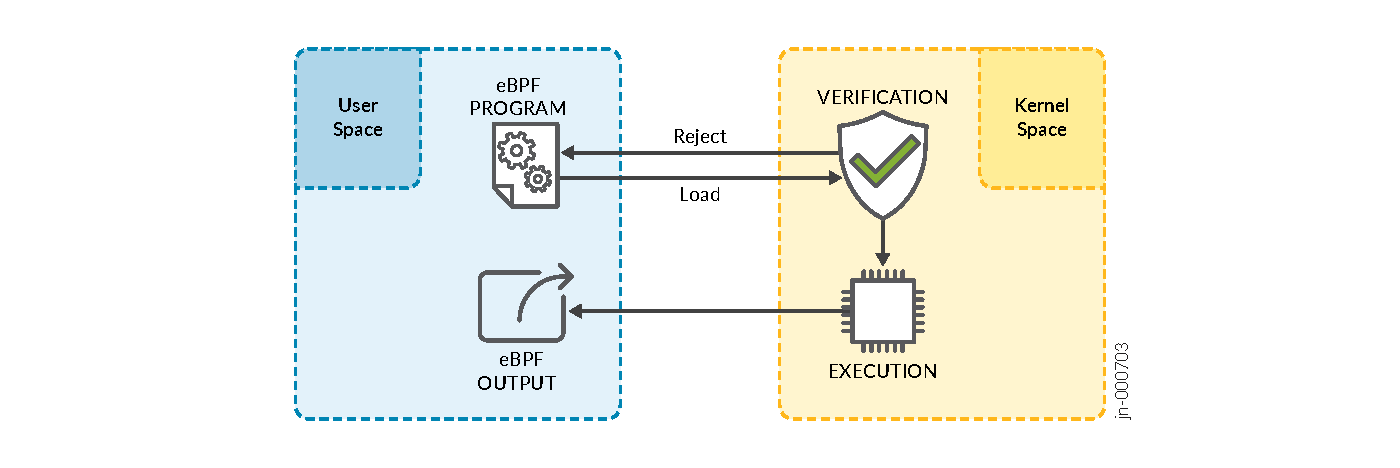
eBPF Kernel Data Plane (Tech Preview) | CN2 23.3 | Juniper Networks
Advertisement Space (300x250)

Issue #002 | Programming the Kernel with eBPF

2: Linux kernel eBPF architecture. | Download Scientific Diagram
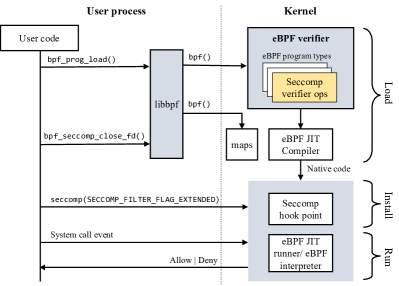
[2302.10366] Programmable System Call Security with eBPF

eBPF Foundation funding for safer, more flexible Linux kernel programming

eBPF for Kernel Exploit Detection and Prevention at BlackHat USA 2022

2: Linux kernel eBPF architecture. | Download Scientific Diagram
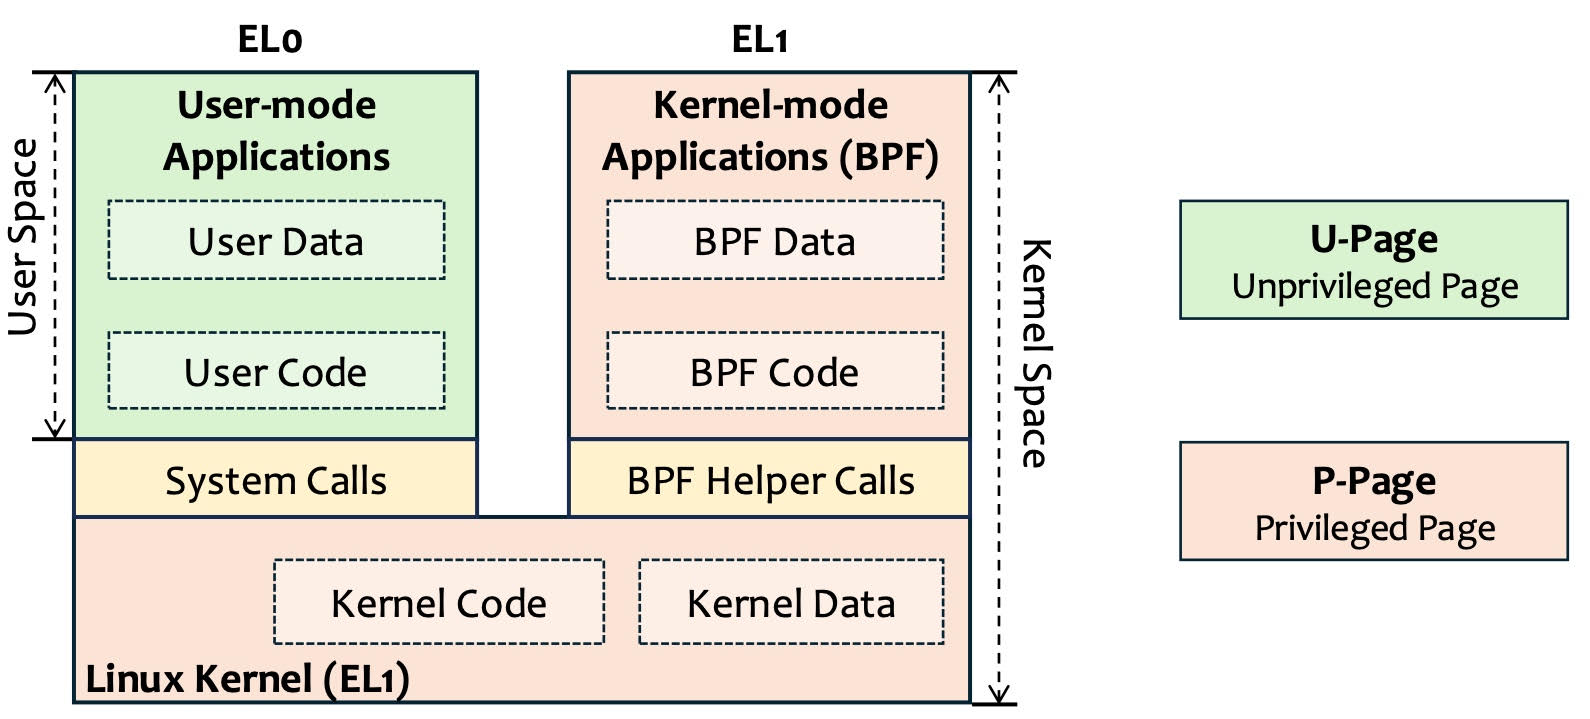
Research Update: Isolated Execution Environment for eBPF (Part 2) – eBPF
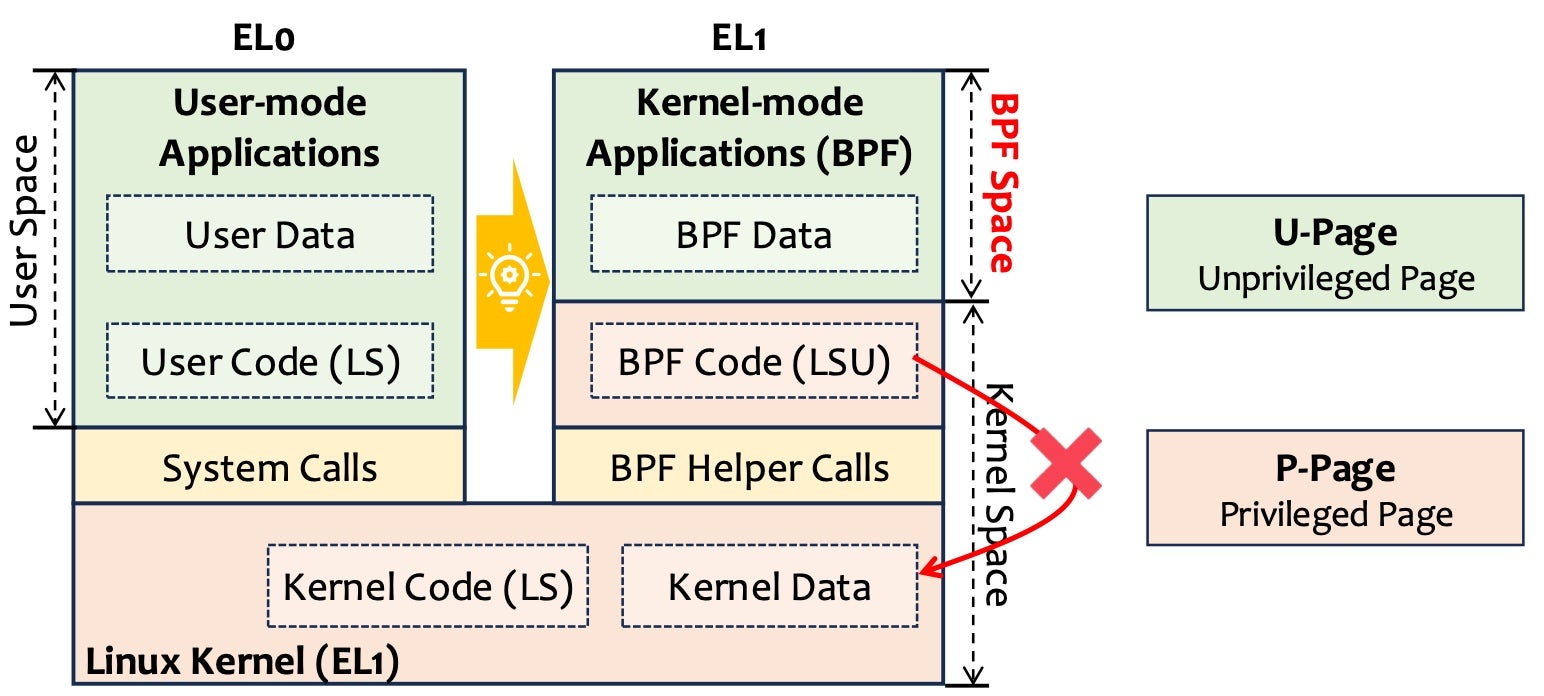
Research Update: Isolated Execution Environment for eBPF (Part 2) – eBPF
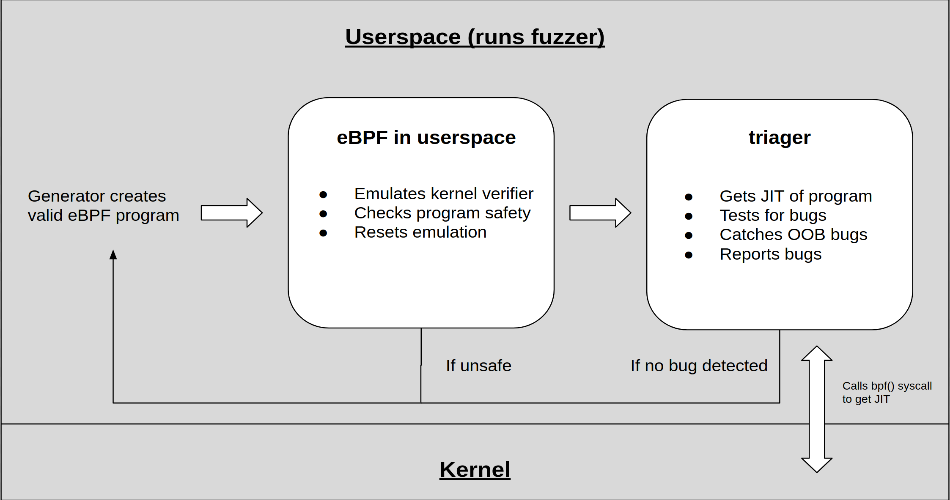
Fuzzing for eBPF JIT bugs in the Linux kernel :: Simon Scannell's ...
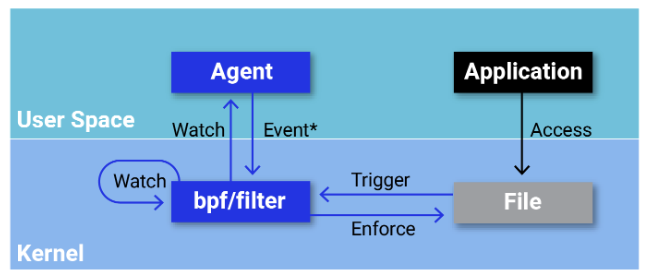
Seccomp, eBPF, and the Importance of Kernel System Call Filtering
Advertisement Space (336x280)
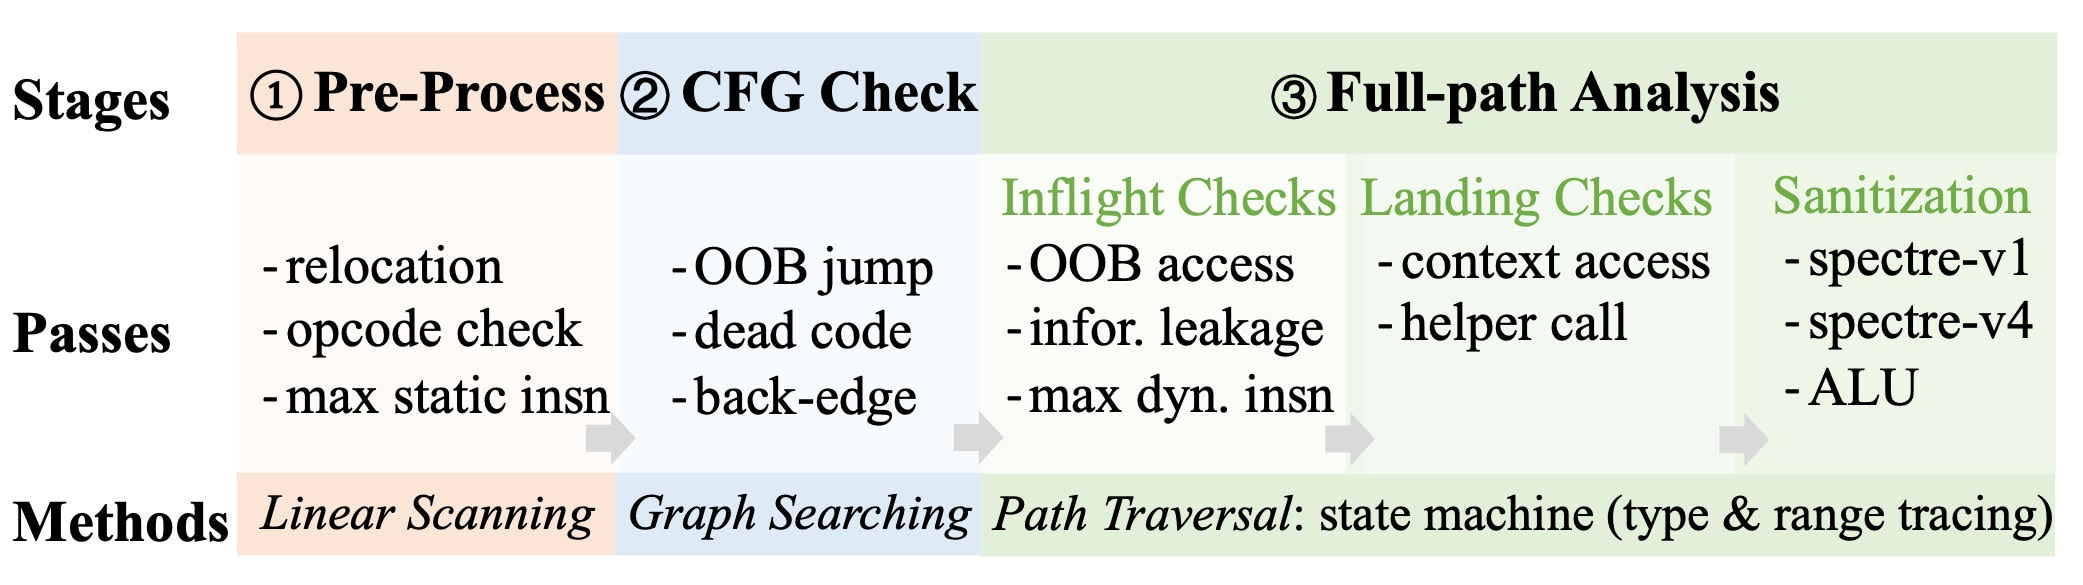
Research Update: Isolated Execution Environment for eBPF – eBPF
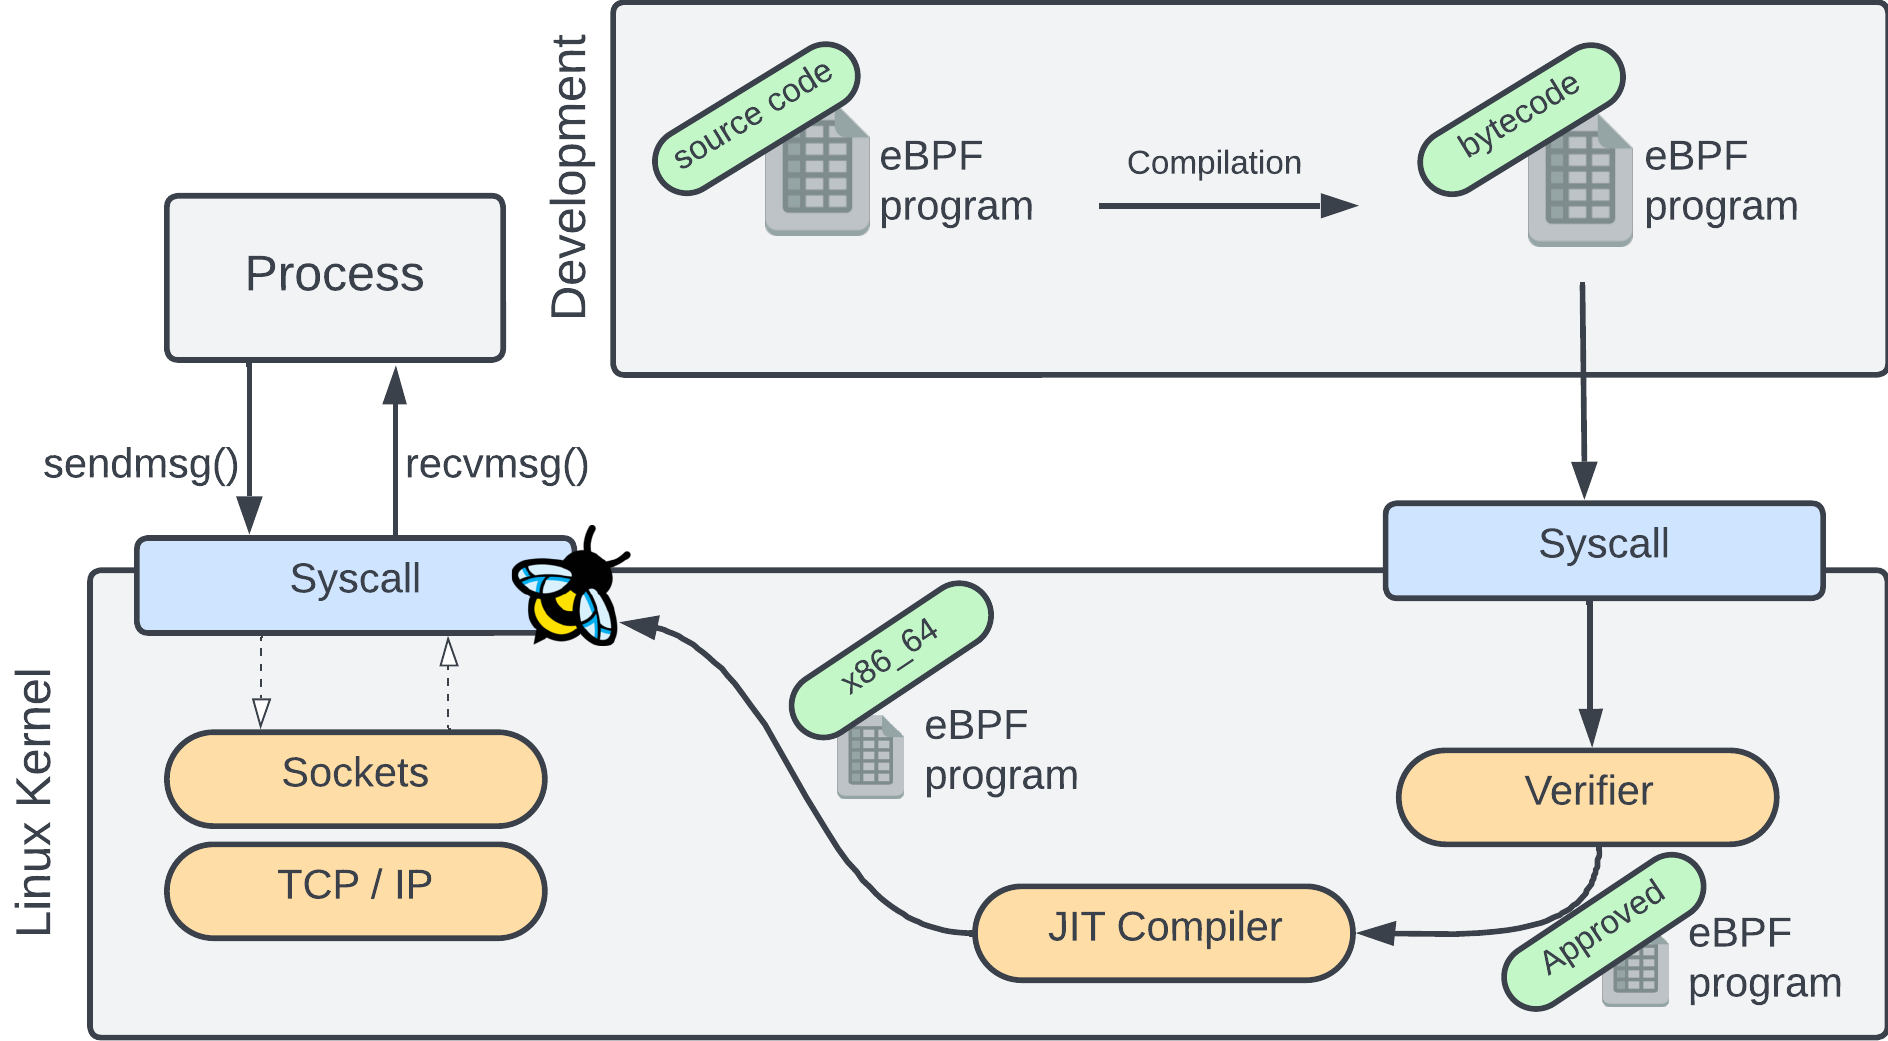
The eBPF Verifier Errors Project - Mostly nerdlessMostly nerdless
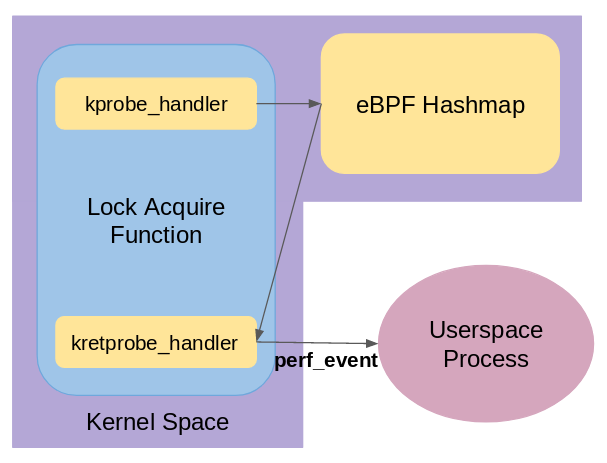
kLockStat: An eBPF Tool To Monitor Linux Kernel Lock Contentions ...
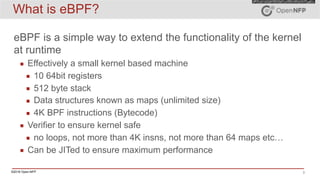
Transparent eBPF Offload: Playing Nice with the Linux Kernel | PPT

Seccomp, eBPF, and the Importance of Kernel System Call Filtering

Harnessing the eBPF Verifier - Security Boulevard
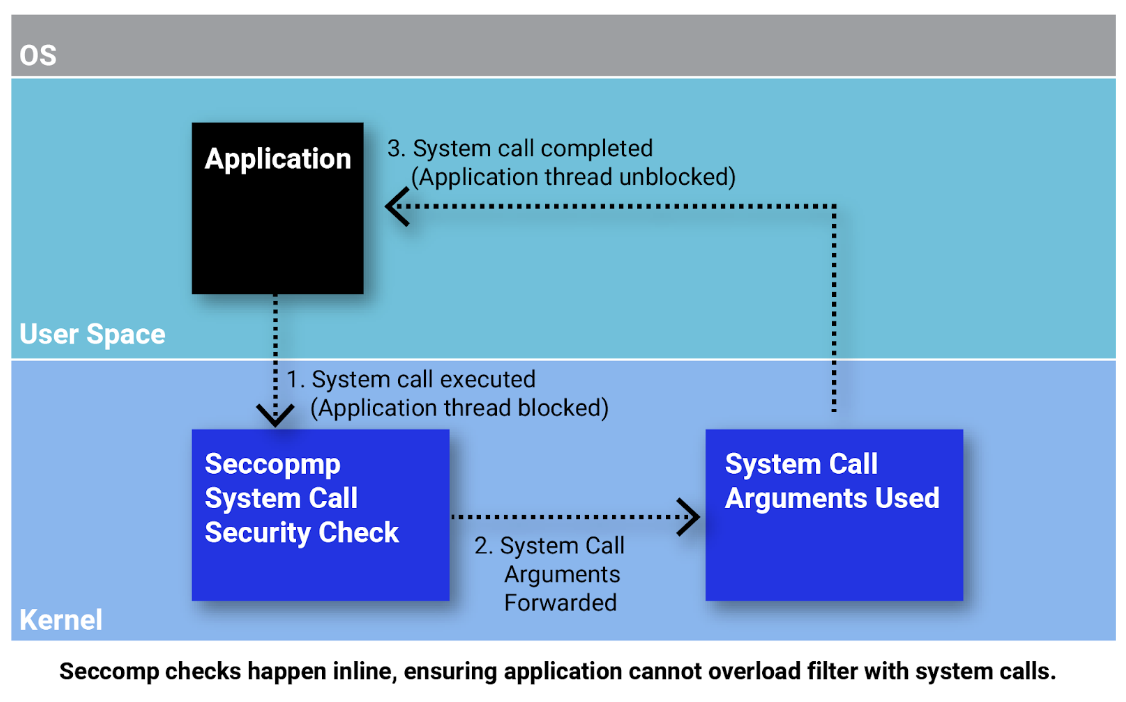
Seccomp, eBPF, and the Importance of Kernel System Call Filtering

Free Video: Secure the Linux Kernel with eBPF Linux Security Module ...
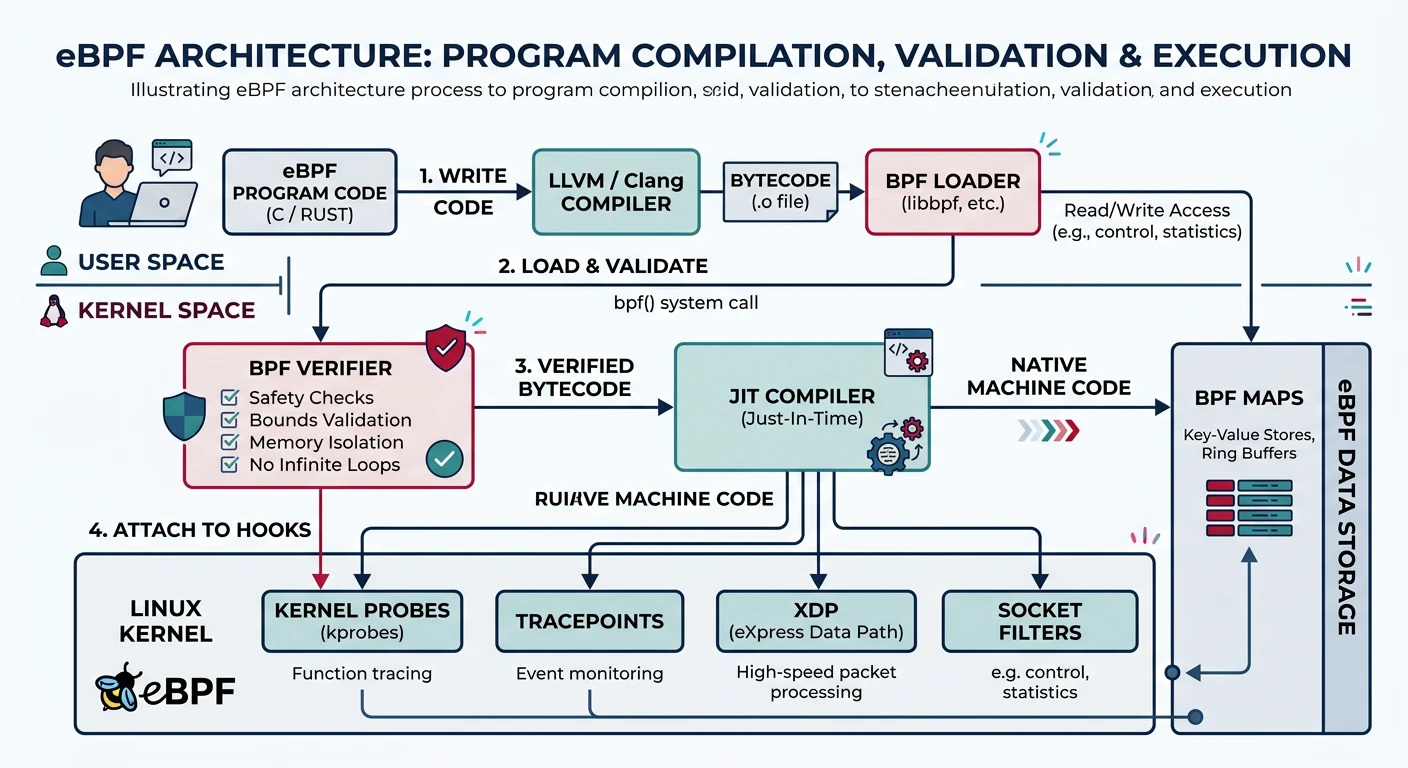
Part 22: Advanced Kernel Internals | Computer Architecture & OS Mastery ...

An introduction to eBPF and where it shines
Advertisement Space (336x280)
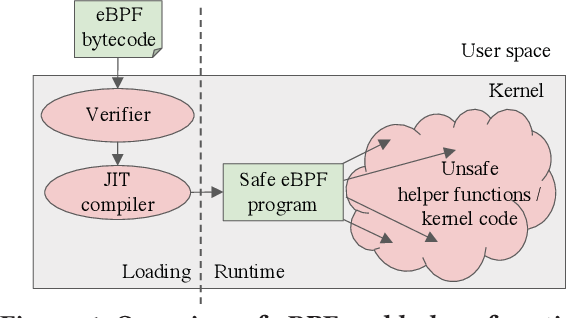
Figure 1 from Kernel extension verification is untenable | Semantic Scholar
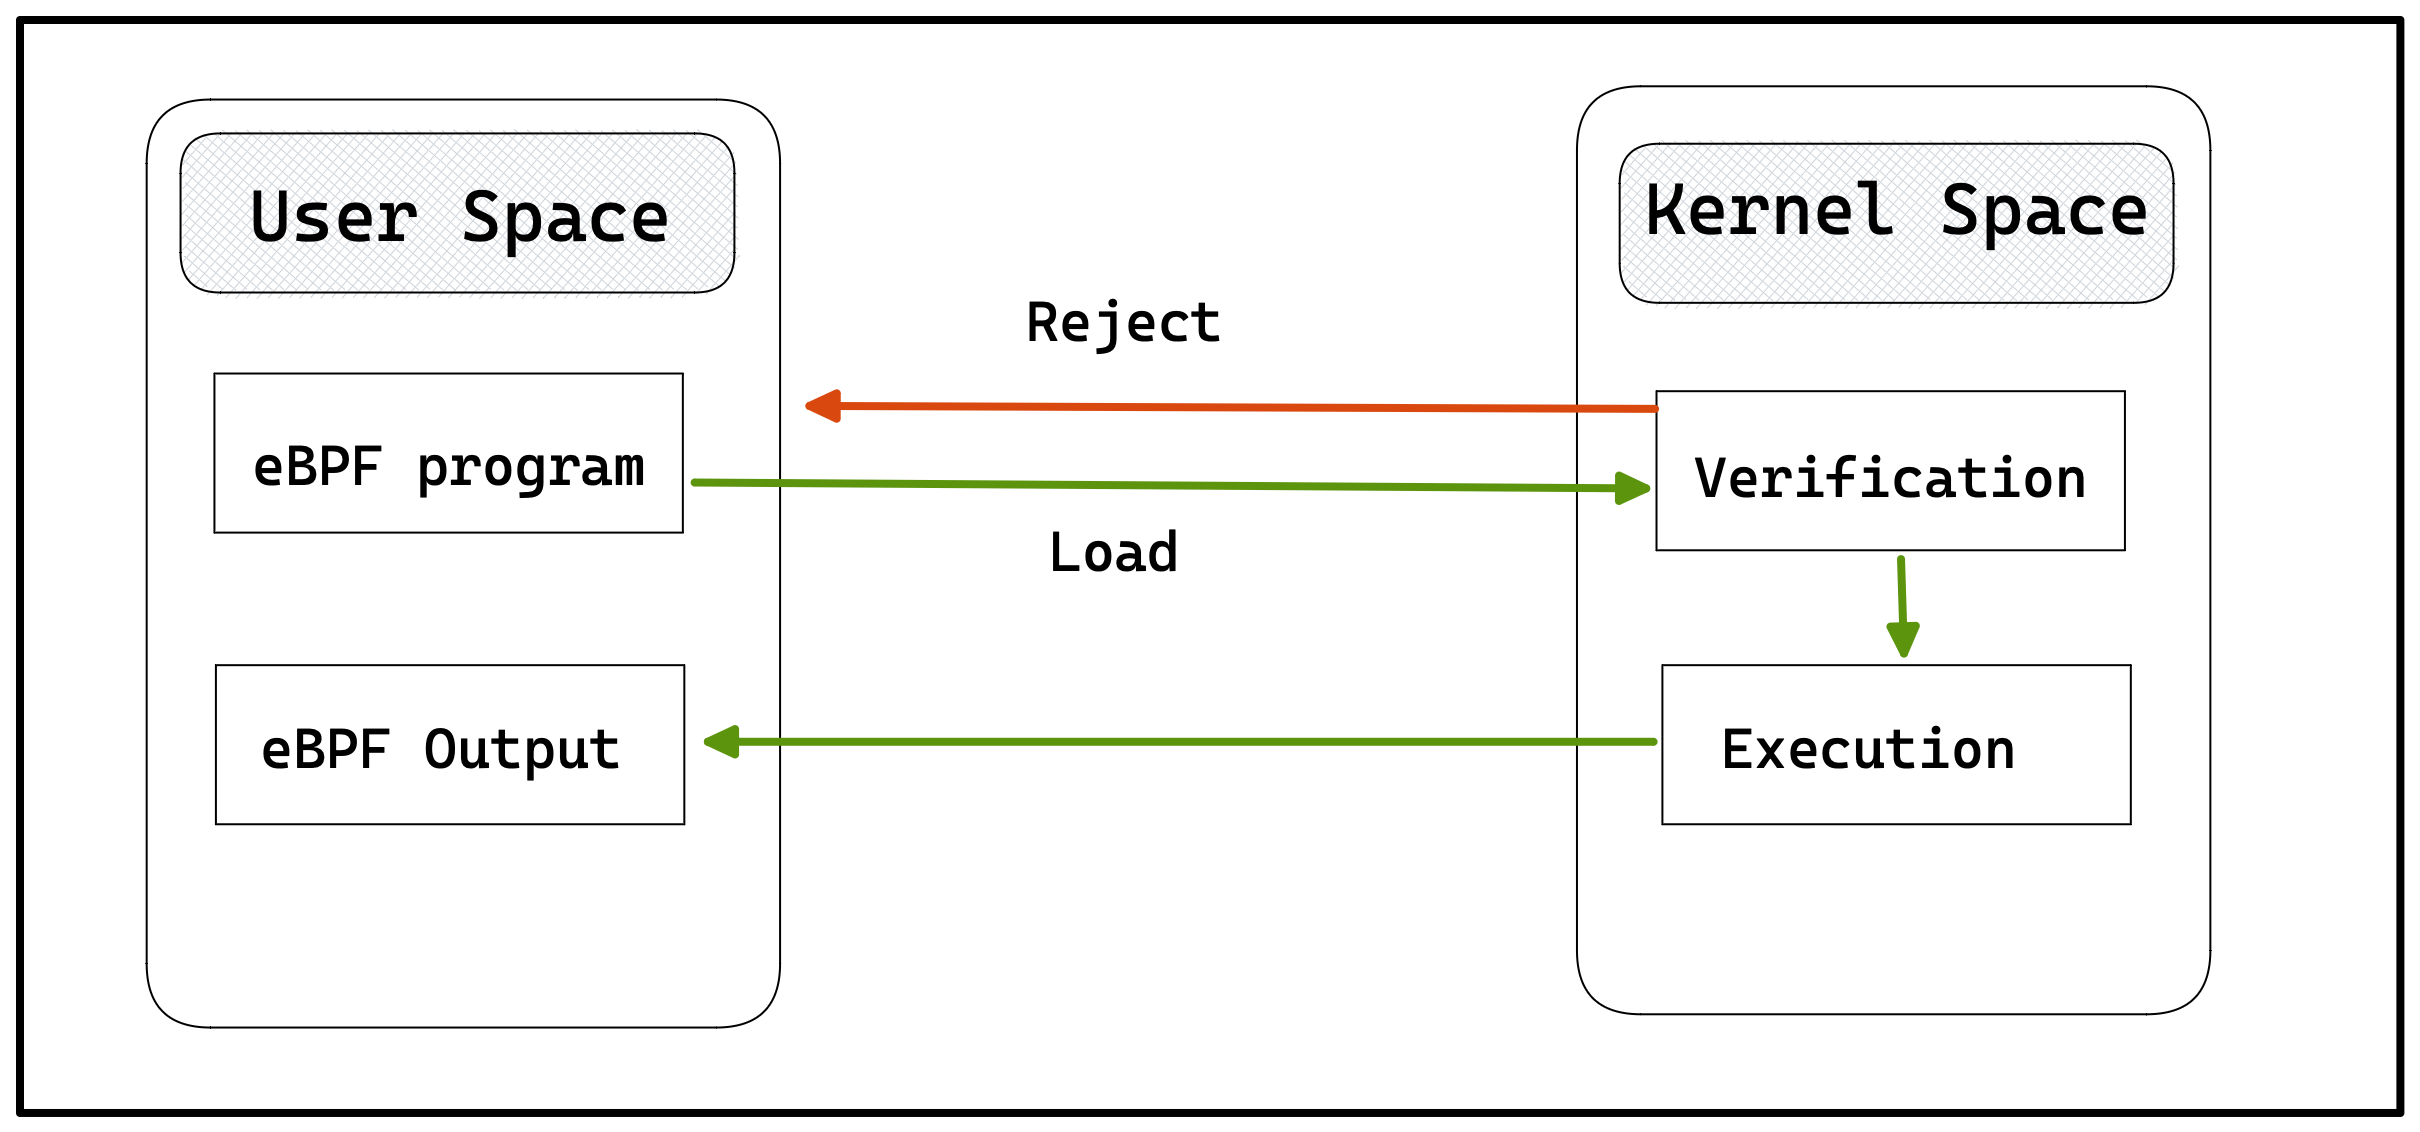
eBPF for Cybersecurity - Part 1
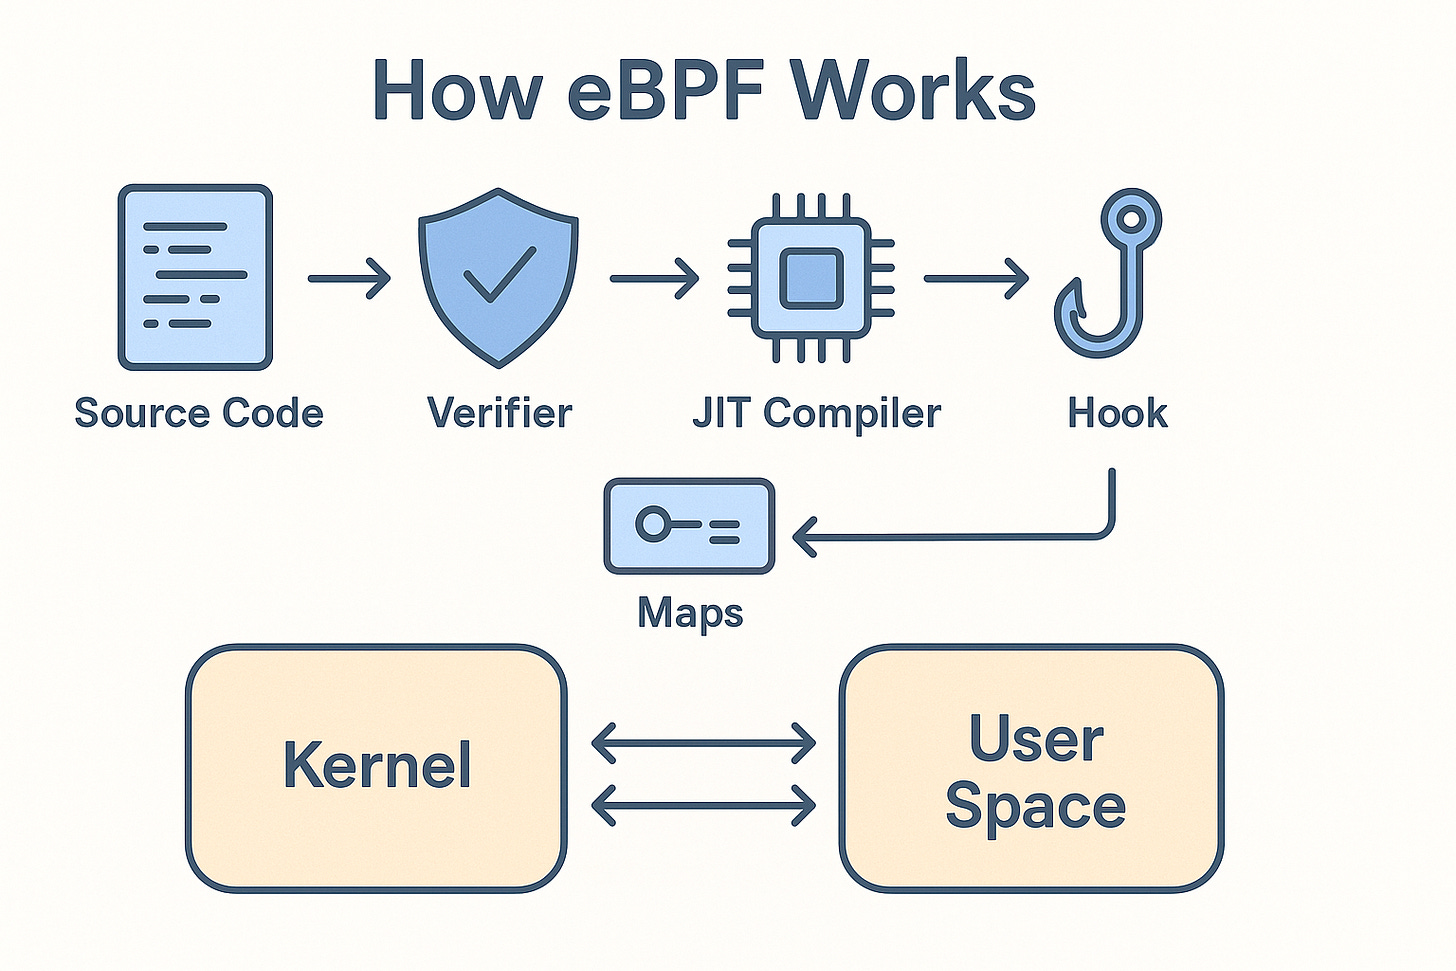
How eBPF Works - Julian Foster

NatiSand: Native Code Sandboxing for JavaScript Runtimes
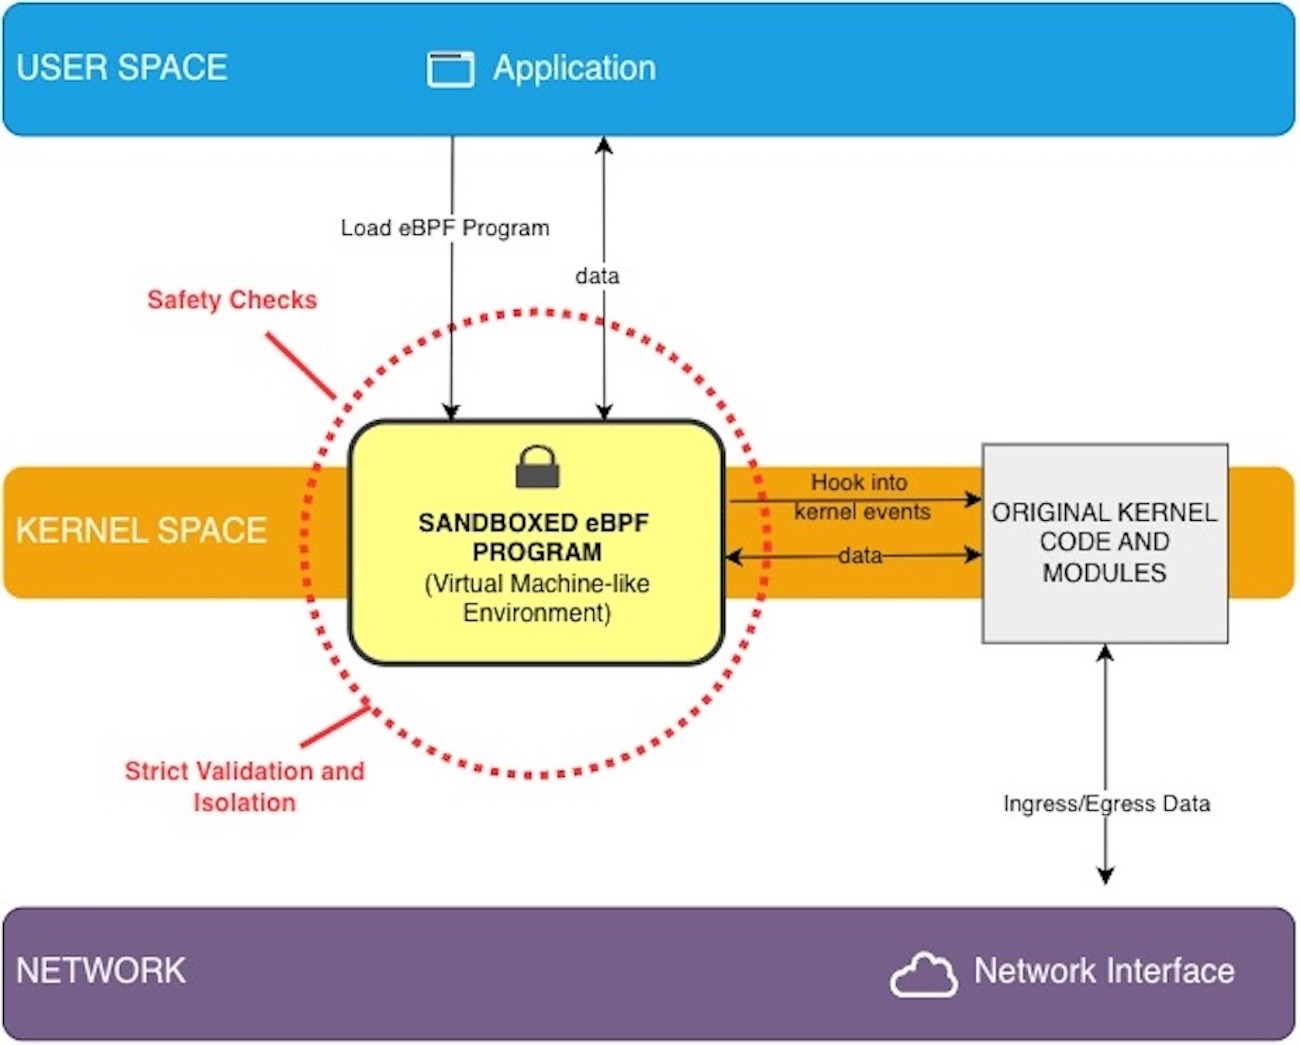
How eBPF Supercharges Kubernetes Networking, Security, and Observability
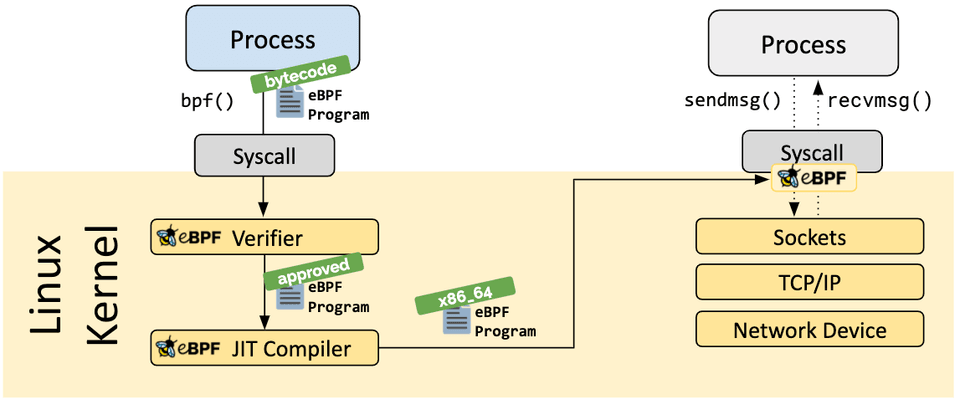
What is eBPF? An Introduction and Deep Dive into the eBPF Technology