
Enhancing Robustness In Federated Learning Against Adversarial Attacks

Enhancing Robustness in Federated Learning against Adversarial Attacks ...
Defense Strategies in Federated Learning Against Adversarial Attacks ...

Enhancing NLP Models for Robustness Against Adversarial Attacks ...

(PDF) Adversarial Attacks and Robustness in Deep Learning Models

Enhancing Robustness in Incremental Learning with Adversarial Training ...

(PDF) On the Robustness of Split Learning Against Adversarial Attacks

Fighting Back Against Attacks in Federated Learning — Scaleout

(PDF) Centered-Ranking learning against Adversarial Attacks in Neural ...

Figure 1 from Mitigating Adversarial Attacks in Federated Learning with ...

Dynamic Label Adversarial Training for Deep Learning Robustness Against ...
Advertisement Space (300x250)
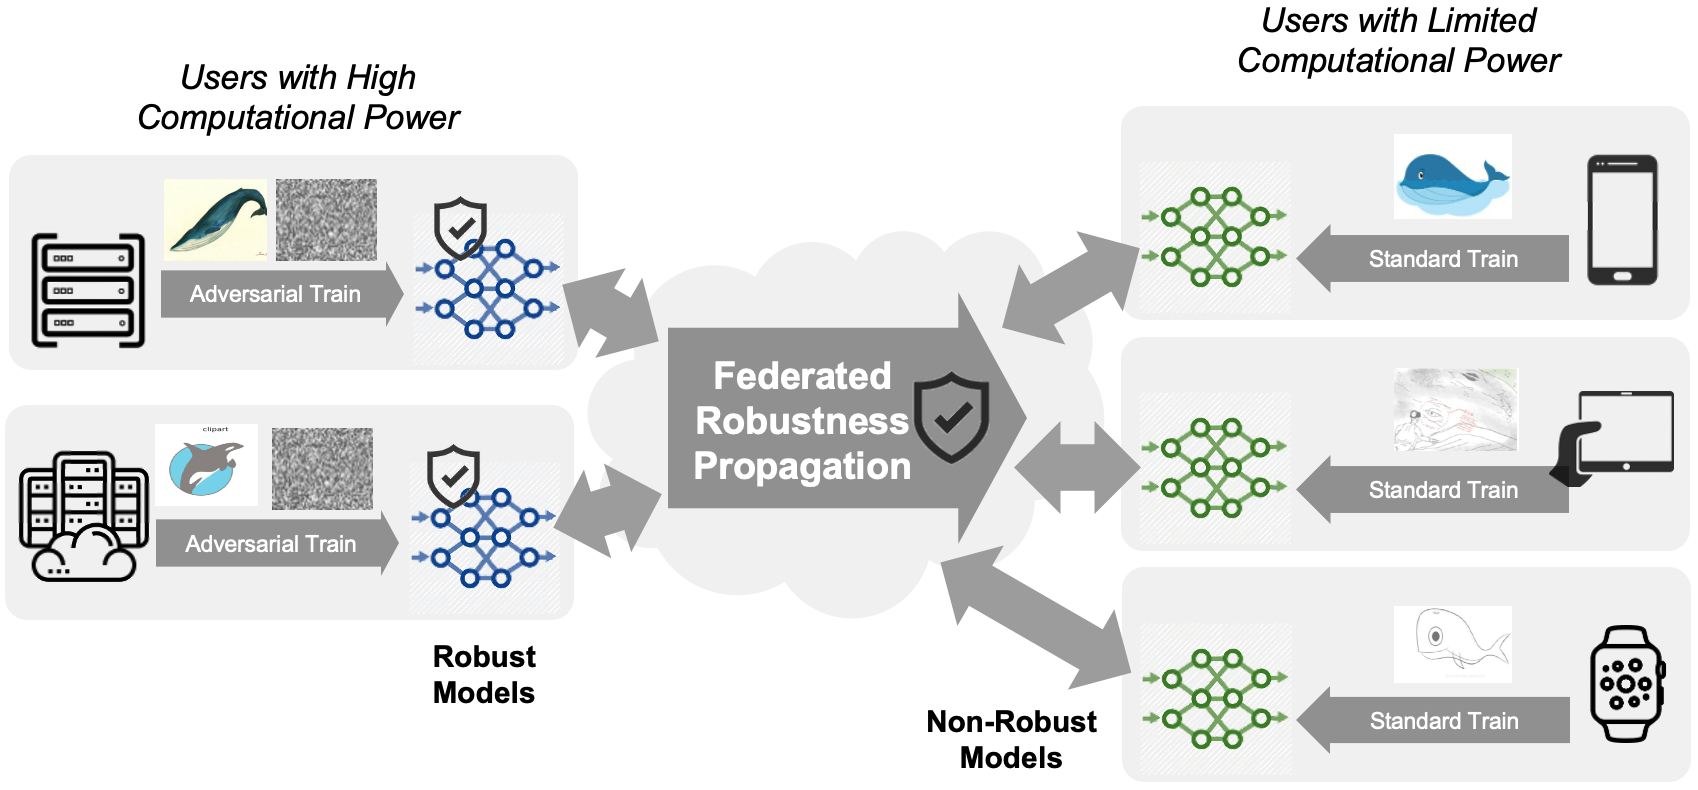
Federated Robustness Propagation: Sharing Adversarial Robustness in ...

Dynamic Label Adversarial Training for Deep Learning Robustness Against ...
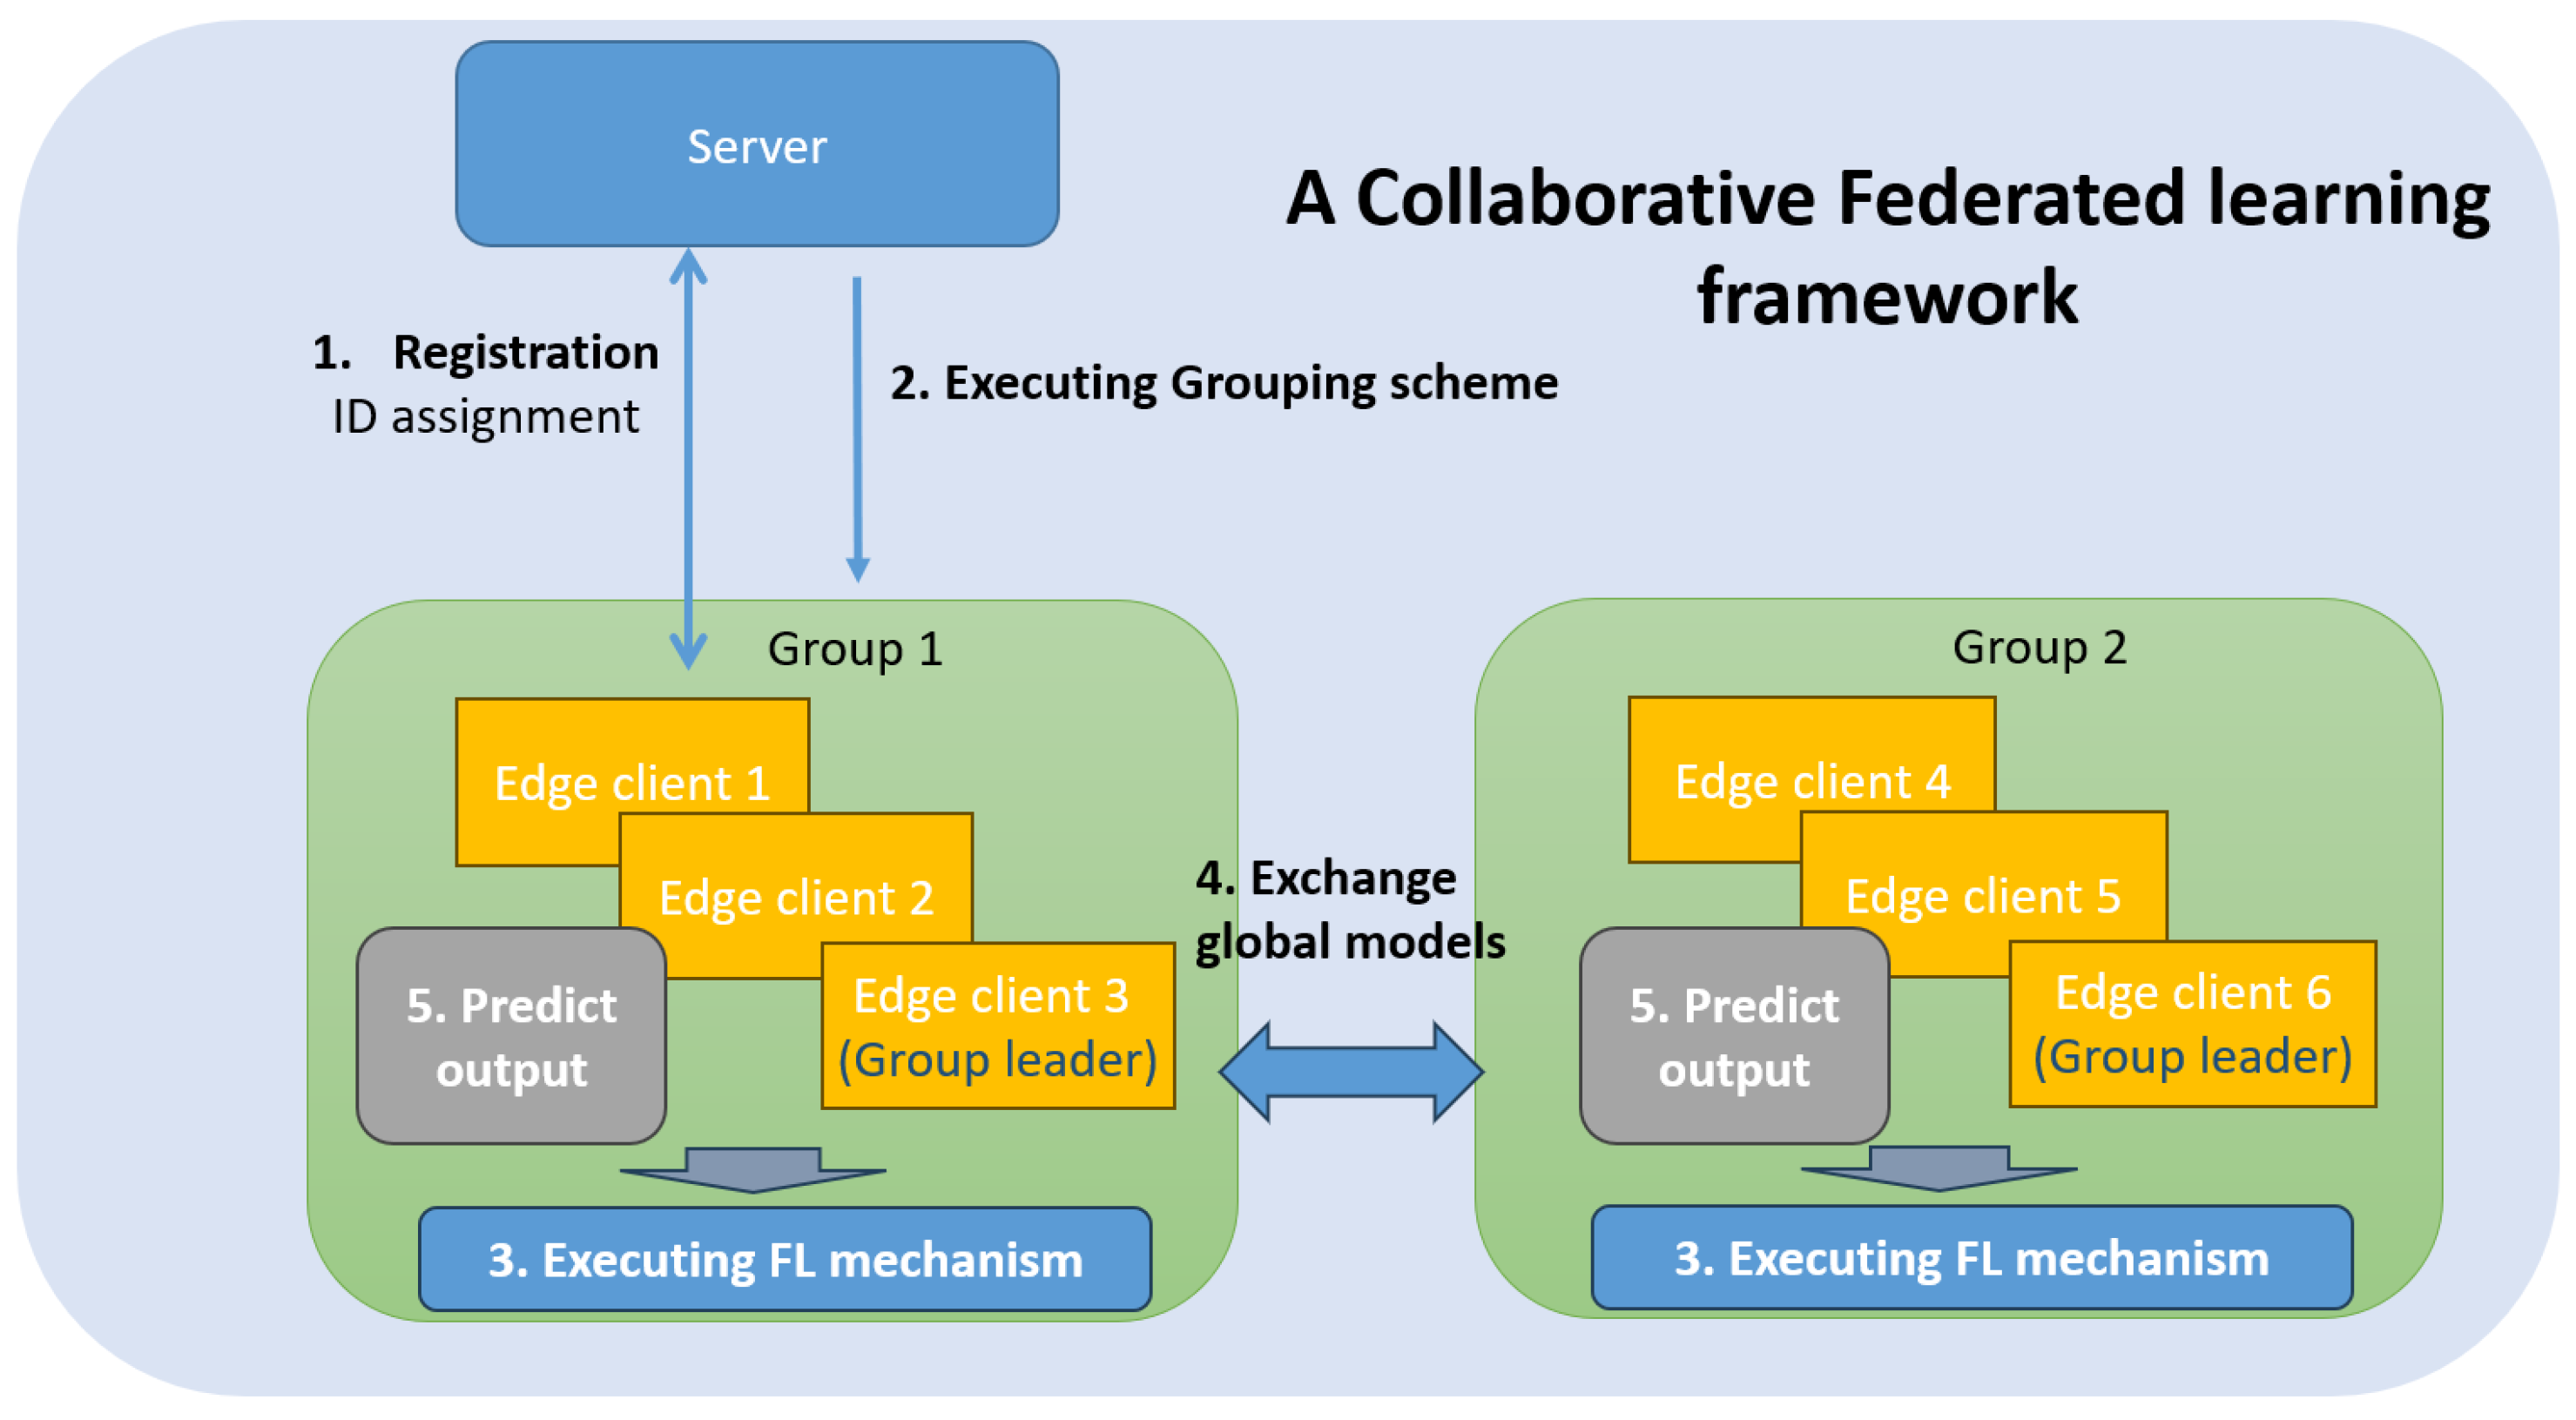
Enhancing Robustness within the Collaborative Federated Learning ...
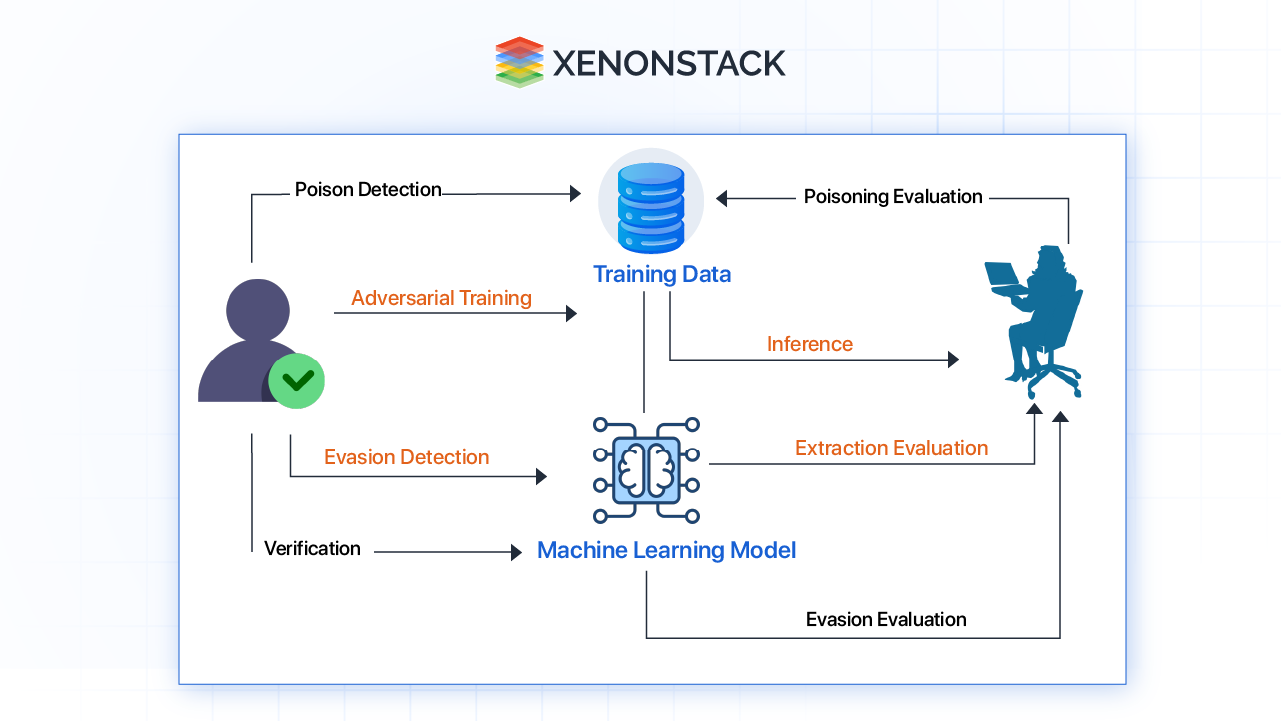
Robustness and Adversarial Attacks in Computer Vision

Figure 2 from Enhancing Adversarial Robustness for Deep Metric Learning ...

Robust Graph Learning Against Adversarial Evasion Attacks via Prior ...

(PDF) Enhancing Model Robustness and Accuracy Against Adversarial ...

(PDF) FedCC: Robust Federated Learning against Model Poisoning Attacks

Attacks on the federated learning process [32] pronounced in

(PDF) Adversarial Attacks in Federated Learning: Privacy Challenges and ...
Advertisement Space (336x280)

(PDF) Delving into the Adversarial Robustness of Federated Learning
Inference attacks against federated learning (passive adversary) by ...

Privacy and Robustness in Federated Learning: Attacks and Defenses ...

FedCC: Robust Federated Learning against Model Poisoning Attacks

Blockchain-Based Federated Learning Against End-Point Adversarial Data ...

A Federated Learning Framework against Data Poisoning Attacks on the ...

(PDF) Adversarial Robustness and Defense Mechanisms in Machine Learning

(PDF) Robustness and Security in Deep Learning: Adversarial Attacks and ...

Robustness against adversarial attack for FGSM attacks for the baseline ...

Shielding Federated Learning Systems against Inference Attacks with ARM ...
Advertisement Space (336x280)

AdvPurge: A Robust Personalized Federated Learning Framework Against ...

Adversarial Attacks and Defenses in Deep Learning: From a Perspective ...

Figure 3 from Enhancing Model Robustness and Accuracy Against ...

(PDF) Federated Adversarial Learning for Scalable and Robust Zero-Day ...

(PDF) A Framework for Robust Deep Learning Models Against Adversarial ...

(PDF) Studying the Robustness of Anti-Adversarial Federated Learning ...