
Exploring The Reverse Command In Splunk Lognalytics
Exploring The Reverse Command In Splunk | Lognalytics
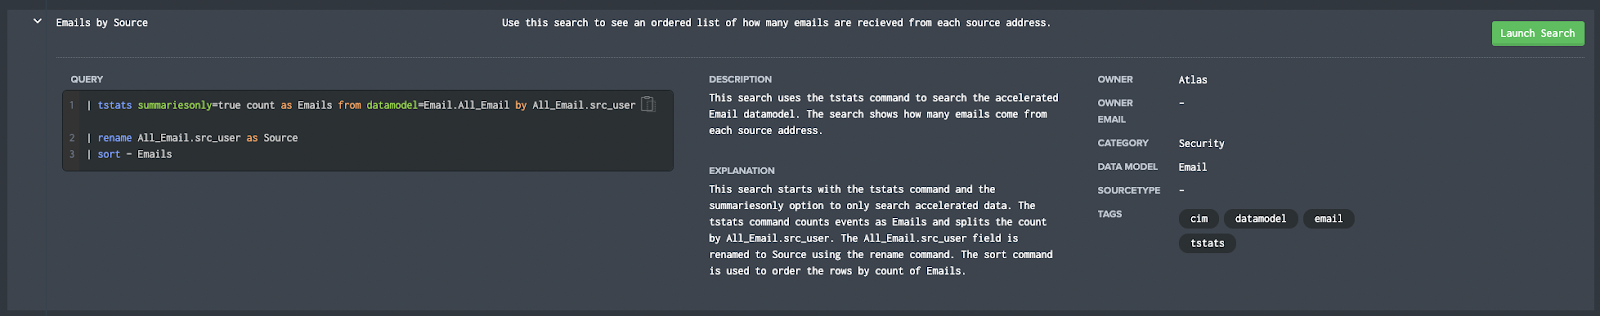
Step Up Your Search: Exploring the Splunk tstats Command

Solved: Reverse the order of values for a multivalue field - Splunk ...
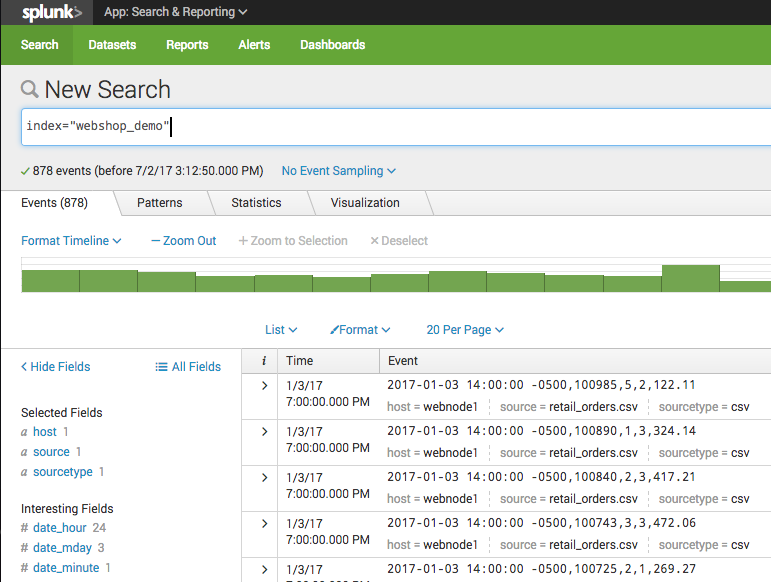
Splunk Spotlight - The Lookup Command
KHAFAGY | Splunk Exploring SPL

Splunk Search Commands | Overview of Search Commands in Splunk
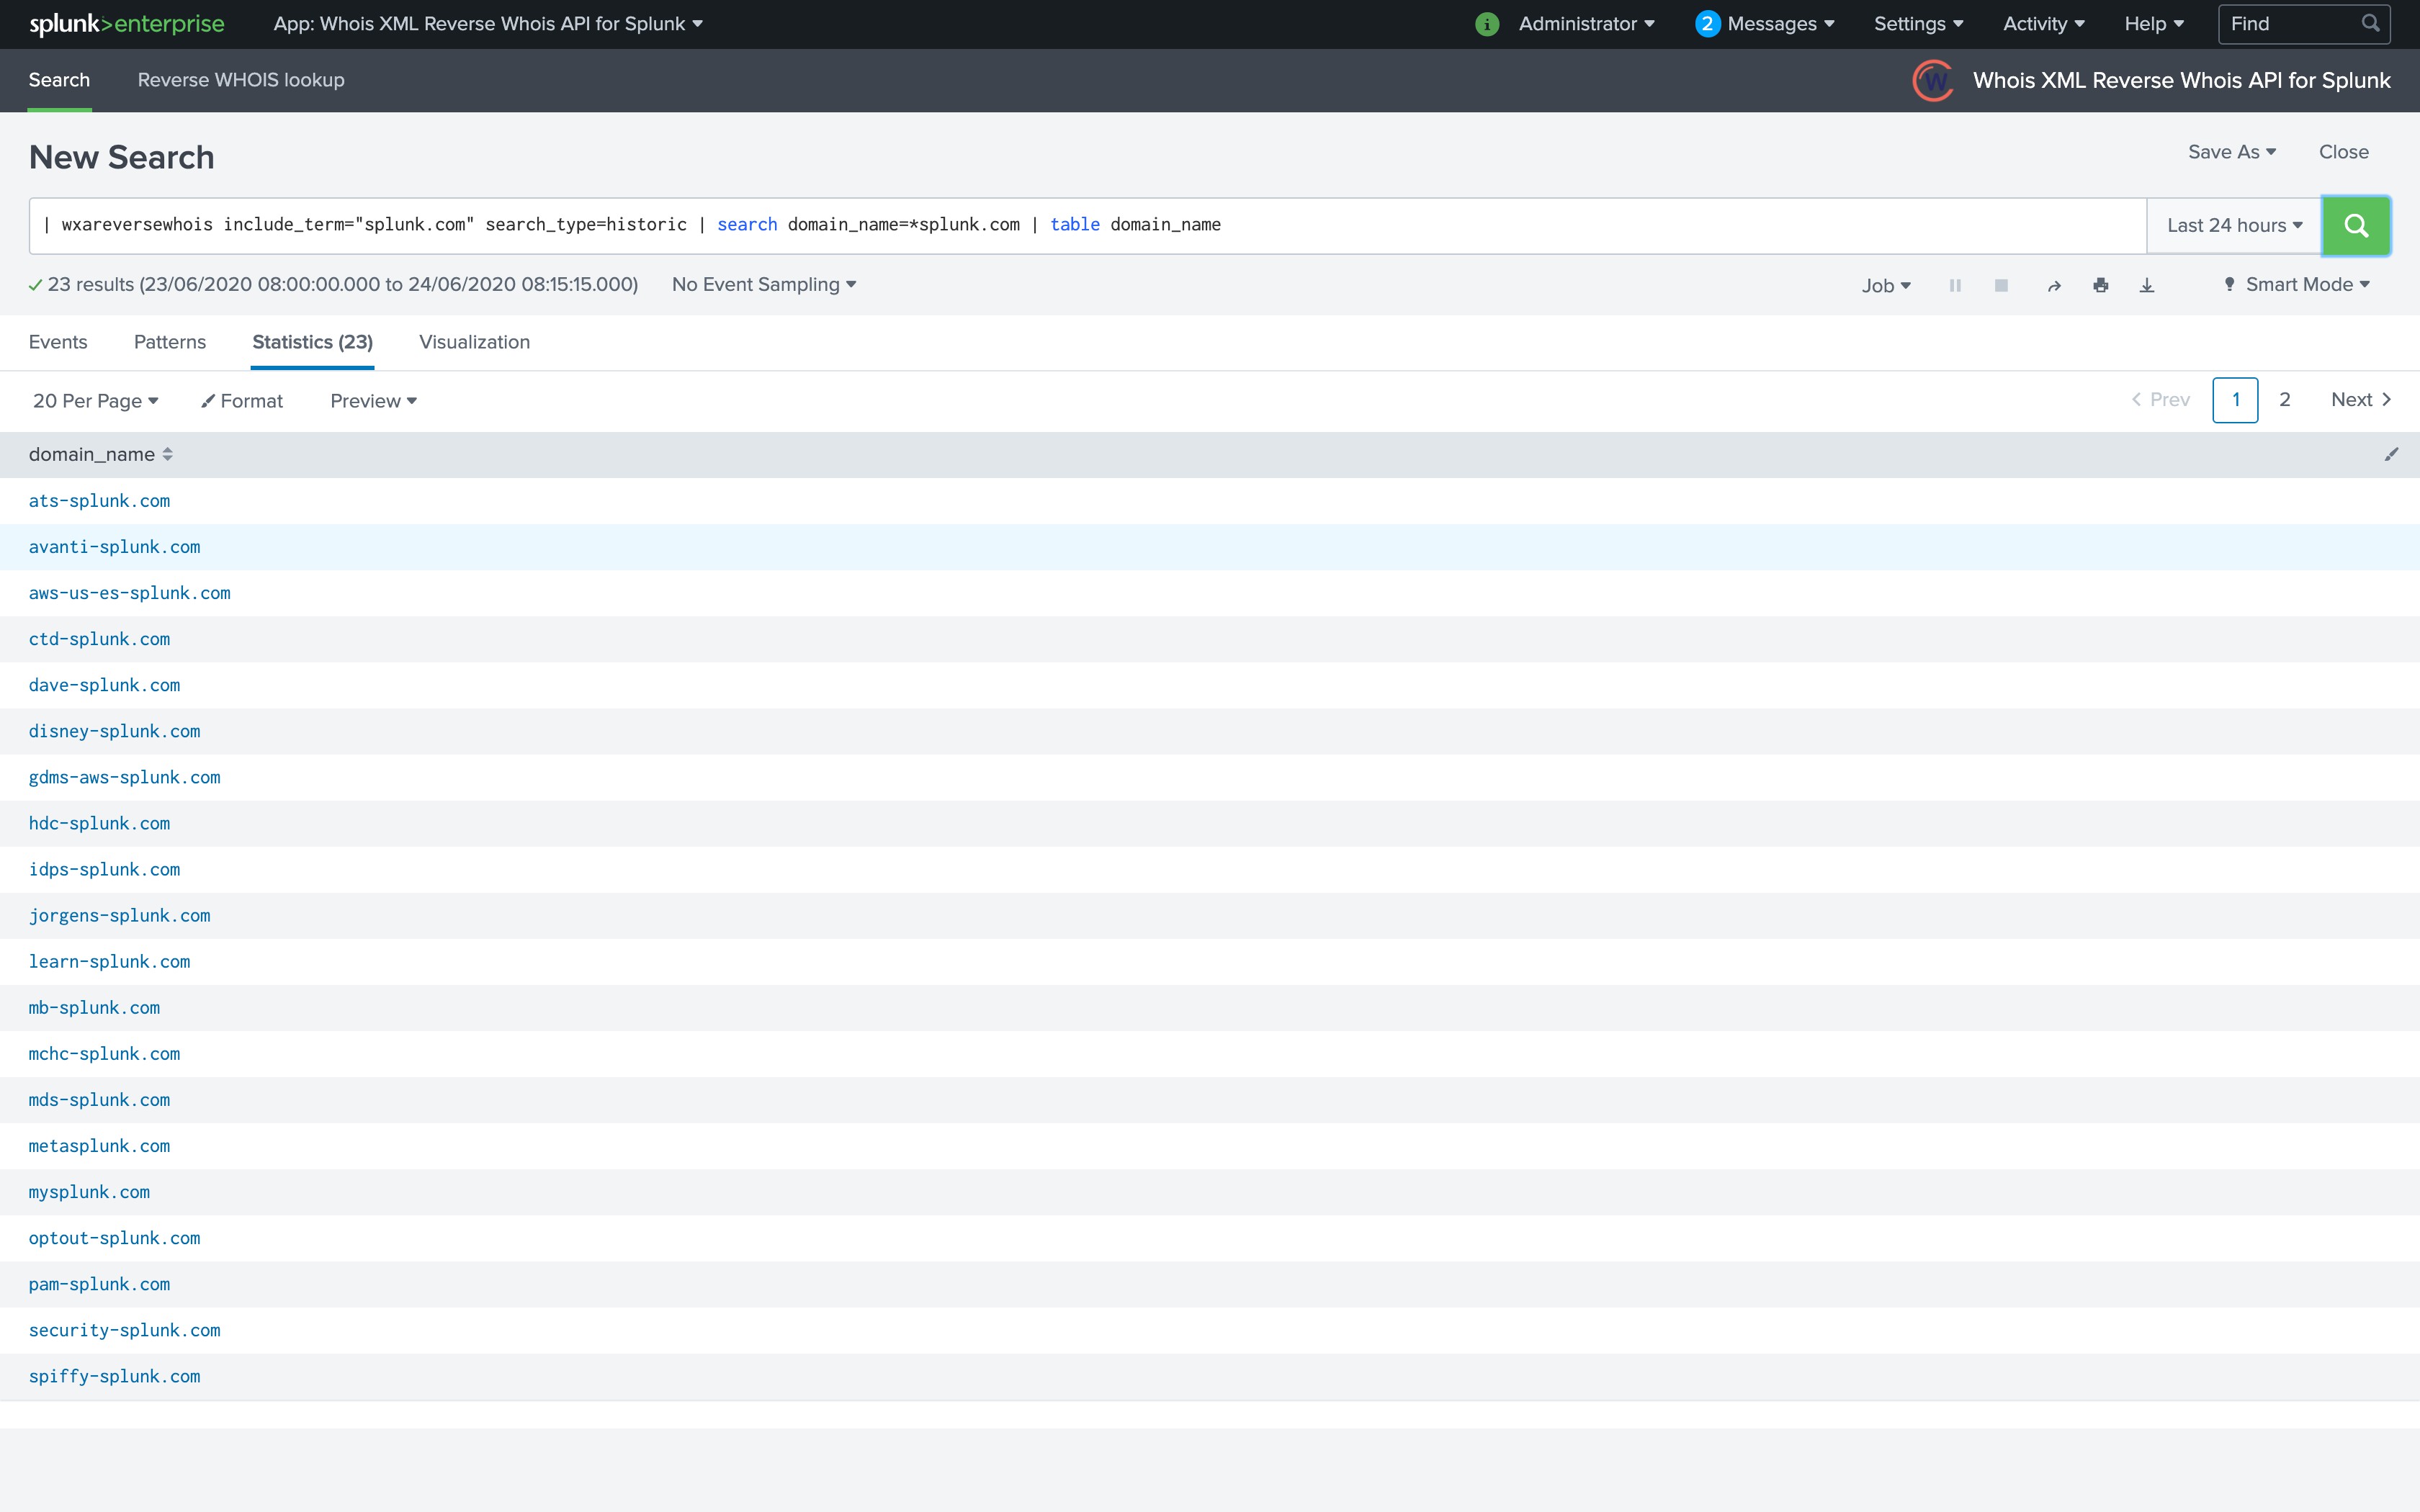
Reverse WHOIS API Splunk application tutorial | Platforms | Reverse ...
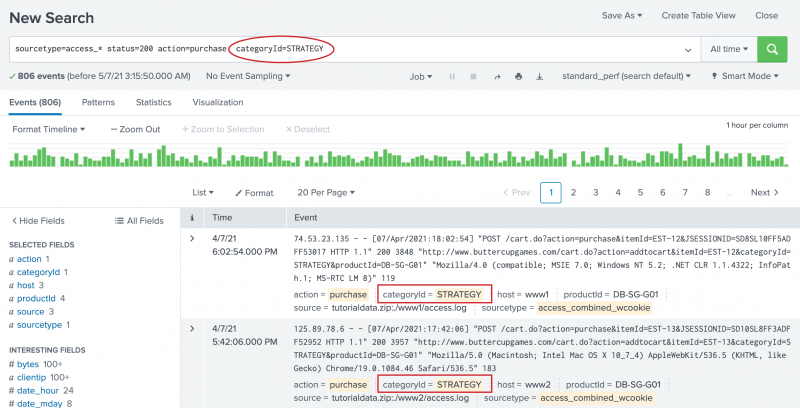
Use the search language - Splunk Documentation
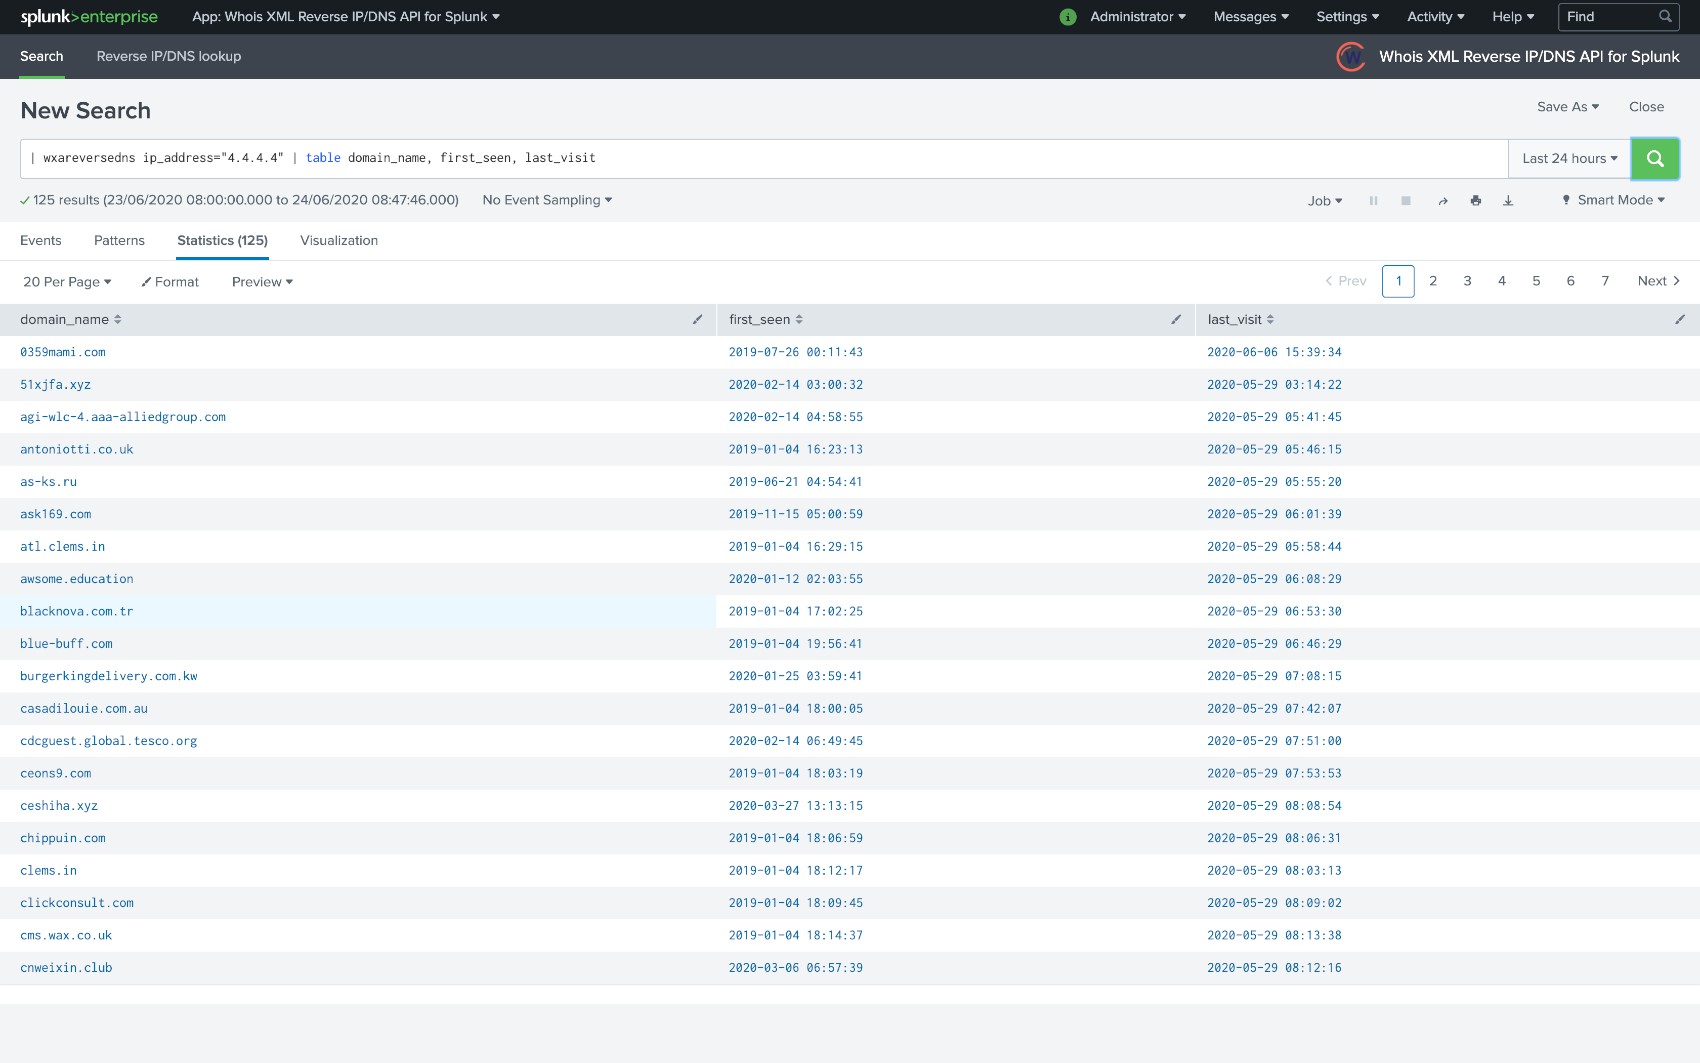
Reverse IP/DNS API Splunk application tutorial | Platforms | Reverse IP ...
Splunk Ordering with Sort and Reverse Commands - Kinney Group
Advertisement Space (300x250)

Reverse WHOIS API Splunk application tutorial | Platforms | Reverse ...
Reverse WHOIS API Splunk application tutorial | Platforms | Reverse ...

Changing Splunk Web Port From 8000 To 443 | Lognalytics

How to Analyze Logs in Splunk 2025 | Complete Log Analytics Tutorial ...
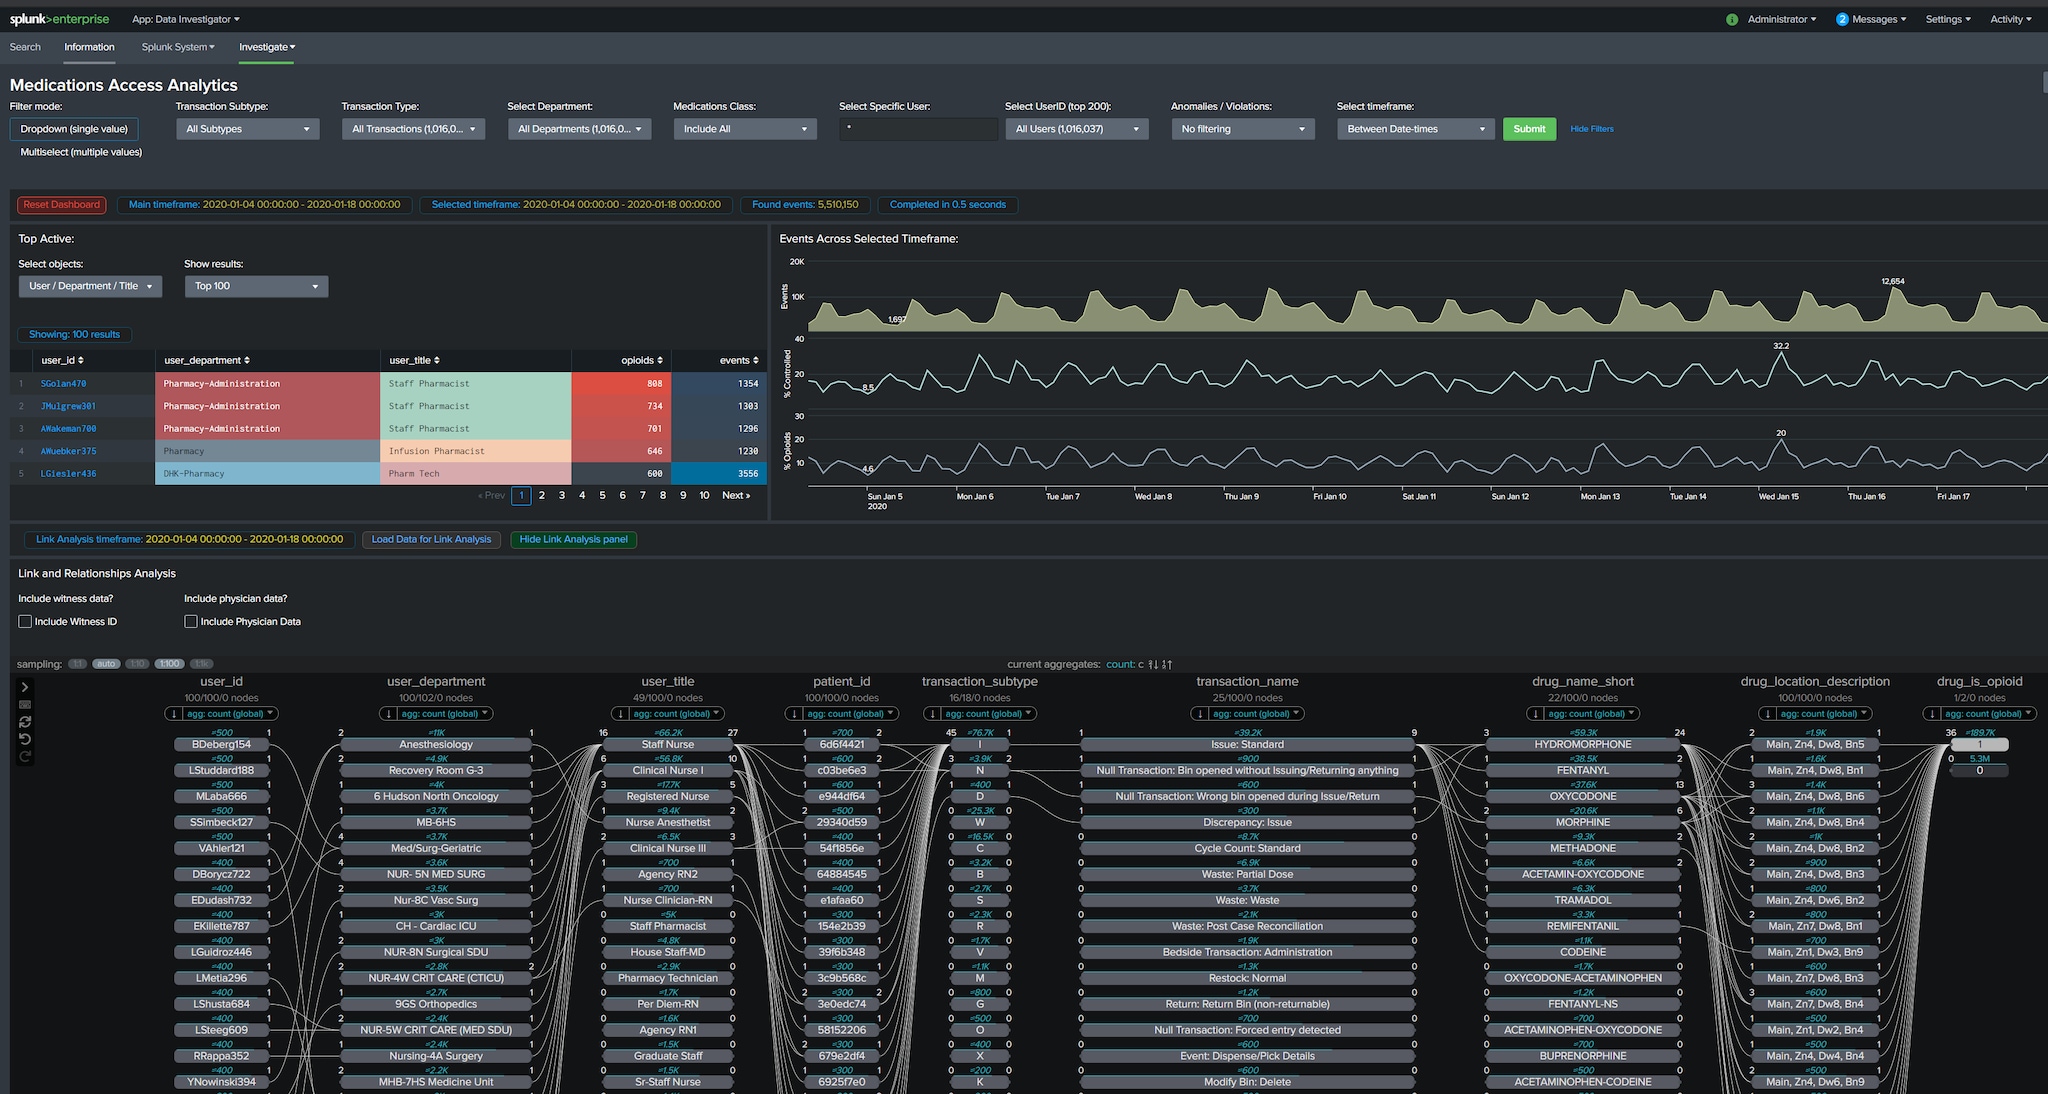
Using the Lookup Command for Threat Hunting (Lookup Before You Go-Go ...

Answers for the TryHackMe Splunk: Exploring SPL Room – Just another ...
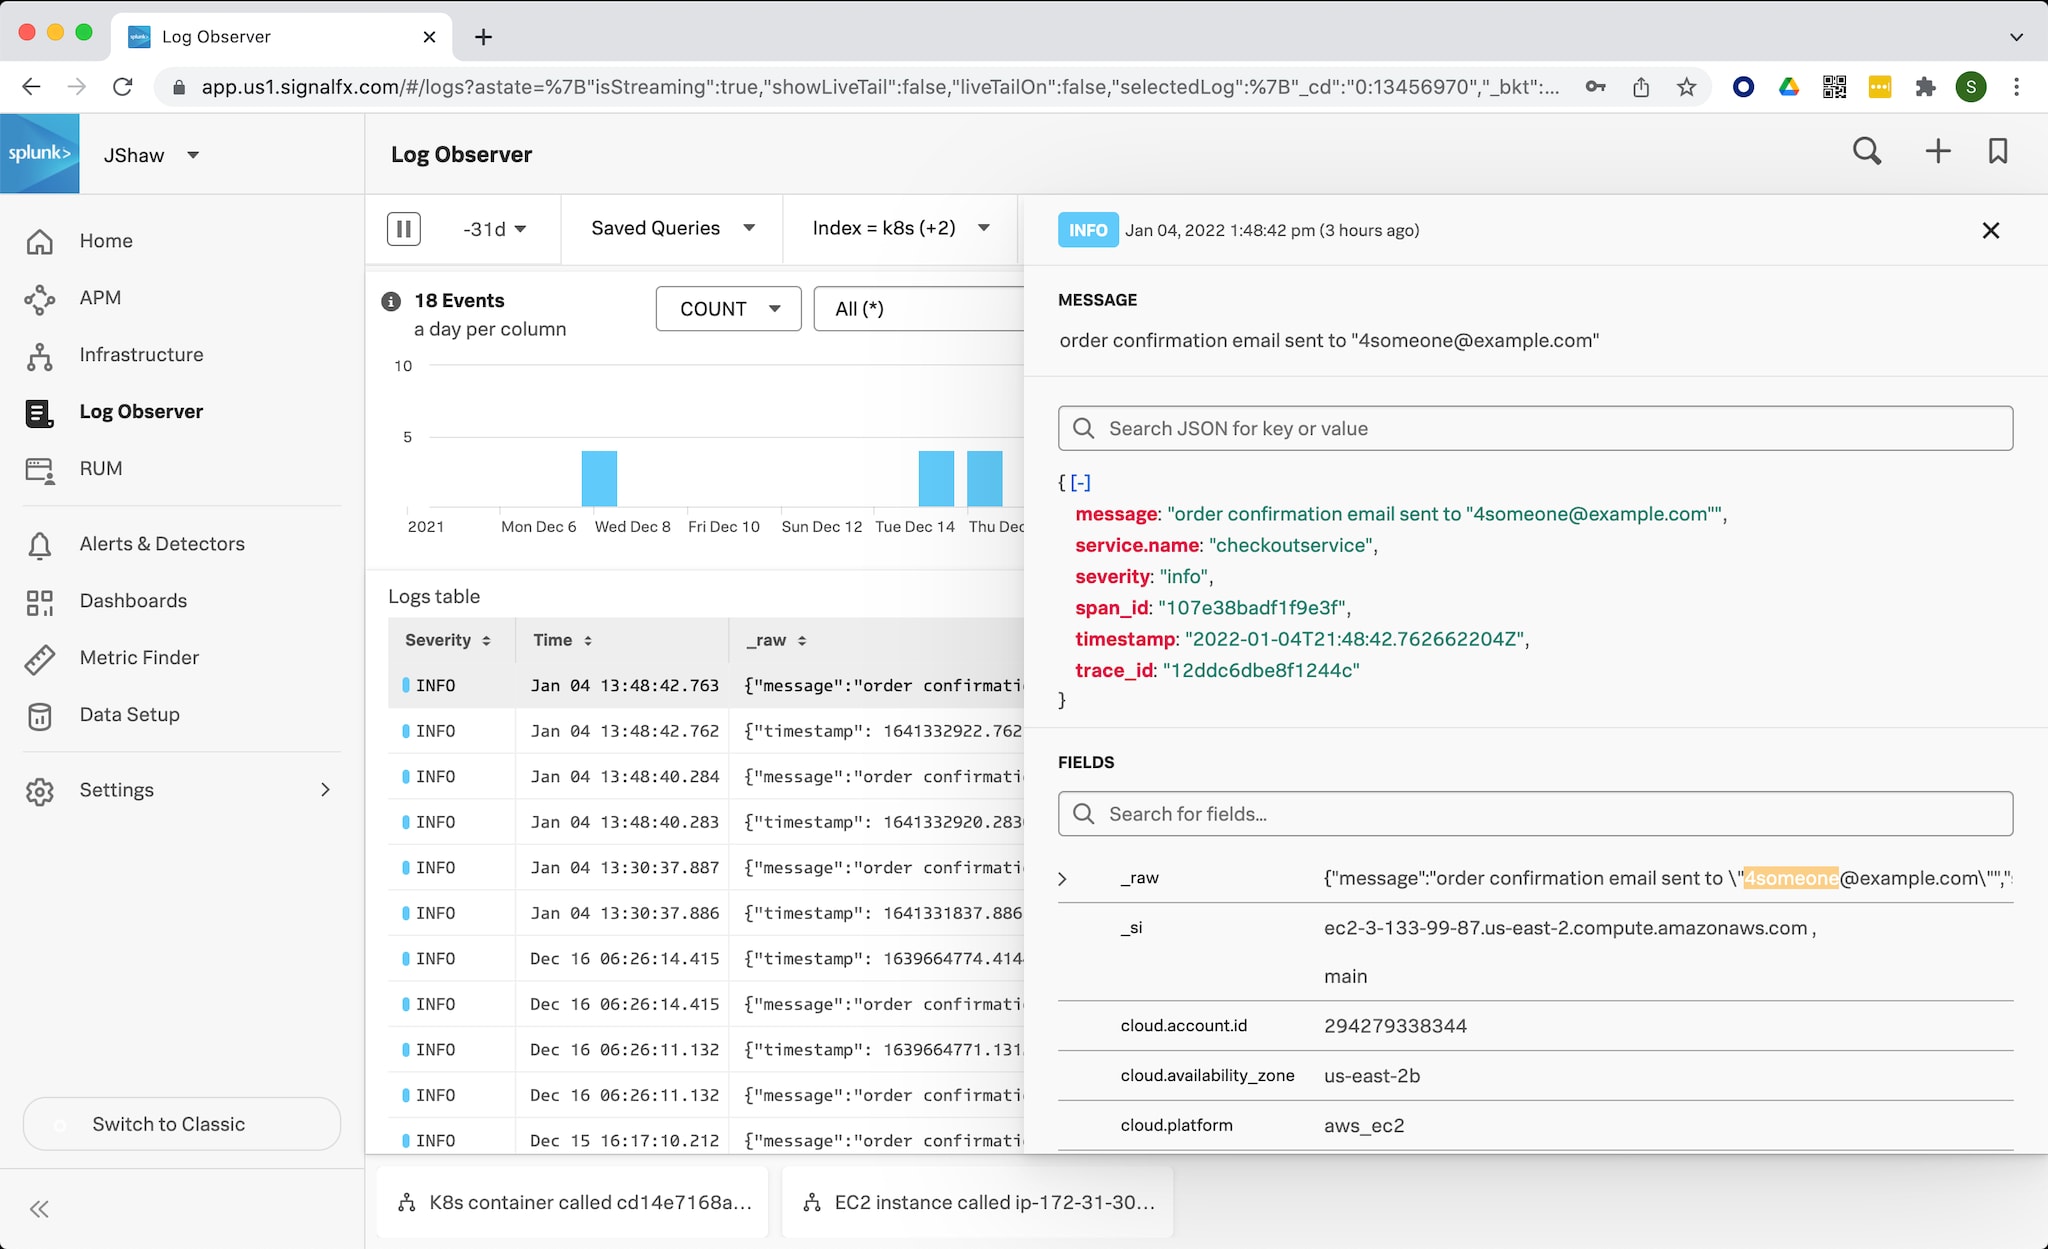
Explore Splunk Cloud Data in Splunk Observability with Log Observer ...
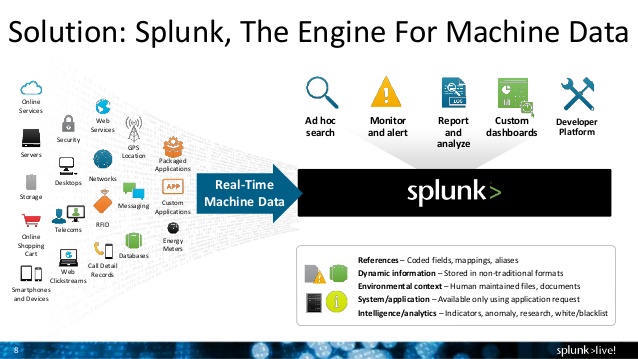
Why Should You Use Splunk for Log Analysis ? | TO THE NEW Blog

NEW! Log Views in Splunk Observability Dashboards ... - Splunk Community
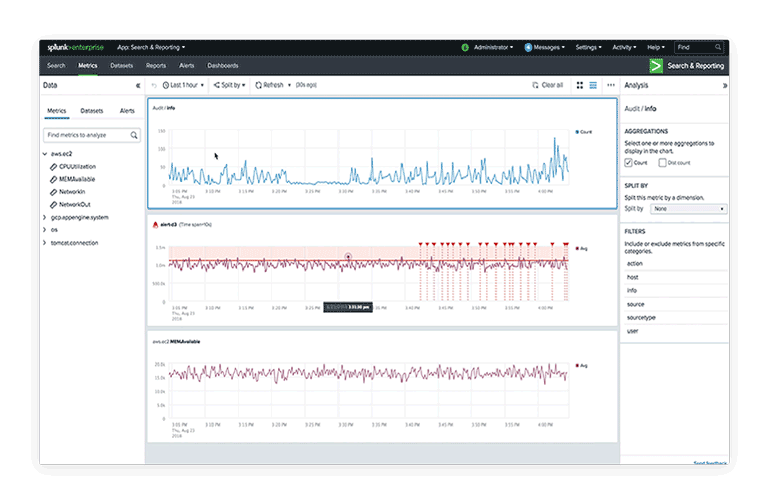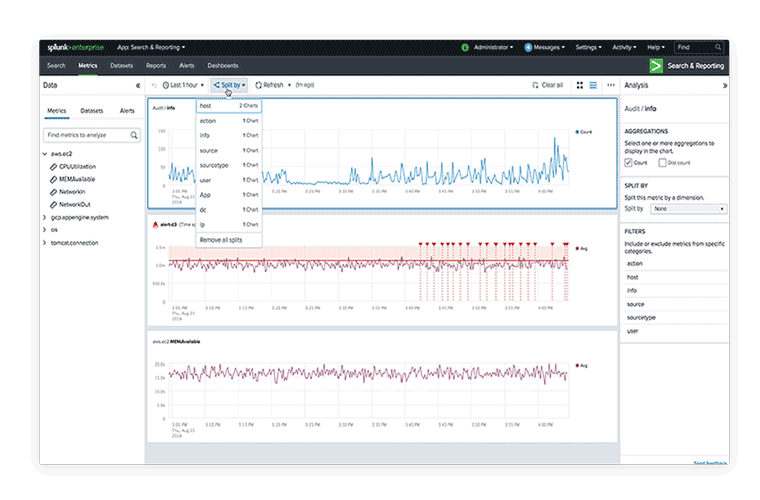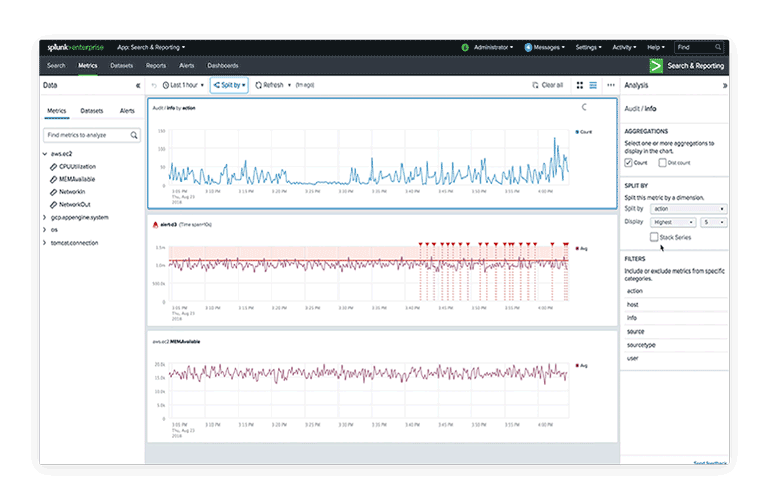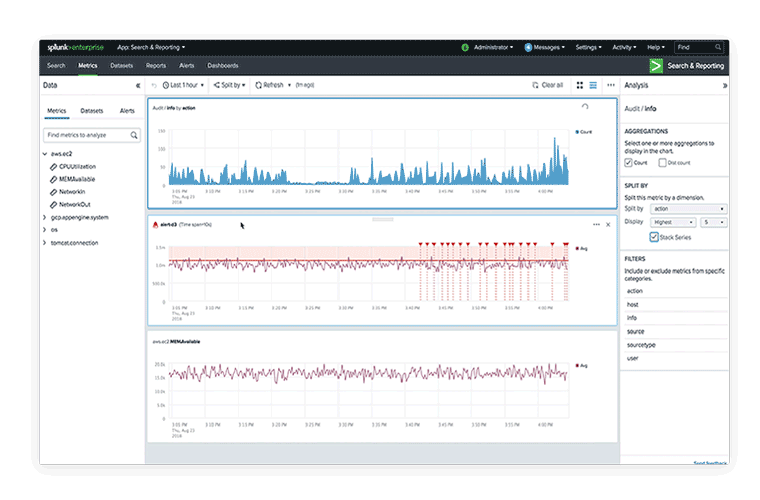
What Is Splunk? The Complete Overview of What Splunk Does | Splunk
Advertisement Space (336x280)
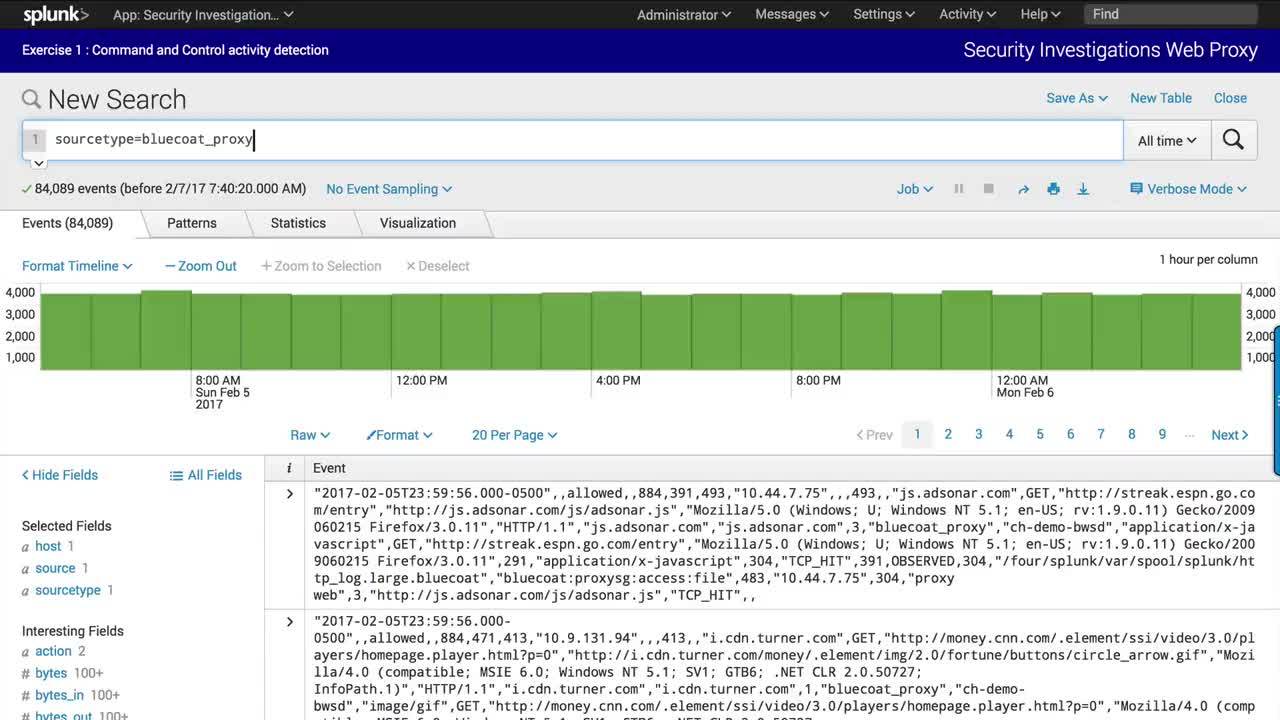
Splunk for Security Investigation: Command and Control Analysis | Splunk

Splunk | Command | Verkada Help
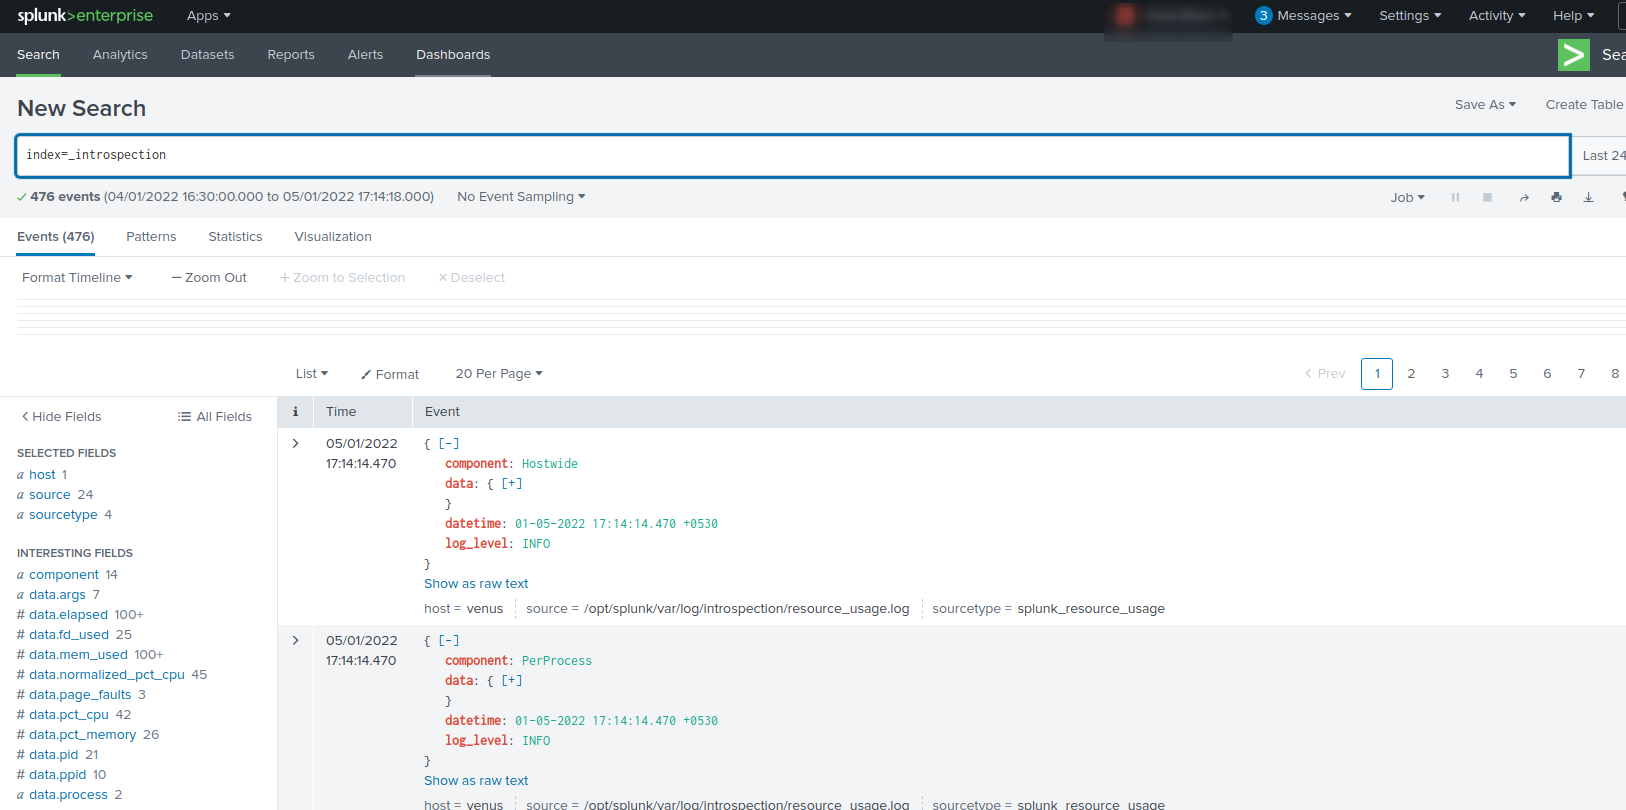
How to Fetch Logs in Your Splunk App [2022]
Splunk Ordering with Sort and Reverse Commands - Kinney Group
Splunk Ordering with Sort and Reverse Commands - Kinney Group

Splunk Search Command Cheatsheet

Changing Splunk Web Port From 8000 To 443 | Lognalytics

Syslog-ng and HEC: Scalable Aggregated Data Collection in Splunk | Splunk

Splunk in 60 Minutes | Splunk Tutorial For Beginners | Splunk Training ...
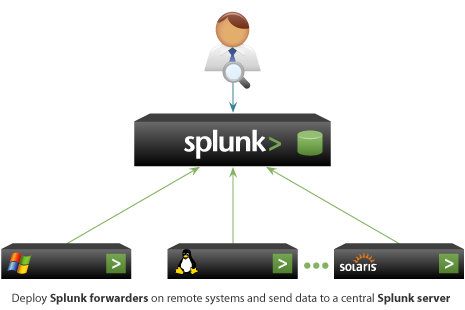
Why Should You Use Splunk for Log Analysis ? | TO THE NEW Blog
Advertisement Space (336x280)

How to Analyze Logs in Splunk - YouTube
Changing Splunk Web Port From 8000 To 443 | Lognalytics

Exploring Splunk Alternatives: Deep Dive into Log Analysis

Splunk - The training questions - The Turtle Dove
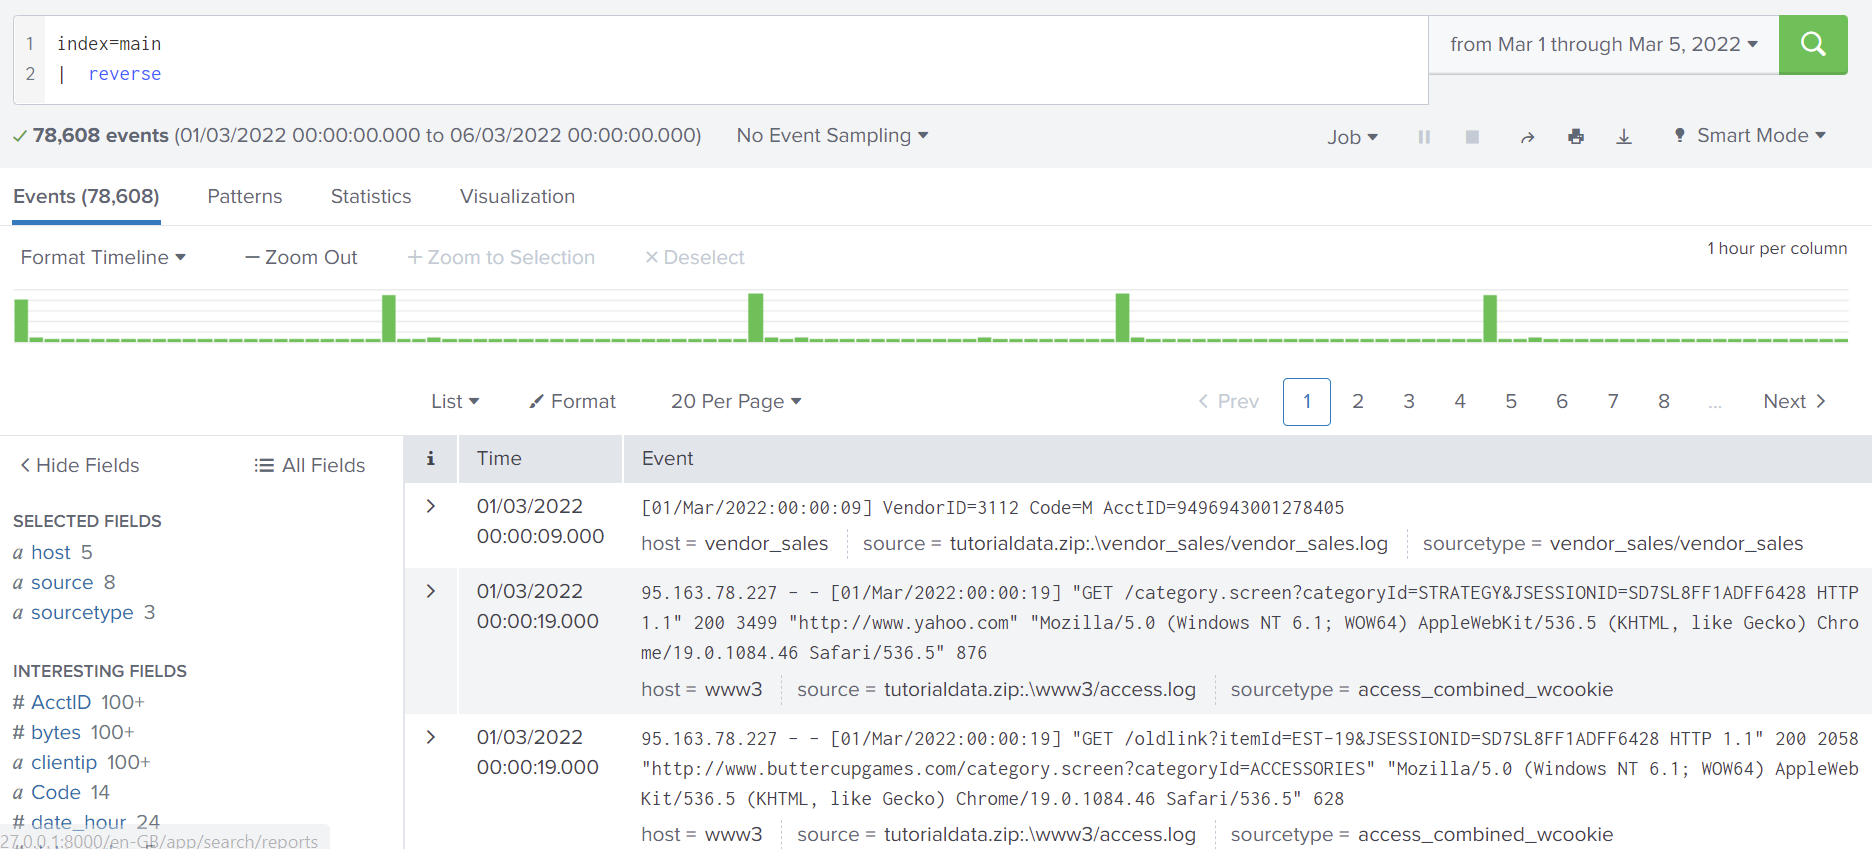
Putting your machine data to use with Splunk
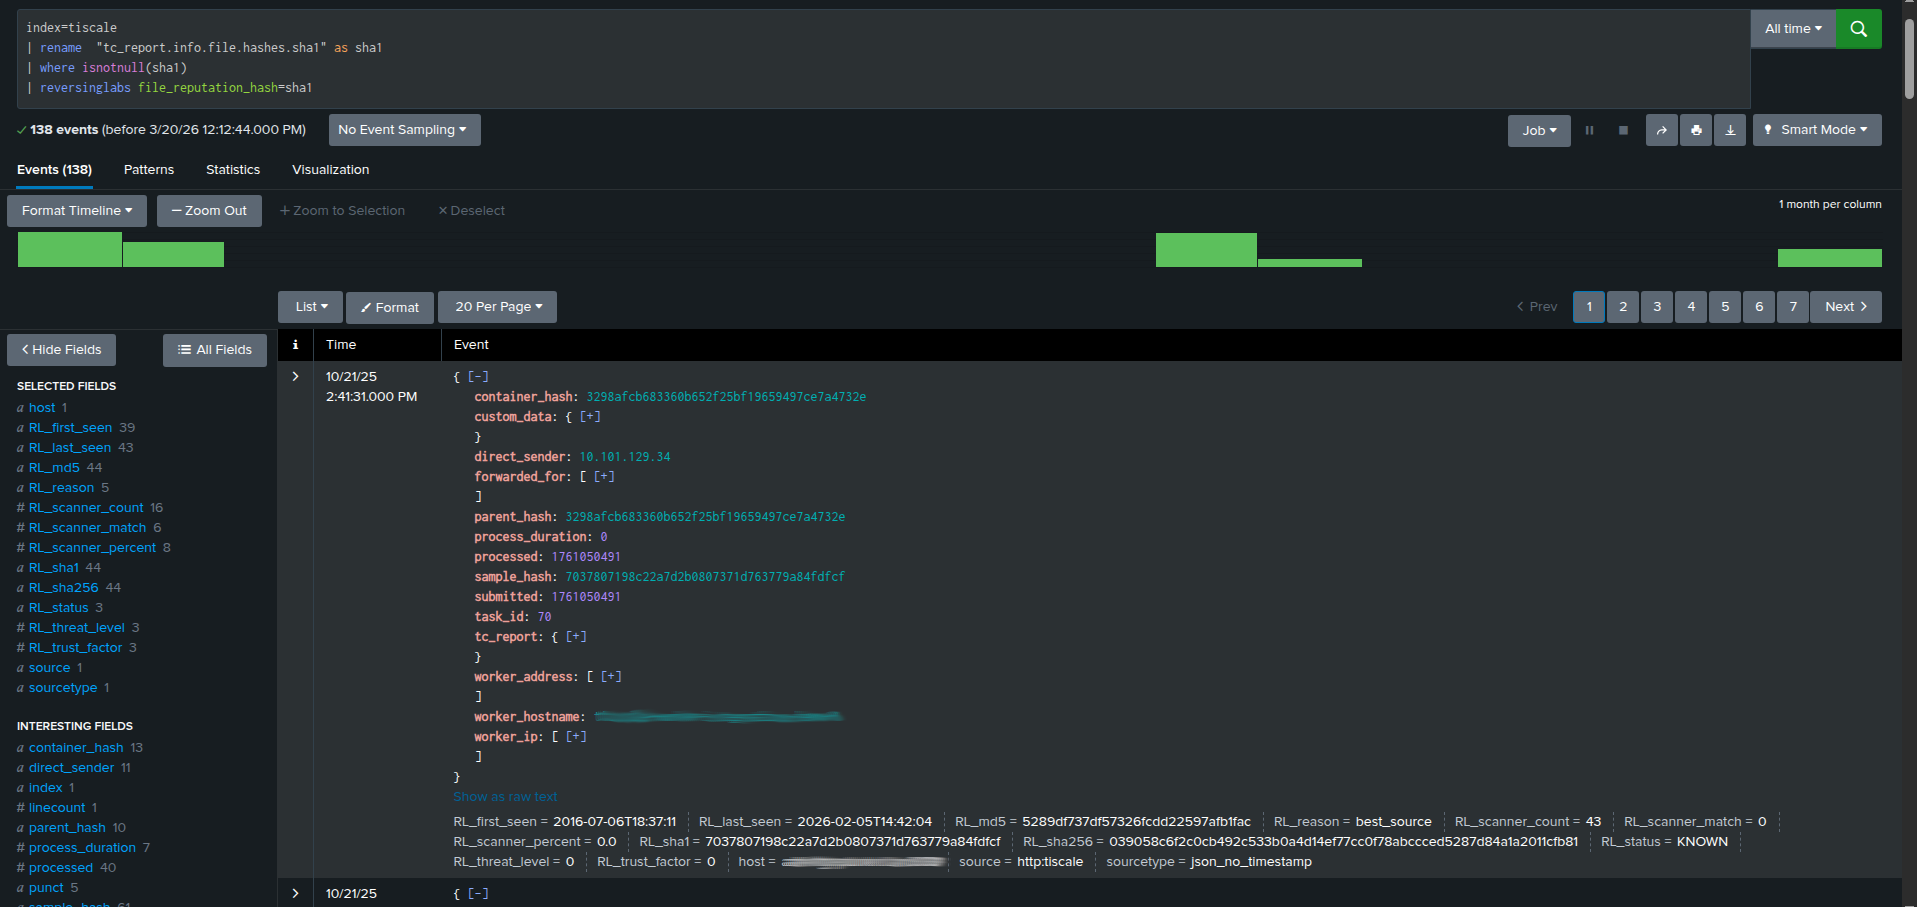
ReversingLabs Search Extension for Splunk Enterprise — Installation and ...