
Extracting Shellcode With Ghidra Youtube

Extracting Shellcode with Ghidra - YouTube

Extracting Shellcode with Ghidra : r/ReverseEngineering
Extracting Ghidra Decompiler Output with Java - HackMD

Unpack Shellcode w/ Ghidra Emulator | Decode XOR Dynamically🔥 - YouTube

Shellcode Loader Analysis and Python3 Scripting in Ghidra - YouTube

Using Ghidra to Statically XOR Obfuscated Shellcode - YouTube

Code Analysis with Ghidra - YouTube

Unpacking Shellcode with Ghidra Emulator : r/ghidra

Unpacking Shellcode with Ghidra Emulator : r/netsec

Unpacking Shellcode with Ghidra Emulator : r/netsec
Advertisement Space (300x250)

Unpack Shellcode w/ Ghidra Emulator | Decode XOR Dynamically🔥 | Jack Ward

Ghidra Basics - Manual Shellcode Analysis and C2 Extraction | Sadia B.

Getting Started with Ghidra: Analyzing Process Hollowing Shellcode from ...
How to Use Ghidra to Analyse Shellcode and Extract Cobalt Strike ...
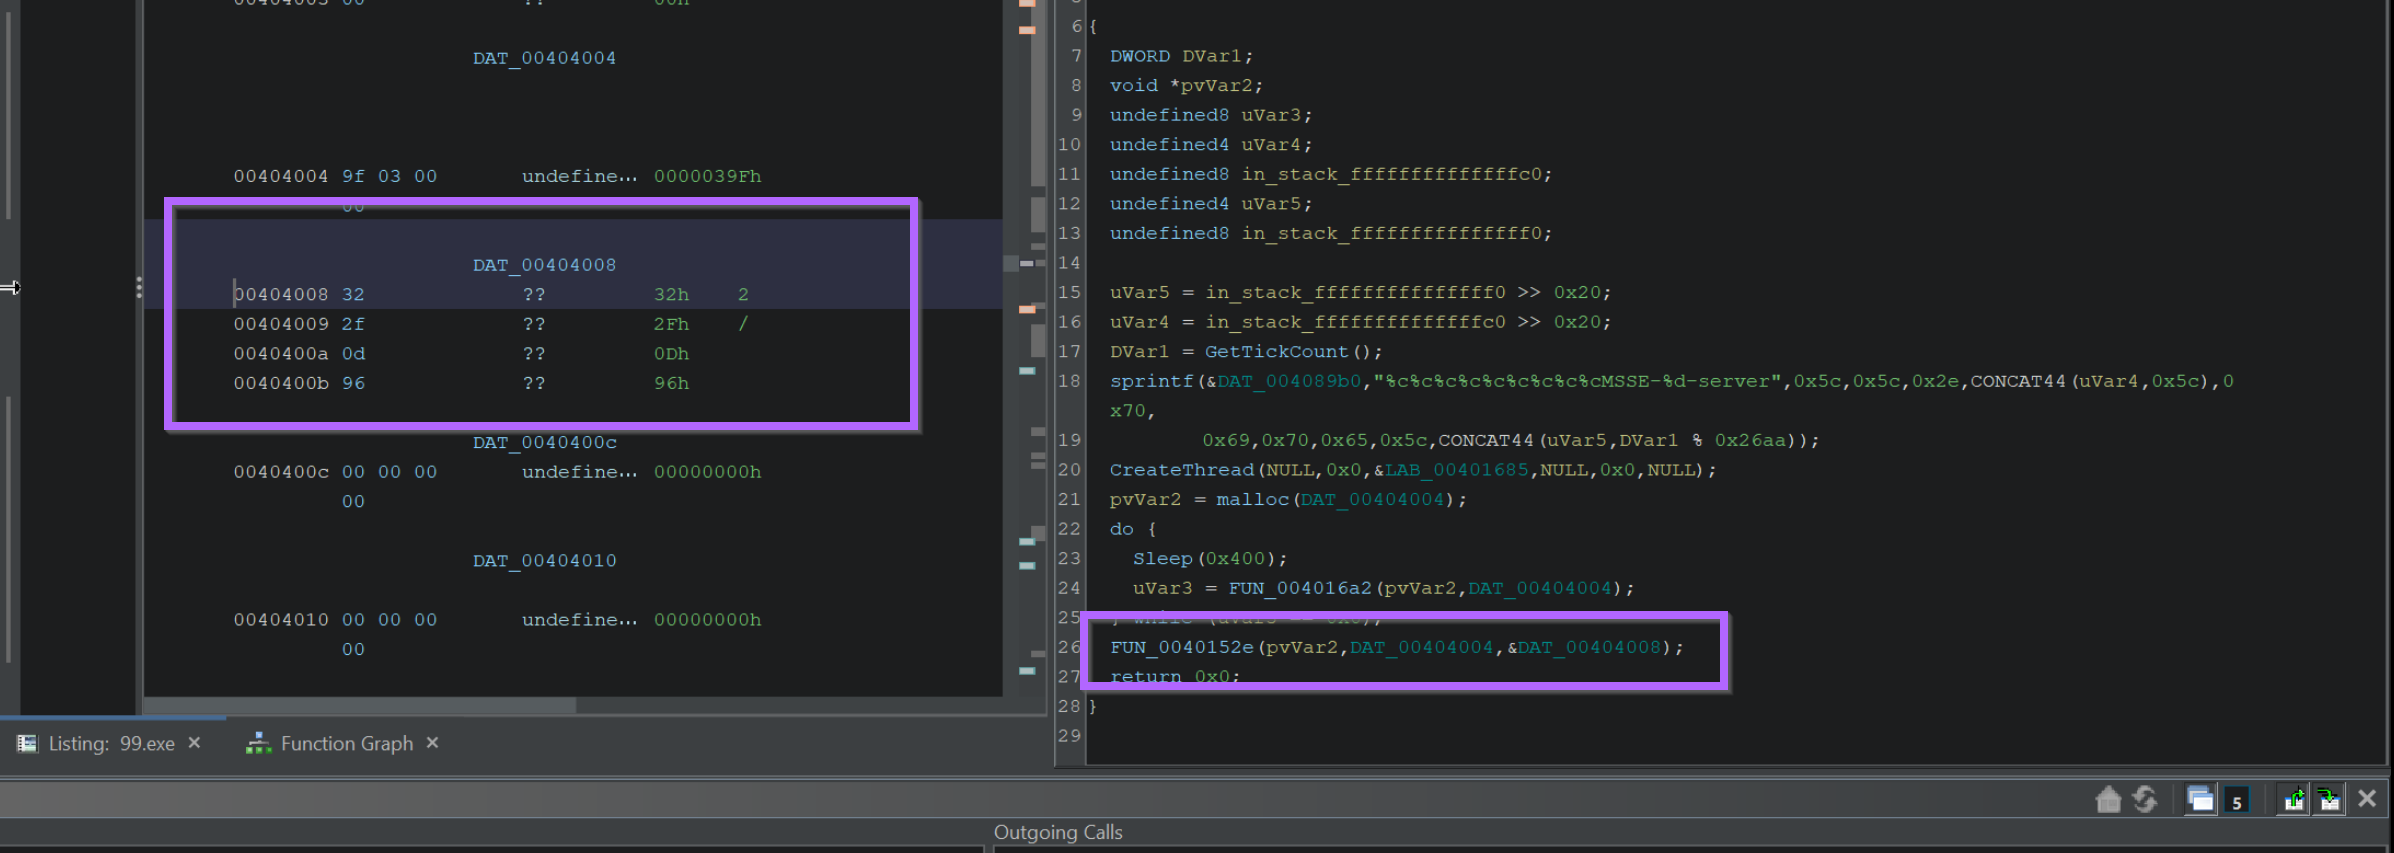
Beginner Ghidra Guide - Manual Shellcode Decryption
GHIDRA Tutorial — Learn How to Use Reverse Engineering Tool - YouTube
How to patch using GHIDRA - YouTube
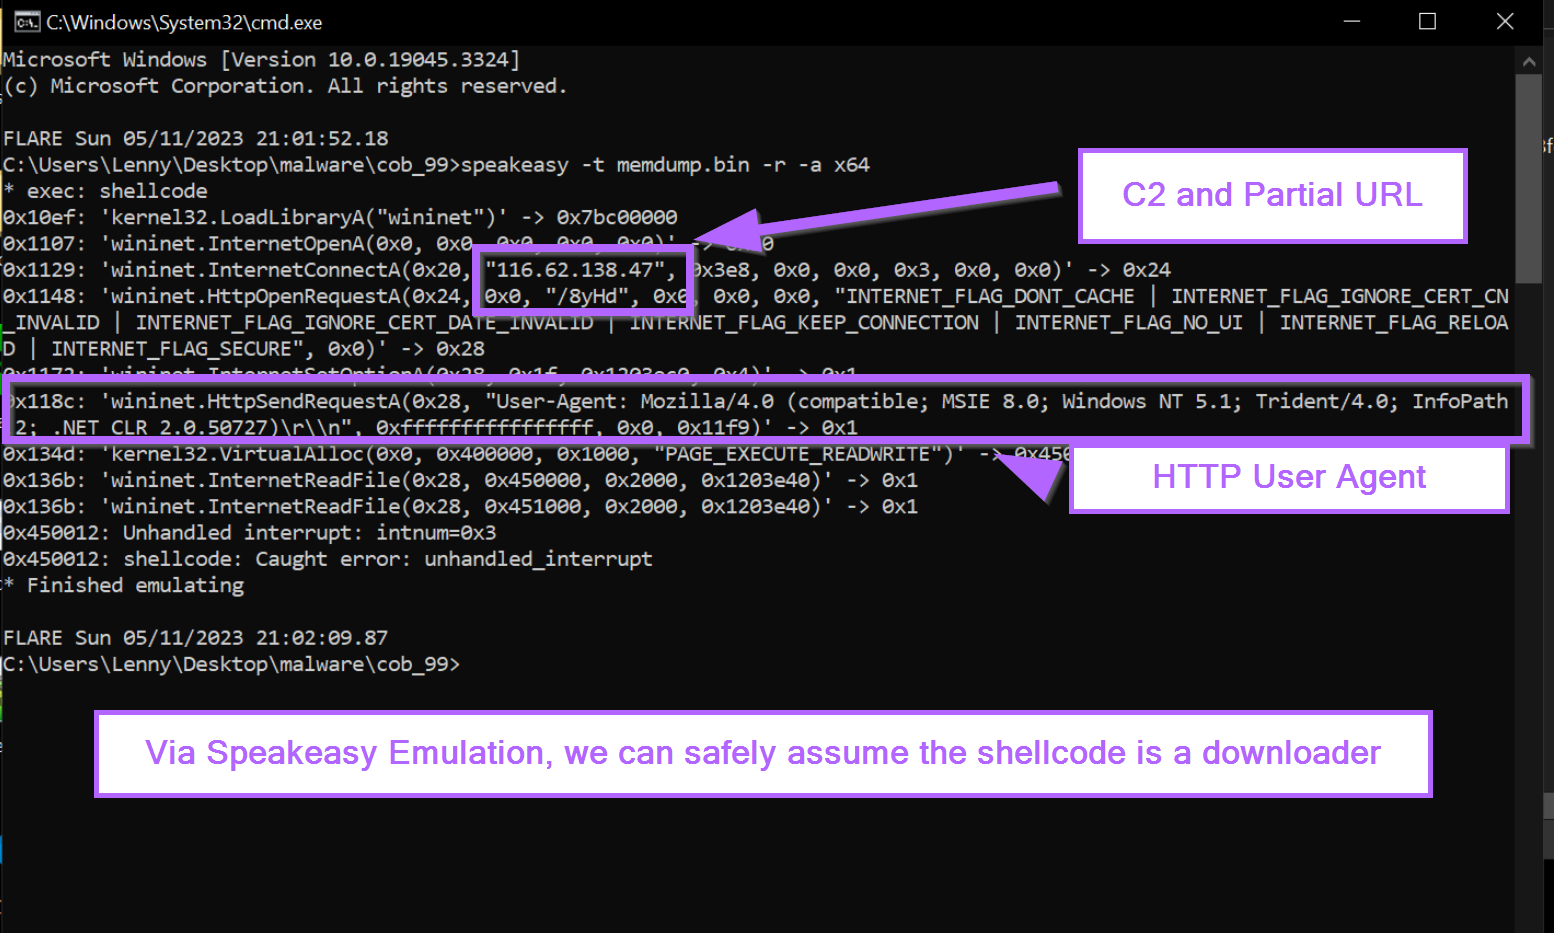
Malware Unpacking With Hardware Breakpoints - Cobalt Strike Shellcode ...
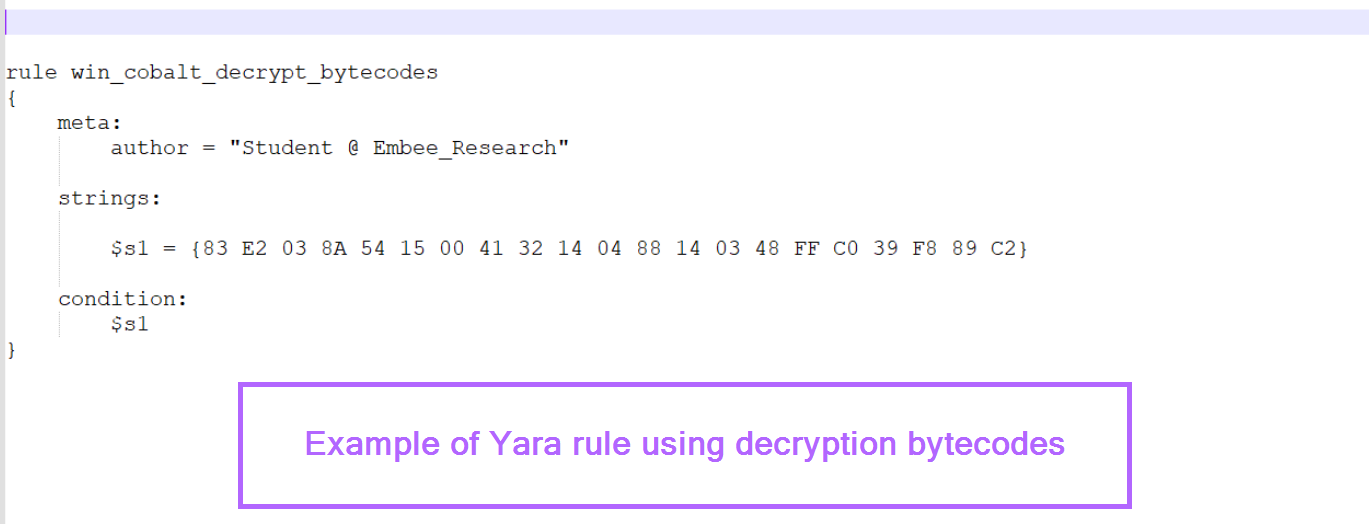
Beginner Ghidra Guide - Manual Shellcode Decryption
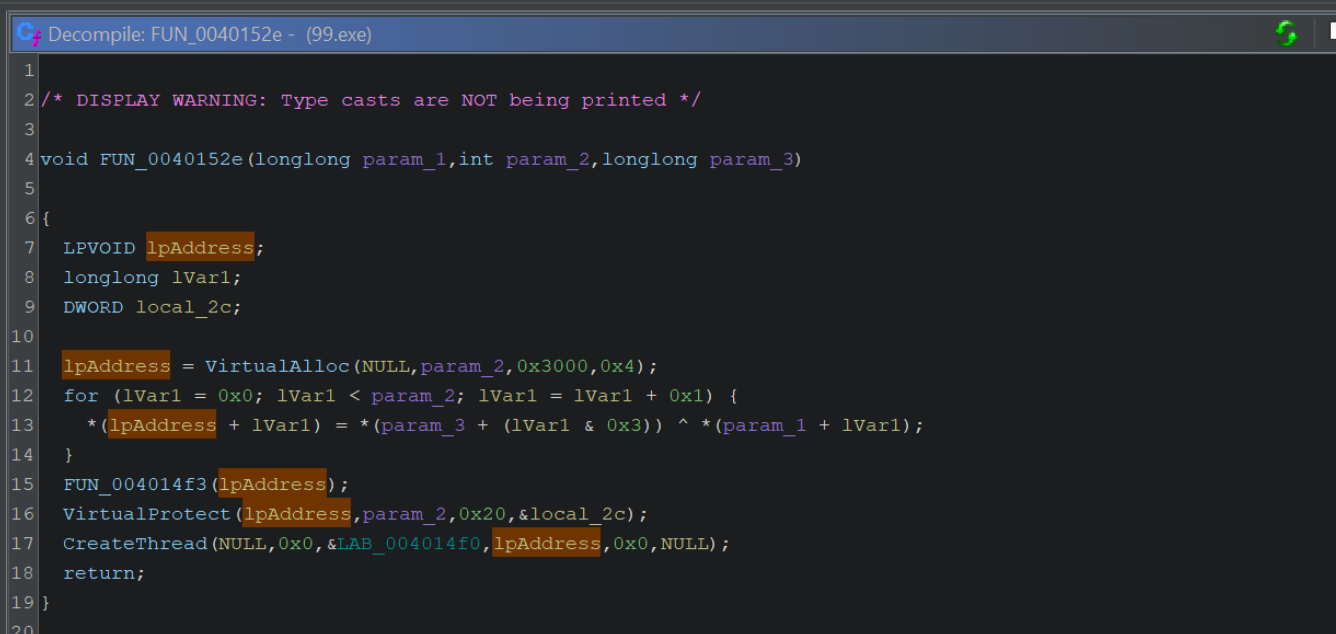
Beginner Ghidra Guide - Manual Shellcode Decryption
Advertisement Space (336x280)
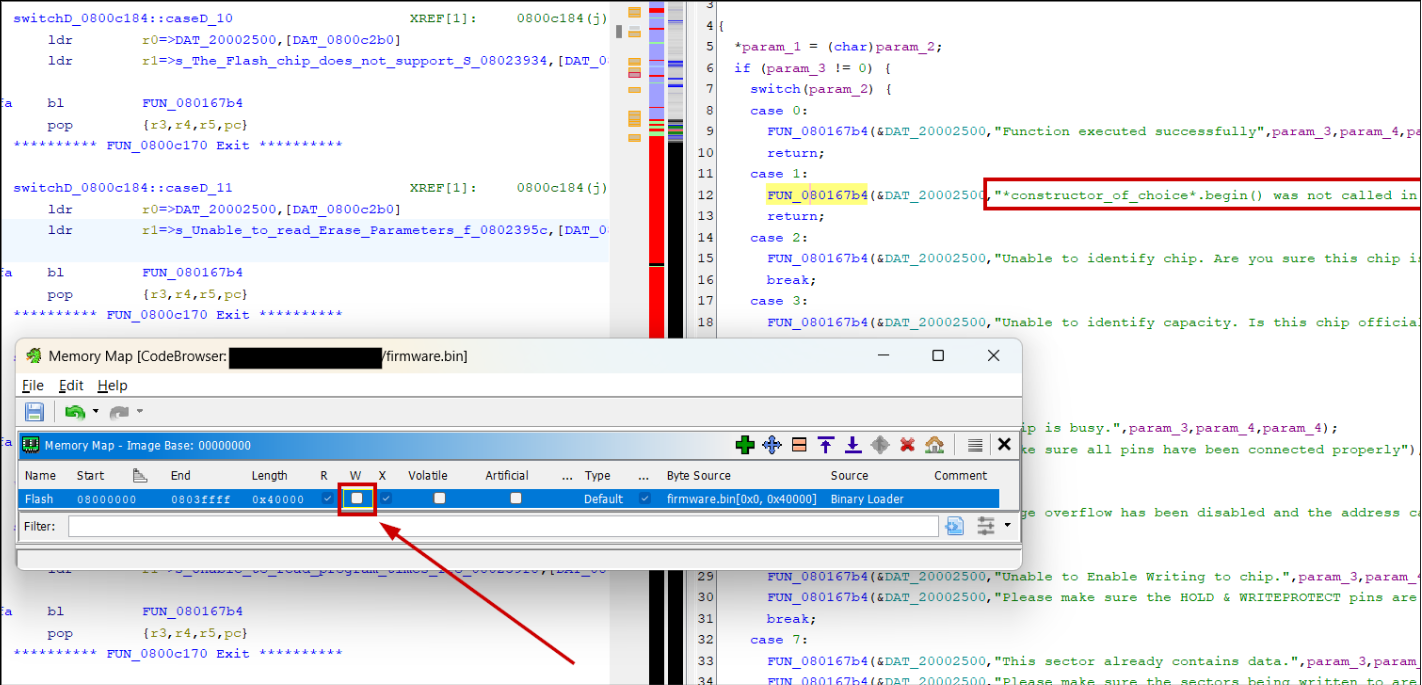
Taming the dragon: reverse engineering firmware with Ghidra | Pen Test ...
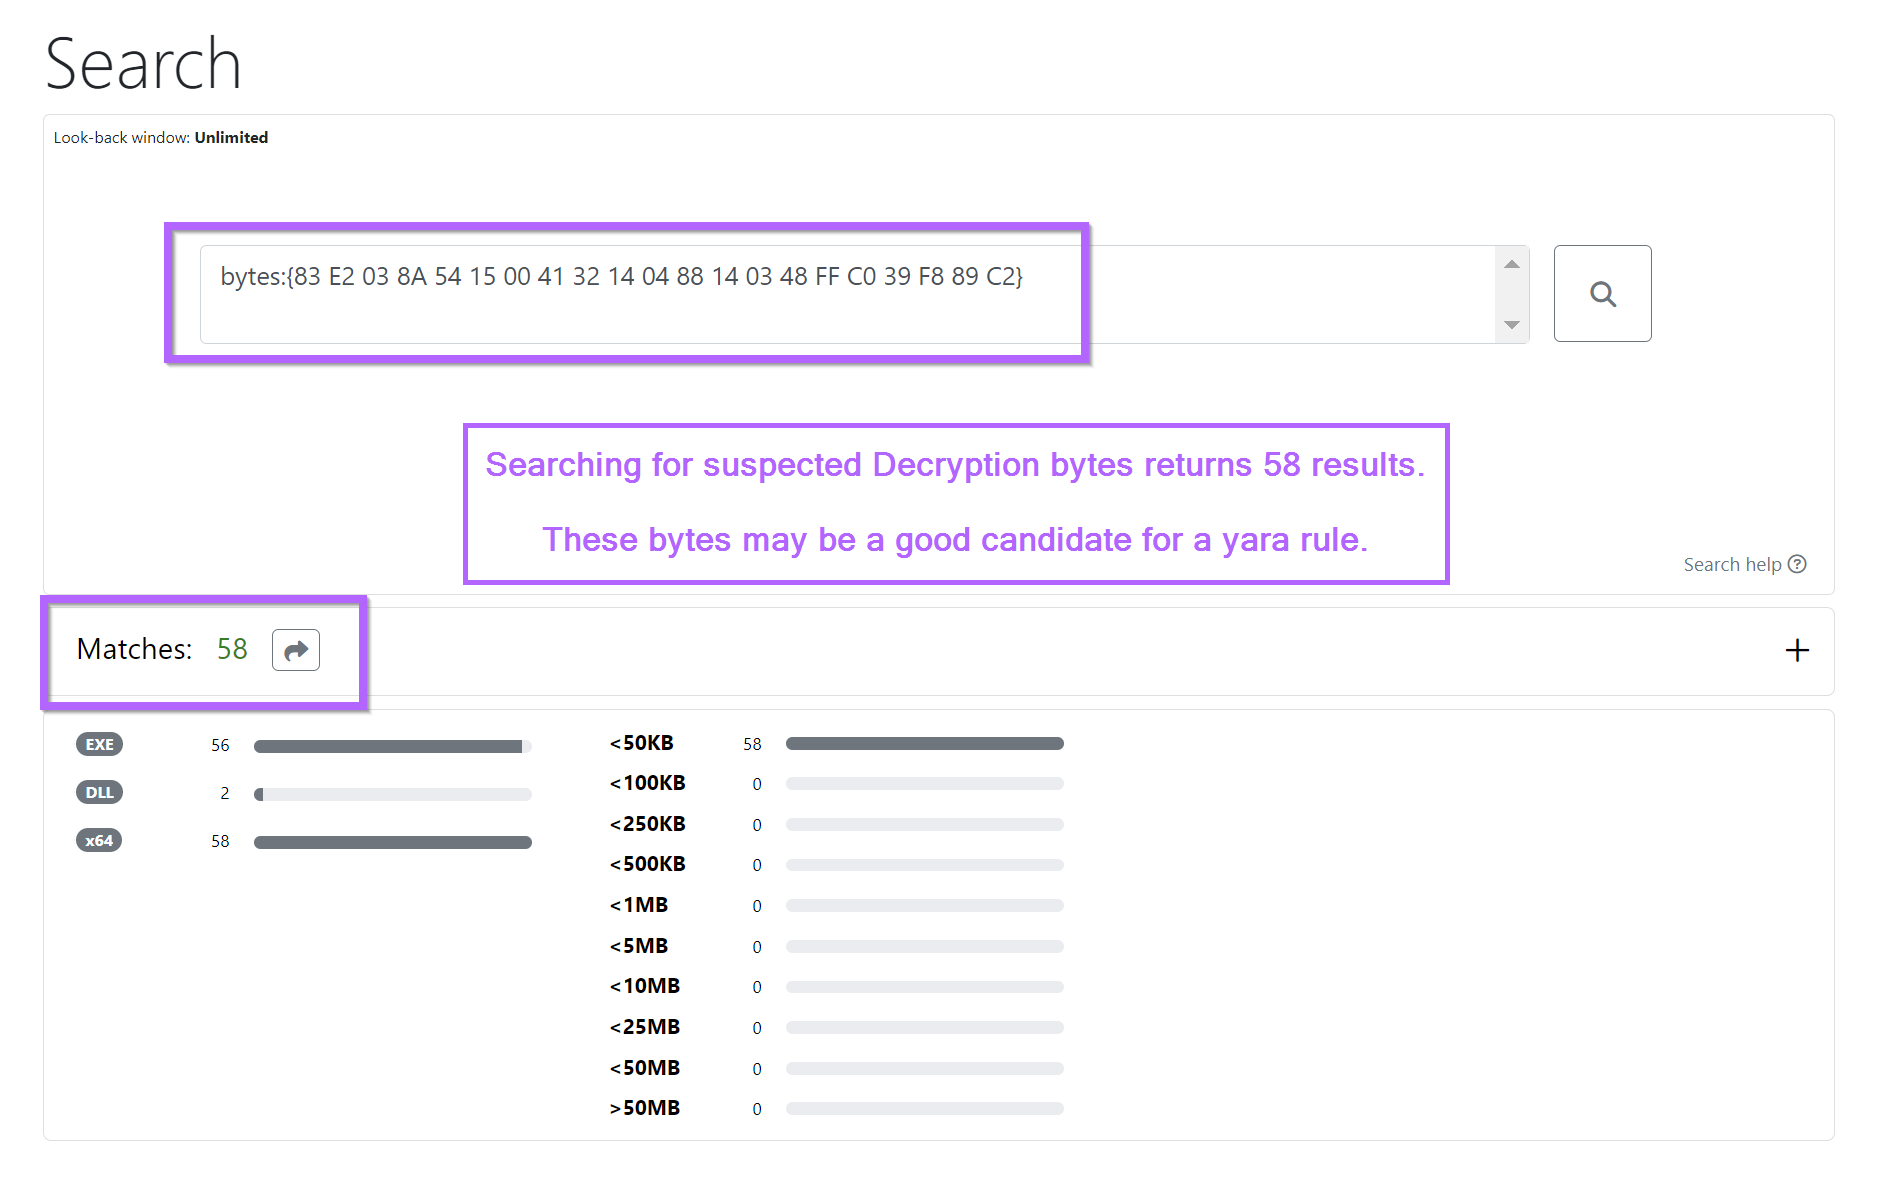
Beginner Ghidra Guide - Manual Shellcode Decryption
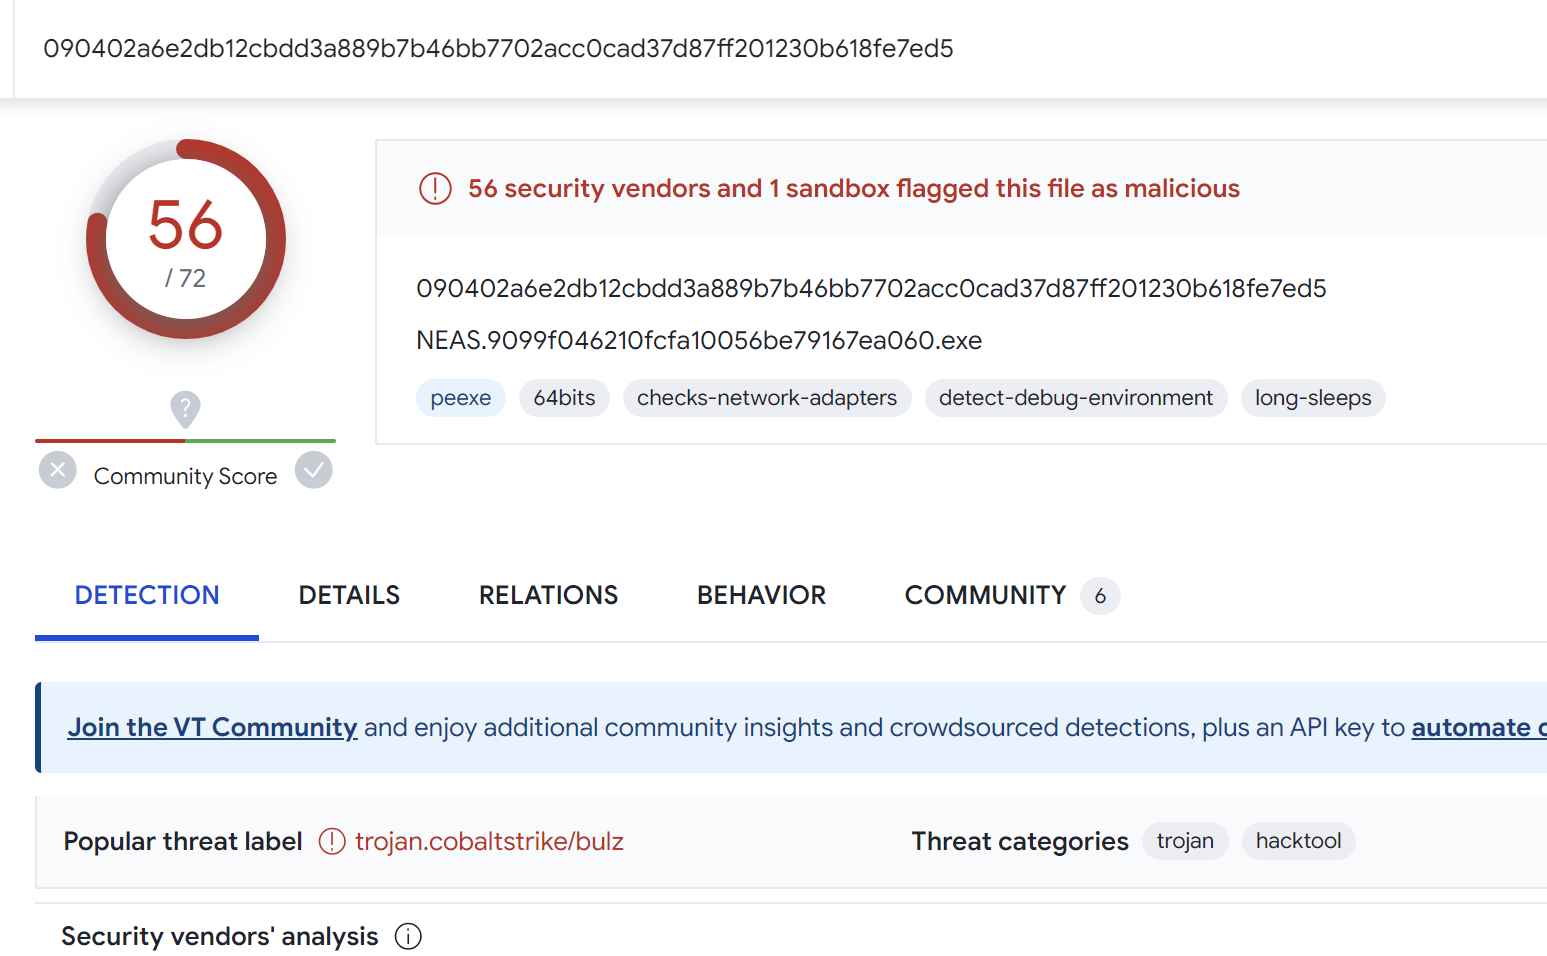
Beginner Ghidra Guide - Manual Shellcode Decryption

Decompiling and Debugging with Ghidra - DEV Community

Pull apart an EXE file with Ghidra (NSA Tool) (Reverse Engineering ...

Demonstrate that you can decompile a function using Ghidra - YouTube

Ghidra Basics - Manual Shellcode Analysis and C2 Extraction : r/blueteamsec

Ghidra Basics - Manual Shellcode Analysis and C2 Extraction : r/blueteamsec

Ghidra Basics - Manual Shellcode Analysis and C2 Extraction : r/blueteamsec
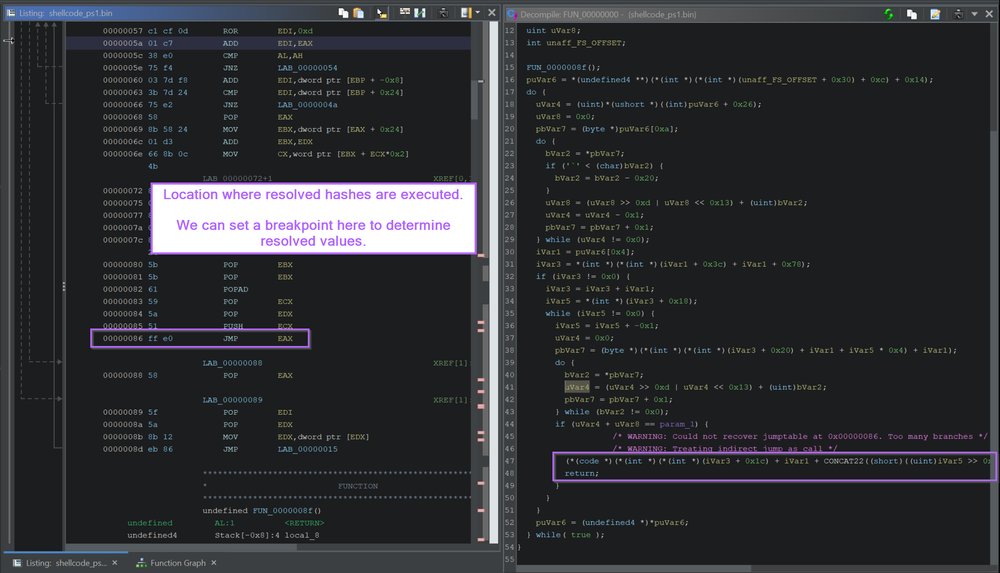
How to Use Ghidra to Analyse Shellcode and Extract Cobalt Strike ...
Advertisement Space (336x280)

How to Use Ghidra to Analyse Shellcode and Extract Cobalt Strike ...

How to Use Ghidra to Analyse Shellcode and Extract Cobalt Strike ...

disassembly - Statically Reverse Engineering Shellcode - IDA to Ghidra ...

disassembly - Statically Reverse Engineering Shellcode - IDA to Ghidra ...

disassembly - Statically Reverse Engineering Shellcode - IDA to Ghidra ...
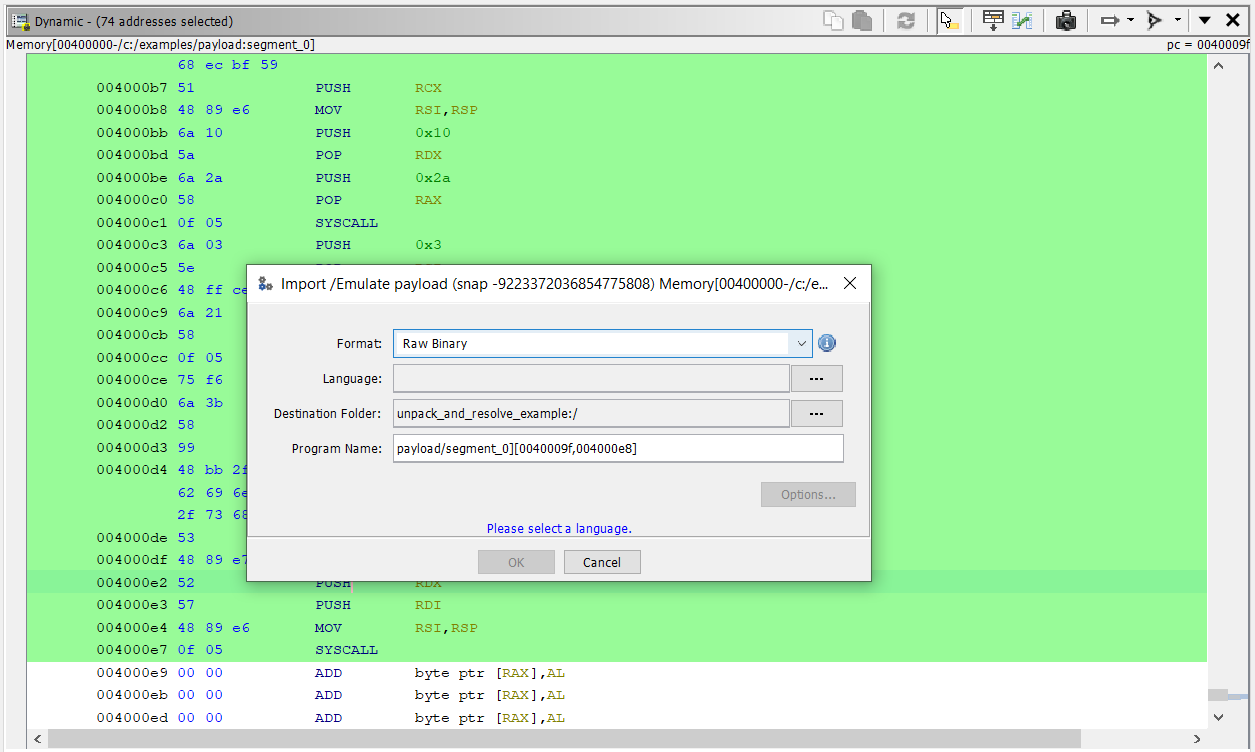
Reversing a Simple CrackMe with Ghidra Decompiler | by Craig Young | Medium