
Figure 1 From Fuzzing Logical Bugs In Ebpf Verifier With Bound
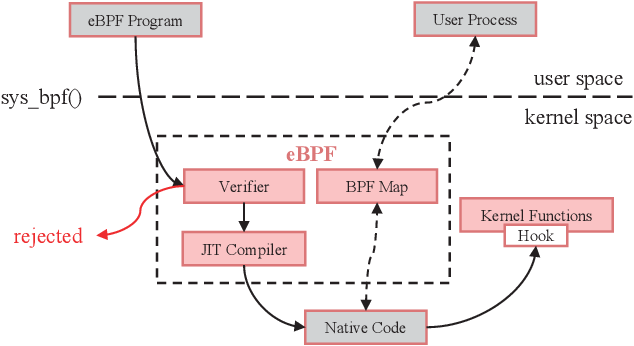
Figure 1 from Fuzzing Logical Bugs in eBPF Verifier with Bound ...
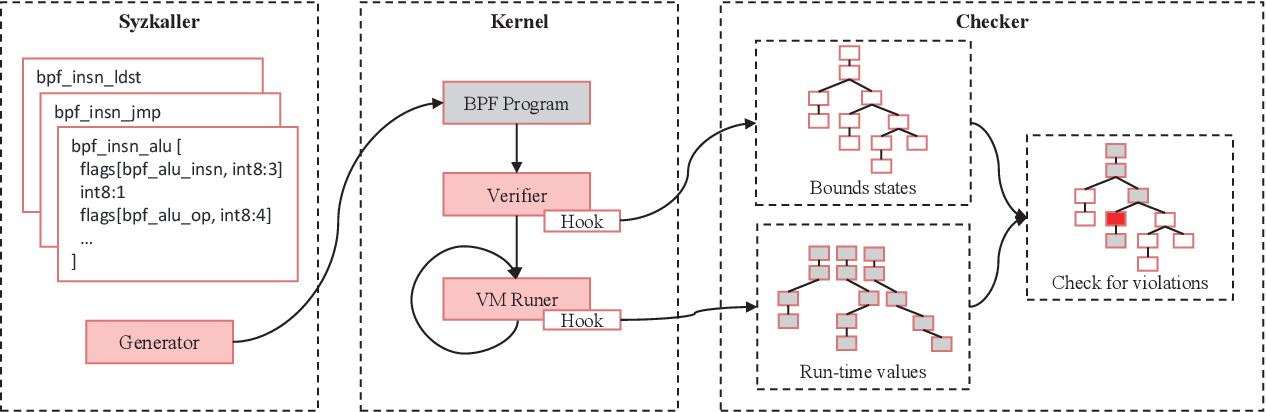
Figure 3 from Fuzzing Logical Bugs in eBPF Verifier with Bound ...
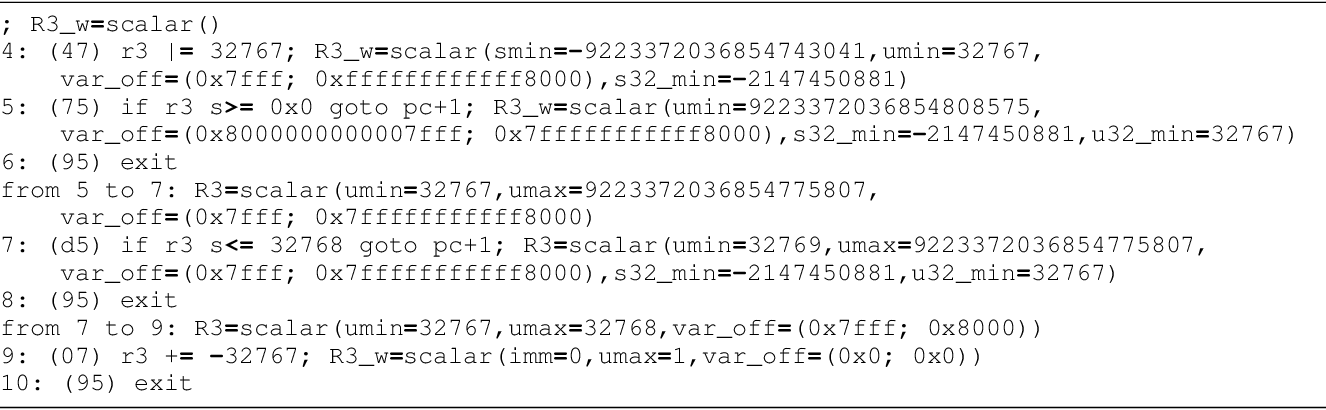
Figure 4 from Fuzzing Logical Bugs in eBPF Verifier with Bound ...
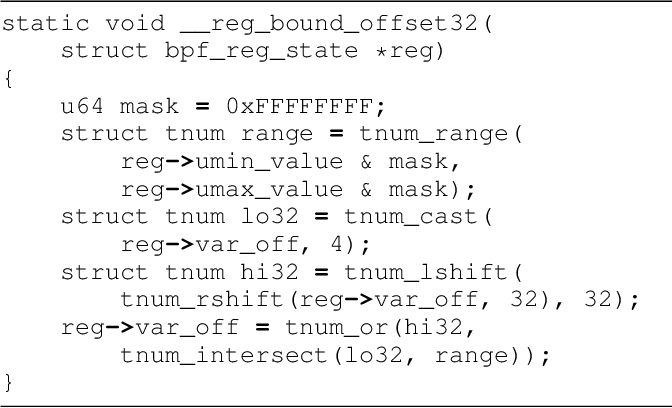
Figure 2 from Fuzzing Logical Bugs in eBPF Verifier with Bound ...
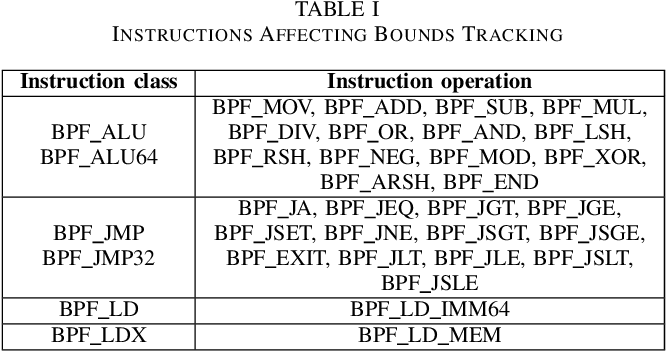
Table I from Fuzzing Logical Bugs in eBPF Verifier with Bound-Violation ...
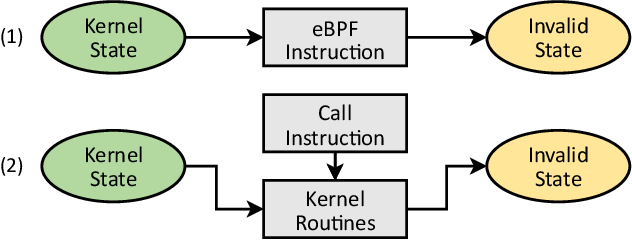
Figure 1 from Finding Correctness Bugs in eBPF Verifier with Structured ...
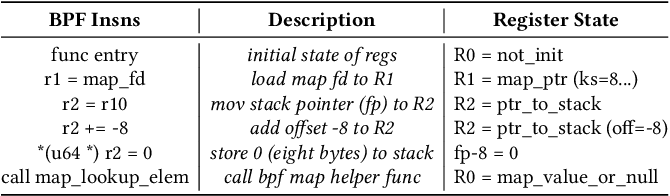
Table 1 from Finding Correctness Bugs in eBPF Verifier with Structured ...
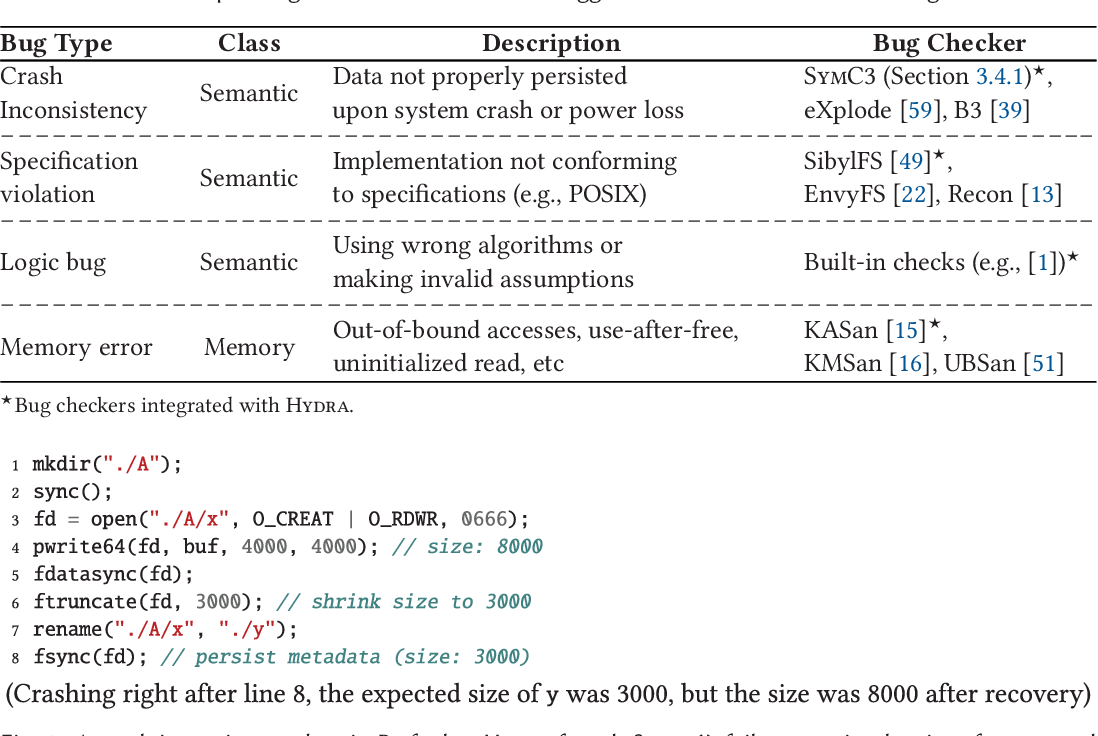
Table 1 from Finding Bugs in File Systems with an Extensible Fuzzing ...
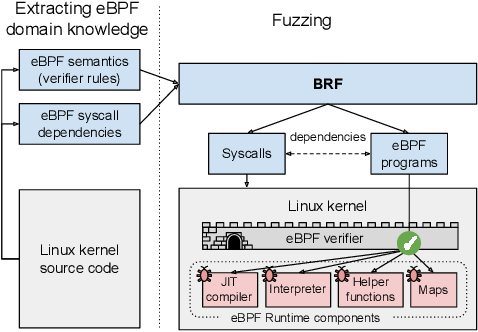
Figure 1 from BRF: Fuzzing the eBPF Runtime | Semantic Scholar
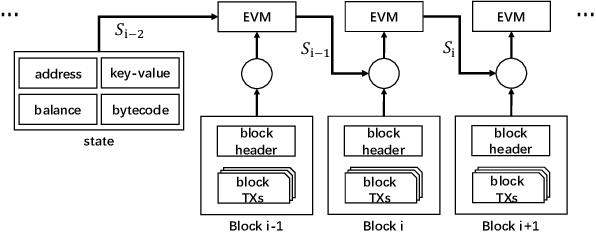
Figure 1 from Detecting State Inconsistency Bugs in DApps via On-Chain ...
Advertisement Space (300x250)
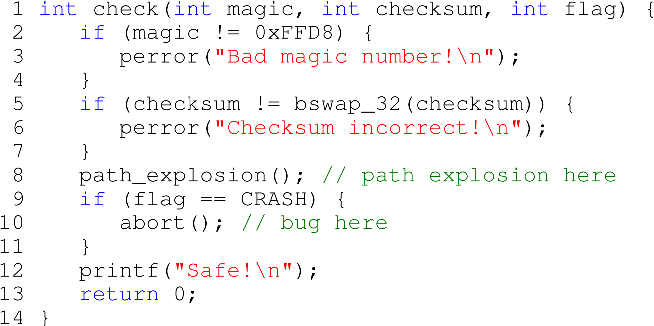
Figure 1 from Discover deeper bugs with dynamic symbolic execution and ...
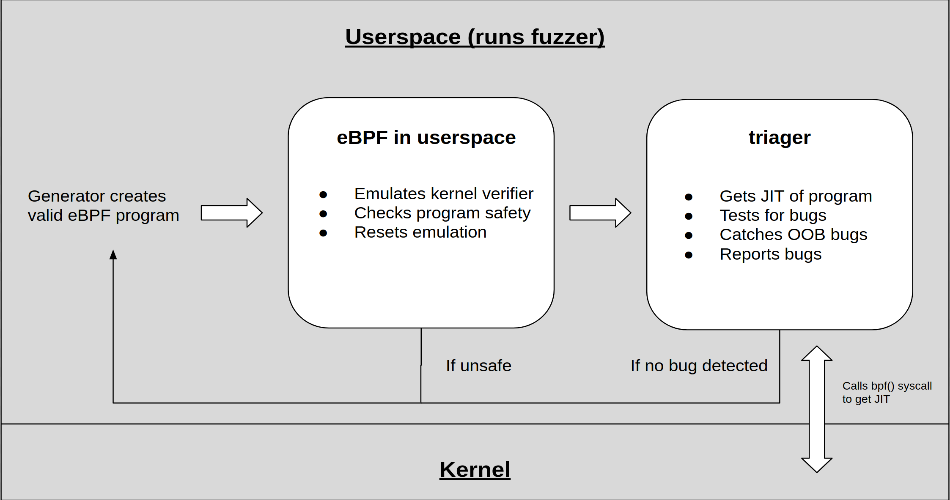
Fuzzing for eBPF JIT bugs in the Linux kernel :: Simon Scannell's ...
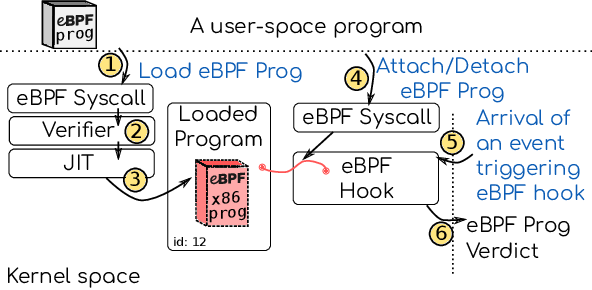
Figure 1 from Demystifying Performance of eBPF Network Applications ...

Fuzzing for eBPF JIT bugs in the Linux kernel :: Simon Scannell's ...
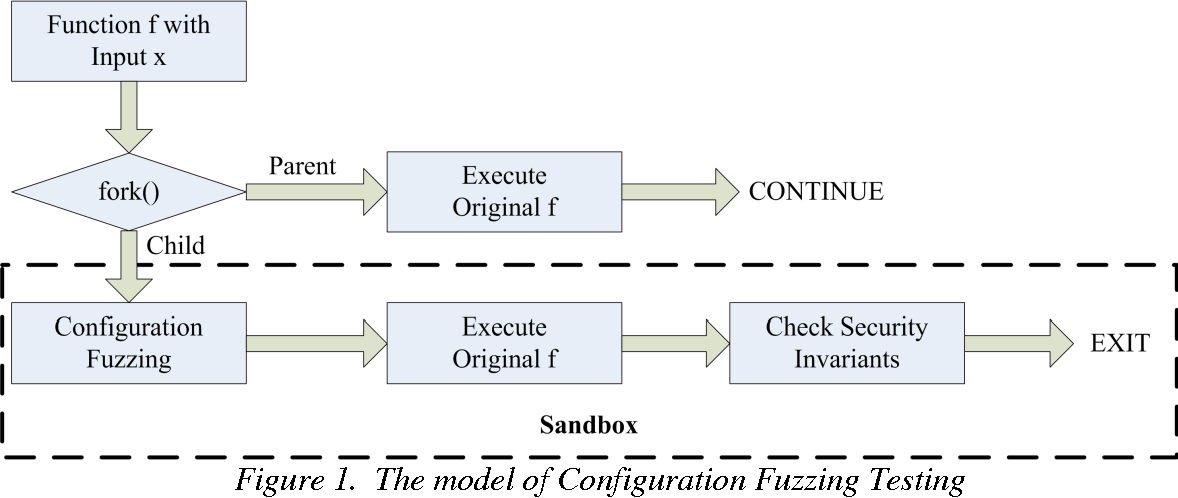
Figure 1 from CONFU: Configuration Fuzzing Testing Framework for ...
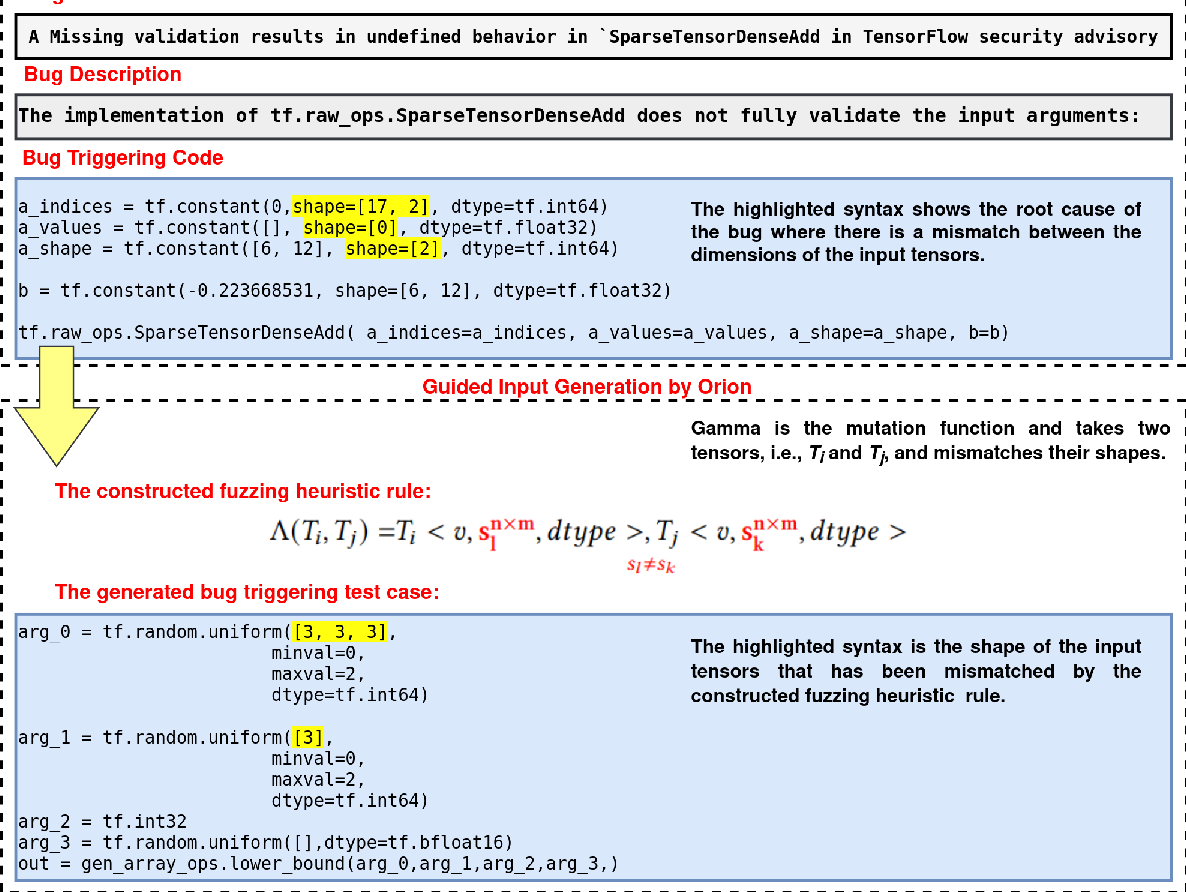
Figure 1 from History-Driven Fuzzing For Deep Learning Libraries ...
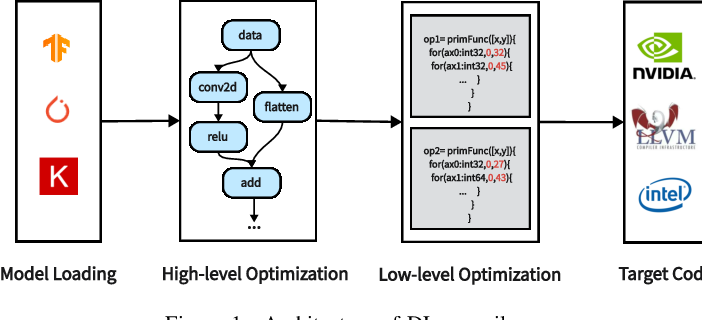
Figure 1 from DeepDiffer: Find Deep Learning Compiler Bugs via Priority ...
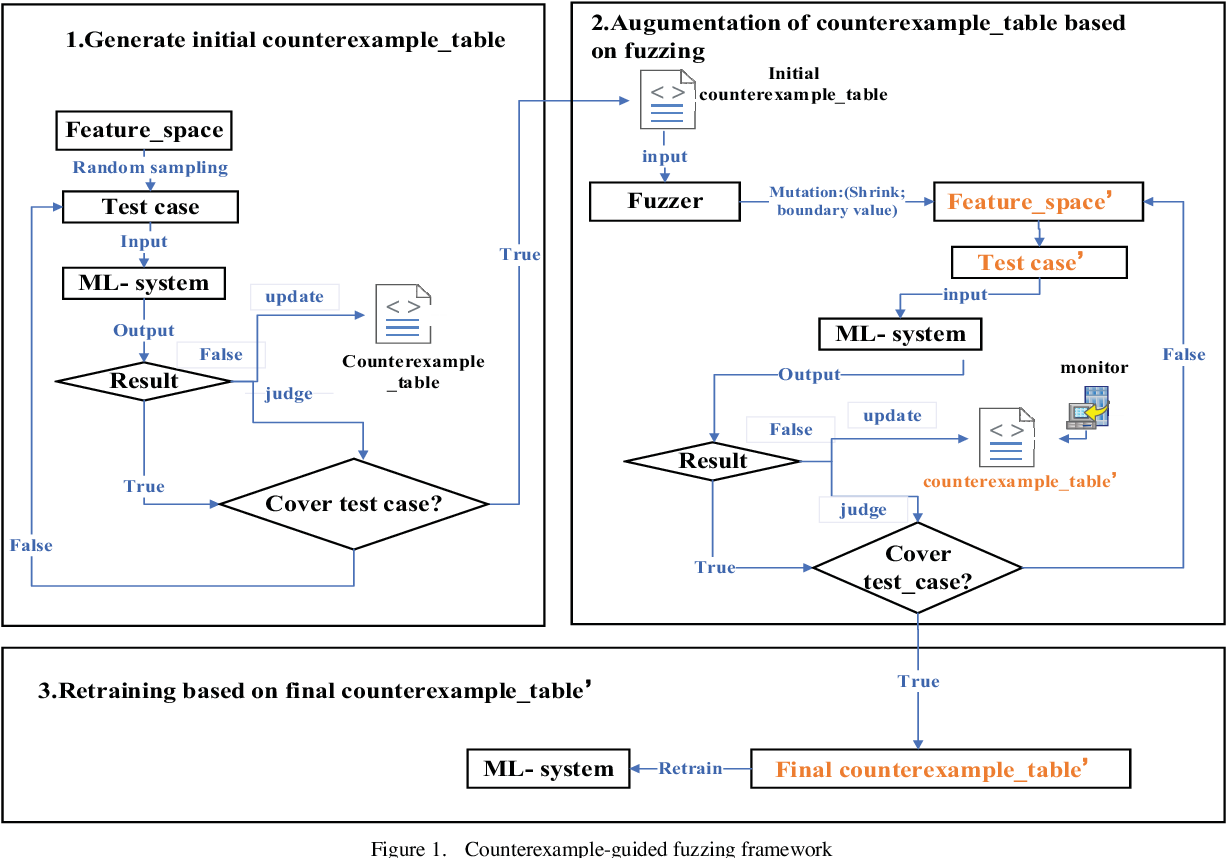
Figure 1 from An Empirical Study of Counterexample-Guided Fuzzing for ...

Figure 1 from Formal and Fuzzing Amplification: Targeting Vulnerability ...

Figure 1 from BIFF: Practical Binary Fuzzing Framework for Programs of ...
Advertisement Space (336x280)

Figure 1 from Exploring Effective Fuzzing Strategies to Analyze ...

Figure 1 from Compiler fuzzing through deep learning | Semantic Scholar
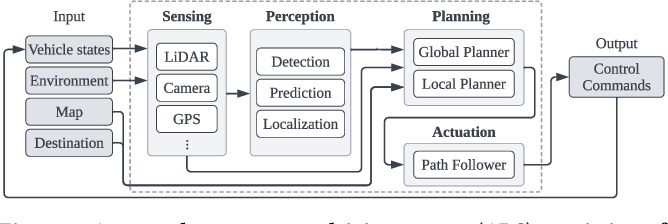
Figure 1 from DriveFuzz: Discovering Autonomous Driving Bugs through ...

Figure 1 from Prompt Fuzzing for Fuzz Driver Generation | Semantic Scholar

Fuzzing for eBPF JIT bugs in the Linux kernel : r/lowlevel

Figure 1 from Program Environment Fuzzing | Semantic Scholar
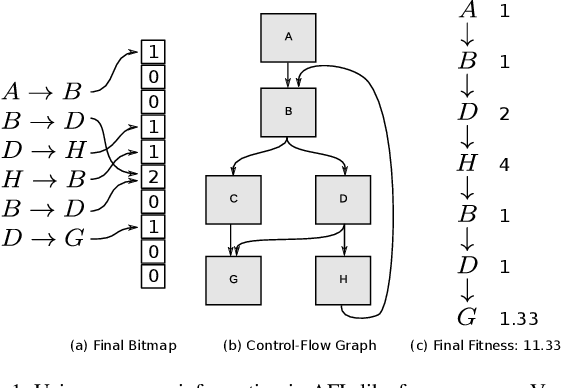
Figure 1 from Impeding Fuzzing Audits of Binary Executables | Semantic ...

Figure 1 from Predecessor-aware Directed Greybox Fuzzing | Semantic Scholar

Finding Bugs in File Systems with an Extensible Fuzzing Framework

Finding Bugs in File Systems with an Extensible Fuzzing Framework
Advertisement Space (336x280)

Figure 1 from A model-based fuzzing approach for DBMS | Semantic Scholar

Figure 1 from Differential Fuzzing for Data Distribution Service ...

Figure 1 from Fuzzing ICS Protocols: Modbus Fuzzer Framework | Semantic ...
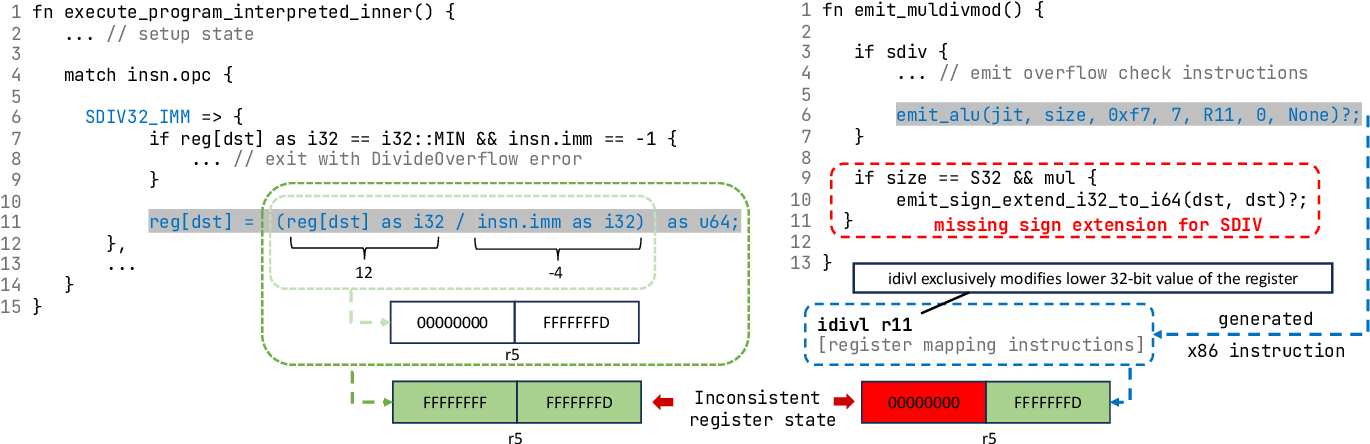
Figure 1 from Toss a Fault to BpfChecker: Revealing Implementation ...
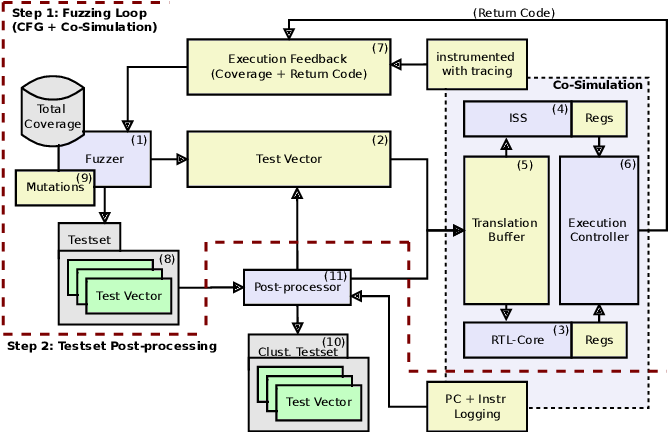
Figure 1 from Efficient Cross-Level Processor Verification using ...
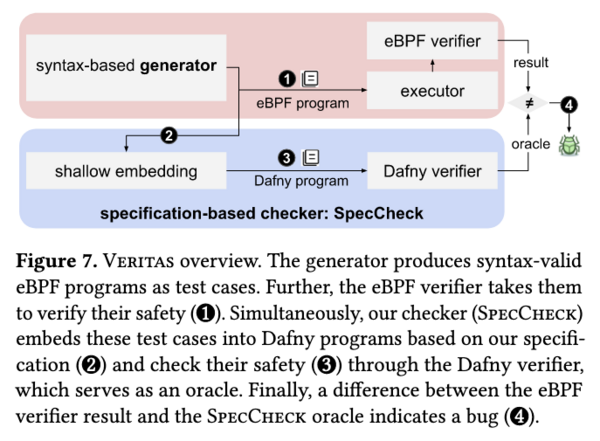
EBPF Misbehavior Detection: Fuzzing with a Specification-Based Oracle ...