
How To Create A Splunk Alert For Spike In Log Even Splunk Community

How to create a Splunk Alert for spike in log even... - Splunk Community

Solved: How to create Alert in Cloud version of Splunk - Splunk Community

Solved: How to create Alert in Cloud version of Splunk - Splunk Community
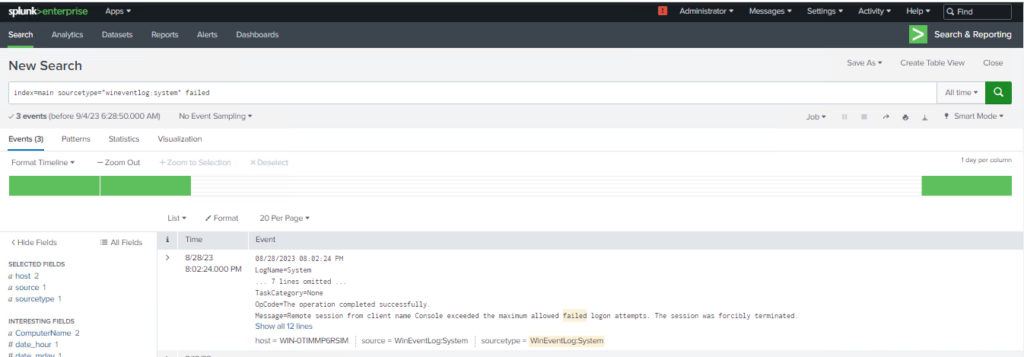
How to create alert in splunk

How to create alert in splunk
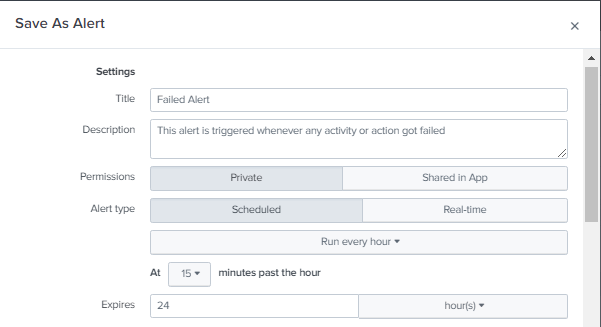
How to create alert in splunk

How to Create Alert in Splunk (easy Method) - YouTube
How to create alert in splunk
How to create alert in splunk

How to create a basic alert? - Splunk Community
Advertisement Space (300x250)
How to Create a Modular Alert | Splunk

How to create alert in splunk

How to create alert in splunk

How to create alert in splunk
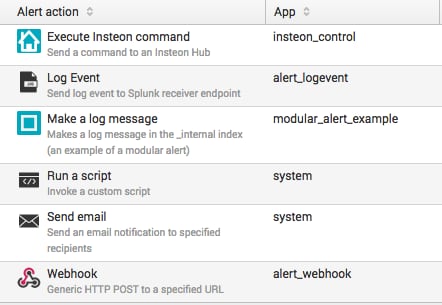
How to Create a Modular Alert | Splunk
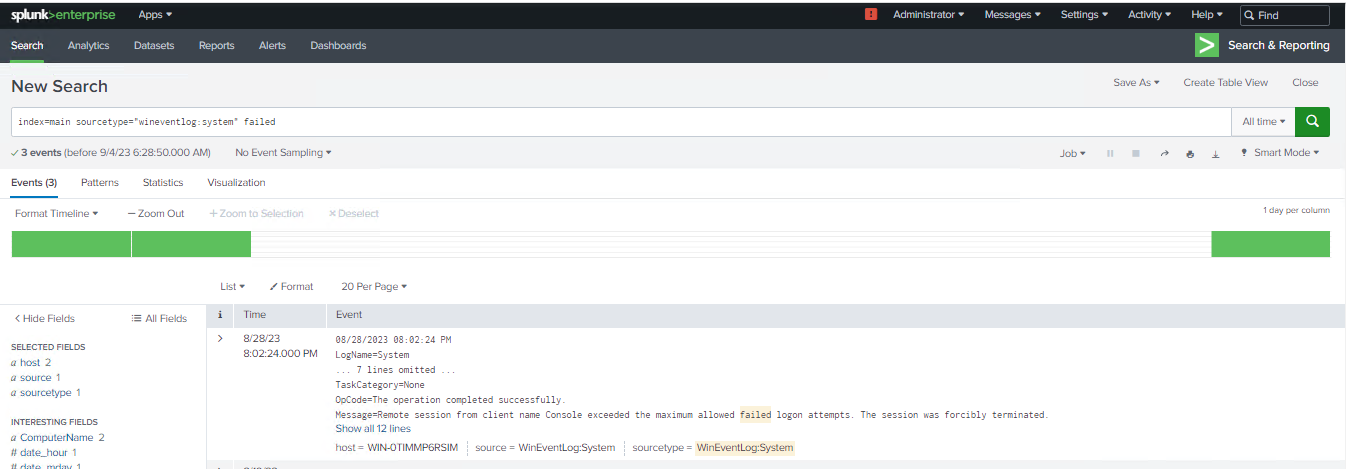
How to create alert in splunk
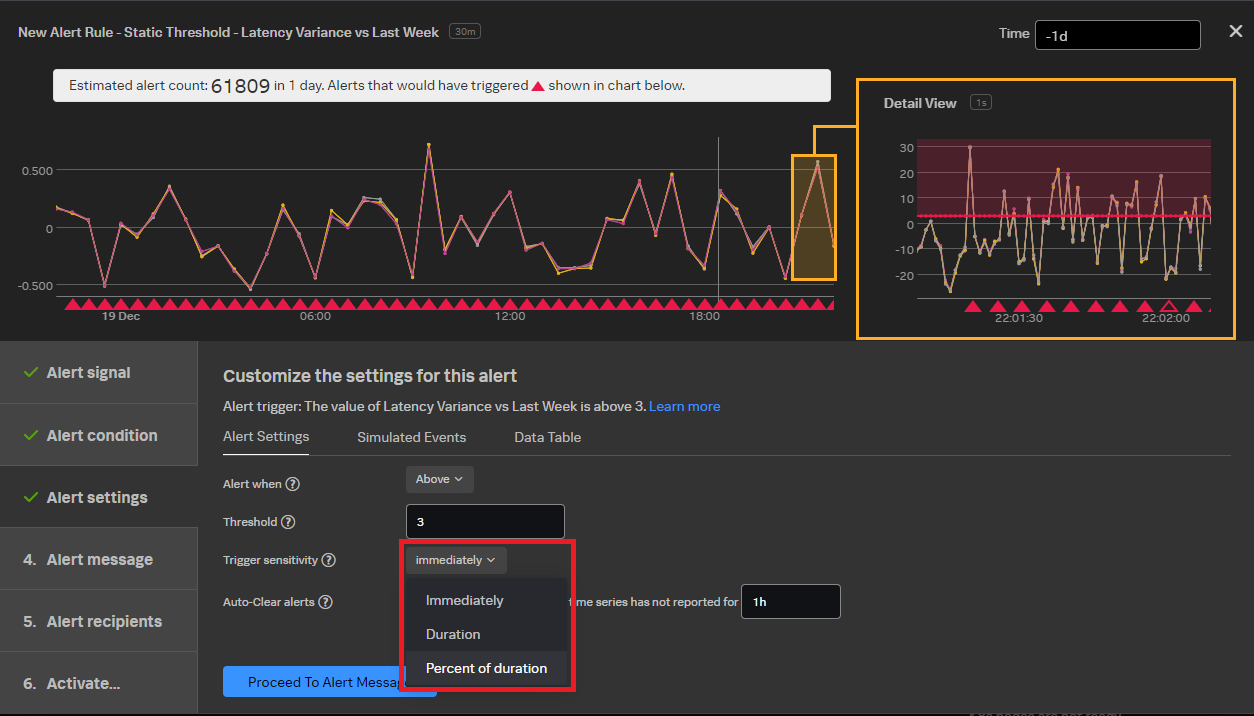
How to Customise Detectors for Even Better Alerting | Splunk
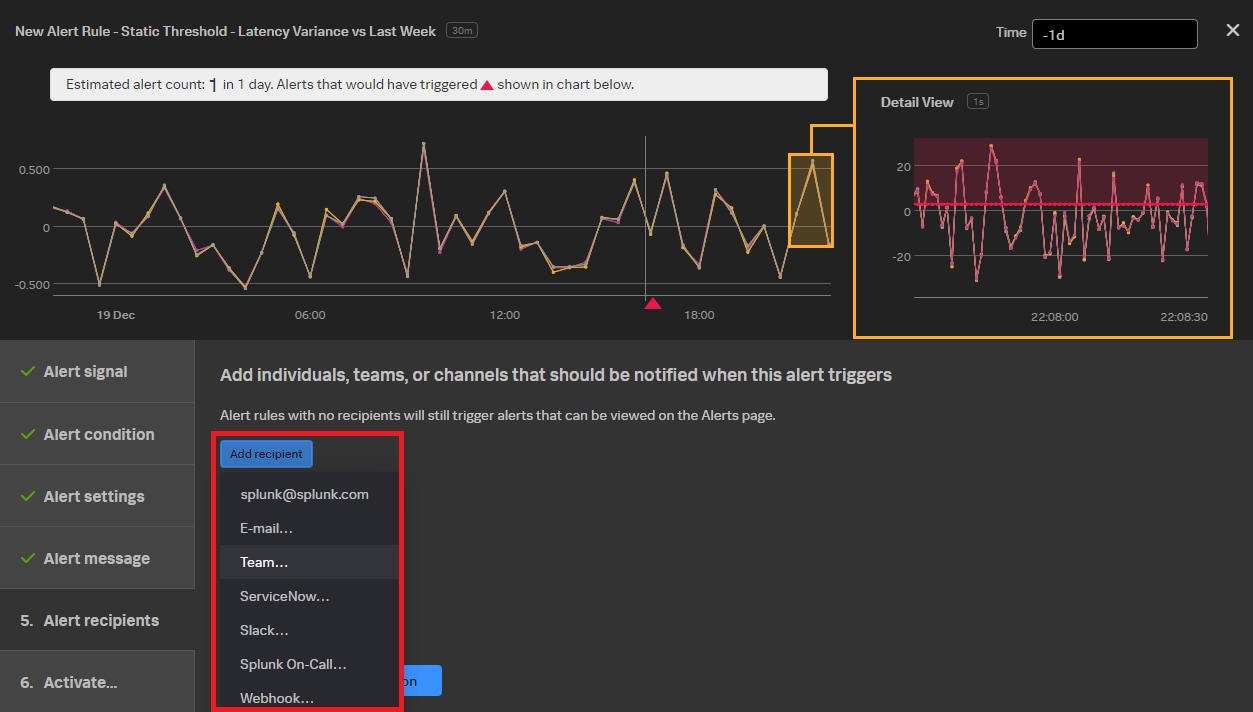
How to Customise Detectors for Even Better Alerting | Splunk
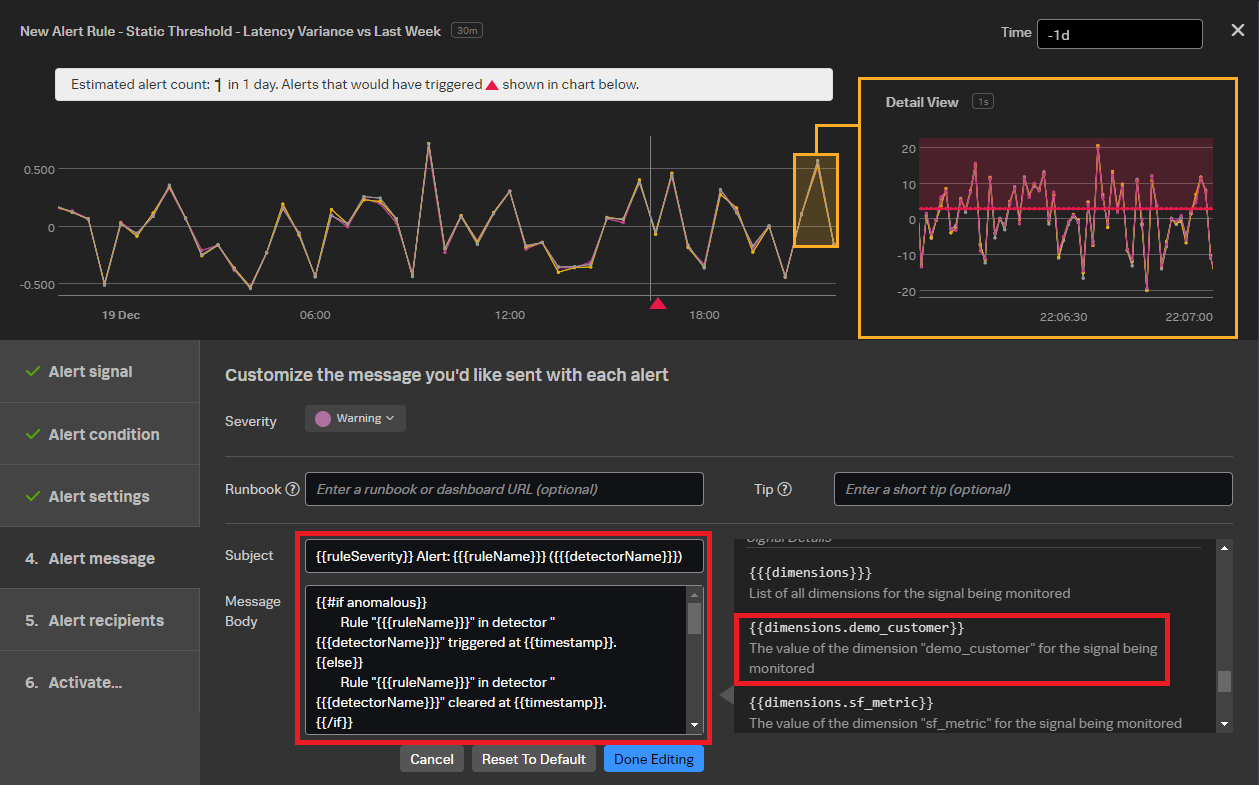
How to Customise Detectors for Even Better Alerting | Splunk
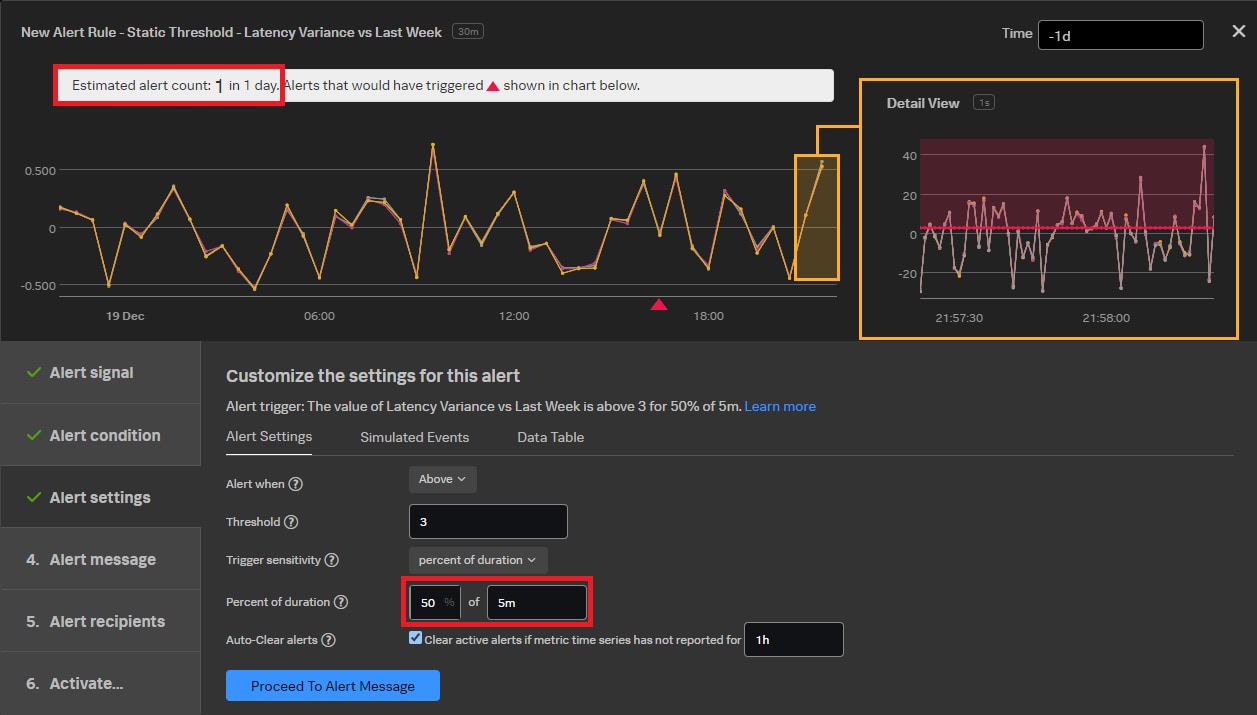
How to Customise Detectors for Even Better Alerting | Splunk
Advertisement Space (336x280)

How to Create Alerts in Splunk Dashboard | Step-by-Step Guide - YouTube

SPLUNK - HOW TO CREATE AN ALERT - YouTube
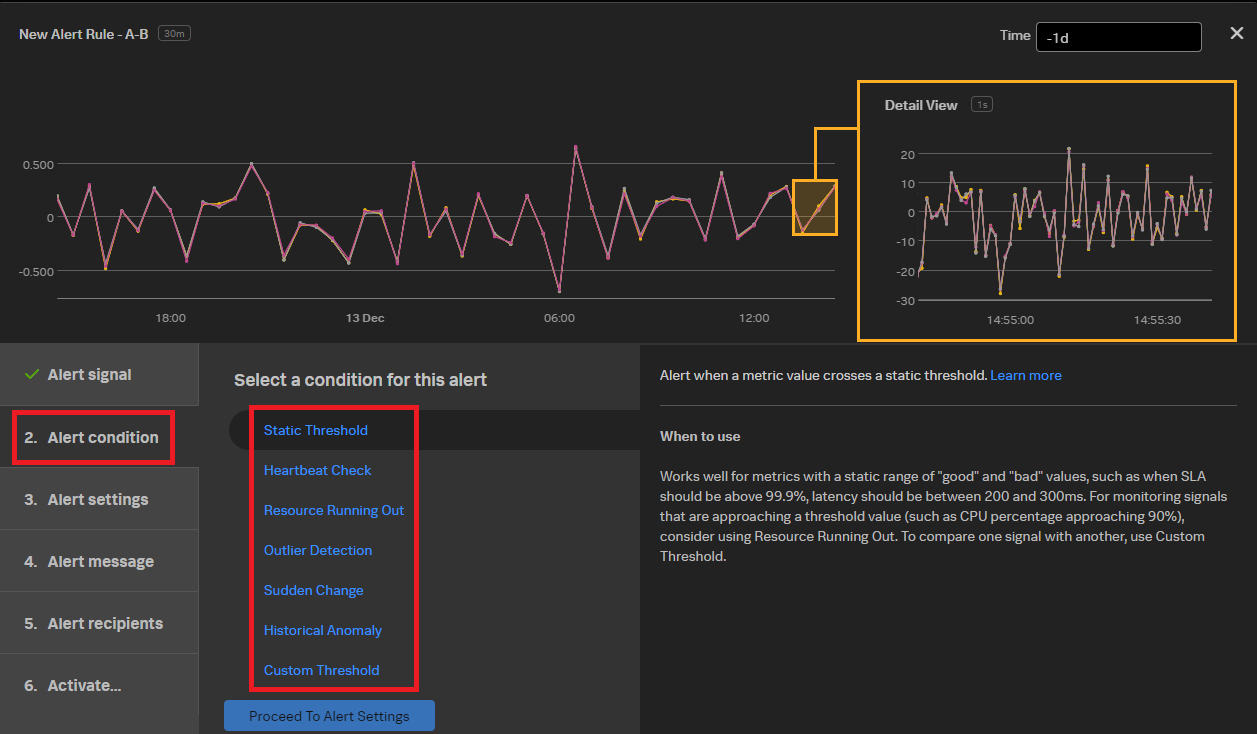
How to Customise Detectors for Even Better Alerting | Splunk

Log alerts - Alert that tell when a log source sto... - Splunk Community
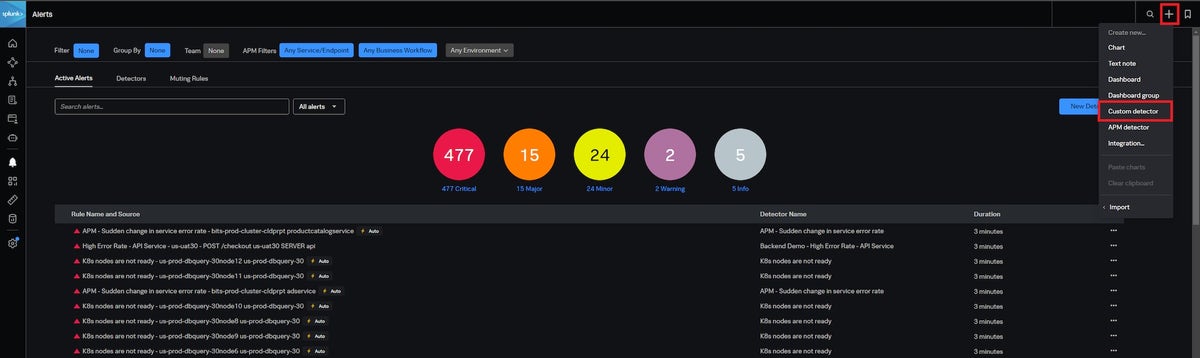
How to Customise Detectors for Even Better Alerting | Splunk
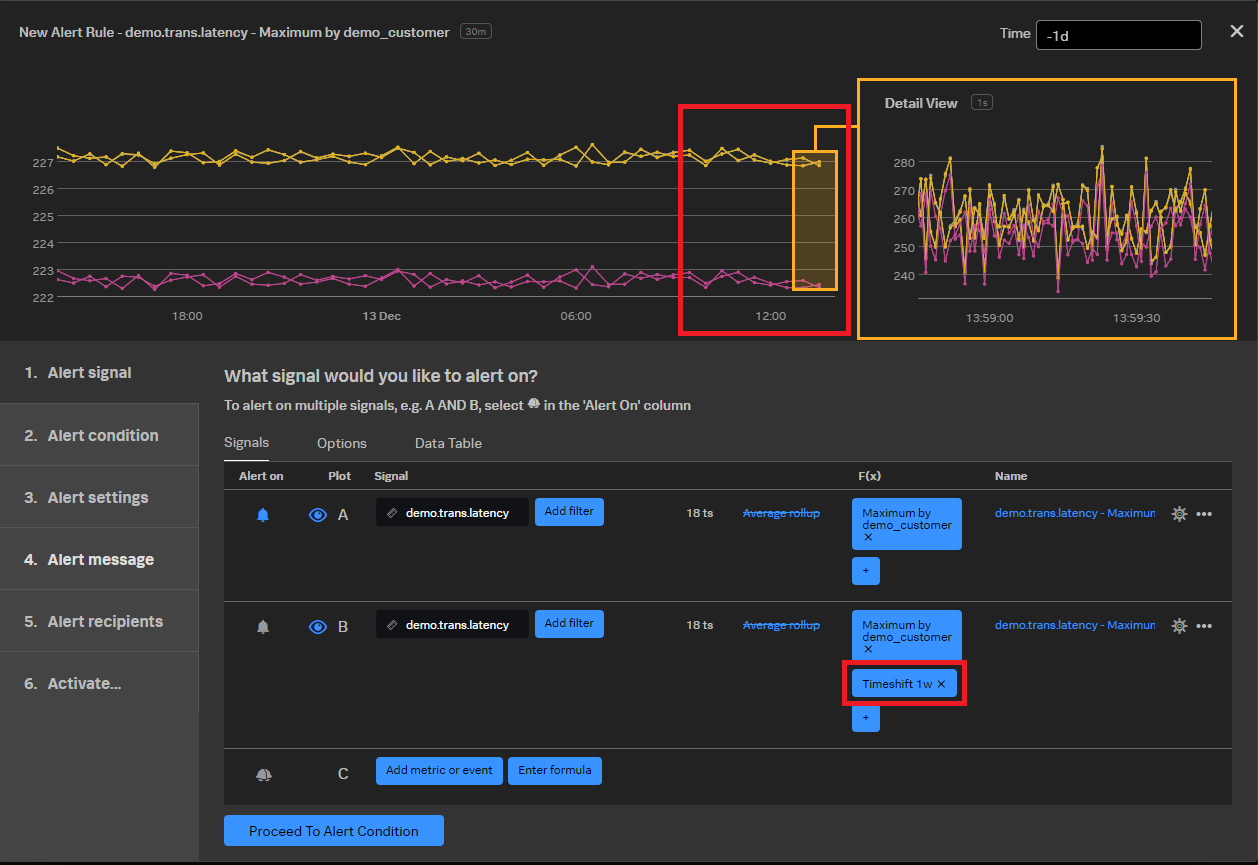
How to Customise Detectors for Even Better Alerting | Splunk

How to Create Alerts in Splunk Dashboard - YouTube

Solved: How to setup a Splunk query to alert and send emai... - Splunk ...

How to configure Alert actions to syslog server? - Splunk Community
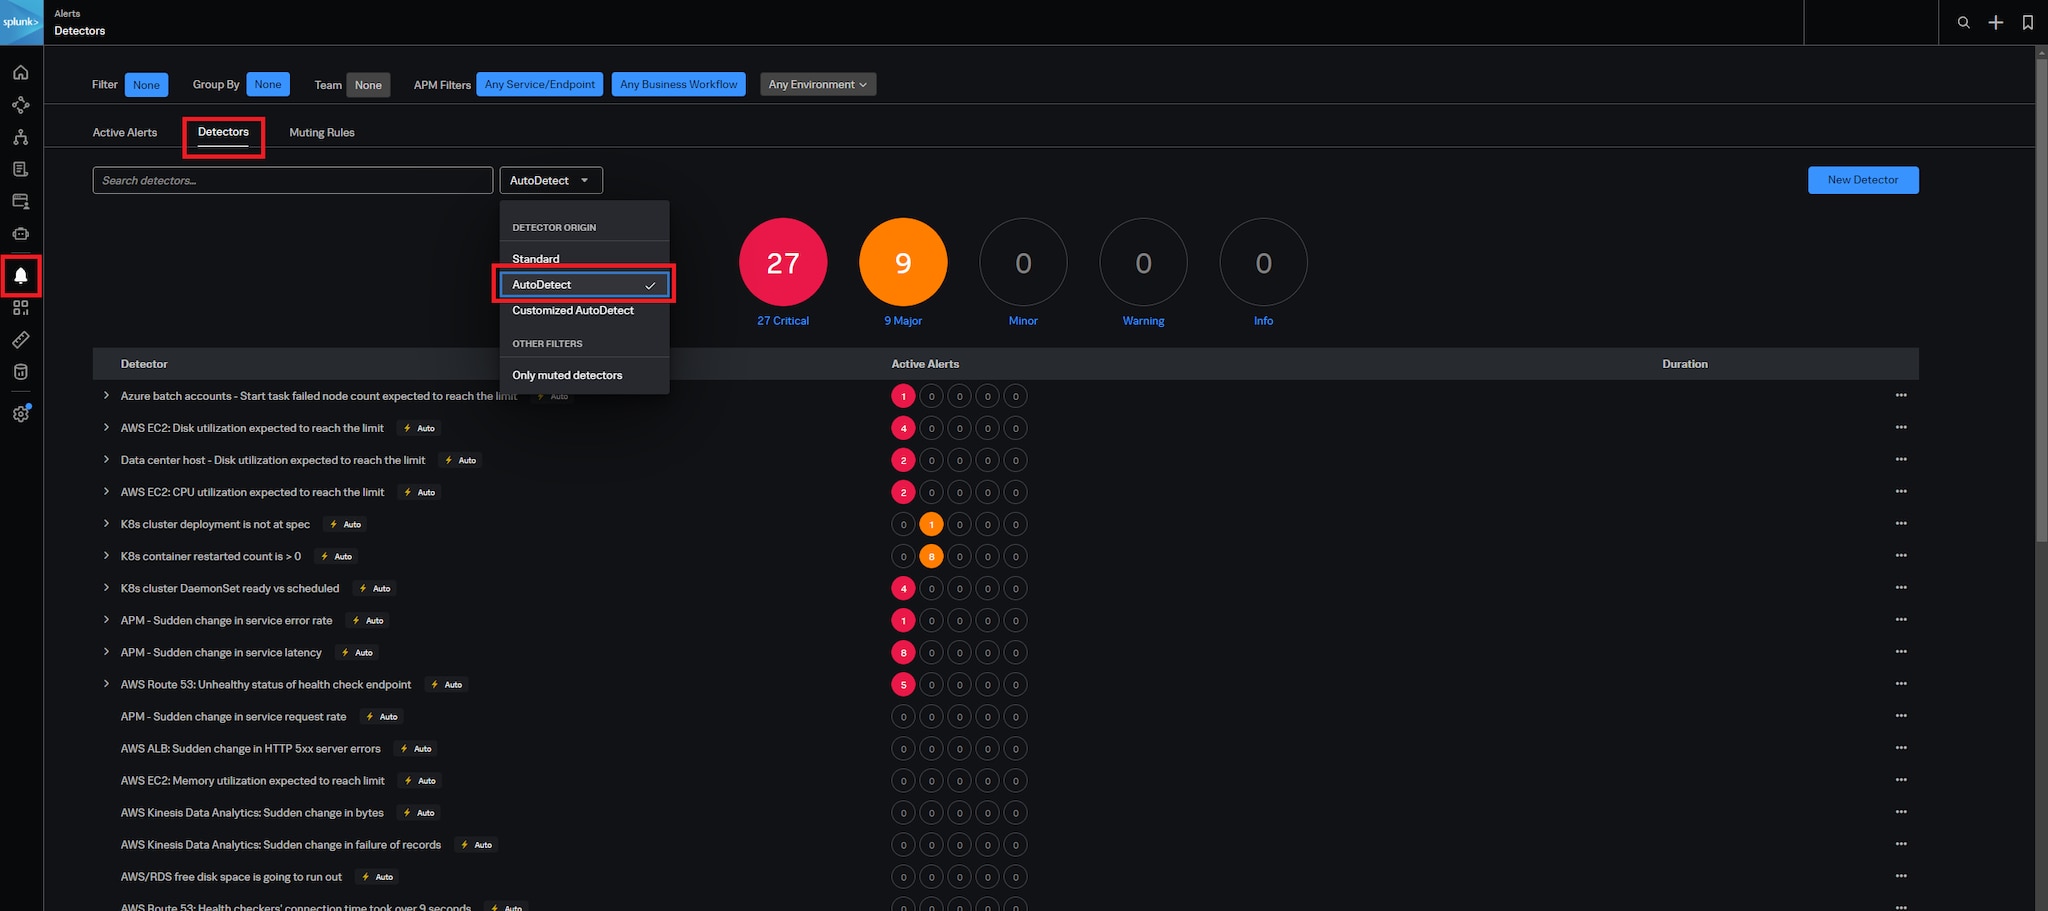
How to Create Great Alerts | Splunk
Advertisement Space (336x280)

How To Create Splunk Alerts? (2024) - YouTube

How to Send Splunk Observability Alerts to Webex t... - Splunk Community
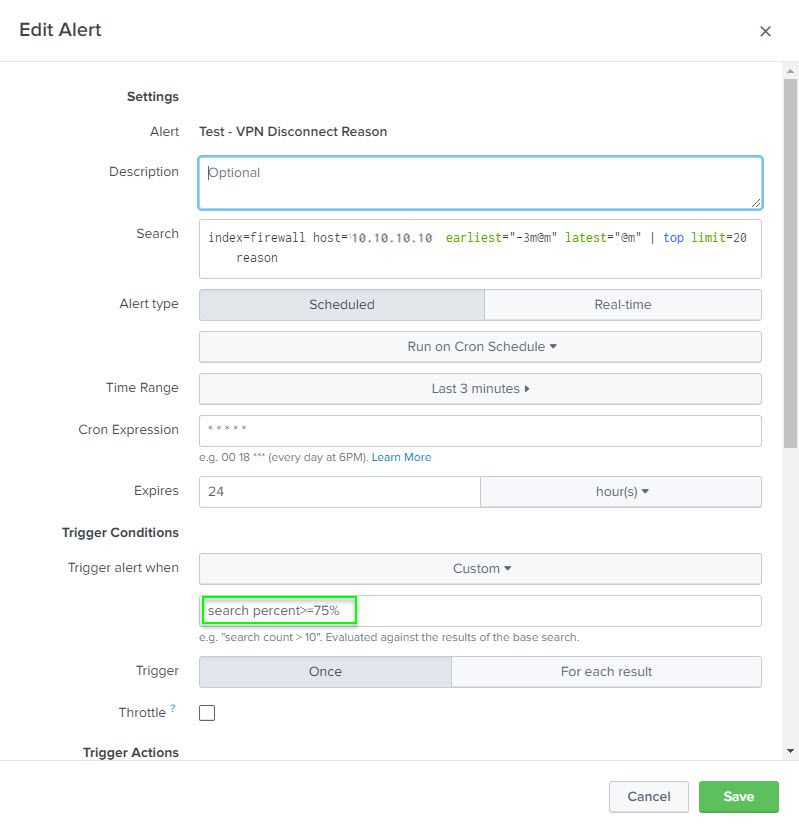
Solved: Create an alert email from a splunk search result - Splunk ...

How to Send Splunk Observability Alerts to Webex t... - Splunk Community

Tech Talk | How to Use Logs from Splunk Platform i... - Splunk Community

How to Send Splunk Observability Alerts to Webex t... - Splunk Community