
How To Extract Json Data Within The Logs Which Als Splunk Community

How to extract JSON data within the logs which als... - Splunk Community

Solved: How to extract fields from json attributes? - Splunk Community

How to extract Json file format as Fields using pr... - Splunk Community

How do you extract a timestamp from JSON logs that... - Splunk Community

Solved: Sourcetype for JSON data fails to extract the time... - Splunk ...

Solved: How to extract fields in json format? - Splunk Community

Solved: Sourcetype for JSON data fails to extract the time... - Splunk ...

Solved: How to format JSON data into a table? - Splunk Community

Solved: How to format JSON data into a table? - Splunk Community

Solved: How to format JSON data into a table? - Splunk Community
Advertisement Space (300x250)

How do you extract a timestamp from JSON logs that... - Splunk Community

Solved: How to parse JSON within Docker JSON? - Splunk Community
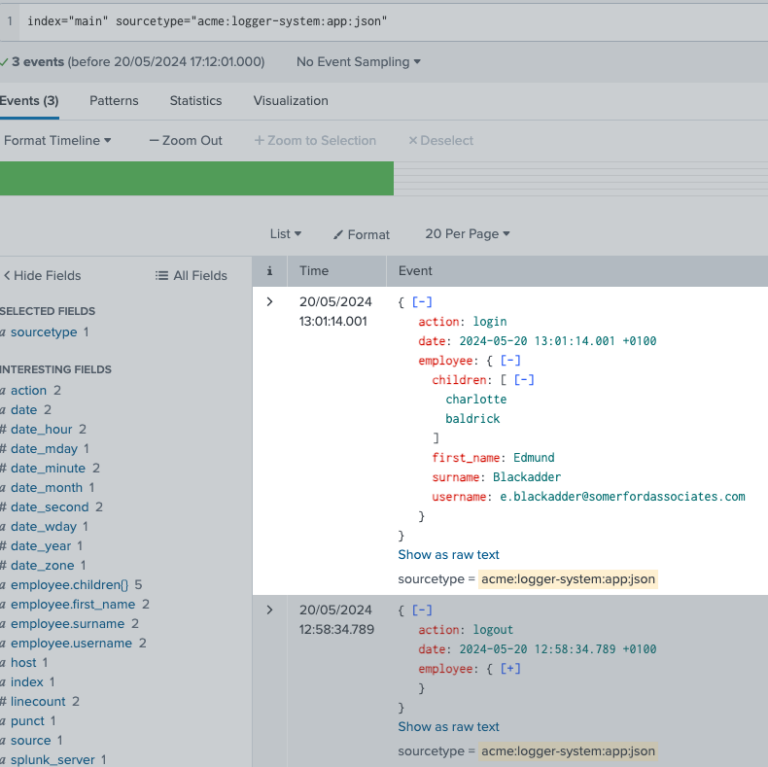
How to Format JSON Data Ready for Splunk - Somerford Associates
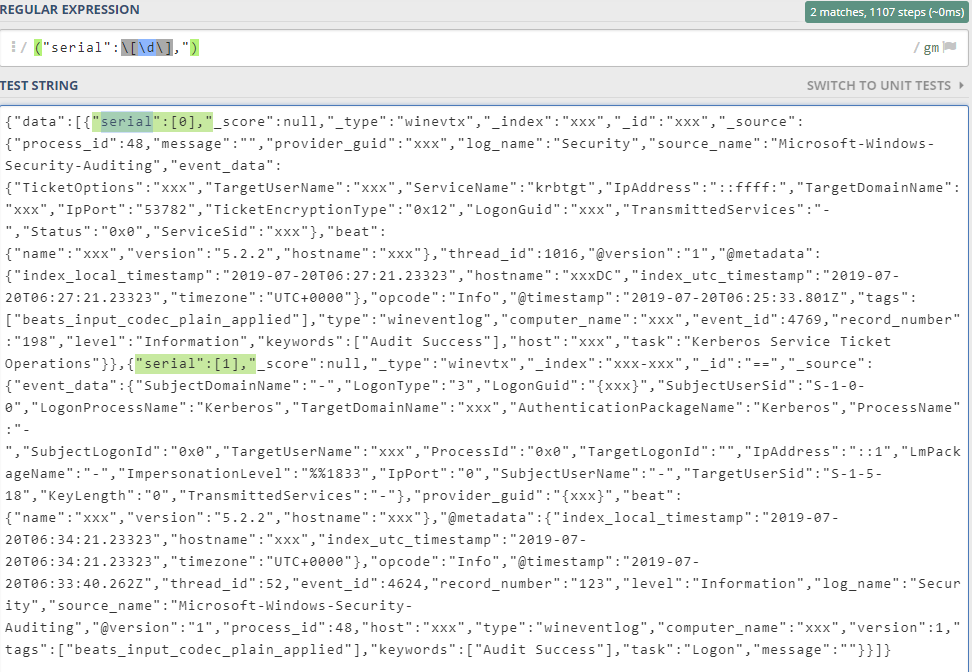
How to configure Splunk to parse and index JSON da... - Splunk Community

How do I extract multiple fields from a json array... - Splunk Community

How to display JSON tree structure in a summary in... - Splunk Community

Solved: How to combine JSON elements in array? - Splunk Community
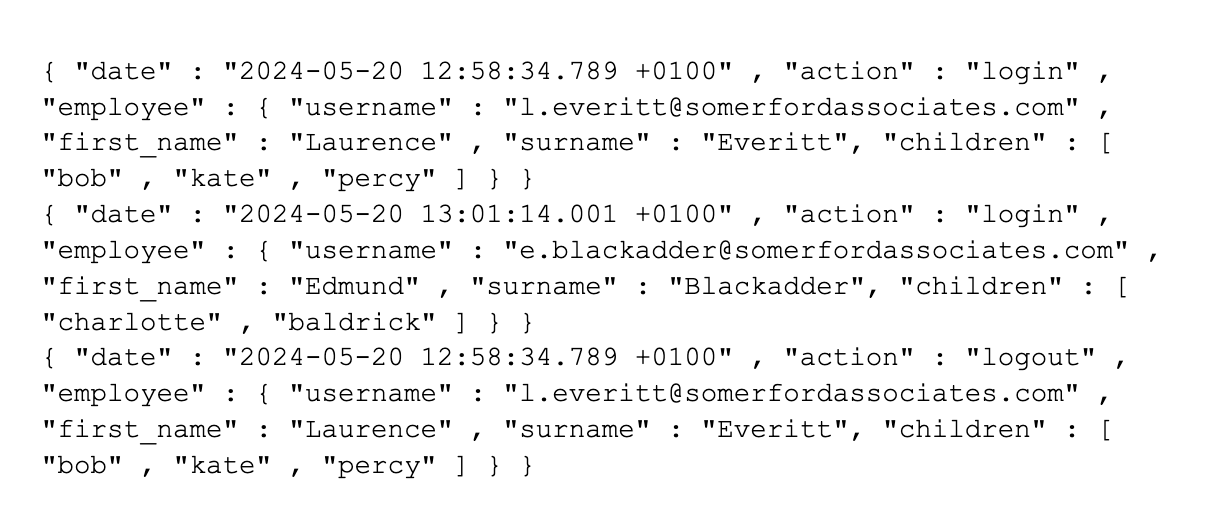
How to Format JSON Data Ready for Splunk - Somerford Associates

Solved: How to parse and extract field from my raw data? - Splunk Community
How to Simulate Data Flow and Pulling Logs From AWS to Splunk | Splunk
Advertisement Space (336x280)

Solved: How to create sample JSON data and display it in a... - Splunk ...
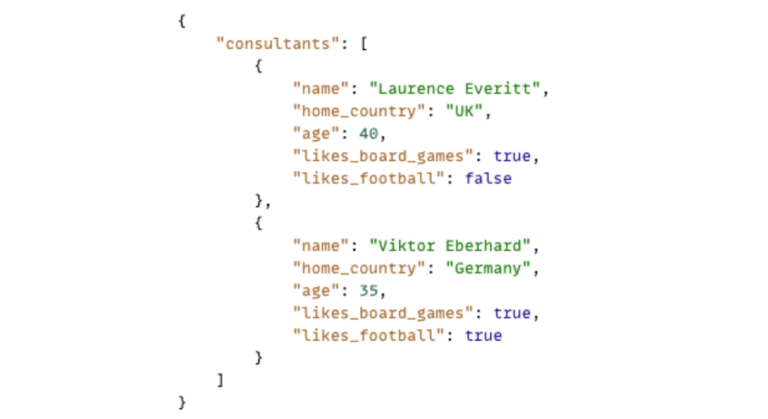
How to Format JSON Data Ready for Splunk - Somerford Associates
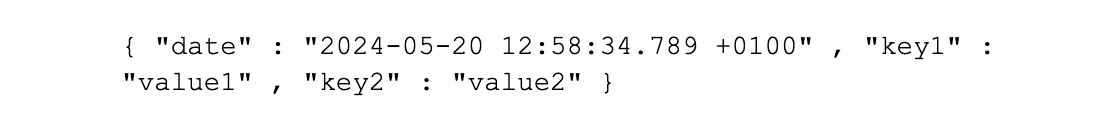
How to Format JSON Data Ready for Splunk - Somerford Associates

How do I extract multiple fields from a json array... - Splunk Community

Tech Talk | How to Use Logs from Splunk Platform i... - Splunk Community

Solved: How to parse my JSON data with spath and table the... - Splunk ...
How to Simulate Data Flow and Pulling Logs From AWS to Splunk | Splunk
How to Simulate Data Flow and Pulling Logs From AWS to Splunk | Splunk
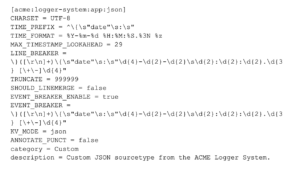
How to Format JSON Data Ready for Splunk - Somerford Associates
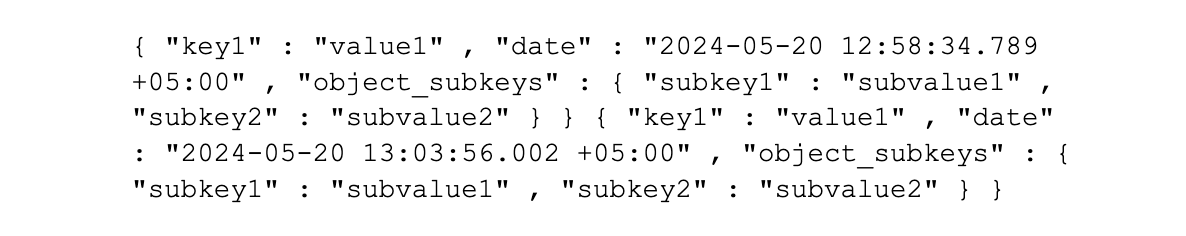
How to Format JSON Data Ready for Splunk - Somerford Associates
Advertisement Space (336x280)
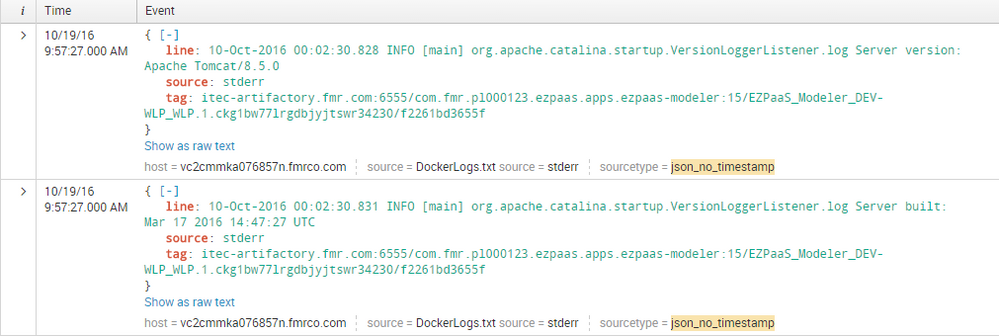
Solved: Extract fields in JSON during index time - Splunk Community

Solved: Extract fields in JSON during index time - Splunk Community

Solved: Extract json fields - Splunk Community

Solved: Extract fields in JSON during index time - Splunk Community

Solved: Extract fields in JSON during index time - Splunk Community
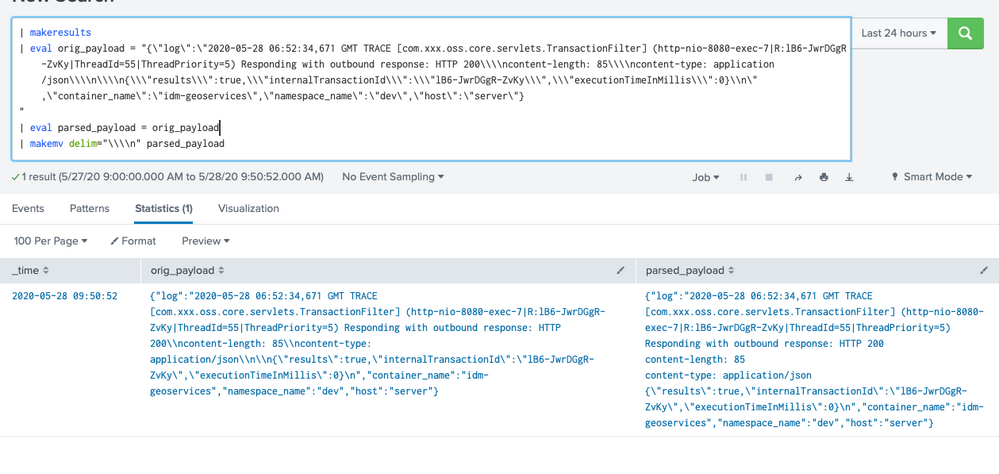
Solved: In a JSON Payload, parse out \n to newline - Splunk Community