
Ingesting Azure Data Into The Splunk Platform This Lantern Article

Ingesting Azure data into the Splunk platform? This Lantern article ...

Getting Microsoft Azure data into the Splunk platform - Splunk ...
Getting Microsoft Azure data into the Splunk platform | Splunk ...
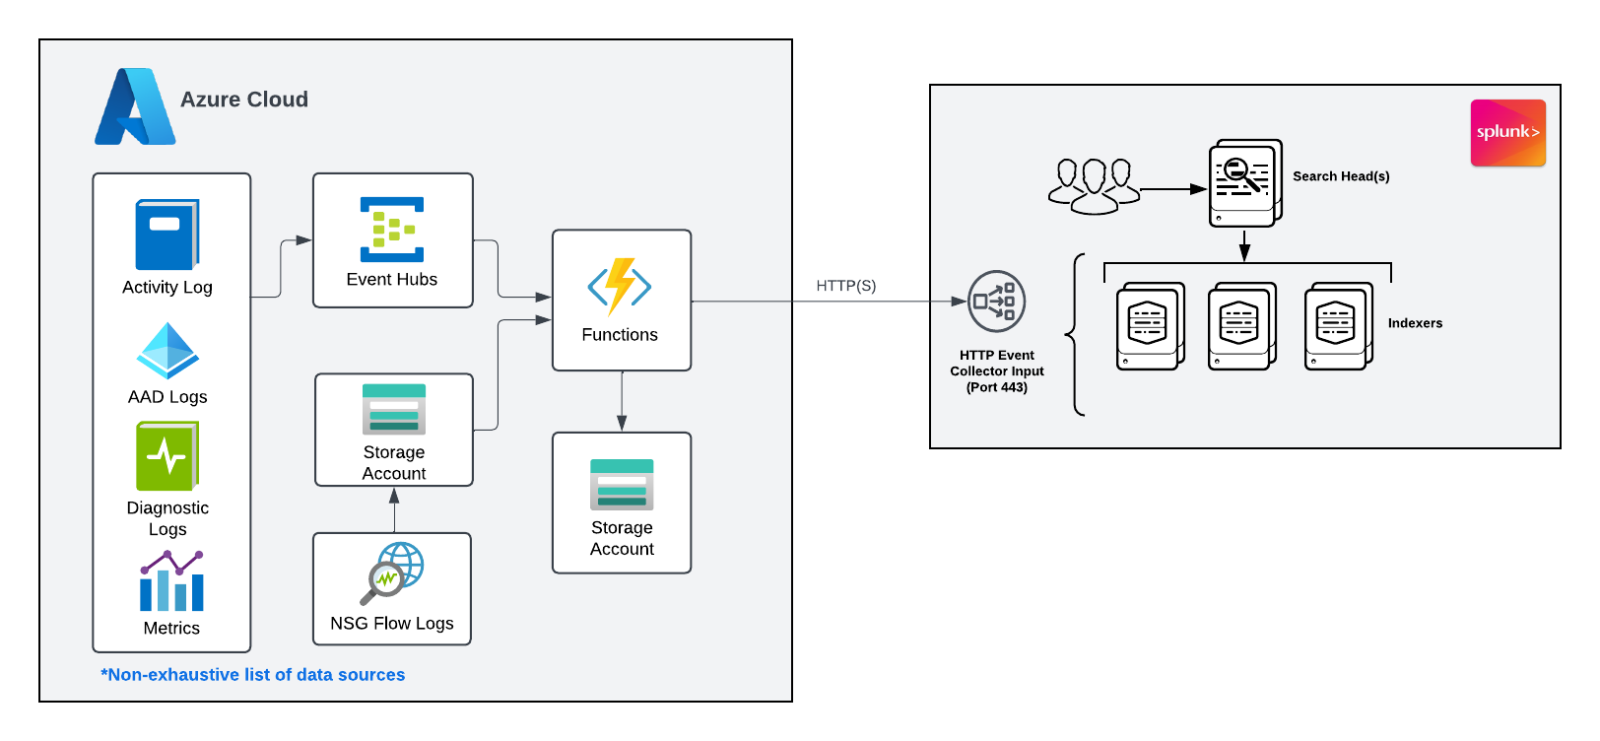
Getting Microsoft Azure data into the Splunk platform - Splunk ...

Getting Microsoft Azure data into the Splunk platform - Splunk ...
Getting Microsoft Azure data into the Splunk platform | Splunk ...
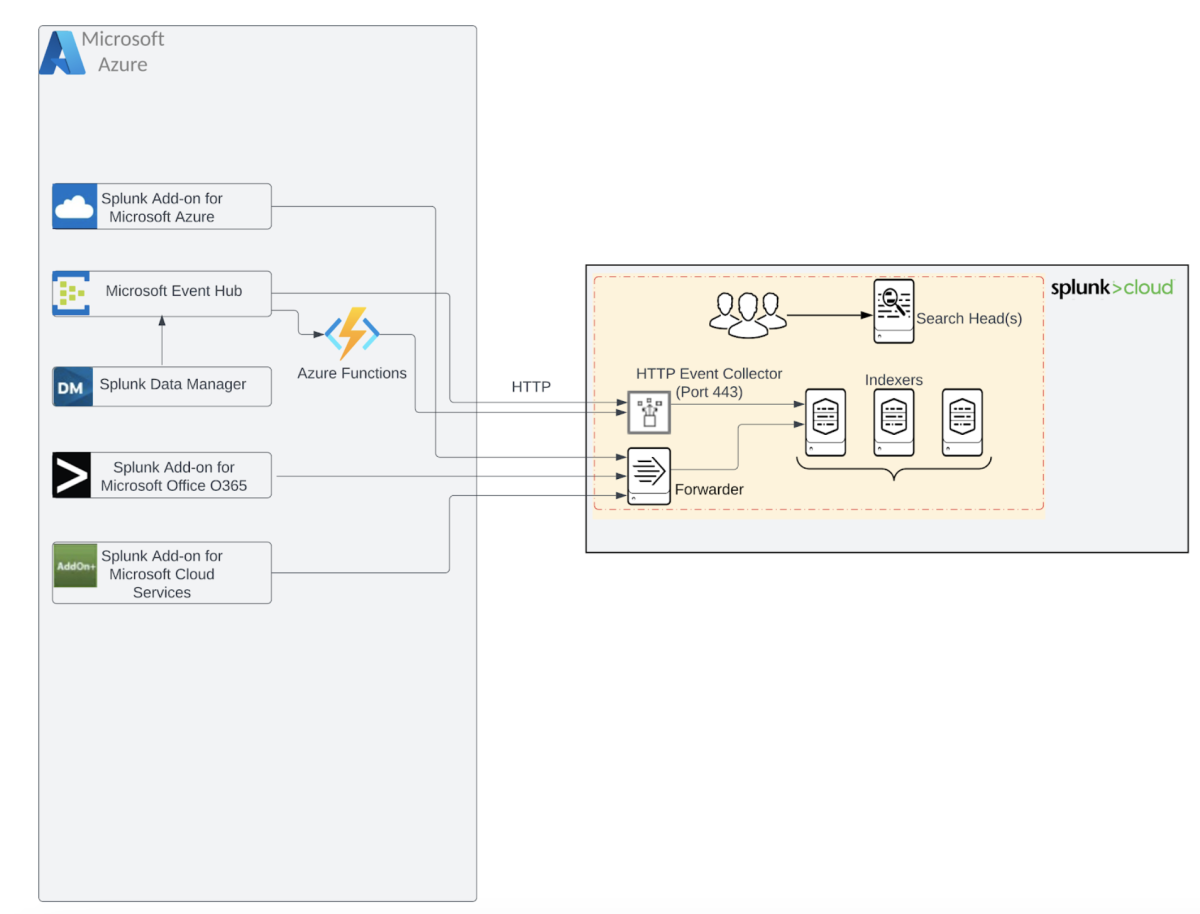
Getting Microsoft Azure data into the Splunk platform - Splunk ...

Getting Microsoft Azure data into the Splunk platform - Splunk ...

Ingesting Azure Data into Splunk - iDelta | iDelta Ltd.

Getting data into the Splunk platform is straightforward most of the ...
Advertisement Space (300x250)
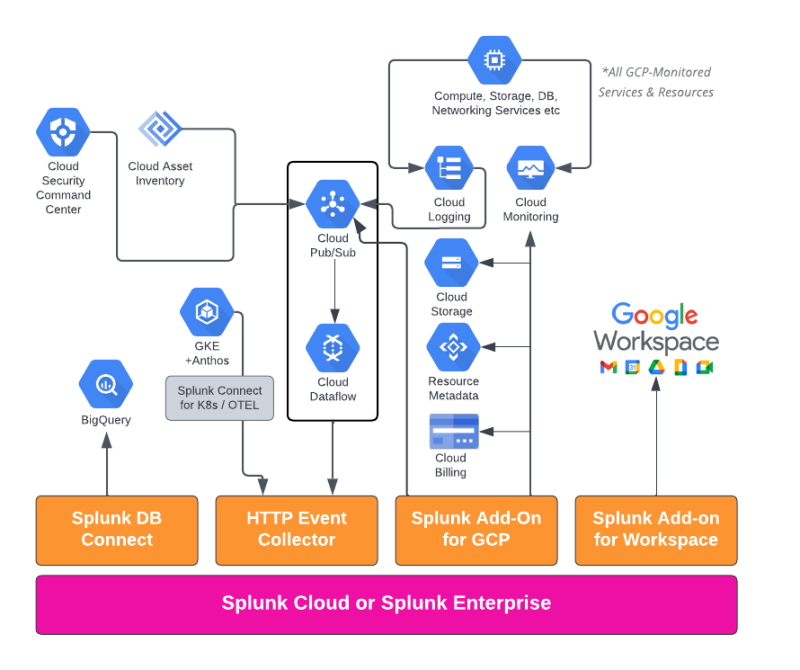
Getting Google Cloud Platform data into the Splunk platform - Splunk ...
Get Microsoft Azure data into Splunk Cloud Platform | Splunk Cloud ...

Add Azure To Splunk , Get Microsoft Azure data into Splunk Cloud ...
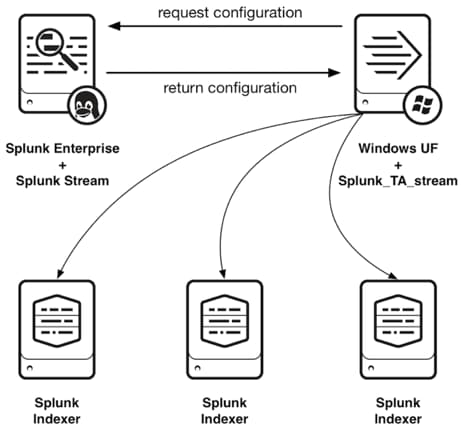
Getting Microsoft Azure Data into Splunk | Splunk
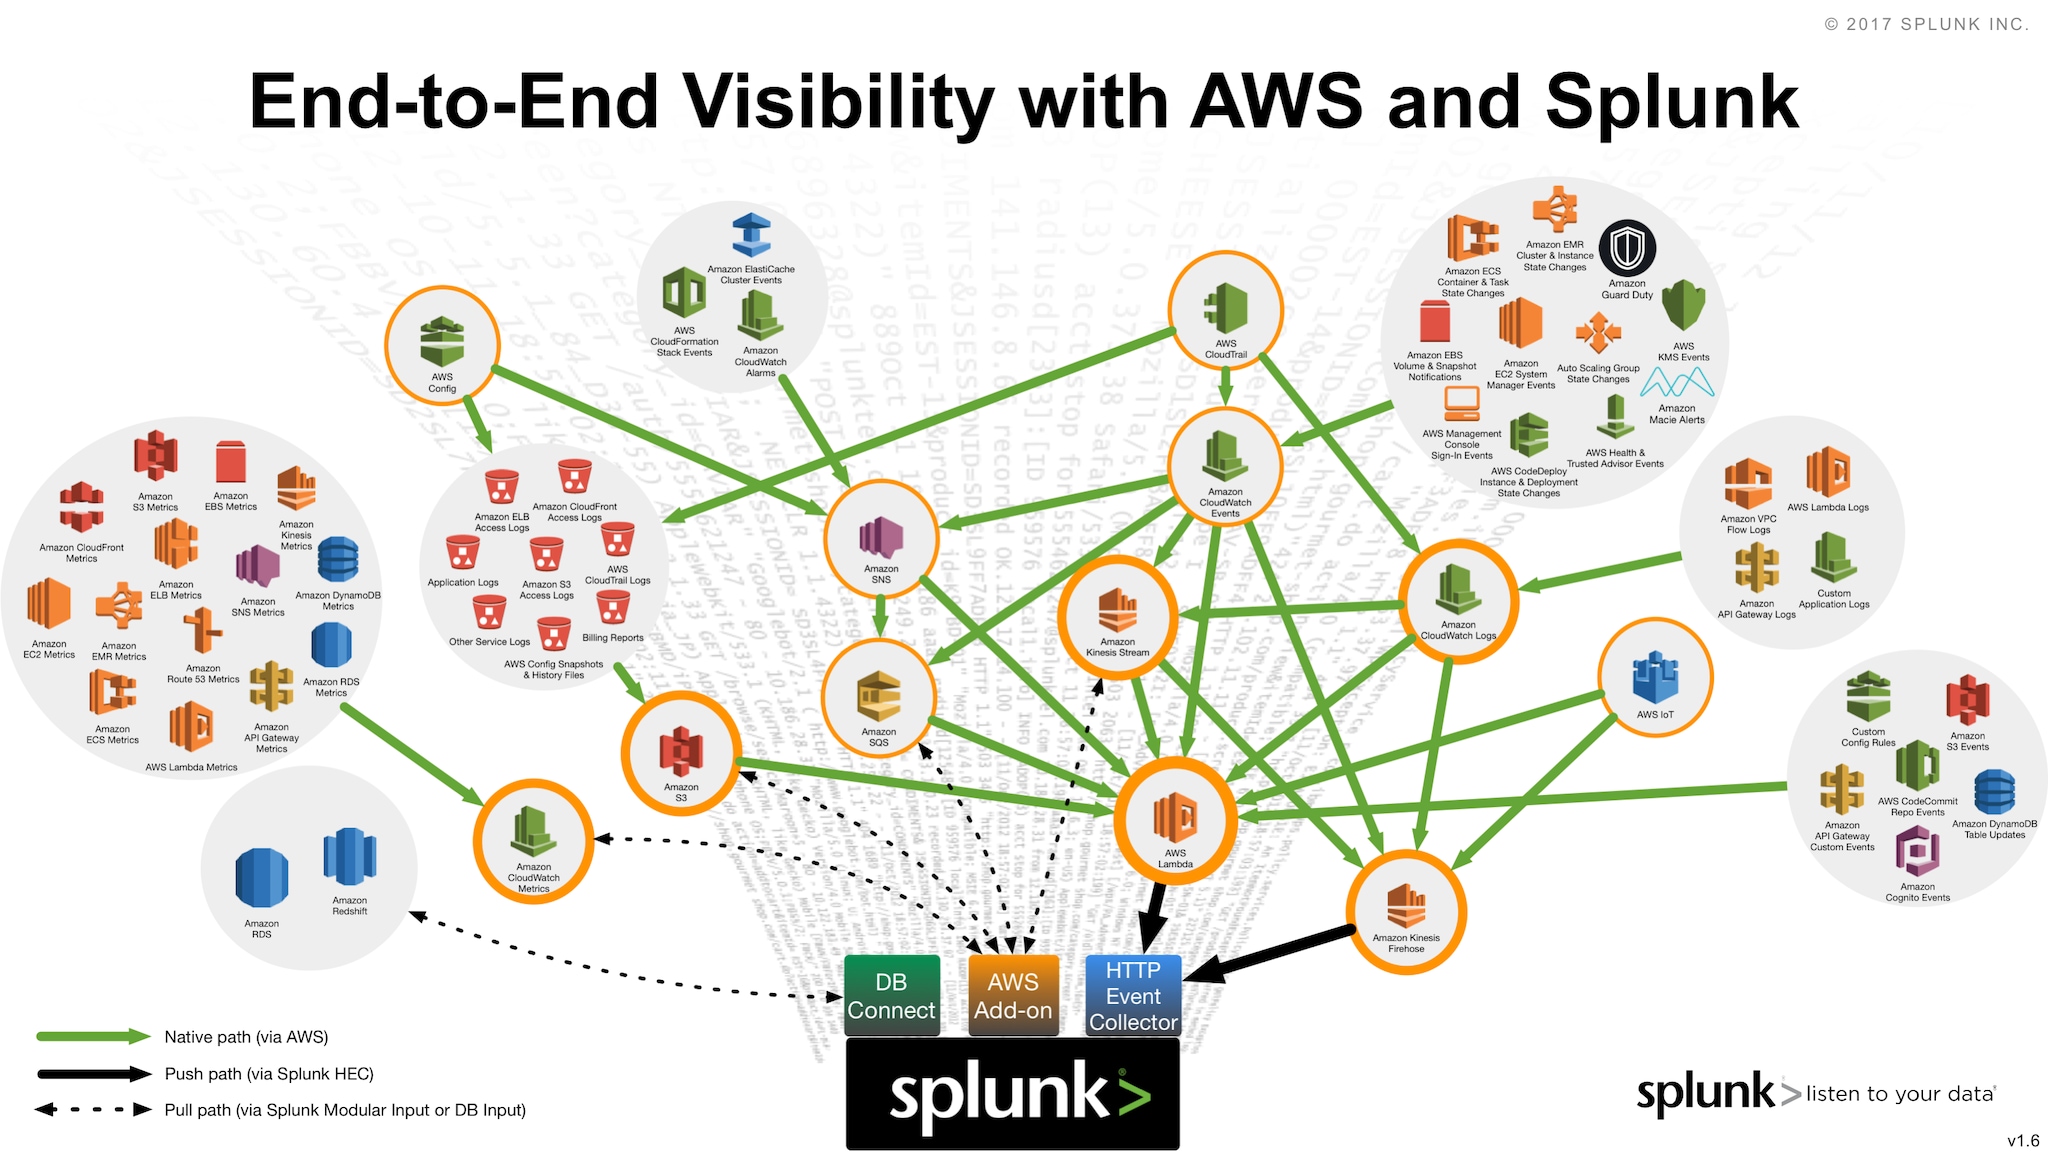
Getting Microsoft Azure Data into Splunk | Splunk
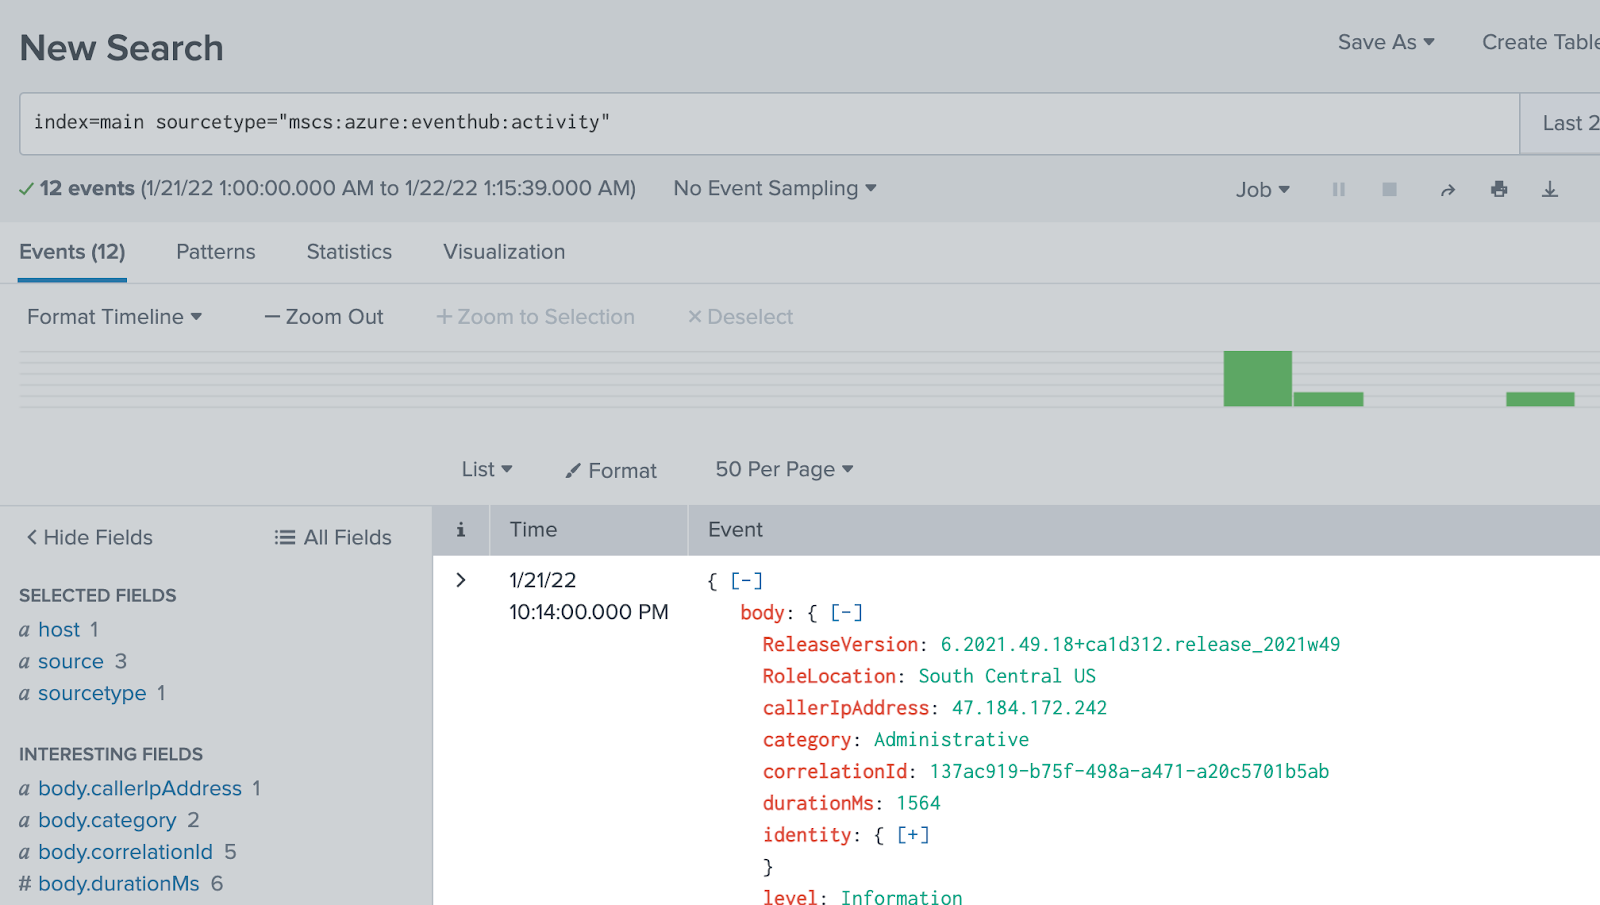
Getting started with Microsoft Azure Event Hub data - Splunk Lantern
Getting Microsoft Azure Data into Splunk | Splunk
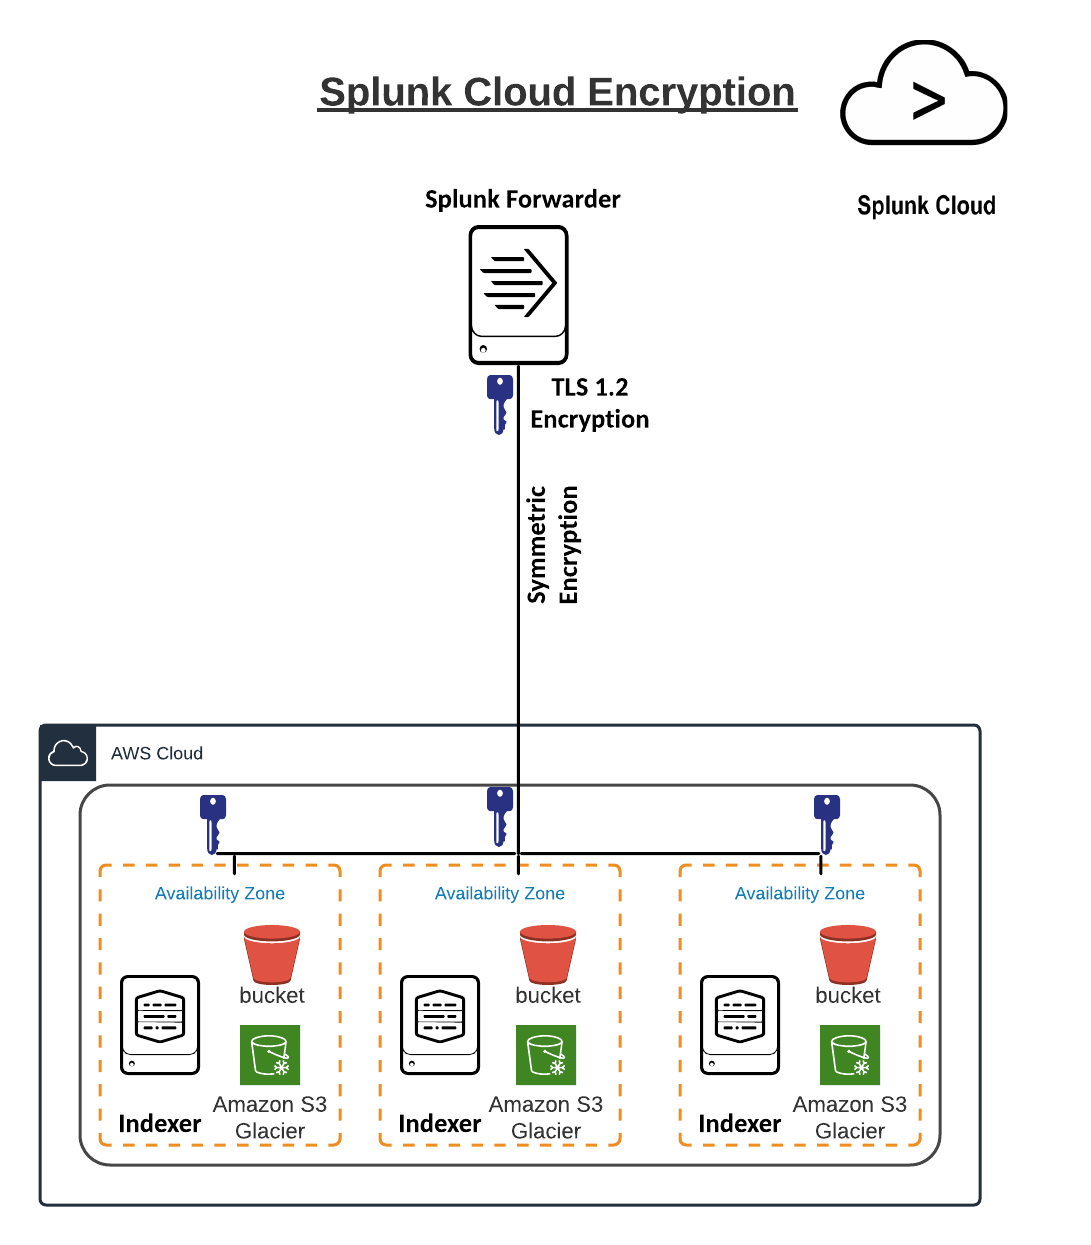
Securing the Splunk Cloud Platform - Splunk Lantern

Onboarding and managing data in Cloud Platform - Splunk Lantern
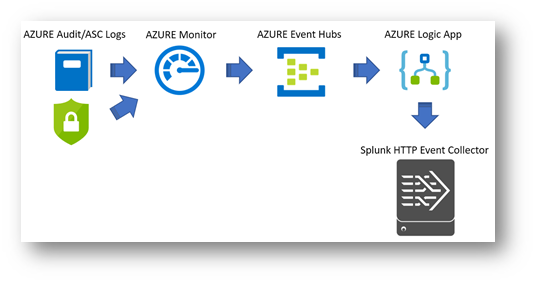
Add Azure To Splunk , Get Microsoft Azure data into Splunk Cloud ...
Advertisement Space (336x280)
Get Azure Key Vault Data into Splunk | Pwntario Team Blog

Getting started with Microsoft Azure Event Hub data - Splunk Lantern

Getting started with Microsoft Azure Event Hub data - Splunk Lantern
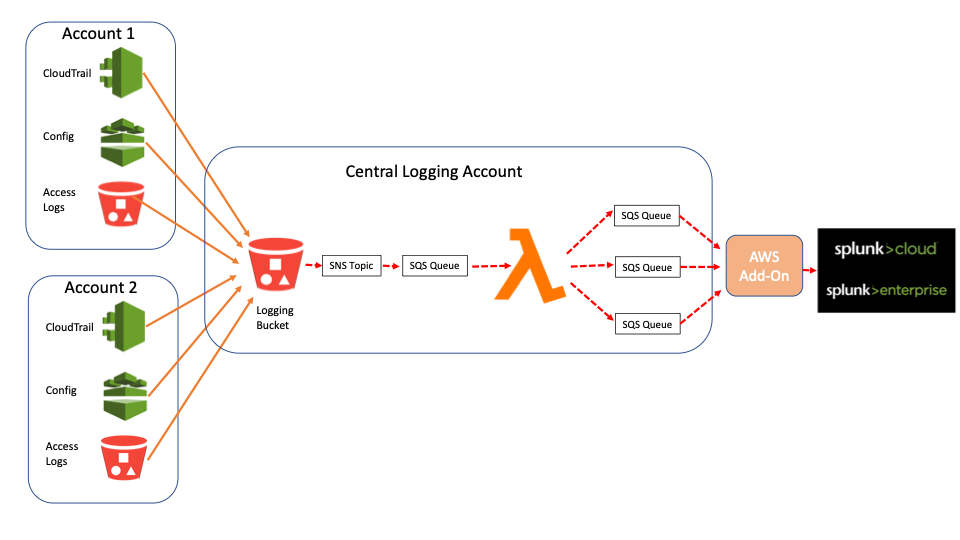
Getting Microsoft Azure Data into Splunk | Splunk

Getting started with Microsoft Azure Event Hub data - Splunk Lantern
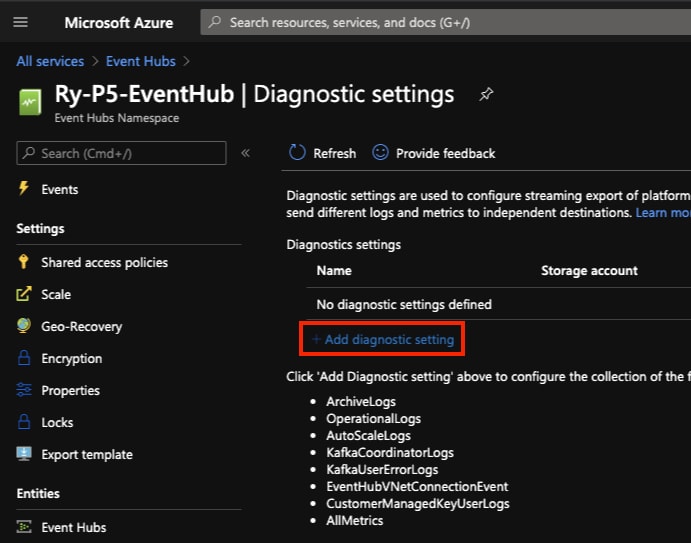
Add Azure To Splunk , Get Microsoft Azure data into Splunk Cloud ...
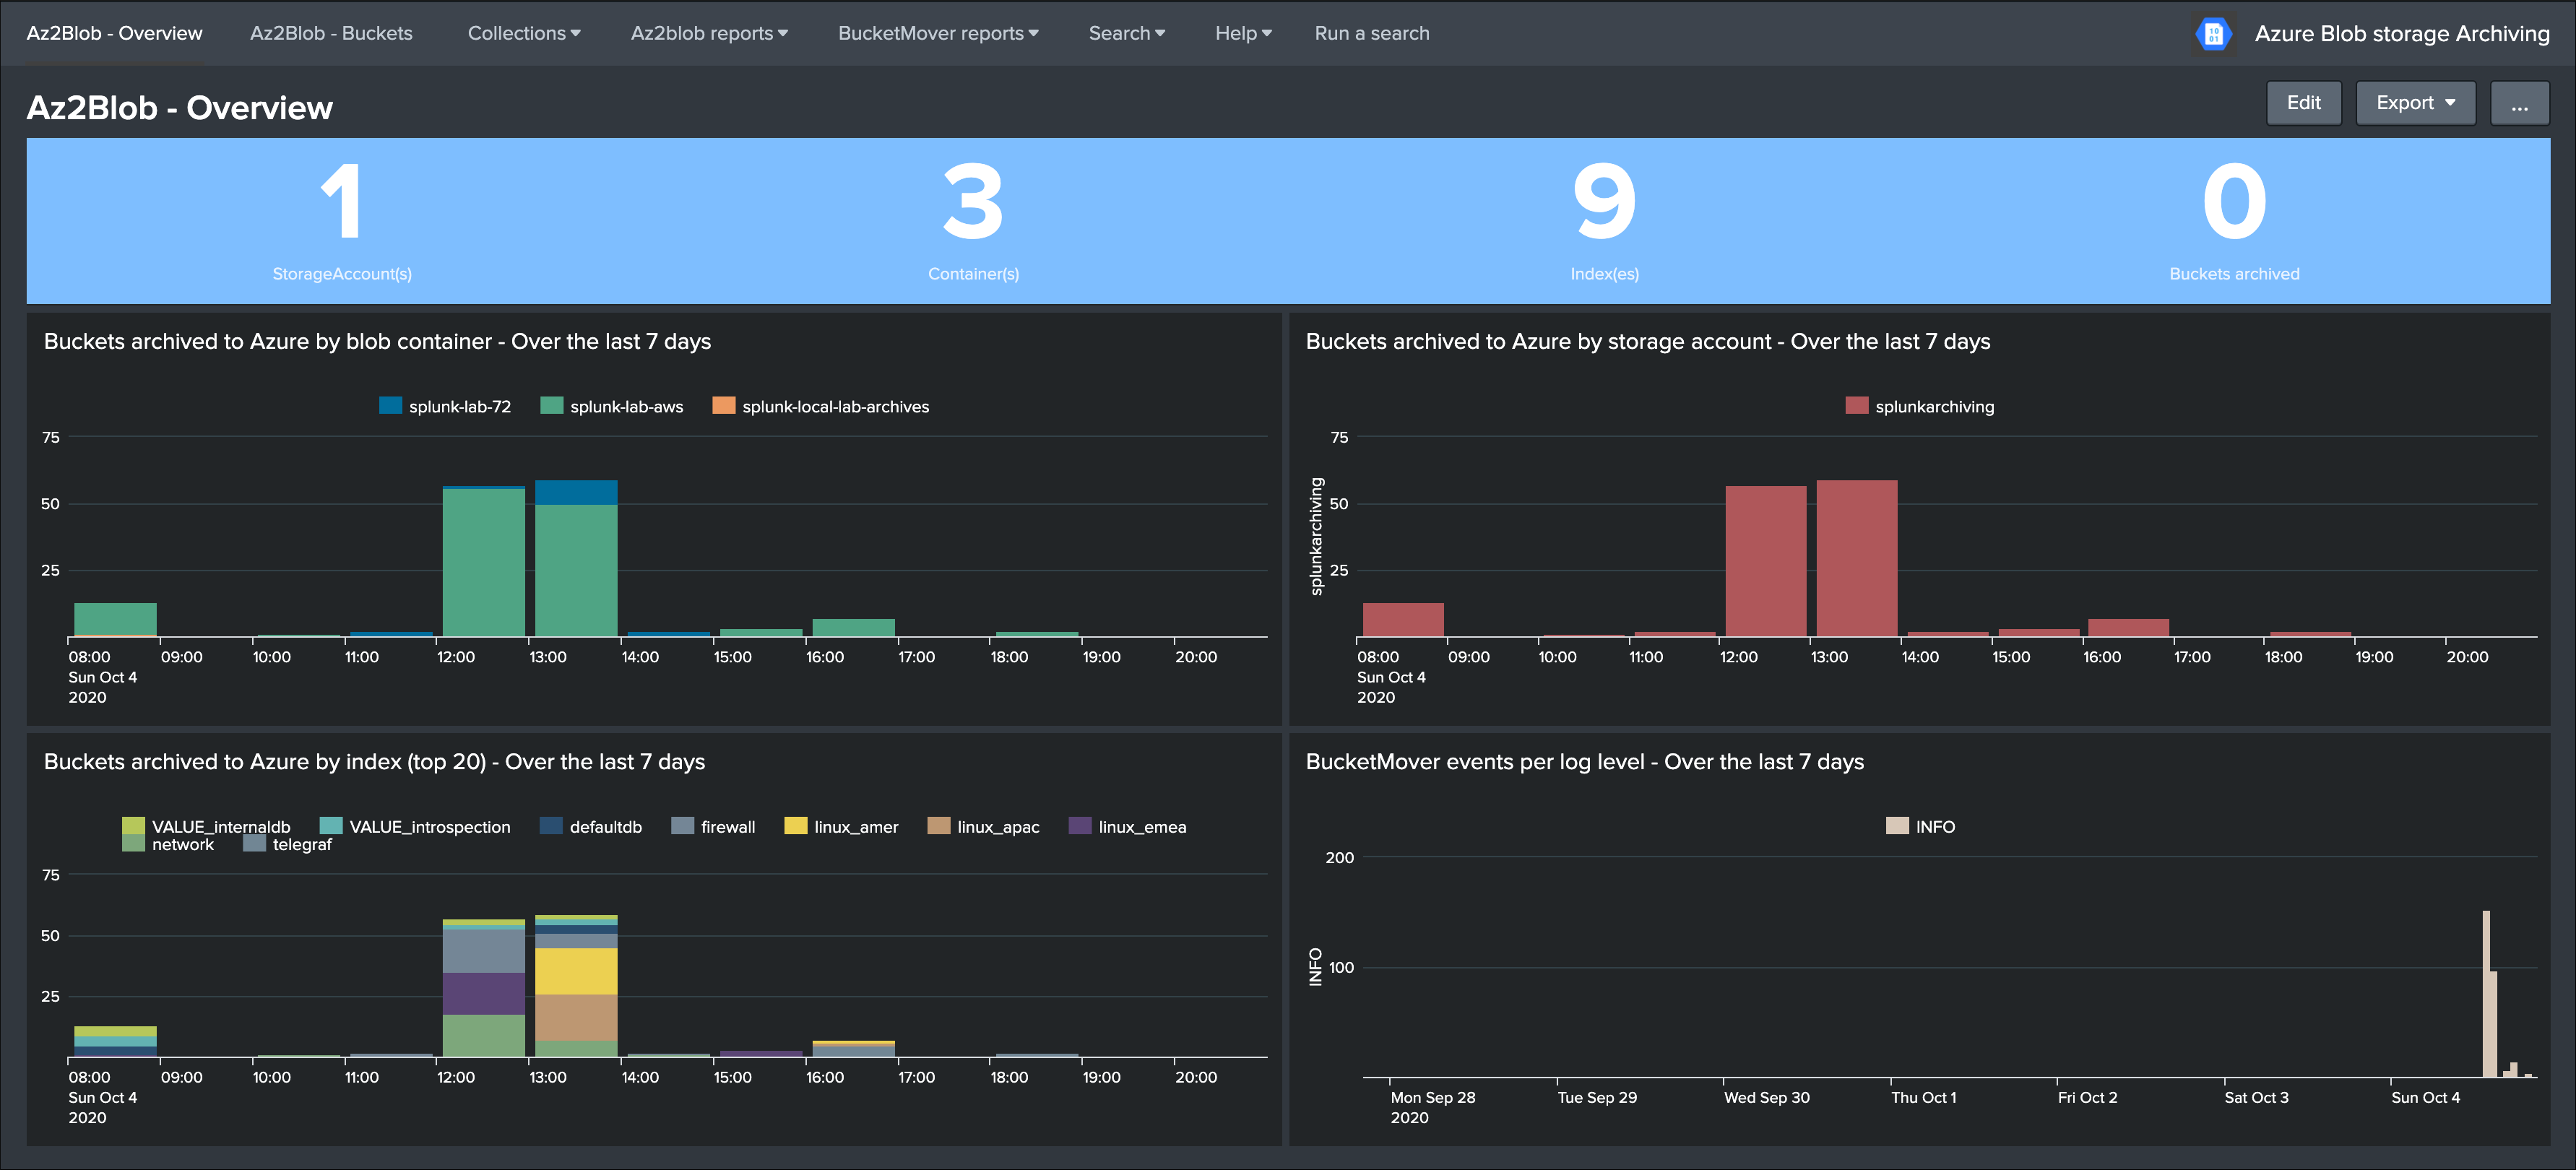
Add Azure To Splunk , Get Microsoft Azure data into Splunk Cloud ...

Getting Docker log data into Splunk Cloud Platform with OpenTelemetry ...
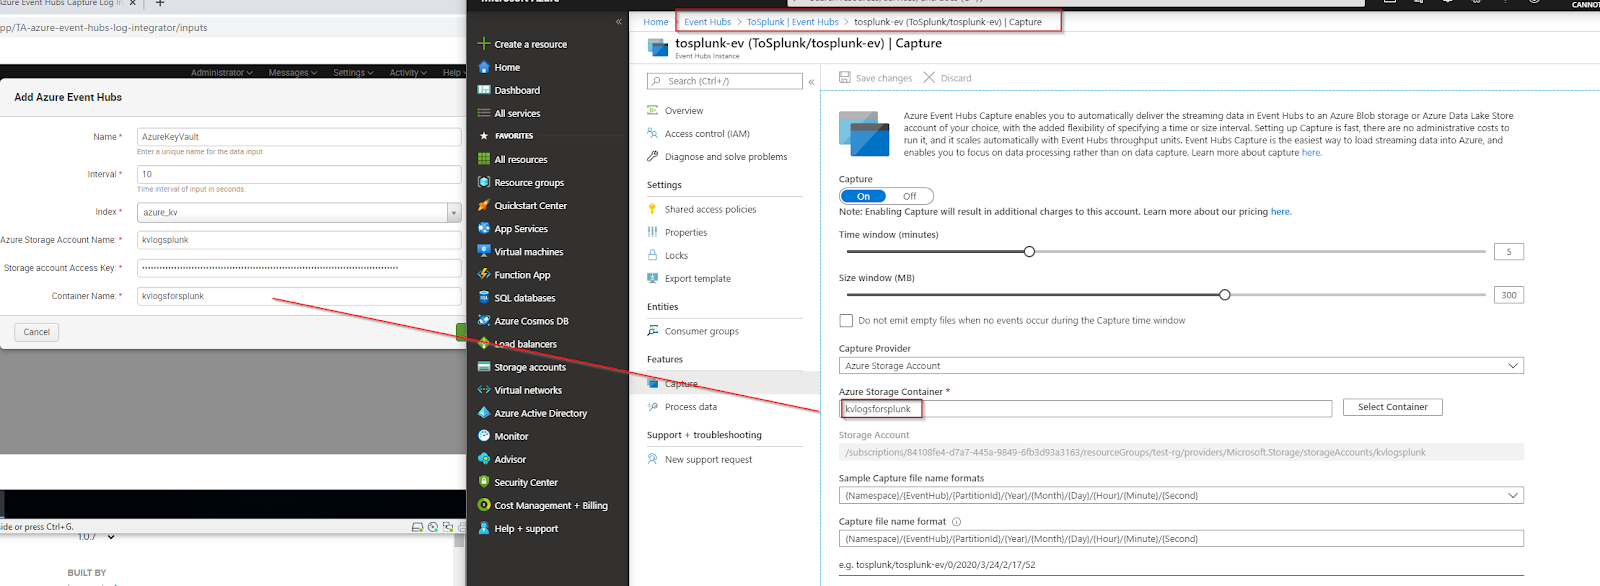
Get Azure Key Vault Data into Splunk | Pwntario Team Blog

Getting started with Microsoft Azure Event Hub data - Splunk Lantern
Advertisement Space (336x280)

Getting started with Microsoft Azure Event Hub data - Splunk Lantern

Getting Docker log data into Splunk Cloud Platform with OpenTelemetry ...

How to use Splunk Universal Forwarder | Azure Data Explorer posted on ...
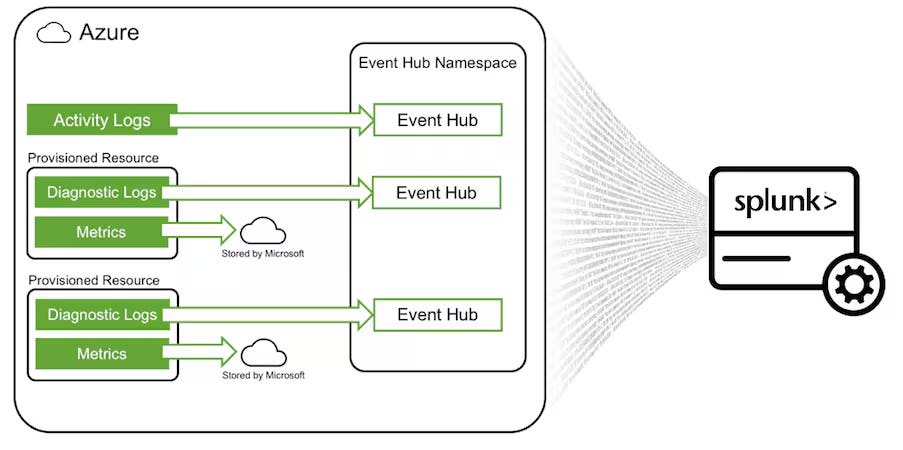
Splunking Microsoft Azure Monitor Data – Part 1 – Azure Setup | Splunk

Solved: How to get logs from Azure and O365 into Splunk? - Splunk Community
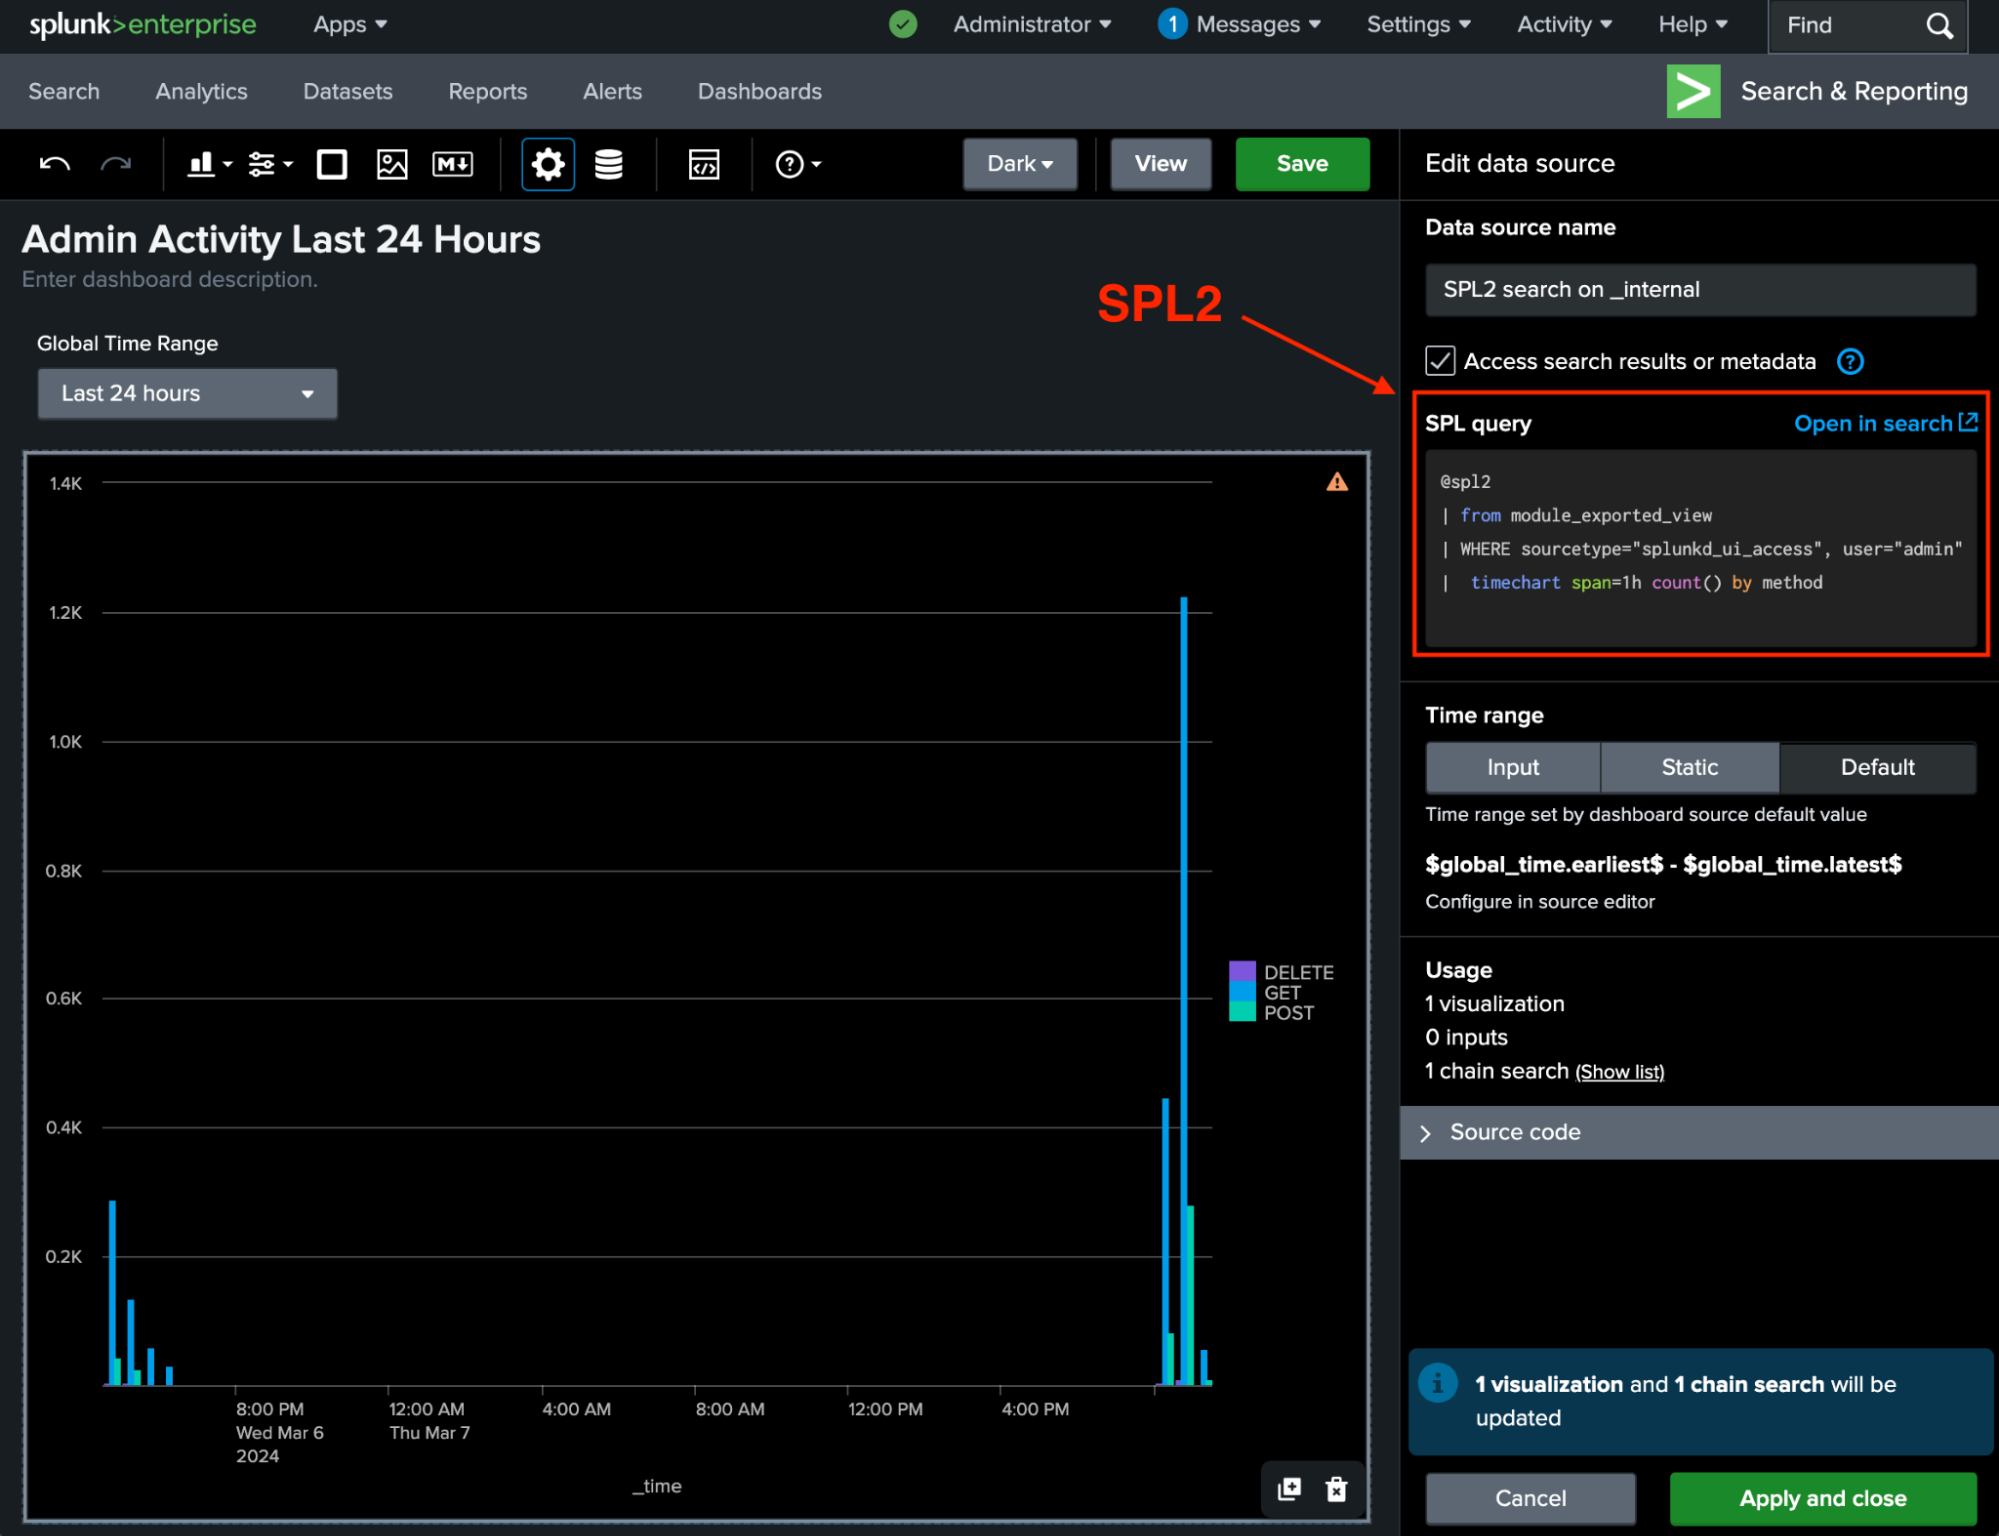
From Setup to Migration: Azure Event Hubs in Data Manager | Splunk