
Linux Platform Process Memory Malicious Code Evidence Obtaining Method
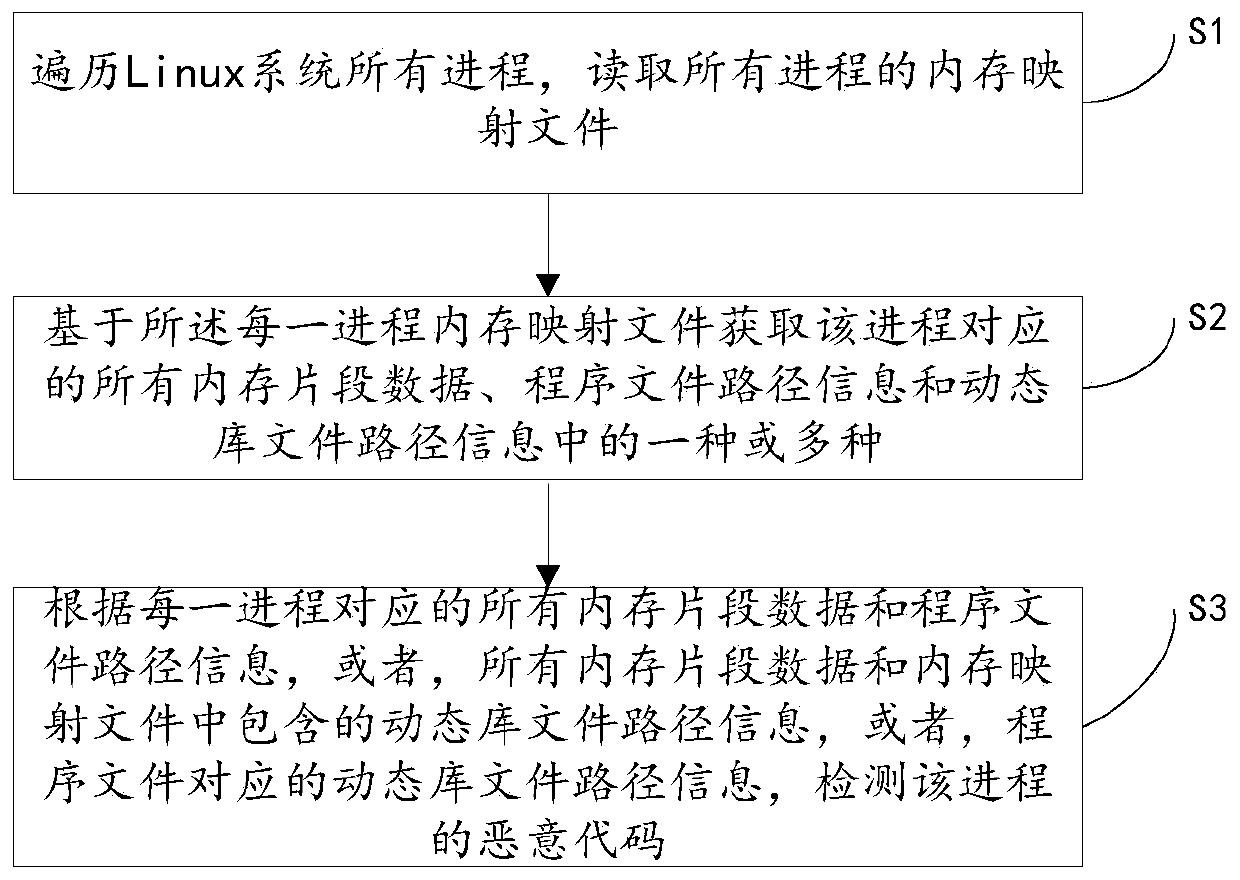
Linux platform process memory malicious code evidence obtaining method ...
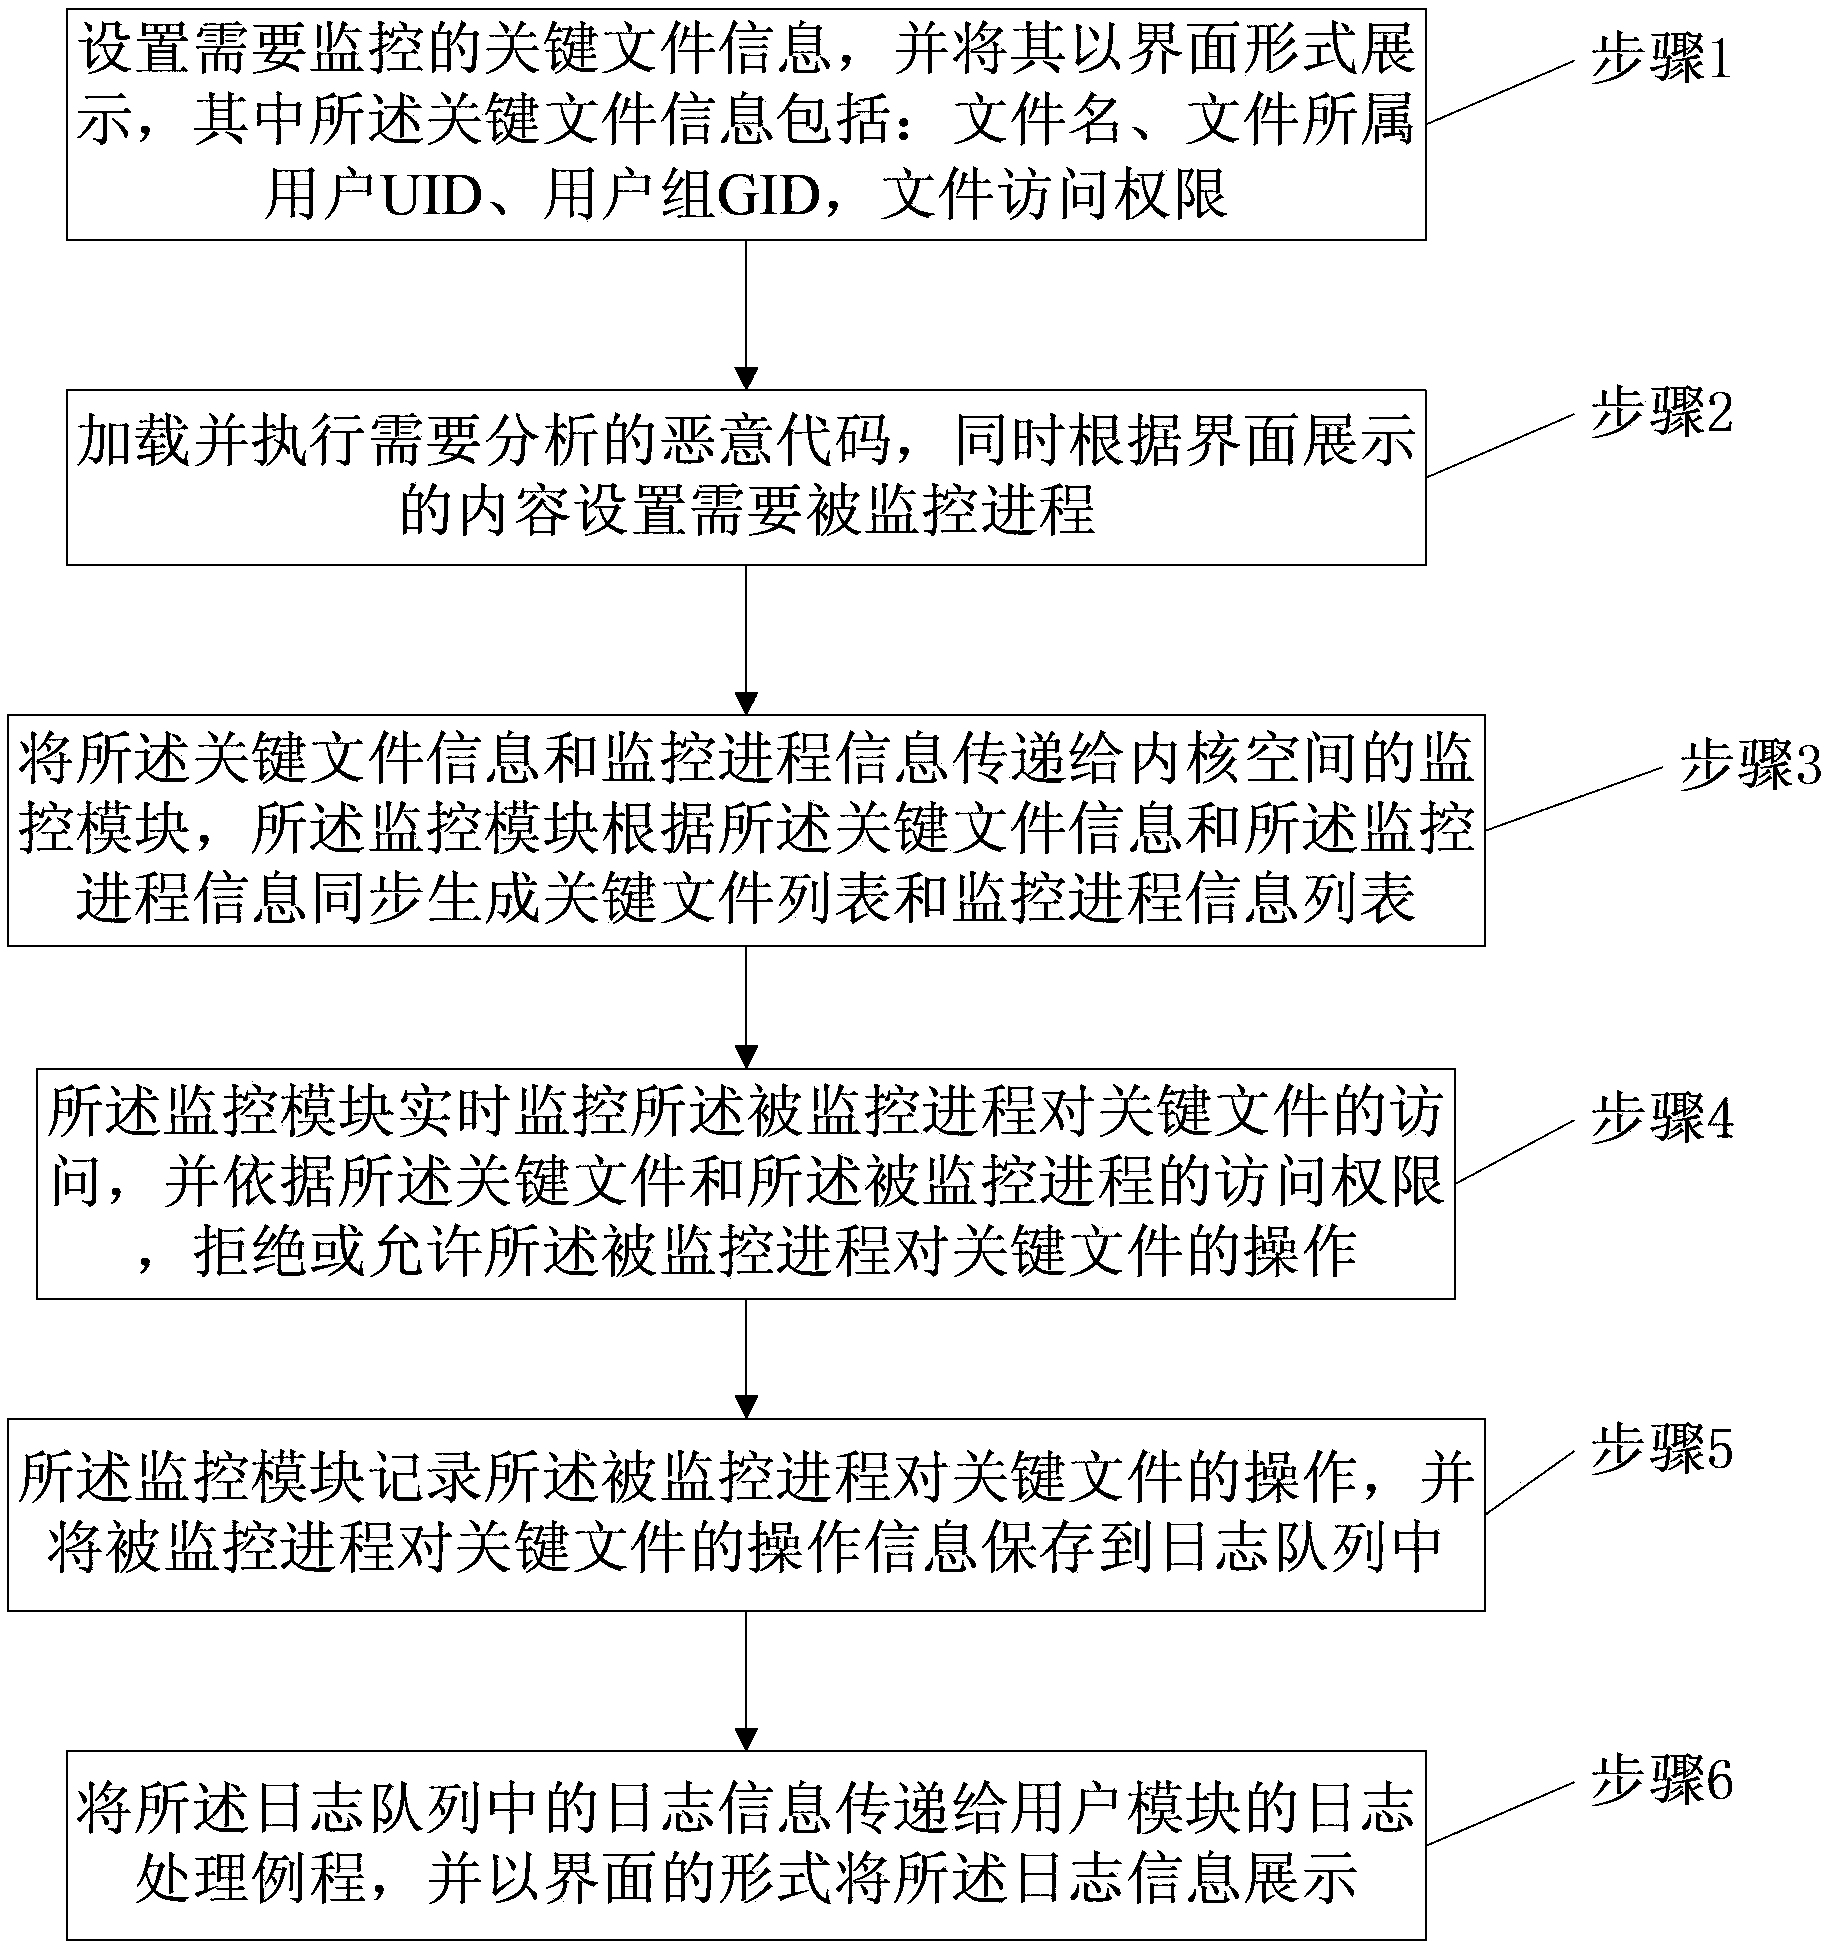
Malicious code analysis method and system under Linux platform - Eureka ...

How Linux maps binary code of a process in Memory - YouTube

A detection method of malicious software on linux platform - Eureka ...

ProcGCN: detecting malicious process in memory based on DGCNN - PMC
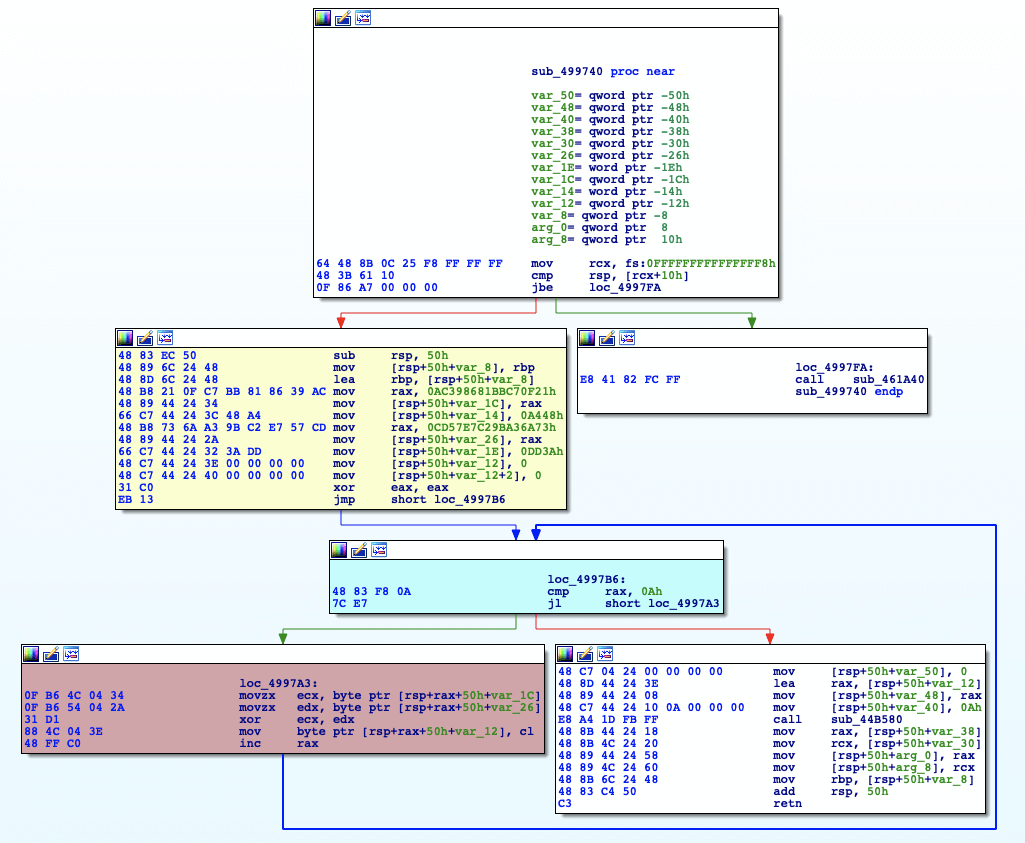
Identifying suspicious code with Process Memory Integrity
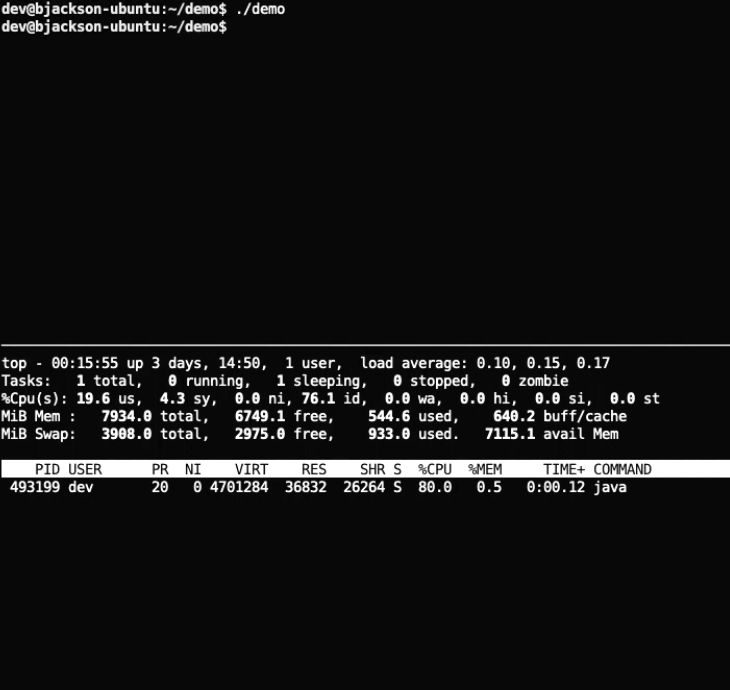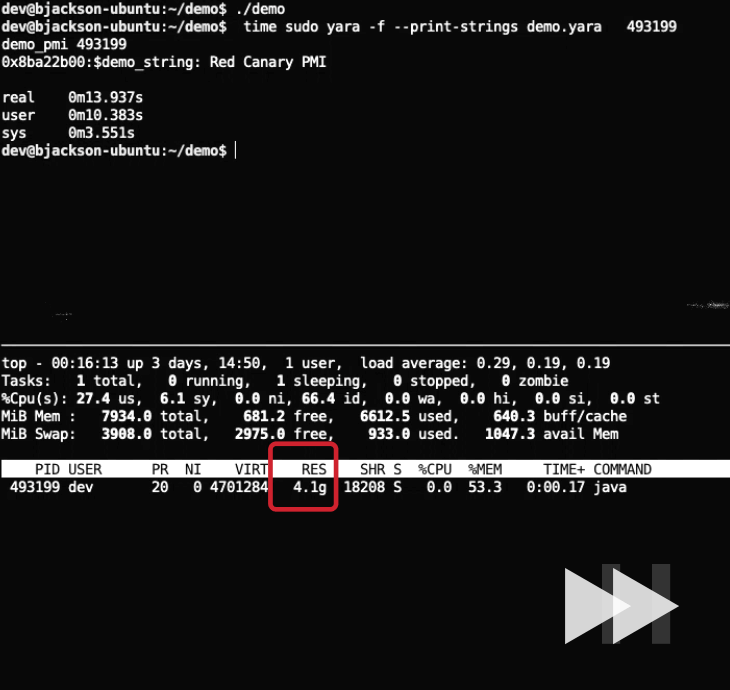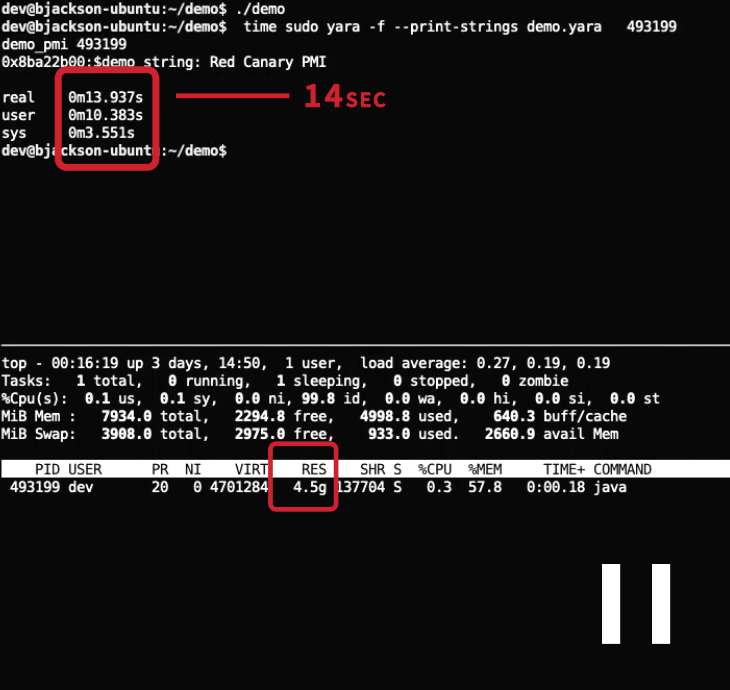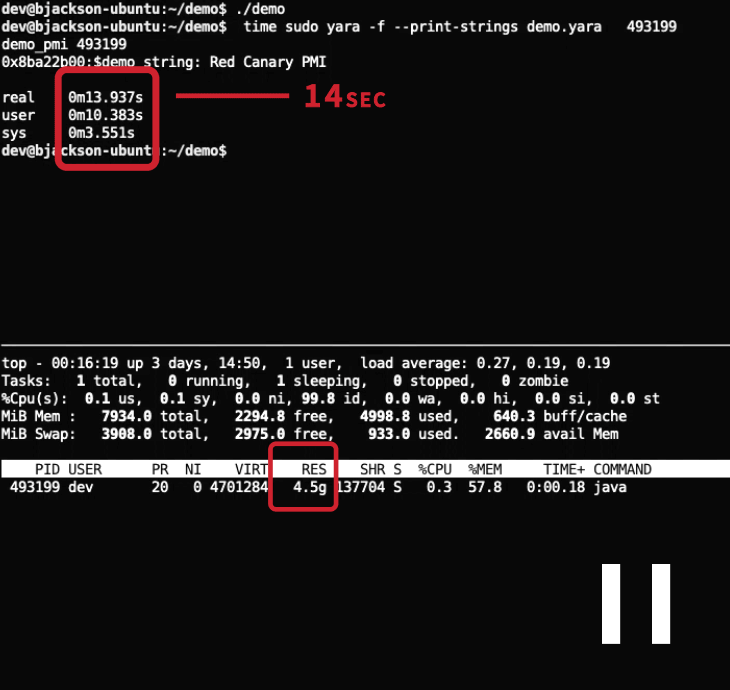
Identifying suspicious code with Process Memory Integrity
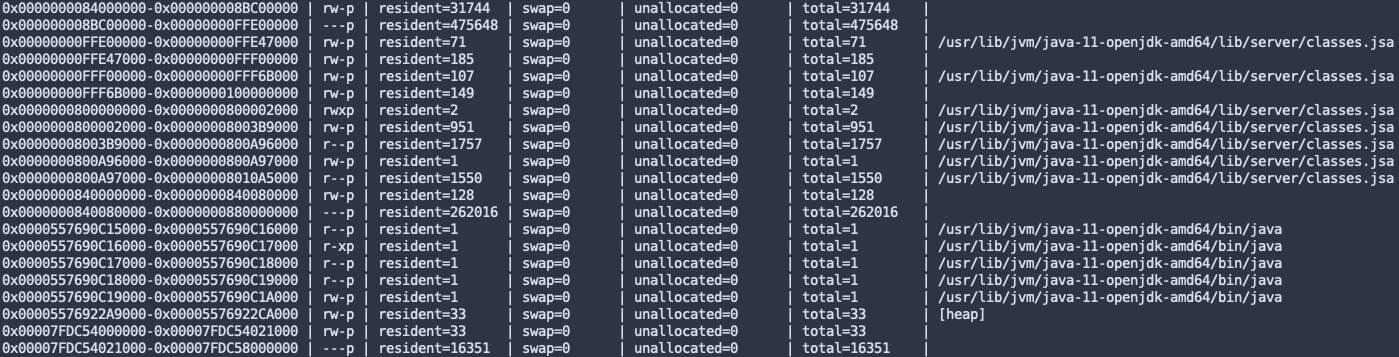
Identifying suspicious code with Process Memory Integrity

Checking process of malicious code | Download Scientific Diagram
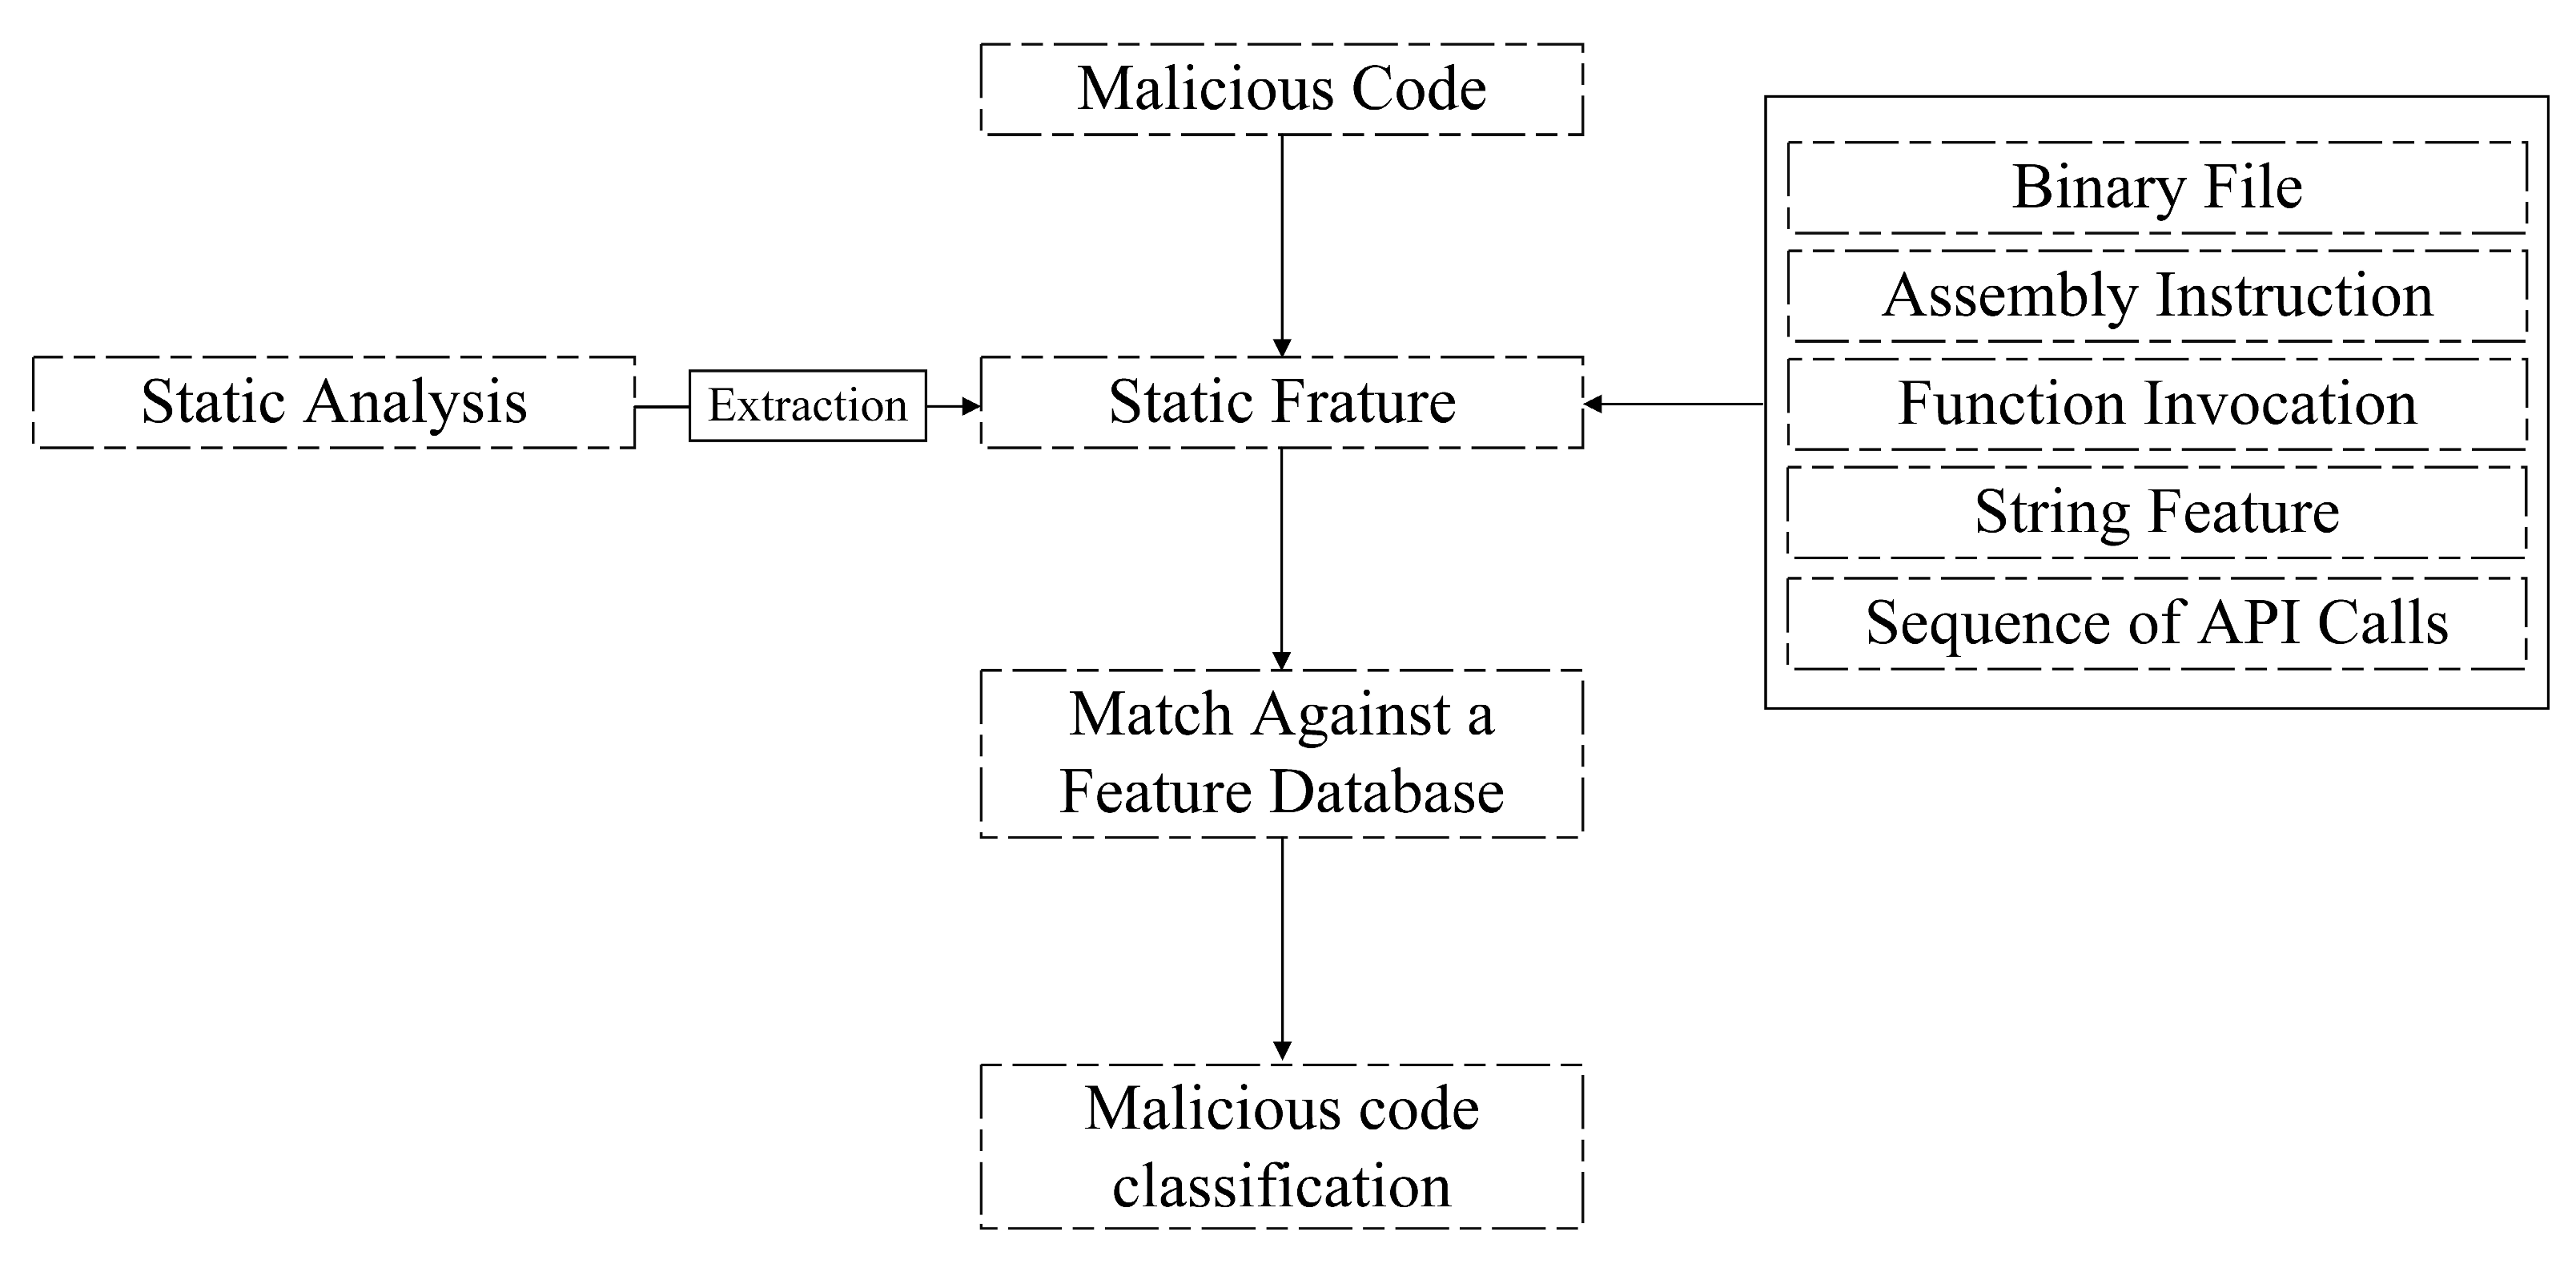
A Malicious Code Detection Method Based on Stacked Depthwise Separable ...
Advertisement Space (300x250)
CVE-2024-3094: Malicious Code in XZ Utils Enables RCE on Linux Systems

Malicious code detection method based on FF-MICNN. | Download ...
PPT - Exploiting the Linux Kernel: Malicious Code Injection via /dev ...

Malicious code detection method based on FF-MICNN. | Download ...

Evidence Collection in Linux Forensics (Disk + Memory Acquisition)

Checking process of malicious code | Download Scientific Diagram
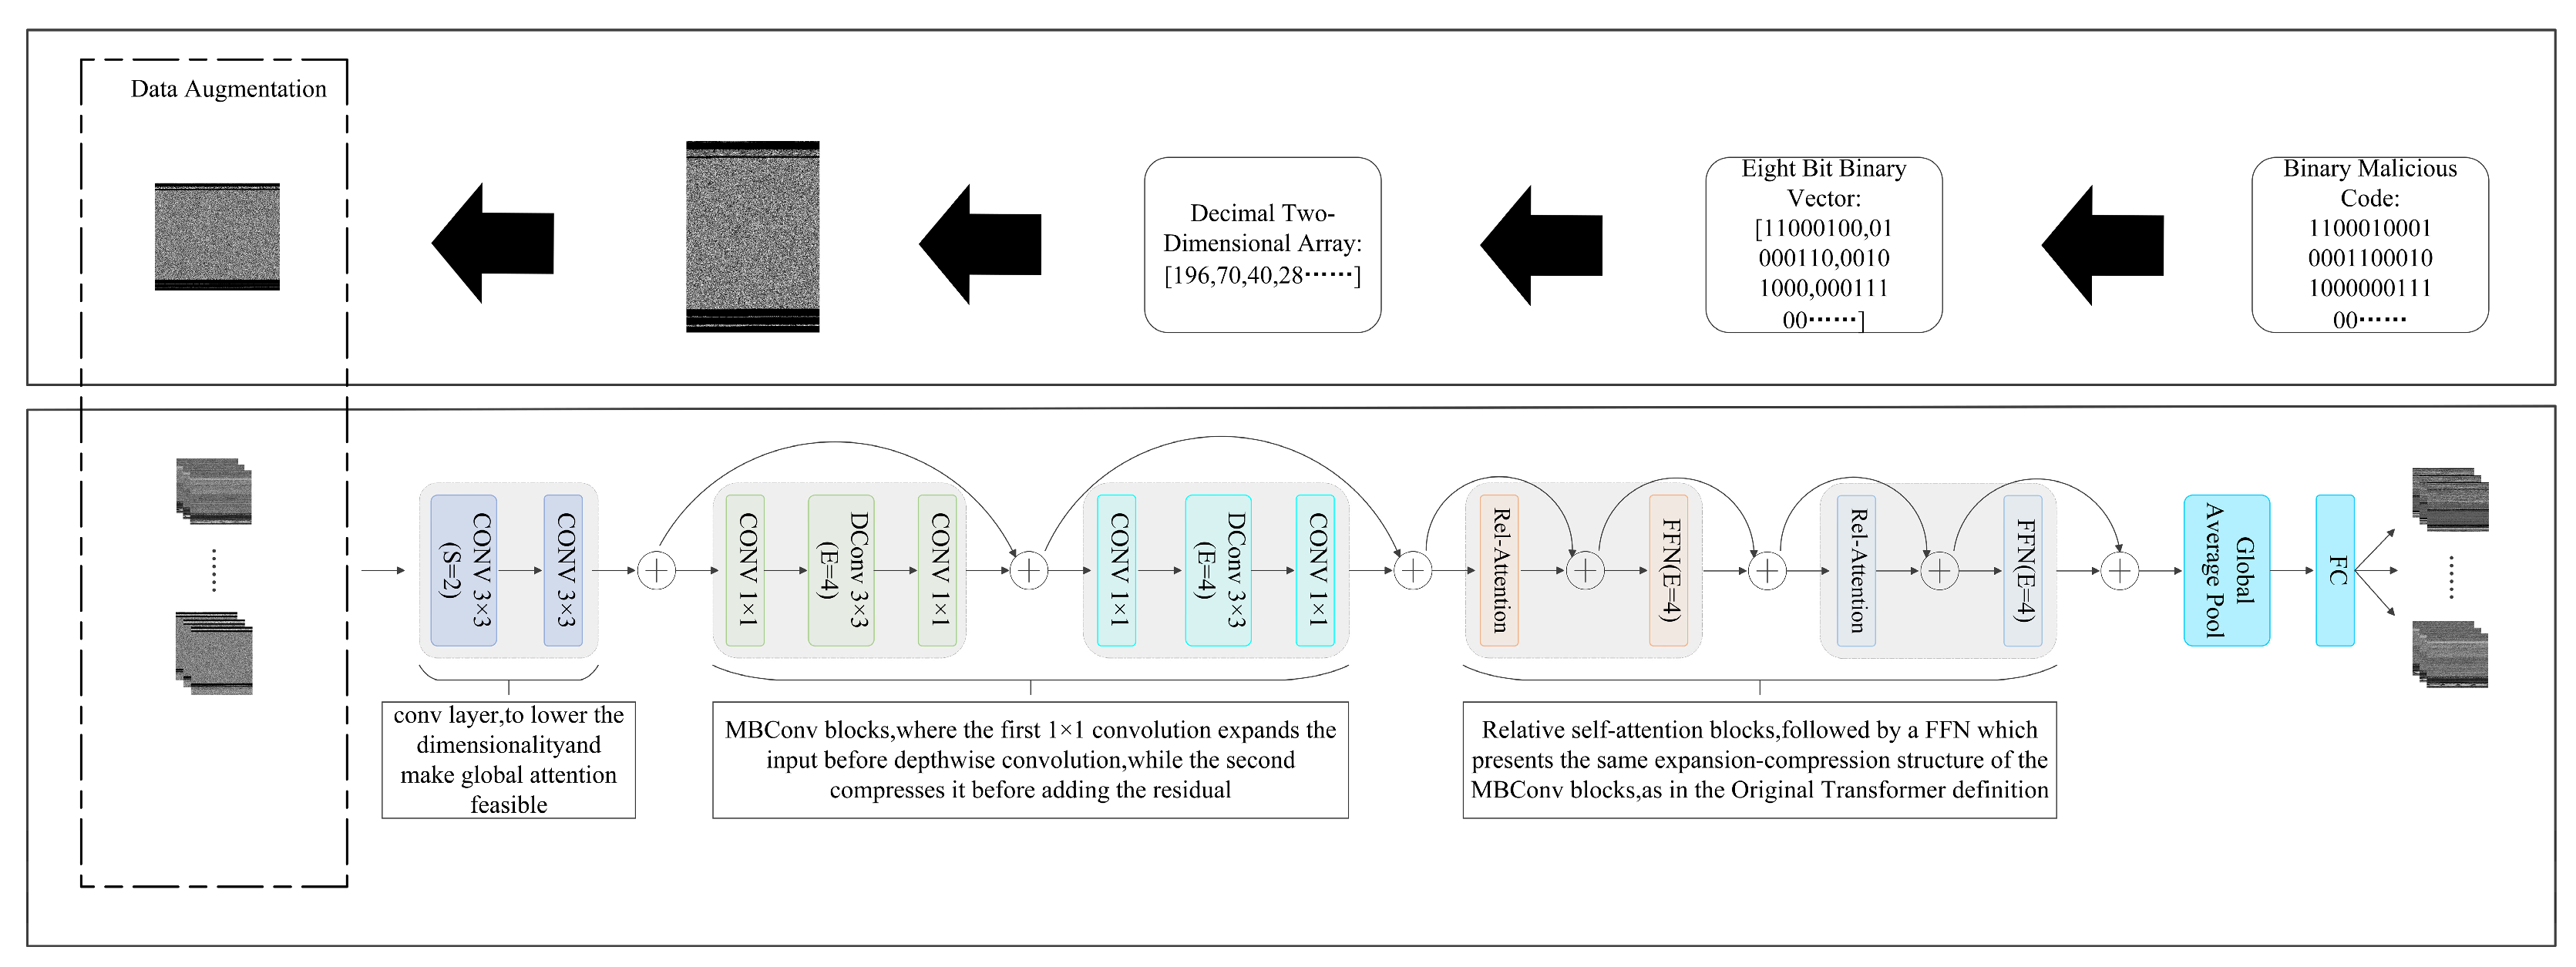
A Malicious Code Detection Method Based on Stacked Depthwise Separable ...
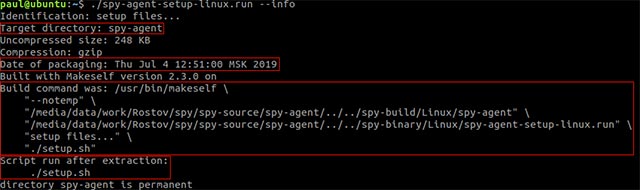
Malicious Code EvilGnome attacks Linux systems with many rare tricks

Memory Analysis of Malicious Code | PDF | Malware | Security

Malicious Code in XZ Utils for Linux Systems Enables Remote Code ...
Advertisement Space (336x280)
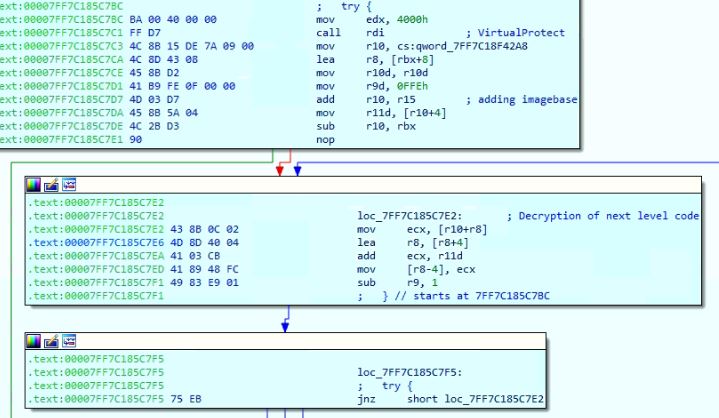
Novel Malicious code evasion method for AI/ML based detection

(PDF) A Malicious Code Detection Method Based on Stacked Depthwise ...

Diagram of detection method for malicious code based on transfer ...

Memory Corruption Vulnerability in Linux "Memory Safe" Rust Code - YouTube
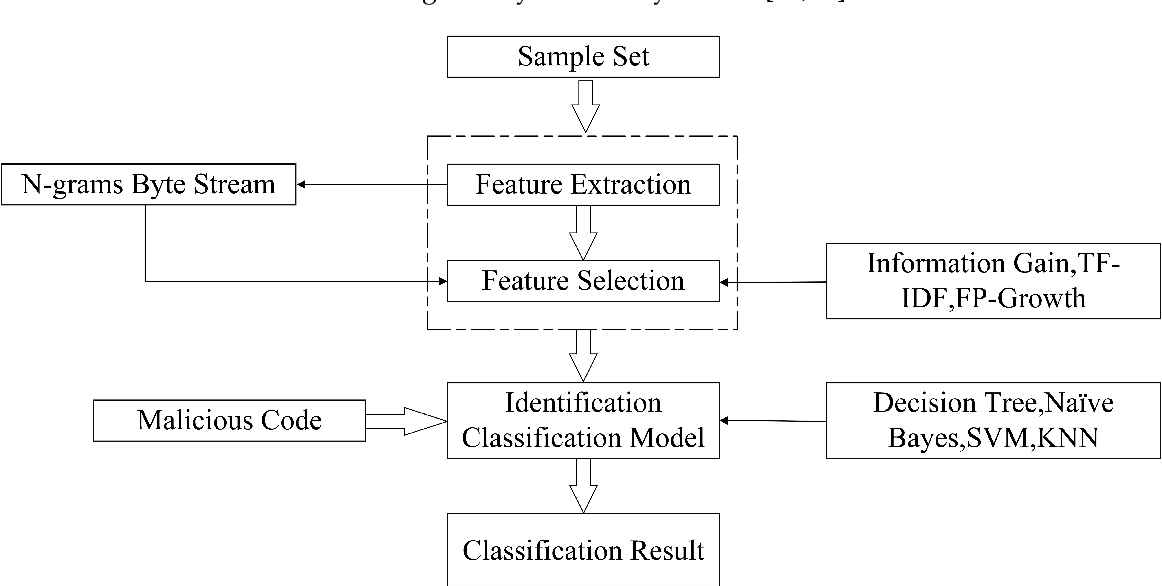
Figure 4 from A Malicious Code Detection Method Based on Stacked ...
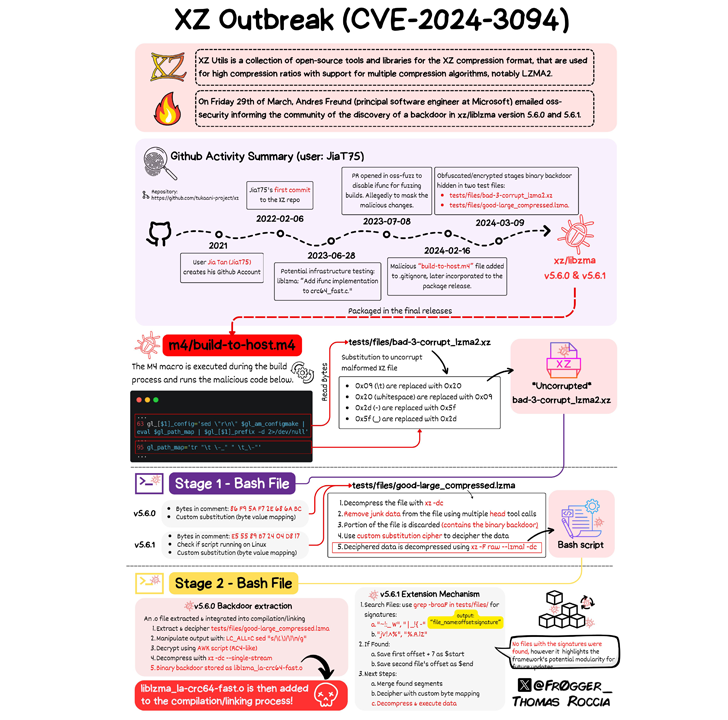
Malicious Code in XZ Utils for Linux Systems Enables Remote Code ...
PPT - Undermining the Linux Kernel: Malicious Code Injection via /dev ...
3 critical malicious code execution vulnerabilities in Linux kernel ...
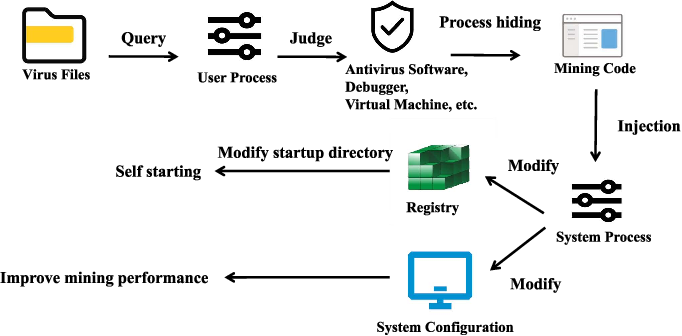
Figure 1 from A Malicious Mining Code Detection Method Based on Multi ...

Evidence Collection in Linux Forensics (Disk + Memory Acquisition)
Advertisement Space (336x280)
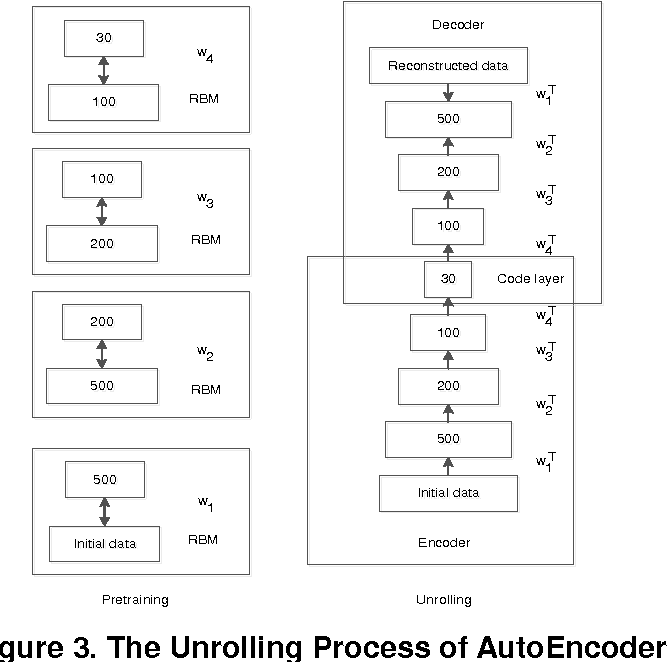
Figure 3 from A Hybrid Malicious Code Detection Method based on Deep ...
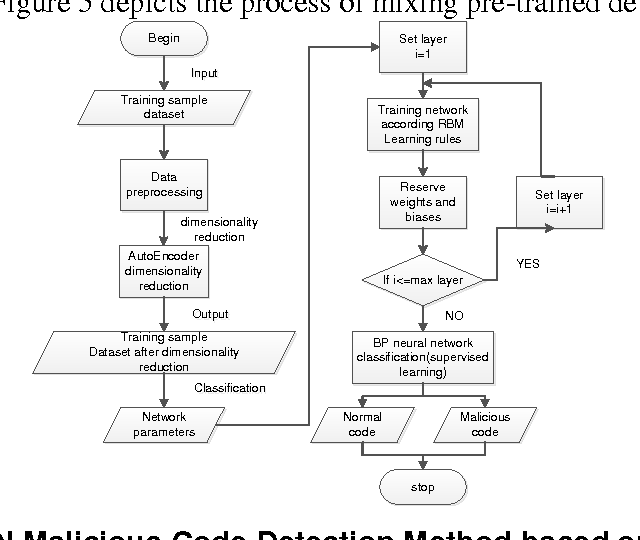
Figure 5 from A Hybrid Malicious Code Detection Method based on Deep ...

Evidence Collection in Linux Forensics (Disk + Memory Acquisition)

A Malicious Code Detection Method Based on Stacked Depthwise Separable ...
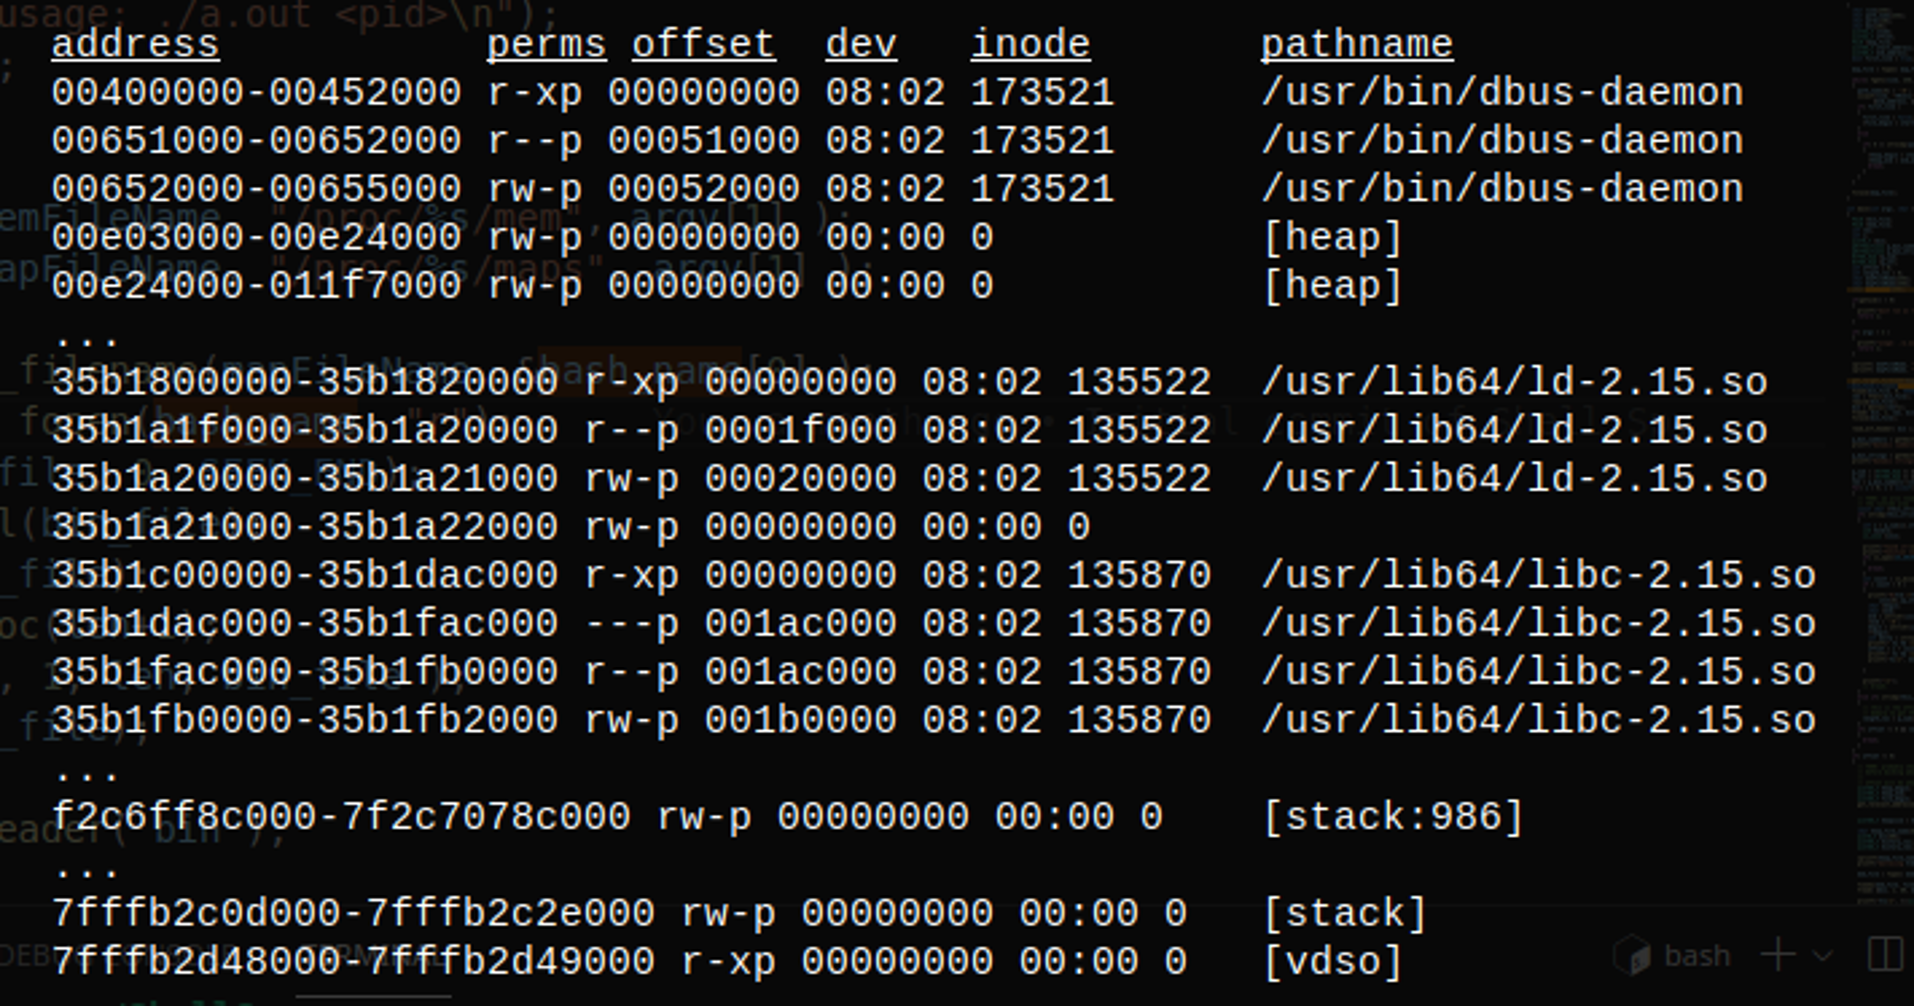
How to Extract Memory Information to Spot Linux Malware | CrowdStrike
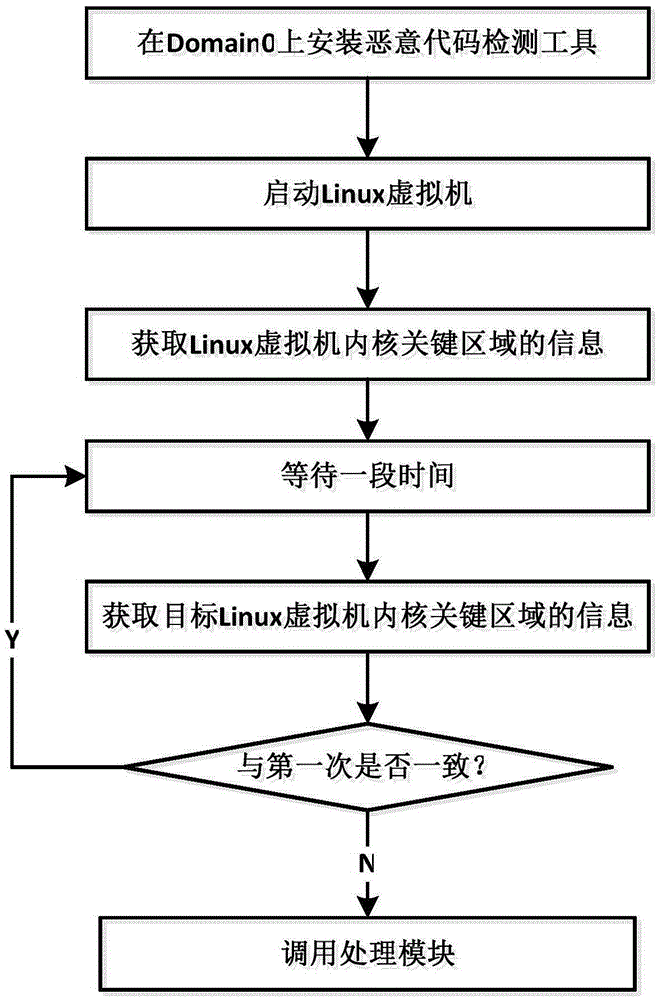
Core integrity detection method for aiming at Xen-based Linux virtual ...