
Regex Help Splunk Community

Regex Help - Splunk Community

Solved: help me in writing Regex for the below data - Splunk Community

Help with Regex in transaction endswith - Splunk Community

Regex Help - Splunk Community

Help with Regex in transaction endswith - Splunk Community

RegEx Help - how to extract the numbers from strin... - Splunk Community

How to create regex to extract the fields - Splunk Community

How to use regex to view data? - Splunk Community

Solved: Convert Regex to Detect Internal Domains - Splunk Community

Solved: How to create a regex to extract data? - Splunk Community
Advertisement Space (300x250)

Need to write a regex for time extraction - Splunk Community

How to create regex to extract the fields - Splunk Community

Need to write a regex for time extraction - Splunk Community

Need to write a regex for time extraction - Splunk Community

How to use regex to view data? - Splunk Community

Solved: Convert Regex to Detect Internal Domains - Splunk Community

Solved: How to set sourcetype using regex on source? - Splunk Community

Using a lookup table to store regex patterns to be... - Splunk Community

How to use regex to view data? - Splunk Community

Solved: Using Regex to split a field? - Splunk Community
Advertisement Space (336x280)

How to use regex to view data? - Splunk Community

How to optimize regex for splunk query and why get... - Splunk Community

Solved: regex extraction - Splunk Community

How to use regex to view data? - Splunk Community

How to create regex to extract the fields - Splunk Community
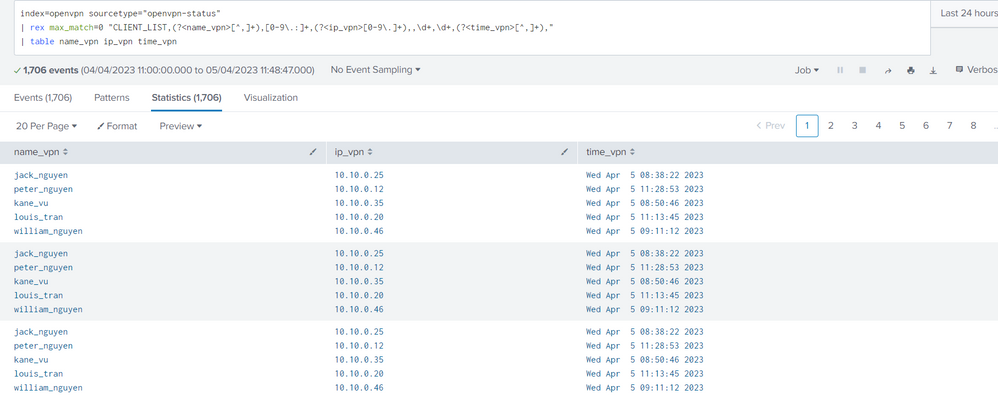
Re: How can I use regex to list a table? - Splunk Community
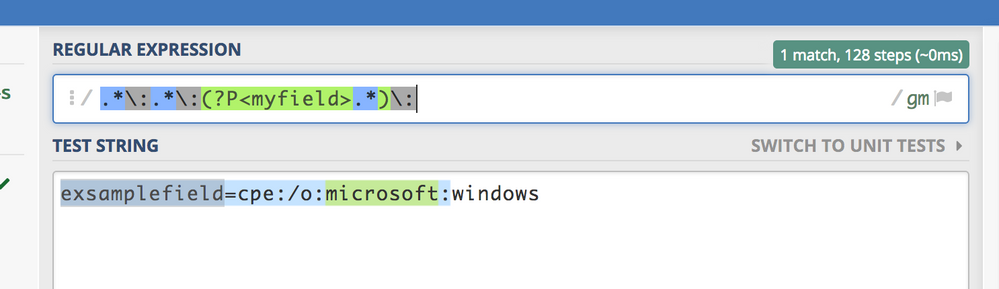
creating a new field using Regex - Splunk Community

Regex for CEF - Splunk Community

How to break a multiline event with regex on the c... - Splunk Community
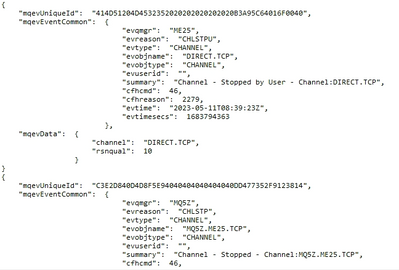
Why does linebreaking regex have no capturing grou... - Splunk Community
Advertisement Space (336x280)

Need to write a regex for time extraction - Splunk Community

Need to write a regex for time extraction - Splunk Community

Solved: Regex for complex search string - Splunk Community

Solved: How to set sourcetype using regex on source? - Splunk Community

How to create regex to extract the fields - Splunk Community

Solved: REGEX - Splunk Community