
Solved Table Format Raw Data Splunk Community

Solved: Table format raw data - Splunk Community

How to change Time format in raw data to a readabl... - Splunk Community

Solved: How to format JSON data into a table? - Splunk Community

Solved: How to format JSON data into a table? - Splunk Community

Solved: How to format JSON data into a table? - Splunk Community

Solved: Extract Key value data from raw events - Splunk Community

Expand table raw using custom row expansion - Splunk Community
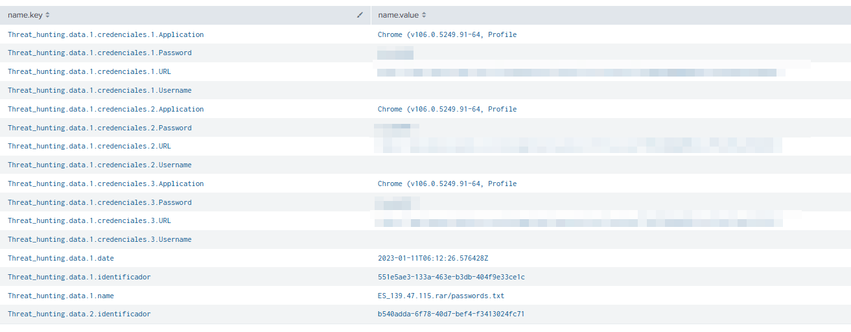
Solved: Help with Table Format - JSON - Splunk Community

Expand table raw using custom row expansion - Splunk Community

Solved: Extract Key value data from raw events - Splunk Community
Advertisement Space (300x250)

Solved: How to format JSON data into a table? - Splunk Community
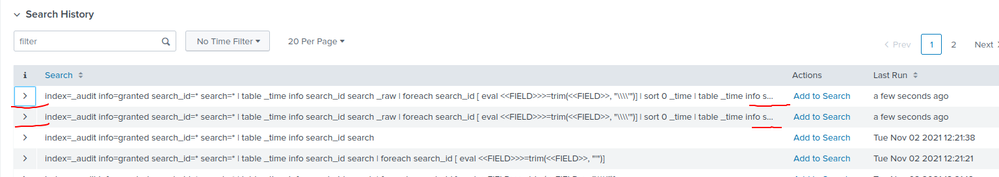
Expand table raw using custom row expansion - Splunk Community

groupby against raw data from multiple logs - Splunk Community

How to show raw data instead of formatted data? - Splunk Community

How to format a table column based on its value us... - Splunk Community

How to show raw data instead of formatted data? - Splunk Community

How to get data from raw array of json from sendgr... - Splunk Community

Expand table raw using custom row expansion - Splunk Community

Solved: Reformat data into 2 dimensional table for chartin... - Splunk ...

Solved: Table headers not visible - Splunk Community
Advertisement Space (336x280)

Solved: How to parse and extract field from my raw data? - Splunk Community
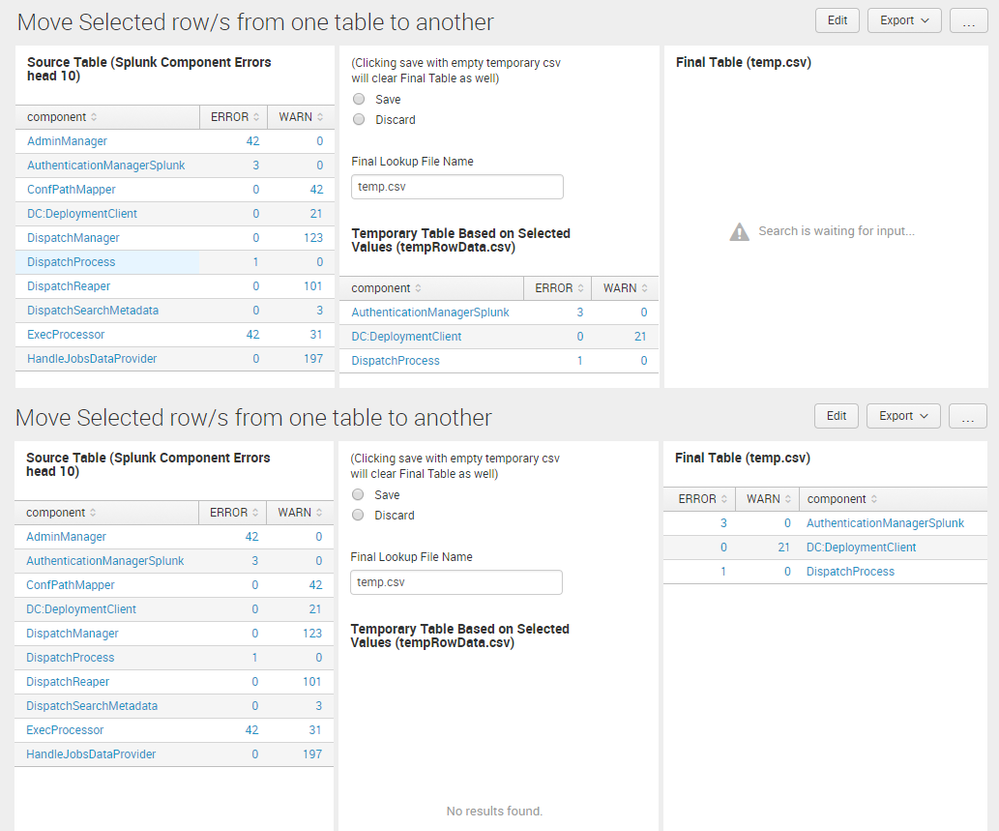
Solved: multiselect table rows - Splunk Community

Solved: How to parse and extract field from my raw data? - Splunk Community

Solved: Need help creating a table from column type logs - Splunk Community

How to create a table row expansion? - Splunk Community

How to create a table row expansion? - Splunk Community

How to create editable table on dashboard - Splunk Community
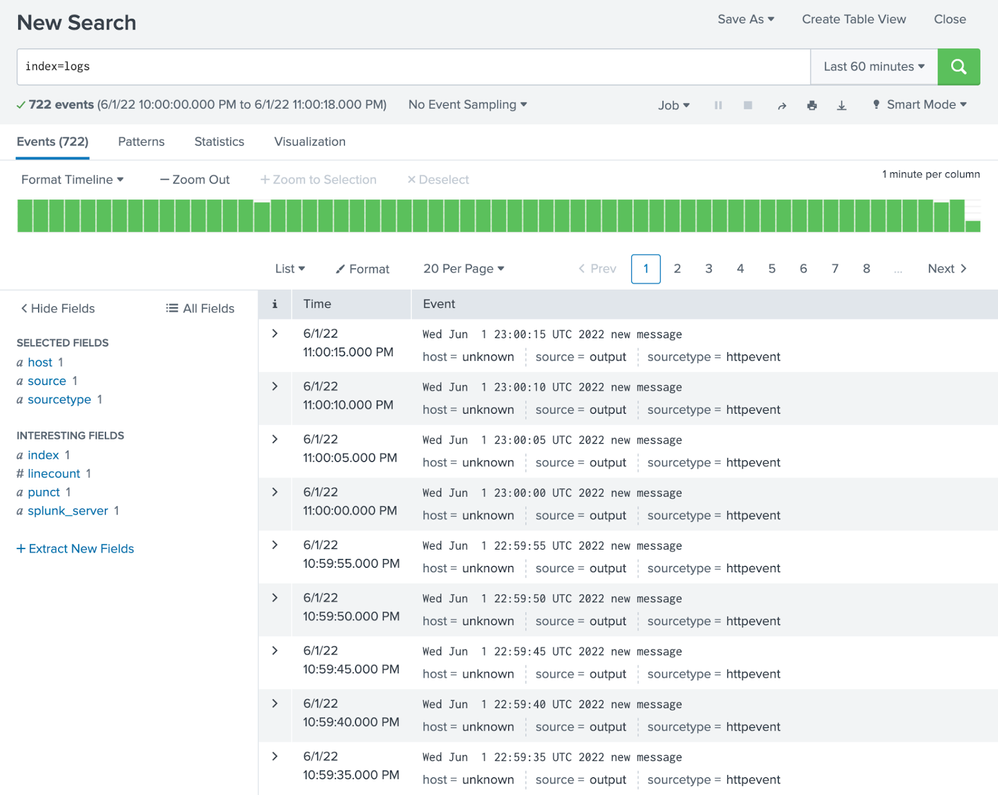
Testing out the OpenTelemetry Collector With raw D... - Splunk Community

How to fetch the values from raw logs - Splunk Community
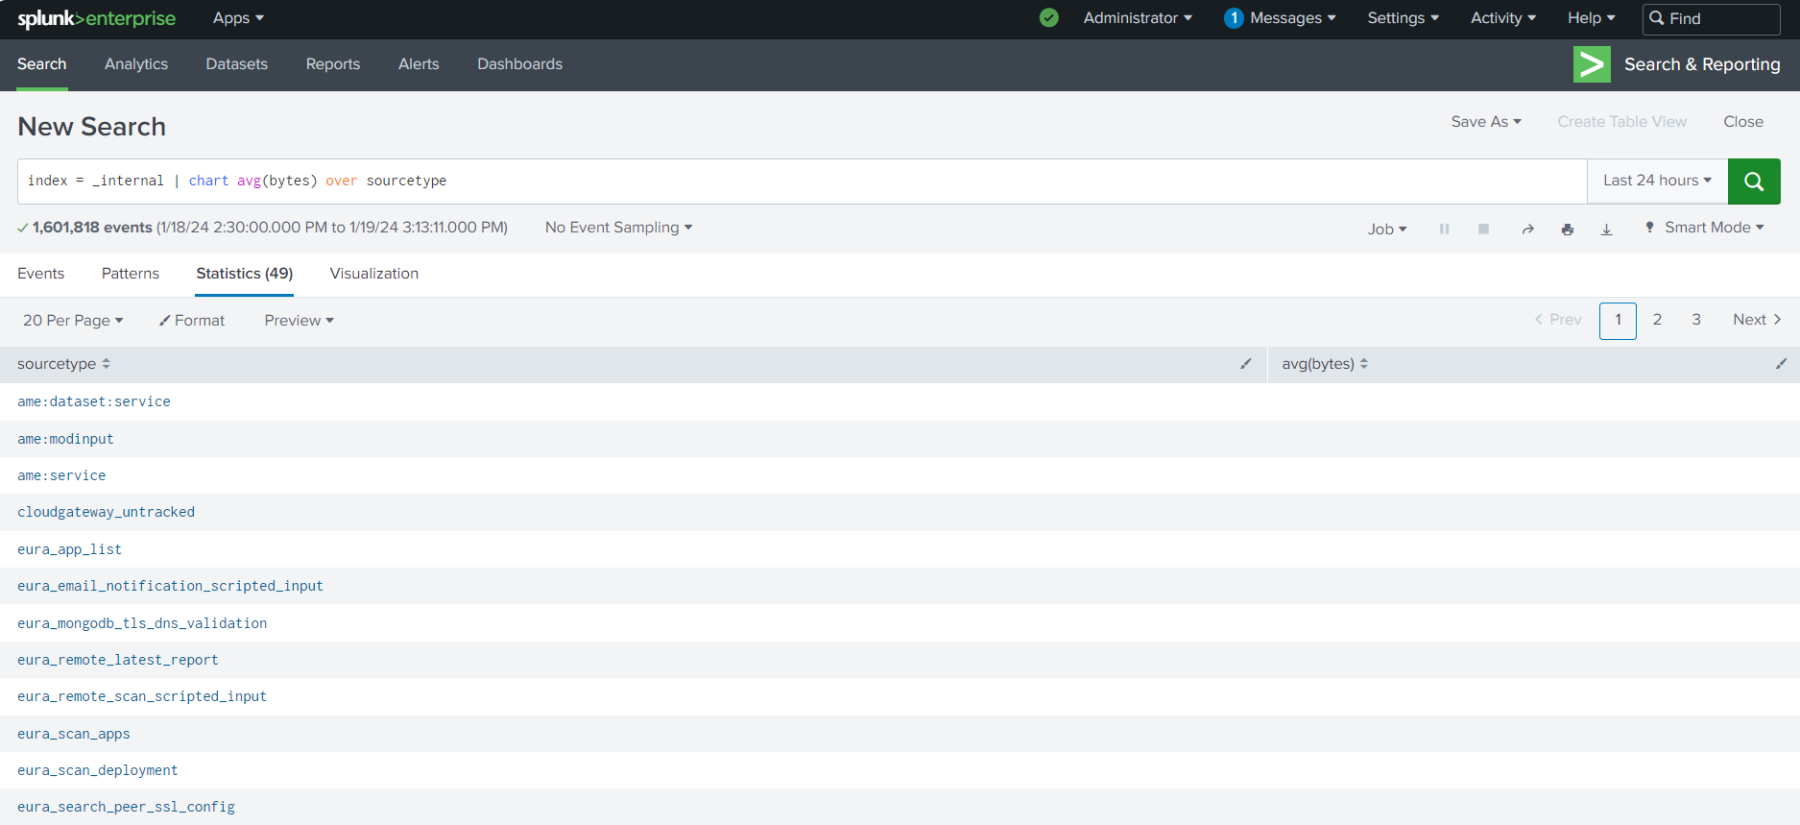
Splunk table command- Generation and data visualization
Advertisement Space (336x280)

Solved: How to parse and extract field from my raw data? - Splunk Community

How to create editable table on dashboard - Splunk Community
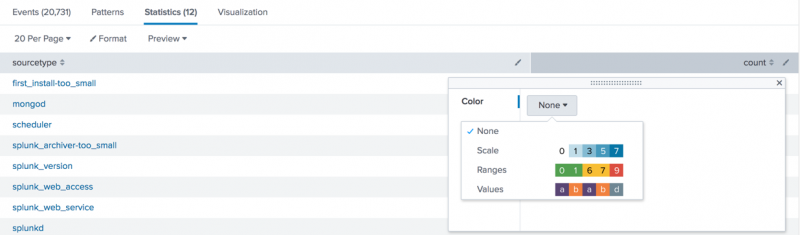
Format table visualizations - Splunk Documentation

How to add rows to table in dashboard? - Splunk Community

Solved: Splunk date not displaying in table correctly - Splunk Community
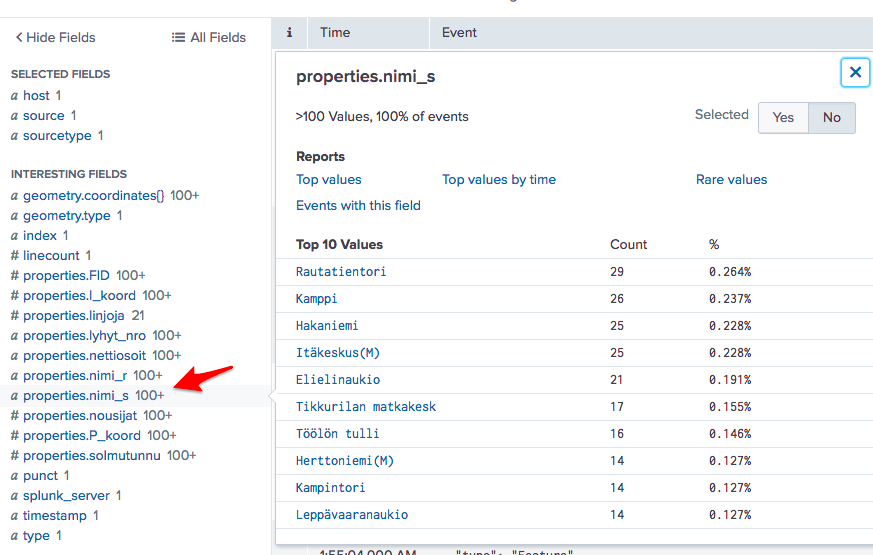
How To Get Raw Data From Splunk at Charles Wilcoxen blog