
Splunk Correlate Command Tutorial Field Correlation Analysis For

Splunk correlate Command Tutorial: Field Correlation Analysis for ...

Unlock the Power of Field Command in Splunk! | SPL Tutorial for Data ...

Splunk Tutorial For Beginners | Stats vs Chart Command in Splunk - YouTube

Splunk SPL fieldsummary Command Tutorial - Generate Field Statistics ...

Splunk SPL Split Command Tutorial - Divide Field Values Into Multiple ...

Splunk eval Command Complete Tutorial - Field Calculations & String ...
Splunk SPL validate Command Tutorial - Data Validation & Field Testing ...
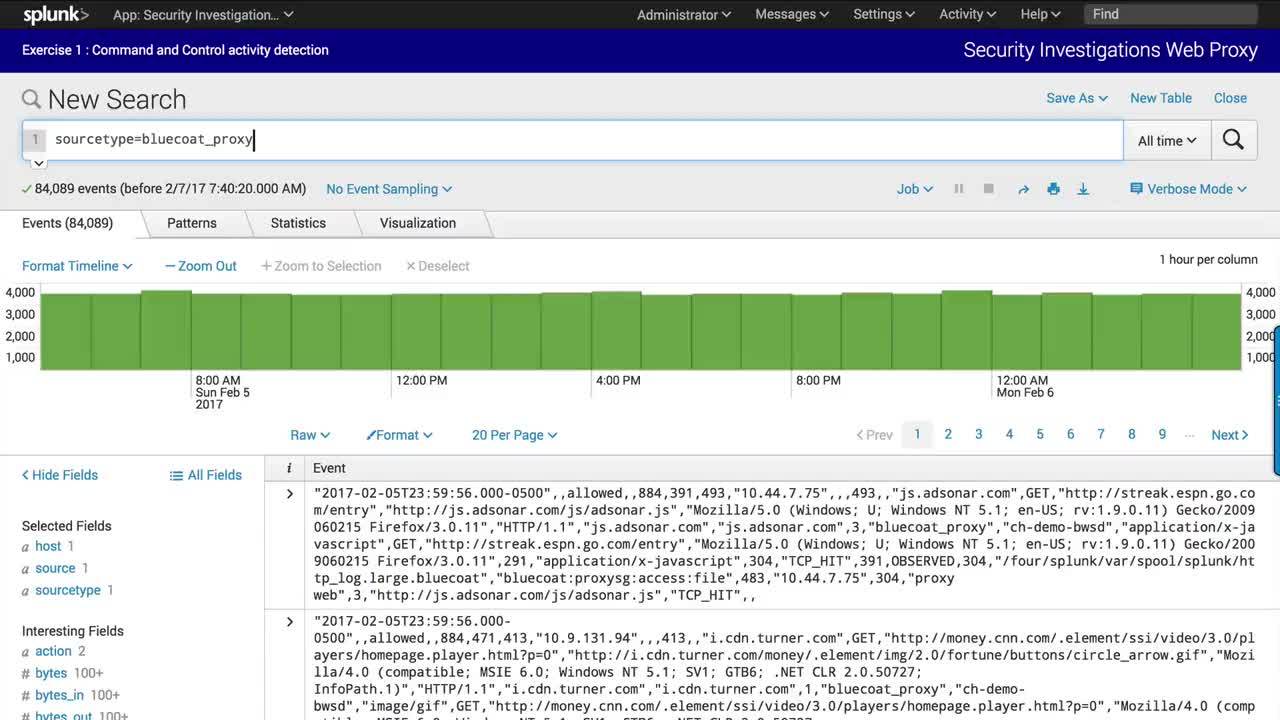
Splunk for Security Investigation: Command and Control Analysis | Splunk

Splunk Lab - Correlation Analysis | PDF
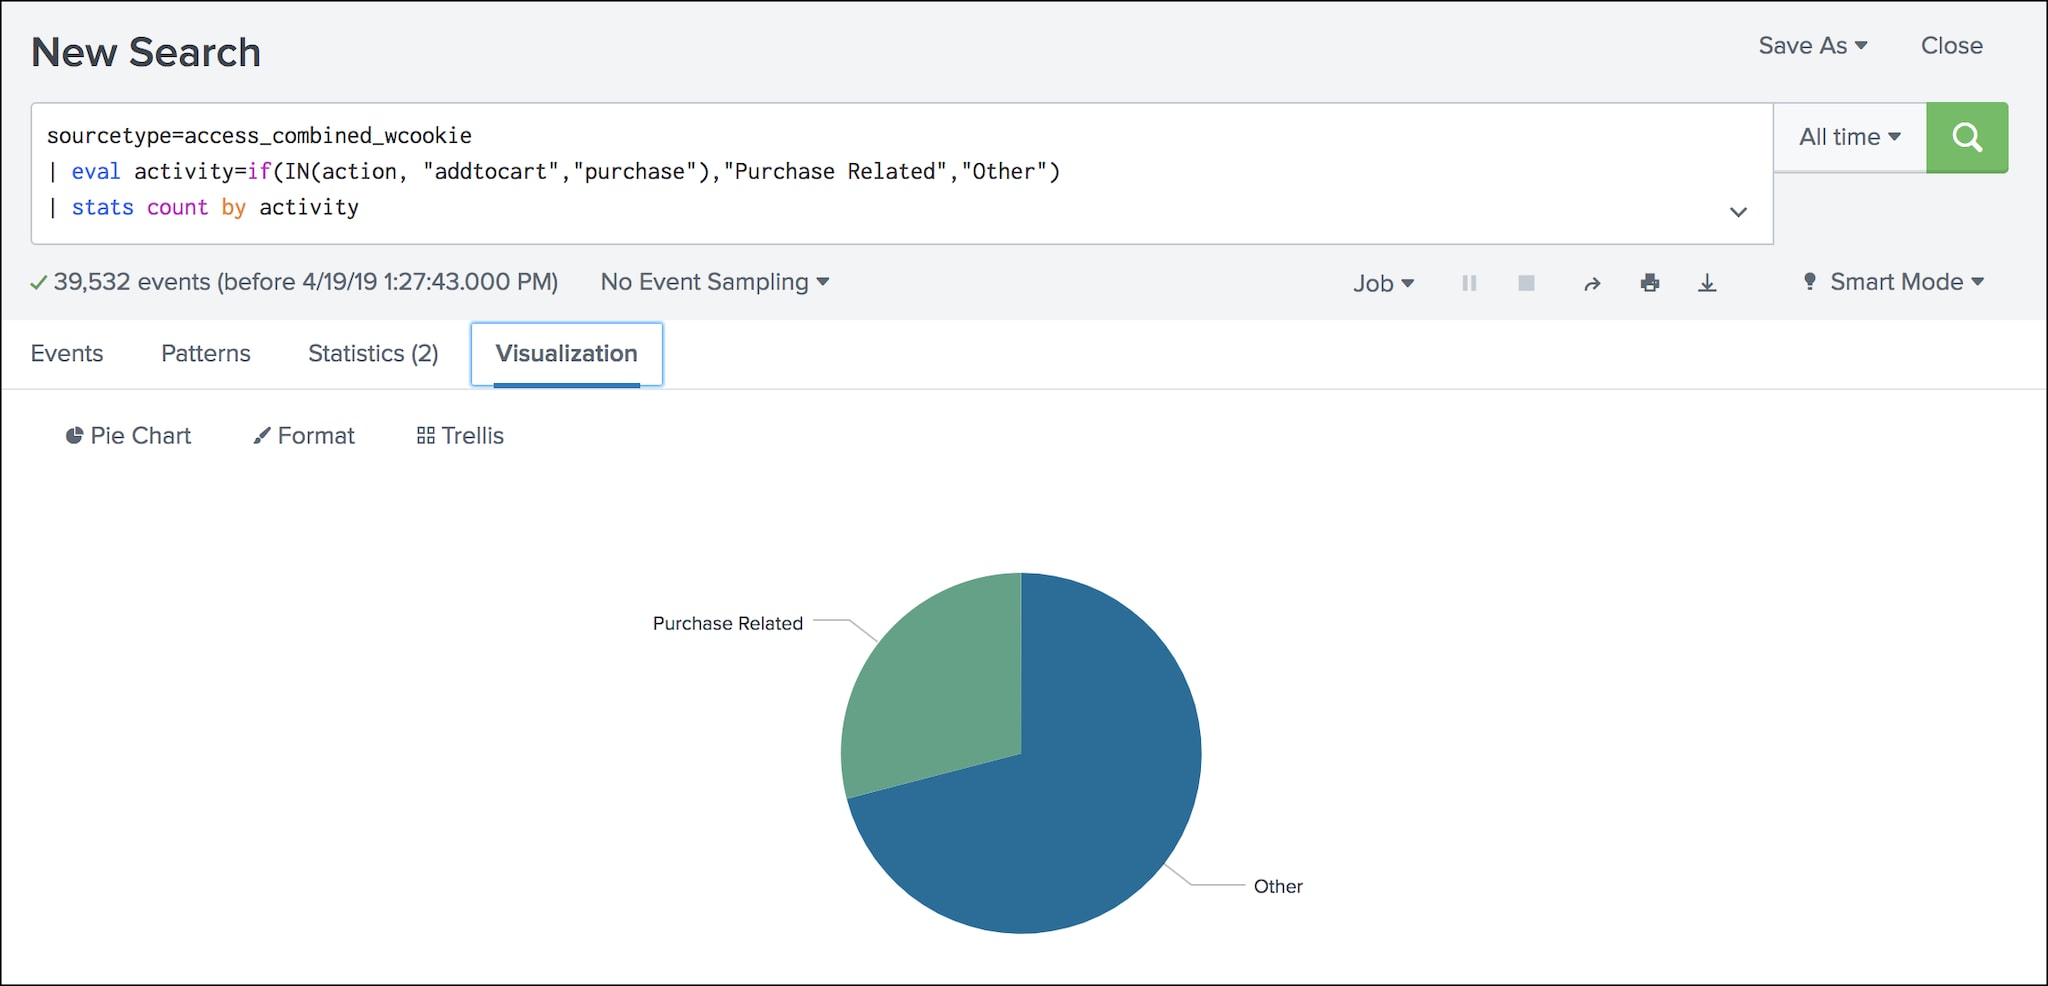
Smooth operator | Searching for multiple field values | Splunk
Advertisement Space (300x250)
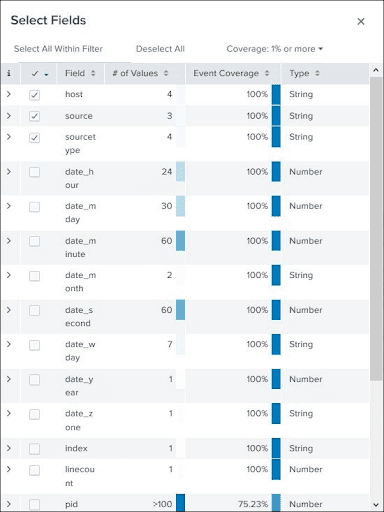
Splunk Tutorial For Beginners | Learn What is Splunk [Updated 2025]

Splunk Search Command of the Week: Using the correlate Command Splunk ...

Splunk SPL JOIN Command Tutorial: Master Left, Inner & Outer Joins for ...
Splunk SPL typer Command - Automatically Determine Field Data Types ...
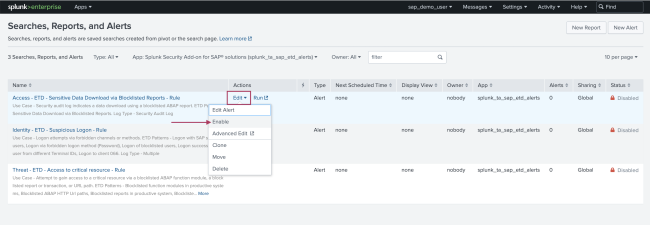
Configure correlation searches in the Splunk Security Add-on for SAP ...
Splunk SPL mvcombine Command Tutorial - Create Multi-Value Fields with ...
Splunk SPL foreach Command Tutorial - Iterate Over Multiple Fields with ...

Splunk Timechart Command Tutorial - Master SPL Time Series ...

8 - TUTORIAL - Correlation Analysis | PDF
Splunk Commands for Data Analysis and Visualization
Advertisement Space (336x280)

Splunk Replace Command Tutorial: Substitute Field Values with Exact ...

Splunk mvfilter Command Tutorial - Filter Multi-Value Fields with ...
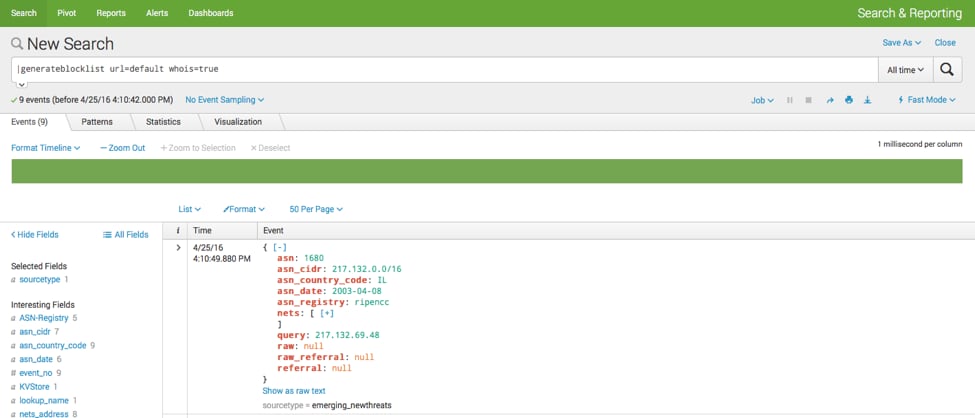
Smooth operator | Searching for multiple field values | Splunk

Identify your Correlation IDs, Steps, and Attributes - Splunk Documentation

Identify your Correlation IDs, Steps, and Attributes - Splunk Documentation
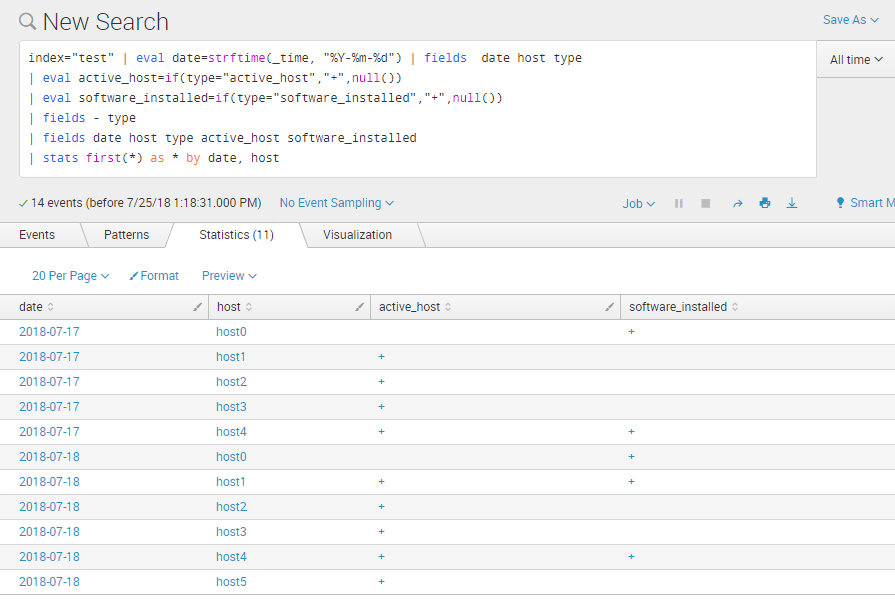
How to correlate different events in Splunk and make dashboards ...
Correlation Search Execution in Splunk ES - ThinkCloudly

Using the Splunk rex and erex Commands with Field Extractions - Kinney ...

A Guide To Easy Log Analysis Using Splunk

Splunk Search Command Cheatsheet
Advertisement Space (336x280)
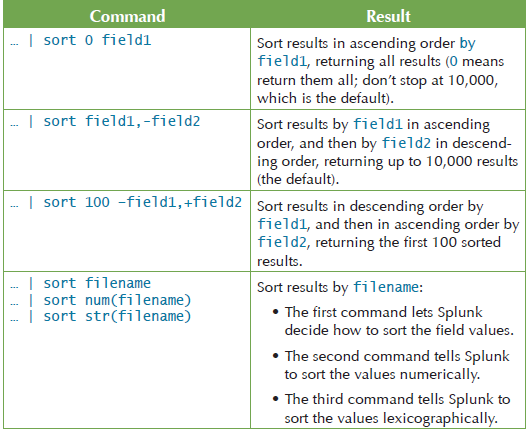
SPL: Search Processing Language - Splunk Tutorial | Intellipaat.com
Using the Splunk rex and erex Commands with Field Extractions - Kinney ...
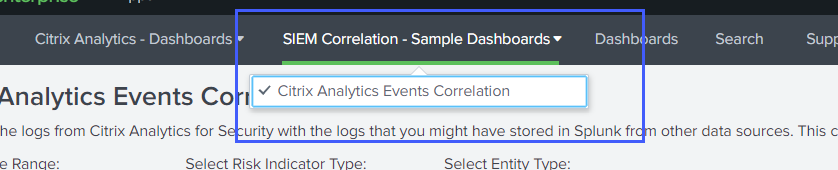
Citrix Analytics dashboards for Splunk | Citrix Analytics for Security™
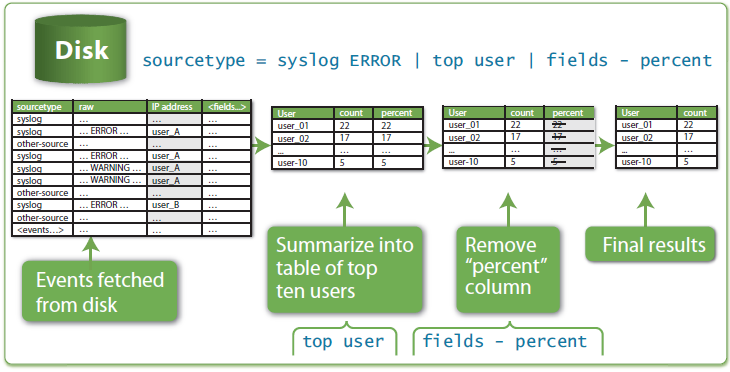
Splunk Commands - Search Commands Tutorial
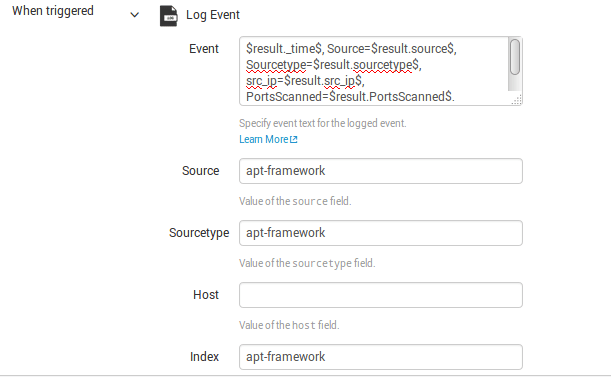
Creating Correlation Events in Splunk using Alerts | SOC Prime
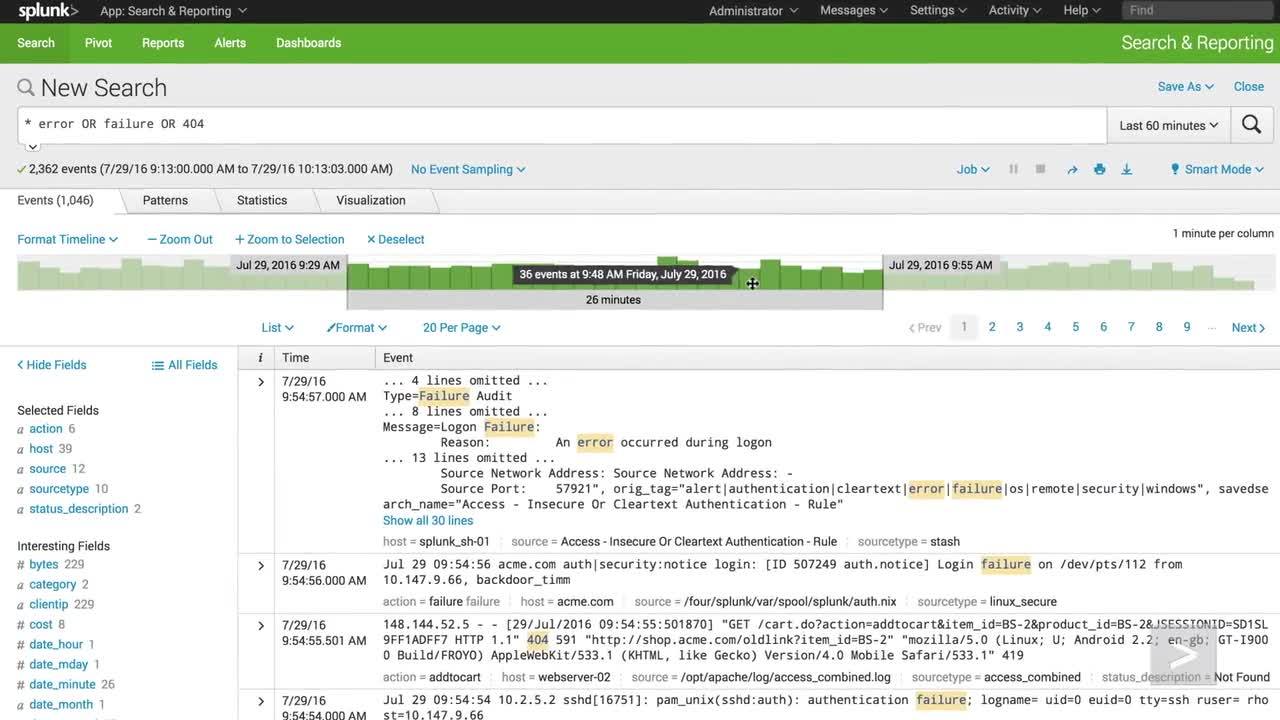
Search, Filter and Correlate | Splunk