
Splunk For Beginners Making Sense Of Logs And Security Data

Splunk for Beginners: Making Sense of Logs and Security Data

Splunk for Beginners: Making Sense of Logs and Security Data

Splunk for Beginners: Making Sense of Logs and Security Data
Splunk for Beginners: Making Sense of Logs and Security Data

Splunk for Beginners: Making Sense of Logs and Security Data
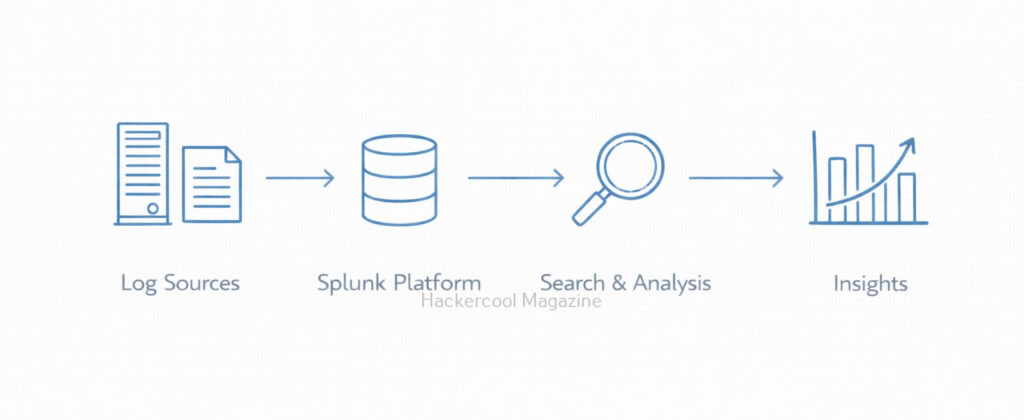
Splunk for Beginners: Making Sense of Logs and Security Data
Splunk for Beginners: Making Sense of Logs and Security Data
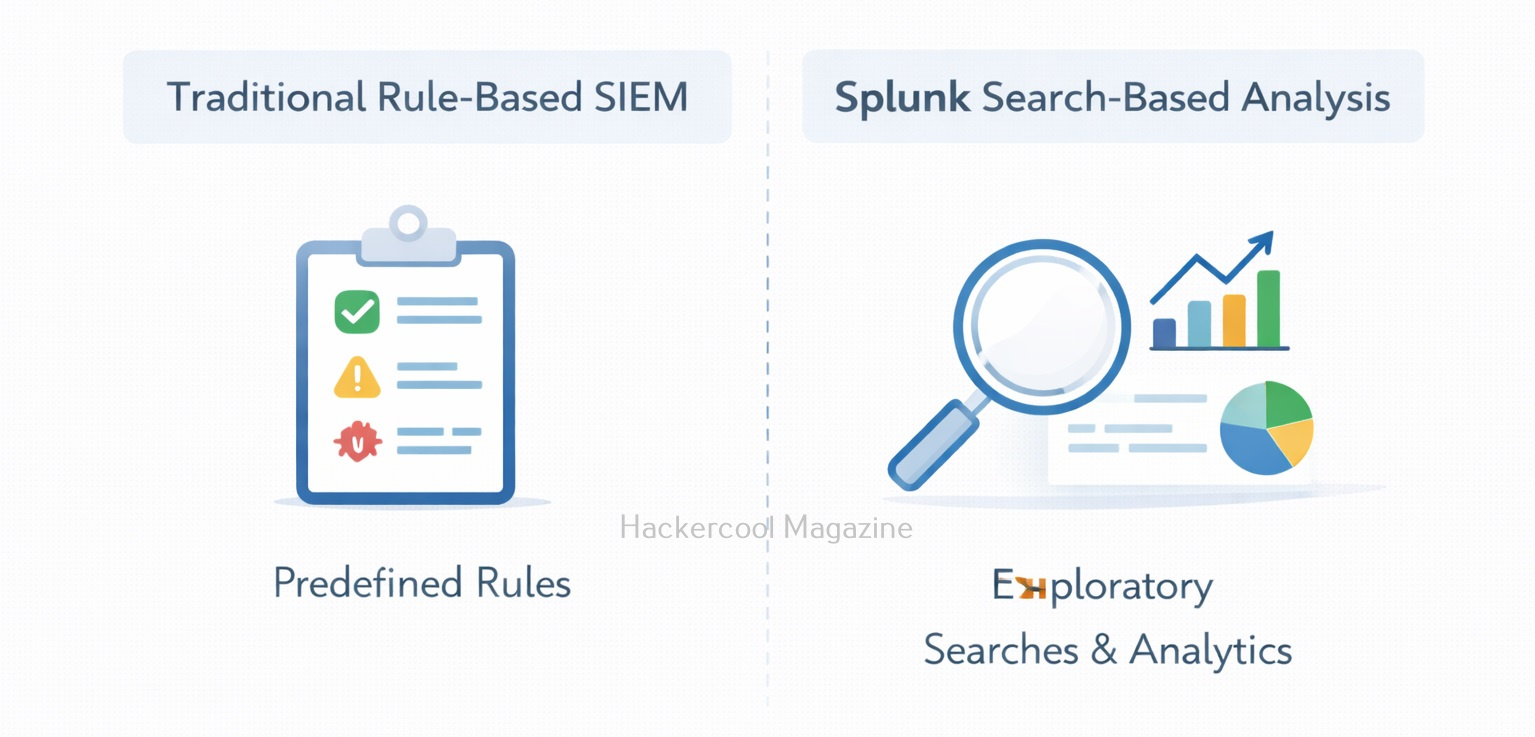
Splunk for Beginners: Making Sense of Logs and Security Data
Splunk for Beginners: Making Sense of Logs and Security Data

Splunk Tutorial for Beginners (Top Cyber Security Tools) - YouTube
Advertisement Space (300x250)
Splunk Basics Tutorial for Beginners | Cyber Security | Doovi
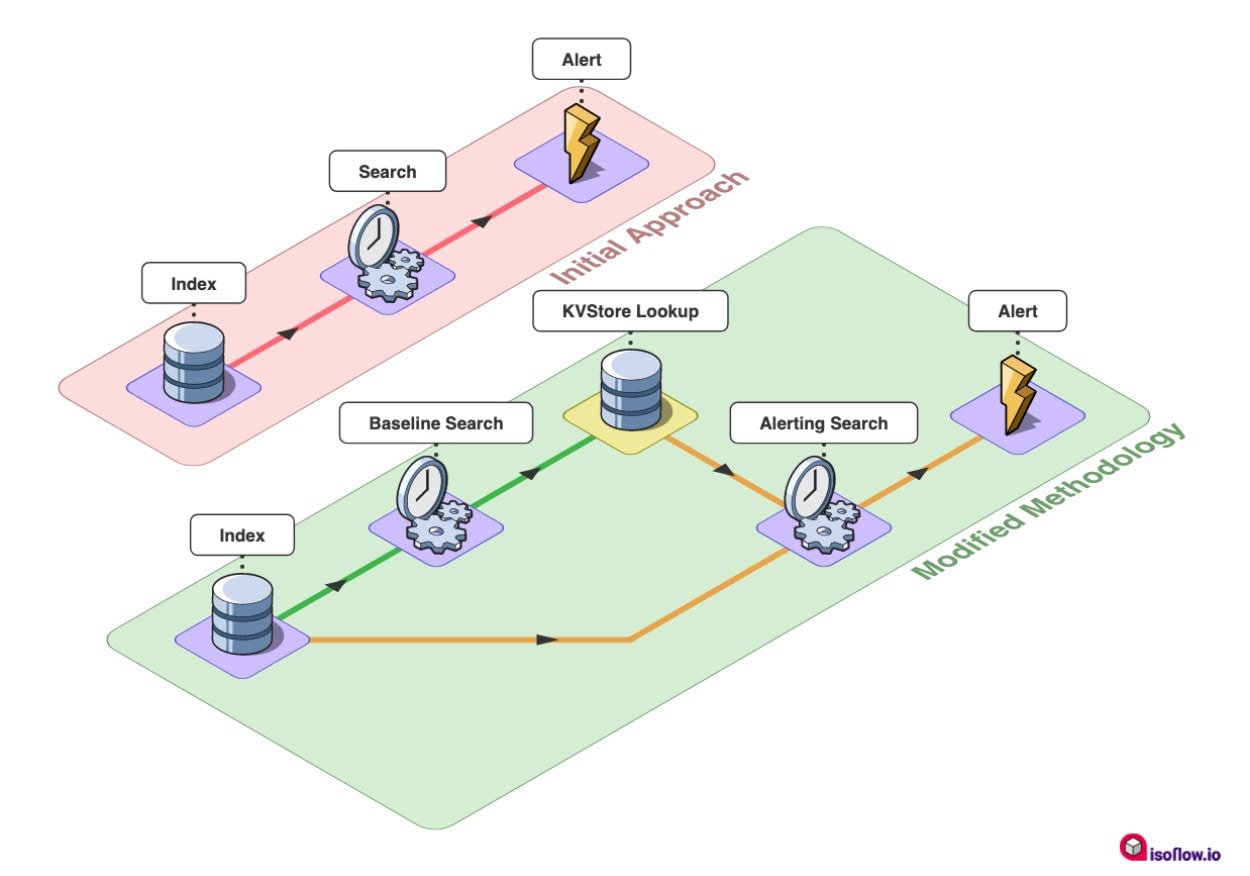
Making the Collection of Centralised S3 Logs into Splunk easy with ...
How to Simulate Data Flow and Pulling Logs From AWS to Splunk | Splunk
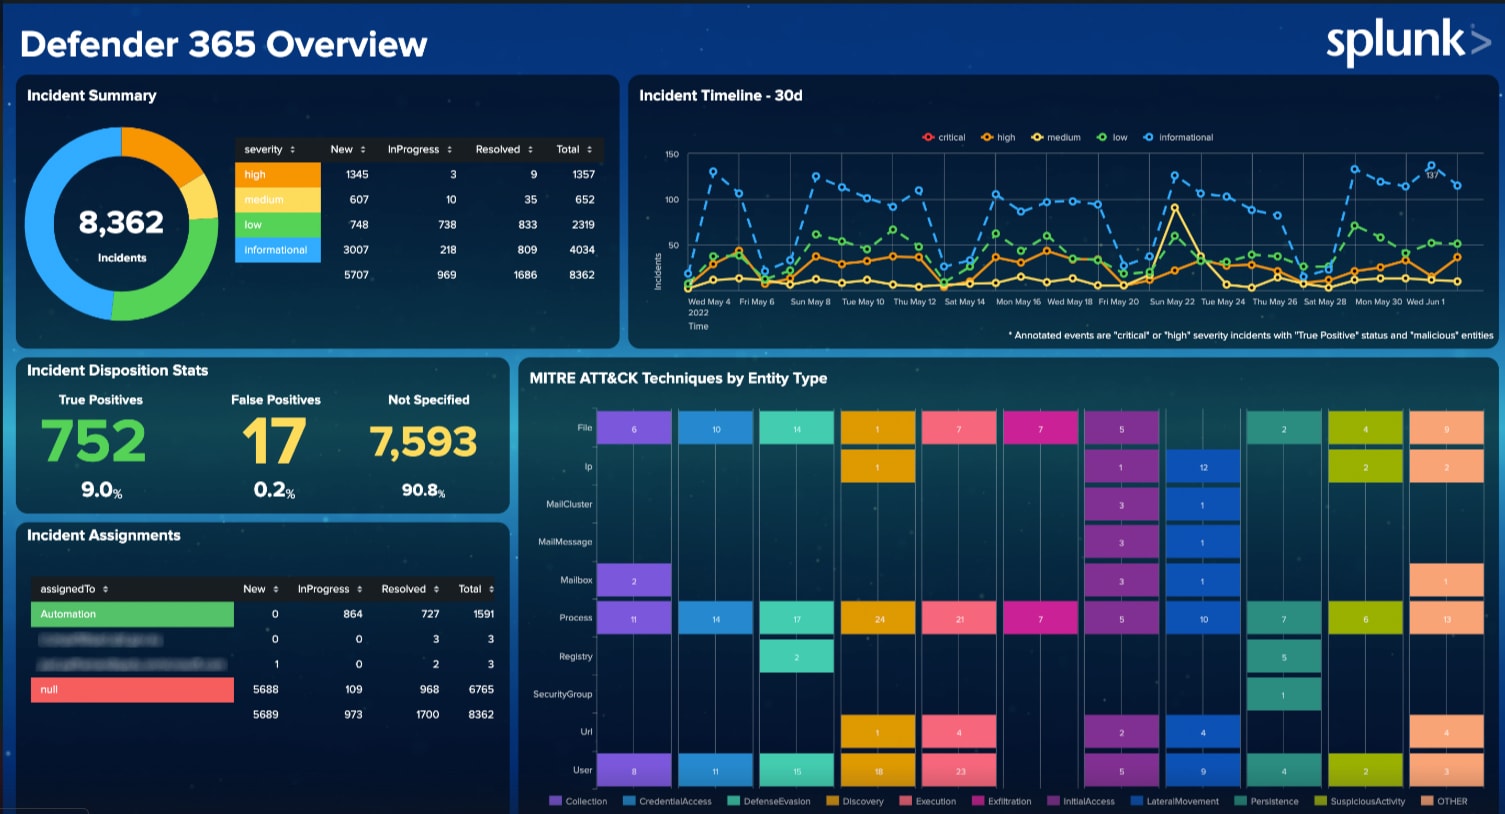
Making the Collection of Centralised S3 Logs into Splunk easy with ...
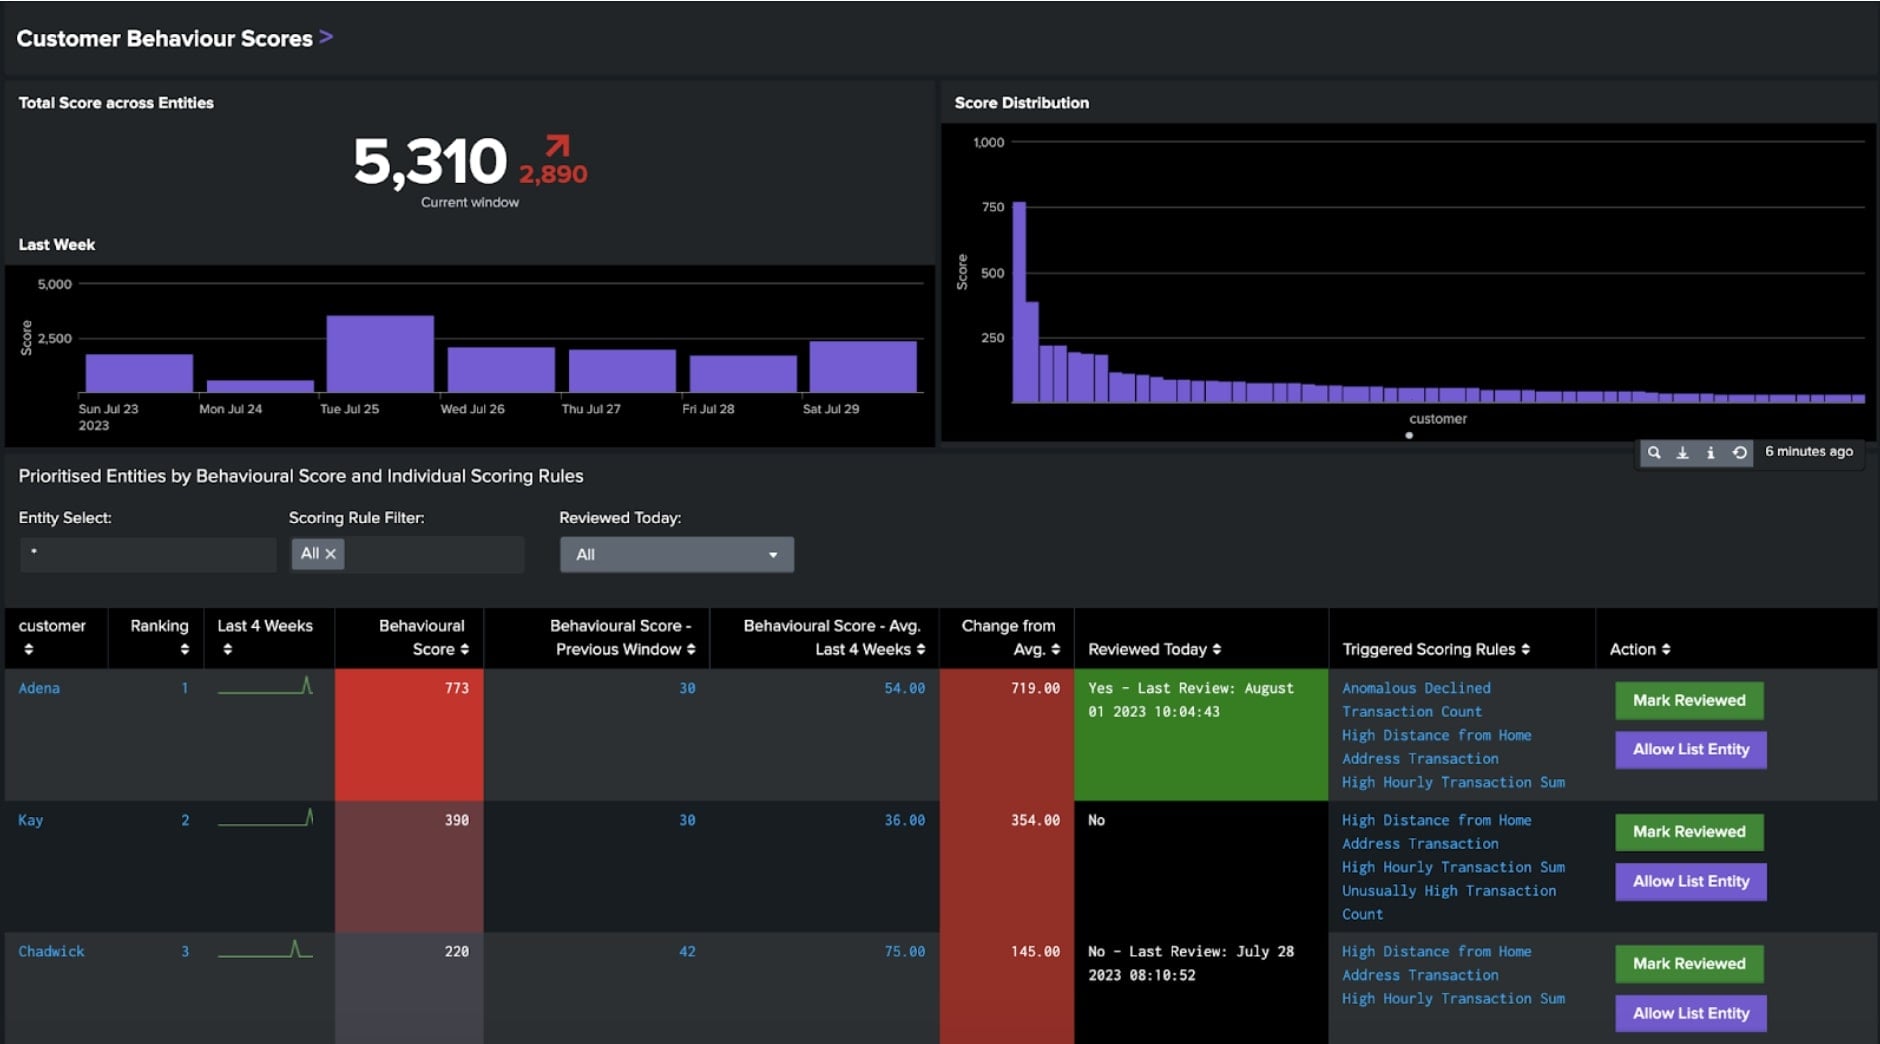
Making the Collection of Centralised S3 Logs into Splunk easy with ...
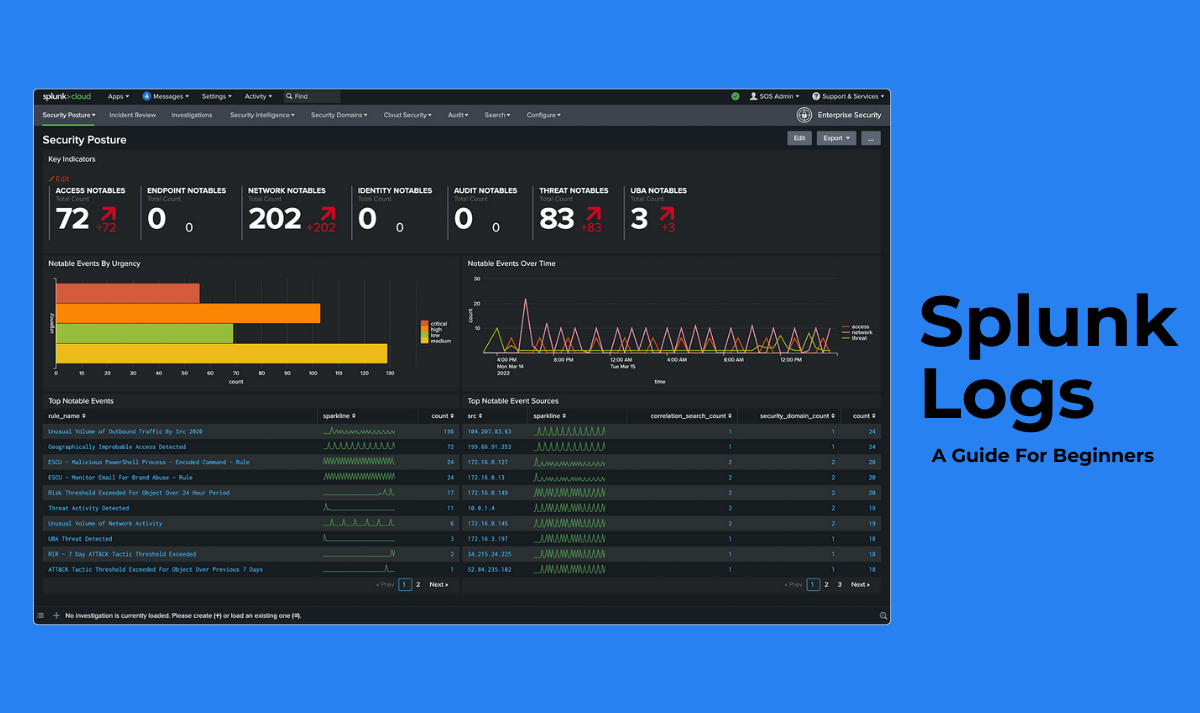
Splunk Logs- Types of Splunk Logs Files Explained (Updated 2025)
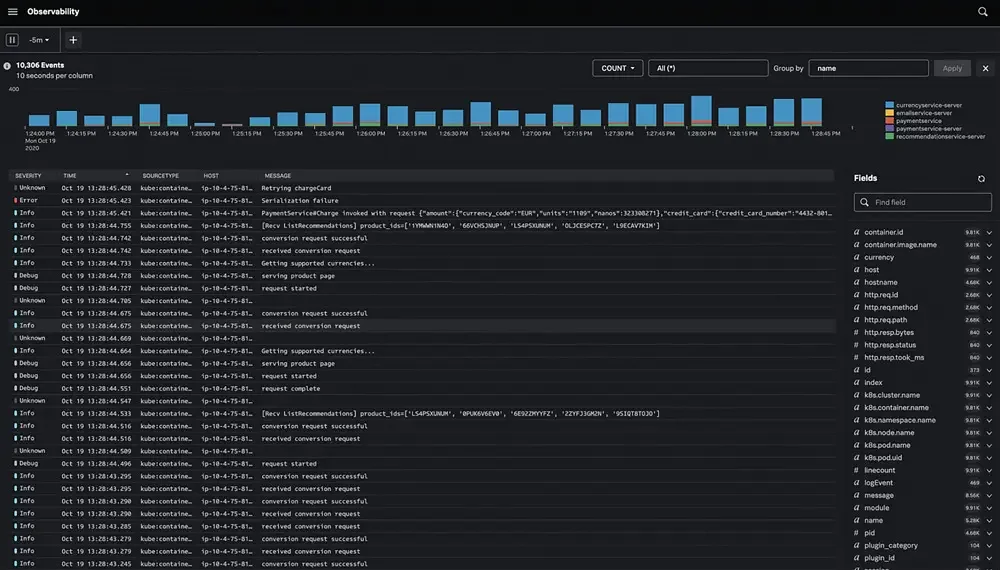
Splunk Logs- Types of Splunk Logs Files Explained

How to Monitor and Analyze AWS Managed Microsoft AD Security Logs Using ...

Splunk in 60 Minutes | Splunk Tutorial For Beginners | Splunk Training ...

#4 How to Upload Data (Event Logs) in Splunk | Splunk Tutorial for ...
Advertisement Space (336x280)
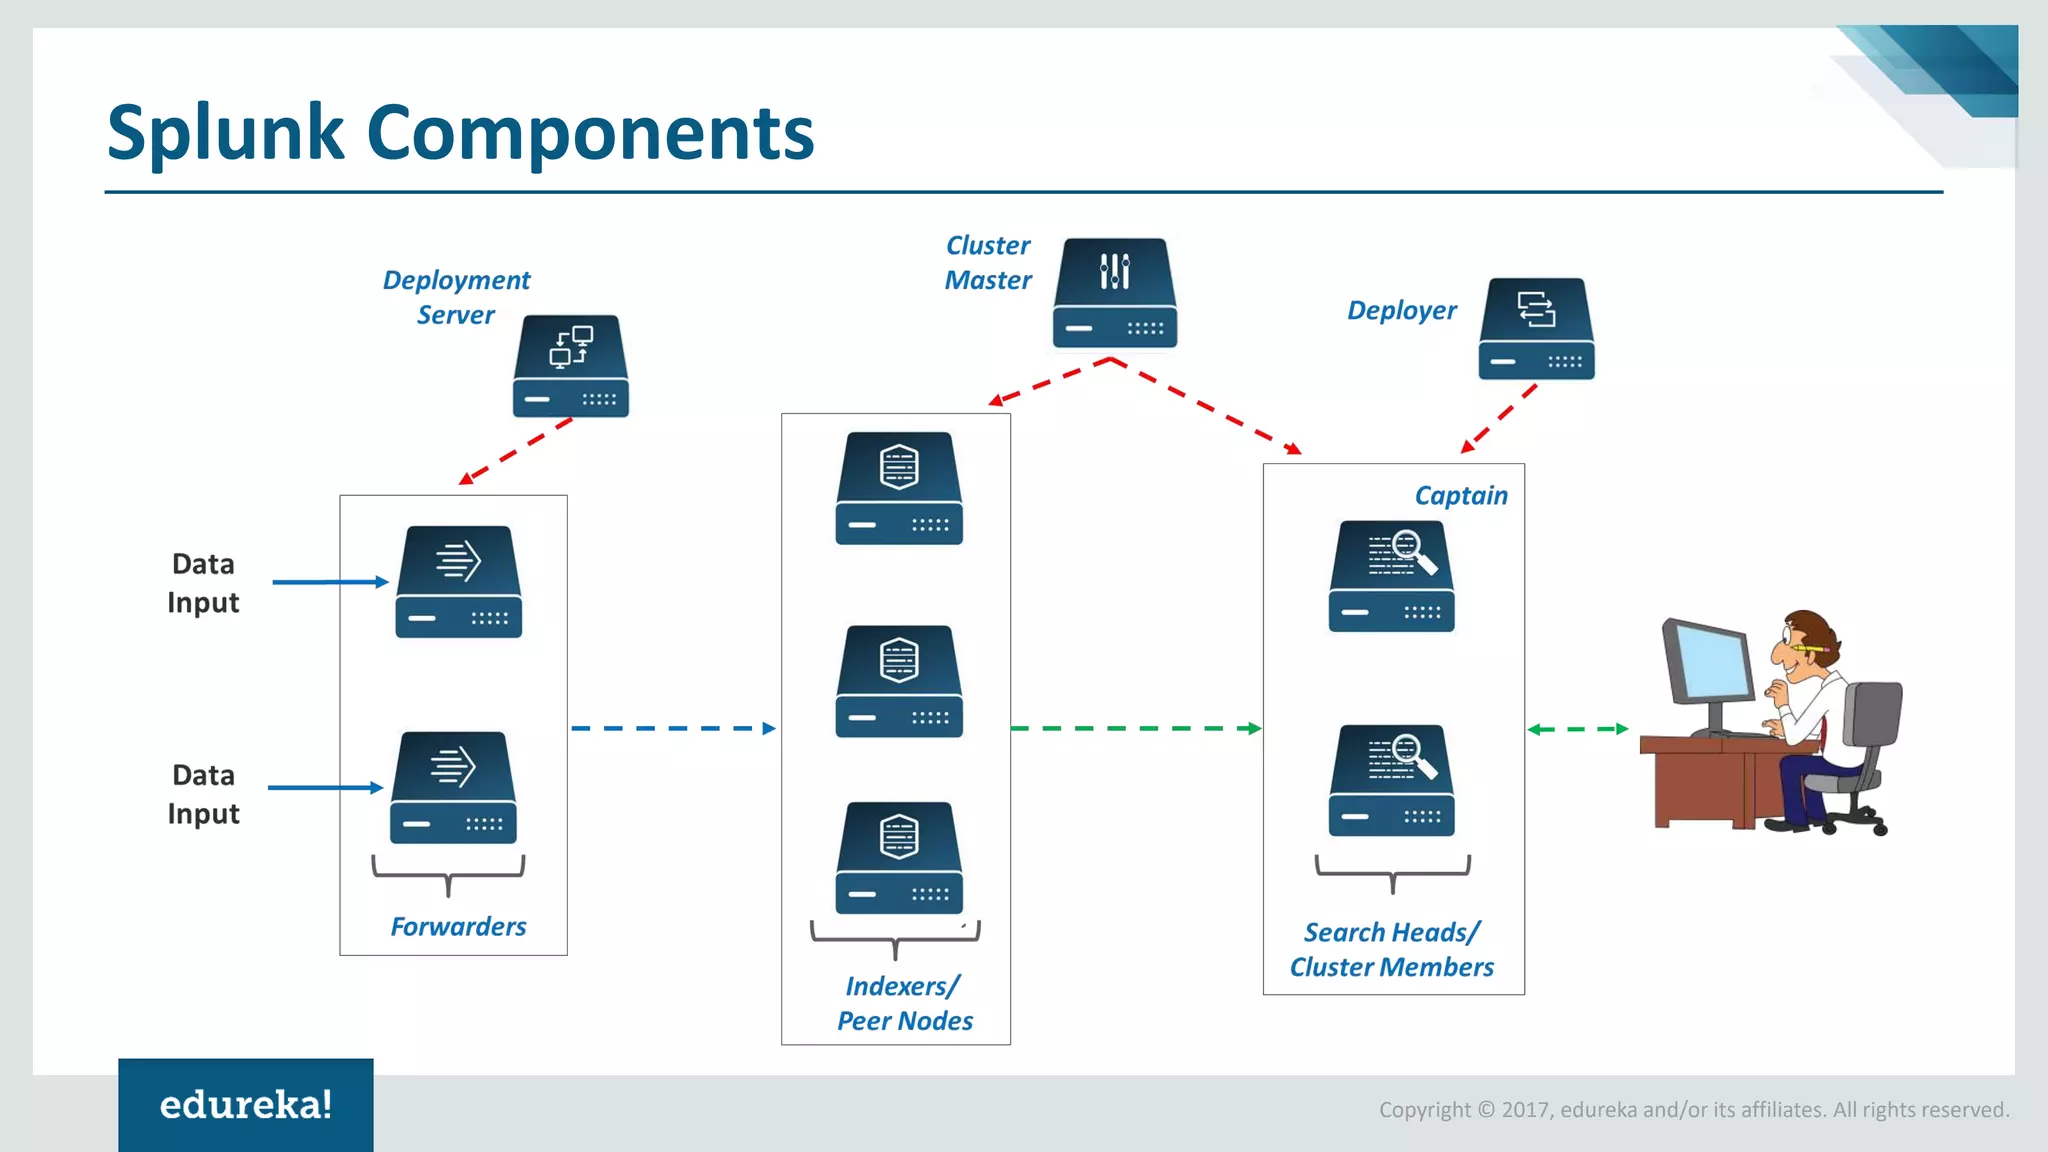
Splunk in 60 Minutes | Splunk Tutorial For Beginners | Splunk Training ...
Day 6 — Splunk for Beginners: From Raw Logs to Dashboards | by ...

Understanding Splunk For Beginners – MZCJW

Splunk for Security Monitoring, Part 01 - Hackers Arise

Ingesting and Parsing Unstructured Logs in Splunk - YouTube
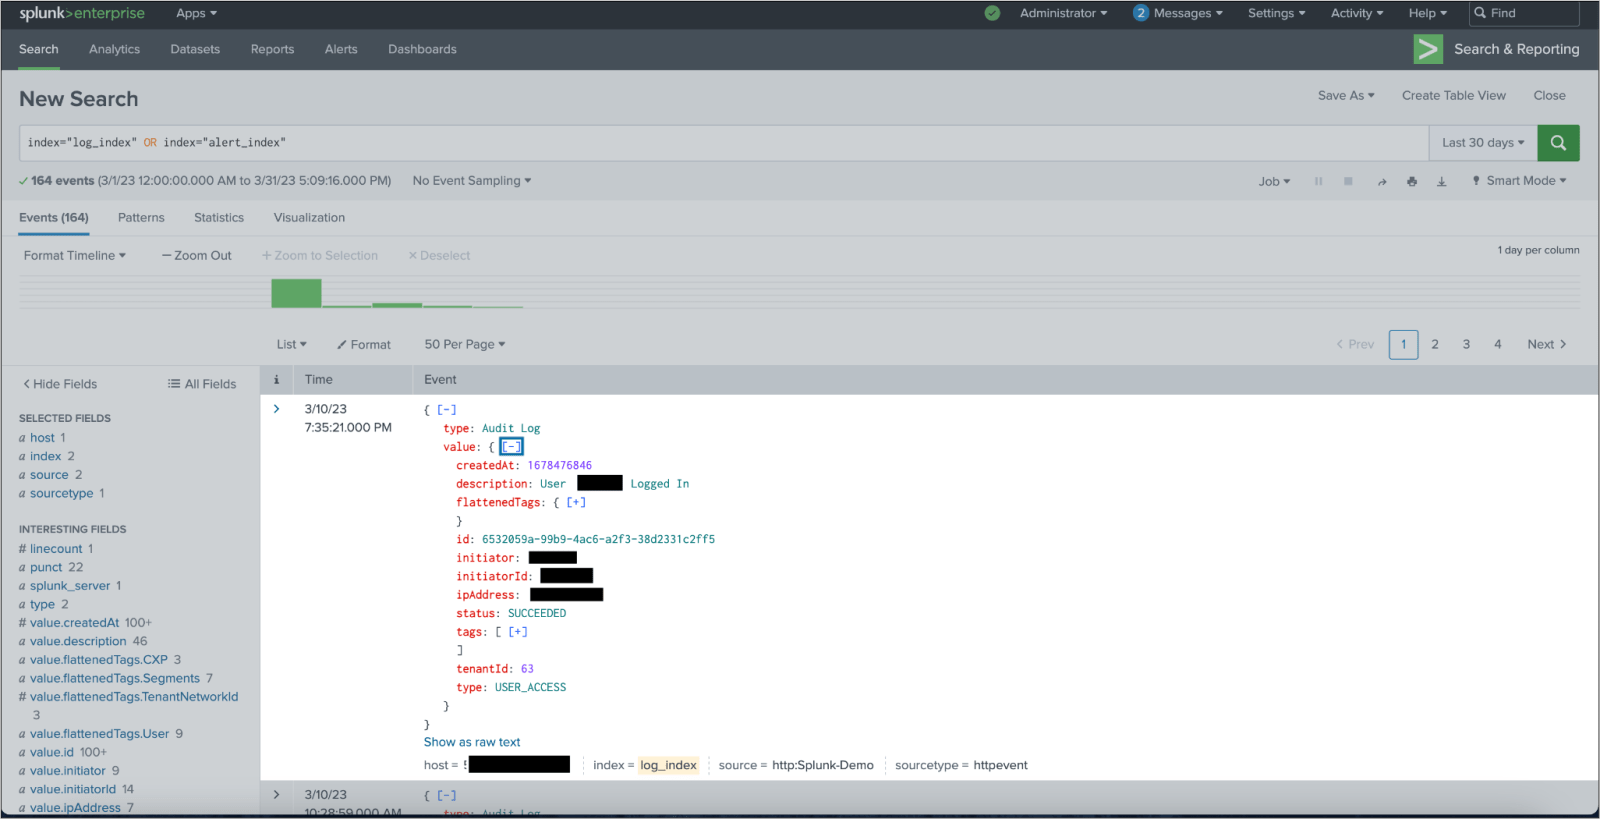
Splunk and Alkira for Resilient Cloud Networking

From Raw Logs to Real Insights: Setting Up Splunk Enterprise for ...

Log and data management with Splunk | Case Study

What is Splunk? — for splunk beginners | by Keerthi Konjety | Medium

How to Monitor and Analyze AWS Managed Microsoft AD Security Logs Using ...
Advertisement Space (336x280)

Splunk Log Observer: Fast and Powerful Log Investigation for DevOps ...

How to Upload Existing Logs to Splunk 📂 | Step-by-Step Guide for ...
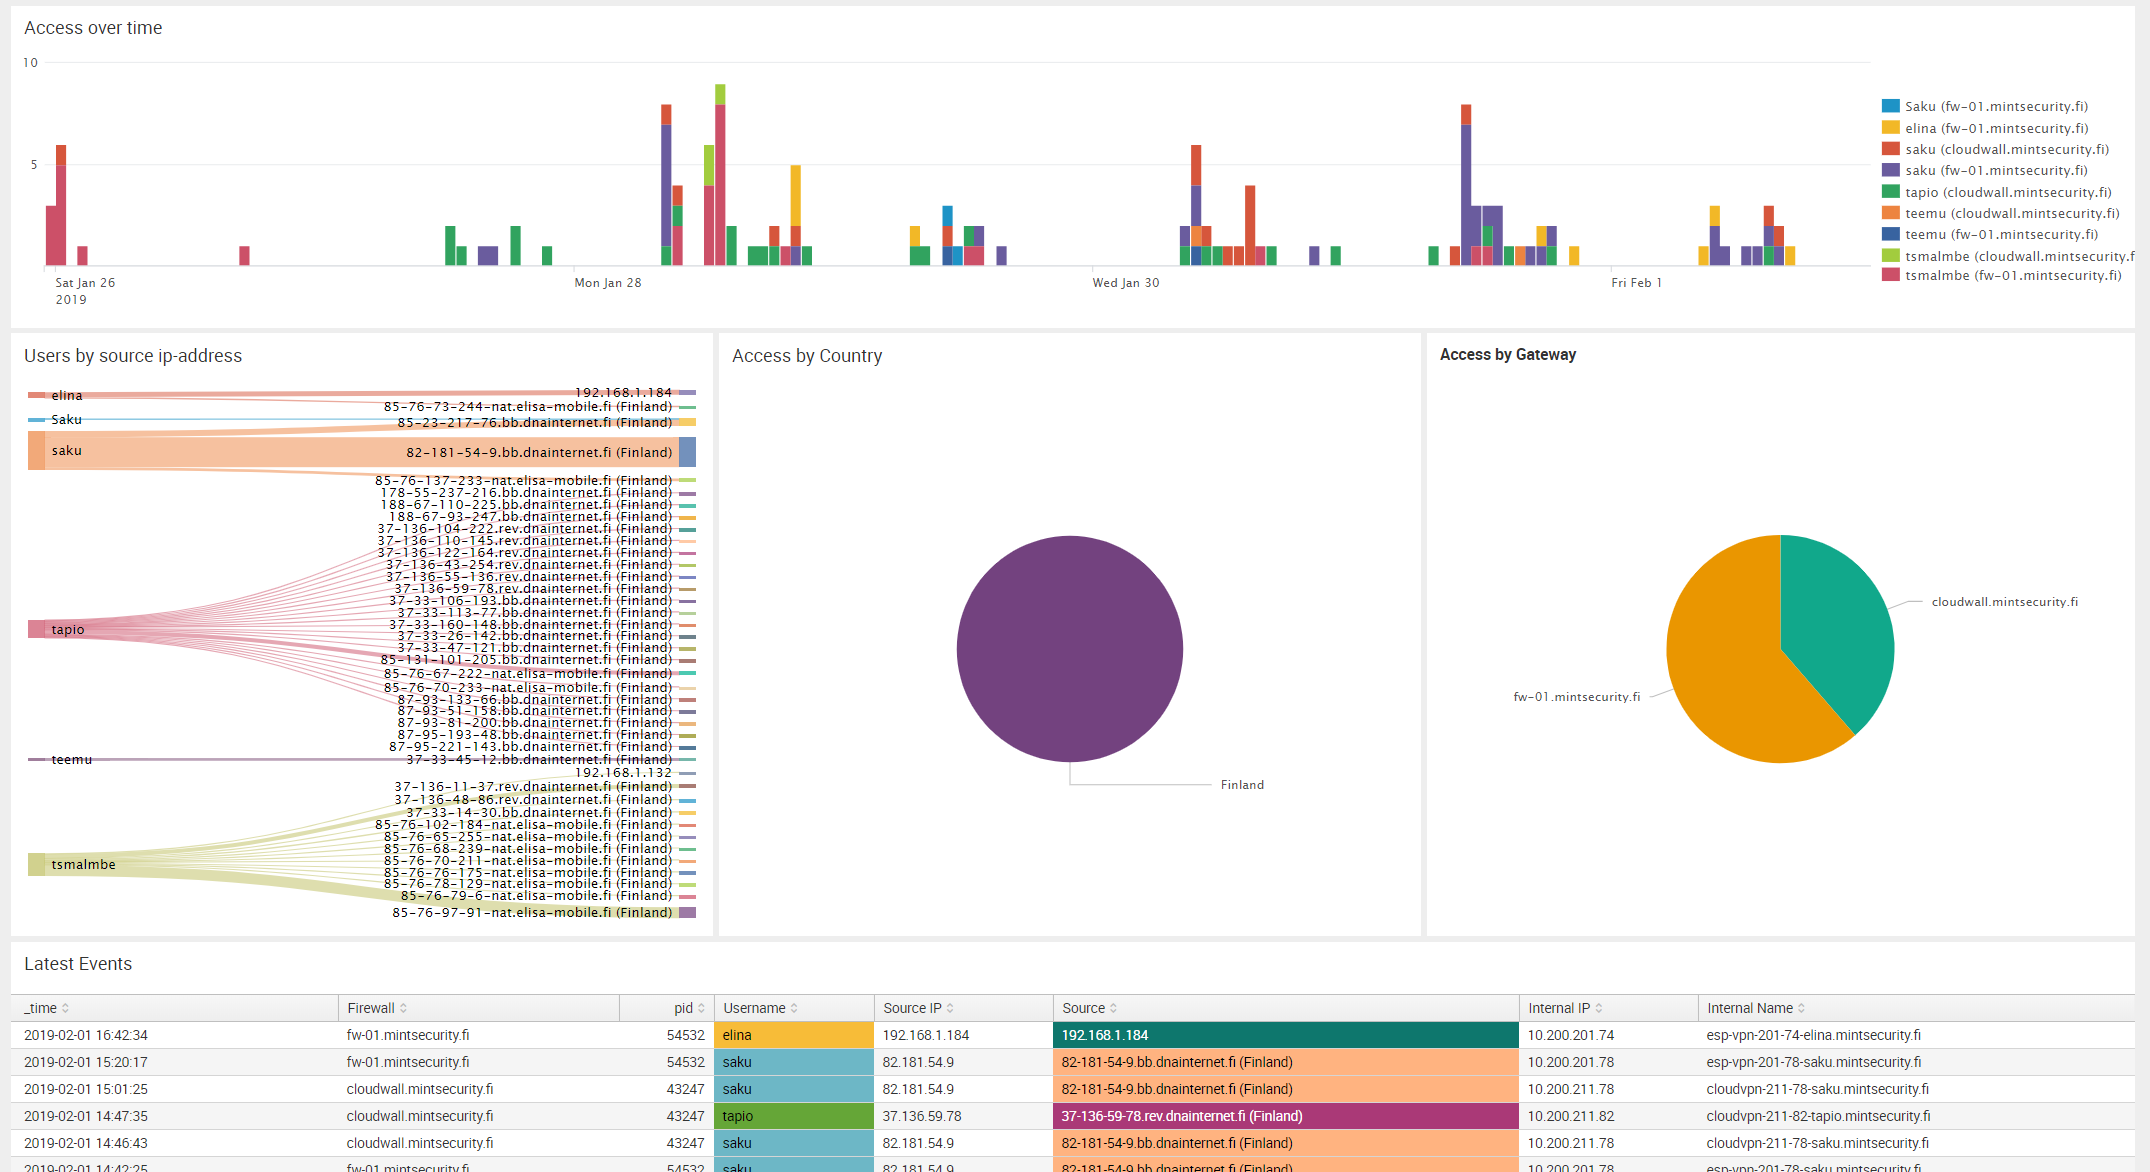
Mint Security - Log Management & SIEM - Splunk and Sentinel
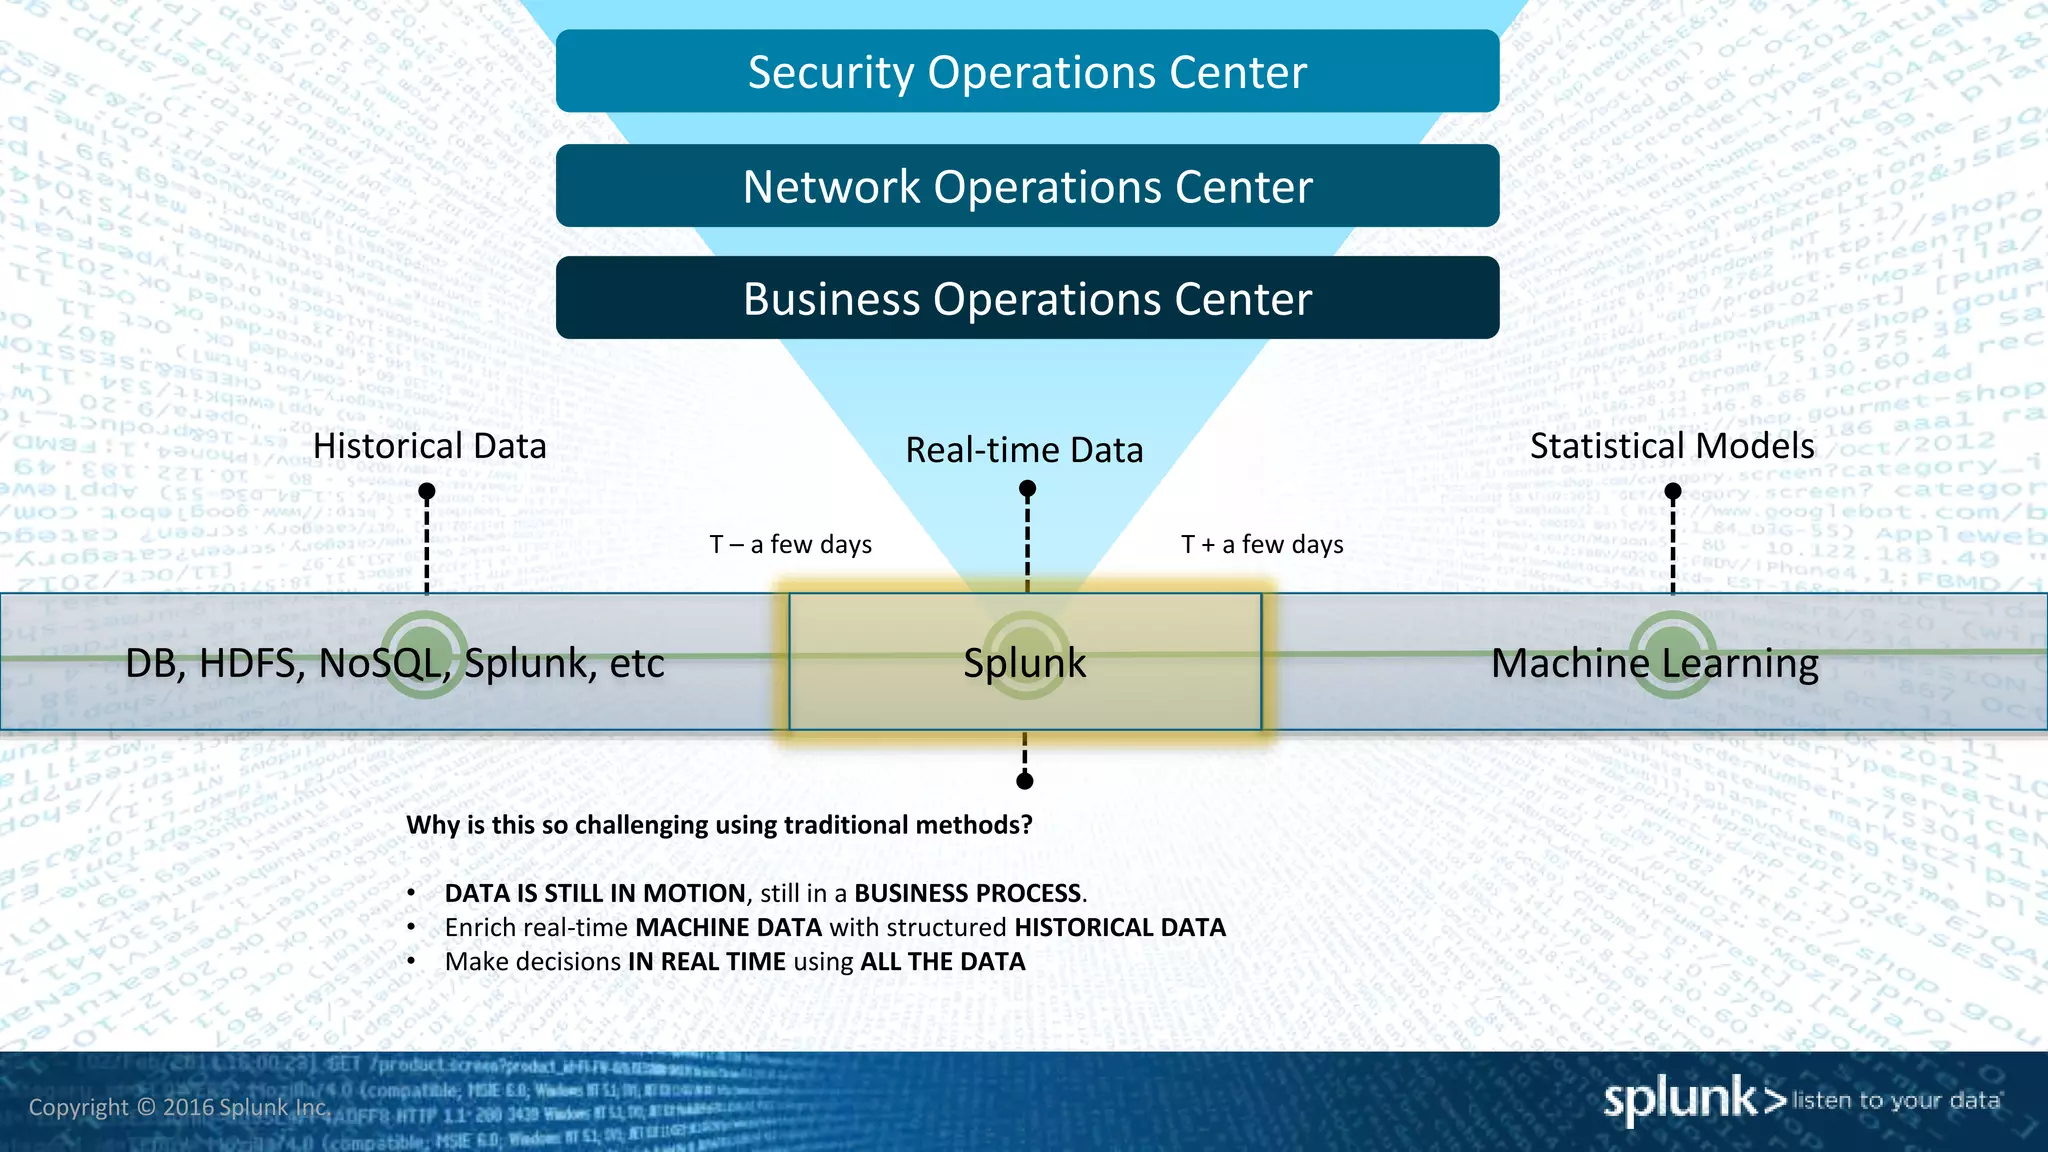
Splunk for Machine Learning and Analytics | PPTX

Splunk for Beginners: FREE Security Lab with Botsv3 Dataset (Dashboards ...

Splunk for Security Monitoring, Part 01 - Hackers Arise