
Splunk Mvfilter Command Tutorial Filter Multi Value Fields With

Splunk mvfilter Command Tutorial - Filter Multi-Value Fields with ...
Splunk SPL mvcombine Command Tutorial - Create Multi-Value Fields with ...

Splunk SPL mvfind Command Tutorial - Search Multi-Value Fields with ...
Splunk SPL mvjoin Command Tutorial - Join Multi-Value Fields with ...
Splunk SPL foreach Command Tutorial - Iterate Over Multiple Fields with ...
Splunk SPL mvzip Command Tutorial - Combine Multi-Value Fields Complete ...

Splunk mvindex Command Tutorial - Extract Multi-Value Fields by Index ...
Splunk mvsort Command Tutorial - Sort Multi-Value Fields Complete Guide ...
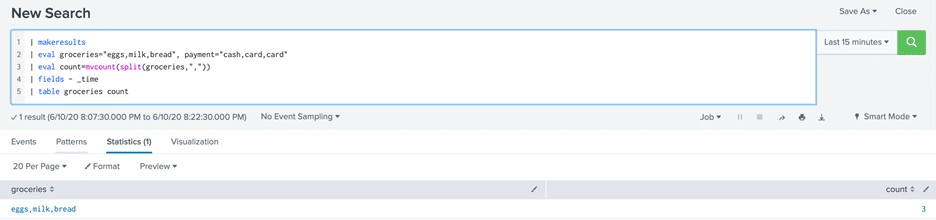
Working with Multivalue Fields in Splunk | TekStream Solutions
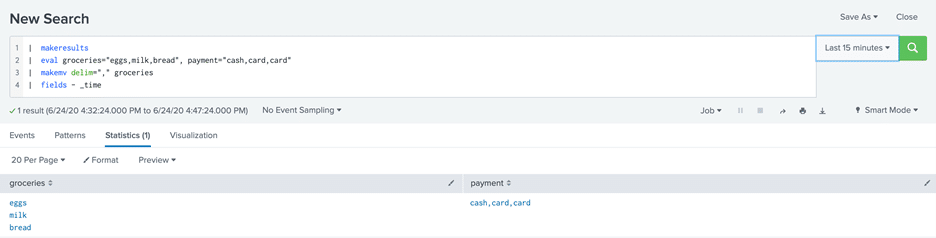
Working with Multivalue Fields in Splunk | TekStream Solutions
Advertisement Space (300x250)
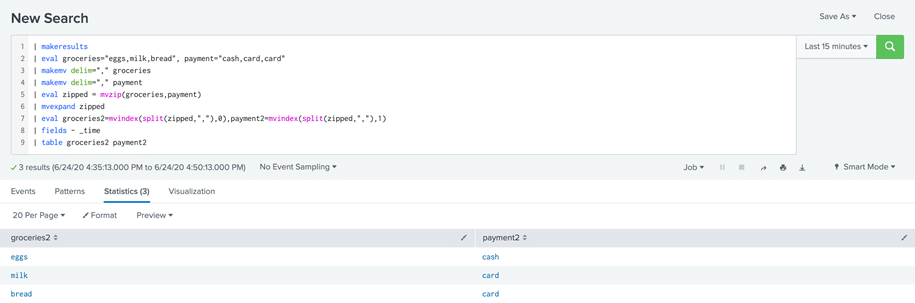
Working with Multivalue Fields in Splunk | TekStream Solutions

Splunk SPL Split Command Tutorial - Divide Field Values Into Multiple ...

Solved: Filter MV field for specified value - Splunk Community
Table showing fields with empty values from excluded events | Splunk
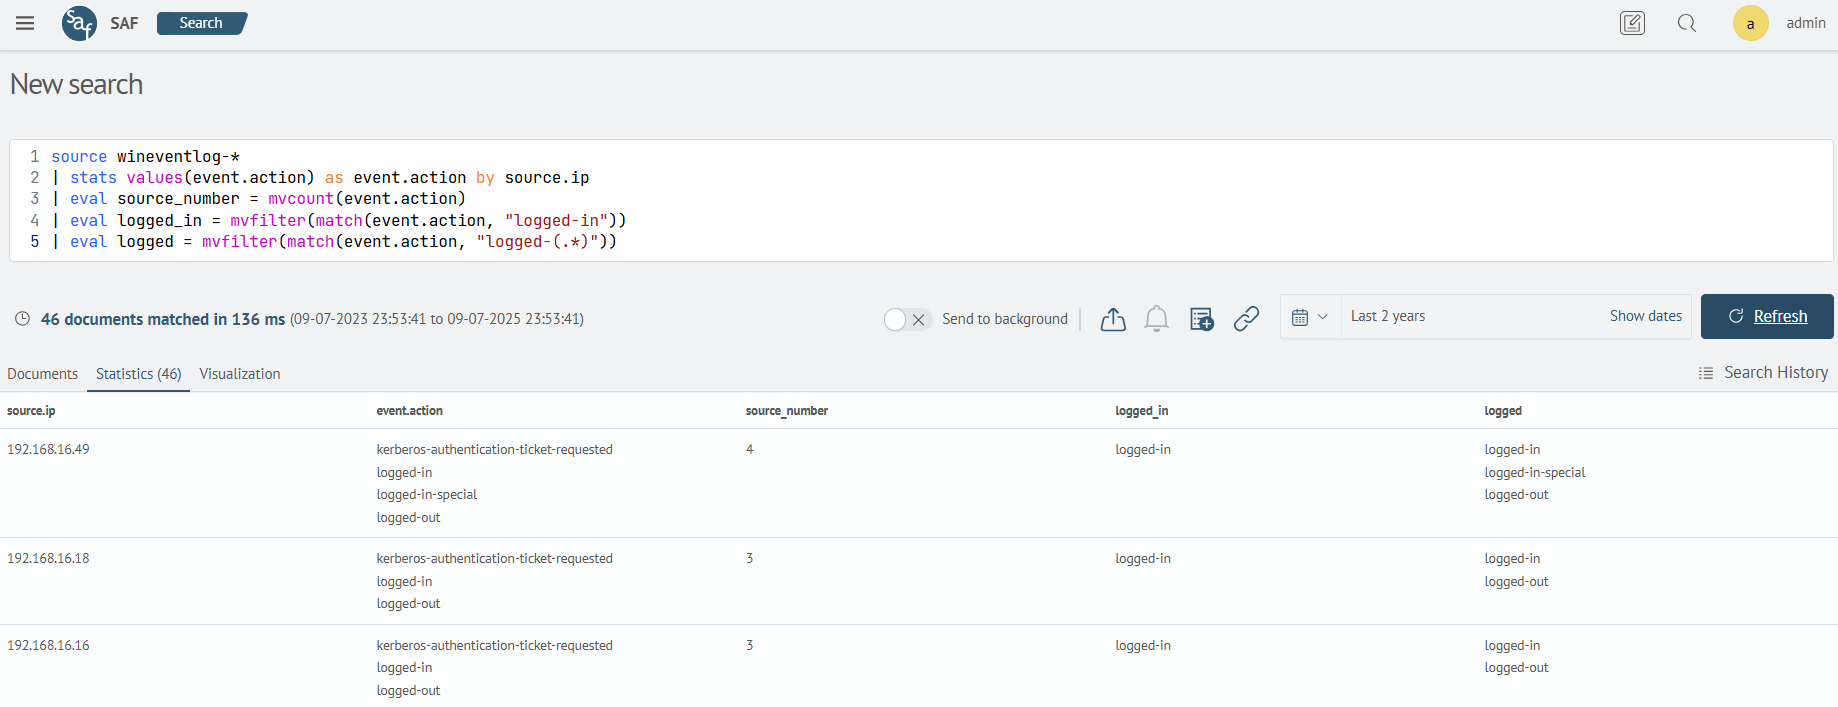
Evaluating fields with multiple values | Documentation | SAF

Evaluating fields with multiple values | Documentation | SAF
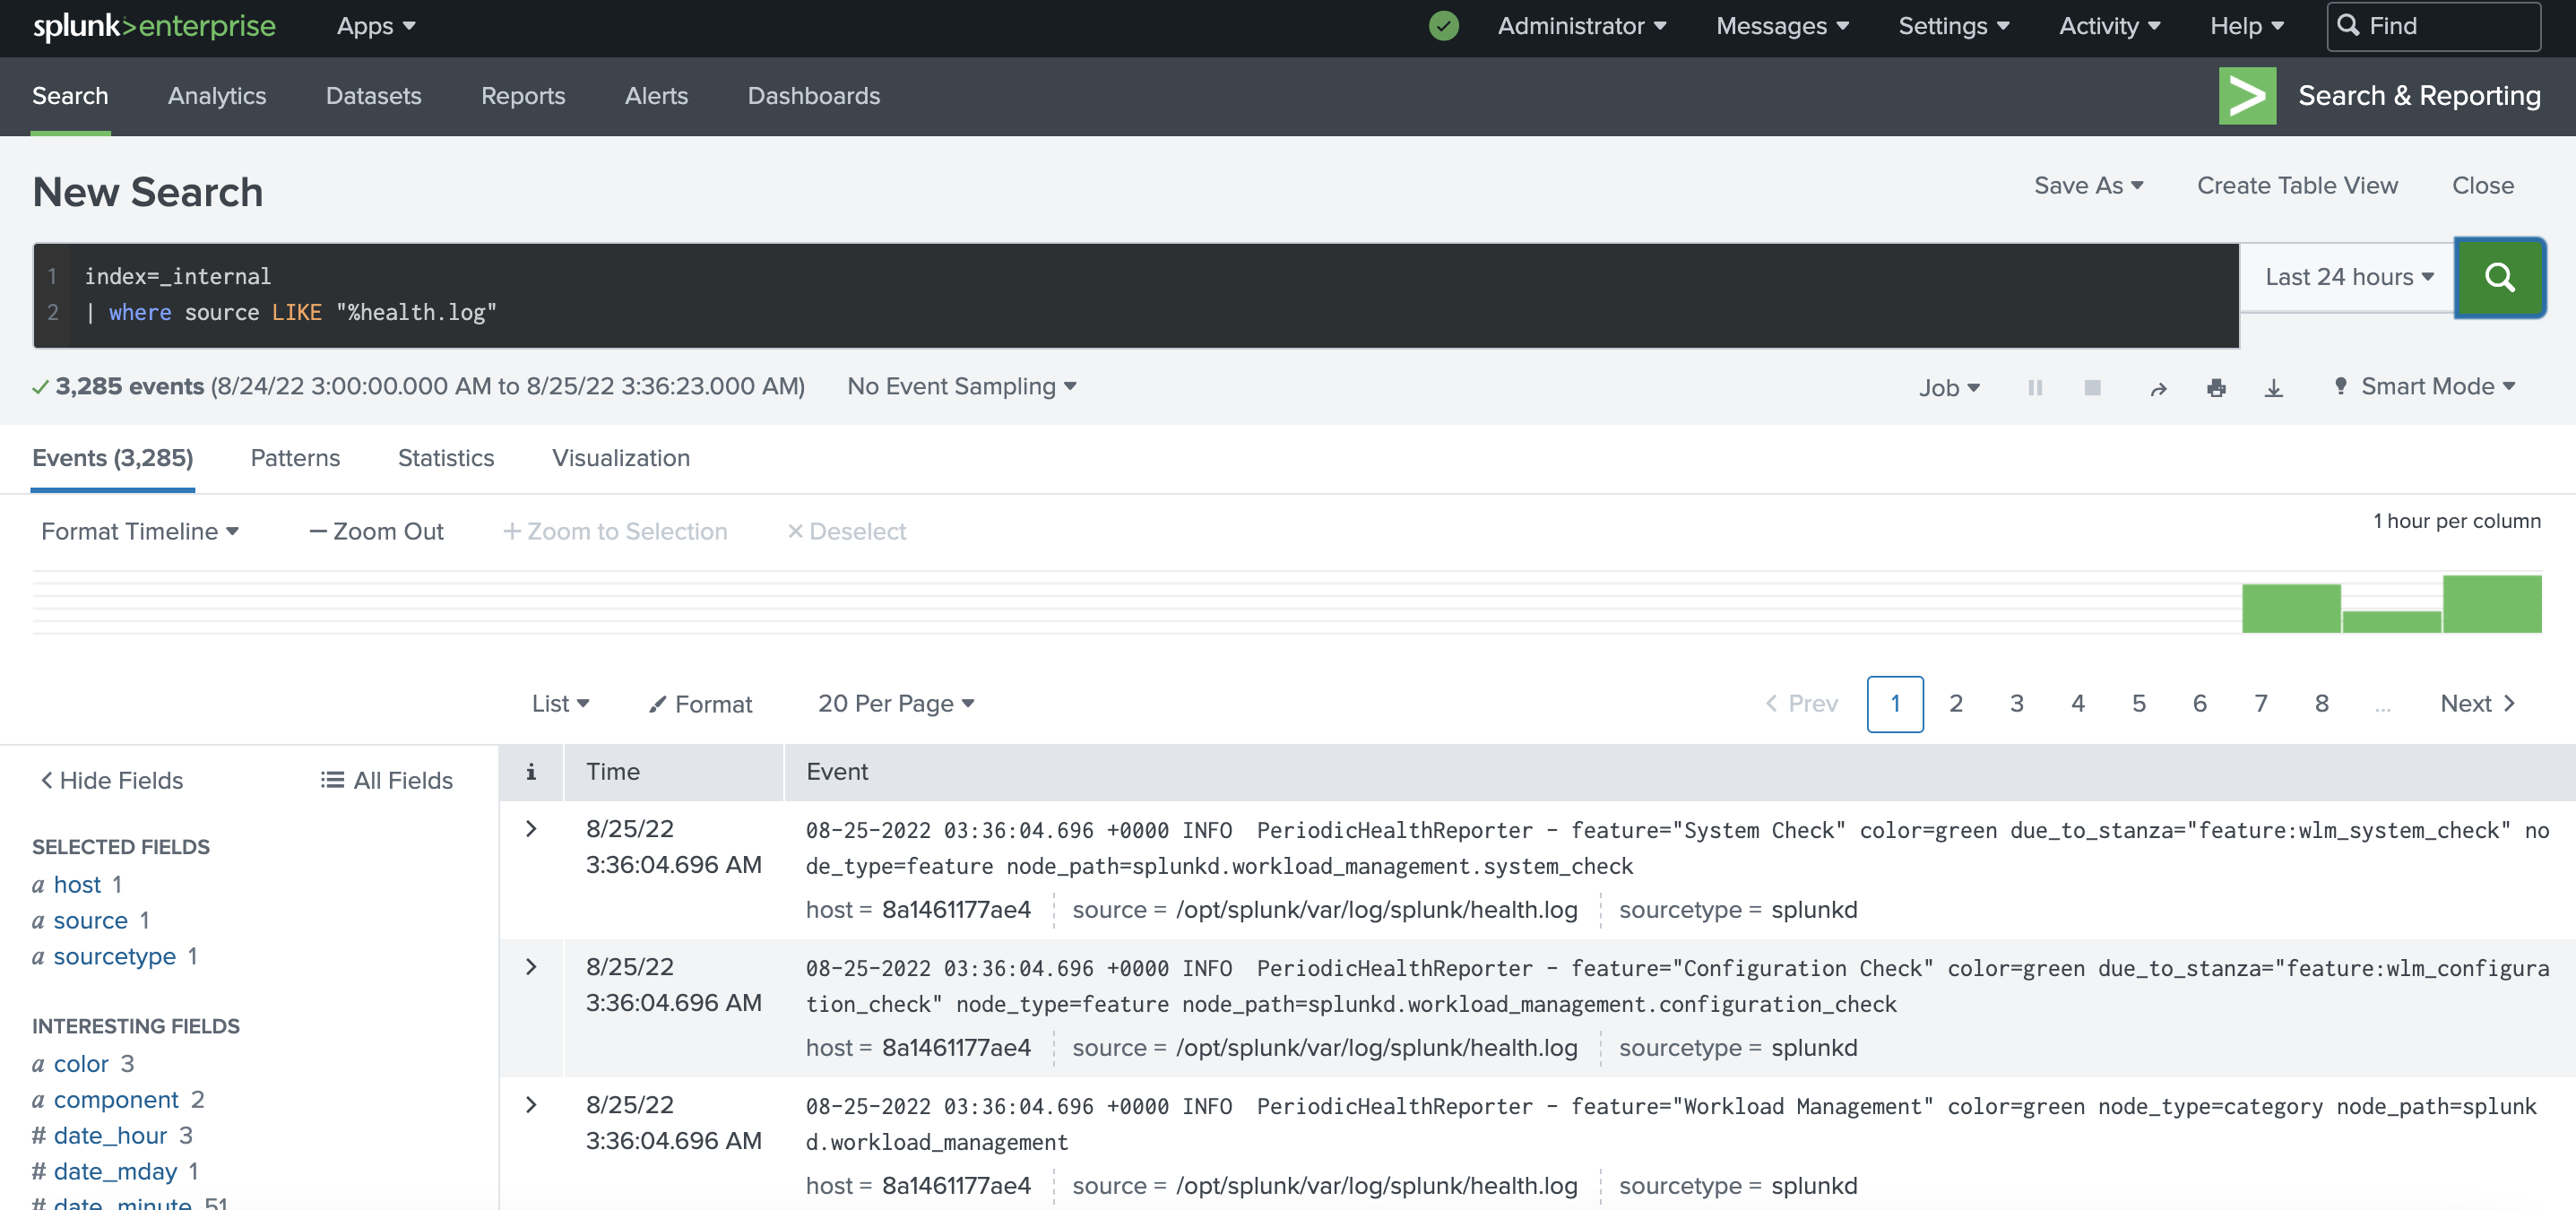
Splunk Filter Example at Hattie Branch blog

Splunk Filter Example at Hattie Branch blog
Primary: Splunk Makemv Command: Handling Multi-Value Fields for Better ...
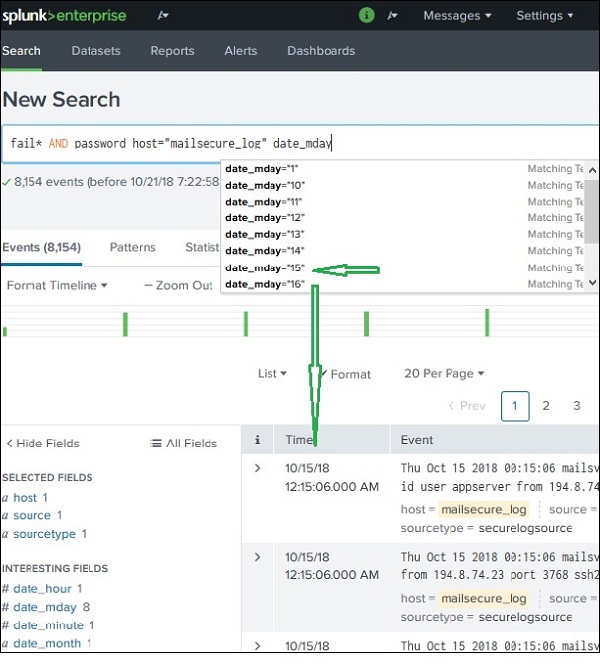
Splunk Fields Explained at Barbara Fowler blog
Advertisement Space (336x280)

Splunk Tutorial For Beginners | Learn What is Splunk [Updated 2021]
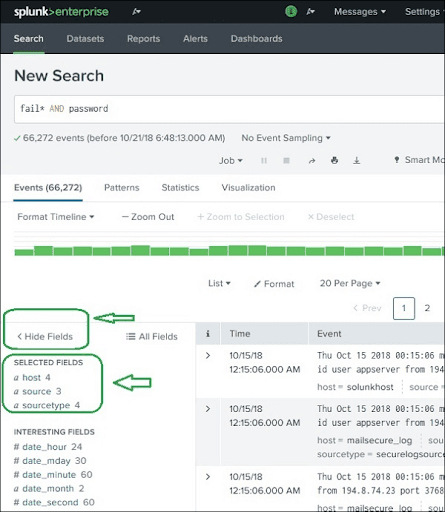
Splunk Tutorial For Beginners | Learn What is Splunk [Updated 2025]
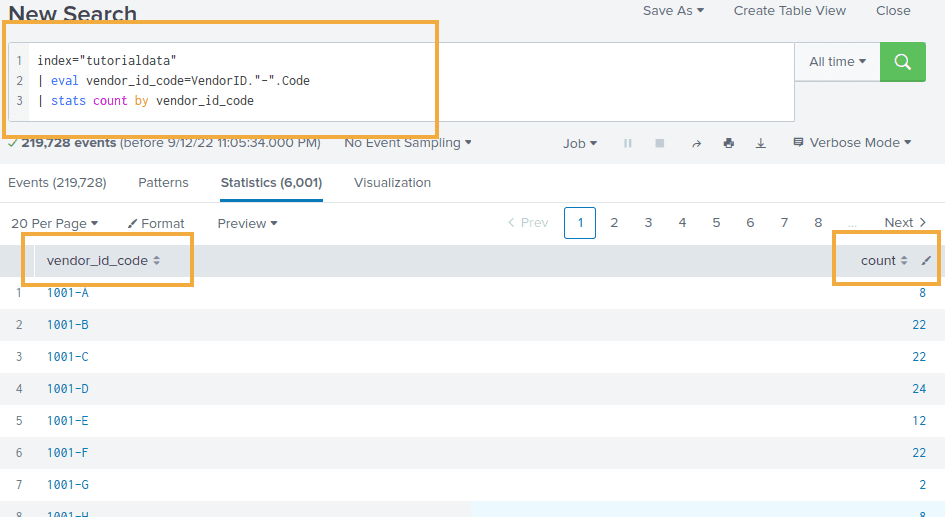
Splunk Groupby: Examples with Stats
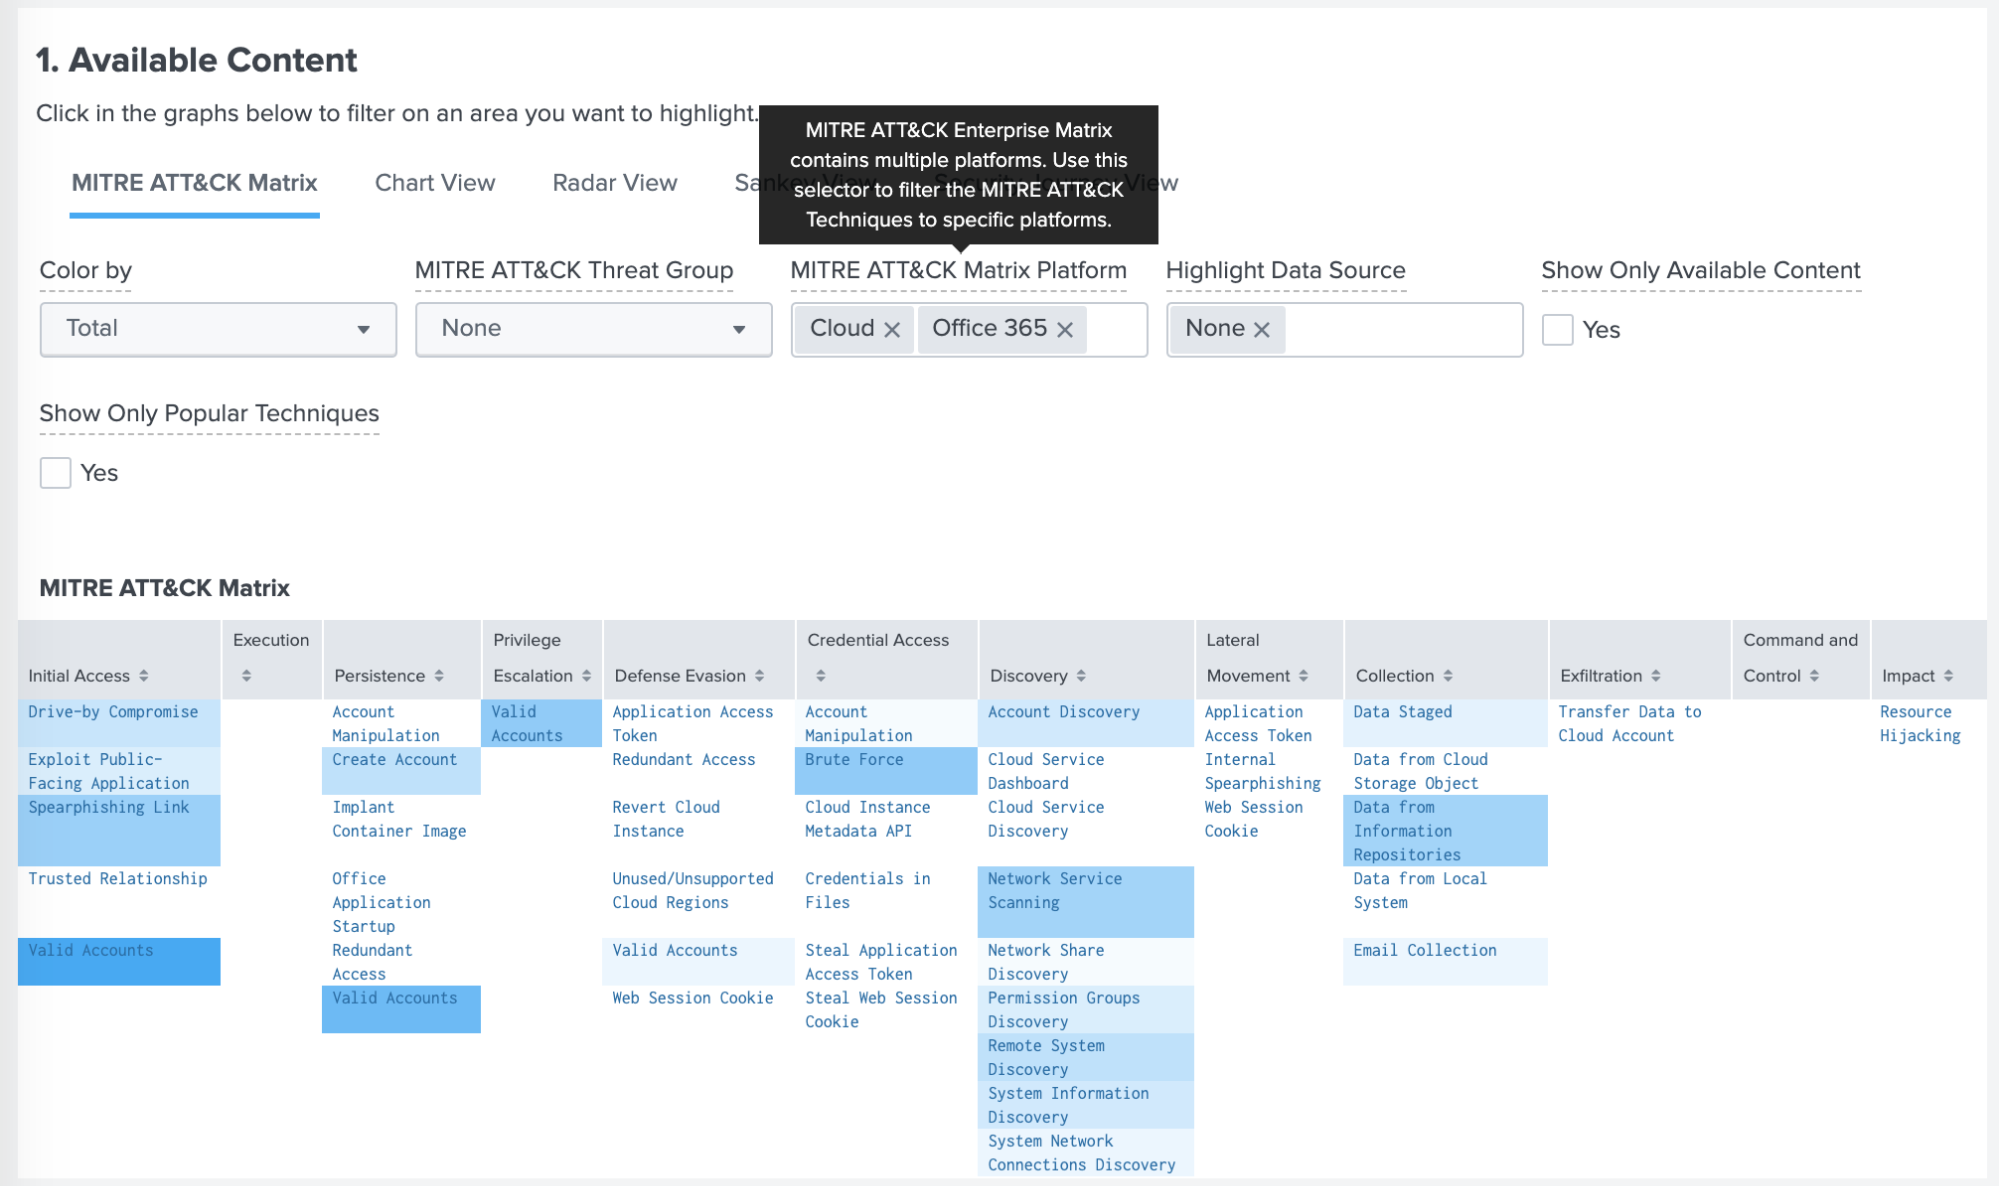
Splunk Filter Example at Hattie Branch blog

Solved: Get first value of a field after filtering its row... - Splunk ...

Evaluating fields with multiple values | Documentation | SAF
Stats Command Produce Different Results on Search heads | Splunk

Splunk Fields Explained at Barbara Fowler blog

Splunk fundamentals | How we can create splunk dashboard with ...
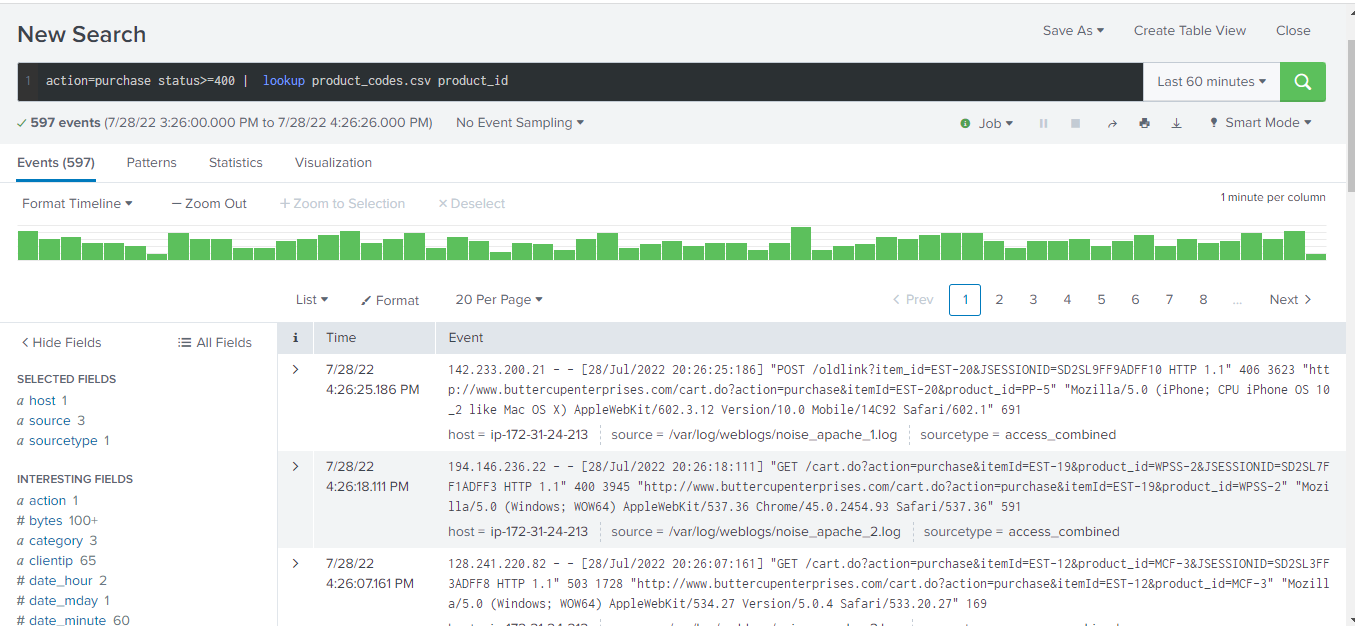
How To Use Splunk Platform Visualizations With Sample Data Insights ...
Advertisement Space (336x280)
Multiple filter option in dashboard tables - Splunk Community

Solved: How to move multivalue fields as separate columns? - Splunk ...
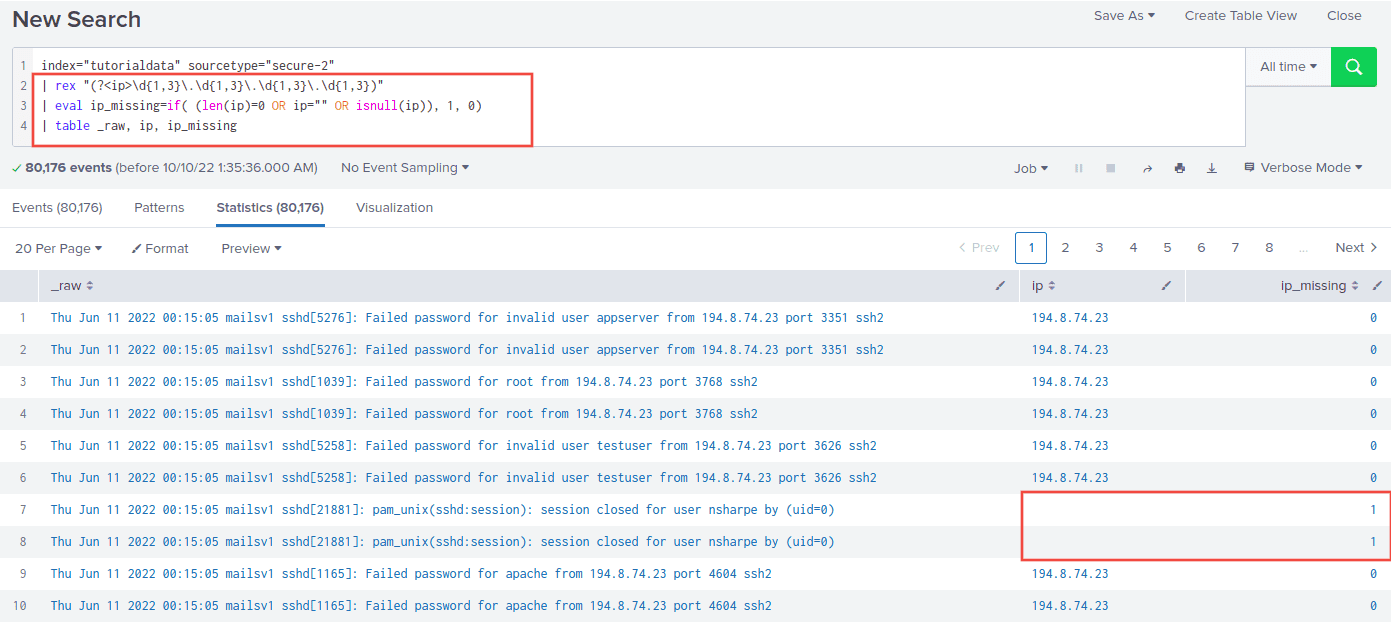
Splunk examples: Dealing with null/empty values
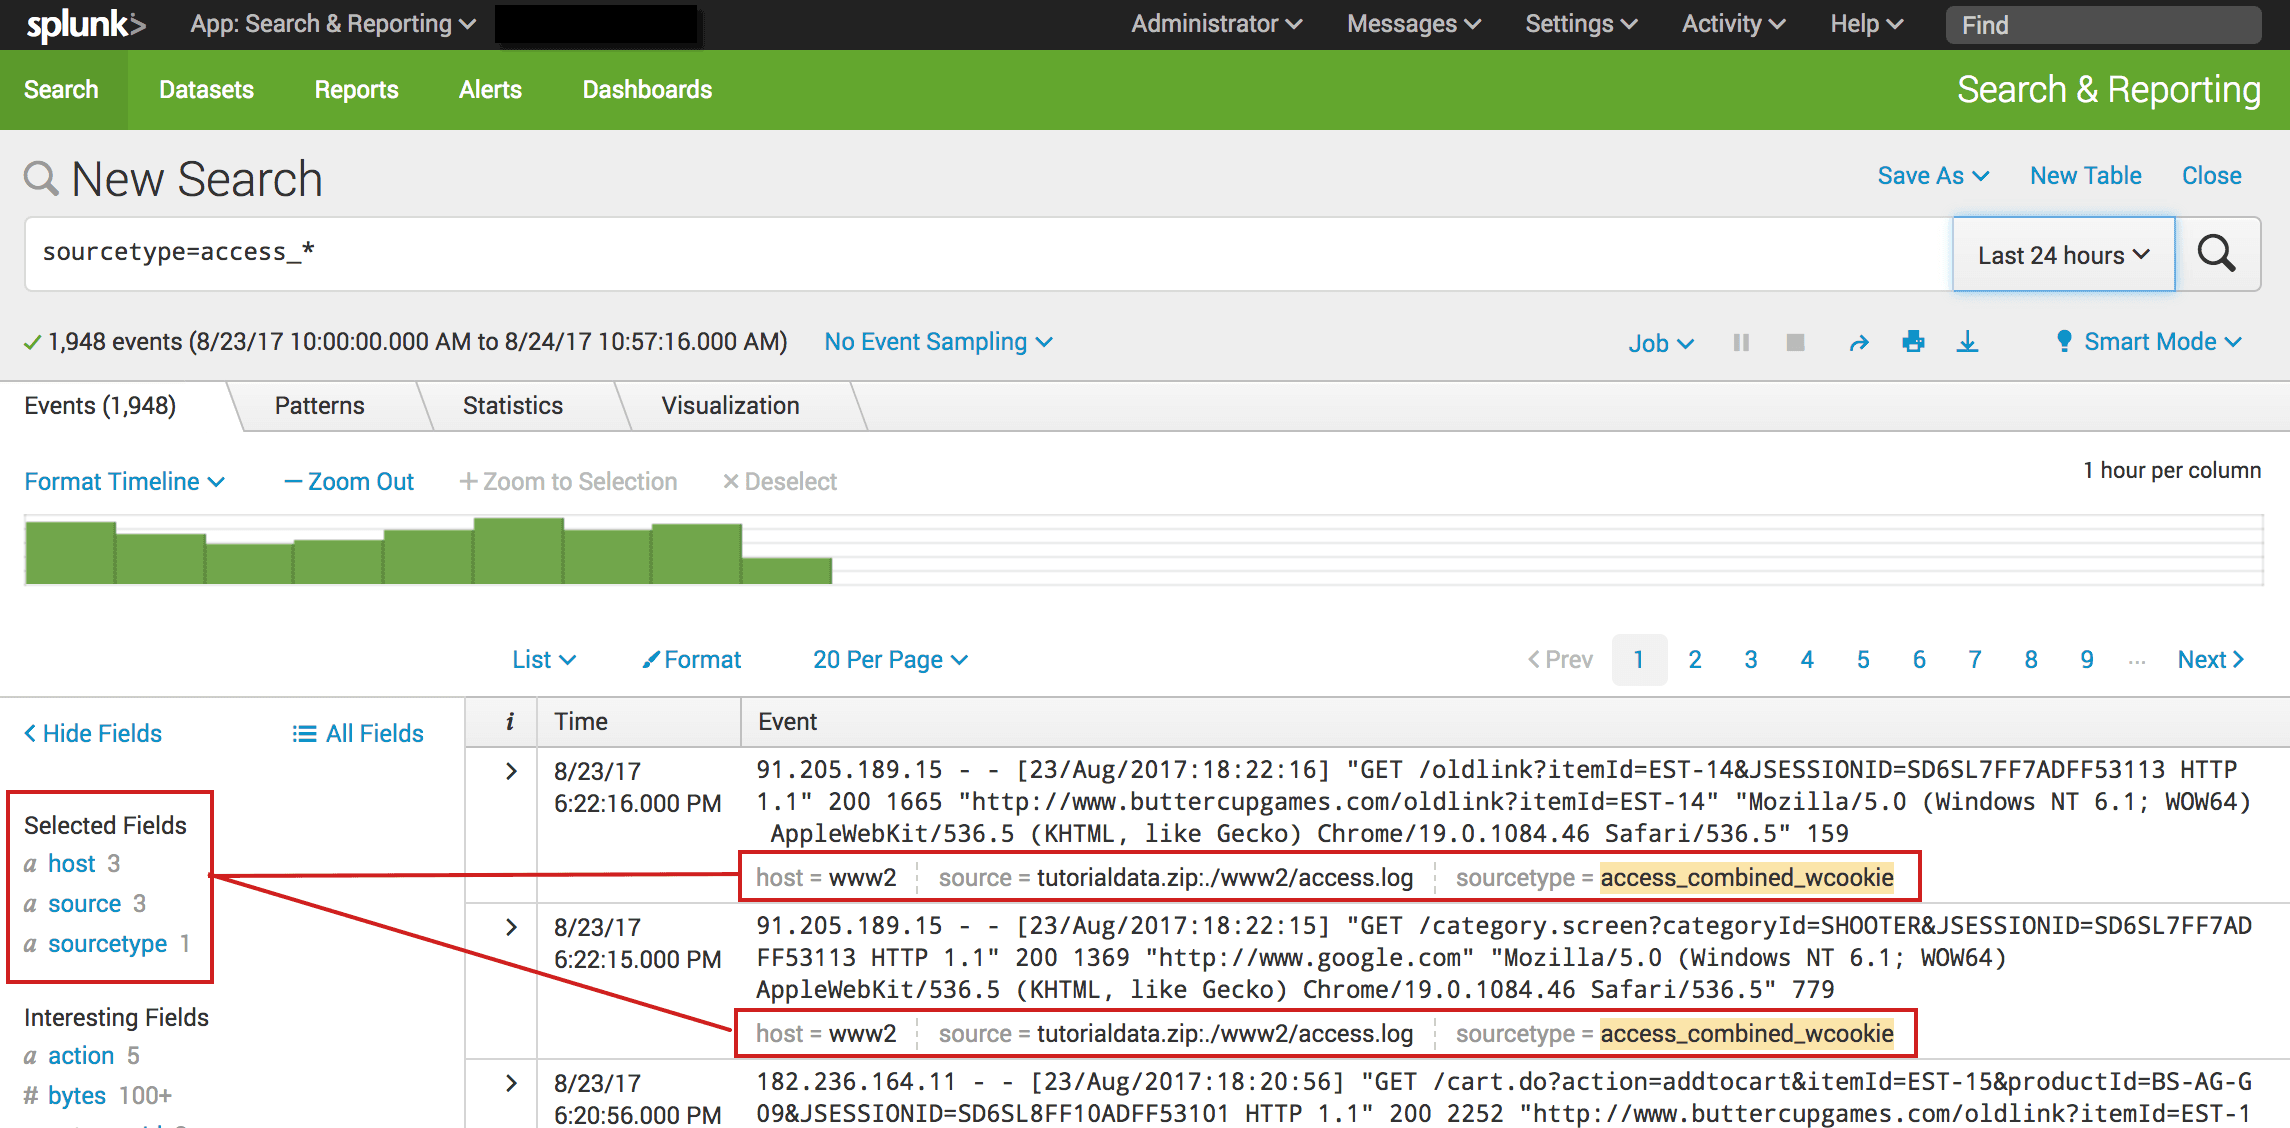
Use fields to search - Splunk Documentation

Extracting Nested JSON Fields in Splunk | TekStream Solutions

Solved: How to list multiple fields results for multiple f... - Splunk ...