
Table Splunk Documentation
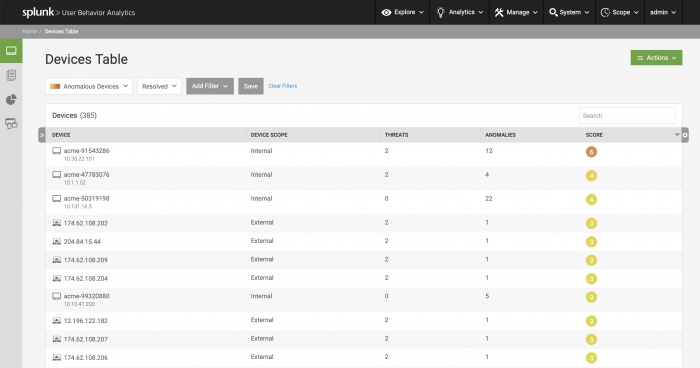
See all devices on the Devices Table - Splunk Documentation
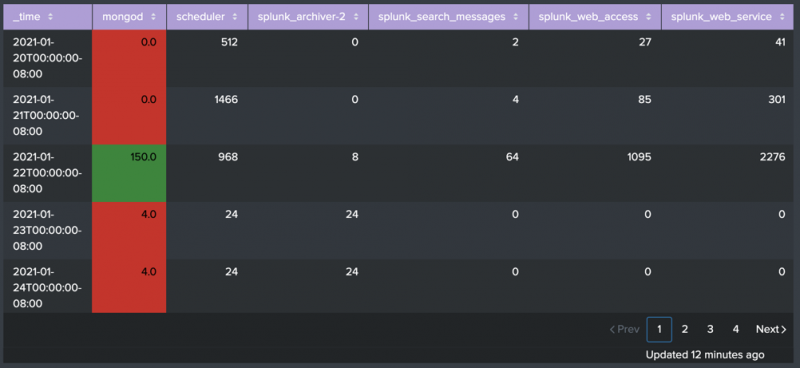
Table - Splunk Documentation
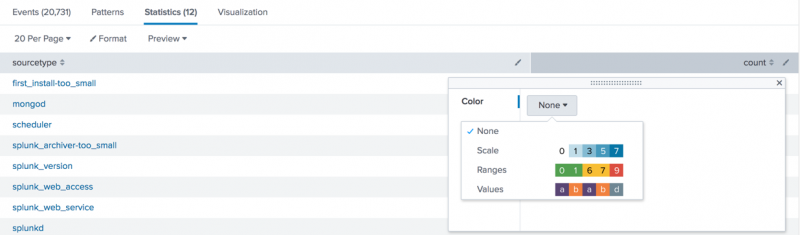
Format table visualizations - Splunk Documentation
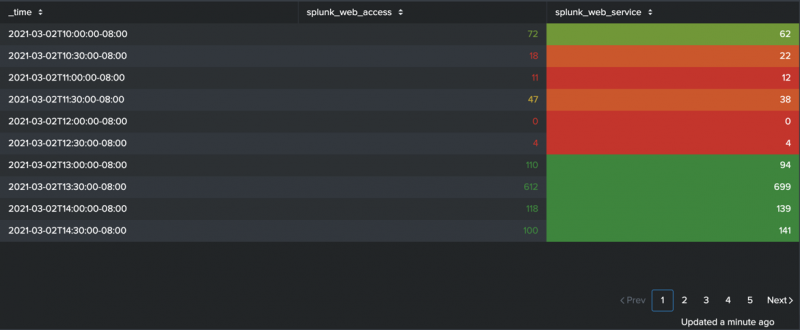
Table - Splunk Documentation

Table - Splunk Documentation

Table - Splunk Documentation
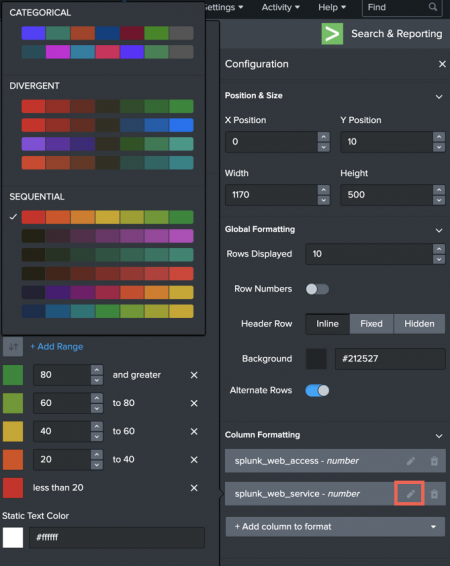
Table - Splunk Documentation

Format table visualizations - Splunk Documentation

Table - Splunk Documentation
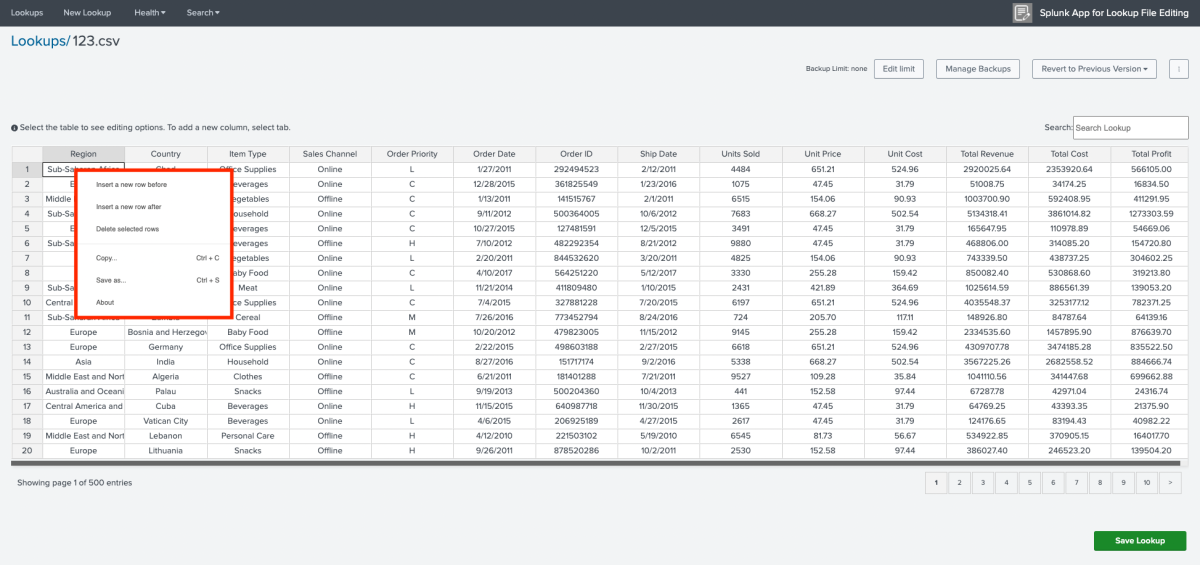
Splunk Check Size Of Lookup Table at Joanne Bender blog
Advertisement Space (300x250)
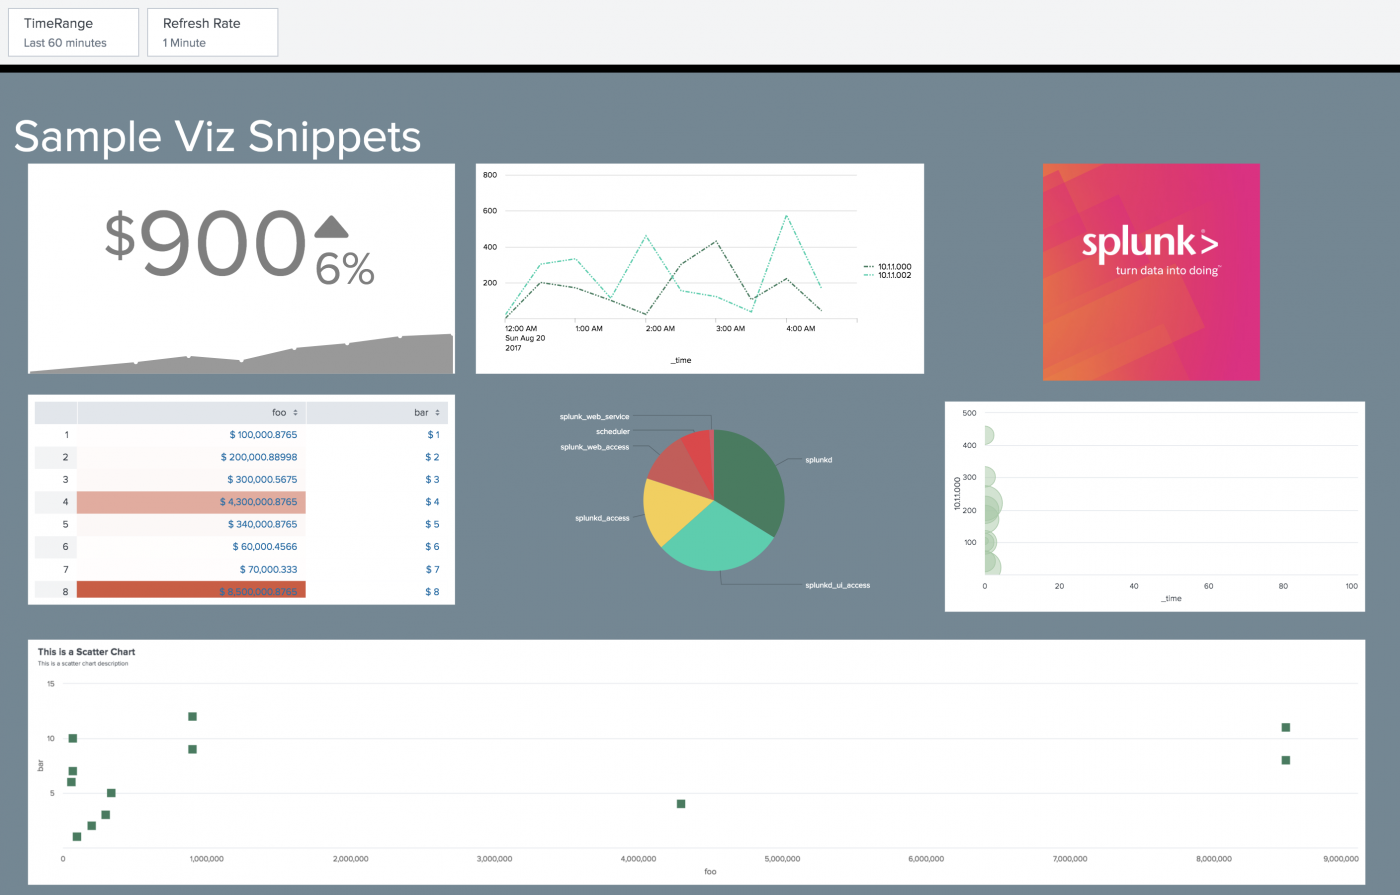
Add visualizations to glass tables in ITSI - Splunk Documentation

How to make table structure in link format? - Splunk Community
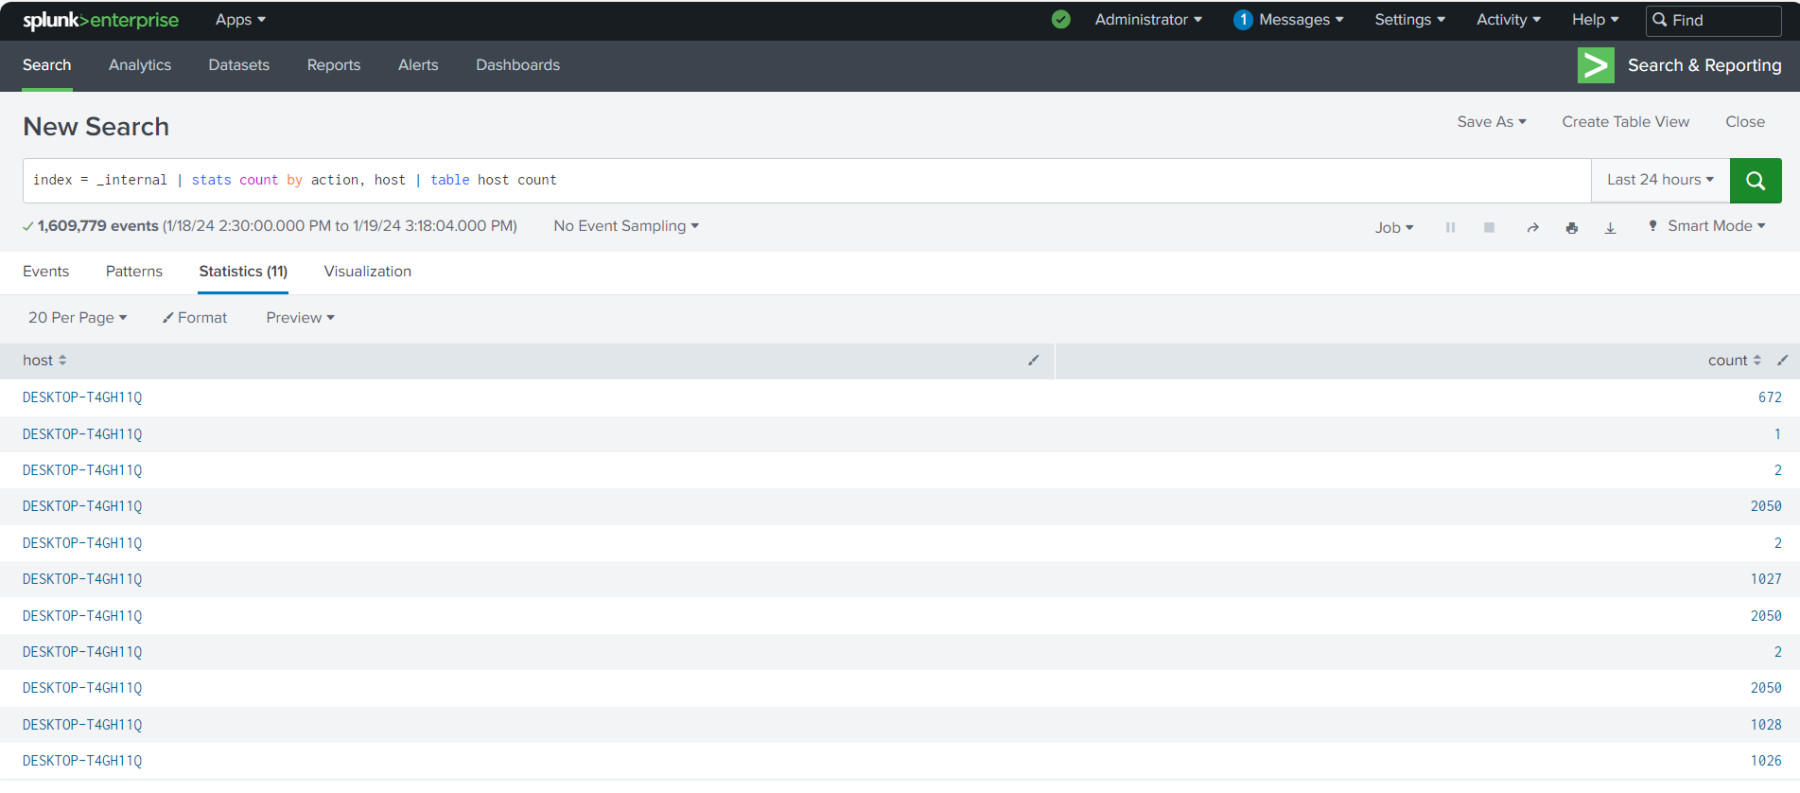
Splunk table command- Generation and data visualization

How to create a table row expansion? - Splunk Community
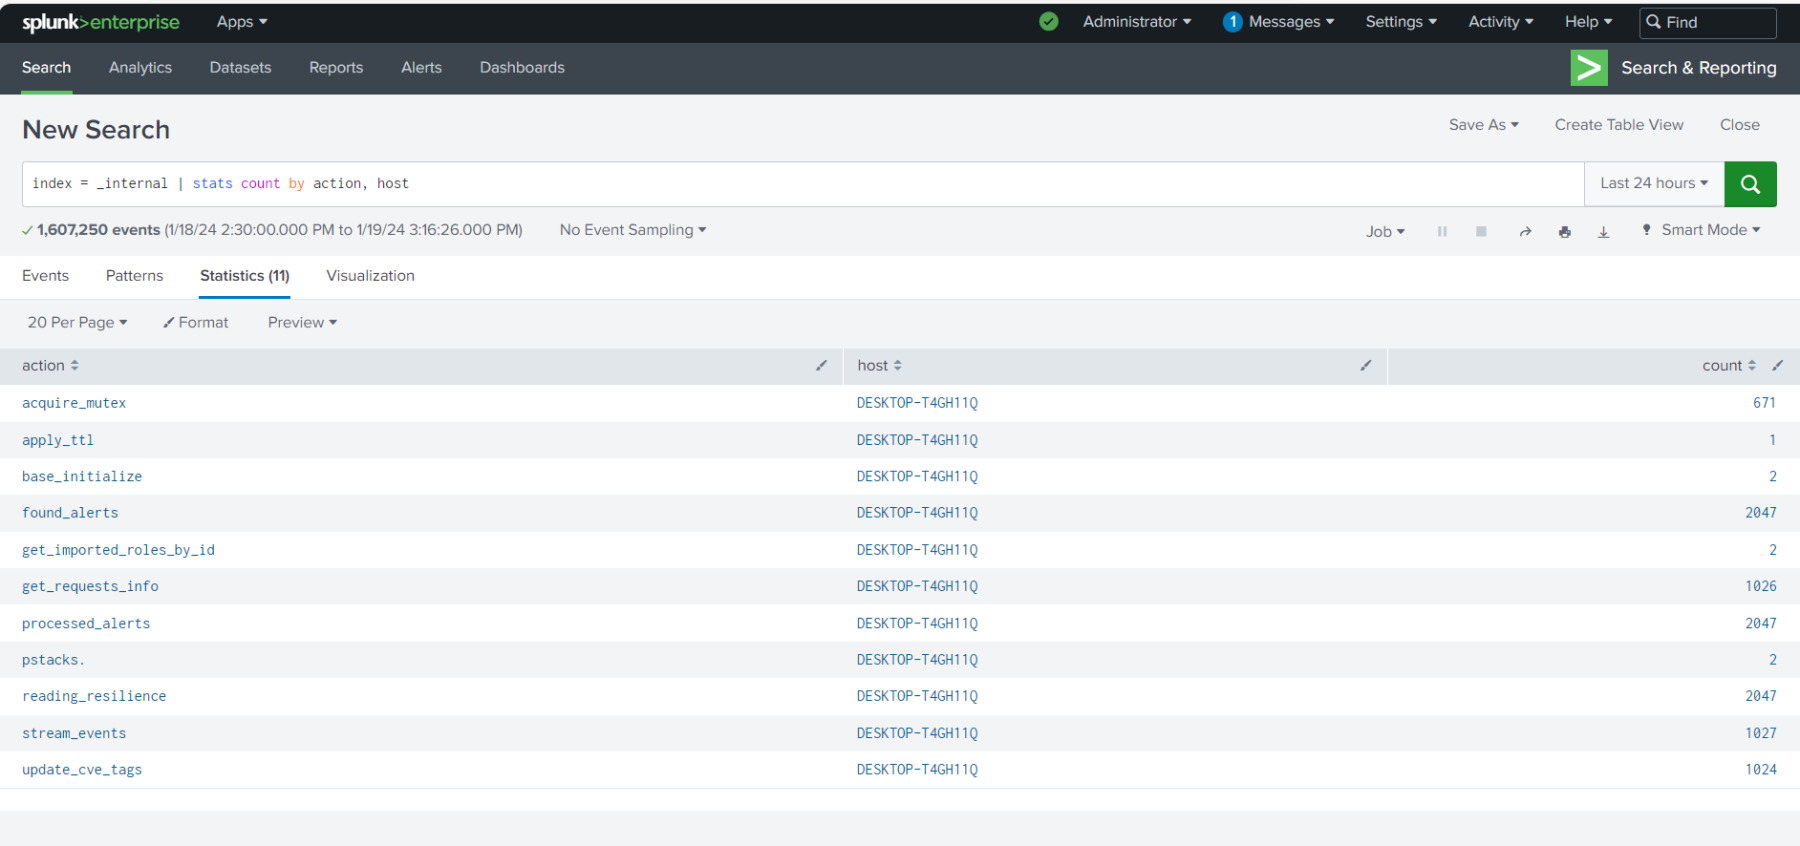
Splunk table command- Generation and data visualization
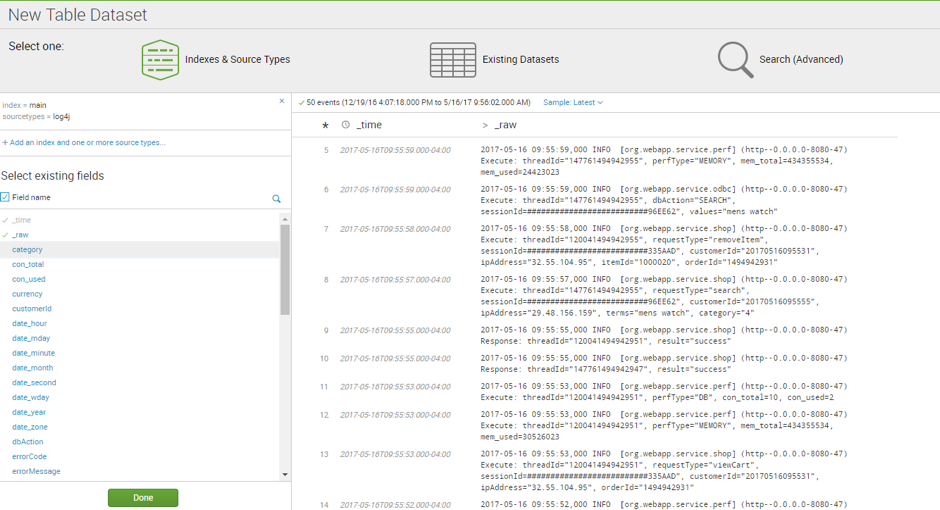
Diving into Splunk Table Datasets - Discovered Intelligence
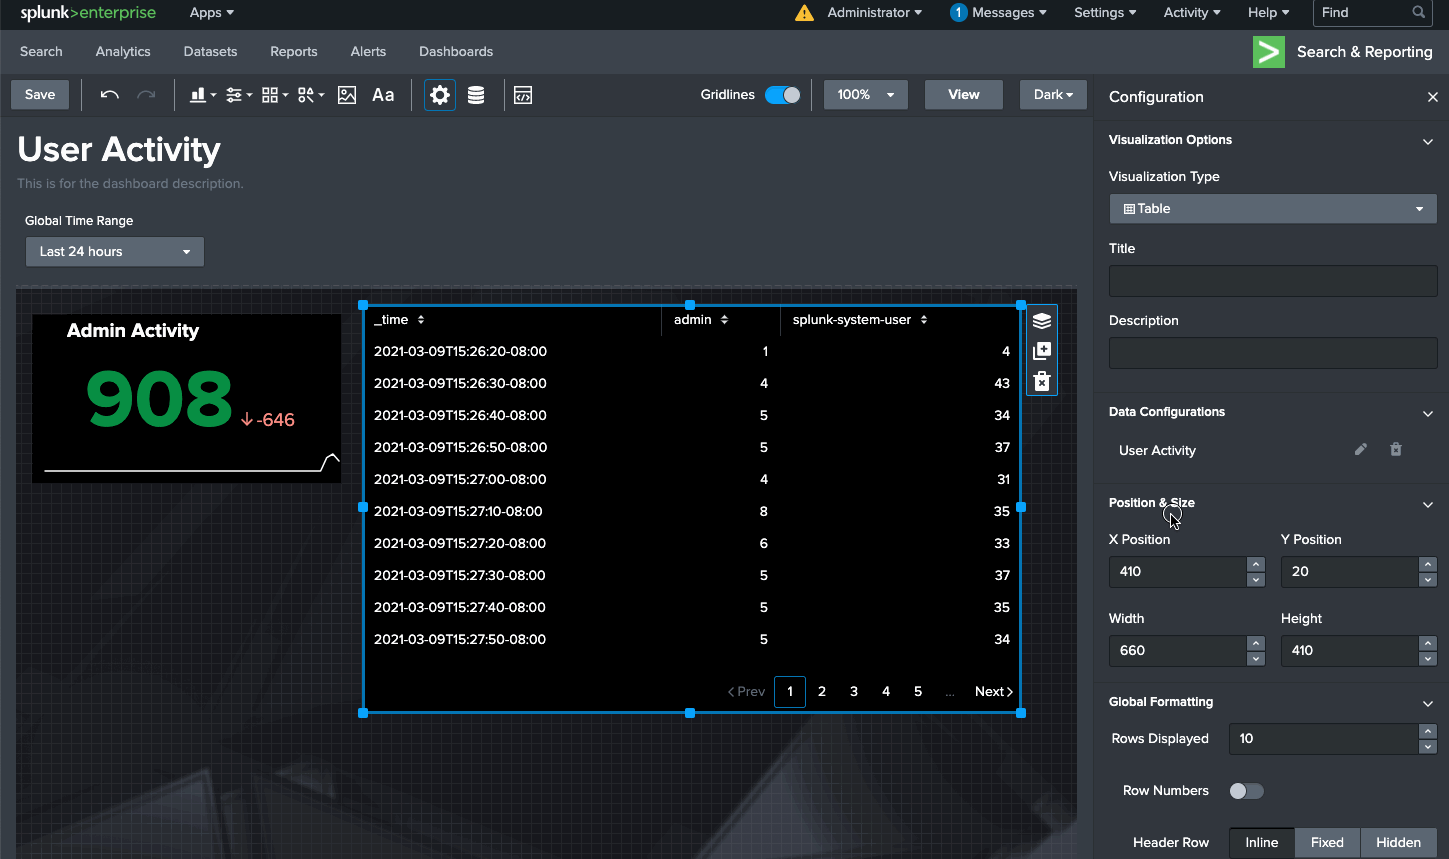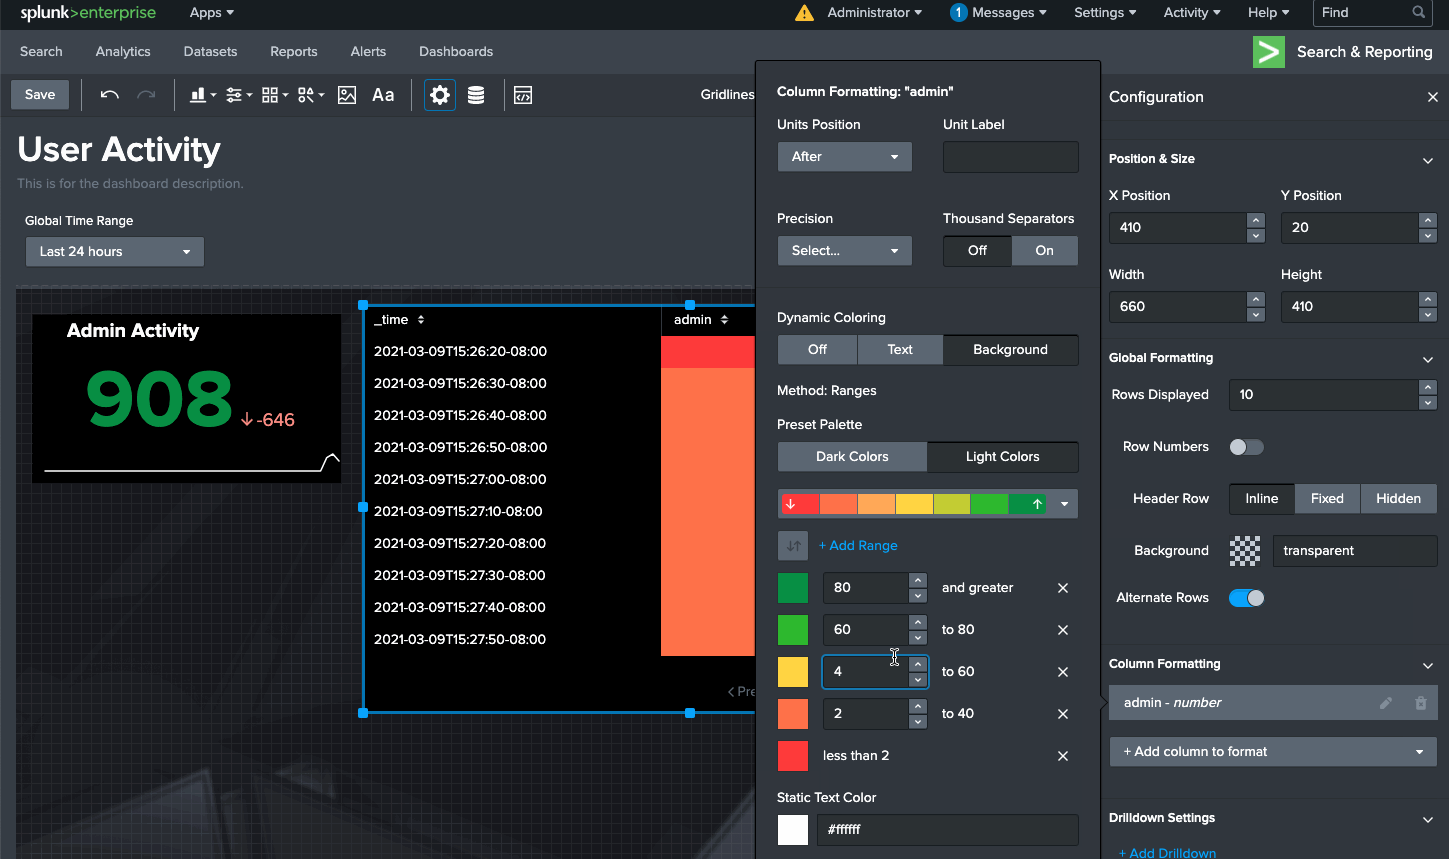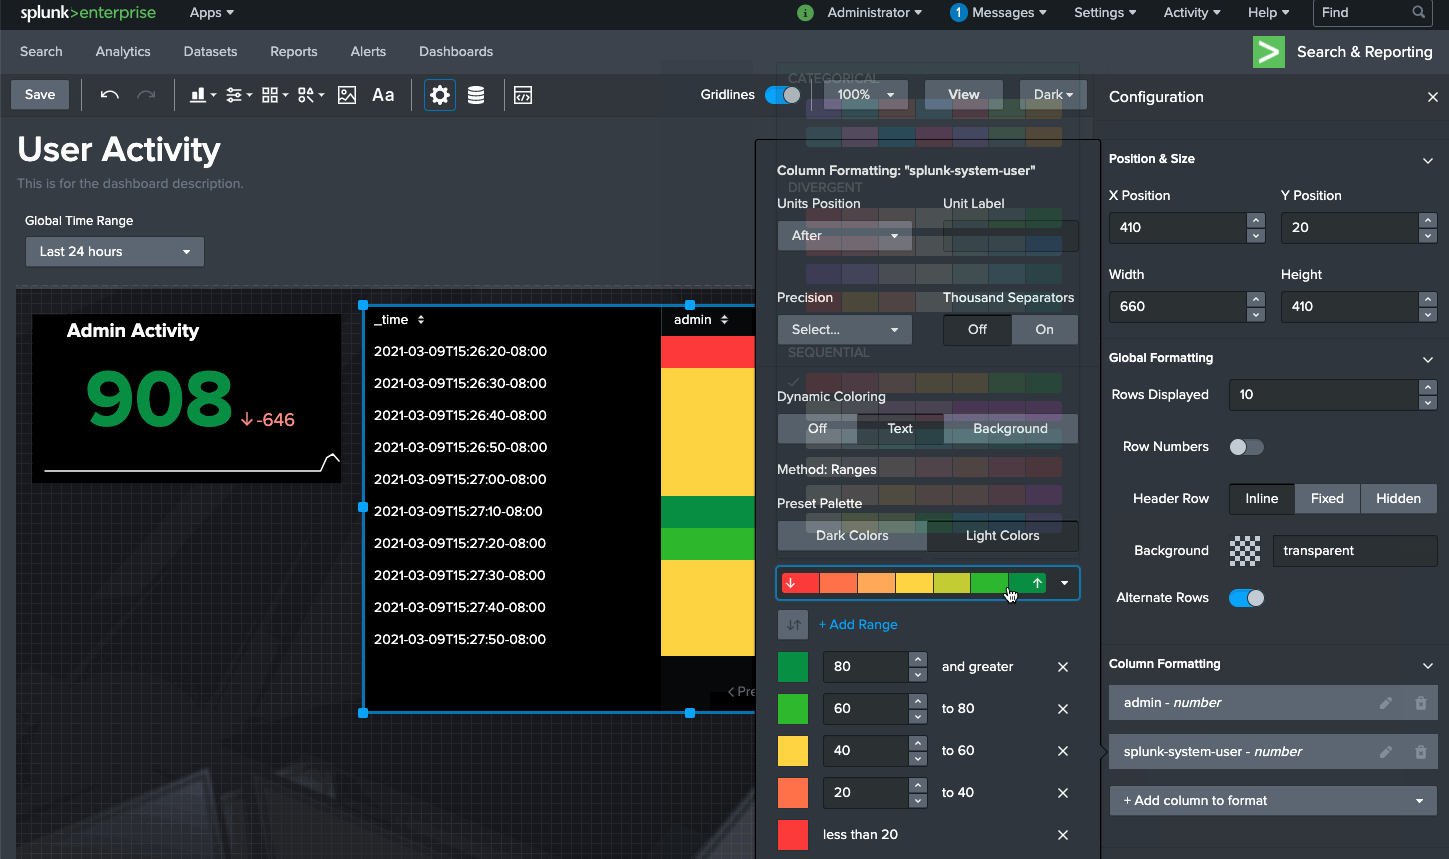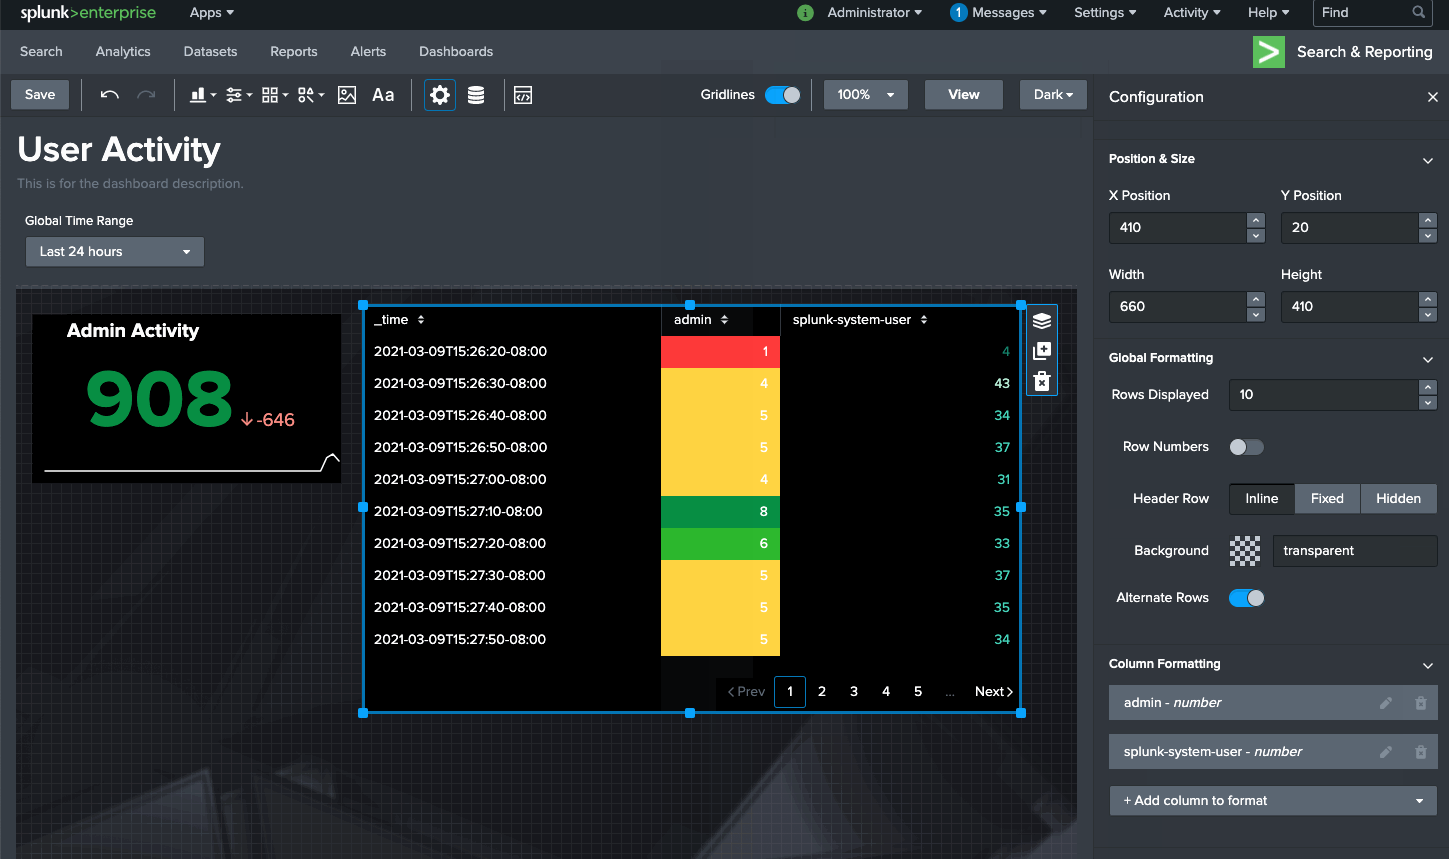
Splunk dashboard studio documentation - seattlekool

How to make table structure in link format? - Splunk Community
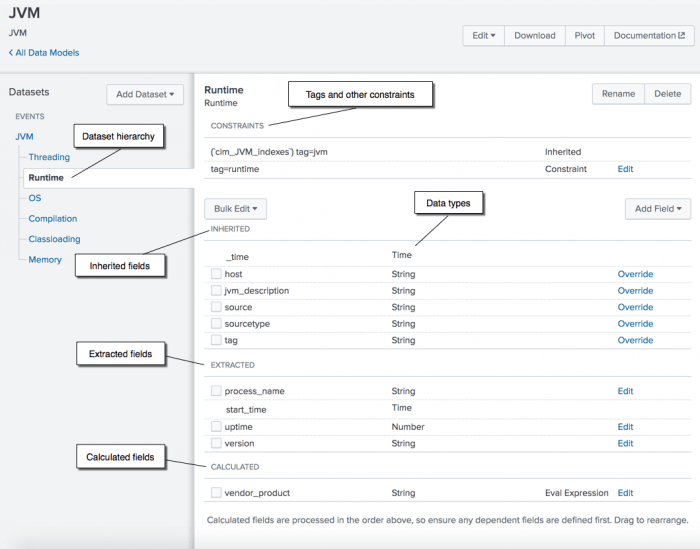
How to use the CIM data model reference tables - Splunk Documentation

How to create a Table Dashboard on Splunk - YouTube
Advertisement Space (336x280)

Solved: Need to expand and create a table from one row to ... - Splunk ...
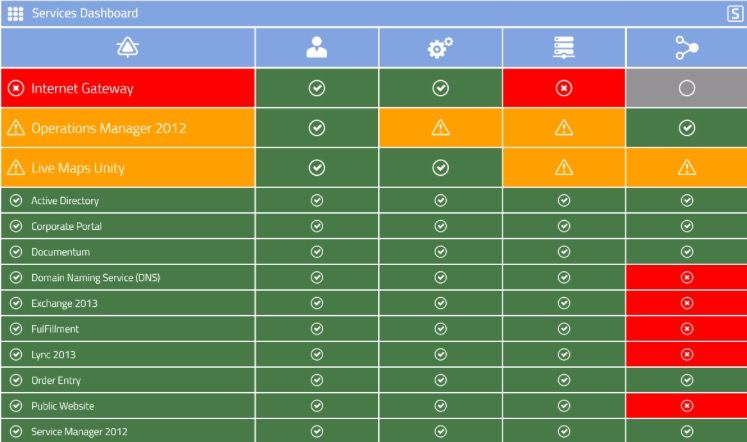
Solved: How to make a Splunk table visualization more inte... - Splunk ...
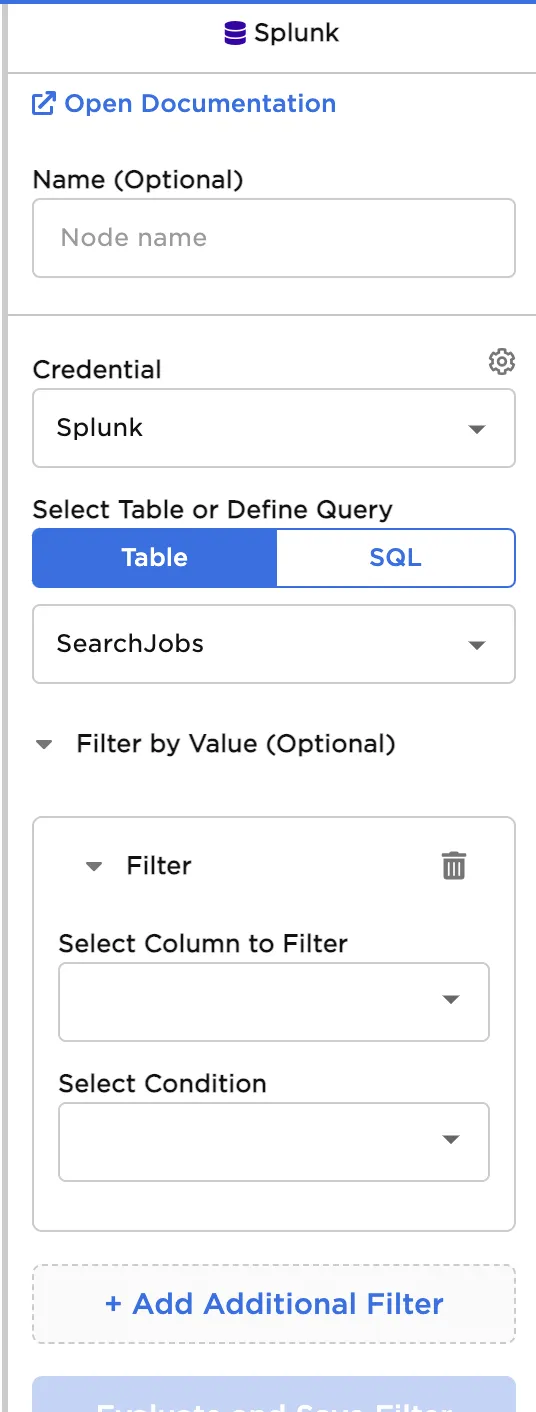
Splunk Node | C3 AI Documentation
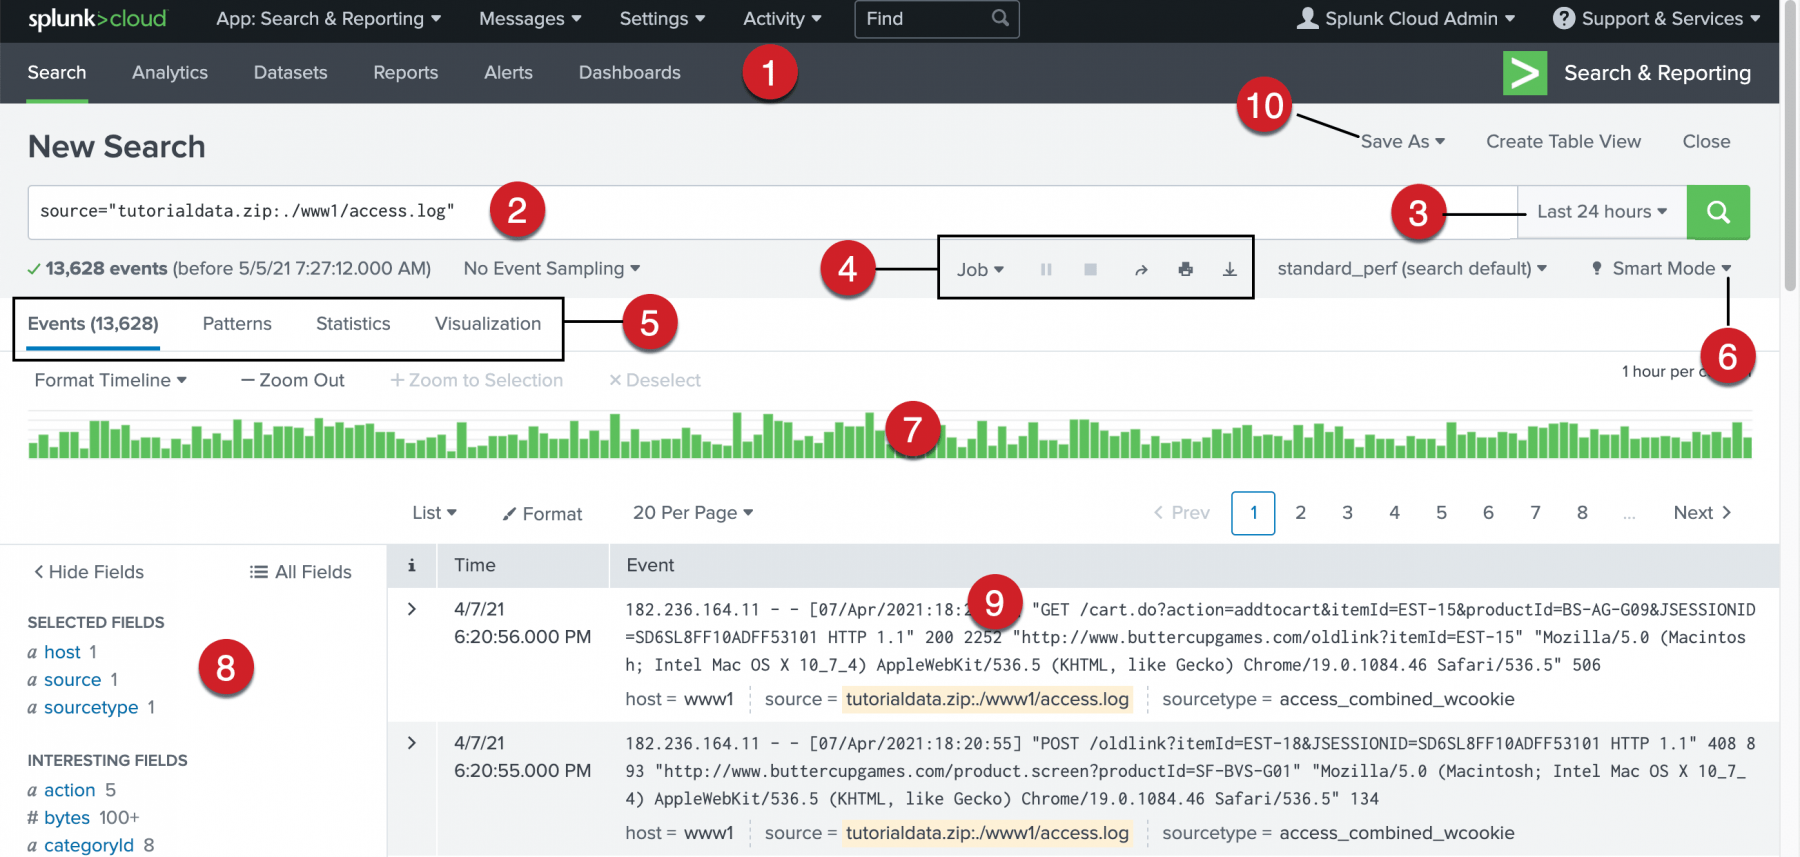
Exploring the Search views - Splunk Documentation

How to create a table row expansion? - Splunk Community

Solved: How to achieve this table representation in Splunk... - Splunk ...

Splunk uba documentation - glopspanish
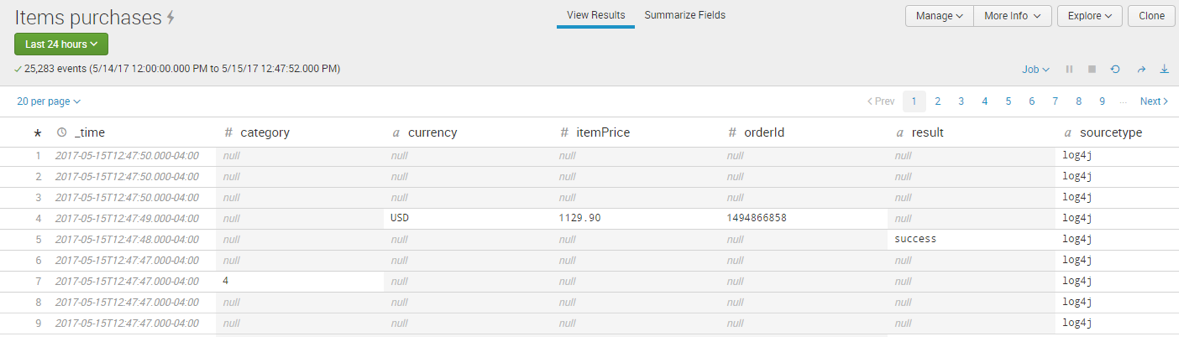
Diving into Splunk Table Datasets - Discovered Intelligence
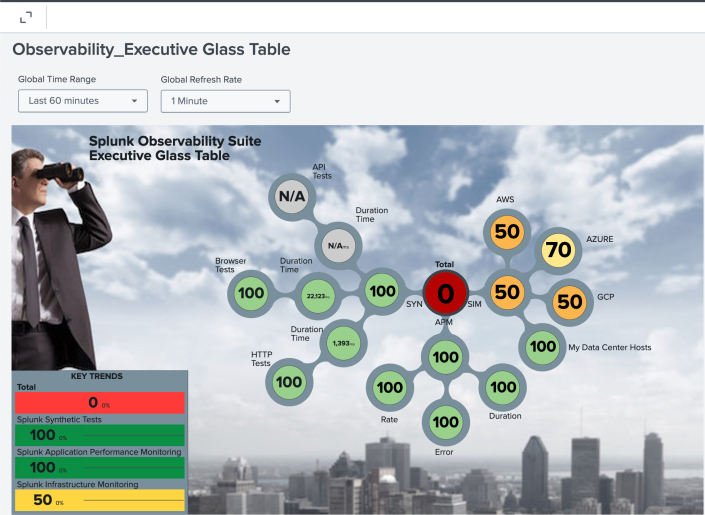
Use the Content Pack for Splunk Observability Cloud - Splunk Documentation

Splunk Check Size Of Lookup Table at Joanne Bender blog
Advertisement Space (336x280)
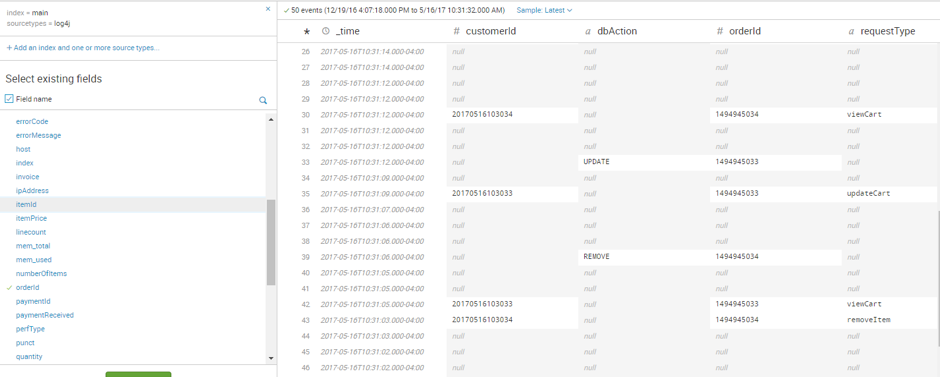
Diving into Splunk Table Datasets - Discovered Intelligence
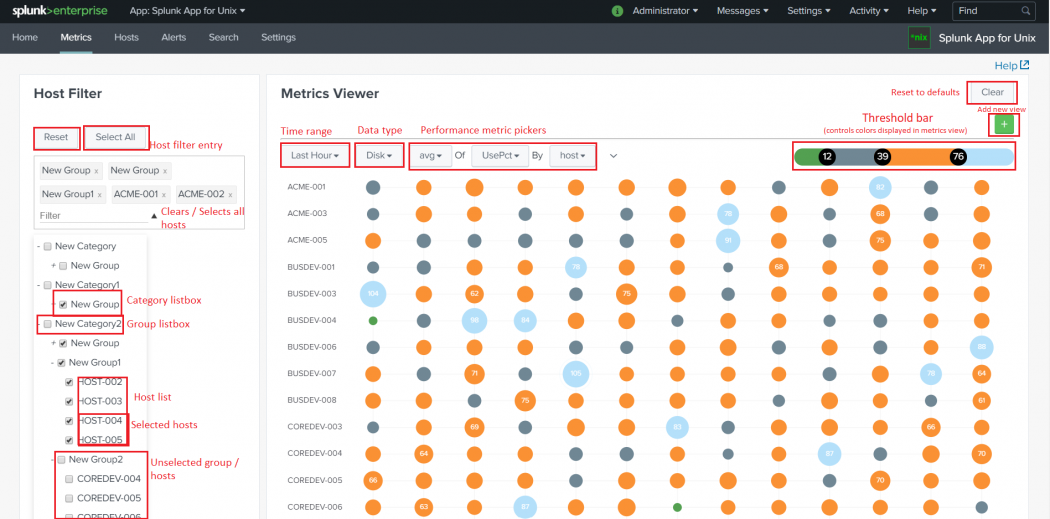
Use the Metrics dashboard - Splunk Documentation
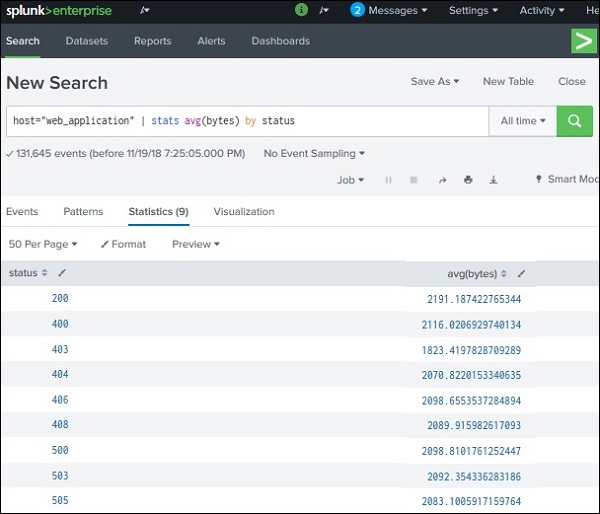
How to use a lookup table in a splunk query? – lookup table matching – PBFF

Diving into Splunk Table Datasets - Discovered Intelligence
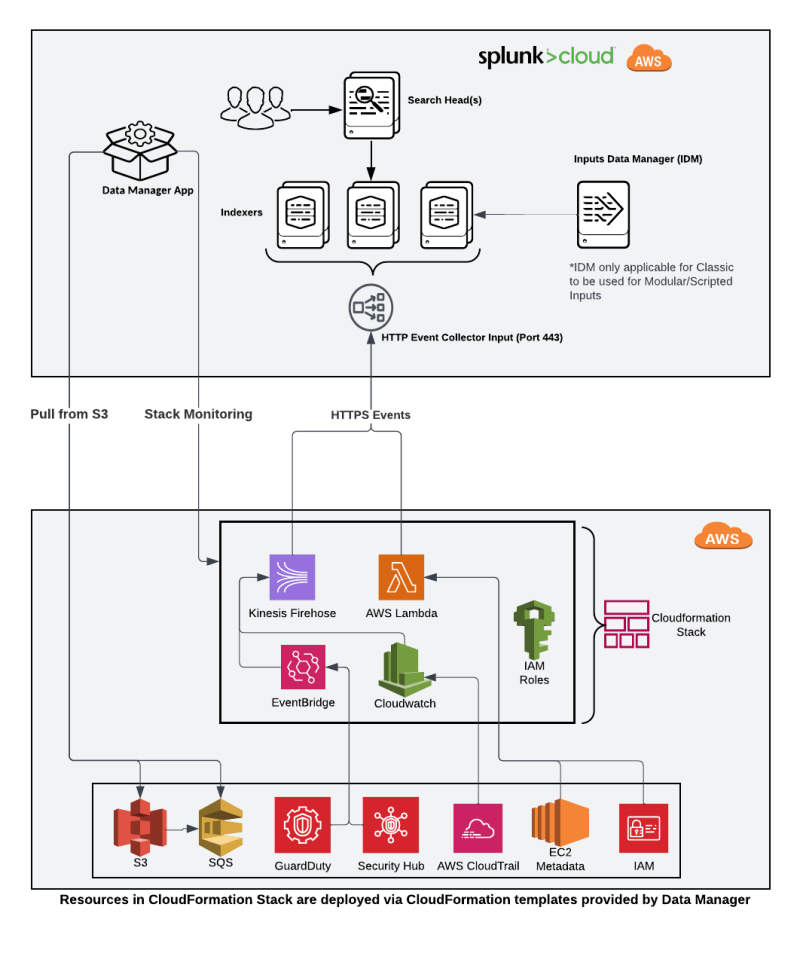
Getting AWS data into the Splunk platform - Splunk Documentation

How to chart a table by two parameters - Splunk Community