
What Is Search Time Field Extraction In Splunk Ramany Muthusamy

What is Search-time Field extraction in Splunk? | Ramany Muthusamy ...

Field extraction in SPLUNK using conf files in search time - YouTube
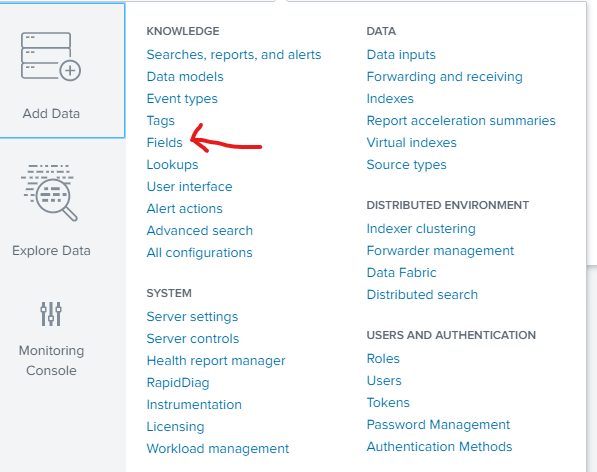
Search Time Field Extraction in SPlunk - Avotrix

Search Time Field Extraction in SPlunk - Avotrix

Search Time Field Extraction in SPlunk - Avotrix
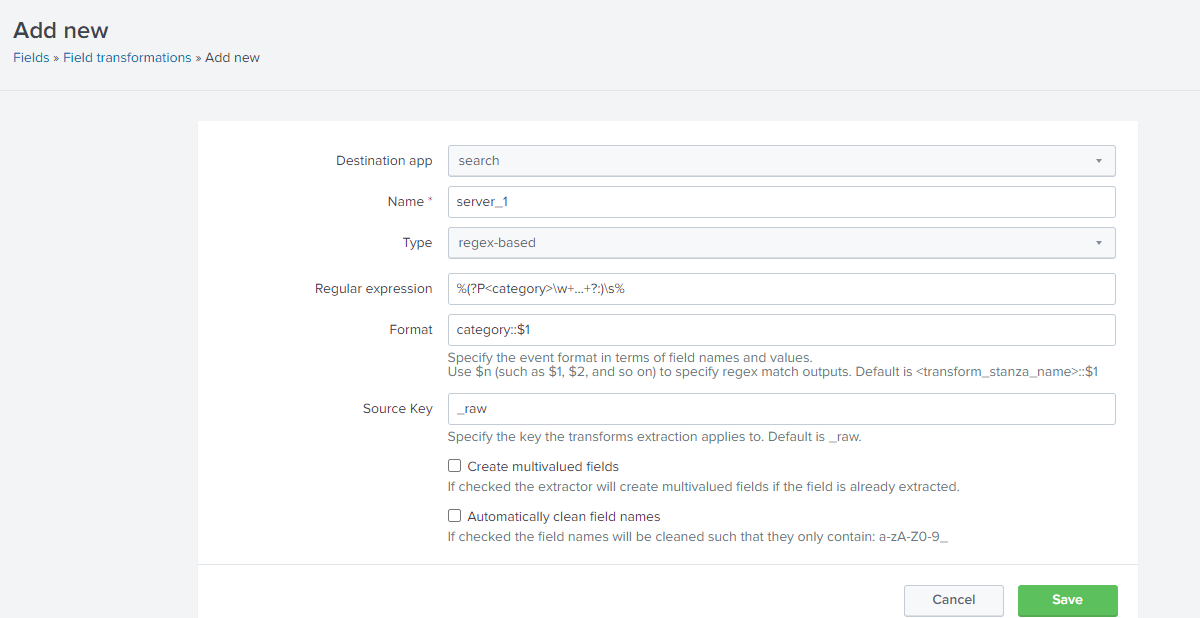
Search Time Field Extraction in SPlunk - Avotrix
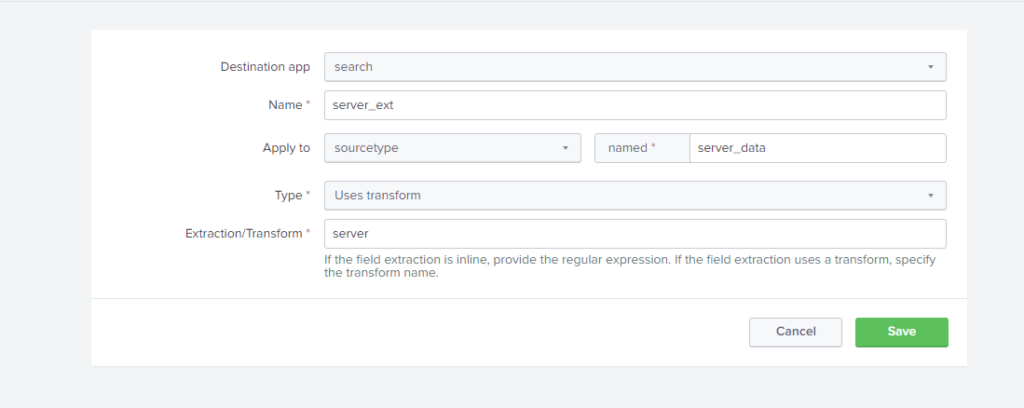
Search Time Field Extraction in SPlunk - Avotrix

Splunk Field Extraction - Search time & Index Time - YouTube

Splunk Configuration Files : Search time field extraction - YouTube

What Is Splunk Search Time at Darlene Watson blog
Advertisement Space (300x250)
Field Extraction at Index Time vs Search Time - ThinkCloudly

Field Extraction in splunk - Avotrix
Index Time vs Search Time Operations in Splunk - ThinkCloudly

Field Extraction in splunk - Avotrix

Splunk Field Extraction Limits: A Game Changer for Log Data | Ramany ...
Extra/Unnecessary Fields are getting extracted during search time | Splunk

Splunk timestamp extraction to epoch | How to extract year, date, time ...

Splunk Nested Field Extraction at Mary Spaulding blog
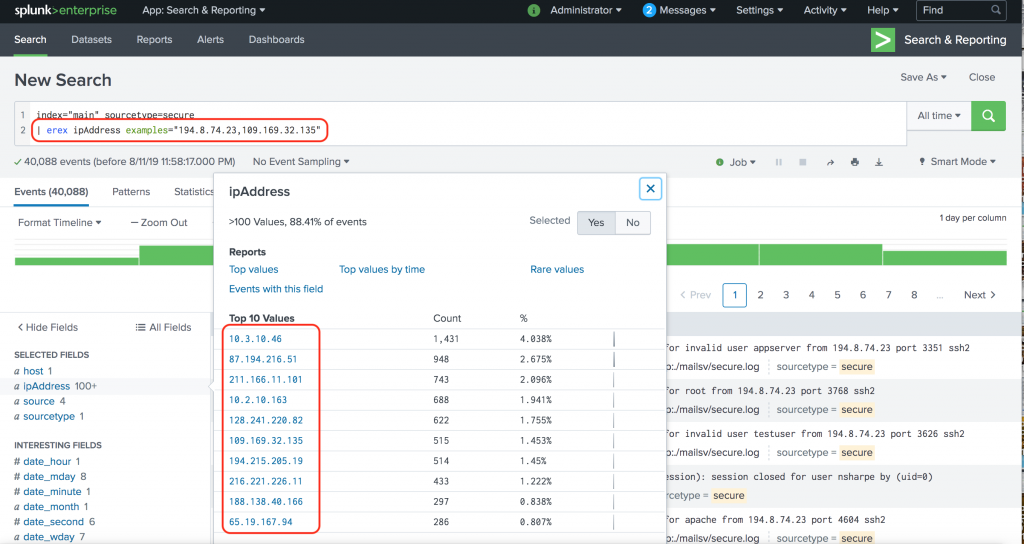
Splunk Nested Field Extraction at Mary Spaulding blog

Solved: How to do field extractions for response time and ... - Splunk ...
Advertisement Space (336x280)
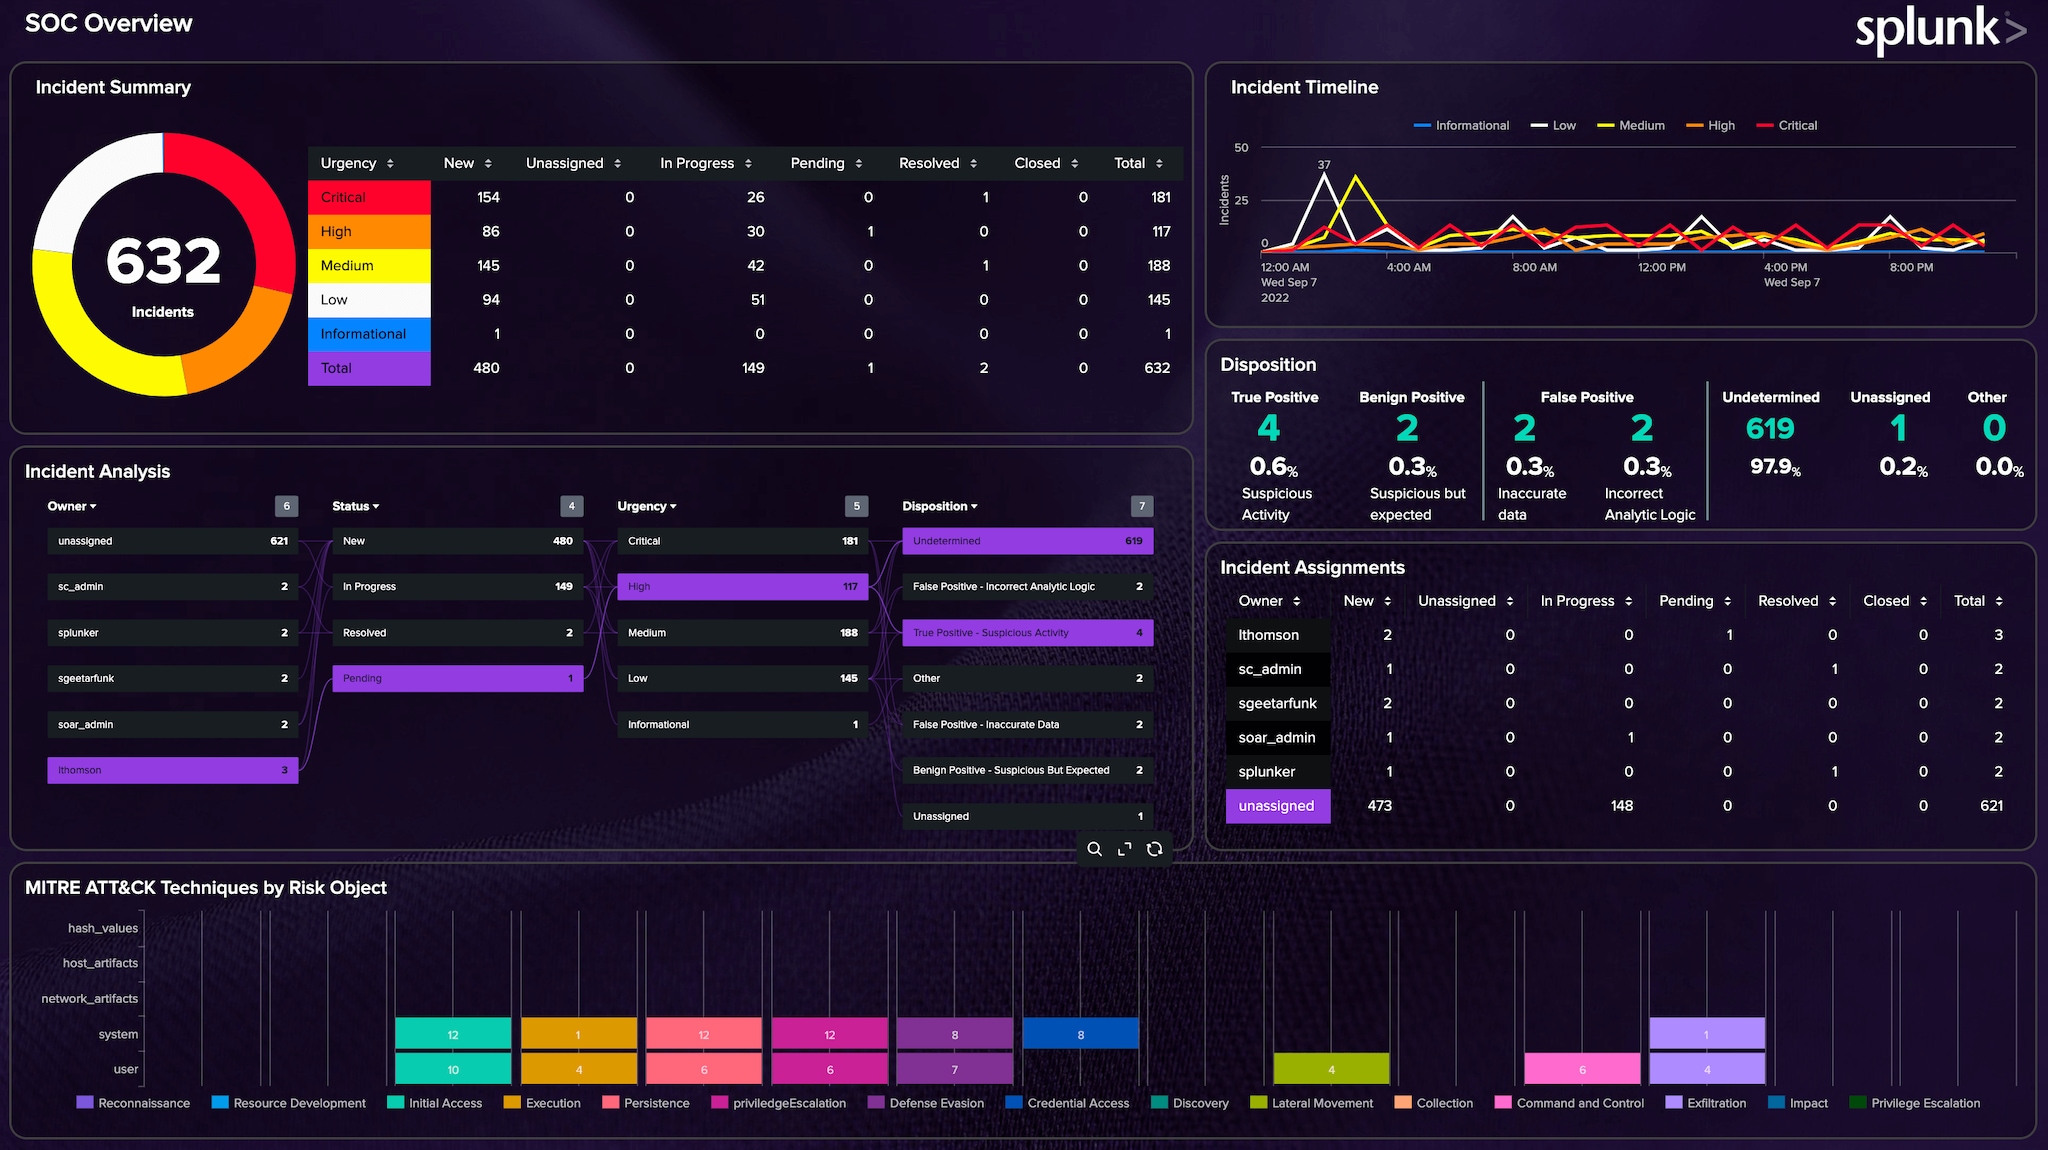
Get _time on your side - How to sort by more than one time field | Splunk

Get _time on your side - How to sort by more than one time field | Splunk
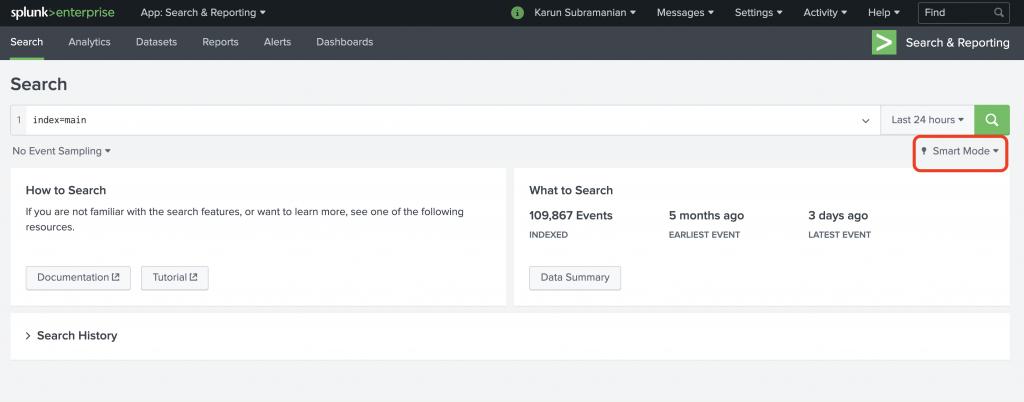
Splunk base search time picker - veryplanning
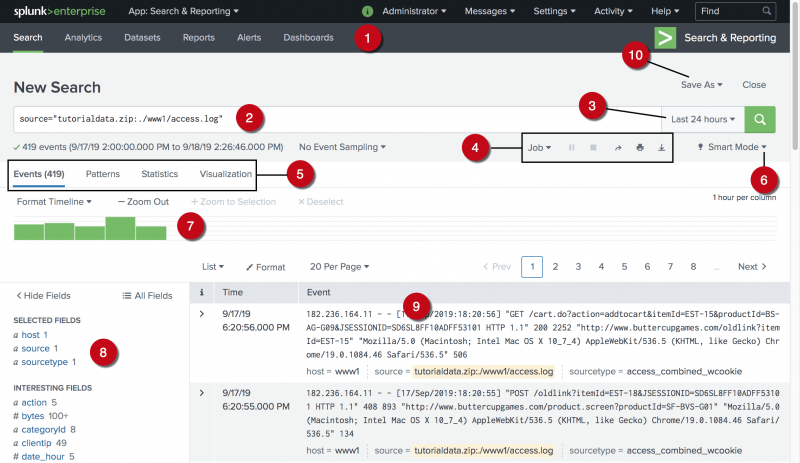
Splunk Search Field Like | Splunk Spl Cheat Sheet – NQFLWV

Splunk Nested Field Extraction at Mary Spaulding blog
Splunk Index Time Field , Timestamps and time ranges – DAOOKN

Play Time – Getting Data In | Splunk Operational Intelligence Cookbook
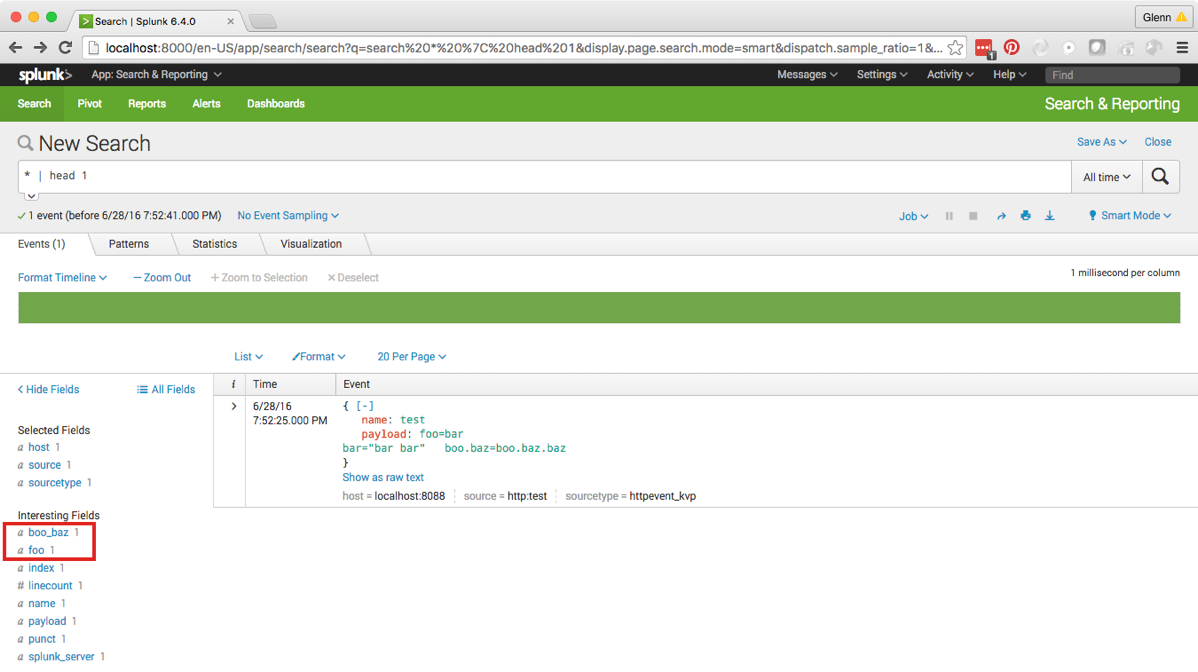
Splunk Nested Field Extraction at Mary Spaulding blog
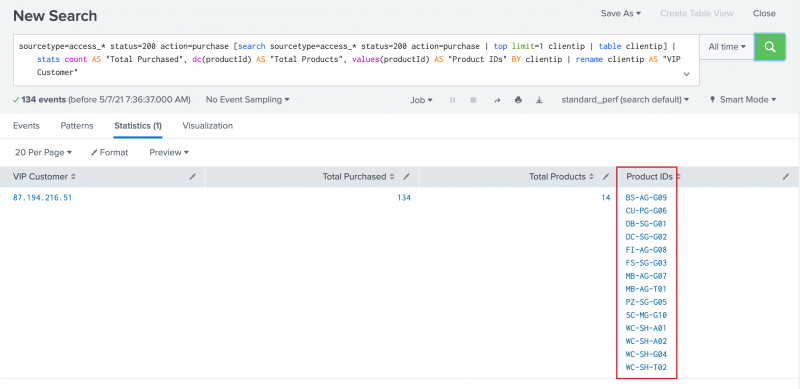
Search with field lookups - Splunk Documentation
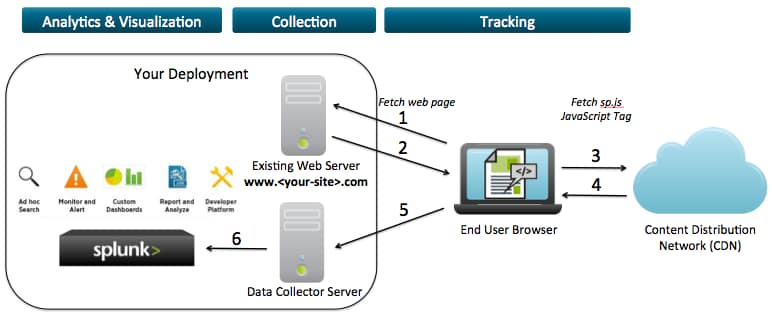
Get _time on your side - How to sort by more than one time field | Splunk
Advertisement Space (336x280)
Default Search Time Changed from 24 Hours to 30 Minutes | Splunk
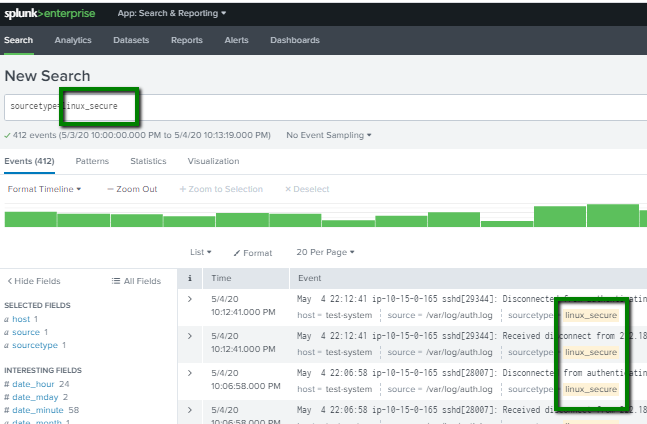
Search in Splunk - Splunk

index time extraction for json logs - Splunk Community

amazon web services - DateTime format search in the splunk search query ...
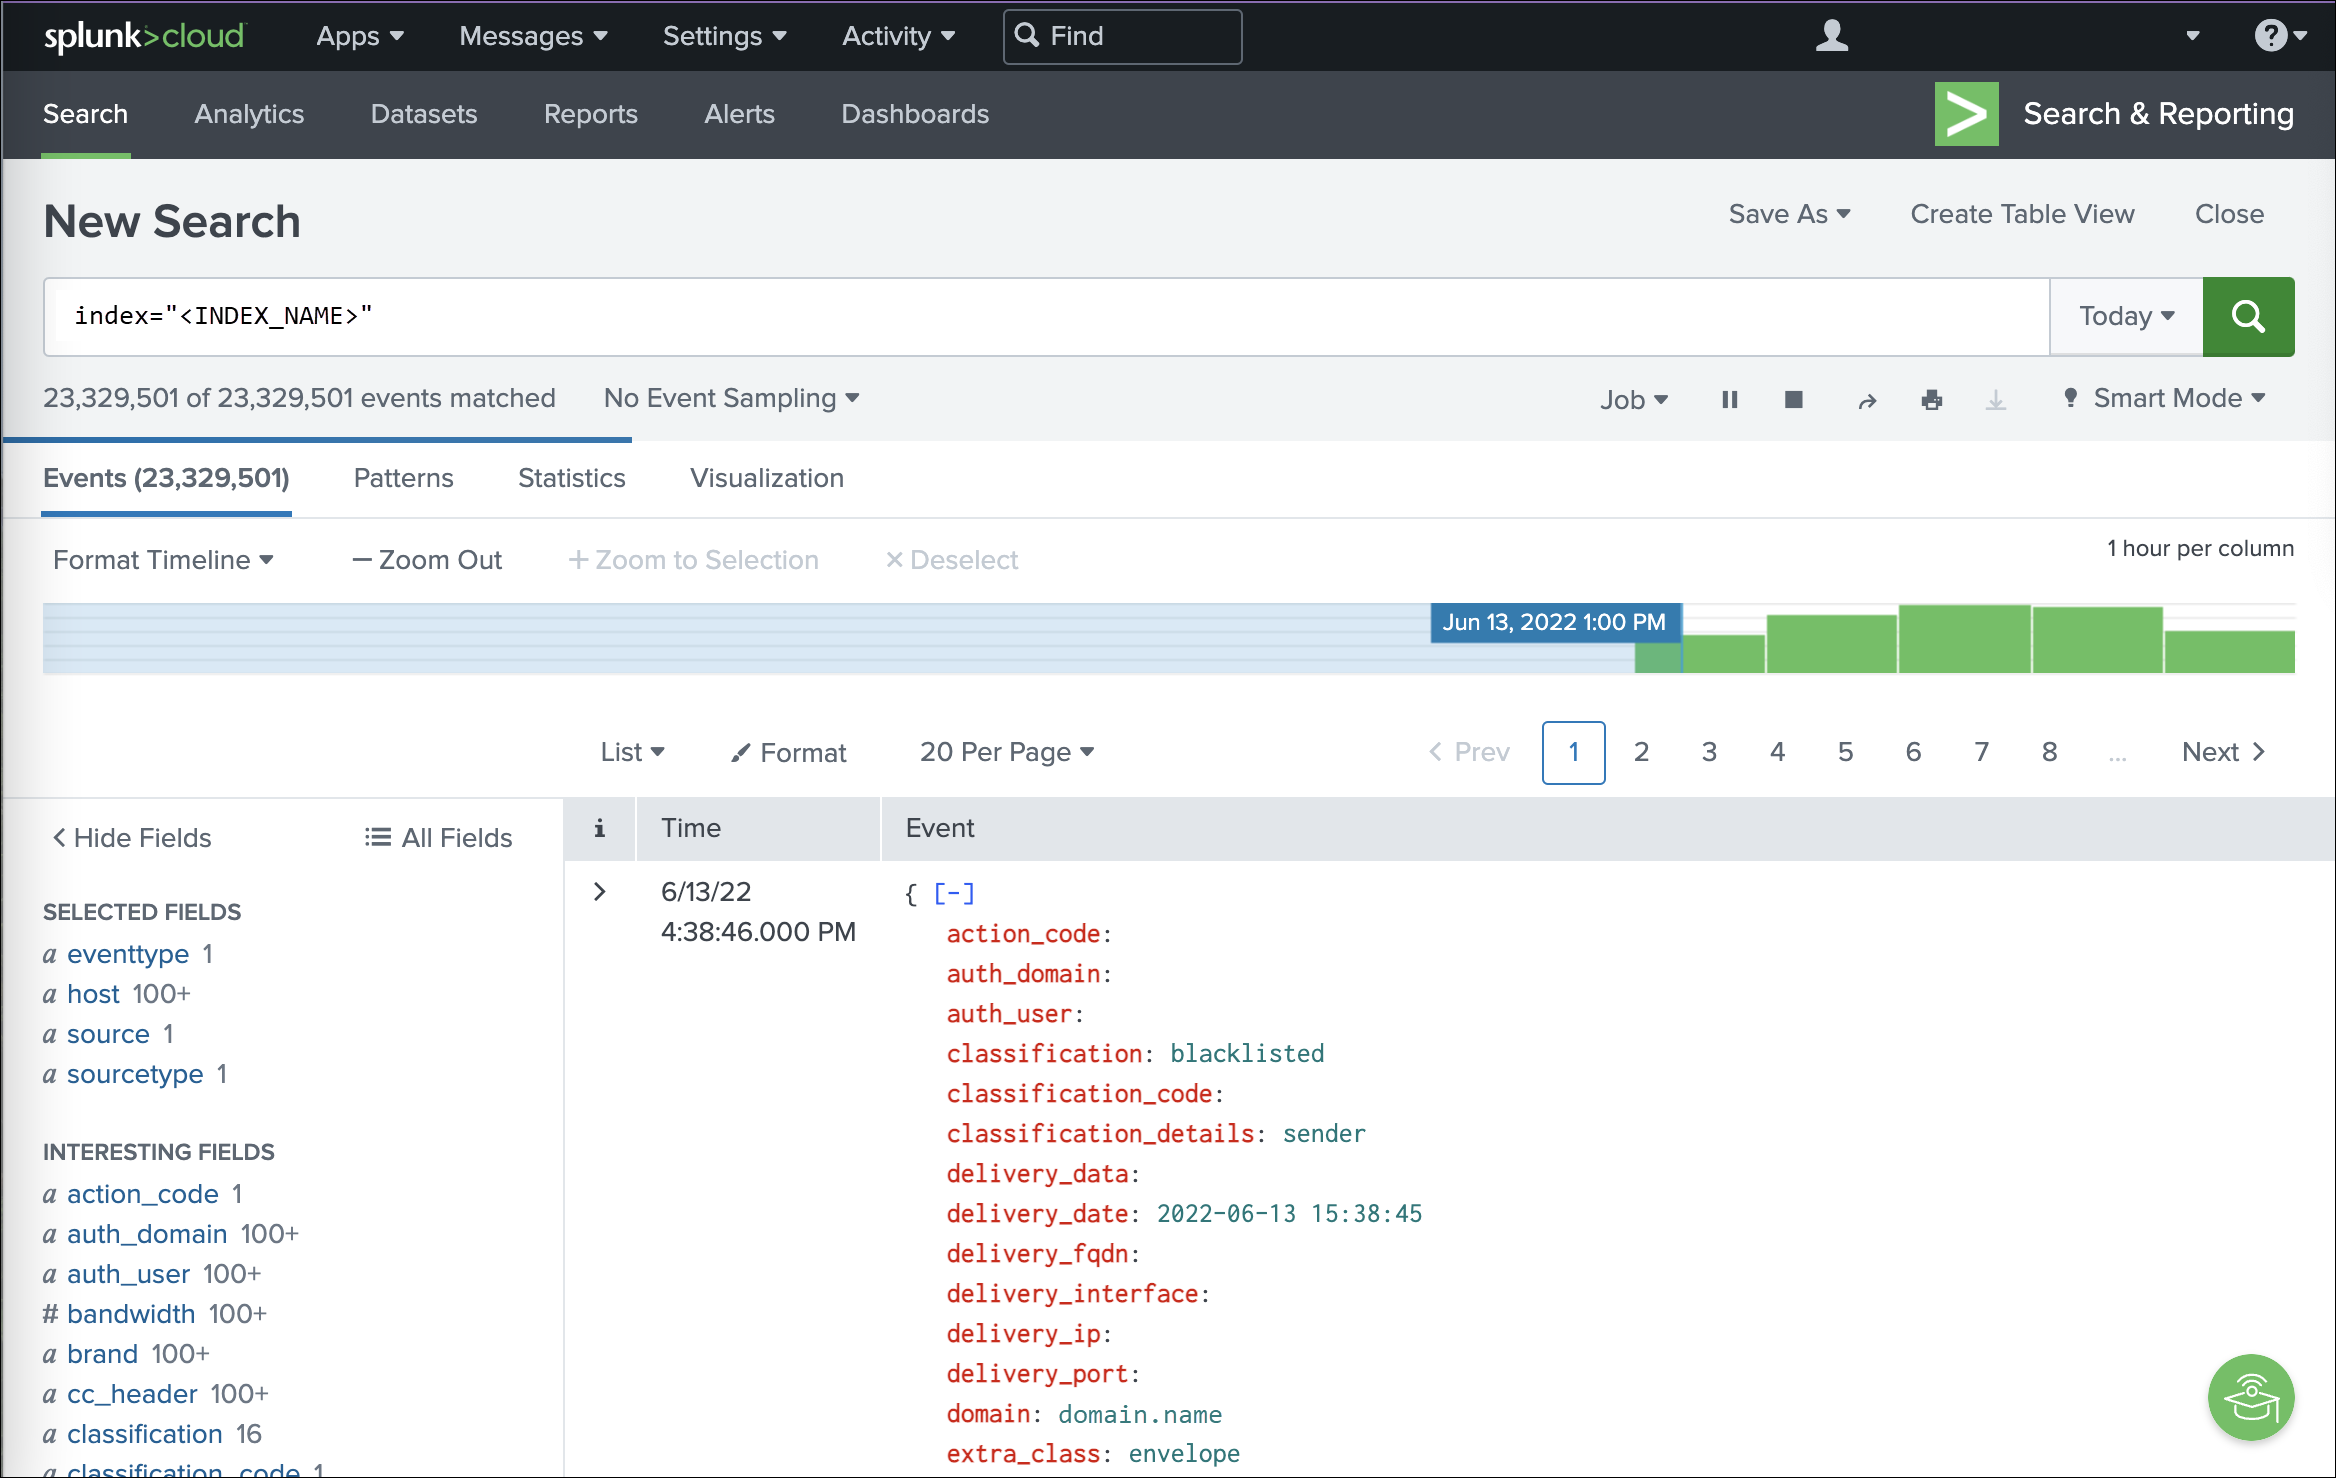
What Is Splunk Log Files at Lucas Cade blog
Get _time on your side - How to sort by more than one time field | Splunk