
Windows Process Parameter Poisoning Enables Low Visibility Shellcode

Windows Process Parameter Poisoning Enables Low-Visibility Shellcode ...

Windows Process Parameter Poisoning Enables Low-Visibility Shellcode ...

Process Parameter Poisoning Technique Hides Shellcode Inside Windows ...

Process Parameter Poisoning Technique Hides Shellcode Inside Windows ...

Process Parameter Poisoning Technique Hides Shellcode Inside Windows ...
Process Parameter Poisoning: New Windows EDR Evasion

New Windows Process Injection Technique Bypasses Four Leading EDR Solutions

New Windows Process Injection Technique Bypasses Four Leading EDR Solutions

Using Syscalls to Inject Shellcode on Windows #pentest #infosec # ...

Running Shellcode Through Windows Callbacks - Marco Ramilli
Advertisement Space (300x250)

Hunting Windows Process Injection by API Calls | PDF

Shellcode Injection in C# - Part 1 - Process Injection | Crypt0ace
Hiding Metasploit Shellcode to Evade Windows Defender | Rapid7 Blog
Analysing Shellcode to understand how they call windows API's - irfan ...
Hiding Metasploit Shellcode to Evade Windows Defender | Rapid7 Blog

Running Shellcode Through Windows Callbacks - Marco Ramilli
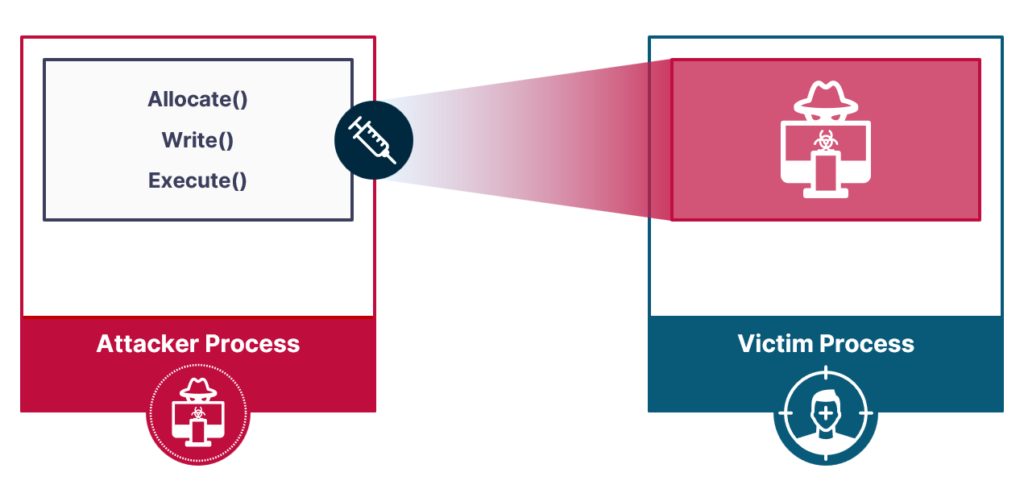
Process Injection Using Windows Thread Pools | Safebreach

Running Shellcode Through Windows Callbacks - Marco Ramilli

Can You Run My Code? A Close Look at Process Injection in Windows ...

Can You Run My Code? A Close Look at Process Injection in Windows ...
Advertisement Space (336x280)

Windows ShellCode Detection - Marco Ramilli

Windows Process Injection(Windows进程注入)技术研究 - 郑瀚 - 博客园

2. Windows x64 Shellcode Development intro | Malware Development

Windows Process Command Line Spoofing Through Symbolic Link - Cybernoz
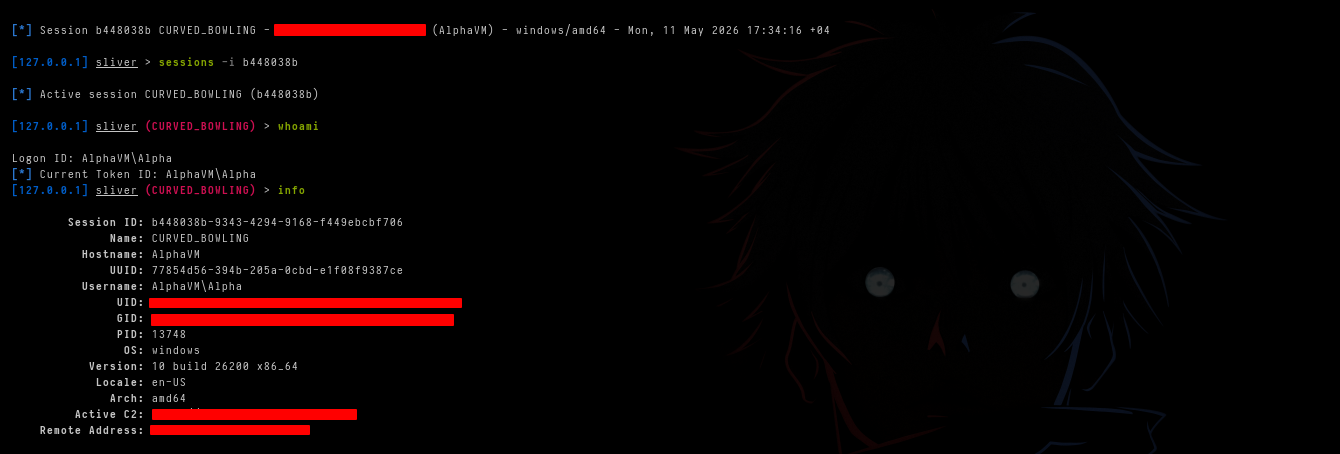
The Art of Windows Defender Bypass and Shellcode Obfuscation | dr-b3tman

2. Windows x64 Shellcode Development intro | Malware Development
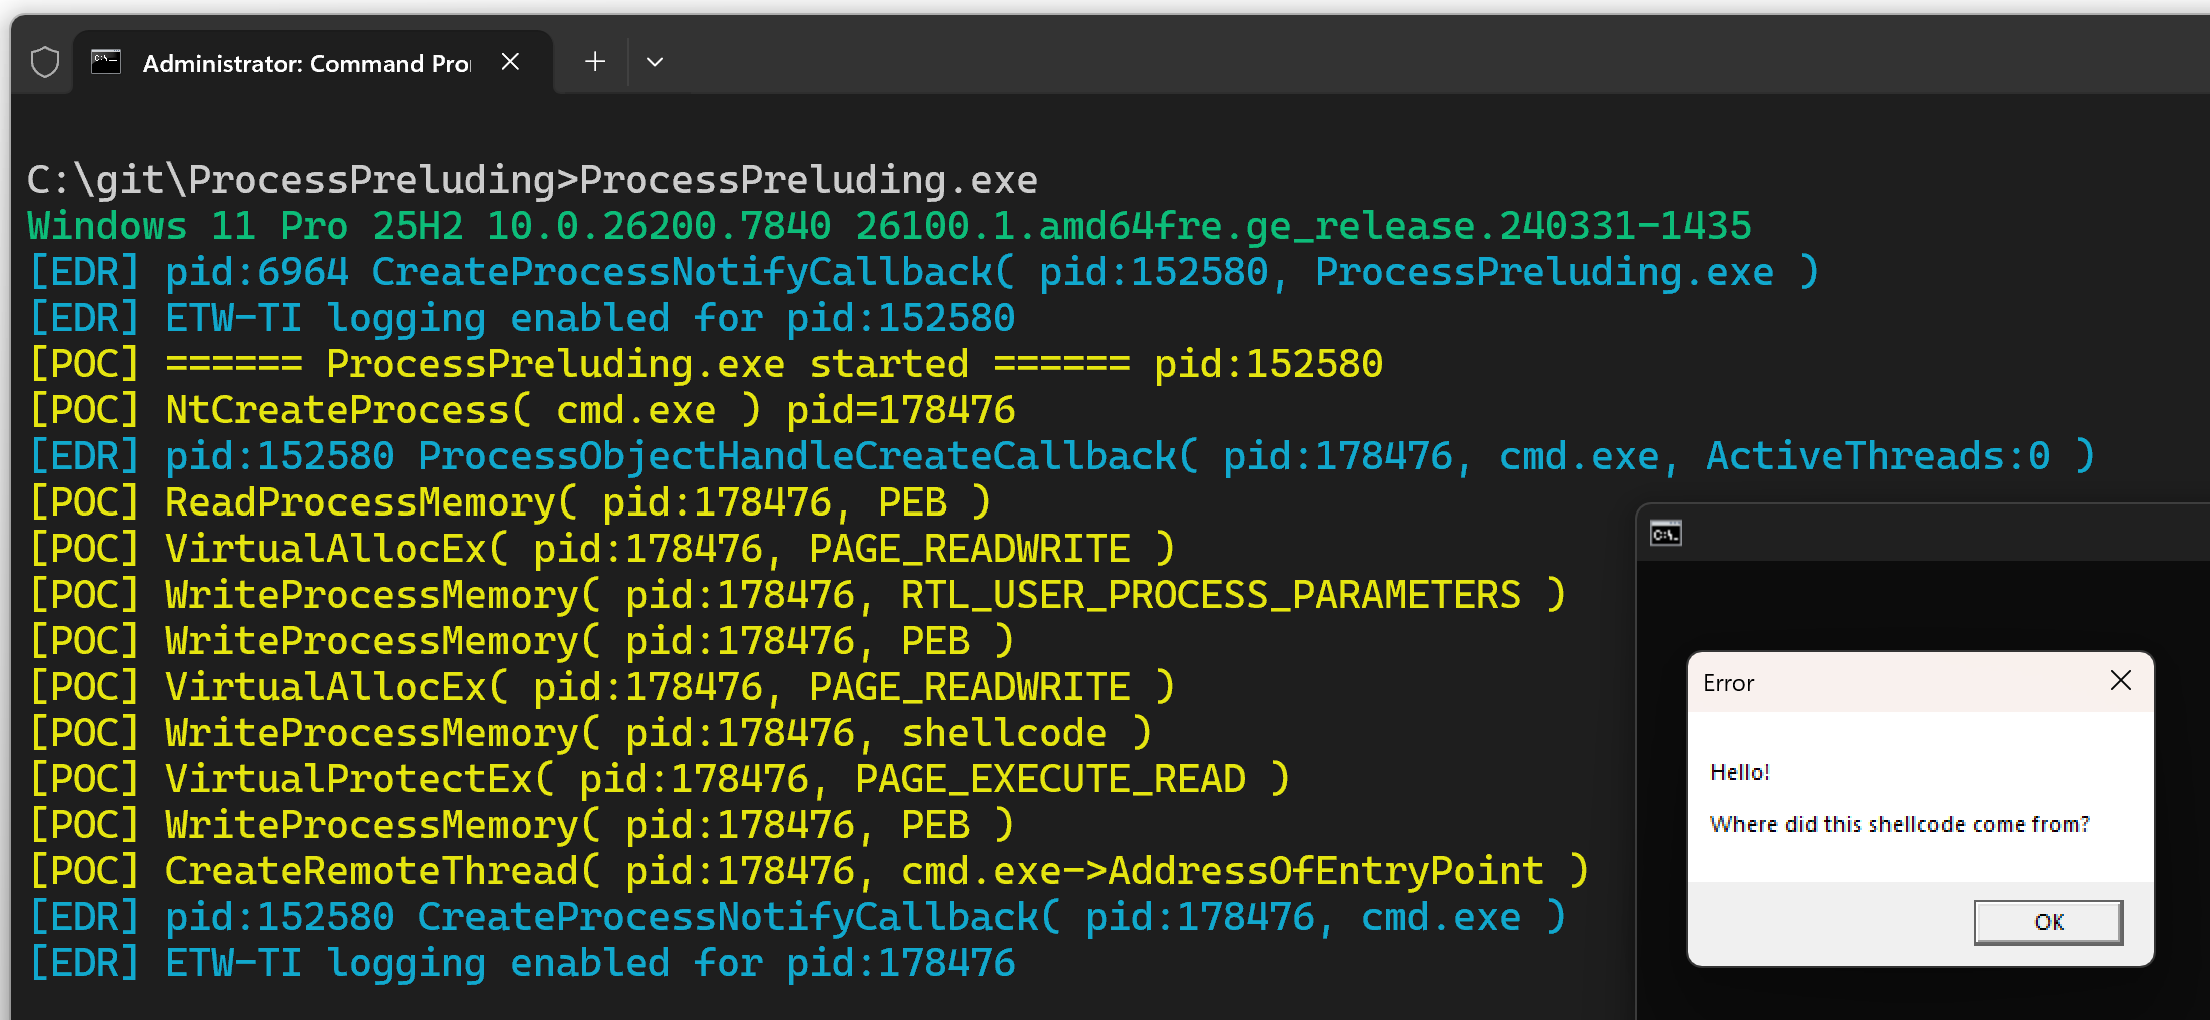
Process Preluding: Child Process Injection Before The Story Begins | Origin
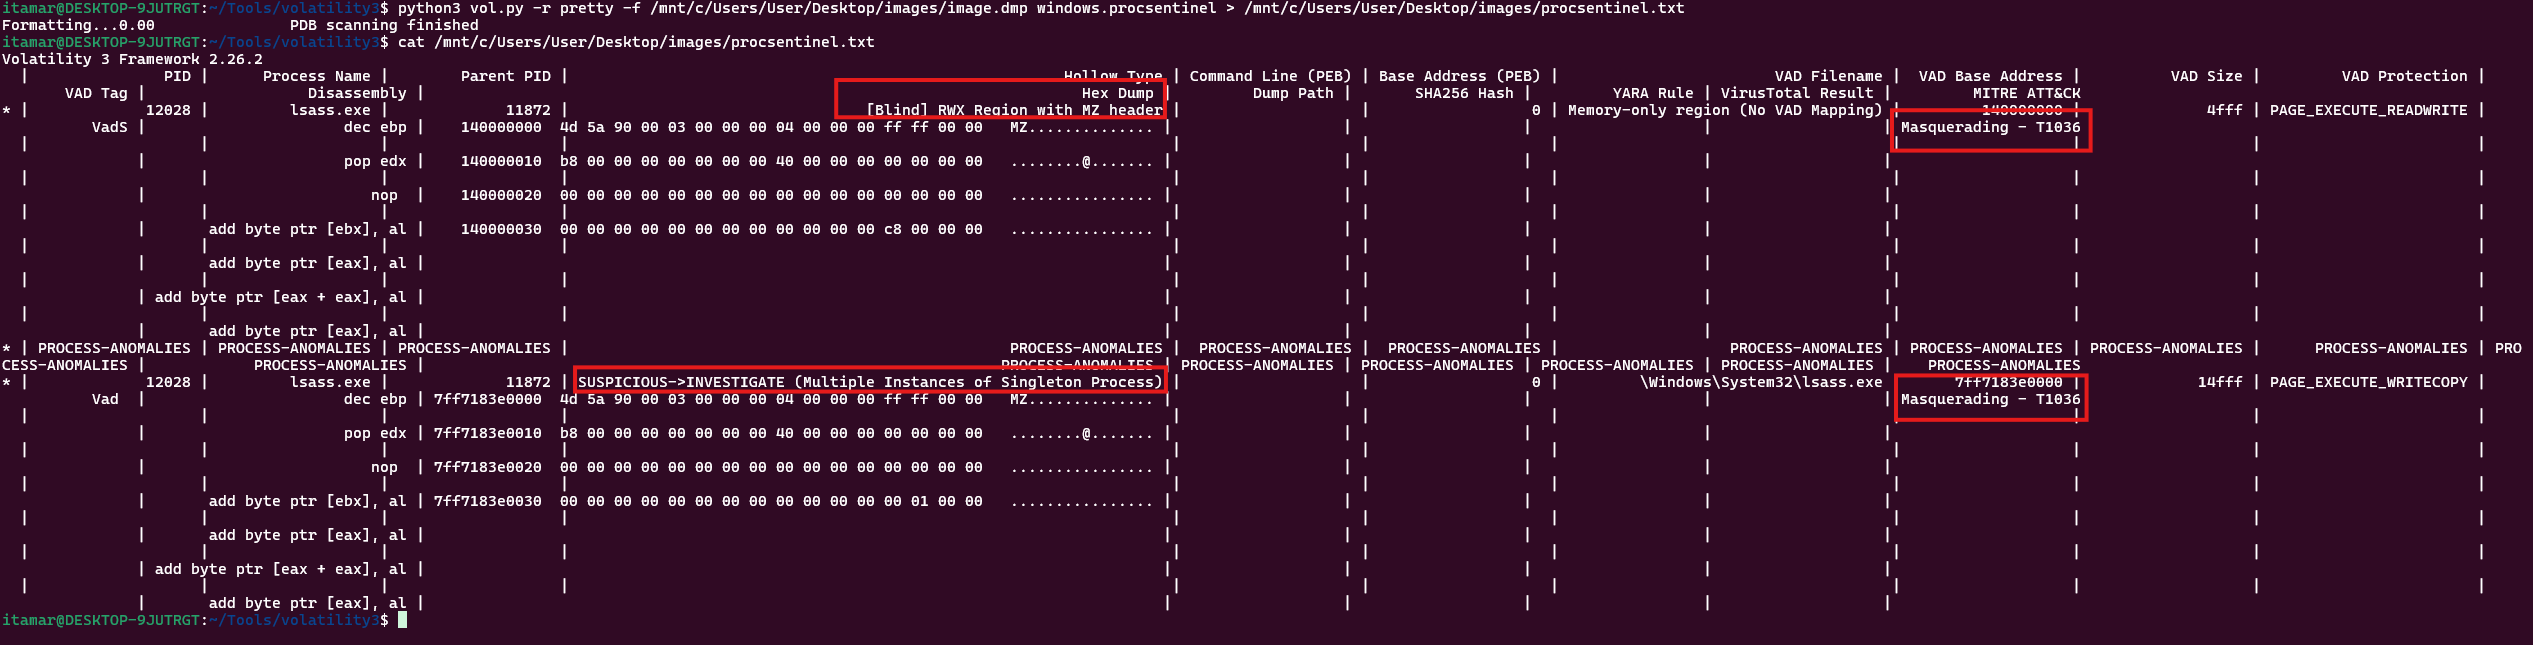
Dissecting Shellcode Execution in Memory | Tracepoint
Dissecting Shellcode Execution in Memory | Tracepoint
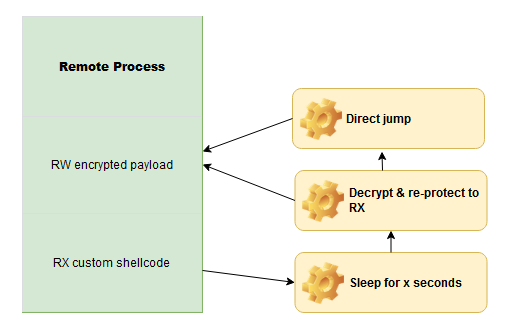
Blog Process Injection - r-tec Cyber Security
Advertisement Space (336x280)
Process Injection: The Journey to Penetrate Windows' Protected Process ...
Malware Development Primer 1- Shellcode Execution » THOVITI SIDDHARTH
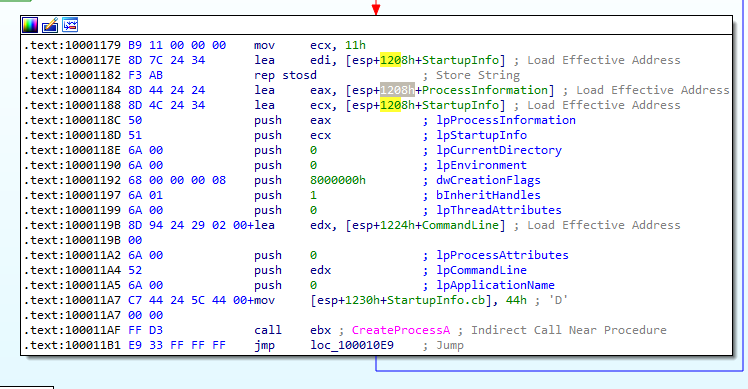
PMA - Analyzing Malicious Windows Programs

Inside a Multi-Stage Windows Malware Campaign
Analysing Windows Malware
Offensive C - Shellcode Obfuscation | Niraj Kharel