
Bpftime Userspace Ebpf Runtime For Fast Uprobe Syscall Hook

bpftime: Userspace eBPF runtime for fast Uprobe & Syscall hook ...
GitHub - CUIKingdom/bpftime-plc: Userspace eBPF runtime for fast Uprobe ...
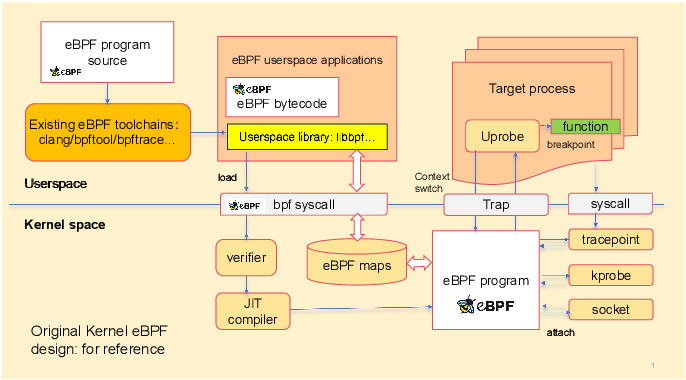
Figure 1 from bpftime: userspace eBPF Runtime for Uprobe, Syscall and ...

文献阅读: bpftime: userspace eBPF Runtime for Uprobe, Syscall and Kernel ...

文献阅读: bpftime: userspace eBPF Runtime for Uprobe, Syscall and Kernel ...

bpftime: un runtime de eBPF en el espacio de usuario para Uprobe y Syscall

bpftime: Userspace eBPF Runtime for Network and Observability - Yusheng ...

Free Video: bpftime - Fast Uprobes with User Space BPF Runtime from ...

eBPF and Wasm: Unifying Userspace Extensions With Bpftime - Yusheng…
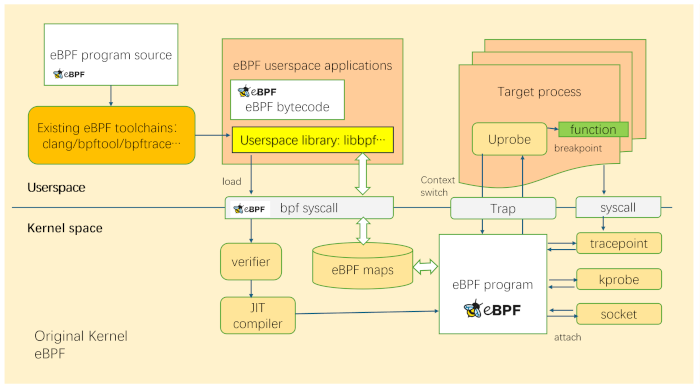
BPFTime Project Creates User-Space EBPF Implementation | Altus Intel
Advertisement Space (300x250)

Il tuo primo hook eBPF: monitoraggio syscall con bpftrace in 30 minuti
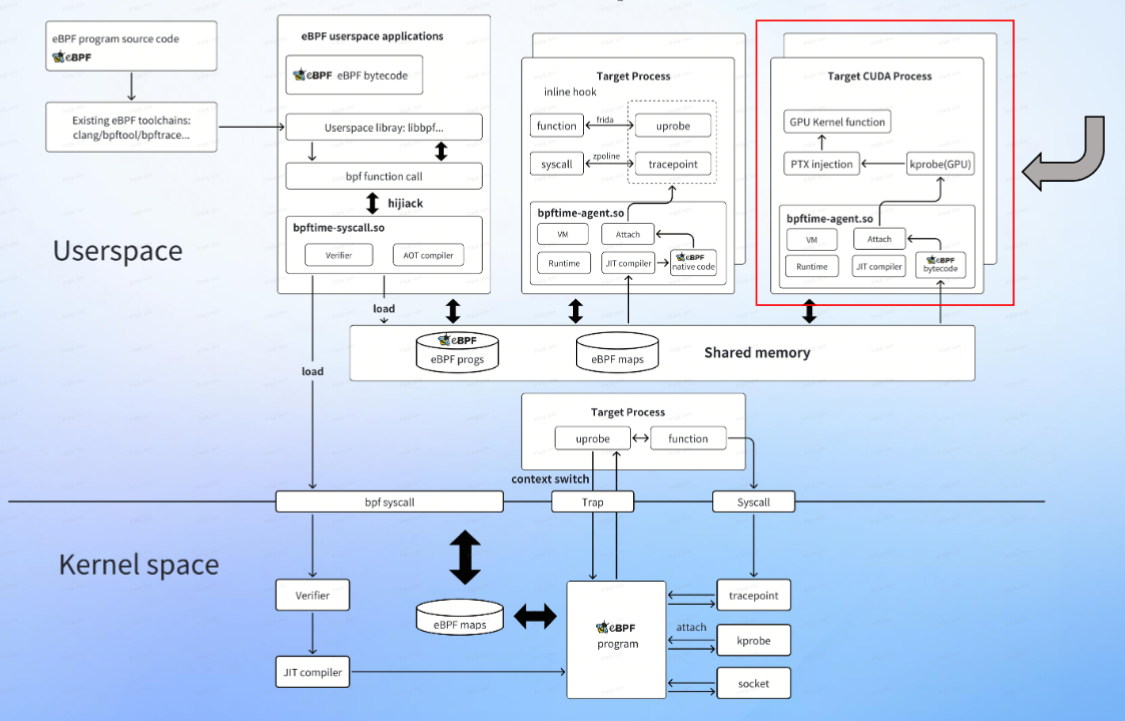
将 eBPF 扩展到 GPU 设备上下文 ── bpftime 的 GPU 可观测性与调度实践 - 知乎
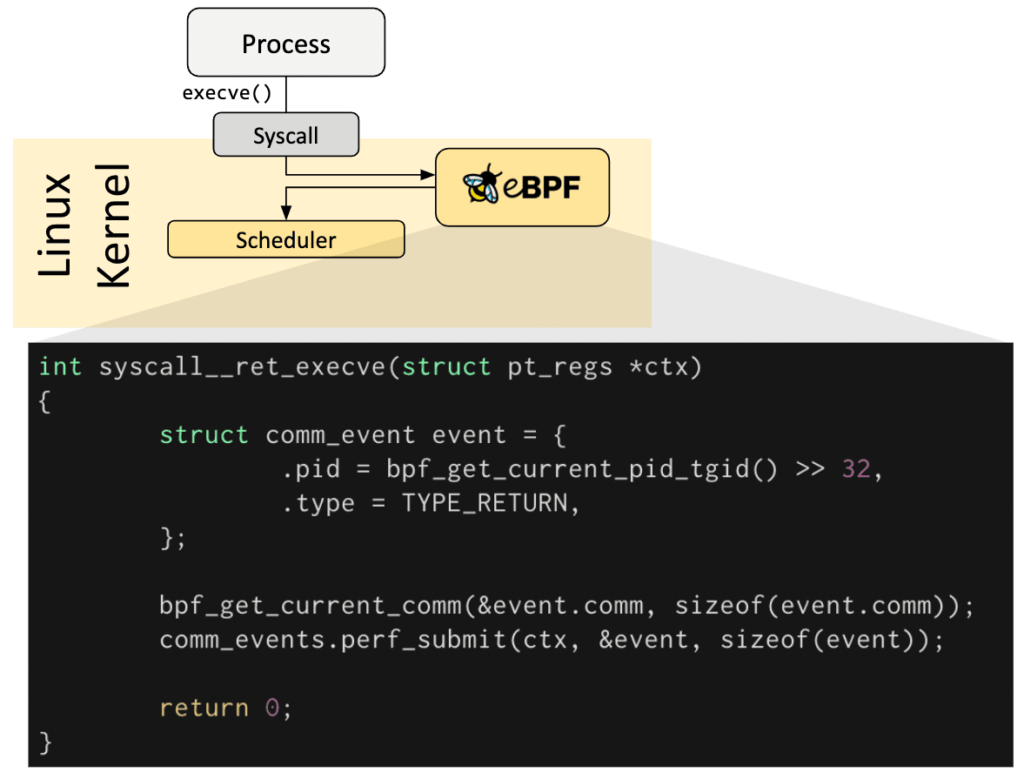
eBPF and its use for Istio service mesh
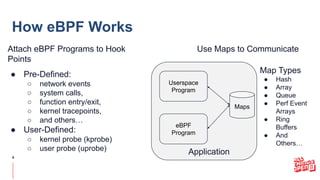
The Open Source Ecosystem for eBPF in Kubernetes | PDF
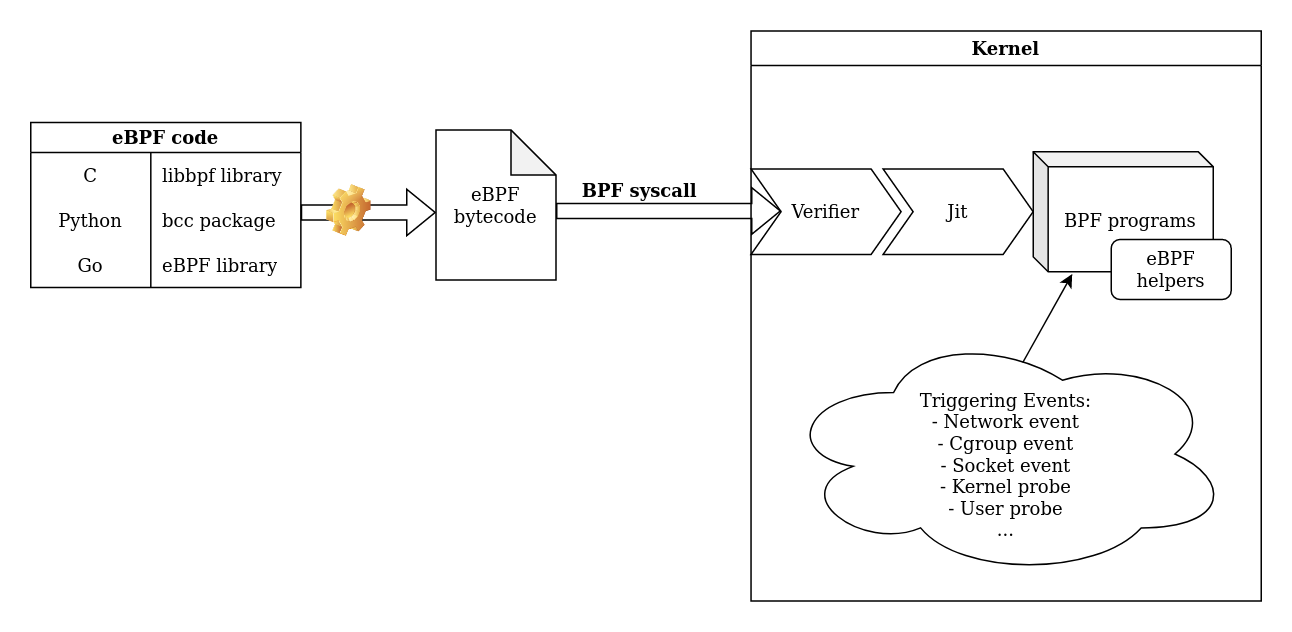
Defeating eBPF Uprobe Monitoring - Quarkslab's blog

eBPF Trace from Kernel to Userspace | PDF | Operating Systems ...
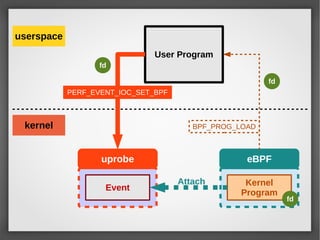
eBPF Trace from Kernel to Userspace | PDF

bpftime: Extending eBPF from Kernel to Userspace - DEV Community
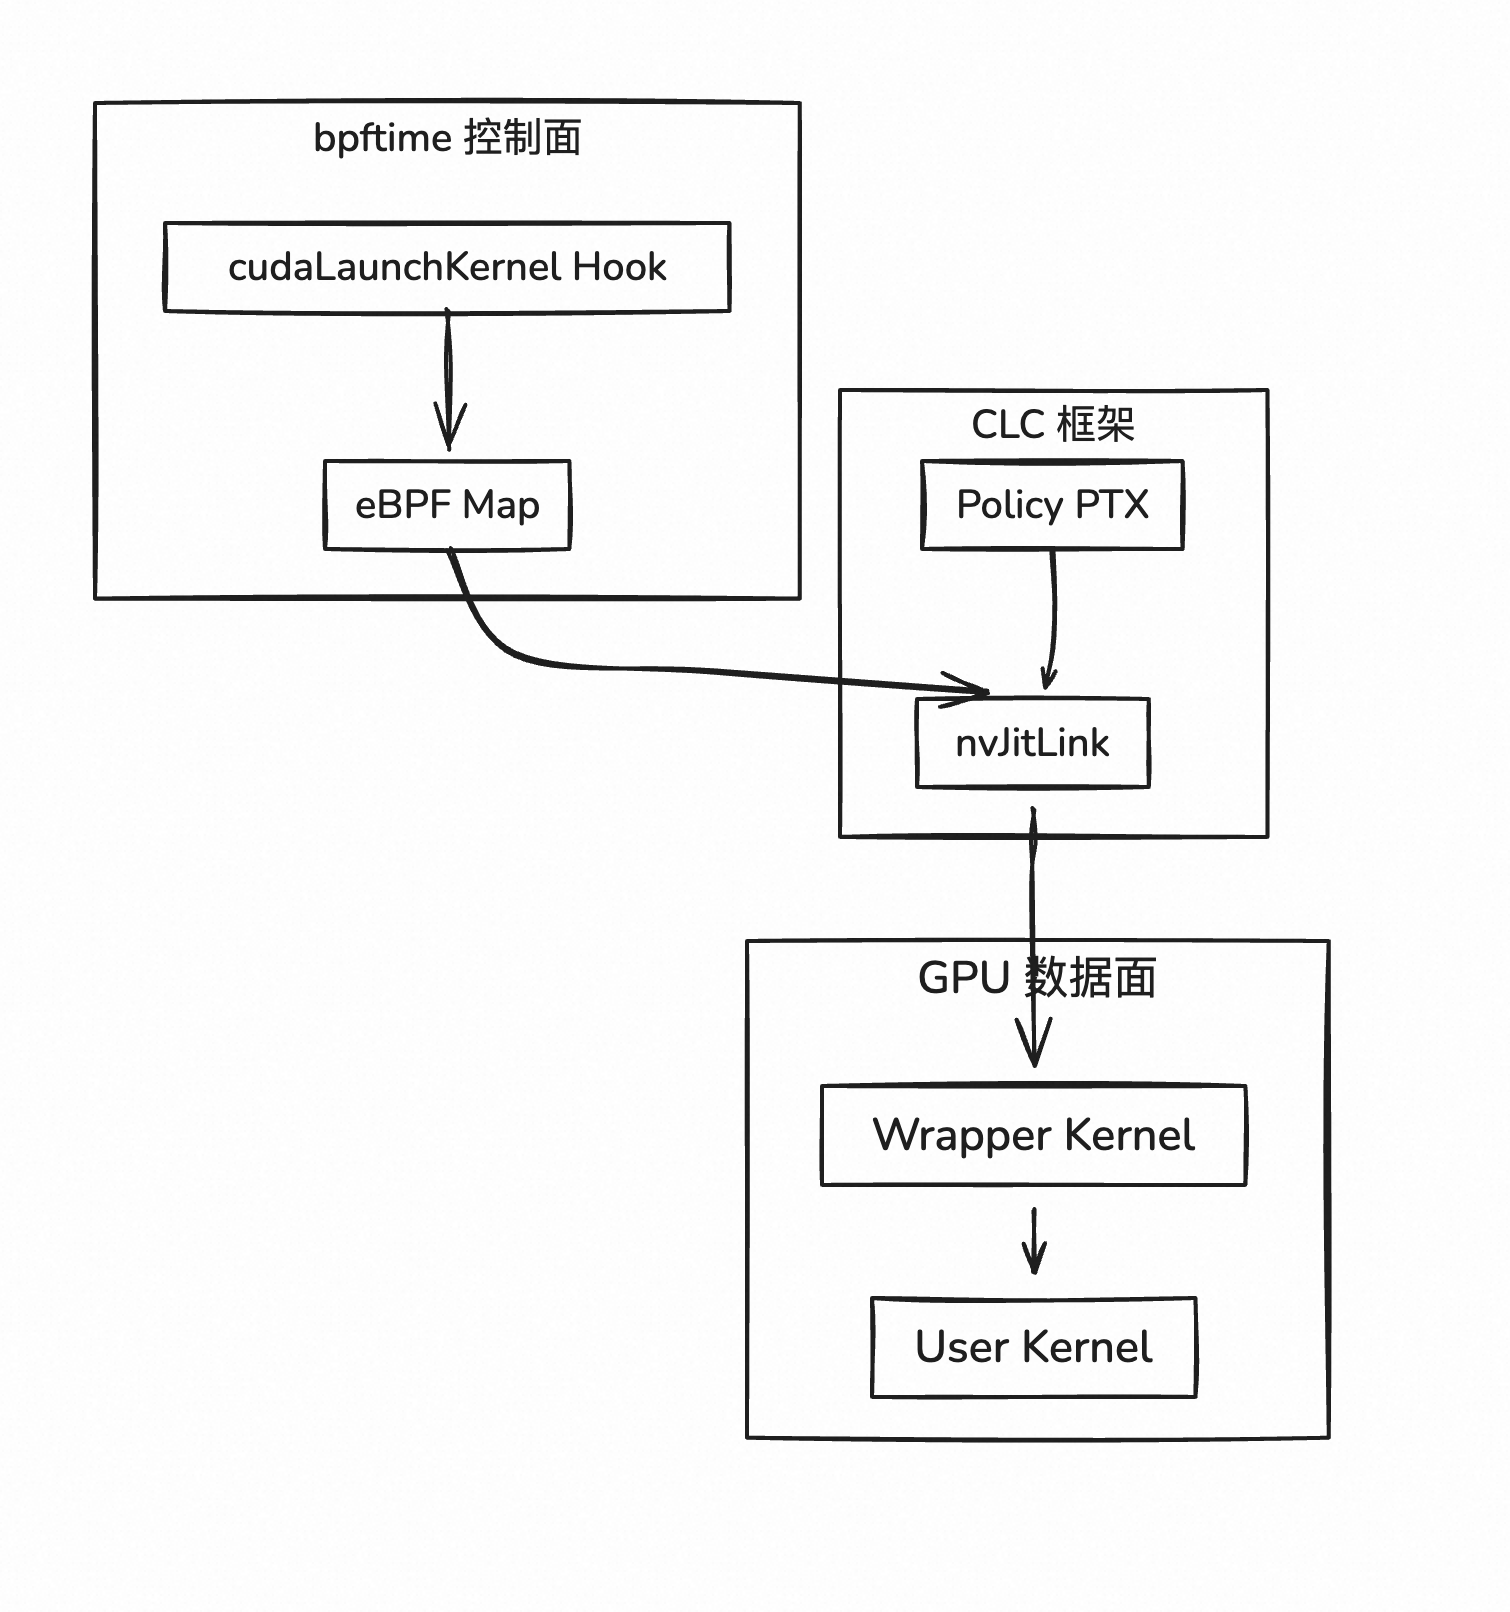
将 eBPF 扩展到 GPU 设备上下文 ── bpftime 的 GPU 可观测性与调度实践 - 知乎
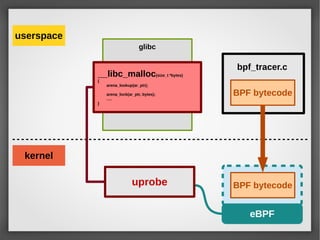
eBPF Trace from Kernel to Userspace | PDF
Advertisement Space (336x280)
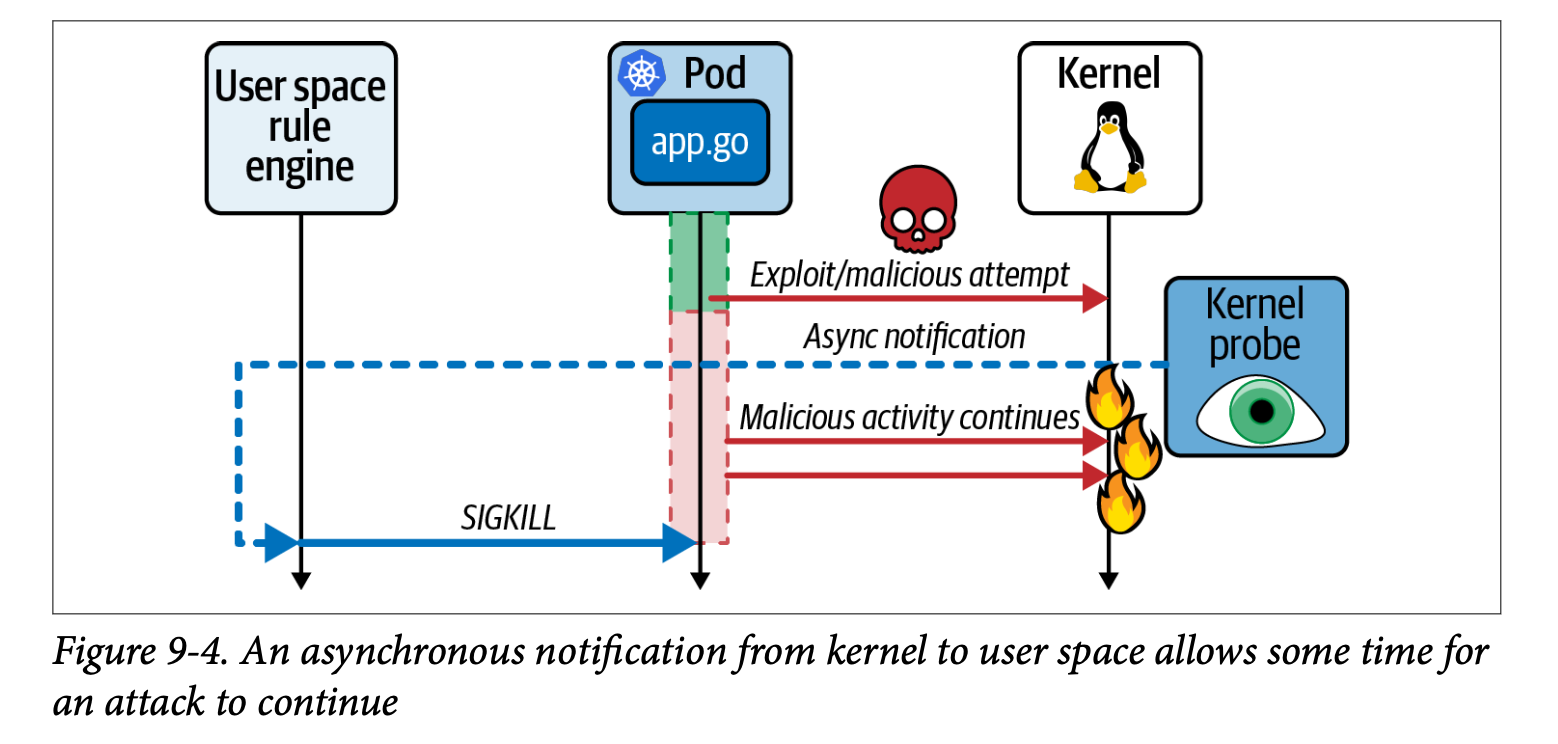
9. eBPF for Security
Syscall command 'BPF_LINK_UPDATE' - eBPF Docs
Libbpf userspace function 'bpf_program__attach_uprobe_opts' - eBPF Docs
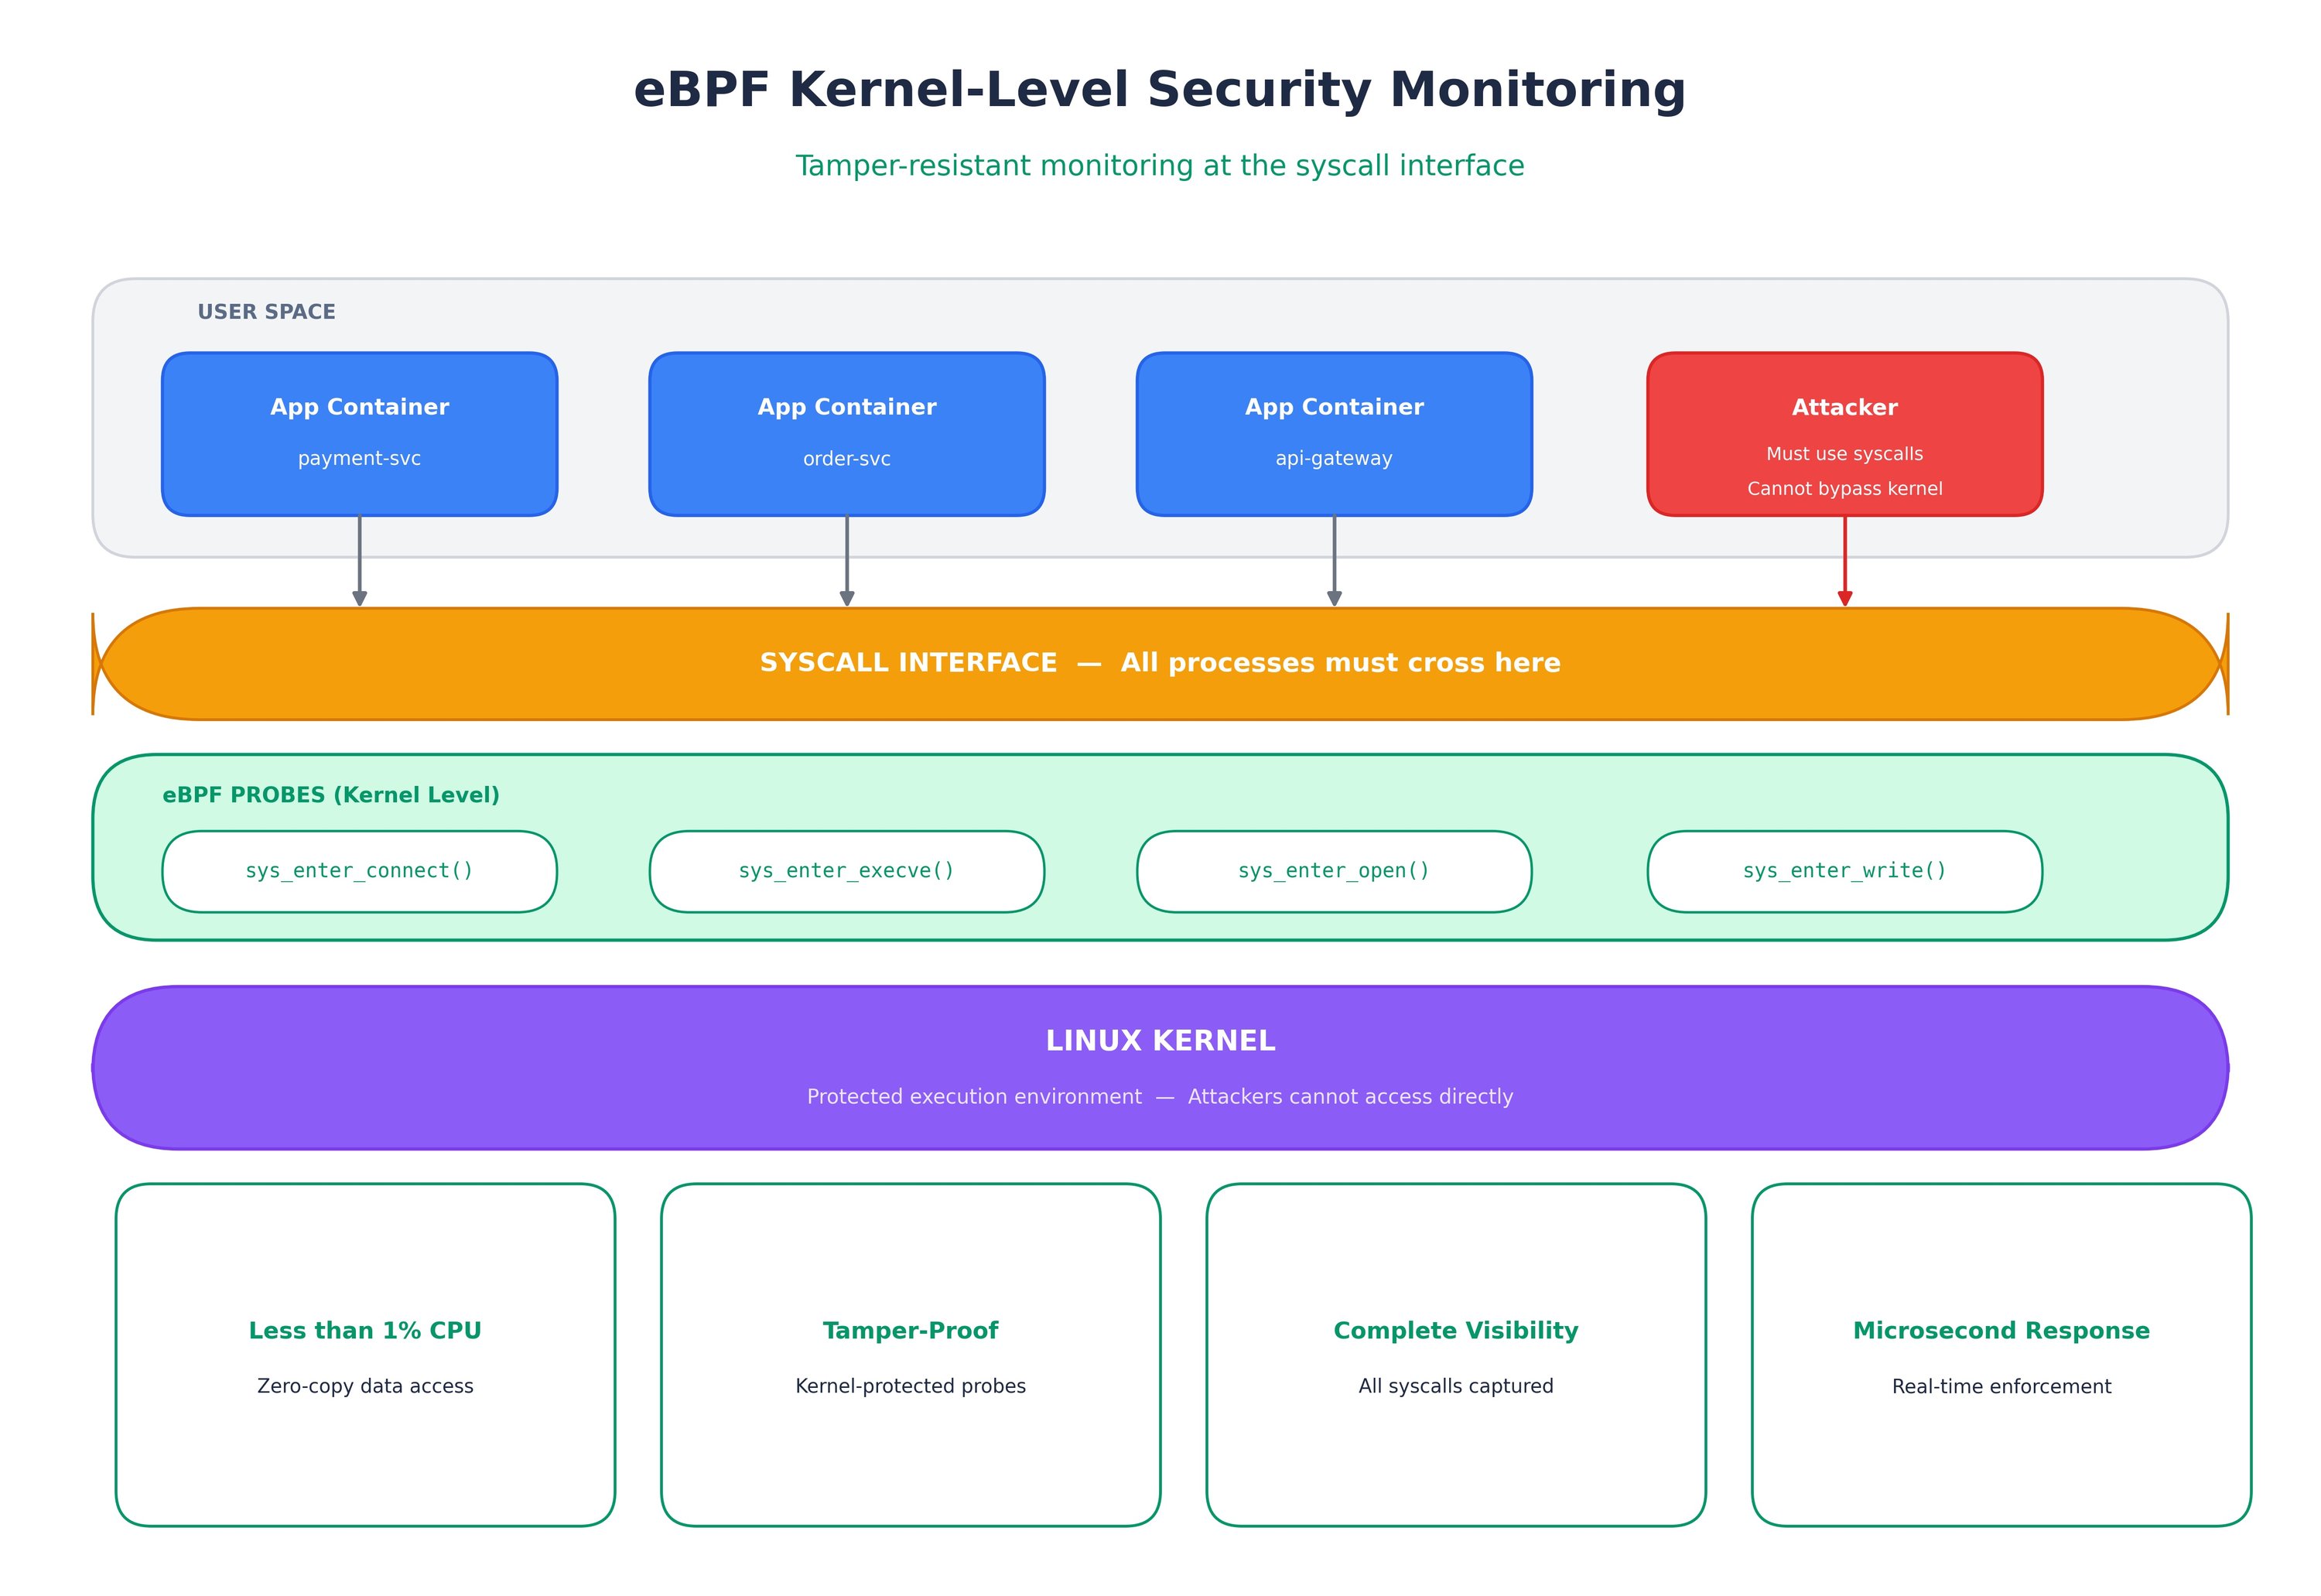
Kernel-Level Ground Truth: Why eBPF is Replacing User-Space Agents for ...
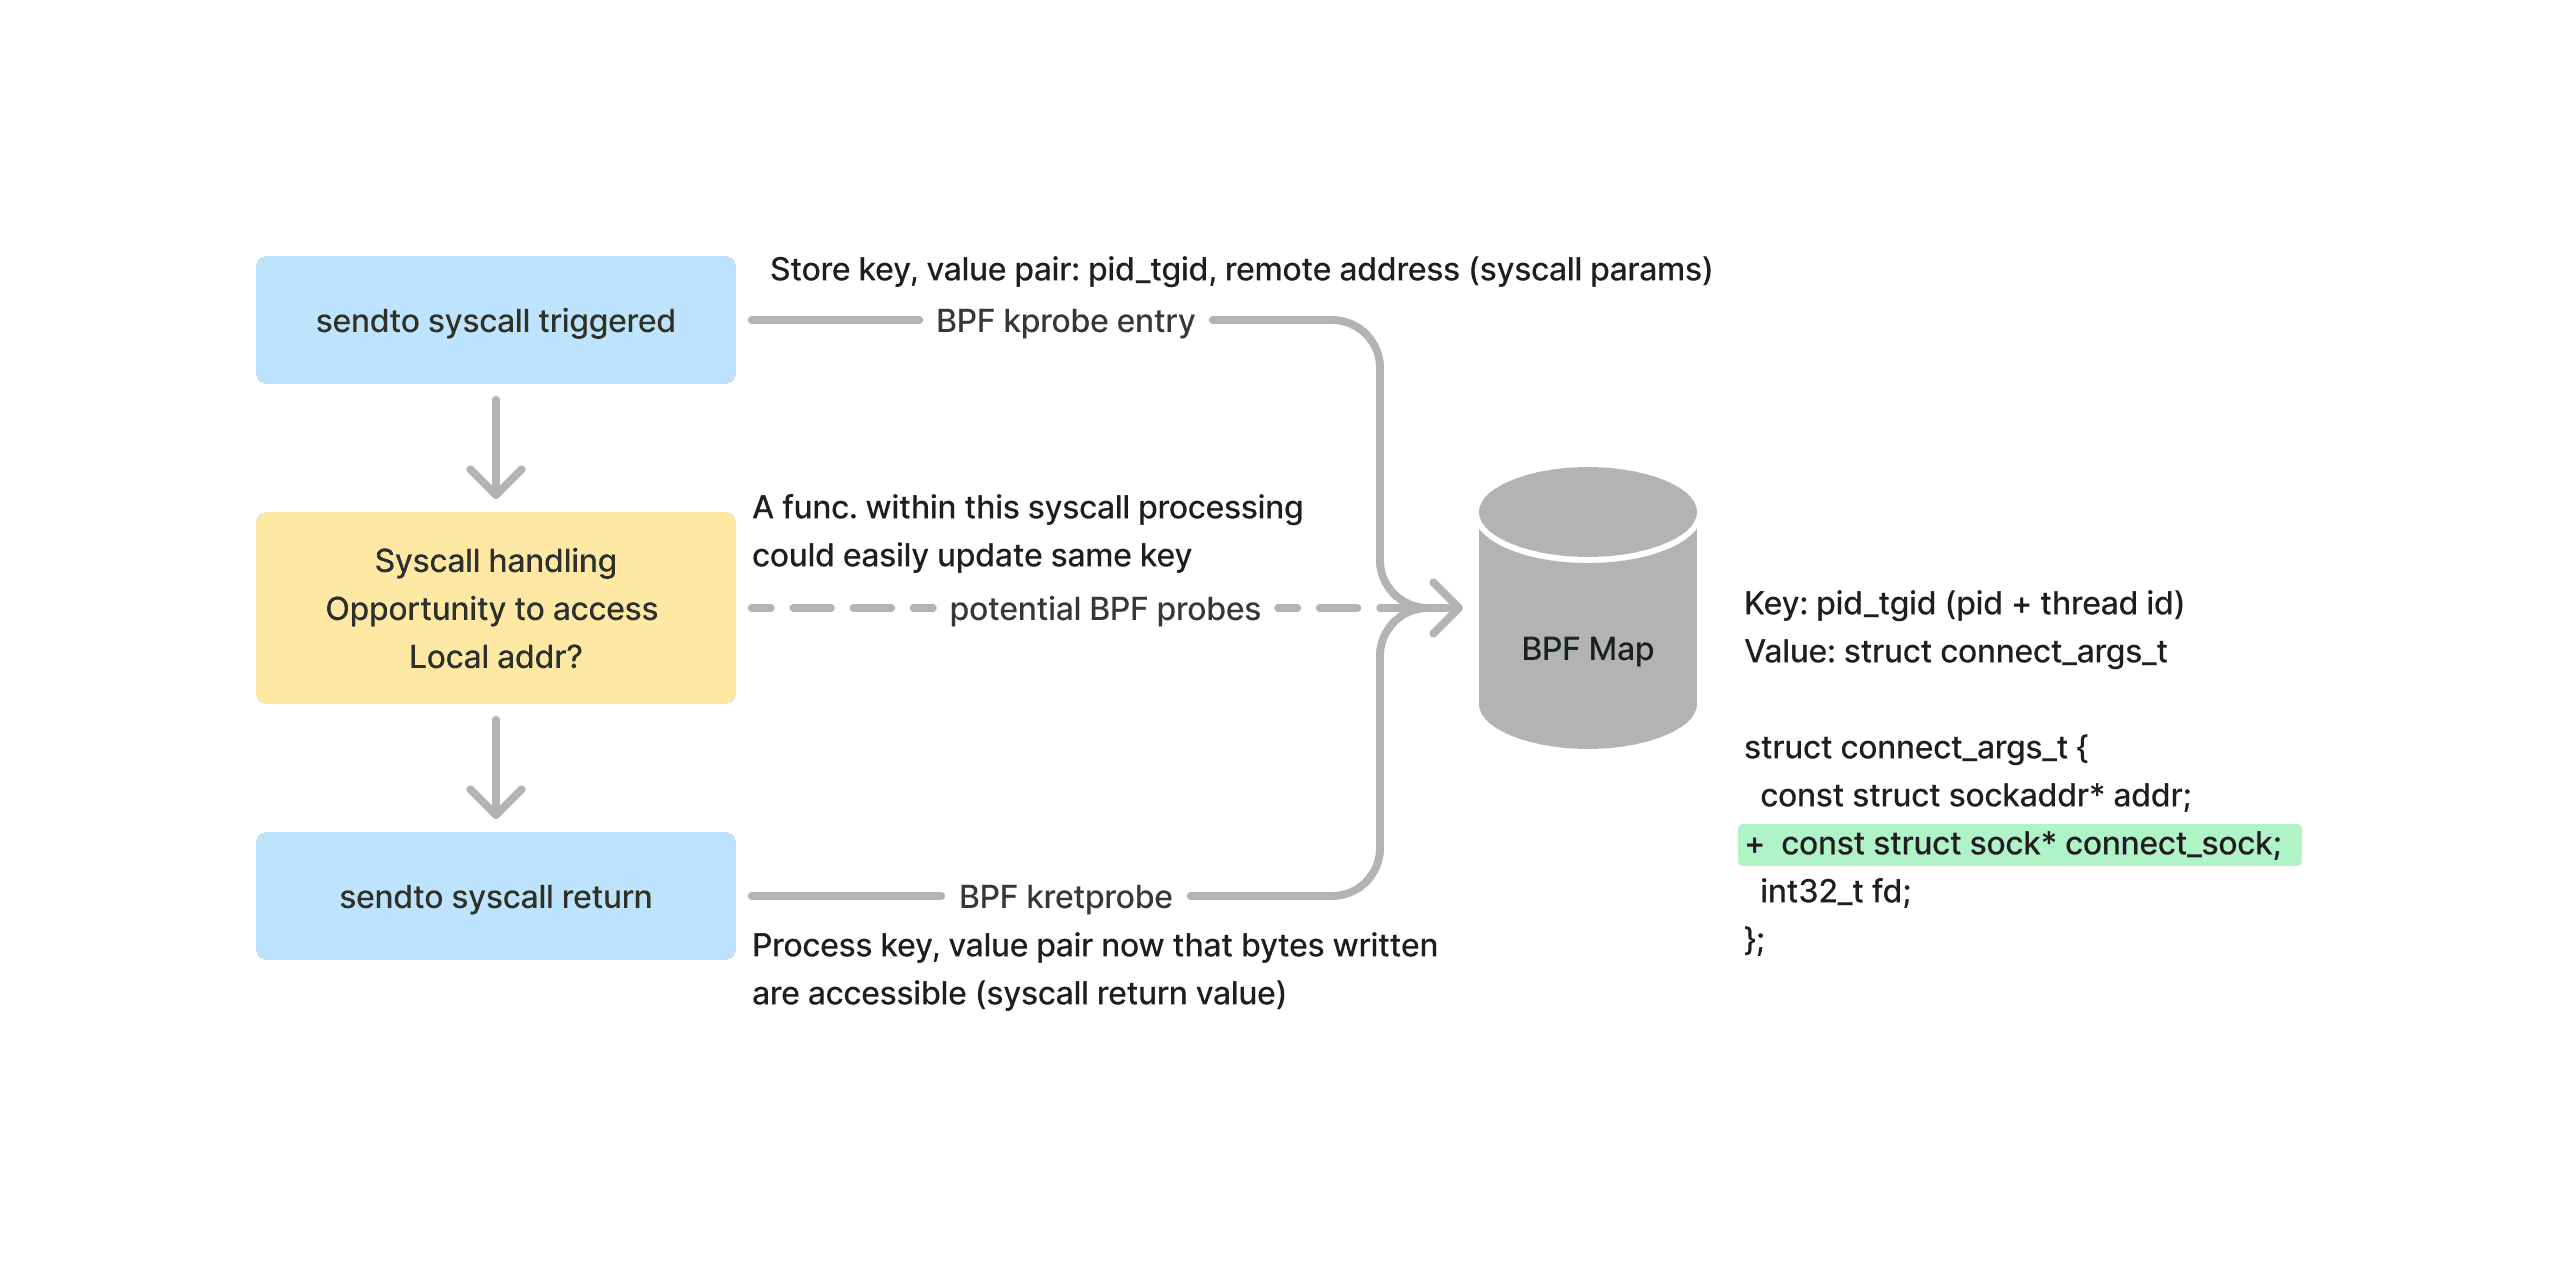
eBPF Probes and You: Navigating the kernel source for tracing | Pixie ...
eBPF and Falco: Runtime Anomaly Detection and Forensics | CleanStart
How to Use bpftrace and eBPF for System Tracing on RHEL
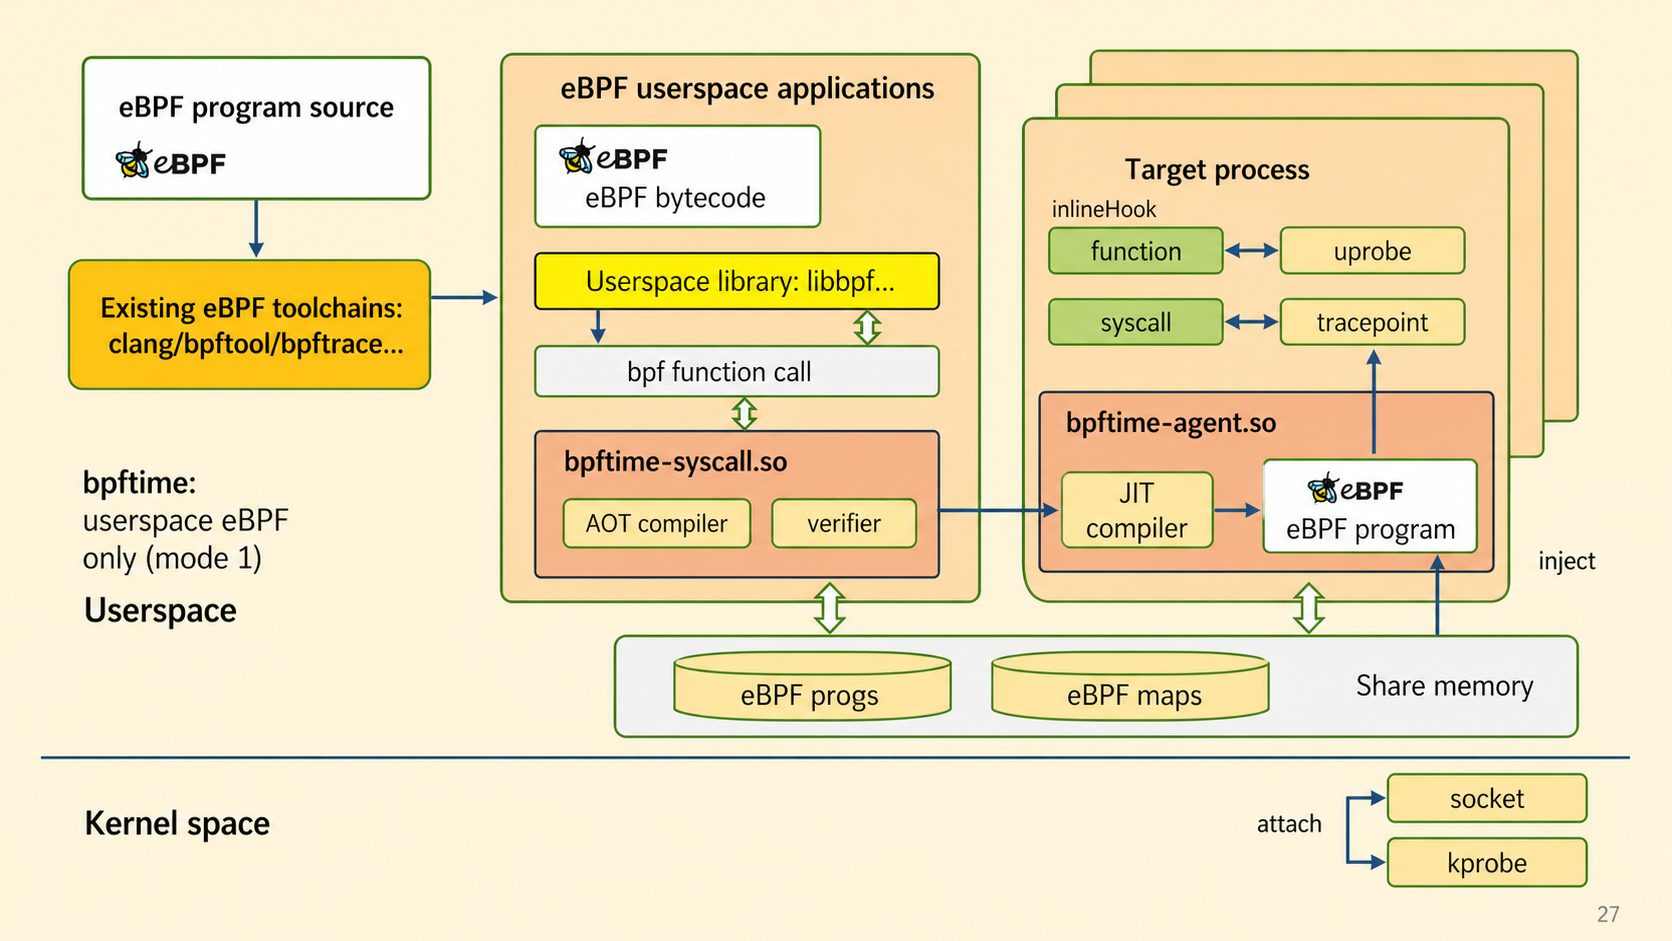
Eunomia - 开源 eBPF 系统研究与工具 | eunomia
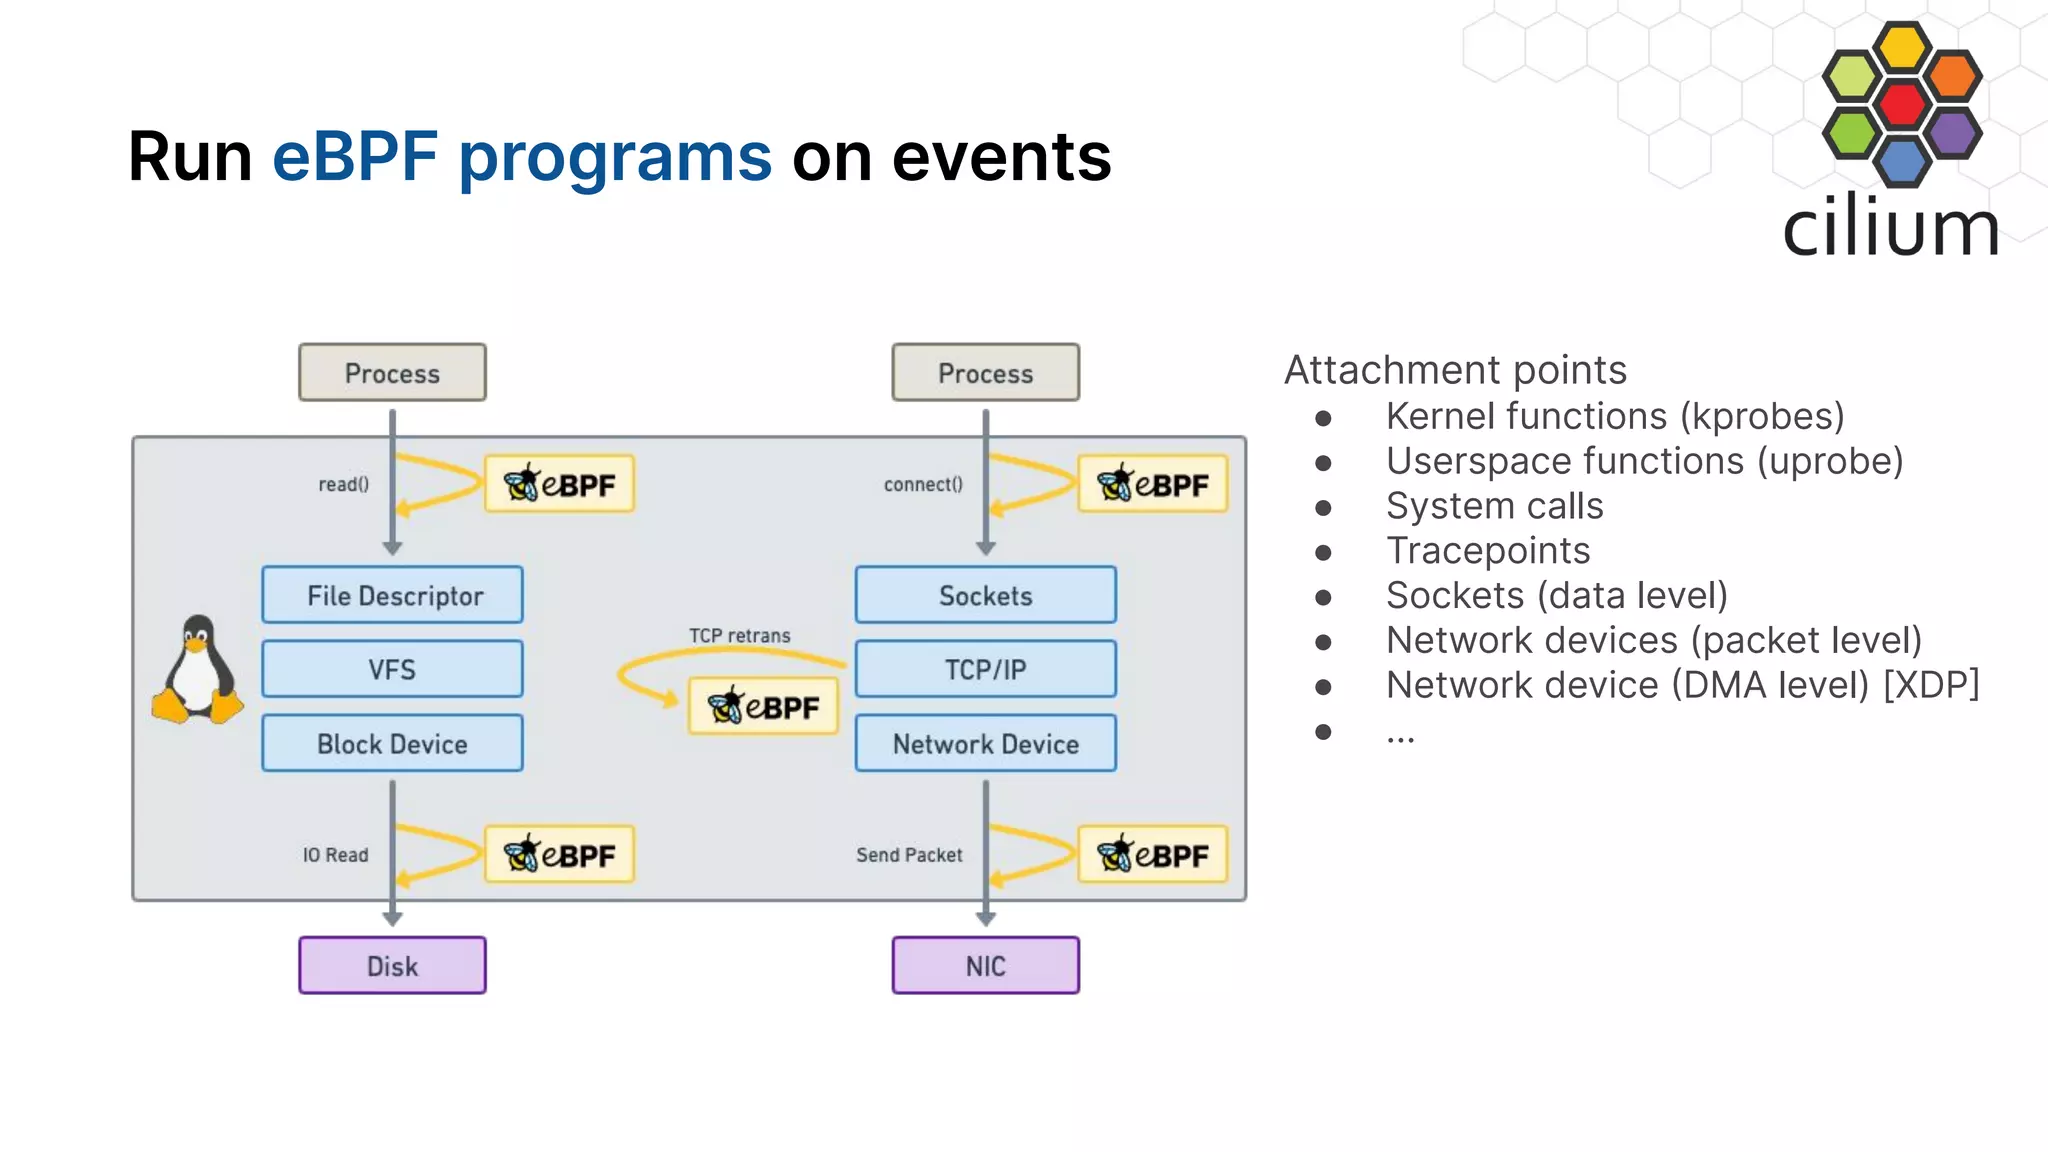
Enhancing Network and Runtime Security with Cilium and Tetragon by ...

4.bpf() 系统调用 - 学习 eBPF [Book]
Advertisement Space (336x280)
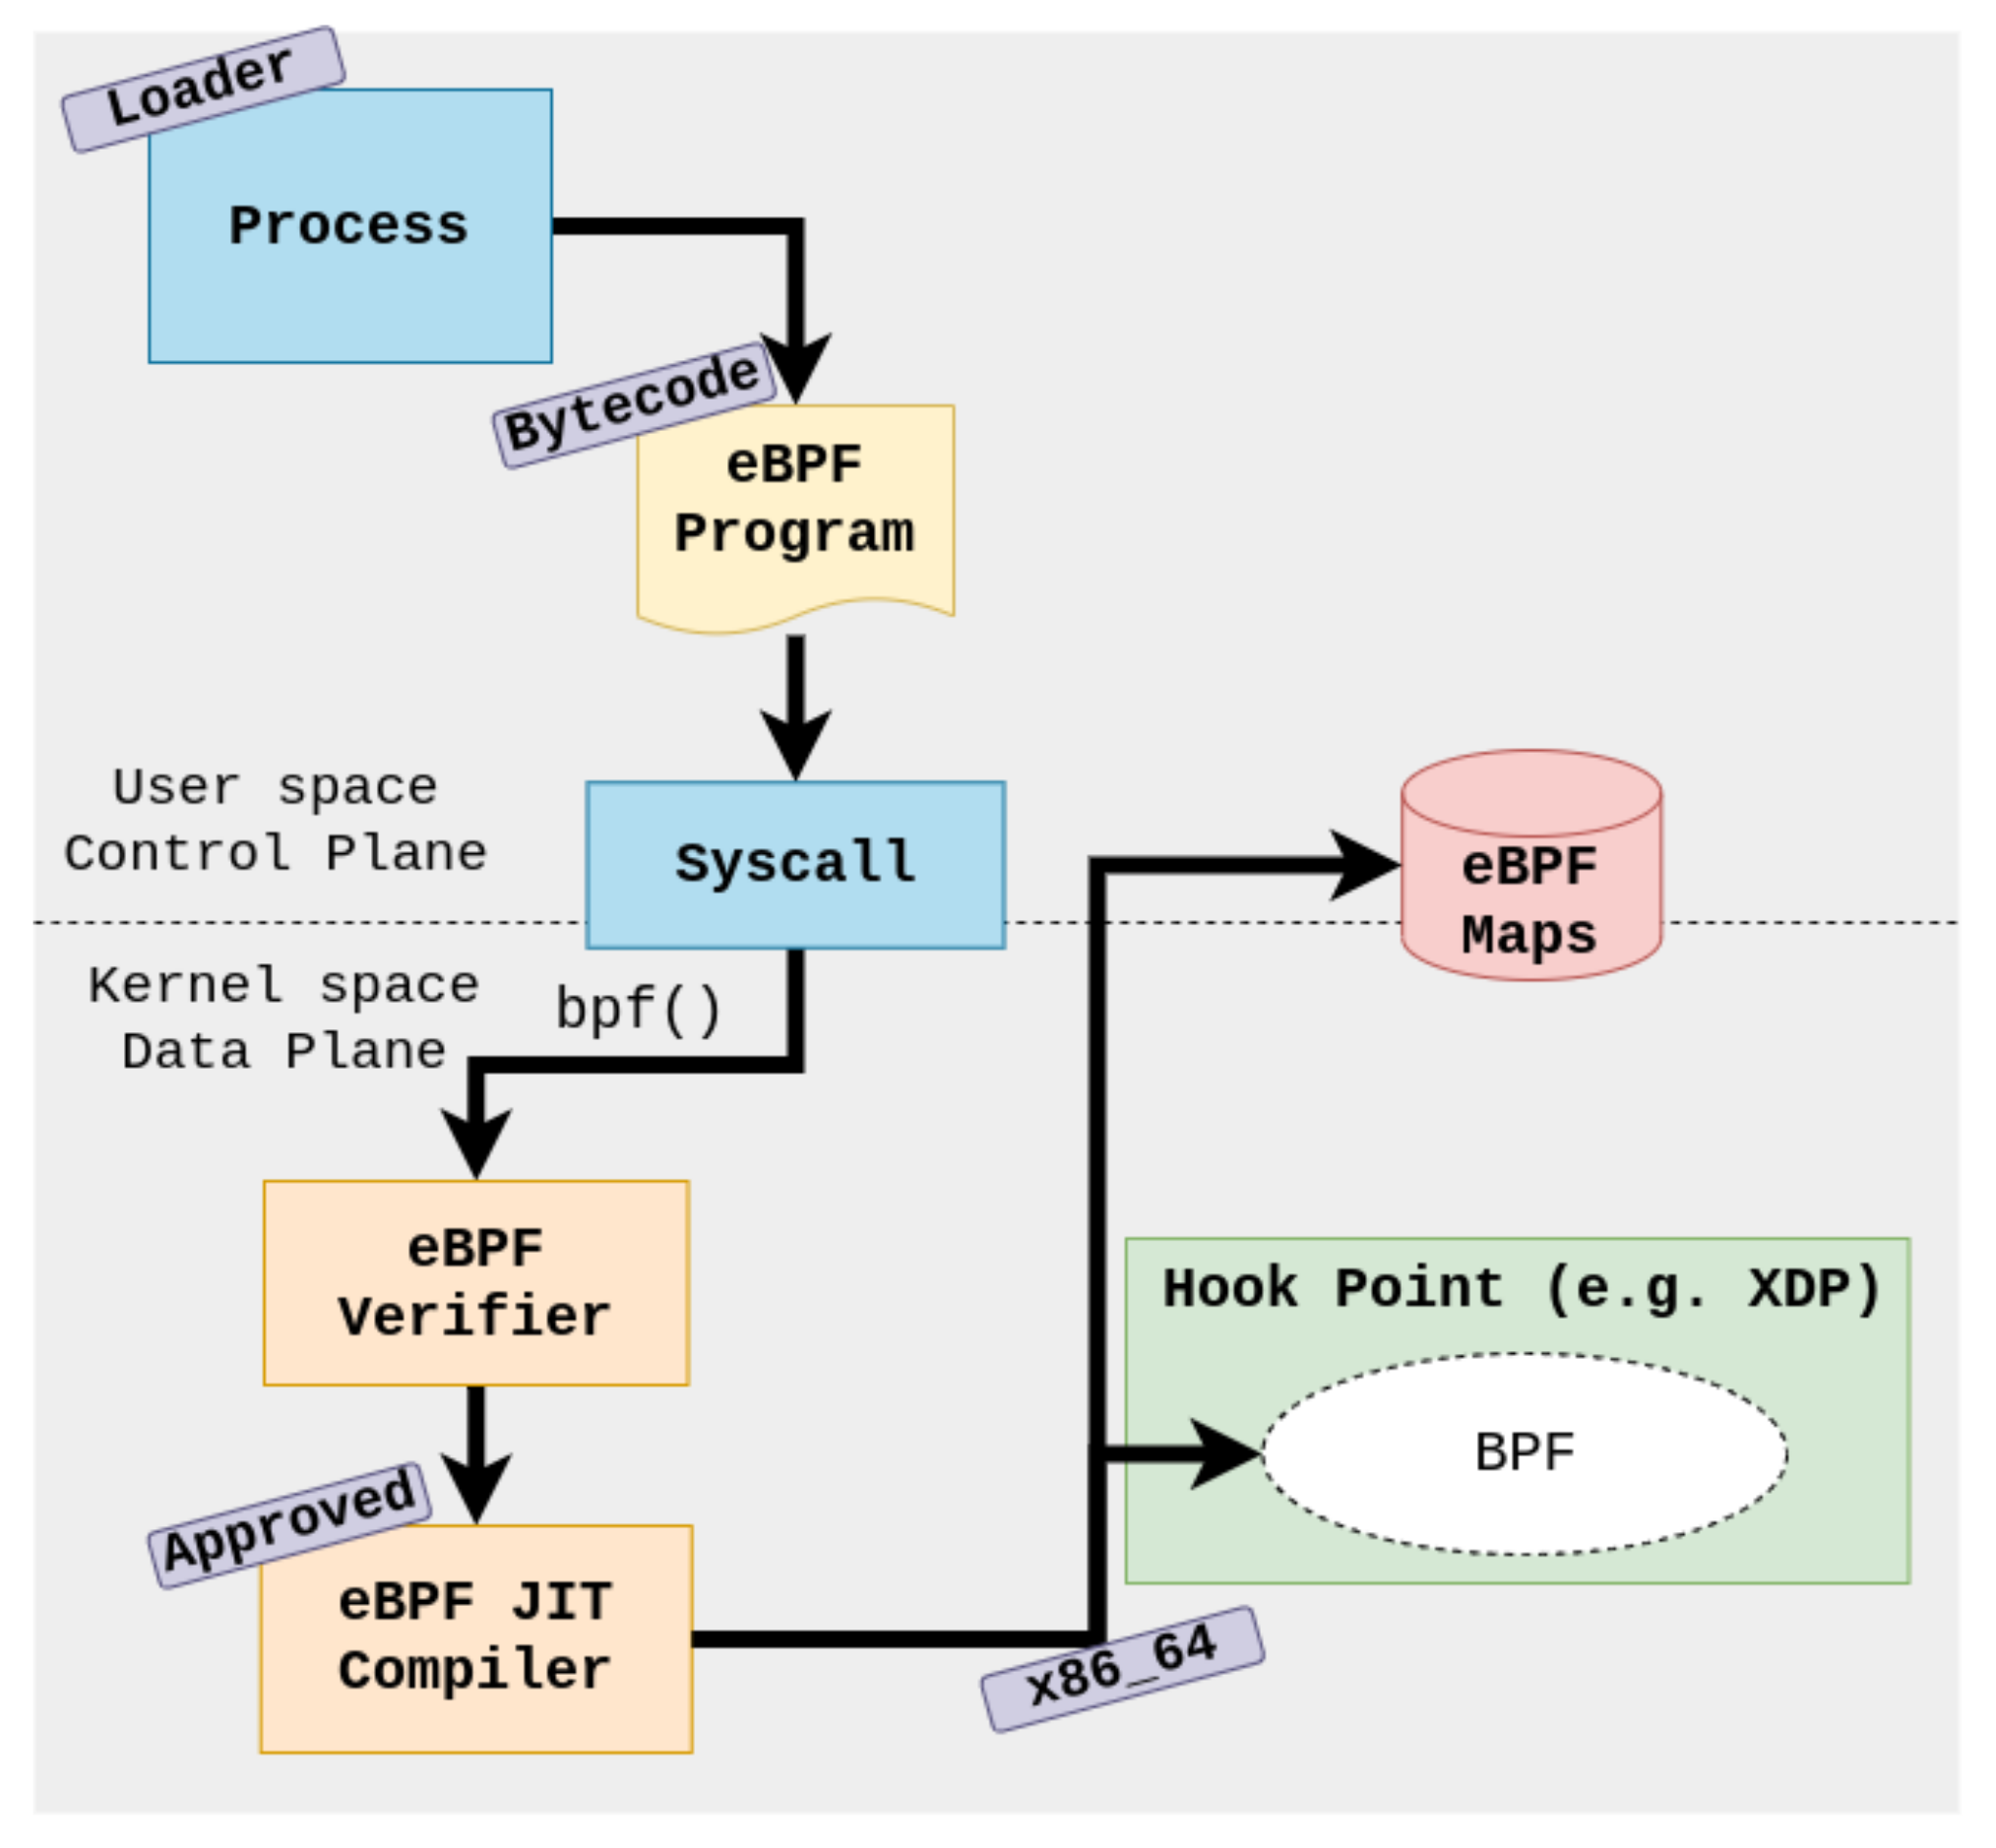
Run-Time Adaptive In-Kernel BPF/XDP Solution for 5G UPF

eBPF 零侵扰分布式追踪的进展和探索 - 云原生-可观测性-零侵扰采集-全栈可观测-分布式追踪-eBPF-Wasm-DeepFlow可观测性平台
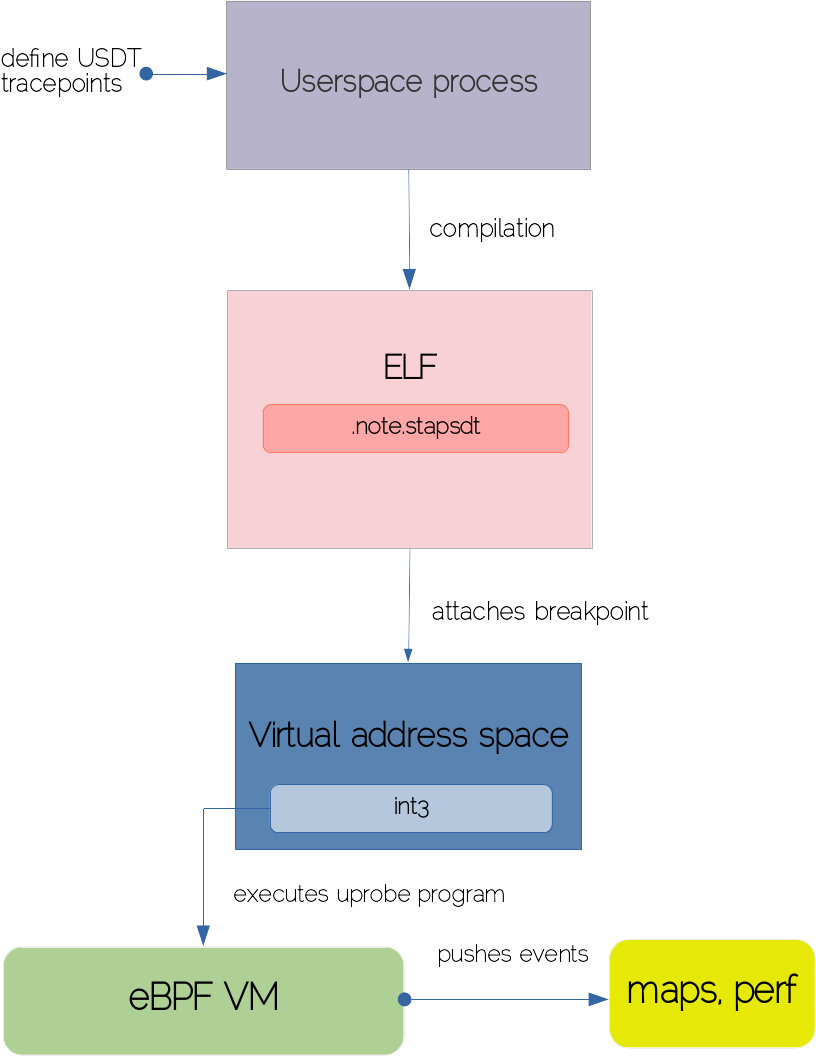
How to Instrument UserLand Apps with eBPF - Sematext

CloudNativeSecurityCon 2023: Identifying Suspicious Behaviors with eBPF ...
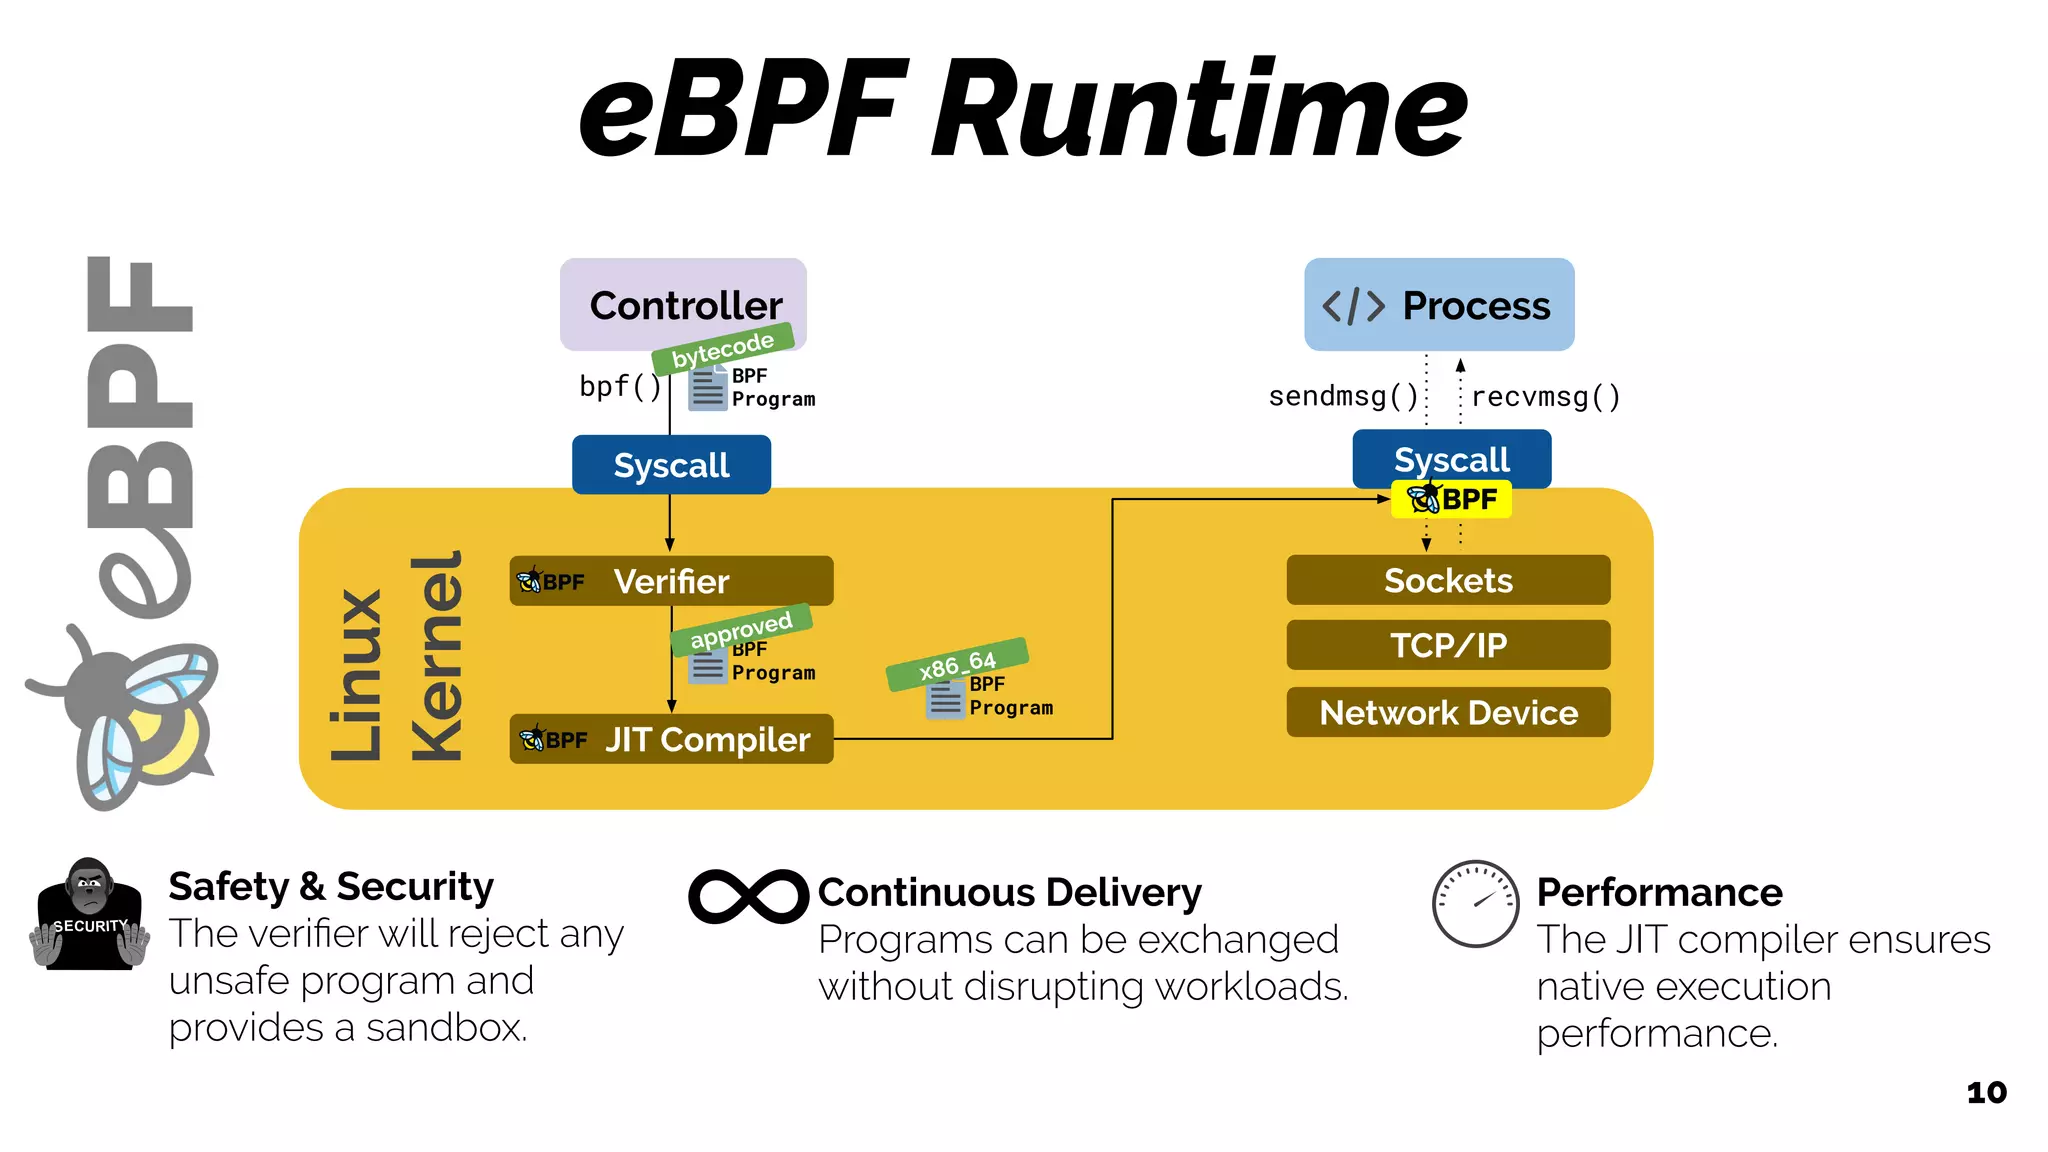
eBPF - Rethinking the Linux Kernel | PDF
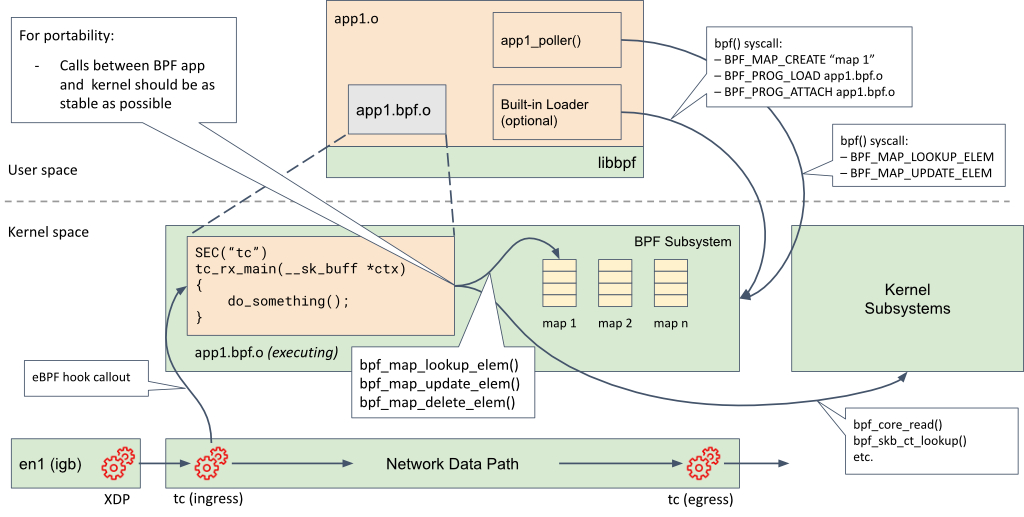
eBPF application development: Beyond the basics | Red Hat Developer