
Bpftime Userspace Ebpf Runtime For Uprobe Syscall And Kernel

文献阅读: bpftime: userspace eBPF Runtime for Uprobe, Syscall and Kernel ...

文献阅读: bpftime: userspace eBPF Runtime for Uprobe, Syscall and Kernel ...

文献阅读: bpftime: userspace eBPF Runtime for Uprobe, Syscall and Kernel ...

bpftime: Userspace eBPF runtime for fast Uprobe & Syscall hook ...
GitHub - CUIKingdom/bpftime-plc: Userspace eBPF runtime for fast Uprobe ...

bpftime: Userspace eBPF Runtime for Network and Observability - Yusheng ...

bpftime: un runtime de eBPF en el espacio de usuario para Uprobe y Syscall
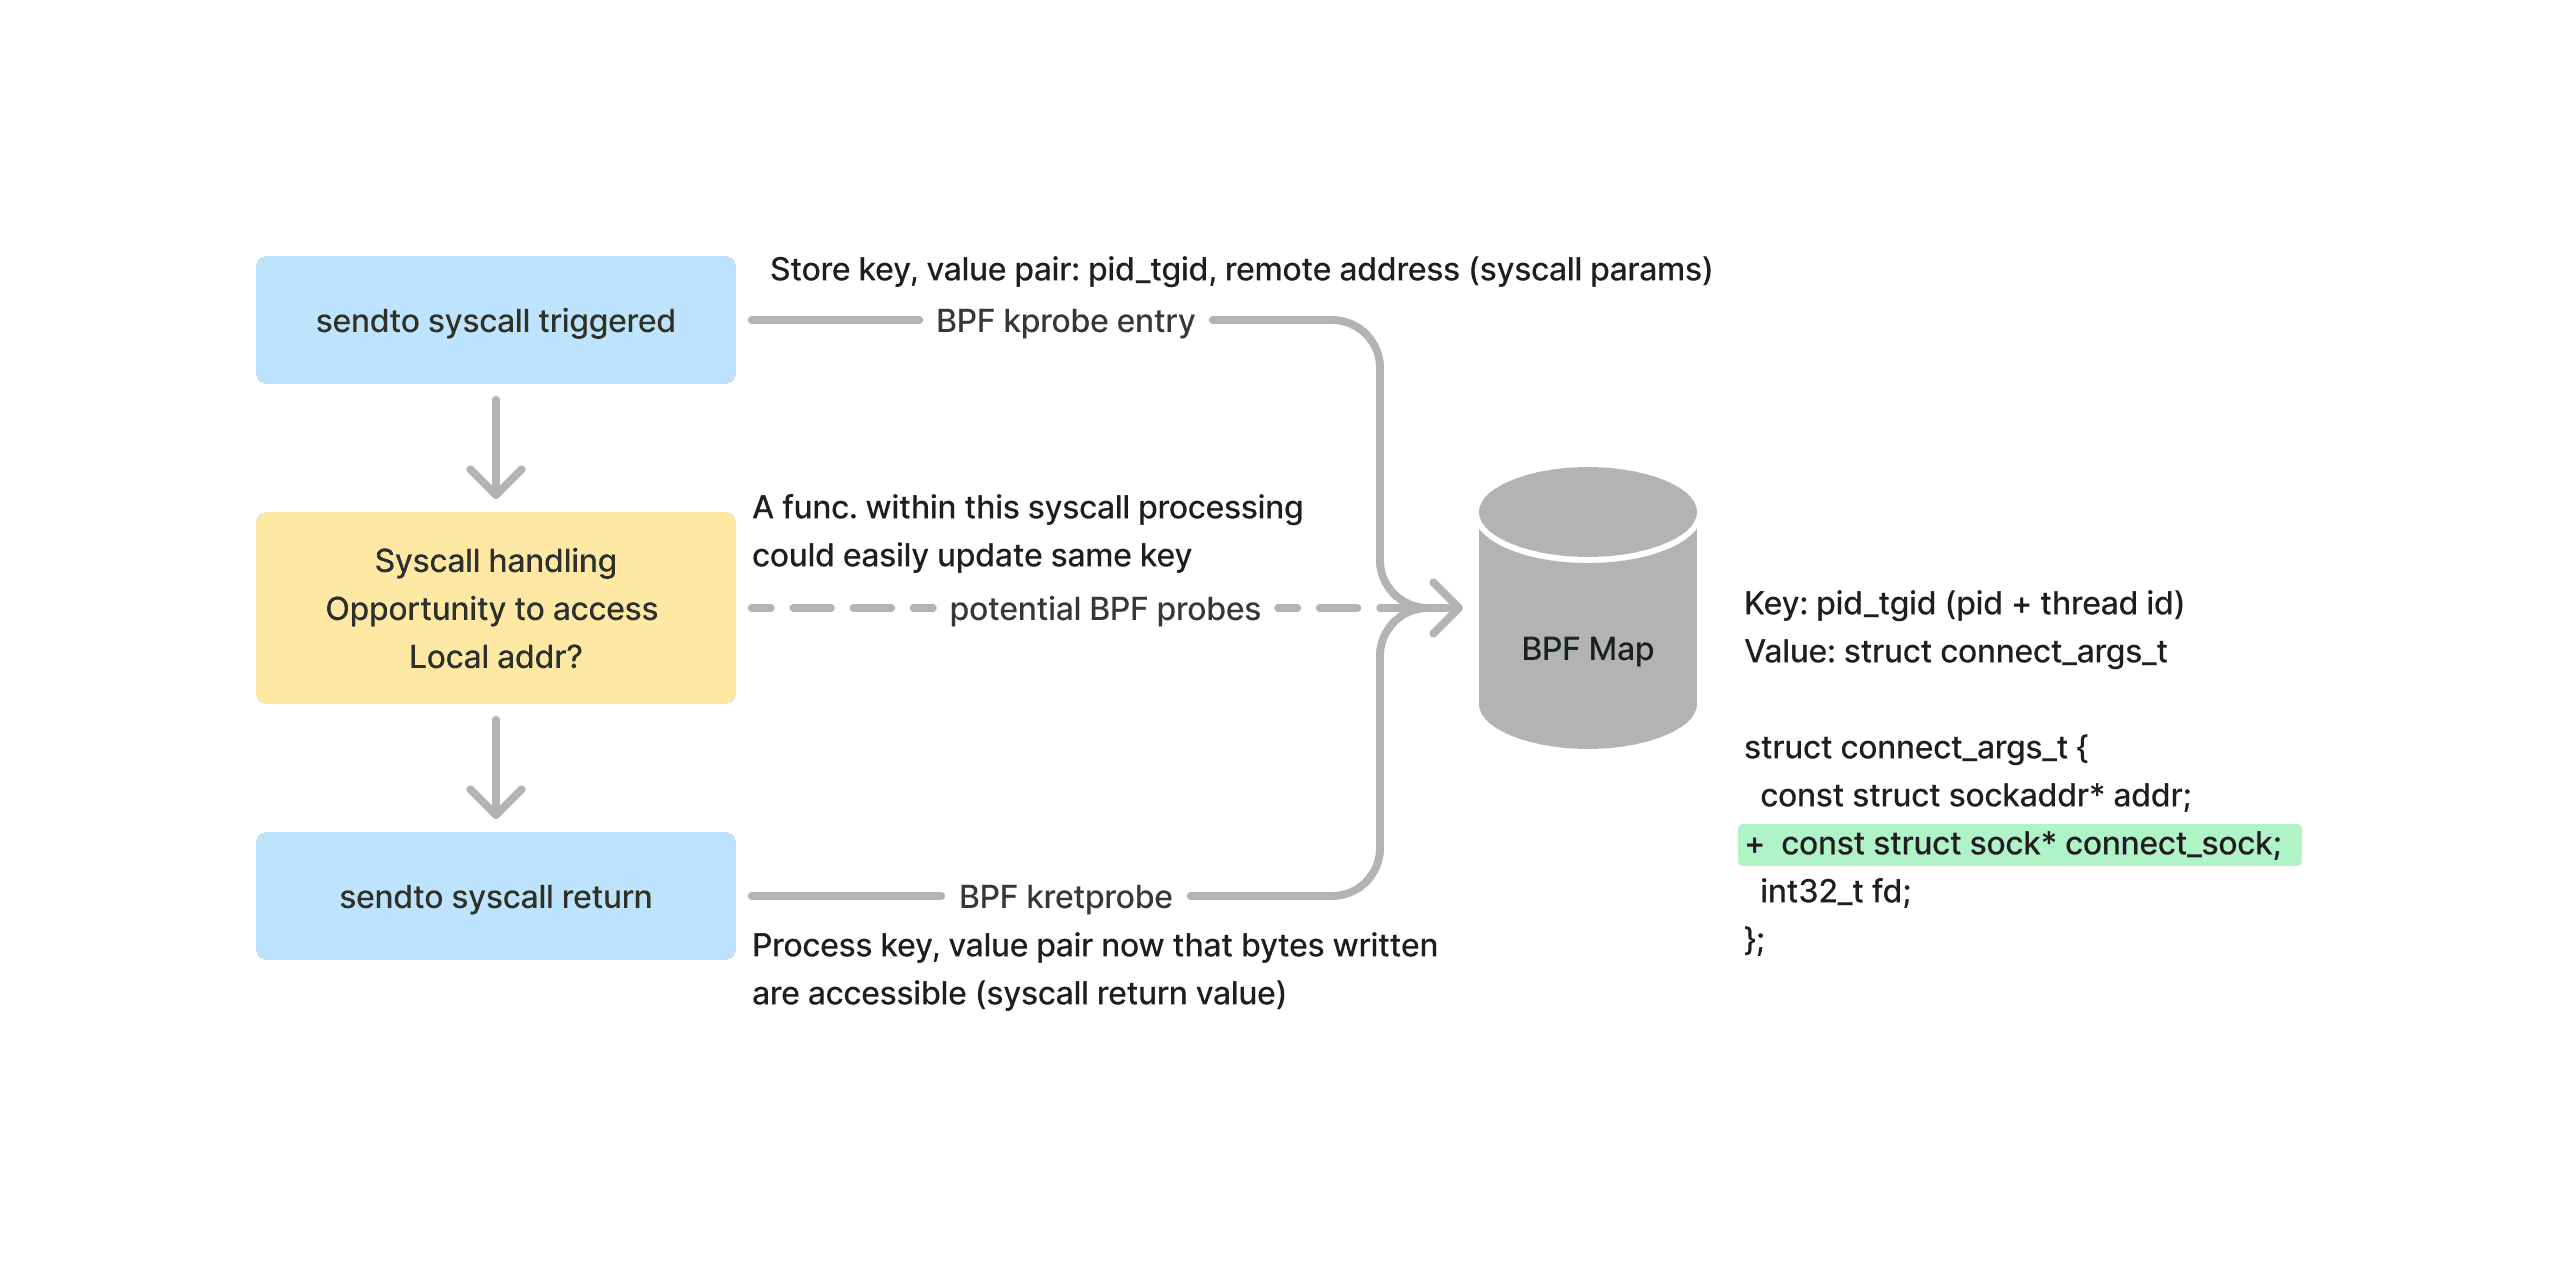
eBPF Probes and You: Navigating the kernel source for tracing | Pixie ...

Master eBPF Kernel Observability: Syscall Tracing, Runtime Security ...

eBPF and Wasm: Unifying Userspace Extensions With Bpftime - Yusheng…
Advertisement Space (300x250)
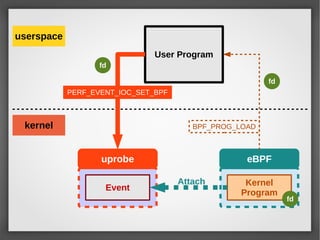
eBPF Trace from Kernel to Userspace | PDF
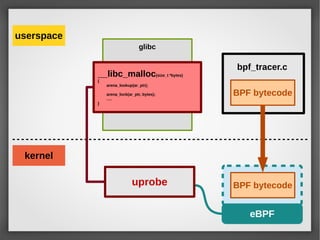
eBPF Trace from Kernel to Userspace | PDF

bpftime: Extending eBPF from Kernel to Userspace - DEV Community

eBPF Trace from Kernel to Userspace | PDF | Operating Systems ...

bpftime: Extending eBPF from Kernel to Userspace - DEV Community
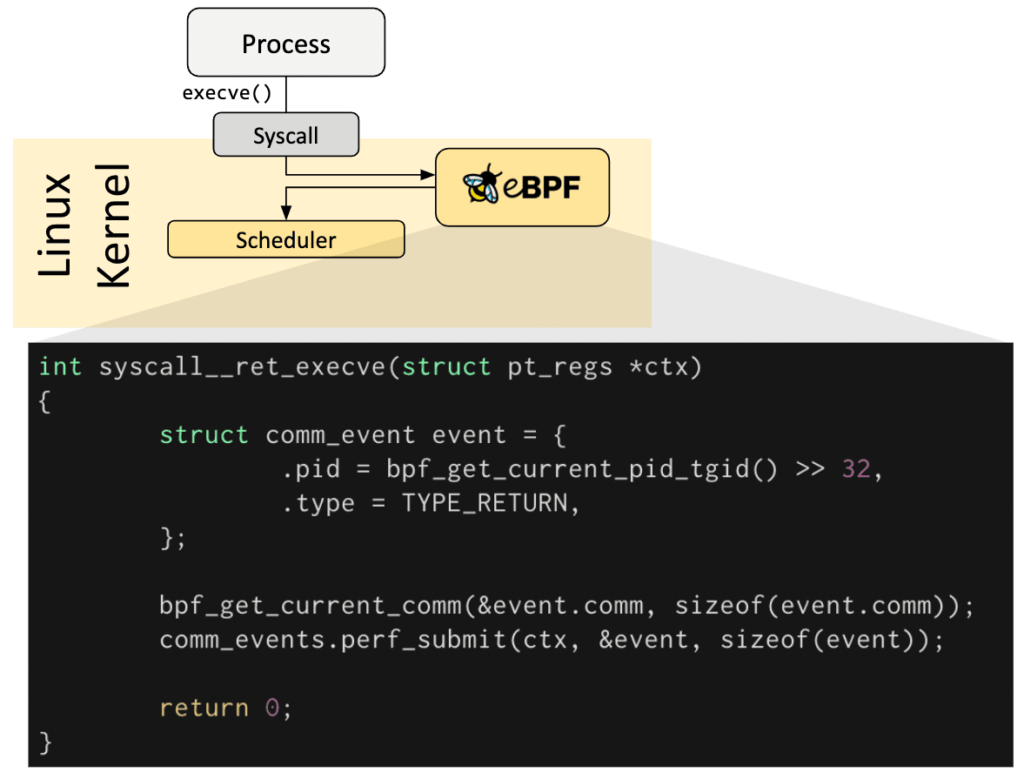
eBPF and its use for Istio service mesh
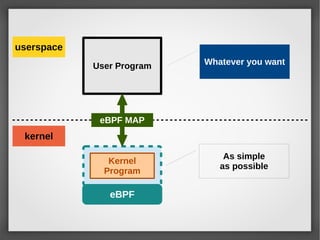
eBPF Trace from Kernel to Userspace | PDF

eBPF and its use for Istio service mesh

eBPF Trace from Kernel to Userspace | PDF
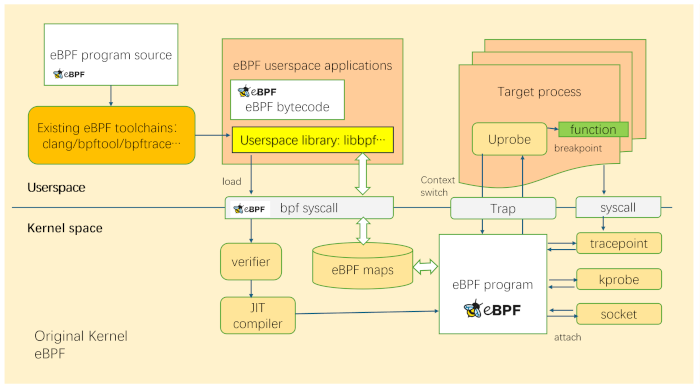
BPFTime Project Creates User-Space EBPF Implementation | Altus Intel
Advertisement Space (336x280)

Issue #002 | Programming the Kernel with eBPF
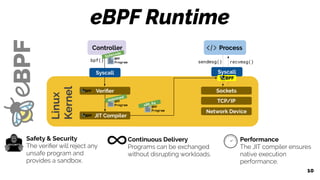
eBPF - Rethinking the Linux Kernel | PDF
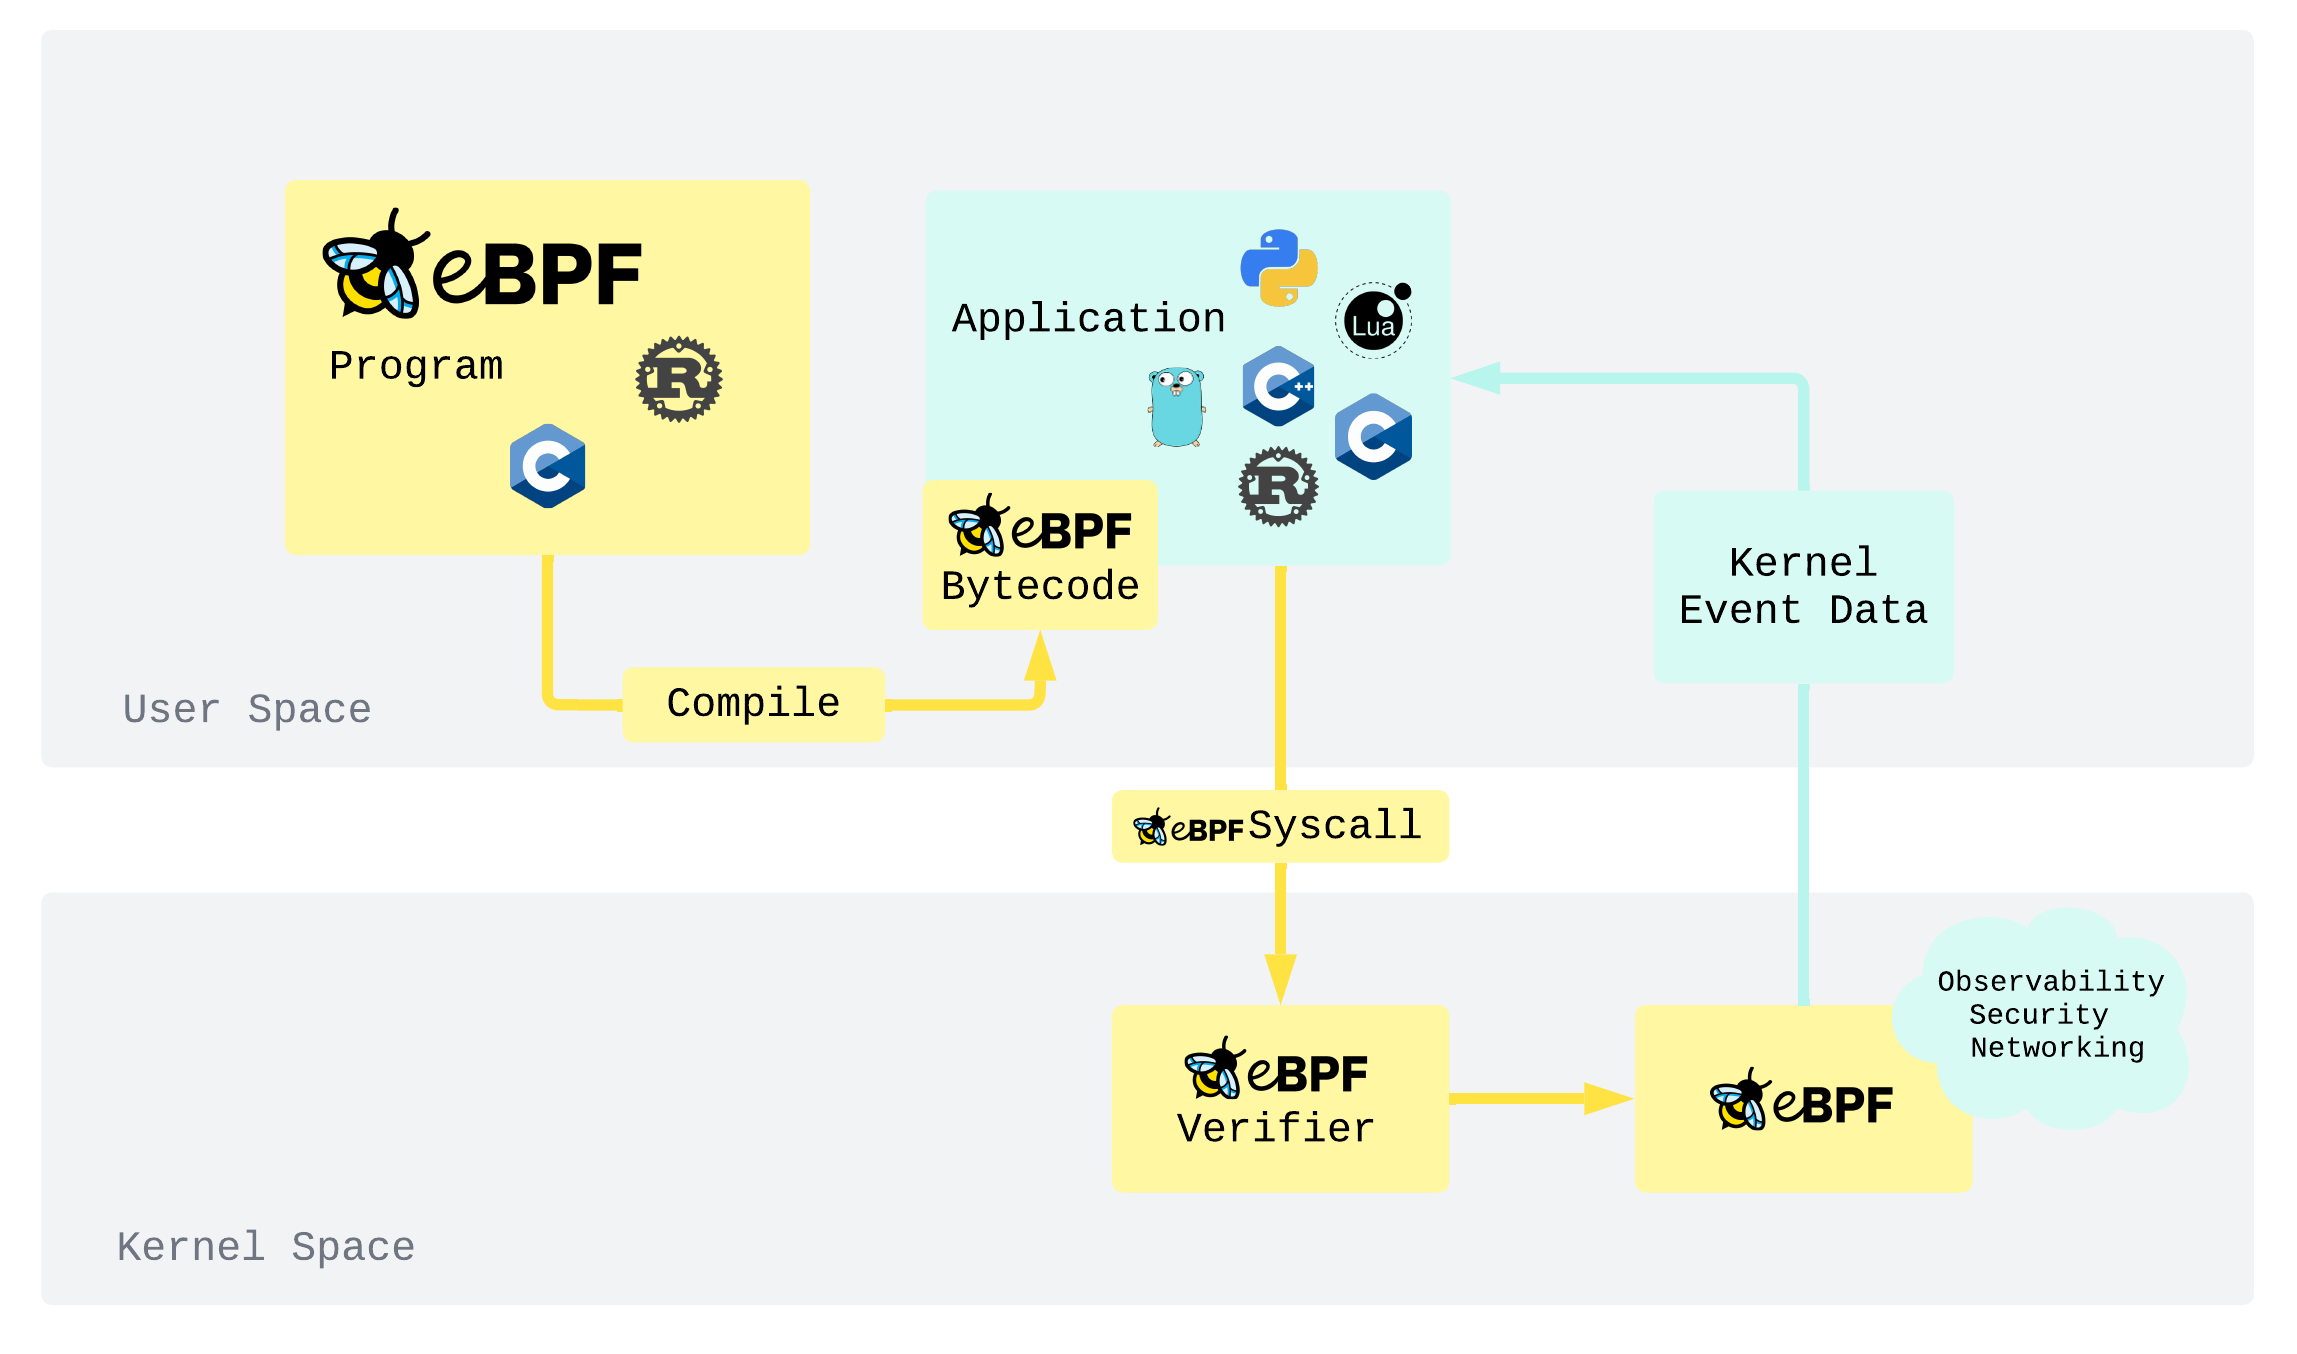
Go, C, Rust, and More: Picking the Right eBPF Application Stack
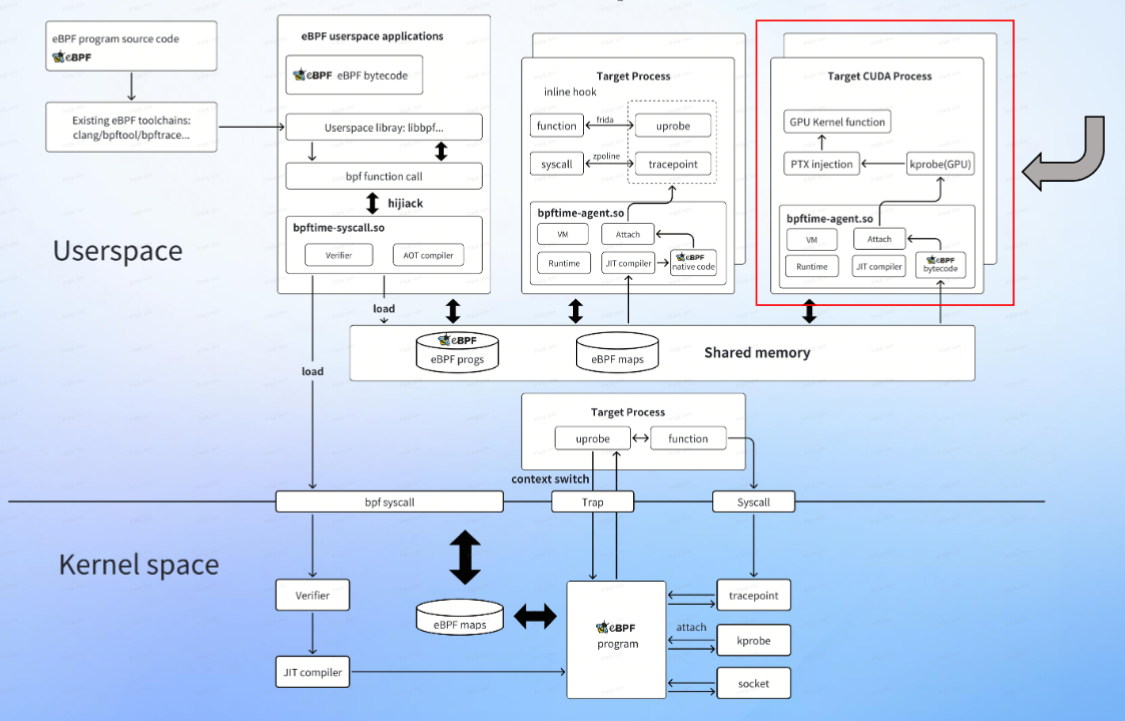
将 eBPF 扩展到 GPU 设备上下文 ── bpftime 的 GPU 可观测性与调度实践 - 知乎
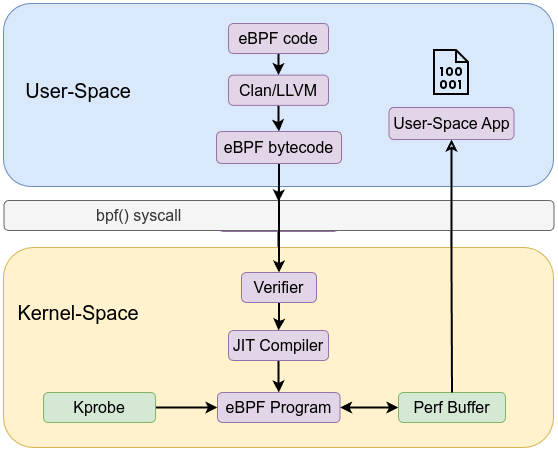
Kprobe and Kretprobe | Engineering Everything with eBPF
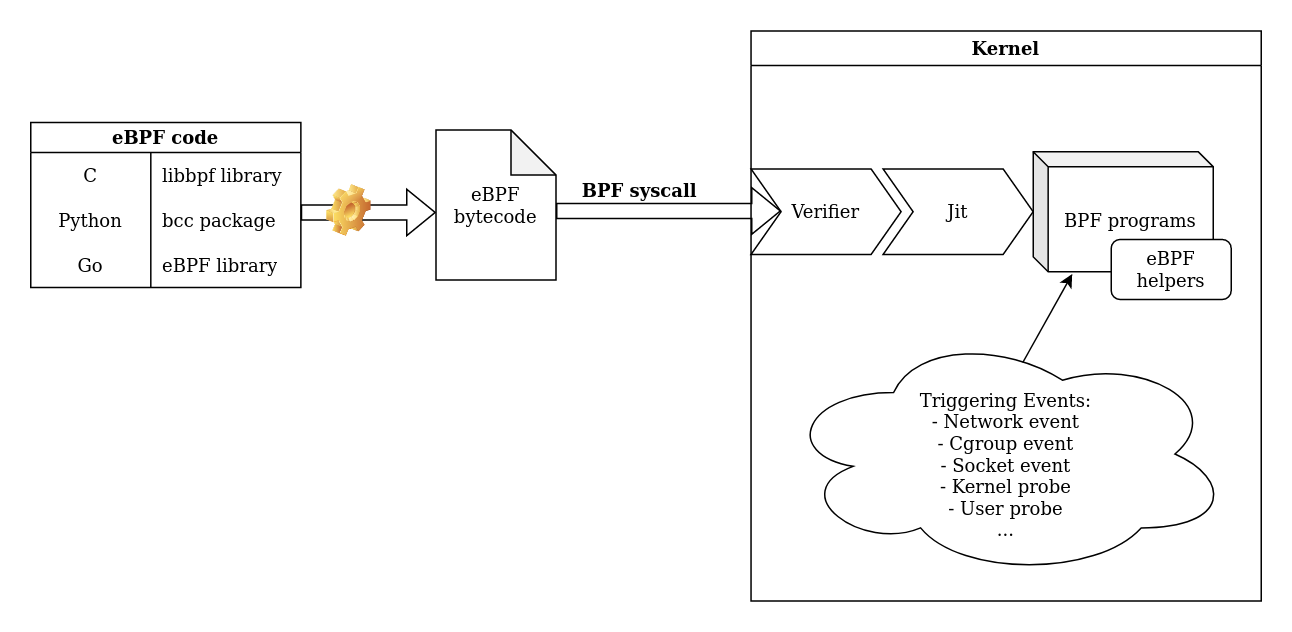
Defeating eBPF Uprobe Monitoring - Quarkslab's blog
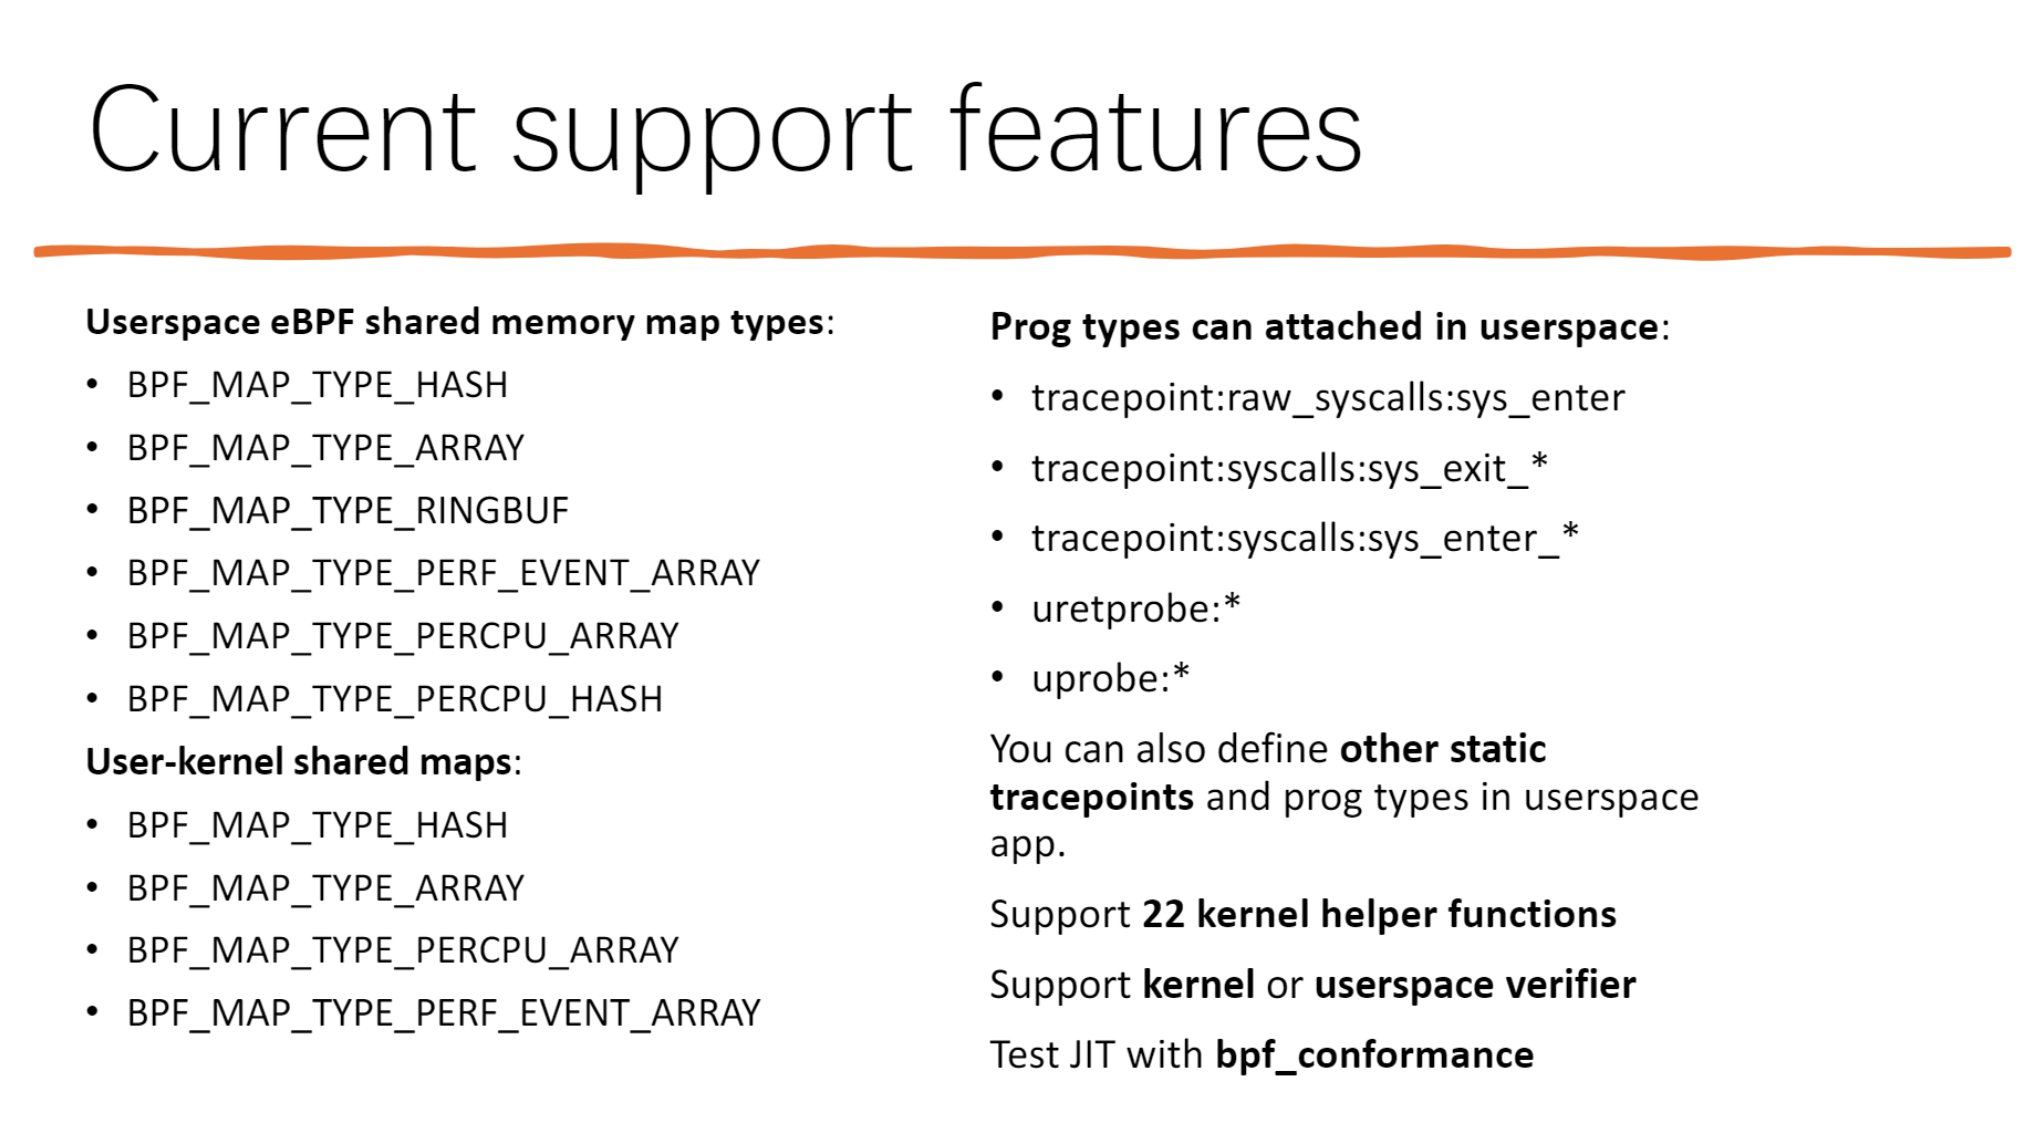
bpftime: Extending eBPF from Kernel to User Space | 云微的胡思乱想
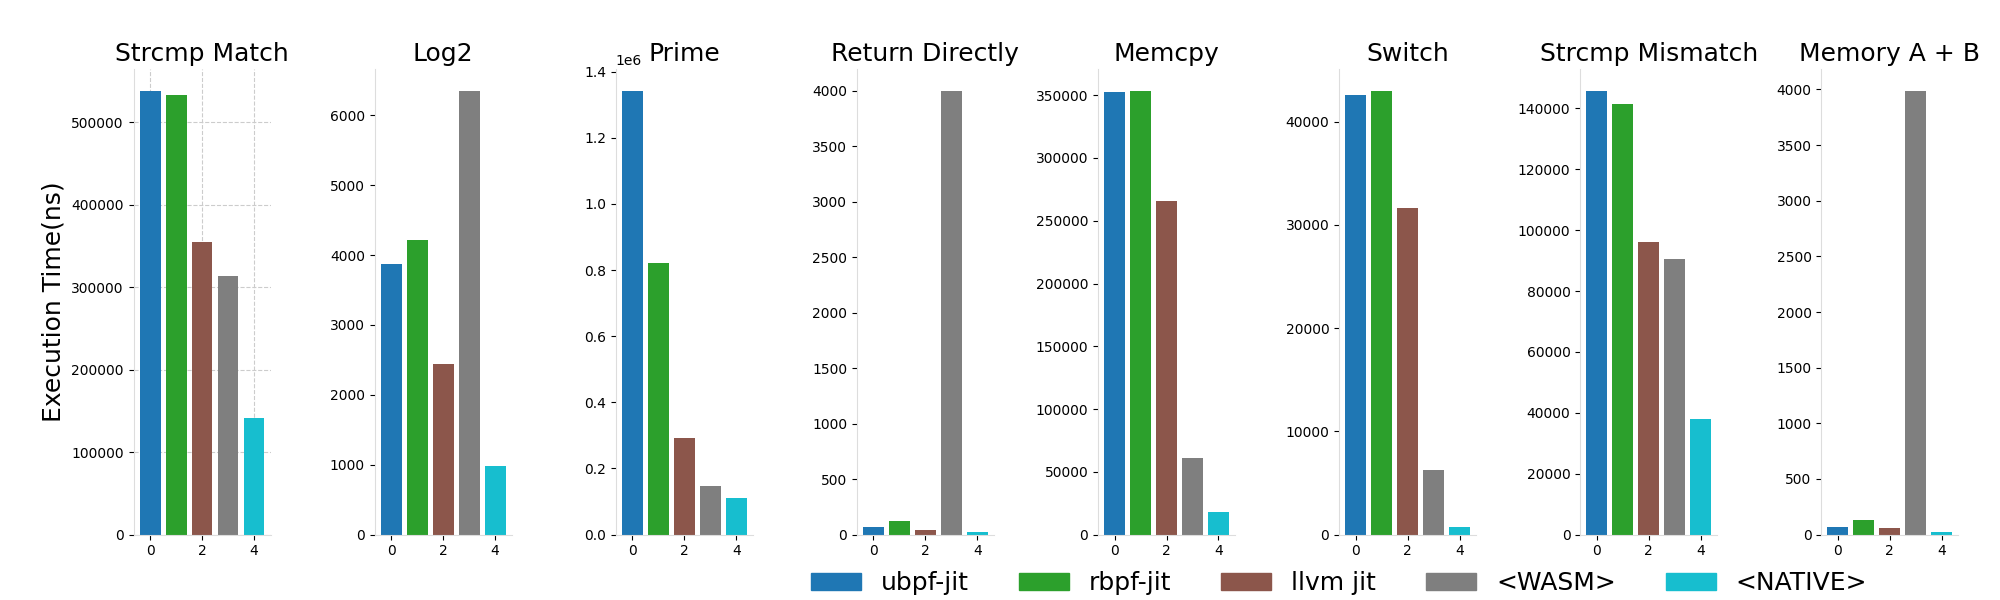
bpftime: Extending eBPF from Kernel to User Space | 云微的胡思乱想
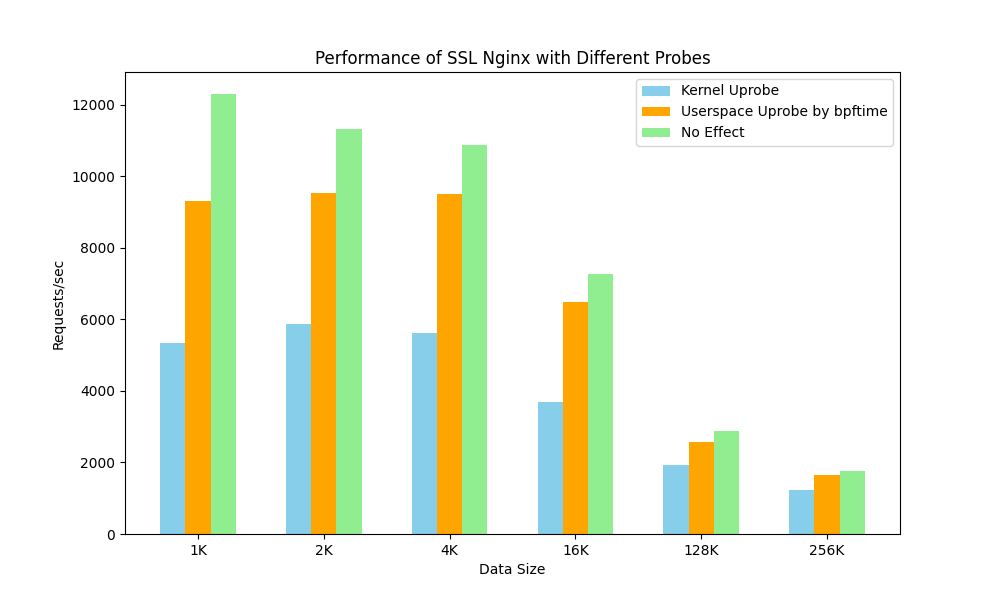
bpftime: Extending eBPF from Kernel to User Space | eunomia
The Open Source Ecosystem for eBPF in Kubernetes | PDF
Advertisement Space (336x280)
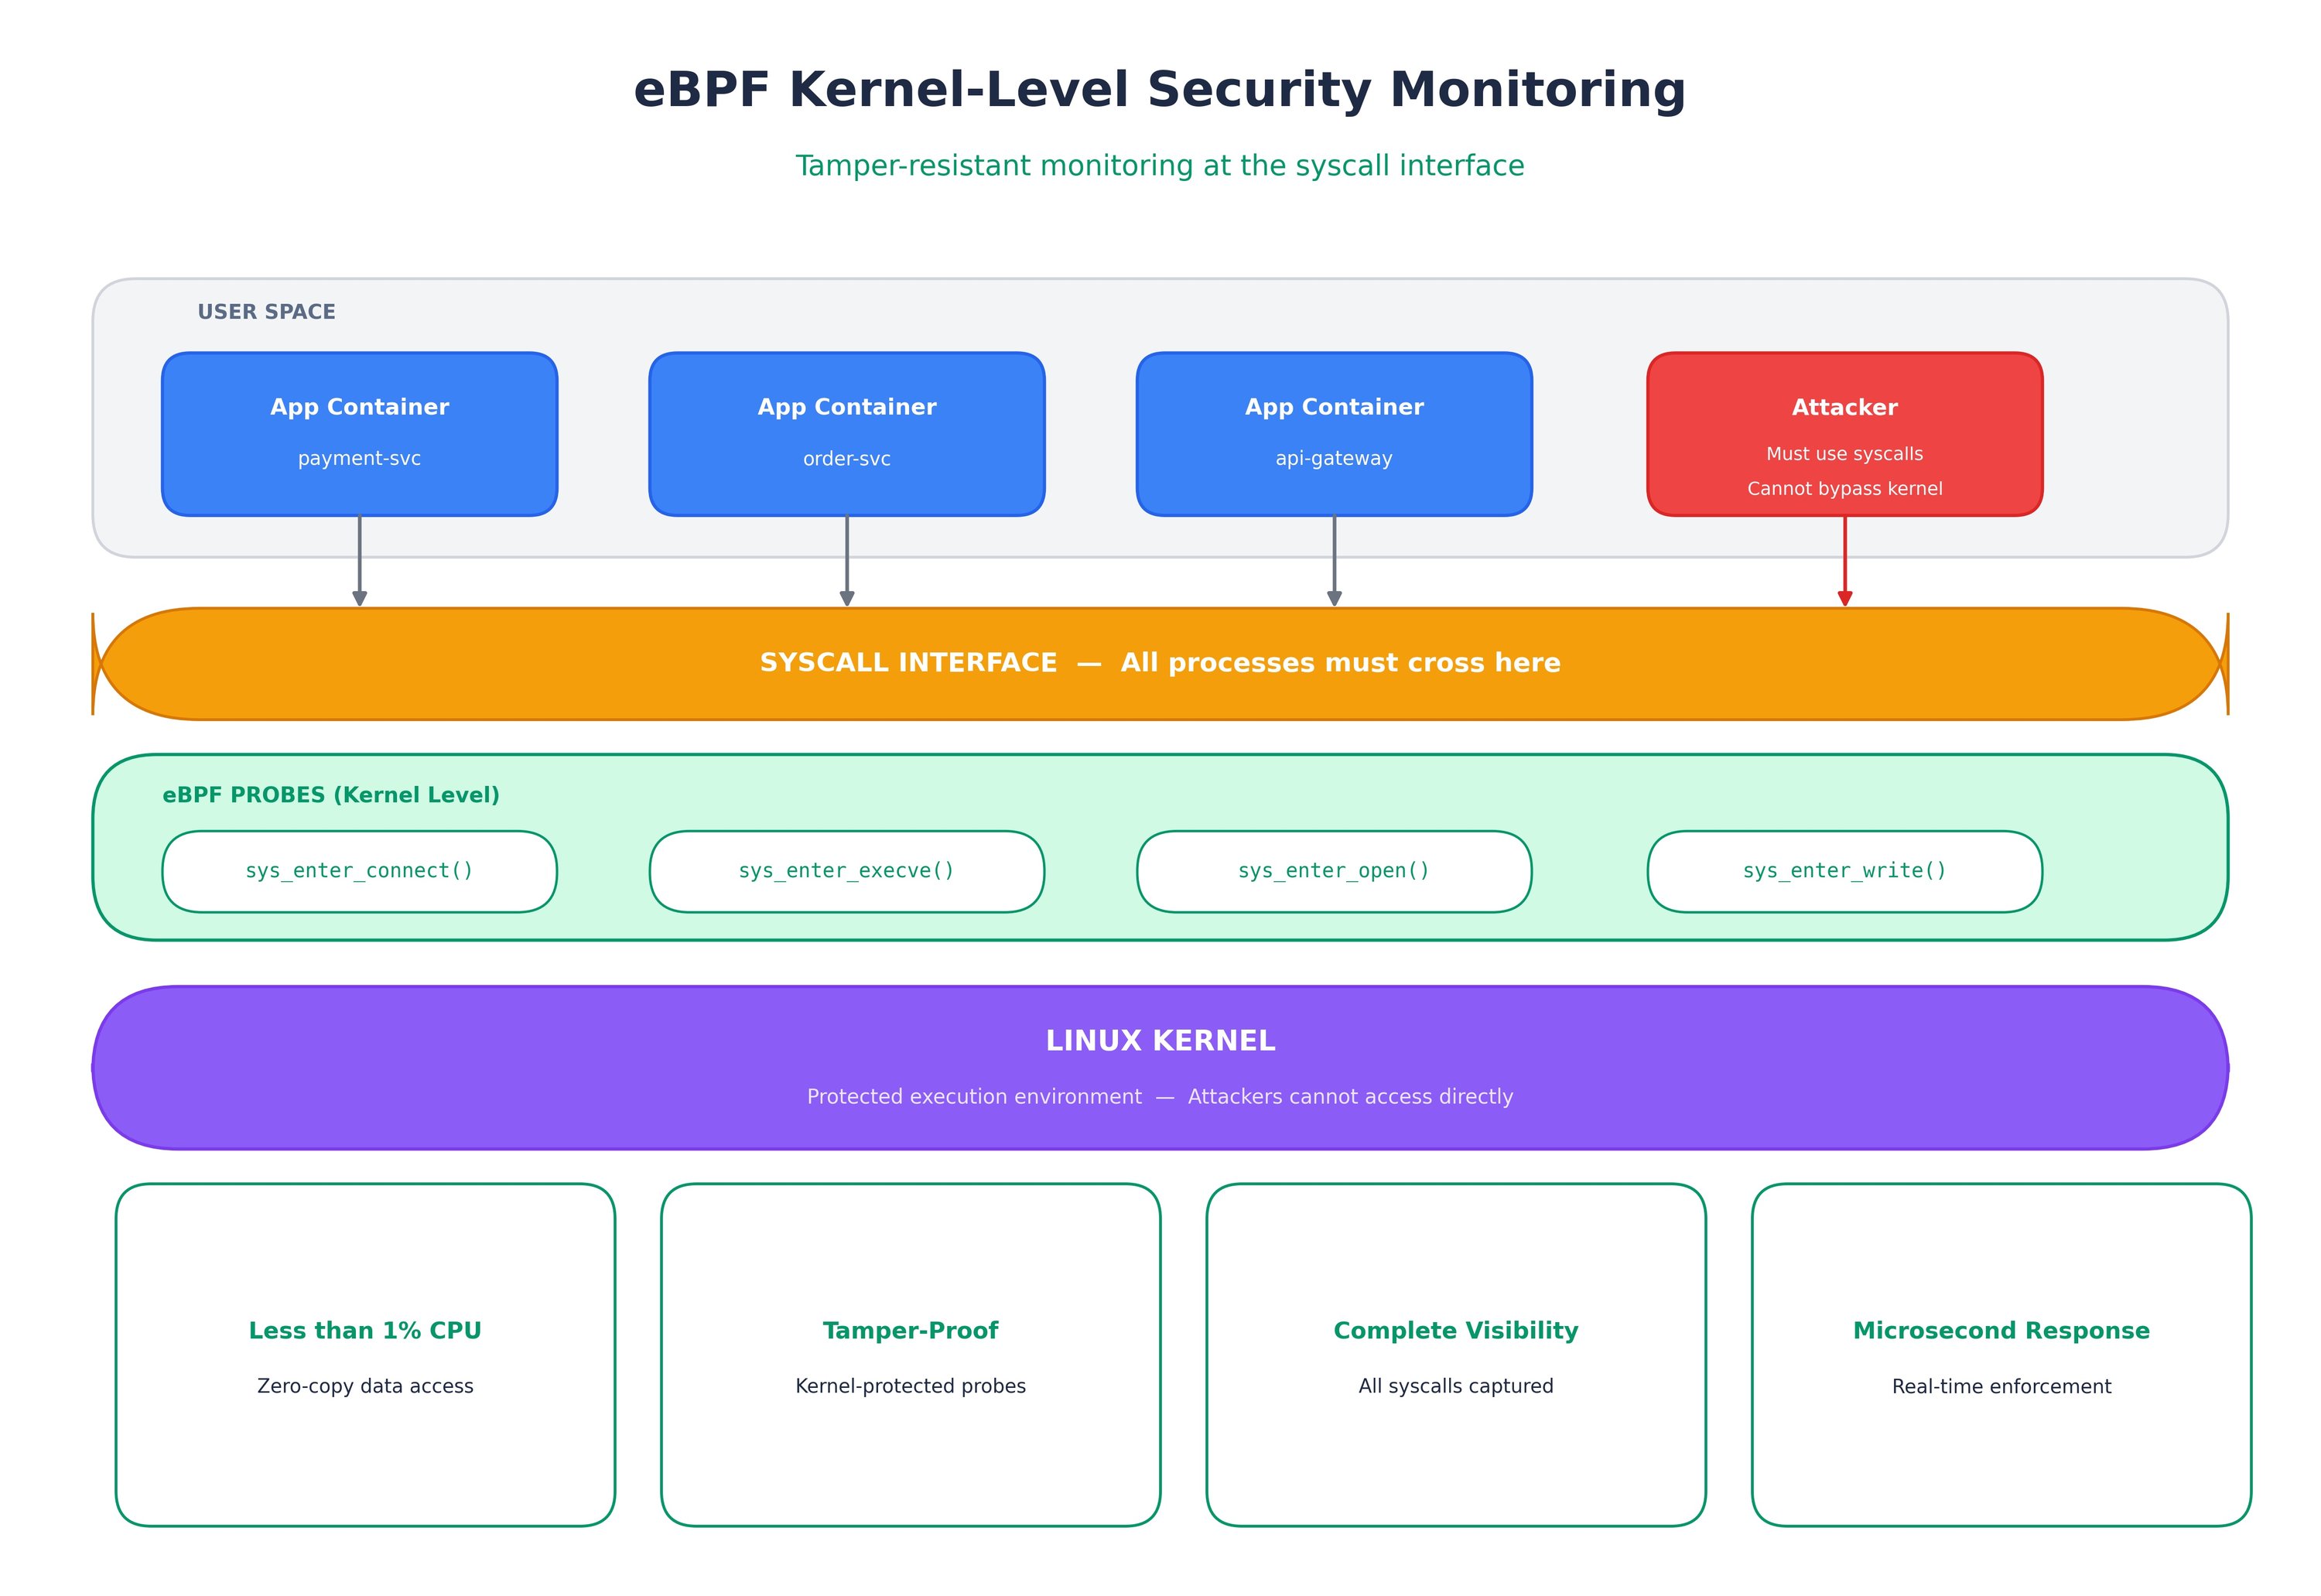
Kernel-Level Ground Truth: Why eBPF is Replacing User-Space Agents for ...
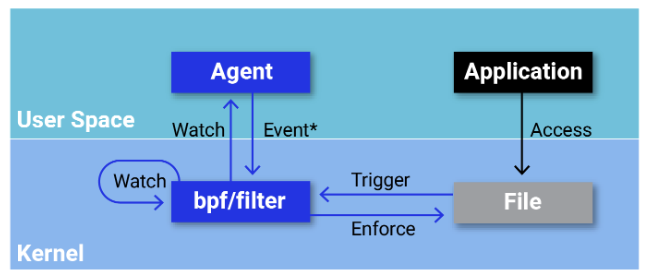
Seccomp, eBPF, and the Importance of Kernel System Call Filtering
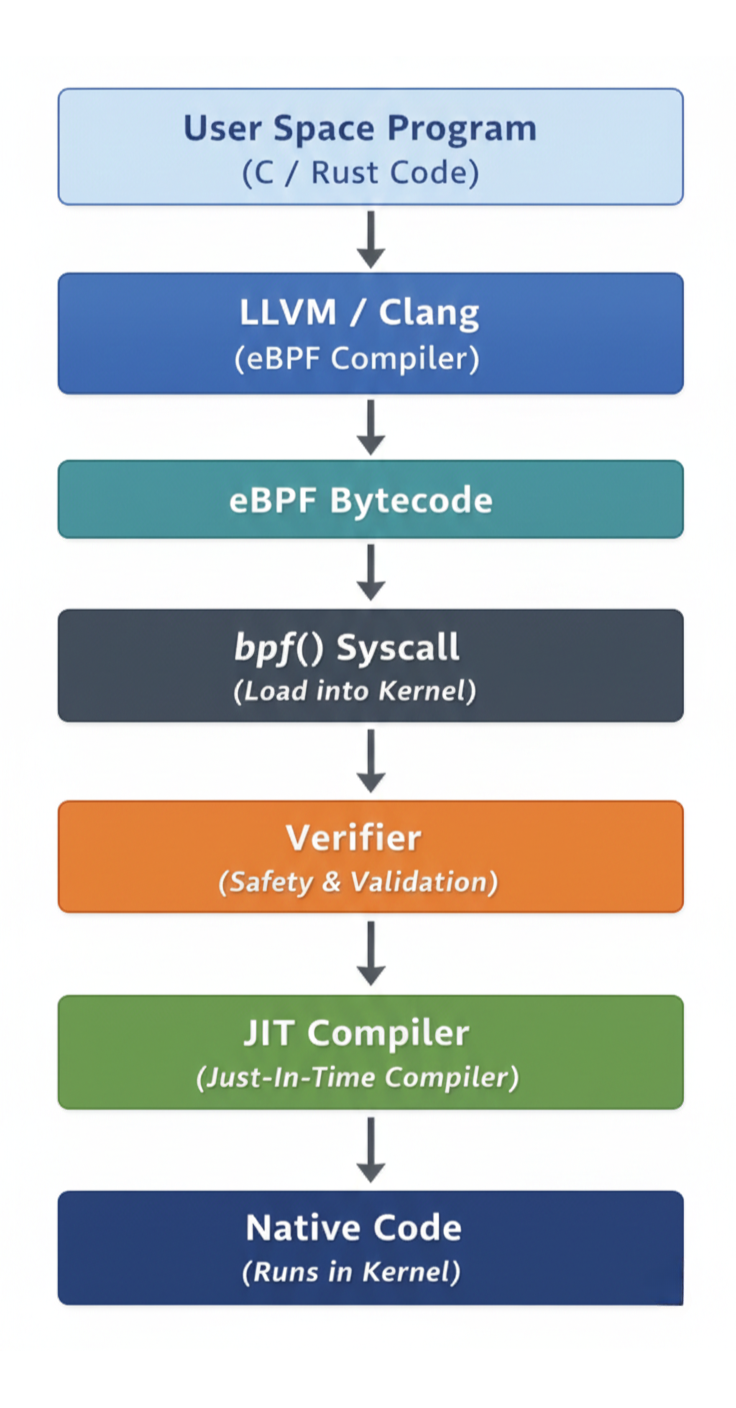
eBPF: Revolutionary Linux Kernel Tech for Observability & Security
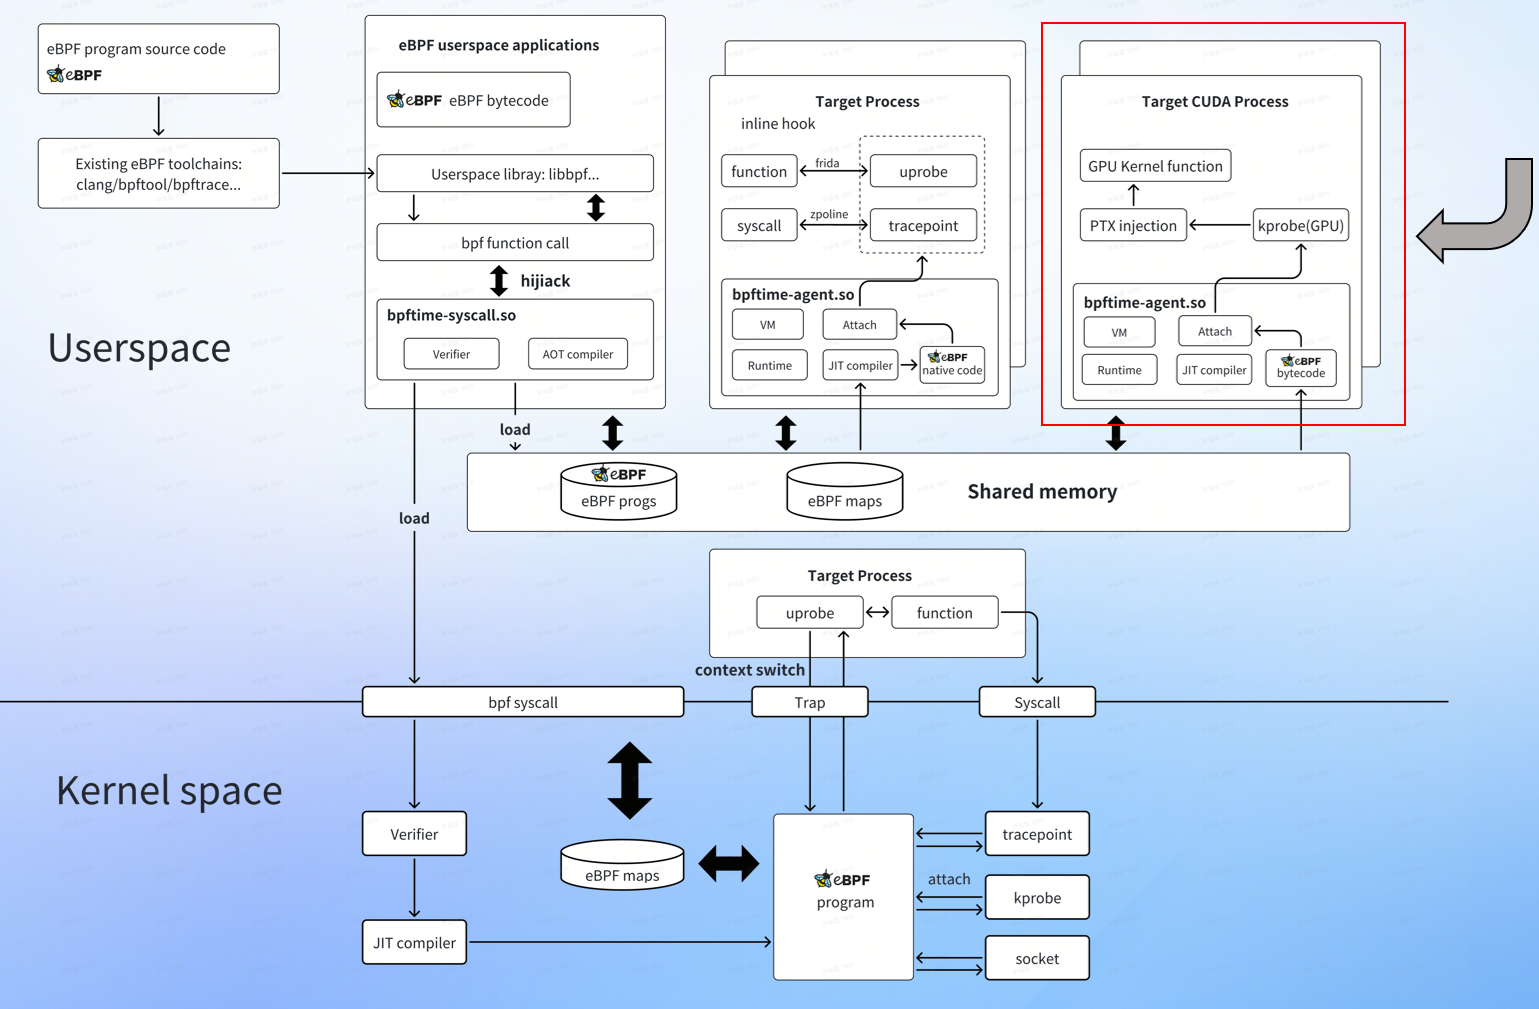
Extending eBPF to GPU Device and Driver Contexts - Slidev

Mastering eBPF Tracing - The Ultimate Guide For Performance Optimization
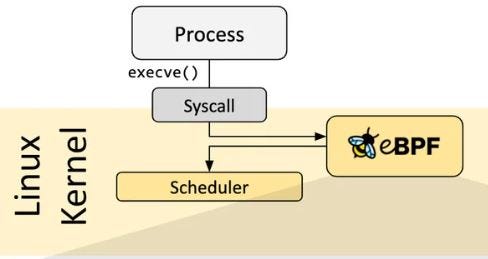
eBPF-Based Linux Filesystem Syscall Runtime Monitoring | by psy_maestro ...