
Github Forensicmattactivitiescacheparser Parse Windows
GitHub - forensicmatt/ActivitiesCacheParser: Parse Windows ...
GitHub - ZaikoARG/AmcacheParser: Forensic Windows Tool to parse the ...

GitHub - Pr0t3an/Greg: Cross Platform (Go app) - to parse Windows Tasks ...
GitHub - PoorBillionaire/Windows-Prefetch-Parser: Parse Windows ...

GitHub - vaidhy555/DigitalForensics: Project to automatically parse ...
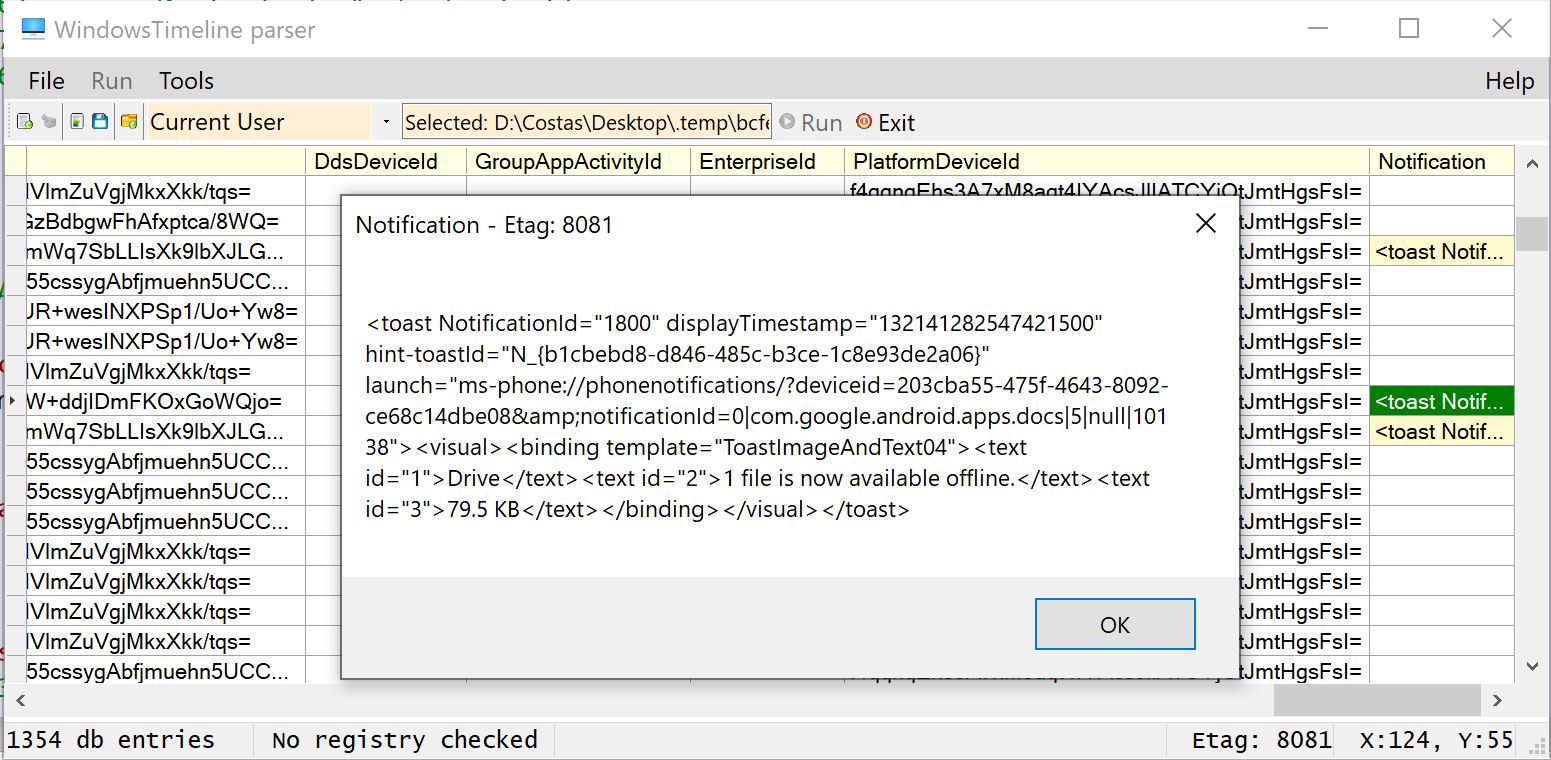
GitHub - kacos2000/WindowsTimeline: Windows 10 (v1803+) ActivitiesCache ...
GitHub - dfirdetective/WinSearchAppCache: Windows Search App Cache ...

GitHub - dfirdetective/WinSearchAppCache: Windows Search App Cache ...

GitHub - Oxygen1a1/oxgenPdb: a Windows kernel Pdb parsing and ...
GitHub - Matmaus/LnkParse3: Windows Shortcut file (LNK) parser · GitHub
Advertisement Space (300x250)

GitHub - auto-mos/AAS-Parser-for-Windows: AAS Parser for Windows 10 and ...
GitHub - WinWare19/Disk-parser: a windows tool that hepls extracting ...
GitHub - kasnria001/mtk_img_parser: Parse Mtk images including ...

GitHub - vaidhy555/DigitalForensics: Project to automatically parse ...
secretsdump.py does not parse Windows Server 2025 NTDS.dit · Issue ...
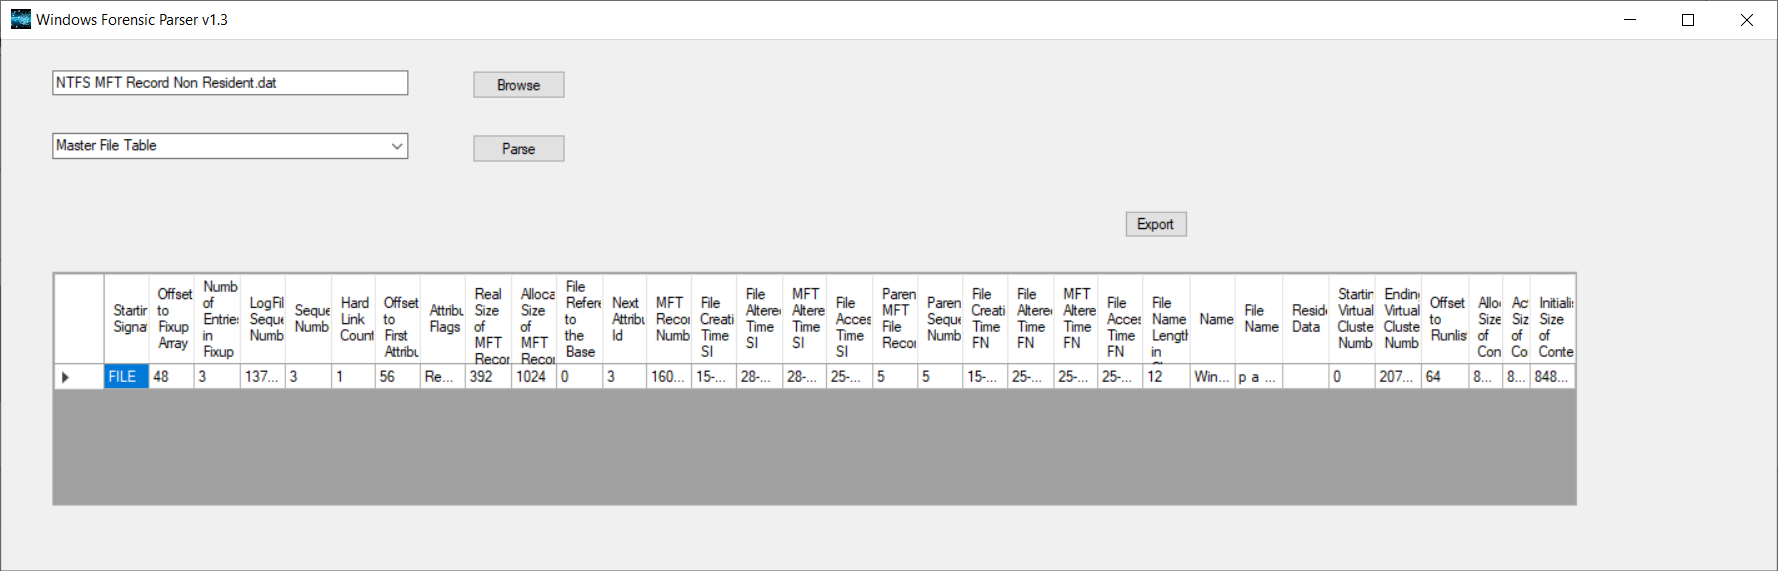
GitHub - vaidhy555/DigitalForensics: Project to automatically parse ...

Forensic Windows : comment trouver des traces avec ShimCache

Forensic Windows - Partie 2 : trouver des traces avec Amcache
GitHub - kevrocks67/recycle-bin-parser: Parses forensic artifacts found ...

GitHub - jklepsercyber/defender-detectionhistory-parser: A parser of ...
Advertisement Space (336x280)
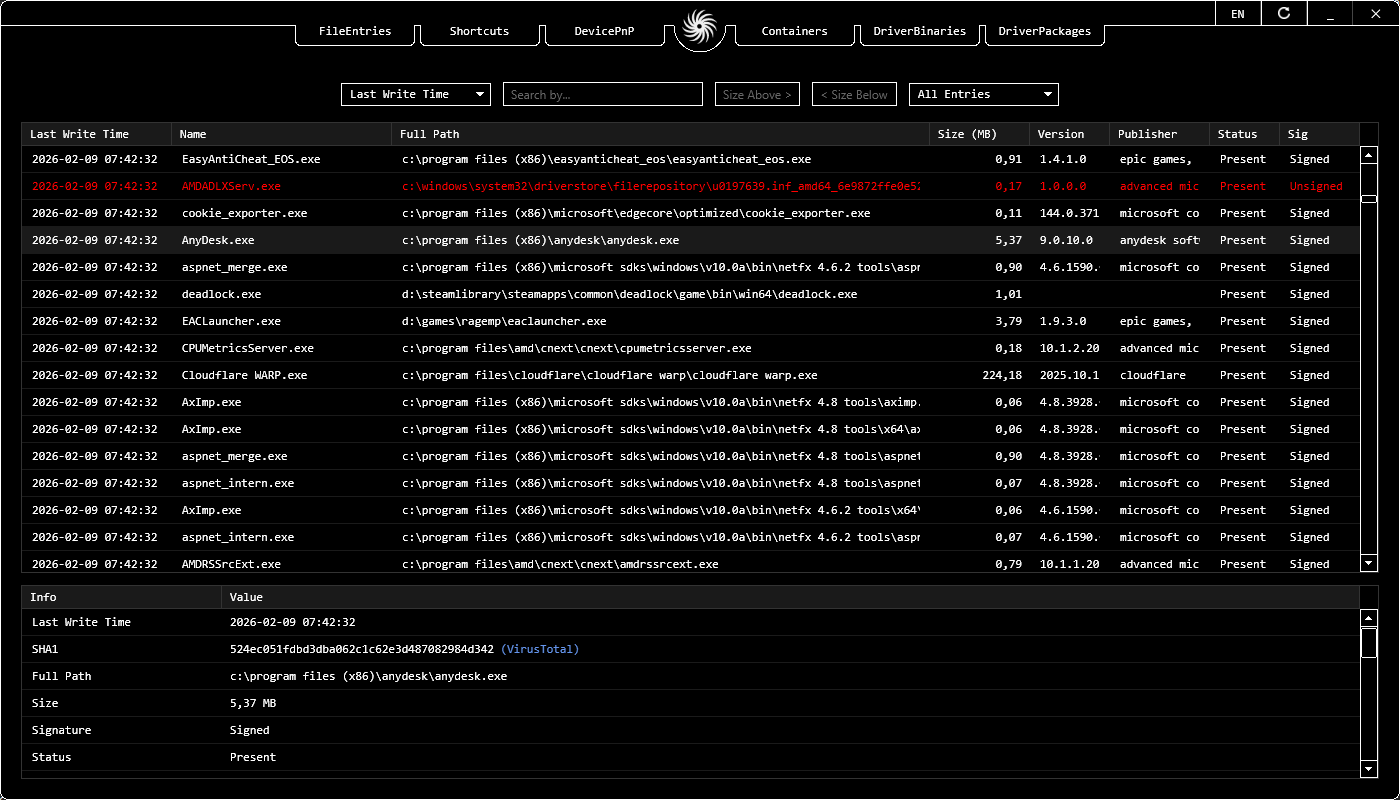
Windows 11 AmCache Parser, SHA1 Registry Extractor & Forensic Program ...
GitHub - jajp777/PS-WindowsForensics: PowerShell scripts for Hard Drive ...
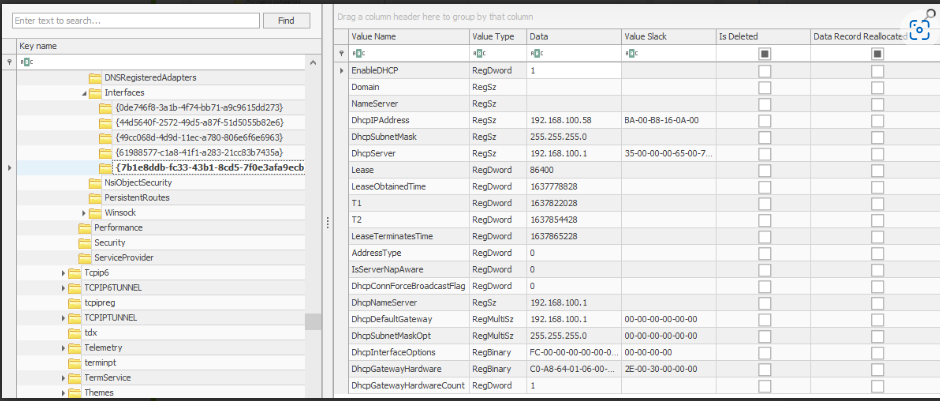
GitHub - m3dium/Windows-Forensics-1 · GitHub
GitHub - jwdfir/discord_cache_parser: A digital forensics toolset for ...
Registry Parser — Forensic Windows Registry Analysis

defender-detectionhistory-parser: A parser of Windows Defender's ...
GitHub - eve-sec/cache-parser-library: An EVE Online cache file parser ...
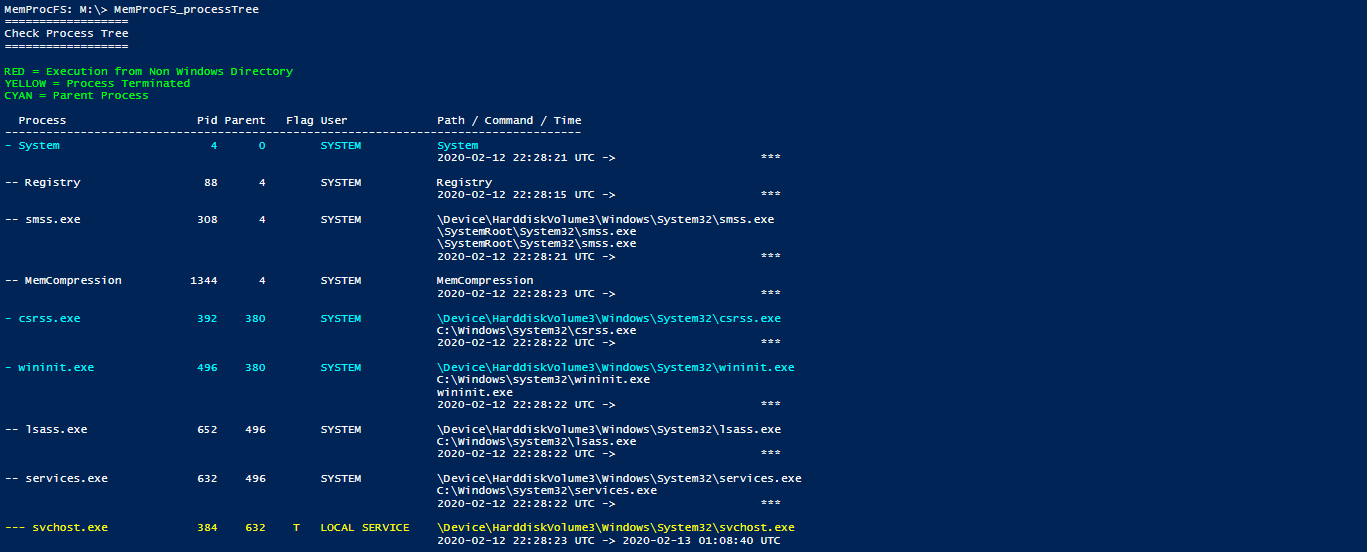
GitHub - memprocfshunt/MemProcFSHunter: A powershell parser for https ...

Forensic Windows - Partie 2 : trouver des traces avec Amcache
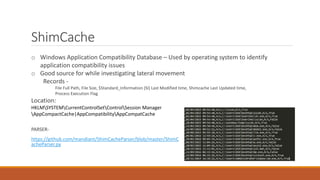
Windows Threat Hunting | PDF
Advertisement Space (336x280)
GitHub - FSchiltz/RawParser: This is a simple app for raw image ...
GitHub - mattcasmith/windows-logon-session-evtx-parser: PowerShell ...

Forensic Windows - Partie 2 : trouver des traces avec Amcache

GitHub - jklepsercyber/defender-detectionhistory-parser: A parser of ...
GitHub - max-scw/CaptureDataParser: Parser to handle the recordings of ...
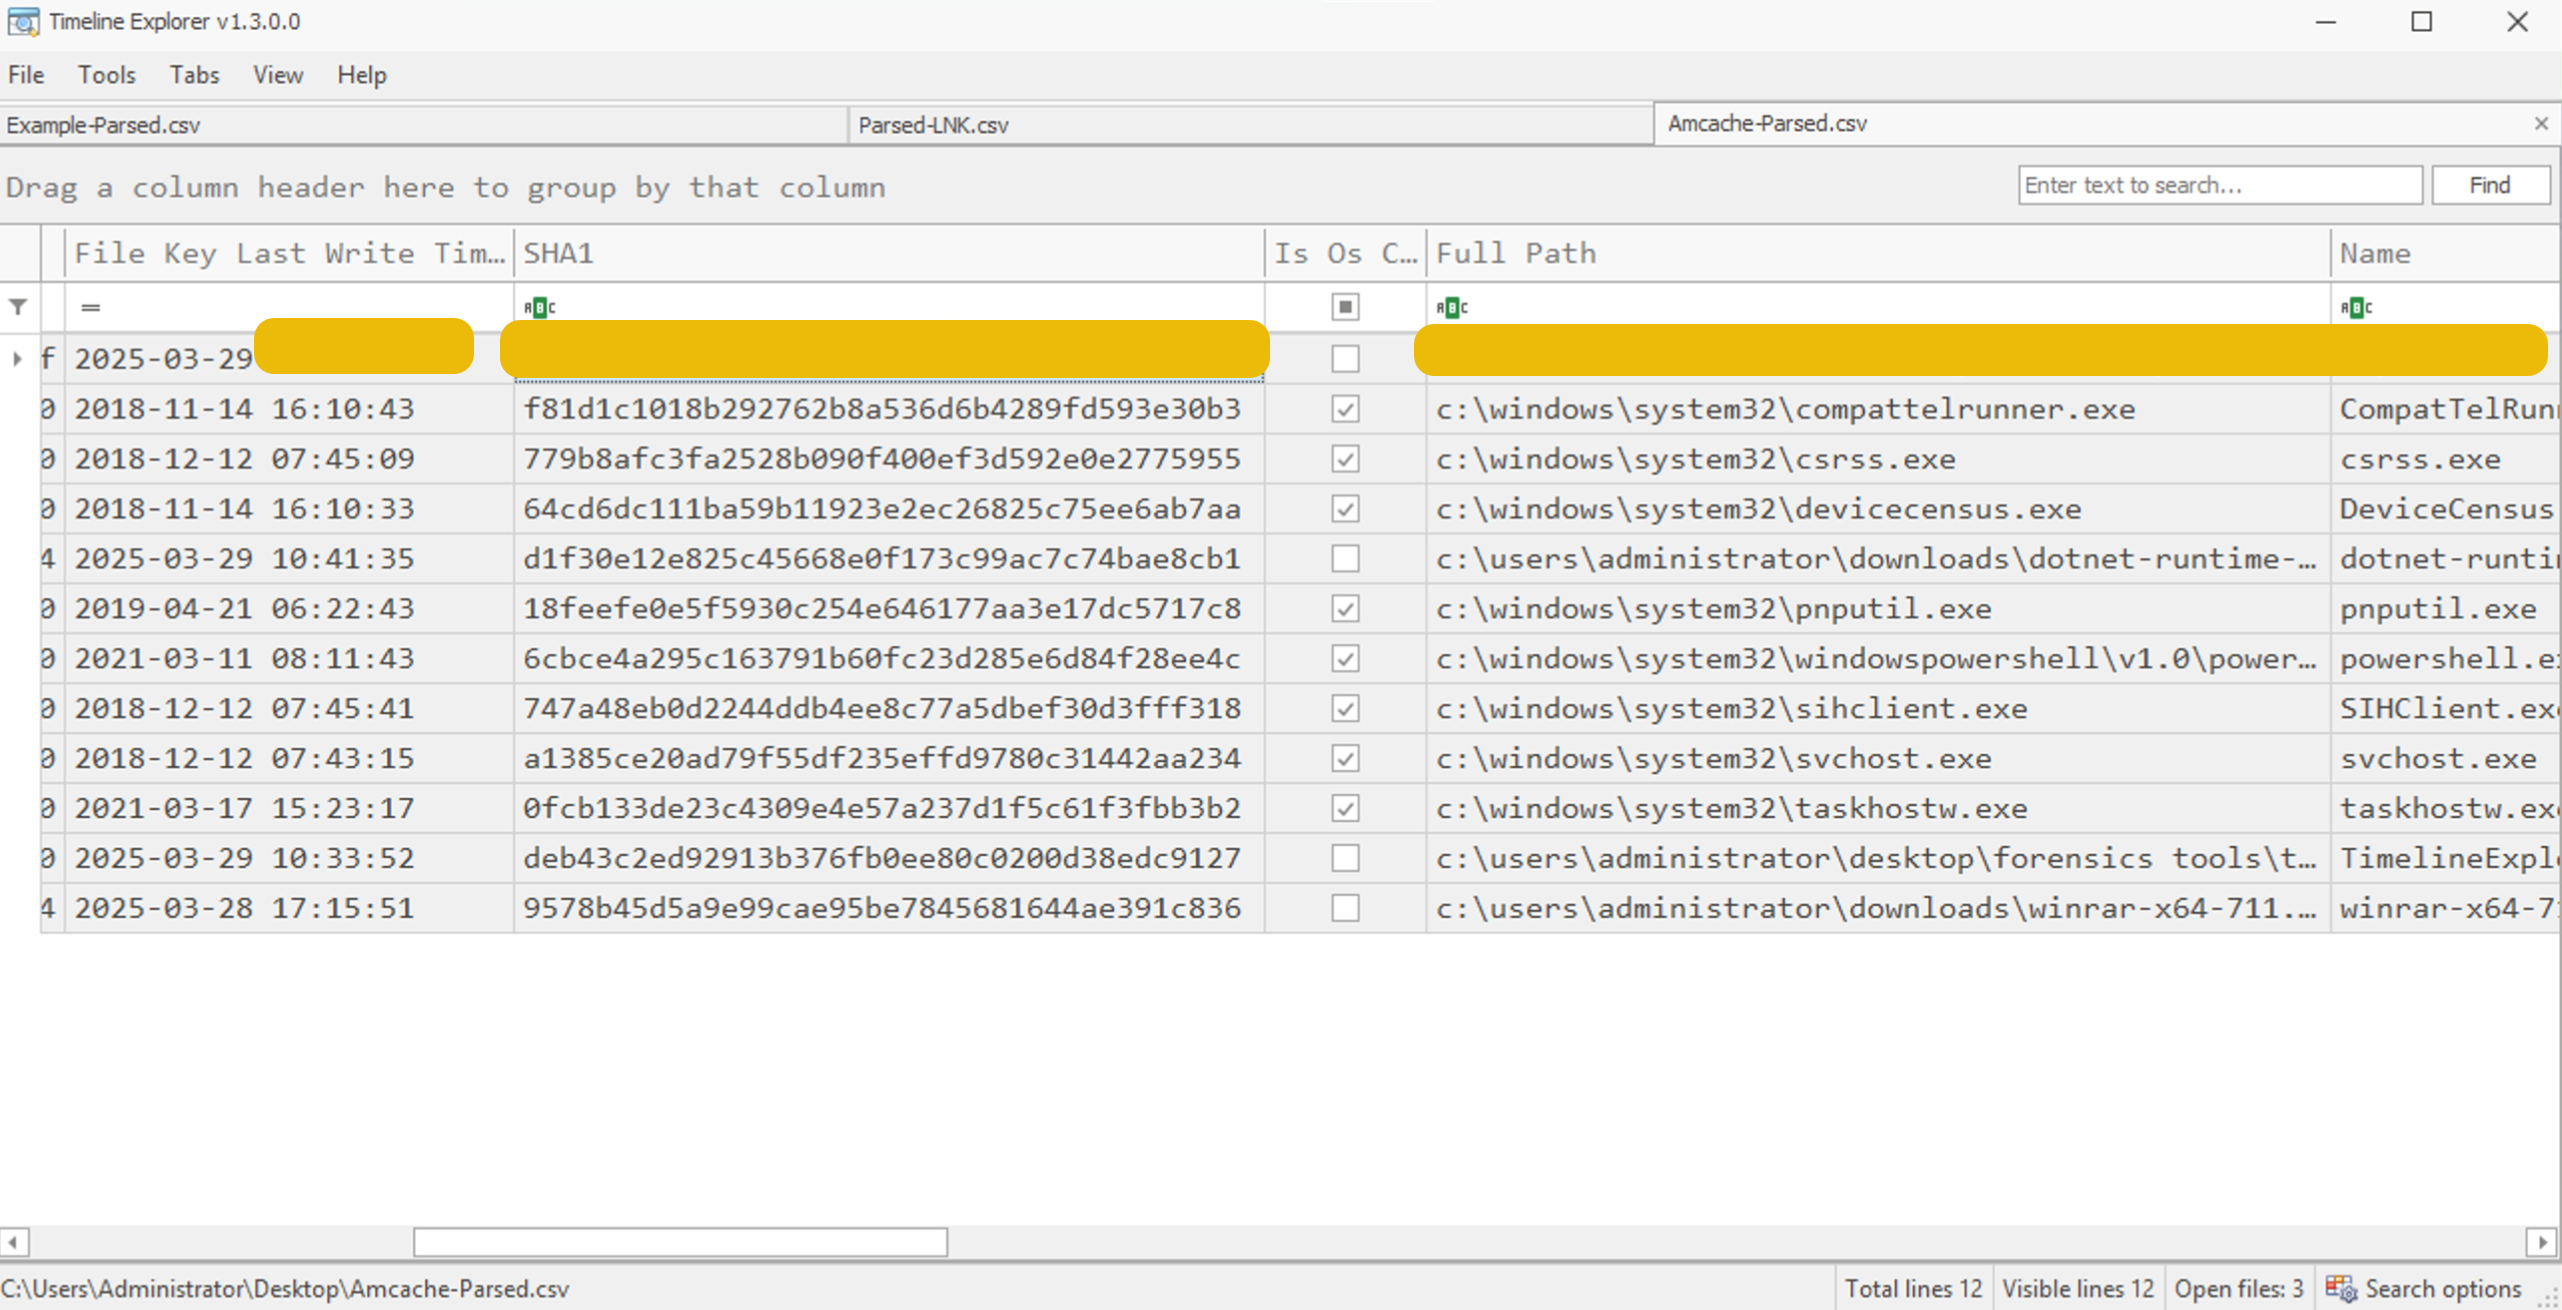
TryHackMe | Compromised Windows Analysis