
Ida Patch Packed Dll By Themida Reverse Engineering Stack Exchange

ida - Patch packed DLL by themida - Reverse Engineering Stack Exchange

dumping - Dump packed dll - Reverse Engineering Stack Exchange

dll - IDA Pro list COM methods - Reverse Engineering Stack Exchange

ida - Themida devirtualization? - Reverse Engineering Stack Exchange

dll - IDA Pro list COM methods - Reverse Engineering Stack Exchange

ida - Reverse engineering old mmo - Reverse Engineering Stack Exchange

ida plugin - IDA Pro Renaming Imports - Reverse Engineering Stack Exchange

IDA failed to construct correct graph - Reverse Engineering Stack Exchange

ida - Reverse function in .rdata field - Reverse Engineering Stack Exchange
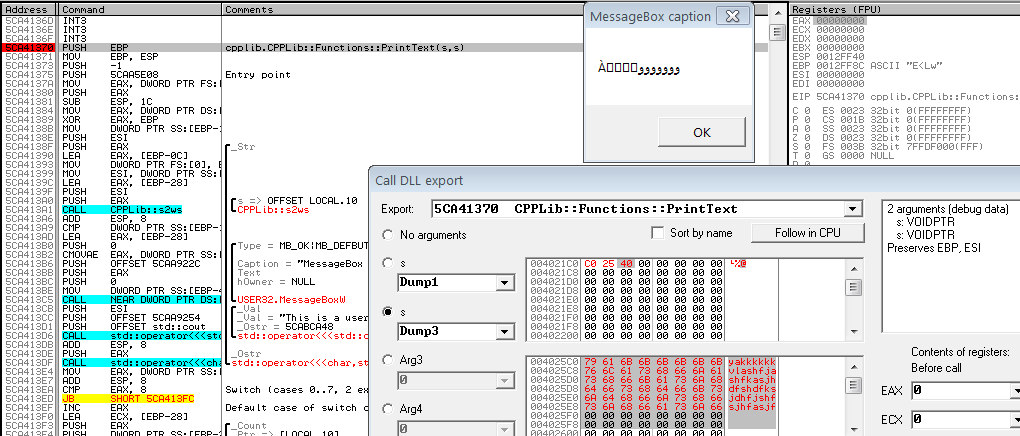
debugging - Call DLL export in OllyDBG - Reverse Engineering Stack Exchange
Advertisement Space (300x250)

IDA and hex editor different values - Reverse Engineering Stack Exchange

stack - Contents of EAX in IDA Free? - Reverse Engineering Stack Exchange

ida - Offset addressing - Reverse Engineering Stack Exchange

malware - what is Off in IDA Pro? - Reverse Engineering Stack Exchange

ida - Imports shifting in the dump - Reverse Engineering Stack Exchange

ida - identifying function prototype from dll - Reverse Engineering ...

disassembly - Patching a program in IDA - Reverse Engineering Stack ...

ida - How identify witch cpu run assembly - Reverse Engineering Stack ...

Rebuild IAT after manually unpacking DLL - Reverse Engineering Stack ...

IDA Pro failed decompilation with "JUMPOUT" - Reverse Engineering Stack ...
Advertisement Space (336x280)

ida - Permanently load a DLL to an executable - Reverse Engineering ...

Packer changed memory in IDA? - Reverse Engineering Stack Exchange

disassembly - dll injection (assembly code) - Reverse Engineering Stack ...

patching - IDA binary patch "has no file mapping" - Reverse Engineering ...

ida - Permanently load a DLL to an executable - Reverse Engineering ...

Rebuild IAT after manually unpacking DLL - Reverse Engineering Stack ...

c++ - IDA Free vs IDA Home (to have Lumina) - Reverse Engineering Stack ...

ida - Permanently load a DLL to an executable - Reverse Engineering ...

Reverse Engineering #1 / Basic IDA Usage – Attacker's Mindset

ida - Exported DLL function has only stdcall with some offset - Reverse ...
Advertisement Space (336x280)

ida - A way to detect a anti-cheating system - Reverse Engineering ...

decompiler - Why is IDA call analysis failing? - Reverse Engineering ...
A Powerful IDA Pro Plugin For Malware Reverse Engineering - Cybernoz ...

reverse engineering - IDA PRO address issue - Information Security ...

ida - How to deal with msvc runtime integrity? - Reverse Engineering ...
Reverse engineering of the extracted firmware with IDA | Download ...