
Missing Data Uf Splunk Community

Missing data UF - Splunk Community

data missing in chart dashboard view - Splunk Community
Missing data observed on Splunk Observability Cloud dashboard charts ...
Missing data observed on Splunk Observability Cloud dashboard charts ...
Missing data observed on Splunk Observability Cloud dashboard charts ...
Data Missing due to Bucket ID Conflicts in Smartstore Deployment | Splunk

Why is uploaded data missing? - Splunk Community

Solved: How to fill empty or missing data values based on ... - Splunk ...

Solved: How to fill empty or missing data values based on ... - Splunk ...

data on indexers disappeared - Splunk Community
Advertisement Space (300x250)

Solved: Selected Fields are missing - Splunk Community

Splunk enterprise not receive any data from Univer... - Splunk Community

Solved: Re: Notification when file is missing - Splunk Community

Solved: Re: Notification when file is missing - Splunk Community

Error saving event-based detection. Missing detect... - Splunk Community

Solved: Data Models and incomplete source data - Splunk Community

See just what you’ve been missing | Observability ... - Splunk Community

Solved: Stats missing on 9.2 Indexes page - Splunk Community

See just what you’ve been missing | Observability ... - Splunk Community

Sourcetype Missing - Splunk Community
Advertisement Space (336x280)

Unable to access event data for comparison reasons - Splunk Community

Indexer Clustering > Data Durability > Replication... - Splunk Community

Troubleshooting EUM custom user data - Splunk Community

Cannot get data Index in Datamodel - Splunk Community

Error message "Unable to retrieve the favorite dat... - Splunk Community

Splunk UF en Linux: envío de logs desde endpoints | Cristian Rebollo

Having errors as a beginner - Splunk Community

Why am I not seeing the finding in Splunk Enterpri... - Splunk Community

Solved: Why aren't all values shown in dashboard? - Splunk Community
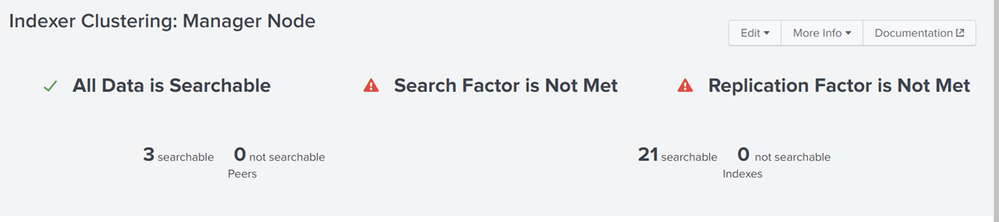
Solved: Search Factor is Not MeT - Splunk Community
Advertisement Space (336x280)
Troubleshooting Missing Events in Splunk Indexes - ThinkCloudly

Solved: Why is Lookup command not working? - Splunk Community

Why am I not seeing the finding in Splunk Enterpri... - Splunk Community

Solved: Why aren't all values shown in dashboard? - Splunk Community
Missing indexes in user role configuration. | Splunk

Solved: Why aren't all values shown in dashboard? - Splunk Community