
Solved Selected Fields Are Missing Splunk Community

Solved: Selected Fields are missing - Splunk Community

Solved: Selected Fields are missing - Splunk Community
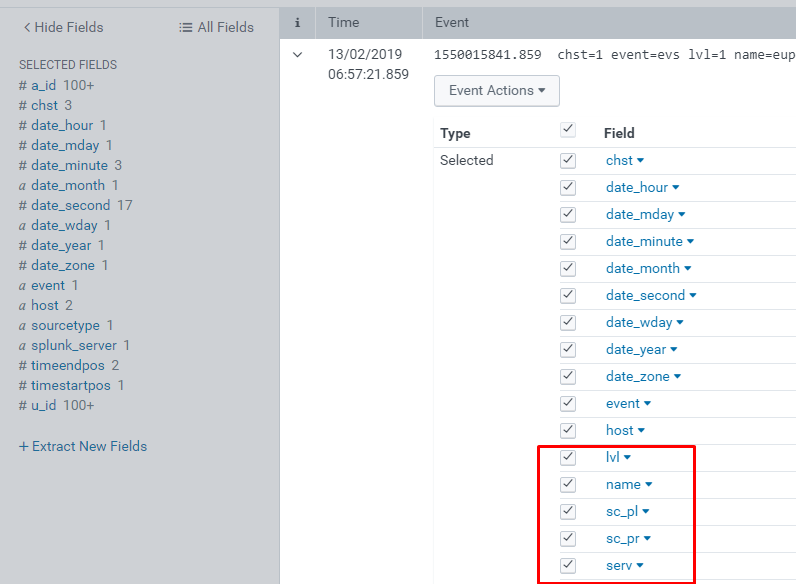
SELECTED FIELDS - Splunk Community

SELECTED FIELDS - Splunk Community

SELECTED FIELDS - Splunk Community

Solved: How to convert selected fields to FQDN - Splunk Community

Solved: How to convert selected fields to FQDN - Splunk Community

Solved: XML Event Viewer Data Missing Message\Fields - Splunk Community

Solved: How to show more selected fields on dashboard even... - Splunk ...

Solved: How to select one of two event fields in stats? - Splunk Community
Advertisement Space (300x250)

Solved: Re: Notification when file is missing - Splunk Community

Solved: Compare fields without wildcards - Splunk Community

Solved: Re: Notification when file is missing - Splunk Community

Solved: Compare fields without wildcards - Splunk Community
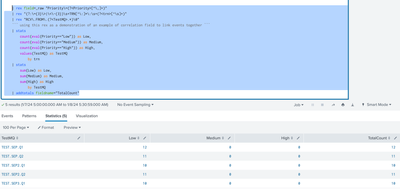
Solved: Splunk stats count group by multiple fields - Splunk Community
Annotations fields missing in Splunk ES correlation search | Splunk
Extra/Unnecessary Fields are getting extracted during search time | Splunk

Missing data UF - Splunk Community
Extra/Unnecessary Fields are getting extracted during search time | Splunk

Error saving event-based detection. Missing detect... - Splunk Community
Advertisement Space (336x280)

Solved: How i can remove unused fields in extracted fields... - Splunk ...
Missing "Selected Fields" with json data collected using HEC | Splunk

Solved: Splunk App for Windows - Missing Task Category, Ev... - Splunk ...
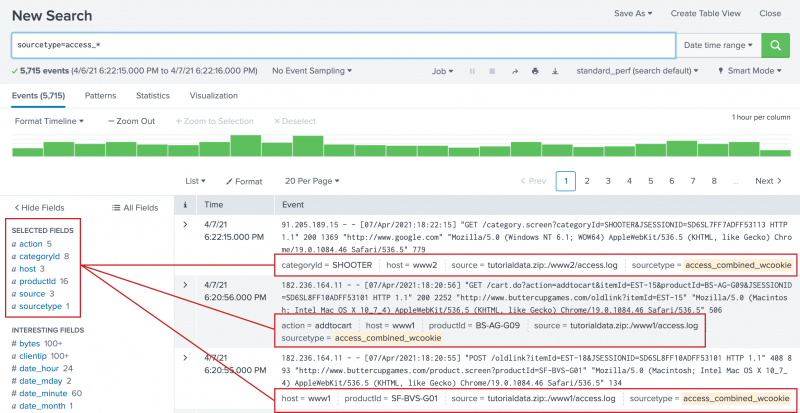
Use fields to search - Splunk Documentation
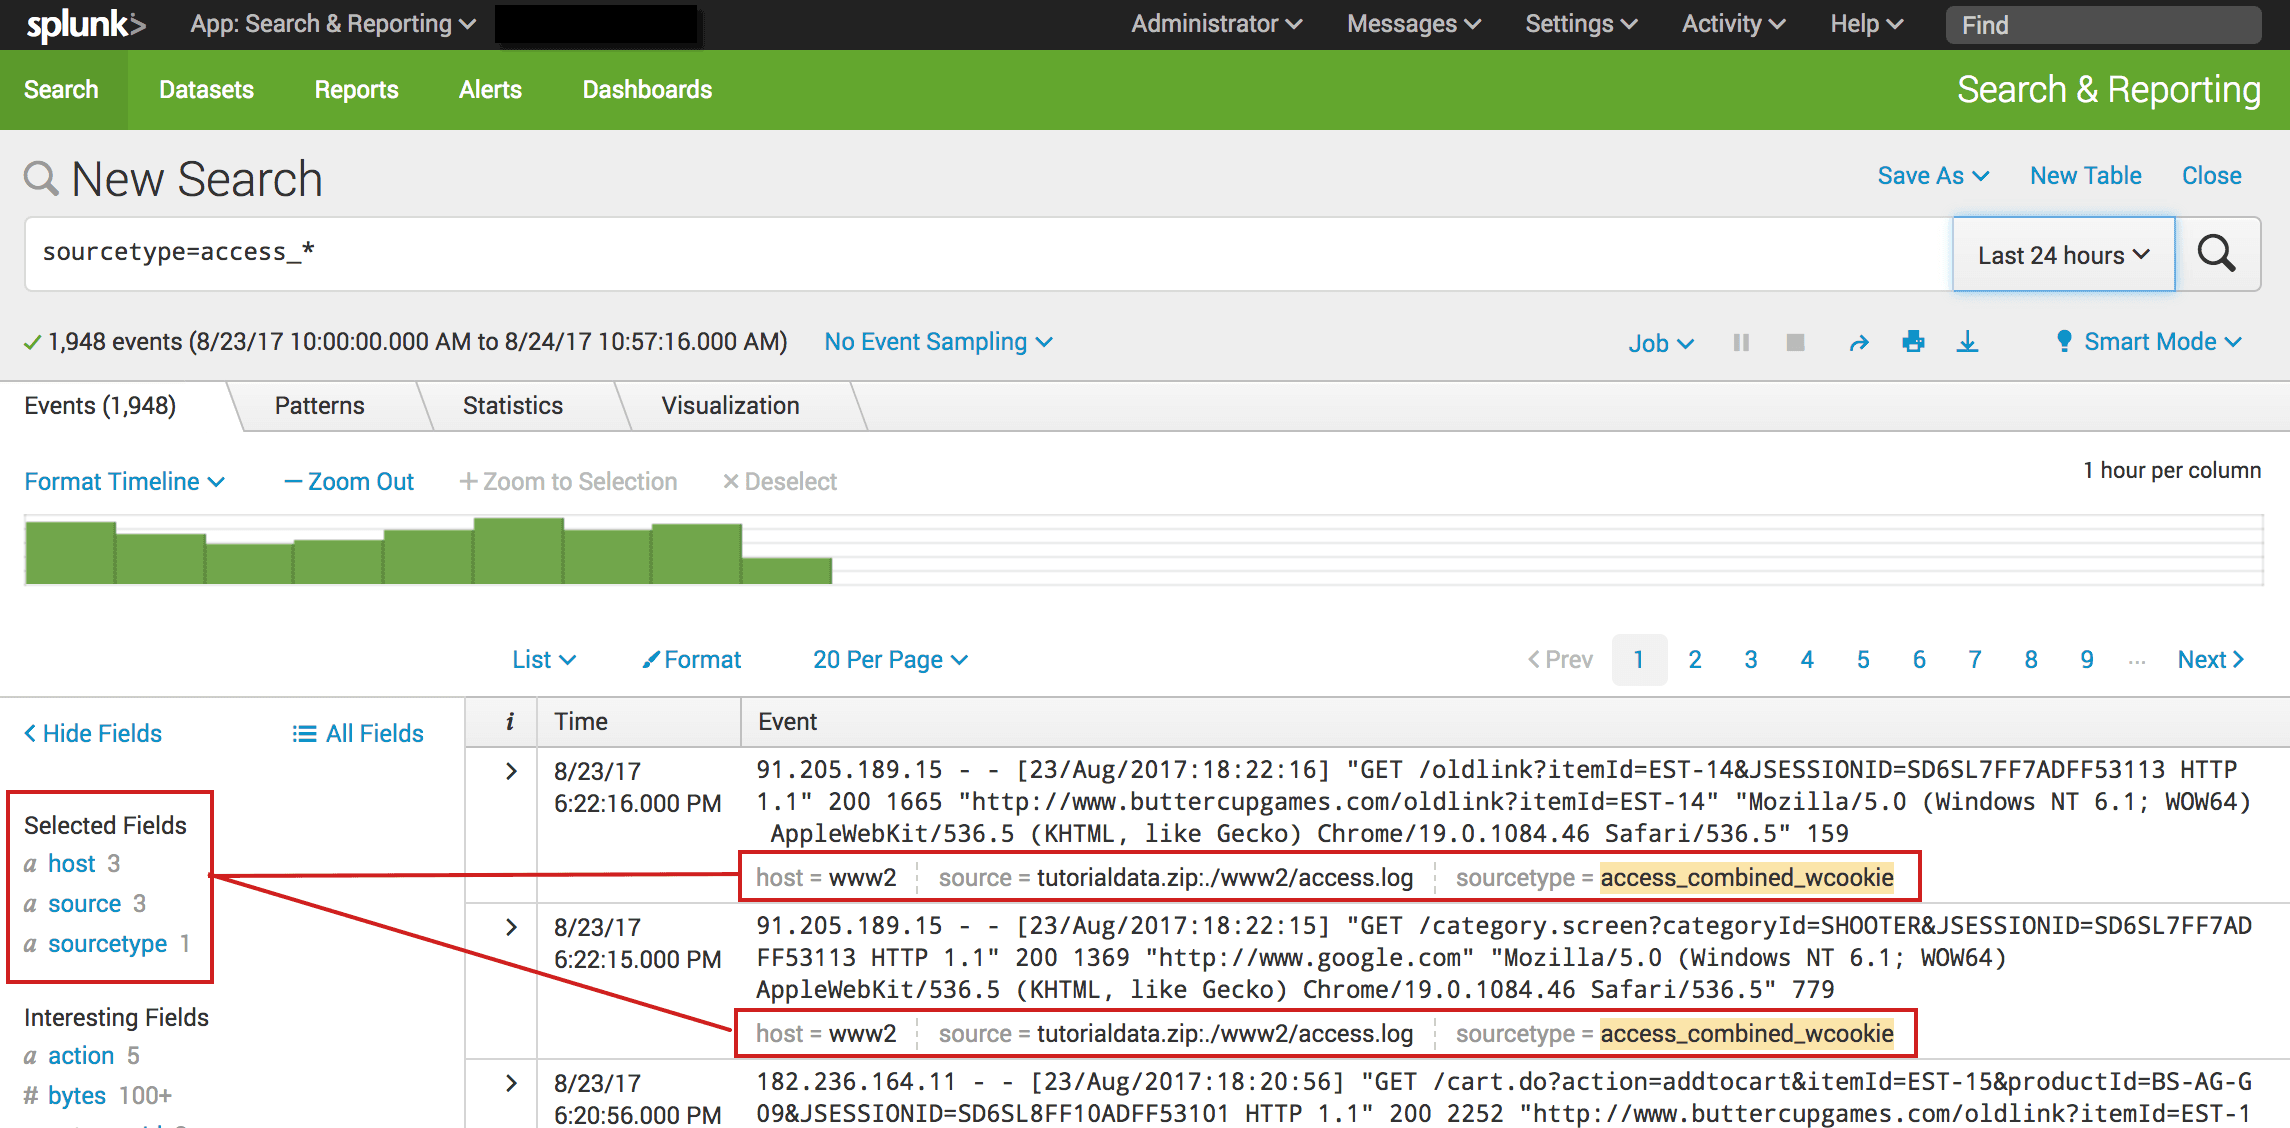
Use fields to search - Splunk Documentation
Selected Fields and Interesting Fields showing intermittently in some ...
Selected Fields and Interesting Fields showing intermittently in some ...

Solved: Can't select timestamp field on DB Connect App? - Splunk Community

Solved: How can I extract multiple fields? - Splunk Community

Solved: Why am I Unable to extract fields from package sou... - Splunk ...
Advertisement Space (336x280)

Solved: How to use Splunk AND command to find field 3? - Splunk Community

Understanding Splunk Default Fields | PDF

Syntax highlighting of Splunk search results is missing when grouping ...

Having errors as a beginner - Splunk Community
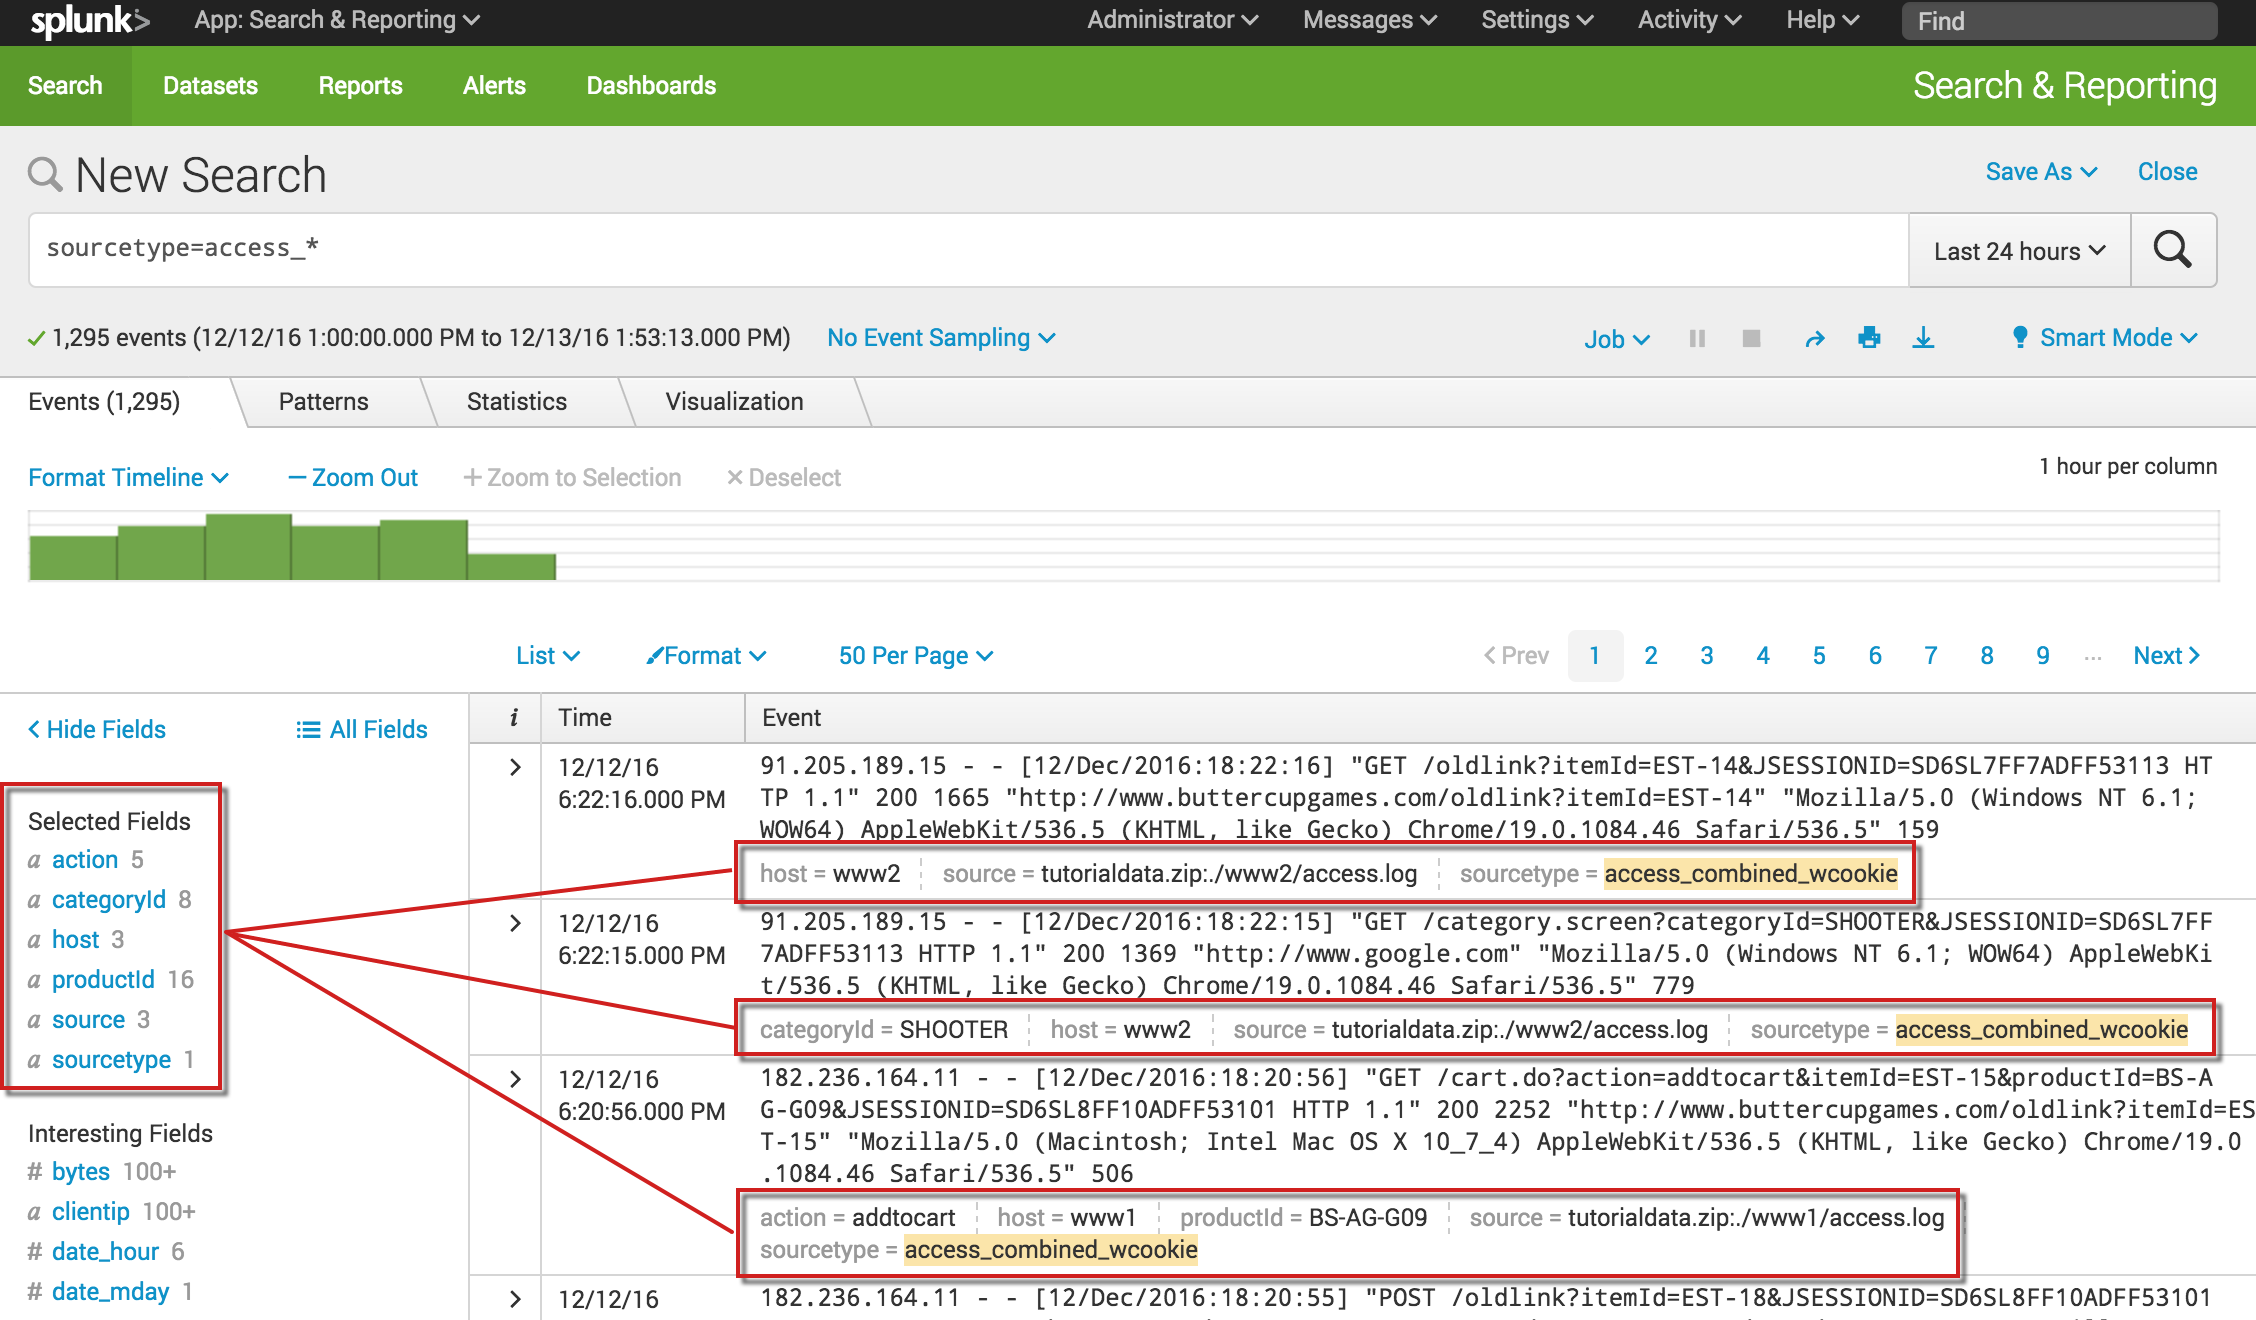
Splunk Find Field Name _ List all fields for an index – YEUNNO

Splunk Fields Explained at Barbara Fowler blog