
Solved Xml Event Viewer Data Missing Messagefields Splunk Community

Solved: XML Event Viewer Data Missing Message\Fields - Splunk Community
Solved: XML Event Viewer Data Missing Message\Fields - Splunk Community

Solved: XML Event Viewer Data Missing Message\Fields - Splunk Community

Missing data UF - Splunk Community
Windows Event field data truncated or missing when ingested into splunk ...

How do you troubleshoot missing windows event logs... - Splunk Community

Unable to access event data for comparison reasons - Splunk Community
Windows event logs incomplete in Splunk due to XML format — messages ...
Windows event logs incomplete in Splunk due to XML format — messages ...
Windows event logs incomplete in Splunk due to XML format — messages ...
Advertisement Space (300x250)
Windows event logs incomplete in Splunk due to XML format — messages ...
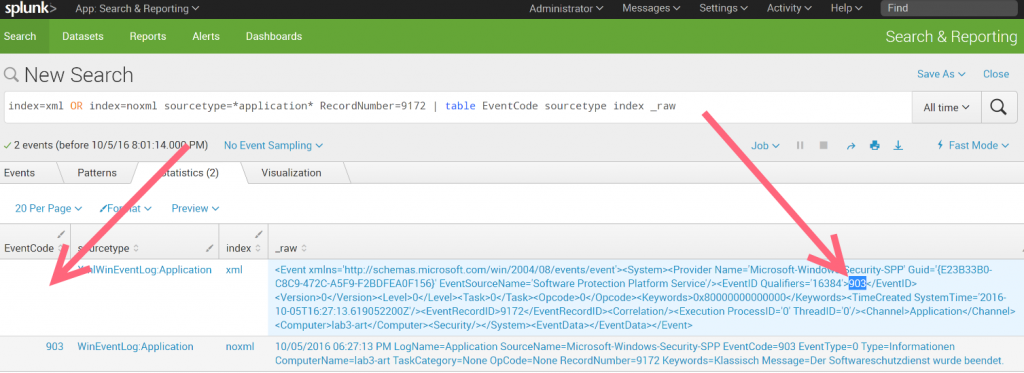
Why using XML Event Logs sucks using Splunk | batchworks.de

Solved: How to parse XML and props.conf? - Splunk Community
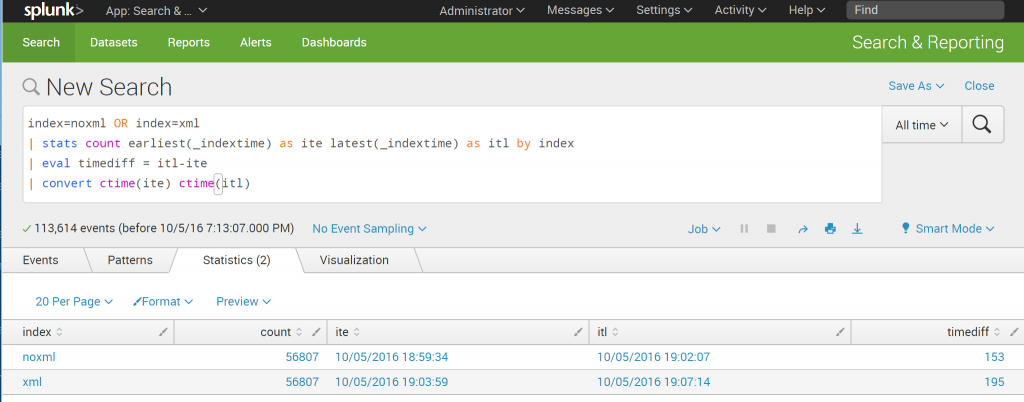
Why using XML Event Logs sucks using Splunk | batchworks.de

Solved: splunk xml dashboard - Splunk Community

How do you extract the following XML fields? - Splunk Community

Solved: Selected Fields are missing - Splunk Community

Solved: Re: Notification when file is missing - Splunk Community

Solved: Re: Notification when file is missing - Splunk Community

Error saving event-based detection. Missing detect... - Splunk Community
Advertisement Space (336x280)

Why is uploaded data missing? - Splunk Community

Why is uploaded data missing? - Splunk Community
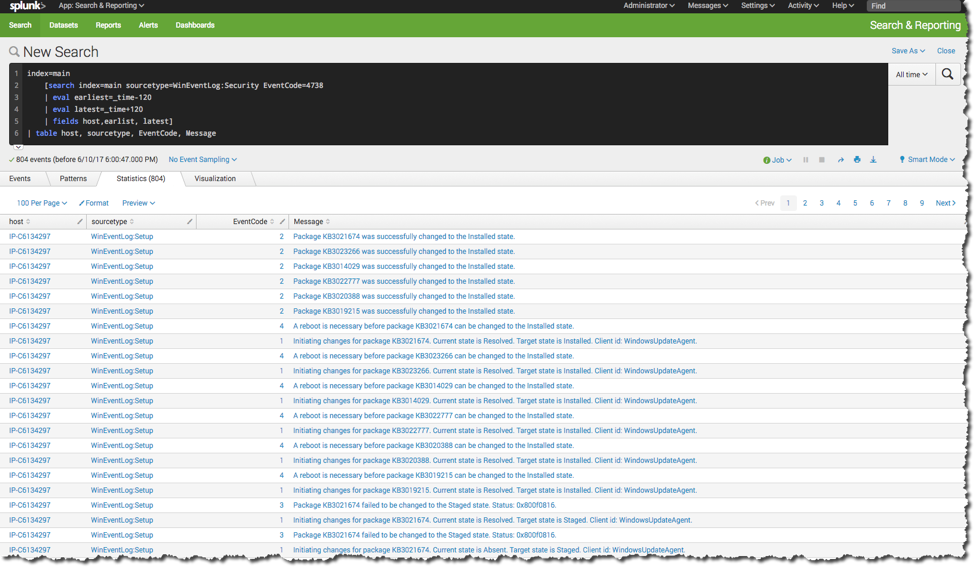
Forwarding Windows Event Viewer Logs To Splunk – RRYBDI

Windows Event Log Xml Splunk at Mary Amundson blog
Data sent using HTTP Event Collector is missing or not indexed in ...
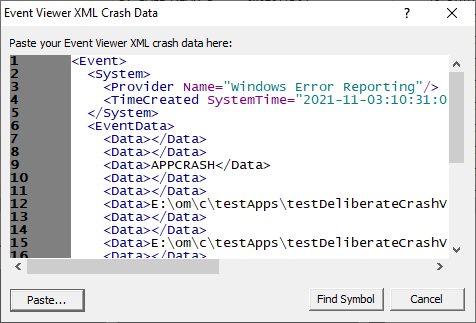
Decoding an Event Viewer XML crash log

Solved: Why is my Azure Event Hub not sending data? - Splunk Community

Splunk not seeing all Event Logs - Networking - Spiceworks Community

Monitor Windows event log data with Splunk Cloud Platform | Splunk ...

Sysmon events not being parsed — stuck as xmlwinev... - Splunk Community
Advertisement Space (336x280)
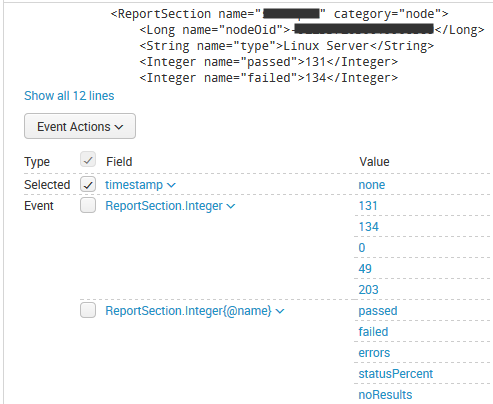
Tips for parsing XML log files in Splunk
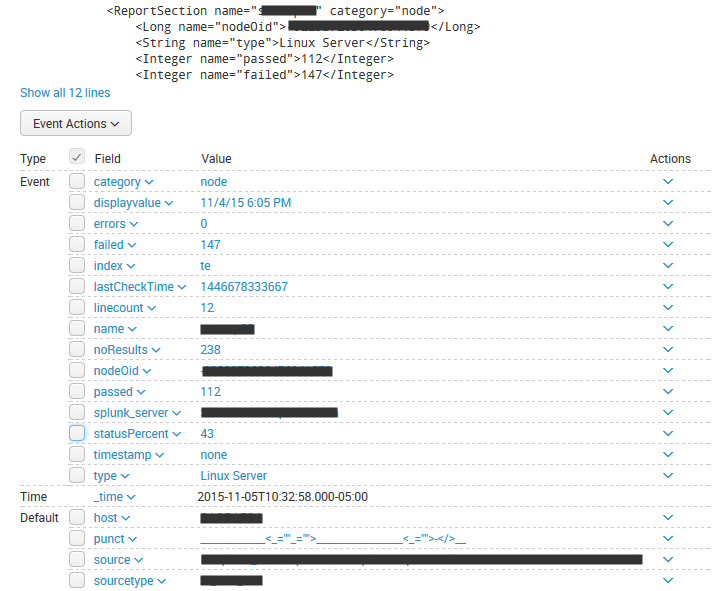
Tips for parsing XML log files in Splunk

Sysmon events not being parsed — stuck as xmlwinev... - Splunk Community
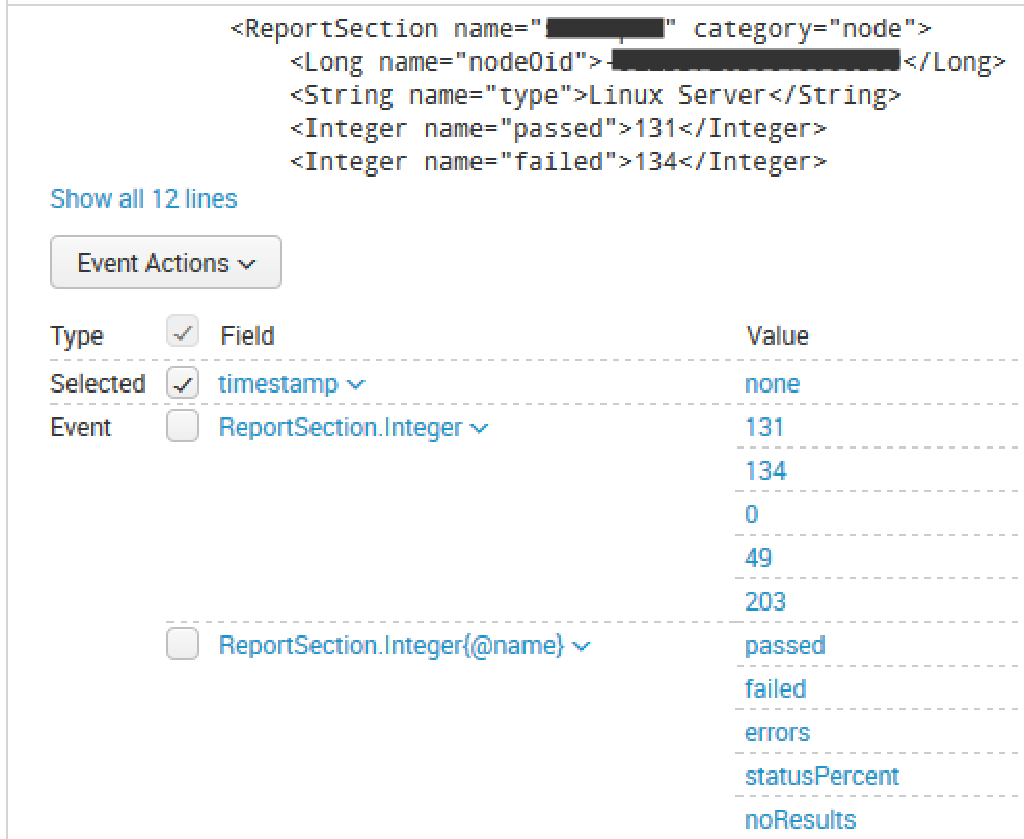
Tips for parsing XML log files in Splunk
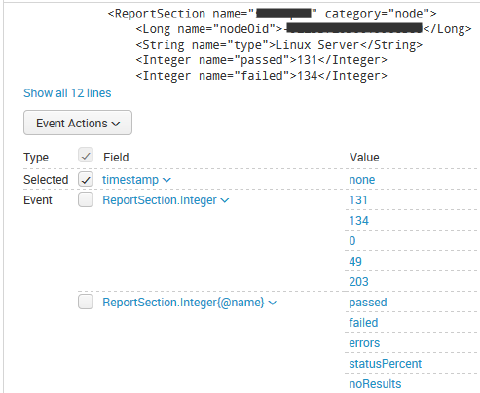
Tips for parsing XML log files in Splunk

Sysmon events not being parsed — stuck as xmlwinev... - Splunk Community